update
 arraykeys
@@ -0,0 +1,340 @@
|
||||
proxy更新日志
|
||||
|
||||
v7.5
|
||||
1.http(s)\socks\sps 增加了本地监听单向tls支持.
|
||||
2.socks5协议兼容了更多不标准的客户端.
|
||||
3.可以使用第三方安卓客户端对接proxy的socks5服务了,支持认证.
|
||||
4.修复了多处不能正常使用ipv6的bug.
|
||||
|
||||
v7.4
|
||||
1.优化了命令行kcp参数的设置,help命令不再强制显示,只有拥有kcp功能的模块才会显示.
|
||||
2.内部增加了插件机制,拓展功能十分方便.
|
||||
3.重构了对配置文件的解析,不再限制参数格式,书写更简单.
|
||||
4.内网穿透增加了http协议的增强支持,增加了--http-host参数,可以强制设置http头部的HOST字段值.
|
||||
HTTP请求客户端会使用server的ip和端口去设置HOST字段,但是与期望的后端实际HOST不一样,这样就造成了tcp是通的,
|
||||
但后端依赖HOST字段定位虚拟主机就不能工作.现在用--http-host参数强制设置http头部的HOST字段值为后端实际的
|
||||
域名和端口即可轻松解决.
|
||||
|
||||
v7.3
|
||||
1.重构了SPS的SS功能,go版本ss,全网唯一一家支持最全加密方式,支持如下:
|
||||
aes-128-cfb , aes-128-ctr , aes-128-gcm , aes-192-cfb , aes-192-ctr , aes-192-gcm , aes-256-cfb ,
|
||||
aes-256-ctr , aes-256-gcm , bf-cfb , cast5-cfb , chacha20 , chacha20-ietf , chacha20-ietf-poly1305 ,
|
||||
des-cfb , rc4-md5 , rc4-md5-6 , salsa20 , xchacha20
|
||||
2.修复某些情况下,--forever可能不能预期工作的问题.
|
||||
3.修复在某些特殊Linux系统下启动失败的问题.
|
||||
4.重构了核心服务管理代码,提升了效率.
|
||||
5.优化了dns功能,支持多个上级负载均衡和高可用,上级写法和SPS的-P参数一致.
|
||||
6.修复了--forever和--deamon存在的资源清理隐患问题.
|
||||
7.优化了更新,提升了稳定性.
|
||||
8.http认证某些特殊情况下不能正常工作的问题.
|
||||
9.优化了所有服务的资源释放,避免某些情况下导致异常的问题.
|
||||
10.SDK得到大量优化,不再会出现并发启动和停止在某些情况下导致异常的问题.
|
||||
|
||||
v7.2
|
||||
1.sps功能增加了不再强制指定一个上级,当上级为空,sps本身即可完成完整的代理功能.
|
||||
如果指定了上级那么就和之前一样使用上级连接目标,
|
||||
2.修复了dns,加密传输-z和-Z参数不能正常工作的问题.
|
||||
3.优化了启动速度,提升了稳定性.
|
||||
4.取消发布几乎没人使用的平台上的二进制.
|
||||
|
||||
v7.1
|
||||
1.socks/http(s)/sps代理,负载均衡里面的权重标志符号由`@`变更为`#`.
|
||||
2.sps支持同时使用不同类型的上级,比如你可以用sps同时使用socks,http,ss三种类型的上级,
|
||||
详细情况请看手册`设置单独认证信息`和`设置单独认证信息的协议类型`
|
||||
3.sps代理,上级设置单独认证信息里面的用户名和密码不再使用base64编码,变更为标准的URLEncode编码.
|
||||
4.修复了所有服务在某些情况下不能正常停止服务释放资源的问题.
|
||||
5.重构了部分代码,运行更加高效.
|
||||
6.socks/http(s)/sps代理增加了域名黑名单支持,用--stop参数指定一个域名列表文件,
|
||||
那么当用户连接文件里面这些域名的时候连接就会被断开.域名文件内容格式参见手册:"域名黑名单".
|
||||
7.针对windows增加了隐藏界面的启动脚本,bootstrap.bat里面可以设置参数,start.vbs是启动脚本.
|
||||
8.增加了一个广告域名列表文件40000+个域名,已经打包在发布的版本压缩包内.
|
||||
|
||||
v7.0
|
||||
1.修复了socks代理,上级为ssh的时候,不能正常工作的问题.
|
||||
|
||||
v6.9
|
||||
1.修复了sps的start潜在的crash问题.
|
||||
2.sps代理增加了--parent-tls-single参数用来支持单向tls上级。
|
||||
3.sps代理增加了对单个上级认证信息的支持,如果没有单独设置,就使用全局-A设置.
|
||||
现在上级格式: -P YTpi#2.2.2.2:33080@1
|
||||
说明:
|
||||
YTpi 是经过base64编码的认证信息,比如是http(s)/socks原始认证信息a:b,用户是a密码是b,base64编码之后是:YTpi
|
||||
如果是ss,那么a就是加密方法,b是密码,比如:aes-192-cfb:your_pass,base64编码之后是:YWVzLTE5Mi1jZmI6eW91cl9wYXNz
|
||||
# 是间隔符号,如果有认证信息,必须有#,没有认证信息可以省略#.
|
||||
2.2.2.2:33080 是上级地址
|
||||
@1 是设置权重,可以参考手册权重部分.
|
||||
4.修复了socks5代理错误处理超时的问题.
|
||||
5.修复了http(s)代理错误处理-Z的问题.
|
||||
|
||||
v6.8
|
||||
1.HTTP(S)\SOCKS5代理,API认证功能,发送给认证接口的参数增加了本地IP,local_ip字段,
|
||||
代表用户访问的是本地服务器的哪个IP.
|
||||
2.fix #194 , fix #134 , 代理更稳定.
|
||||
3.增加了一波英文文档.
|
||||
|
||||
v6.6
|
||||
1.优化了limitconn的关闭逻辑,释放更多资源.
|
||||
2.http(s)\socks代理增加了--intelligent,智能模式设置,可以是intelligent|direct|parent三者之一,
|
||||
默认是:intelligent.每个值的含义如下.
|
||||
--intelligent=direct,不在blocked里面的目标都直连.
|
||||
--intelligent=parent,不在direct里面的目标都走上级.
|
||||
--intelligent=intelligent,blocked和direct里面都没有的目标,智能判断是否使用上级访问目标.
|
||||
|
||||
v6.5
|
||||
1.修复了合并企业版遗留的一些bug.
|
||||
|
||||
v6.4
|
||||
1.http(s)代理增加了--jumper参数,可以穿透外部代理连接上级.
|
||||
2.优化了socks5代理UDP功能可能存在的内存占用过多问题.
|
||||
3.优化了jumper,避免某些情况下不能正确返回错误的问题.
|
||||
4.sps代理增加了--jumper参数,可以穿透外部代理连接上级.
|
||||
5.修复了--debug不能正常工作的问题.
|
||||
|
||||
v6.3
|
||||
1.fixed #156
|
||||
2.修复DNS代理,没有定时保存缓存结果到文件.重启会降低查询速度.
|
||||
|
||||
|
||||
v6.2
|
||||
1.修复encrypt.Conn释放内存,导致的潜在panic问题.
|
||||
2.修复了basic认证,处理认证文件没有正确处理注释的bug.
|
||||
3.修正了ssh中转手册参数-A调整为-D.
|
||||
|
||||
v6.1
|
||||
1.黑白名单支持设置顶级域了,比如:com,匹配所有的.com域名
|
||||
2.优化TCPS内存释放.
|
||||
3.优化了域名检查.
|
||||
4.内网穿透增加了TCPS和TOU协议,
|
||||
TCPS提供了多种自定义加密TCP方式传输.
|
||||
TOU提供了TCP over UDP,多种自定义加密UDP方式传输TCP数据.
|
||||
5.优化了DST,防止意外crash.
|
||||
6.修复了mapx的Keys()方法的bug导致内网穿透bridge不稳定的问题.
|
||||
7.修复了部分服务不能绑定IPv6地址的bug.
|
||||
|
||||
v6.0 企业版开源啦
|
||||
本次更新主要是把企业版开源,把企业版代码合并到现在的开源goproxy当中,继续遵循GPLv3,免费开源,
|
||||
之所以直接跳过5.x,用6.0版本号是为了与现有开源版本做一个明显的区分,下面功能主要来自企业版.
|
||||
企业版代码结构更合理,核心与开源版本有很大区别,与此同时企业版有一个core开发库,基于此库可以
|
||||
几行代码实现自己高度定制化的各种网络安全传输服务器和客户端和代理服务器与客户端.与此同时企
|
||||
业版独创了TCPS协议,处于应用层和TCP层之间,可以为应用提供透明化的安全传输功能,另外还对dst协
|
||||
议进行了一些改造,集成到goproxy中,实现了tcp over udp功能,那么除了kcp之外现在还可以选择dst
|
||||
作为底层的tcp over udp的传输.下一步加入插件机制,定制功能可以使用插件方式开发了,热插拔,
|
||||
不需要修改goproxy二进制,可以插件so或者dylib注入.
|
||||
|
||||
1.预编译的二进制增加了armv8支持.
|
||||
2.预编译的mipsle和mips二进制增加了softfloat支持.
|
||||
3.优化连接HTTP(s)上级代理的CONNECT指令,附带更多的信息.
|
||||
4.重构了内网穿透的UDP功能,性能大幅度提升,可以愉快的与异地基友玩依赖UDP的局域网游戏了.
|
||||
5.重构了UDP端口映射,性能大幅度提升.
|
||||
6.HTTP(S)\SOCKS5\SPS代理支持上级负载均衡,可以同时指定多个上级.
|
||||
7.SPS支持HTTP(S)\SOCKS5\SS协议相互转换.
|
||||
8.HTTP(S)\SOCKS5\SPS代理支持限速.
|
||||
9.HTTP(S)\SOCKS5代理支持指定出口IP.
|
||||
10.SOCKS5代理支持级联认证.
|
||||
11.修复了tclient可能意外退出的bug.
|
||||
12.优化了错误捕获,防止意外crash.
|
||||
13.优化了停止服务,释放内存.
|
||||
|
||||
v5.4
|
||||
1.优化了获取本地IP信息导致CPU过高的问题.
|
||||
2.所有服务都增加了--nolog参数,可以关闭日志输出,节省CPU.
|
||||
3.优化sdk,支持并发启动/关闭操作.
|
||||
4.修复了多连接版本的内网穿透,tserver连接不能正确释放的bug.
|
||||
5.内网穿透增加了client/tclient和server/tserver使用代理连接bridge/tbridge的功能,详细内容参考手册.
|
||||
6.TCP端口映射(TCP代理)增加了使用代理连接上级的功能,详细内容参考手册.
|
||||
|
||||
v5.3
|
||||
1.优化了socks_client握手端口判断,避免了sstap测试UDP失败的问题.
|
||||
|
||||
v5.2
|
||||
1.修复了HTTP(S)\SPS反向代理无法正常工作的问题.
|
||||
2.优化了智能判断,减少不必要的DNS解析.
|
||||
3.重构了SOCKS和SPS的UDP功能,基于UDP的游戏加速嗖嗖的.
|
||||
|
||||
v5.1
|
||||
1.优化了kcp默认mtu配置,调整为450.
|
||||
2.优化了HTTP(S)\SOCKS5代理智能判断,更加精确。
|
||||
3.fix #97 , 修复了RemoveProxyHeaders方法忽略了第一行的bug。
|
||||
4.修复了-g参数长格式没有连接符号的bug.
|
||||
5.重构了证书生成功能,不再有任何外部依赖,任何平台都可以独立生成证书.
|
||||
|
||||
v5.0
|
||||
1.修复了SPS多端口无效的bug.
|
||||
2.增加了DNS代理功能,提供安全无污染的DNS解析.
|
||||
|
||||
v4.9
|
||||
1.修复了HTTP Basic代理返回不合适的头部,导致浏览器不会弹框,个别代理插件无法认证的问题.
|
||||
2.内网穿透切换smux到yamux.
|
||||
3.优化了HTTP(S)\SOCKS5代理--always的处理逻辑.
|
||||
|
||||
v4.8
|
||||
1.优化了SPS连接HTTP上级的指令,避免了某些代理不响应的问题.
|
||||
2.SPS功能增加了参数:
|
||||
--disable-http:禁用http(s)代理
|
||||
--disable-socks:禁用socks代理
|
||||
默认都是false(开启).
|
||||
3.重构了部分代码的日志部分,保证了日志按着预期输出.
|
||||
4.修复了sps\http代理初始化服务的时机不正确,导致nil异常的bug.
|
||||
5.优化了sps日志输出.
|
||||
6.--debug参数增加了Profiling功能,可以保存cpu,内存等多种调试数据到文件.
|
||||
7.优化了服务注册,避免了不必要的内存开销.
|
||||
8.增加了Dockerfile和docker安装手册.
|
||||
9.优化了ioCopy避免了内存泄漏,大大提升了内存占用的稳定性.
|
||||
|
||||
|
||||
v4.7
|
||||
1.增加了基于gomobile的sdk,对android/ios/windows/linux/mac提供SDK支持.
|
||||
2.优化了bridge的日志,增加了client和server的掉线日志.
|
||||
3.优化了sps读取http(s)代理响应的缓冲大小,同时优化了CONNECT请求,
|
||||
避免了某些代理服务器返回过多数据导致不能正常通讯的问题.
|
||||
4.去除了鸡肋连接池功能.
|
||||
5.优化了所有服务代码,方便对sdk提供支持.
|
||||
6.增加了SDK手册.
|
||||
7.增加了GUI客户端(windows/web/android/ios)介绍主页.
|
||||
8.SPS\HTTP(s)\Socks代理增加了自定义加密传输,只需要通过参数-z和-Z设置一个密码即可.
|
||||
9.SPS\HTTP(s)\Socks代理增加了压缩传输,只需要通过参数-m和-M设置即可.
|
||||
10.手册增加了SPS\HTTP(s)\Socks自定义加密的使用示例.
|
||||
11.手册增加了SPS\HTTP(s)\Socks压缩传输的使用示例.
|
||||
12.优化了多链接版本的内网穿透,融合了多链接和smux的优点,即能够拥有大的吞吐量,
|
||||
同时又具备mux的心跳机制保证了链接的稳定性.
|
||||
13.手册增加了大量配图.
|
||||
14.优化了socks代理udp上级的设置逻辑,智能判断parent上级填充udp parent.
|
||||
15.优化了项目文件夹结构,使用源码可以直接go get.
|
||||
|
||||
v4.6
|
||||
1.sps,http(s),socks5,内网穿透都做了大量的超时优化处理,更加稳定.
|
||||
2.sps增加了强大的树形级联认证支持,可以轻松构建你的认证代理网络.
|
||||
3.手册增加了6.6对sps认证功能的介绍.
|
||||
|
||||
|
||||
v4.5
|
||||
1.优化了mux内网穿透连接管理逻辑,增强了稳定性.
|
||||
2.mux内网穿透增加了tcp和kcp协议支持,之前是tls,现在支持三种协议tcp,tls,kcp.
|
||||
3.keygen参数增加了用法: proxy keygen usage.
|
||||
4.http(s)/socks5代理,tls增加了自签名证书支持.
|
||||
5.建议升级.
|
||||
v4.4
|
||||
1.增加了协议转换sps功能,代理协议转换使用的是sps子命令(socks+https的缩写),
|
||||
sps本身不提供代理功能,只是接受代理请求"转换并转发"给已经存在的http(s)代理
|
||||
或者socks5代理;sps可以把已经存在的http(s)代理或者socks5代理转换为一个端口
|
||||
同时支持http(s)和socks5代理,而且http(s)代理支持正向代理和反向代理(SNI),转
|
||||
换后的SOCKS5代理不支持UDP功能;另外对于已经存在的http(s)代理或者socks5代理,
|
||||
支持tls、tcp、kcp三种模式,支持链式连接,也就是可以多个sps结点层级连接构建
|
||||
加密通道。
|
||||
2.增加了对KCP传输参数的配置,多达17个参数可以自由的配置对kcp传输效率调优。
|
||||
3.内网穿透功能,server和client增加了--session-count参数,可以设置server每个
|
||||
监听端口到bridge打开的session数量,可以设置client到bridge打开的session数量,
|
||||
之前都是1个,现在性能提升N倍,N就是你自己设置的--session-count,这个参数很大
|
||||
程度上解决了多路复用的拥塞问题,v4.4开始默认10个。
|
||||
|
||||
v4.3
|
||||
1.优化了参数keygen生成证书逻辑,避免证书出现特征。
|
||||
2.http(s)和socks代理增加了--dns-address和--dns-ttl参数。
|
||||
用于自己指定proxy访问域名的时候使用的dns(--dns-address)以及解析结果缓存时间(--dns-ttl)秒数,
|
||||
避免系统dns对proxy的干扰,另外缓存功能还能减少dns解析时间提高访问速度。
|
||||
3.优化了http代理的basic认证逻辑。
|
||||
提示:
|
||||
v4.3生成的证书不适用于v4.2及以下版本。
|
||||
|
||||
v4.2
|
||||
1.优化了内网穿透,避免了client意外下线,导致链接信息残留的问题.
|
||||
2.http代理增加了SNI支持,现在http(s)代理模式支持反向代理,支持http(s)透明代理.
|
||||
3.增加了英文手册.
|
||||
|
||||
v4.1
|
||||
1.优化了http(s),socks5代理中的域名智能判断,如果是内网IP,直接走本地网络,提升浏览体验,
|
||||
同时优化了检查机制,判断更快.
|
||||
2.http代理basic认证增加了对https协议的支持,现在basic认证可以控制所有http(s)流量了.
|
||||
3.项目代码增加了依赖类库vendor目录,clone下来就能go build,再也不用担心go get依赖类库
|
||||
失败导致不能编译了.
|
||||
|
||||
v4.0
|
||||
1.内网穿透三端重构了一个multiplexing版本,使用github.com/xtaci/smux实现了tcp链接的多路复用,
|
||||
鼎鼎大名的kcp-go底层就是使用的这个库,基于kcp-go的双边加速工具kcptun的广泛使用已经很好
|
||||
的验证来该库的强大与稳定。multiplexing版的内网穿透对应的子命令分别是server,client,bridge
|
||||
使用方式和参数与之前的子命令tserver,tclient,tserver完全一样,另外server,client增加了
|
||||
压缩传输参数--c,使用压缩传输速度更快。
|
||||
|
||||
v3.9
|
||||
1.增加了守护运行参数--forever,比如: proxy http --forever ,
|
||||
proxy会fork子进程,然后监控子进程,如果子进程异常退出,5秒后重启子进程.
|
||||
该参数配合后台运行参数--daemon和日志参数--log,可以保障proxy一直在后台执行不会因为意外退出,
|
||||
而且可以通过日志文件看到proxy的输出日志内容.
|
||||
比如: proxy http -p ":9090" --forever --log proxy.log --daemon
|
||||
|
||||
v3.8
|
||||
1.增加了日志输出到文件--log参数,比如: --log proxy.log,日志就会输出到proxy.log方便排除问题.
|
||||
|
||||
v3.7
|
||||
1.修复了socks代理不能正常和上级代理通讯的问题.
|
||||
|
||||
|
||||
v3.6
|
||||
1.http(s),socks代理,集成了外部HTTP API认证,可以通过外部API对用户名和密码进行认证.
|
||||
2.手册http(s),socks代理认证部分增加了集成外部HTTP API认证的使用说明.
|
||||
|
||||
v3.5
|
||||
1.优化了kcp参数,速度有所提升.
|
||||
2.修复了socks无法正常工作的问题.
|
||||
3.修正了文档中的一些描述.
|
||||
4.tcp代理增加了kcp协议传输数据.
|
||||
5.优化了死循环检查,增加了添加本地IP参数,当VPS在nat设备后面,
|
||||
vps上网卡IP都是内网IP,这个时候可以通过-g参数添加vps的外网ip防止死循环.
|
||||
6.增加了--daemon参数,可以后台运行程序哟.
|
||||
|
||||
v3.4
|
||||
1.socks5代理新增了用户名密码验证支持.
|
||||
2.socks5,http(s)代理增加了kcp传输协议支持.
|
||||
3.优化了内网穿透的心跳机制.
|
||||
|
||||
v3.3
|
||||
1.修复了socks代理模式对证书文件的判断逻辑.
|
||||
2.增强了http代理,socks代理的ssh中转模式的稳定性.
|
||||
3.socks代理tls,tcp模式新增了CMD_ASSOCIATE(udp)支持.socks代理ssh模式不支持udp.
|
||||
4.修复了http代理某些情况下会崩溃的bug.
|
||||
|
||||
v3.2
|
||||
1.内网穿透功能server端-r参数增加了协议和key设置.
|
||||
2.手册增加了对-r参数的详细说明.
|
||||
3.修复了普通模式也检查证书文件的bug.
|
||||
4.增加了Socks5支持,目前只支持TCP协议,不支持UDP协议.
|
||||
5.Socks5上级代理支持ssh中转,linux服务器不需要任何服务端,本地一个proxy即可开心上网.
|
||||
6.http(s)代理增加了ssh中转支持,linux服务器不需要任何服务端,本地一个proxy即可开心上网.
|
||||
|
||||
v3.1
|
||||
1.优化了内网穿透功能,bridge,client和server只需要启动一个即可。
|
||||
server端启动的时候可以指定client端要暴露的一个或者多个端口。
|
||||
2.修复了重复解析命令行参数的问题。
|
||||
3.手册增加了微信接口本地开发的示例。
|
||||
4.增加了配置文件使用说明.
|
||||
|
||||
v3.0
|
||||
1.此次更新不兼容2.x版本,重构了全部代码,架构更合理,利于功能模块的增加与维护。
|
||||
2.增加了代理死循环检查,增强了安全性。
|
||||
3.增加了反向代理模式(即:内网穿透),支持TCP和UDP两种协议,可以把任何局域网的机器A所在网络的任何端。
|
||||
暴露到任何局域网的机器B的本地端口或暴露到任何公网VPS上。
|
||||
4.正向代理增加了UDP模式支持。
|
||||
|
||||
|
||||
v2.2
|
||||
1.增加了强制使用上级代理参数always.可以使所有流量都走上级代理。
|
||||
2.增加了定时检查网络是否正常,可以在本地网络不稳定的时候修复连接池状态,提升代理访问体验。
|
||||
3.http代理增加了对ipv6地址的支持。
|
||||
|
||||
v2.1
|
||||
1.增加了http basic验证功能,可以对http代理协议设置basic验证,用户名和密码支持来自文件或者命令行。
|
||||
2.优化了域名检查方法,避免空连接的出现。
|
||||
3.修复了连接上级代理超时参数传递错误导致超时过大的问题。
|
||||
4.增加了连接池状态监测,如果上级代理或者网络出现问题,会及时重新初始化连接池,防止大量无效连接,降低浏览体验。
|
||||
5.增加了对系统kill信号的捕获,可以在收到系统kill信号之后执行清理释放连接的操作.避免出现大量CLOSE_WAIT。
|
||||
|
||||
v2.0
|
||||
1.增加了连接池功能,大幅提高了通过上级代理访问的速度。
|
||||
2.HTTP代理模式,优化了请求URL的获取逻辑,可以支持:http,https,websocke。
|
||||
3.增加了TCP代理模式,支持是否加密通讯。
|
||||
4.优化了链接关闭逻辑,避免出现大量CLOSE_WAIT。
|
||||
5.增加了黑白名单机制,更自由快速的访问。
|
||||
6.优化了网站Block机制检测,判断更准确。
|
||||
|
||||
v1.0
|
||||
1.始发版本,可以代理http,https。
|
||||
@@ -0,0 +1,34 @@
|
||||
<!--- Provide a general summary of the issue in the Title above -->
|
||||
|
||||
## Expected Behavior
|
||||
<!--- Tell us what should happen -->
|
||||
|
||||
## Current Behavior
|
||||
<!--- Tell us what happens instead of the expected behavior -->
|
||||
|
||||
## Possible Solution
|
||||
<!--- Not obligatory, but suggest a fix/reason for the bug, -->
|
||||
|
||||
## Steps to Reproduce
|
||||
<!--- Provide a link to a live example, or an unambiguous set of steps to -->
|
||||
<!--- reproduce this bug. Include code to reproduce, if relevant -->
|
||||
1.
|
||||
1.
|
||||
1.
|
||||
1.
|
||||
|
||||
## Context (Environment)
|
||||
<!--- How has this issue affected you? What are you trying to accomplish? -->
|
||||
<!--- Providing context helps us come up with a solution that is most useful in the real world -->
|
||||
1. proxy version is : v?
|
||||
1. full command is :?
|
||||
1. system is :
|
||||
1. full log is: ?
|
||||
|
||||
<!--- Provide a general summary of the issue in the Title above -->
|
||||
|
||||
## Detailed Description
|
||||
<!--- Provide a detailed description of the change or addition you are proposing -->
|
||||
|
||||
## Possible Implementation
|
||||
<!--- Not obligatory, but suggest an idea for implementing addition or change -->
|
||||
@@ -0,0 +1,674 @@
|
||||
GNU GENERAL PUBLIC LICENSE
|
||||
Version 3, 29 June 2007
|
||||
|
||||
Copyright (C) 2007 Free Software Foundation, Inc. <http://fsf.org/>
|
||||
Everyone is permitted to copy and distribute verbatim copies
|
||||
of this license document, but changing it is not allowed.
|
||||
|
||||
Preamble
|
||||
|
||||
The GNU General Public License is a free, copyleft license for
|
||||
software and other kinds of works.
|
||||
|
||||
The licenses for most software and other practical works are designed
|
||||
to take away your freedom to share and change the works. By contrast,
|
||||
the GNU General Public License is intended to guarantee your freedom to
|
||||
share and change all versions of a program--to make sure it remains free
|
||||
software for all its users. We, the Free Software Foundation, use the
|
||||
GNU General Public License for most of our software; it applies also to
|
||||
any other work released this way by its authors. You can apply it to
|
||||
your programs, too.
|
||||
|
||||
When we speak of free software, we are referring to freedom, not
|
||||
price. Our General Public Licenses are designed to make sure that you
|
||||
have the freedom to distribute copies of free software (and charge for
|
||||
them if you wish), that you receive source code or can get it if you
|
||||
want it, that you can change the software or use pieces of it in new
|
||||
free programs, and that you know you can do these things.
|
||||
|
||||
To protect your rights, we need to prevent others from denying you
|
||||
these rights or asking you to surrender the rights. Therefore, you have
|
||||
certain responsibilities if you distribute copies of the software, or if
|
||||
you modify it: responsibilities to respect the freedom of others.
|
||||
|
||||
For example, if you distribute copies of such a program, whether
|
||||
gratis or for a fee, you must pass on to the recipients the same
|
||||
freedoms that you received. You must make sure that they, too, receive
|
||||
or can get the source code. And you must show them these terms so they
|
||||
know their rights.
|
||||
|
||||
Developers that use the GNU GPL protect your rights with two steps:
|
||||
(1) assert copyright on the software, and (2) offer you this License
|
||||
giving you legal permission to copy, distribute and/or modify it.
|
||||
|
||||
For the developers' and authors' protection, the GPL clearly explains
|
||||
that there is no warranty for this free software. For both users' and
|
||||
authors' sake, the GPL requires that modified versions be marked as
|
||||
changed, so that their problems will not be attributed erroneously to
|
||||
authors of previous versions.
|
||||
|
||||
Some devices are designed to deny users access to install or run
|
||||
modified versions of the software inside them, although the manufacturer
|
||||
can do so. This is fundamentally incompatible with the aim of
|
||||
protecting users' freedom to change the software. The systematic
|
||||
pattern of such abuse occurs in the area of products for individuals to
|
||||
use, which is precisely where it is most unacceptable. Therefore, we
|
||||
have designed this version of the GPL to prohibit the practice for those
|
||||
products. If such problems arise substantially in other domains, we
|
||||
stand ready to extend this provision to those domains in future versions
|
||||
of the GPL, as needed to protect the freedom of users.
|
||||
|
||||
Finally, every program is threatened constantly by software patents.
|
||||
States should not allow patents to restrict development and use of
|
||||
software on general-purpose computers, but in those that do, we wish to
|
||||
avoid the special danger that patents applied to a free program could
|
||||
make it effectively proprietary. To prevent this, the GPL assures that
|
||||
patents cannot be used to render the program non-free.
|
||||
|
||||
The precise terms and conditions for copying, distribution and
|
||||
modification follow.
|
||||
|
||||
TERMS AND CONDITIONS
|
||||
|
||||
0. Definitions.
|
||||
|
||||
"This License" refers to version 3 of the GNU General Public License.
|
||||
|
||||
"Copyright" also means copyright-like laws that apply to other kinds of
|
||||
works, such as semiconductor masks.
|
||||
|
||||
"The Program" refers to any copyrightable work licensed under this
|
||||
License. Each licensee is addressed as "you". "Licensees" and
|
||||
"recipients" may be individuals or organizations.
|
||||
|
||||
To "modify" a work means to copy from or adapt all or part of the work
|
||||
in a fashion requiring copyright permission, other than the making of an
|
||||
exact copy. The resulting work is called a "modified version" of the
|
||||
earlier work or a work "based on" the earlier work.
|
||||
|
||||
A "covered work" means either the unmodified Program or a work based
|
||||
on the Program.
|
||||
|
||||
To "propagate" a work means to do anything with it that, without
|
||||
permission, would make you directly or secondarily liable for
|
||||
infringement under applicable copyright law, except executing it on a
|
||||
computer or modifying a private copy. Propagation includes copying,
|
||||
distribution (with or without modification), making available to the
|
||||
public, and in some countries other activities as well.
|
||||
|
||||
To "convey" a work means any kind of propagation that enables other
|
||||
parties to make or receive copies. Mere interaction with a user through
|
||||
a computer network, with no transfer of a copy, is not conveying.
|
||||
|
||||
An interactive user interface displays "Appropriate Legal Notices"
|
||||
to the extent that it includes a convenient and prominently visible
|
||||
feature that (1) displays an appropriate copyright notice, and (2)
|
||||
tells the user that there is no warranty for the work (except to the
|
||||
extent that warranties are provided), that licensees may convey the
|
||||
work under this License, and how to view a copy of this License. If
|
||||
the interface presents a list of user commands or options, such as a
|
||||
menu, a prominent item in the list meets this criterion.
|
||||
|
||||
1. Source Code.
|
||||
|
||||
The "source code" for a work means the preferred form of the work
|
||||
for making modifications to it. "Object code" means any non-source
|
||||
form of a work.
|
||||
|
||||
A "Standard Interface" means an interface that either is an official
|
||||
standard defined by a recognized standards body, or, in the case of
|
||||
interfaces specified for a particular programming language, one that
|
||||
is widely used among developers working in that language.
|
||||
|
||||
The "System Libraries" of an executable work include anything, other
|
||||
than the work as a whole, that (a) is included in the normal form of
|
||||
packaging a Major Component, but which is not part of that Major
|
||||
Component, and (b) serves only to enable use of the work with that
|
||||
Major Component, or to implement a Standard Interface for which an
|
||||
implementation is available to the public in source code form. A
|
||||
"Major Component", in this context, means a major essential component
|
||||
(kernel, window system, and so on) of the specific operating system
|
||||
(if any) on which the executable work runs, or a compiler used to
|
||||
produce the work, or an object code interpreter used to run it.
|
||||
|
||||
The "Corresponding Source" for a work in object code form means all
|
||||
the source code needed to generate, install, and (for an executable
|
||||
work) run the object code and to modify the work, including scripts to
|
||||
control those activities. However, it does not include the work's
|
||||
System Libraries, or general-purpose tools or generally available free
|
||||
programs which are used unmodified in performing those activities but
|
||||
which are not part of the work. For example, Corresponding Source
|
||||
includes interface definition files associated with source files for
|
||||
the work, and the source code for shared libraries and dynamically
|
||||
linked subprograms that the work is specifically designed to require,
|
||||
such as by intimate data communication or control flow between those
|
||||
subprograms and other parts of the work.
|
||||
|
||||
The Corresponding Source need not include anything that users
|
||||
can regenerate automatically from other parts of the Corresponding
|
||||
Source.
|
||||
|
||||
The Corresponding Source for a work in source code form is that
|
||||
same work.
|
||||
|
||||
2. Basic Permissions.
|
||||
|
||||
All rights granted under this License are granted for the term of
|
||||
copyright on the Program, and are irrevocable provided the stated
|
||||
conditions are met. This License explicitly affirms your unlimited
|
||||
permission to run the unmodified Program. The output from running a
|
||||
covered work is covered by this License only if the output, given its
|
||||
content, constitutes a covered work. This License acknowledges your
|
||||
rights of fair use or other equivalent, as provided by copyright law.
|
||||
|
||||
You may make, run and propagate covered works that you do not
|
||||
convey, without conditions so long as your license otherwise remains
|
||||
in force. You may convey covered works to others for the sole purpose
|
||||
of having them make modifications exclusively for you, or provide you
|
||||
with facilities for running those works, provided that you comply with
|
||||
the terms of this License in conveying all material for which you do
|
||||
not control copyright. Those thus making or running the covered works
|
||||
for you must do so exclusively on your behalf, under your direction
|
||||
and control, on terms that prohibit them from making any copies of
|
||||
your copyrighted material outside their relationship with you.
|
||||
|
||||
Conveying under any other circumstances is permitted solely under
|
||||
the conditions stated below. Sublicensing is not allowed; section 10
|
||||
makes it unnecessary.
|
||||
|
||||
3. Protecting Users' Legal Rights From Anti-Circumvention Law.
|
||||
|
||||
No covered work shall be deemed part of an effective technological
|
||||
measure under any applicable law fulfilling obligations under article
|
||||
11 of the WIPO copyright treaty adopted on 20 December 1996, or
|
||||
similar laws prohibiting or restricting circumvention of such
|
||||
measures.
|
||||
|
||||
When you convey a covered work, you waive any legal power to forbid
|
||||
circumvention of technological measures to the extent such circumvention
|
||||
is effected by exercising rights under this License with respect to
|
||||
the covered work, and you disclaim any intention to limit operation or
|
||||
modification of the work as a means of enforcing, against the work's
|
||||
users, your or third parties' legal rights to forbid circumvention of
|
||||
technological measures.
|
||||
|
||||
4. Conveying Verbatim Copies.
|
||||
|
||||
You may convey verbatim copies of the Program's source code as you
|
||||
receive it, in any medium, provided that you conspicuously and
|
||||
appropriately publish on each copy an appropriate copyright notice;
|
||||
keep intact all notices stating that this License and any
|
||||
non-permissive terms added in accord with section 7 apply to the code;
|
||||
keep intact all notices of the absence of any warranty; and give all
|
||||
recipients a copy of this License along with the Program.
|
||||
|
||||
You may charge any price or no price for each copy that you convey,
|
||||
and you may offer support or warranty protection for a fee.
|
||||
|
||||
5. Conveying Modified Source Versions.
|
||||
|
||||
You may convey a work based on the Program, or the modifications to
|
||||
produce it from the Program, in the form of source code under the
|
||||
terms of section 4, provided that you also meet all of these conditions:
|
||||
|
||||
a) The work must carry prominent notices stating that you modified
|
||||
it, and giving a relevant date.
|
||||
|
||||
b) The work must carry prominent notices stating that it is
|
||||
released under this License and any conditions added under section
|
||||
7. This requirement modifies the requirement in section 4 to
|
||||
"keep intact all notices".
|
||||
|
||||
c) You must license the entire work, as a whole, under this
|
||||
License to anyone who comes into possession of a copy. This
|
||||
License will therefore apply, along with any applicable section 7
|
||||
additional terms, to the whole of the work, and all its parts,
|
||||
regardless of how they are packaged. This License gives no
|
||||
permission to license the work in any other way, but it does not
|
||||
invalidate such permission if you have separately received it.
|
||||
|
||||
d) If the work has interactive user interfaces, each must display
|
||||
Appropriate Legal Notices; however, if the Program has interactive
|
||||
interfaces that do not display Appropriate Legal Notices, your
|
||||
work need not make them do so.
|
||||
|
||||
A compilation of a covered work with other separate and independent
|
||||
works, which are not by their nature extensions of the covered work,
|
||||
and which are not combined with it such as to form a larger program,
|
||||
in or on a volume of a storage or distribution medium, is called an
|
||||
"aggregate" if the compilation and its resulting copyright are not
|
||||
used to limit the access or legal rights of the compilation's users
|
||||
beyond what the individual works permit. Inclusion of a covered work
|
||||
in an aggregate does not cause this License to apply to the other
|
||||
parts of the aggregate.
|
||||
|
||||
6. Conveying Non-Source Forms.
|
||||
|
||||
You may convey a covered work in object code form under the terms
|
||||
of sections 4 and 5, provided that you also convey the
|
||||
machine-readable Corresponding Source under the terms of this License,
|
||||
in one of these ways:
|
||||
|
||||
a) Convey the object code in, or embodied in, a physical product
|
||||
(including a physical distribution medium), accompanied by the
|
||||
Corresponding Source fixed on a durable physical medium
|
||||
customarily used for software interchange.
|
||||
|
||||
b) Convey the object code in, or embodied in, a physical product
|
||||
(including a physical distribution medium), accompanied by a
|
||||
written offer, valid for at least three years and valid for as
|
||||
long as you offer spare parts or customer support for that product
|
||||
model, to give anyone who possesses the object code either (1) a
|
||||
copy of the Corresponding Source for all the software in the
|
||||
product that is covered by this License, on a durable physical
|
||||
medium customarily used for software interchange, for a price no
|
||||
more than your reasonable cost of physically performing this
|
||||
conveying of source, or (2) access to copy the
|
||||
Corresponding Source from a network server at no charge.
|
||||
|
||||
c) Convey individual copies of the object code with a copy of the
|
||||
written offer to provide the Corresponding Source. This
|
||||
alternative is allowed only occasionally and noncommercially, and
|
||||
only if you received the object code with such an offer, in accord
|
||||
with subsection 6b.
|
||||
|
||||
d) Convey the object code by offering access from a designated
|
||||
place (gratis or for a charge), and offer equivalent access to the
|
||||
Corresponding Source in the same way through the same place at no
|
||||
further charge. You need not require recipients to copy the
|
||||
Corresponding Source along with the object code. If the place to
|
||||
copy the object code is a network server, the Corresponding Source
|
||||
may be on a different server (operated by you or a third party)
|
||||
that supports equivalent copying facilities, provided you maintain
|
||||
clear directions next to the object code saying where to find the
|
||||
Corresponding Source. Regardless of what server hosts the
|
||||
Corresponding Source, you remain obligated to ensure that it is
|
||||
available for as long as needed to satisfy these requirements.
|
||||
|
||||
e) Convey the object code using peer-to-peer transmission, provided
|
||||
you inform other peers where the object code and Corresponding
|
||||
Source of the work are being offered to the general public at no
|
||||
charge under subsection 6d.
|
||||
|
||||
A separable portion of the object code, whose source code is excluded
|
||||
from the Corresponding Source as a System Library, need not be
|
||||
included in conveying the object code work.
|
||||
|
||||
A "User Product" is either (1) a "consumer product", which means any
|
||||
tangible personal property which is normally used for personal, family,
|
||||
or household purposes, or (2) anything designed or sold for incorporation
|
||||
into a dwelling. In determining whether a product is a consumer product,
|
||||
doubtful cases shall be resolved in favor of coverage. For a particular
|
||||
product received by a particular user, "normally used" refers to a
|
||||
typical or common use of that class of product, regardless of the status
|
||||
of the particular user or of the way in which the particular user
|
||||
actually uses, or expects or is expected to use, the product. A product
|
||||
is a consumer product regardless of whether the product has substantial
|
||||
commercial, industrial or non-consumer uses, unless such uses represent
|
||||
the only significant mode of use of the product.
|
||||
|
||||
"Installation Information" for a User Product means any methods,
|
||||
procedures, authorization keys, or other information required to install
|
||||
and execute modified versions of a covered work in that User Product from
|
||||
a modified version of its Corresponding Source. The information must
|
||||
suffice to ensure that the continued functioning of the modified object
|
||||
code is in no case prevented or interfered with solely because
|
||||
modification has been made.
|
||||
|
||||
If you convey an object code work under this section in, or with, or
|
||||
specifically for use in, a User Product, and the conveying occurs as
|
||||
part of a transaction in which the right of possession and use of the
|
||||
User Product is transferred to the recipient in perpetuity or for a
|
||||
fixed term (regardless of how the transaction is characterized), the
|
||||
Corresponding Source conveyed under this section must be accompanied
|
||||
by the Installation Information. But this requirement does not apply
|
||||
if neither you nor any third party retains the ability to install
|
||||
modified object code on the User Product (for example, the work has
|
||||
been installed in ROM).
|
||||
|
||||
The requirement to provide Installation Information does not include a
|
||||
requirement to continue to provide support service, warranty, or updates
|
||||
for a work that has been modified or installed by the recipient, or for
|
||||
the User Product in which it has been modified or installed. Access to a
|
||||
network may be denied when the modification itself materially and
|
||||
adversely affects the operation of the network or violates the rules and
|
||||
protocols for communication across the network.
|
||||
|
||||
Corresponding Source conveyed, and Installation Information provided,
|
||||
in accord with this section must be in a format that is publicly
|
||||
documented (and with an implementation available to the public in
|
||||
source code form), and must require no special password or key for
|
||||
unpacking, reading or copying.
|
||||
|
||||
7. Additional Terms.
|
||||
|
||||
"Additional permissions" are terms that supplement the terms of this
|
||||
License by making exceptions from one or more of its conditions.
|
||||
Additional permissions that are applicable to the entire Program shall
|
||||
be treated as though they were included in this License, to the extent
|
||||
that they are valid under applicable law. If additional permissions
|
||||
apply only to part of the Program, that part may be used separately
|
||||
under those permissions, but the entire Program remains governed by
|
||||
this License without regard to the additional permissions.
|
||||
|
||||
When you convey a copy of a covered work, you may at your option
|
||||
remove any additional permissions from that copy, or from any part of
|
||||
it. (Additional permissions may be written to require their own
|
||||
removal in certain cases when you modify the work.) You may place
|
||||
additional permissions on material, added by you to a covered work,
|
||||
for which you have or can give appropriate copyright permission.
|
||||
|
||||
Notwithstanding any other provision of this License, for material you
|
||||
add to a covered work, you may (if authorized by the copyright holders of
|
||||
that material) supplement the terms of this License with terms:
|
||||
|
||||
a) Disclaiming warranty or limiting liability differently from the
|
||||
terms of sections 15 and 16 of this License; or
|
||||
|
||||
b) Requiring preservation of specified reasonable legal notices or
|
||||
author attributions in that material or in the Appropriate Legal
|
||||
Notices displayed by works containing it; or
|
||||
|
||||
c) Prohibiting misrepresentation of the origin of that material, or
|
||||
requiring that modified versions of such material be marked in
|
||||
reasonable ways as different from the original version; or
|
||||
|
||||
d) Limiting the use for publicity purposes of names of licensors or
|
||||
authors of the material; or
|
||||
|
||||
e) Declining to grant rights under trademark law for use of some
|
||||
trade names, trademarks, or service marks; or
|
||||
|
||||
f) Requiring indemnification of licensors and authors of that
|
||||
material by anyone who conveys the material (or modified versions of
|
||||
it) with contractual assumptions of liability to the recipient, for
|
||||
any liability that these contractual assumptions directly impose on
|
||||
those licensors and authors.
|
||||
|
||||
All other non-permissive additional terms are considered "further
|
||||
restrictions" within the meaning of section 10. If the Program as you
|
||||
received it, or any part of it, contains a notice stating that it is
|
||||
governed by this License along with a term that is a further
|
||||
restriction, you may remove that term. If a license document contains
|
||||
a further restriction but permits relicensing or conveying under this
|
||||
License, you may add to a covered work material governed by the terms
|
||||
of that license document, provided that the further restriction does
|
||||
not survive such relicensing or conveying.
|
||||
|
||||
If you add terms to a covered work in accord with this section, you
|
||||
must place, in the relevant source files, a statement of the
|
||||
additional terms that apply to those files, or a notice indicating
|
||||
where to find the applicable terms.
|
||||
|
||||
Additional terms, permissive or non-permissive, may be stated in the
|
||||
form of a separately written license, or stated as exceptions;
|
||||
the above requirements apply either way.
|
||||
|
||||
8. Termination.
|
||||
|
||||
You may not propagate or modify a covered work except as expressly
|
||||
provided under this License. Any attempt otherwise to propagate or
|
||||
modify it is void, and will automatically terminate your rights under
|
||||
this License (including any patent licenses granted under the third
|
||||
paragraph of section 11).
|
||||
|
||||
However, if you cease all violation of this License, then your
|
||||
license from a particular copyright holder is reinstated (a)
|
||||
provisionally, unless and until the copyright holder explicitly and
|
||||
finally terminates your license, and (b) permanently, if the copyright
|
||||
holder fails to notify you of the violation by some reasonable means
|
||||
prior to 60 days after the cessation.
|
||||
|
||||
Moreover, your license from a particular copyright holder is
|
||||
reinstated permanently if the copyright holder notifies you of the
|
||||
violation by some reasonable means, this is the first time you have
|
||||
received notice of violation of this License (for any work) from that
|
||||
copyright holder, and you cure the violation prior to 30 days after
|
||||
your receipt of the notice.
|
||||
|
||||
Termination of your rights under this section does not terminate the
|
||||
licenses of parties who have received copies or rights from you under
|
||||
this License. If your rights have been terminated and not permanently
|
||||
reinstated, you do not qualify to receive new licenses for the same
|
||||
material under section 10.
|
||||
|
||||
9. Acceptance Not Required for Having Copies.
|
||||
|
||||
You are not required to accept this License in order to receive or
|
||||
run a copy of the Program. Ancillary propagation of a covered work
|
||||
occurring solely as a consequence of using peer-to-peer transmission
|
||||
to receive a copy likewise does not require acceptance. However,
|
||||
nothing other than this License grants you permission to propagate or
|
||||
modify any covered work. These actions infringe copyright if you do
|
||||
not accept this License. Therefore, by modifying or propagating a
|
||||
covered work, you indicate your acceptance of this License to do so.
|
||||
|
||||
10. Automatic Licensing of Downstream Recipients.
|
||||
|
||||
Each time you convey a covered work, the recipient automatically
|
||||
receives a license from the original licensors, to run, modify and
|
||||
propagate that work, subject to this License. You are not responsible
|
||||
for enforcing compliance by third parties with this License.
|
||||
|
||||
An "entity transaction" is a transaction transferring control of an
|
||||
organization, or substantially all assets of one, or subdividing an
|
||||
organization, or merging organizations. If propagation of a covered
|
||||
work results from an entity transaction, each party to that
|
||||
transaction who receives a copy of the work also receives whatever
|
||||
licenses to the work the party's predecessor in interest had or could
|
||||
give under the previous paragraph, plus a right to possession of the
|
||||
Corresponding Source of the work from the predecessor in interest, if
|
||||
the predecessor has it or can get it with reasonable efforts.
|
||||
|
||||
You may not impose any further restrictions on the exercise of the
|
||||
rights granted or affirmed under this License. For example, you may
|
||||
not impose a license fee, royalty, or other charge for exercise of
|
||||
rights granted under this License, and you may not initiate litigation
|
||||
(including a cross-claim or counterclaim in a lawsuit) alleging that
|
||||
any patent claim is infringed by making, using, selling, offering for
|
||||
sale, or importing the Program or any portion of it.
|
||||
|
||||
11. Patents.
|
||||
|
||||
A "contributor" is a copyright holder who authorizes use under this
|
||||
License of the Program or a work on which the Program is based. The
|
||||
work thus licensed is called the contributor's "contributor version".
|
||||
|
||||
A contributor's "essential patent claims" are all patent claims
|
||||
owned or controlled by the contributor, whether already acquired or
|
||||
hereafter acquired, that would be infringed by some manner, permitted
|
||||
by this License, of making, using, or selling its contributor version,
|
||||
but do not include claims that would be infringed only as a
|
||||
consequence of further modification of the contributor version. For
|
||||
purposes of this definition, "control" includes the right to grant
|
||||
patent sublicenses in a manner consistent with the requirements of
|
||||
this License.
|
||||
|
||||
Each contributor grants you a non-exclusive, worldwide, royalty-free
|
||||
patent license under the contributor's essential patent claims, to
|
||||
make, use, sell, offer for sale, import and otherwise run, modify and
|
||||
propagate the contents of its contributor version.
|
||||
|
||||
In the following three paragraphs, a "patent license" is any express
|
||||
agreement or commitment, however denominated, not to enforce a patent
|
||||
(such as an express permission to practice a patent or covenant not to
|
||||
sue for patent infringement). To "grant" such a patent license to a
|
||||
party means to make such an agreement or commitment not to enforce a
|
||||
patent against the party.
|
||||
|
||||
If you convey a covered work, knowingly relying on a patent license,
|
||||
and the Corresponding Source of the work is not available for anyone
|
||||
to copy, free of charge and under the terms of this License, through a
|
||||
publicly available network server or other readily accessible means,
|
||||
then you must either (1) cause the Corresponding Source to be so
|
||||
available, or (2) arrange to deprive yourself of the benefit of the
|
||||
patent license for this particular work, or (3) arrange, in a manner
|
||||
consistent with the requirements of this License, to extend the patent
|
||||
license to downstream recipients. "Knowingly relying" means you have
|
||||
actual knowledge that, but for the patent license, your conveying the
|
||||
covered work in a country, or your recipient's use of the covered work
|
||||
in a country, would infringe one or more identifiable patents in that
|
||||
country that you have reason to believe are valid.
|
||||
|
||||
If, pursuant to or in connection with a single transaction or
|
||||
arrangement, you convey, or propagate by procuring conveyance of, a
|
||||
covered work, and grant a patent license to some of the parties
|
||||
receiving the covered work authorizing them to use, propagate, modify
|
||||
or convey a specific copy of the covered work, then the patent license
|
||||
you grant is automatically extended to all recipients of the covered
|
||||
work and works based on it.
|
||||
|
||||
A patent license is "discriminatory" if it does not include within
|
||||
the scope of its coverage, prohibits the exercise of, or is
|
||||
conditioned on the non-exercise of one or more of the rights that are
|
||||
specifically granted under this License. You may not convey a covered
|
||||
work if you are a party to an arrangement with a third party that is
|
||||
in the business of distributing software, under which you make payment
|
||||
to the third party based on the extent of your activity of conveying
|
||||
the work, and under which the third party grants, to any of the
|
||||
parties who would receive the covered work from you, a discriminatory
|
||||
patent license (a) in connection with copies of the covered work
|
||||
conveyed by you (or copies made from those copies), or (b) primarily
|
||||
for and in connection with specific products or compilations that
|
||||
contain the covered work, unless you entered into that arrangement,
|
||||
or that patent license was granted, prior to 28 March 2007.
|
||||
|
||||
Nothing in this License shall be construed as excluding or limiting
|
||||
any implied license or other defenses to infringement that may
|
||||
otherwise be available to you under applicable patent law.
|
||||
|
||||
12. No Surrender of Others' Freedom.
|
||||
|
||||
If conditions are imposed on you (whether by court order, agreement or
|
||||
otherwise) that contradict the conditions of this License, they do not
|
||||
excuse you from the conditions of this License. If you cannot convey a
|
||||
covered work so as to satisfy simultaneously your obligations under this
|
||||
License and any other pertinent obligations, then as a consequence you may
|
||||
not convey it at all. For example, if you agree to terms that obligate you
|
||||
to collect a royalty for further conveying from those to whom you convey
|
||||
the Program, the only way you could satisfy both those terms and this
|
||||
License would be to refrain entirely from conveying the Program.
|
||||
|
||||
13. Use with the GNU Affero General Public License.
|
||||
|
||||
Notwithstanding any other provision of this License, you have
|
||||
permission to link or combine any covered work with a work licensed
|
||||
under version 3 of the GNU Affero General Public License into a single
|
||||
combined work, and to convey the resulting work. The terms of this
|
||||
License will continue to apply to the part which is the covered work,
|
||||
but the special requirements of the GNU Affero General Public License,
|
||||
section 13, concerning interaction through a network will apply to the
|
||||
combination as such.
|
||||
|
||||
14. Revised Versions of this License.
|
||||
|
||||
The Free Software Foundation may publish revised and/or new versions of
|
||||
the GNU General Public License from time to time. Such new versions will
|
||||
be similar in spirit to the present version, but may differ in detail to
|
||||
address new problems or concerns.
|
||||
|
||||
Each version is given a distinguishing version number. If the
|
||||
Program specifies that a certain numbered version of the GNU General
|
||||
Public License "or any later version" applies to it, you have the
|
||||
option of following the terms and conditions either of that numbered
|
||||
version or of any later version published by the Free Software
|
||||
Foundation. If the Program does not specify a version number of the
|
||||
GNU General Public License, you may choose any version ever published
|
||||
by the Free Software Foundation.
|
||||
|
||||
If the Program specifies that a proxy can decide which future
|
||||
versions of the GNU General Public License can be used, that proxy's
|
||||
public statement of acceptance of a version permanently authorizes you
|
||||
to choose that version for the Program.
|
||||
|
||||
Later license versions may give you additional or different
|
||||
permissions. However, no additional obligations are imposed on any
|
||||
author or copyright holder as a result of your choosing to follow a
|
||||
later version.
|
||||
|
||||
15. Disclaimer of Warranty.
|
||||
|
||||
THERE IS NO WARRANTY FOR THE PROGRAM, TO THE EXTENT PERMITTED BY
|
||||
APPLICABLE LAW. EXCEPT WHEN OTHERWISE STATED IN WRITING THE COPYRIGHT
|
||||
HOLDERS AND/OR OTHER PARTIES PROVIDE THE PROGRAM "AS IS" WITHOUT WARRANTY
|
||||
OF ANY KIND, EITHER EXPRESSED OR IMPLIED, INCLUDING, BUT NOT LIMITED TO,
|
||||
THE IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS FOR A PARTICULAR
|
||||
PURPOSE. THE ENTIRE RISK AS TO THE QUALITY AND PERFORMANCE OF THE PROGRAM
|
||||
IS WITH YOU. SHOULD THE PROGRAM PROVE DEFECTIVE, YOU ASSUME THE COST OF
|
||||
ALL NECESSARY SERVICING, REPAIR OR CORRECTION.
|
||||
|
||||
16. Limitation of Liability.
|
||||
|
||||
IN NO EVENT UNLESS REQUIRED BY APPLICABLE LAW OR AGREED TO IN WRITING
|
||||
WILL ANY COPYRIGHT HOLDER, OR ANY OTHER PARTY WHO MODIFIES AND/OR CONVEYS
|
||||
THE PROGRAM AS PERMITTED ABOVE, BE LIABLE TO YOU FOR DAMAGES, INCLUDING ANY
|
||||
GENERAL, SPECIAL, INCIDENTAL OR CONSEQUENTIAL DAMAGES ARISING OUT OF THE
|
||||
USE OR INABILITY TO USE THE PROGRAM (INCLUDING BUT NOT LIMITED TO LOSS OF
|
||||
DATA OR DATA BEING RENDERED INACCURATE OR LOSSES SUSTAINED BY YOU OR THIRD
|
||||
PARTIES OR A FAILURE OF THE PROGRAM TO OPERATE WITH ANY OTHER PROGRAMS),
|
||||
EVEN IF SUCH HOLDER OR OTHER PARTY HAS BEEN ADVISED OF THE POSSIBILITY OF
|
||||
SUCH DAMAGES.
|
||||
|
||||
17. Interpretation of Sections 15 and 16.
|
||||
|
||||
If the disclaimer of warranty and limitation of liability provided
|
||||
above cannot be given local legal effect according to their terms,
|
||||
reviewing courts shall apply local law that most closely approximates
|
||||
an absolute waiver of all civil liability in connection with the
|
||||
Program, unless a warranty or assumption of liability accompanies a
|
||||
copy of the Program in return for a fee.
|
||||
|
||||
END OF TERMS AND CONDITIONS
|
||||
|
||||
How to Apply These Terms to Your New Programs
|
||||
|
||||
If you develop a new program, and you want it to be of the greatest
|
||||
possible use to the public, the best way to achieve this is to make it
|
||||
free software which everyone can redistribute and change under these terms.
|
||||
|
||||
To do so, attach the following notices to the program. It is safest
|
||||
to attach them to the start of each source file to most effectively
|
||||
state the exclusion of warranty; and each file should have at least
|
||||
the "copyright" line and a pointer to where the full notice is found.
|
||||
|
||||
{one line to give the program's name and a brief idea of what it does.}
|
||||
Copyright (C) {year} {name of author}
|
||||
|
||||
This program is free software: you can redistribute it and/or modify
|
||||
it under the terms of the GNU General Public License as published by
|
||||
the Free Software Foundation, either version 3 of the License, or
|
||||
(at your option) any later version.
|
||||
|
||||
This program is distributed in the hope that it will be useful,
|
||||
but WITHOUT ANY WARRANTY; without even the implied warranty of
|
||||
MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE. See the
|
||||
GNU General Public License for more details.
|
||||
|
||||
You should have received a copy of the GNU General Public License
|
||||
along with this program. If not, see <http://www.gnu.org/licenses/>.
|
||||
|
||||
Also add information on how to contact you by electronic and paper mail.
|
||||
|
||||
If the program does terminal interaction, make it output a short
|
||||
notice like this when it starts in an interactive mode:
|
||||
|
||||
{project} Copyright (C) {year} {fullname}
|
||||
This program comes with ABSOLUTELY NO WARRANTY; for details type `show w'.
|
||||
This is free software, and you are welcome to redistribute it
|
||||
under certain conditions; type `show c' for details.
|
||||
|
||||
The hypothetical commands `show w' and `show c' should show the appropriate
|
||||
parts of the General Public License. Of course, your program's commands
|
||||
might be different; for a GUI interface, you would use an "about box".
|
||||
|
||||
You should also get your employer (if you work as a programmer) or school,
|
||||
if any, to sign a "copyright disclaimer" for the program, if necessary.
|
||||
For more information on this, and how to apply and follow the GNU GPL, see
|
||||
<http://www.gnu.org/licenses/>.
|
||||
|
||||
The GNU General Public License does not permit incorporating your program
|
||||
into proprietary programs. If your program is a subroutine library, you
|
||||
may consider it more useful to permit linking proprietary applications with
|
||||
the library. If this is what you want to do, use the GNU Lesser General
|
||||
Public License instead of this License. But first, please read
|
||||
<http://www.gnu.org/philosophy/why-not-lgpl.html>.
|
||||
@@ -0,0 +1,2039 @@
|
||||
## Advertisement
|
||||
<a href="https://www.huobi.bi/zh-cn/topic/invited/?invite_code=qpi54">
|
||||
<img width="auto" height="100" src="/doc/images/zanzhu-1.png"/>
|
||||
</a>
|
||||
|
||||
## GOPROXY Introduction
|
||||
<img src="https://github.com/snail007/goproxy/blob/master/doc/images/logo.jpg?raw=true" width="200" height="auto"/>
|
||||
The GoProxy is a high-performance http proxy, https proxy, socks5 proxy, ss proxy, websocket proxies, tcp proxies, udp proxies, game shield, game proxies. Support forward proxies, reverse proxy, transparent proxy, internet nat proxies, https proxy load balancing, http proxy load balancing , socks5 proxies load balancing, socket proxy load balancing, ss proxy load balancing, TCP / UDP port mapping, SSH transit, TLS encrypted transmission, protocol conversion, anti-pollution DNS proxy, API authentication, speed limit, limit connection. Reverse proxies to help you expose a local server behind a NAT or firewall to the internet so that you or your visitors can access it directly and easily.
|
||||
|
||||
---
|
||||
|
||||
[](https://github.com/snail007/goproxy/) []() [](https://github.com/snail007/goproxy/releases) [](https://github.com/snail007/goproxy/releases)
|
||||
|
||||
---
|
||||
|
||||
### [点击我观看视频教程](https://space.bilibili.com/472844633)
|
||||
- [中文介绍(必看)](https://github.com/snail007/goproxy/blob/master/README_ZH.md)
|
||||
- [下载地址](https://github.com/snail007/goproxy/releases)
|
||||
- [官方手册(国外)](https://snail007.github.io/goproxy/manual/zh/)
|
||||
- [官方手册(国内)](https://snail.gitee.io/proxy/manual/zh/)
|
||||
- [Download](https://github.com/snail007/goproxy/releases)
|
||||
- [Desktop Edition, Web Console : ProxyAdmin](https://github.com/snail007/proxy_admin_free)
|
||||
- [Android Global Proxy Edition](https://github.com/snail007/goproxy-ss-plugin-android)
|
||||
- [Android Proxy Server Edition](https://github.com/snail007/goproxy-android)
|
||||
- [SDK](https://github.com/snail007/goproxy-sdk)
|
||||
- [GORPOXY Manual](https://snail007.github.io/goproxy/manual/)
|
||||
- [GORPOXY Tutorial](https://snail007.github.io/goproxy)
|
||||
- [Free version VS commercial version](https://snail007.github.io/goproxy/page/free_vs_commercial/)
|
||||
|
||||
### ProxyAdmin Demo
|
||||
And ProxyAdmin is a powerful web console of snail007/goproxy .
|
||||
|
||||

|
||||
|
||||
### What can it do?
|
||||
- Chained proxies, the program itself can be used as an proxies, and if it is set up, it can be used as a secondary proxies or even an N-level proxies.
|
||||
- Communication encryption, if the program is not a level one proxies, and the upper level proxies is also the program, then the communication between the upper level proxies and the upper level proxies can be encrypted, and the underlying tls high-intensity encryption is used, and the security is featureless.
|
||||
- Smart HTTP, SOCKS5 proxy, will automatically determine whether the visited website is blocked. If it is blocked, it will use the upstream proxies (provided that the upstream proxies is configured) to access the website; if the visited website is not blocked, in order to speed up the access, the proxies will Direct access to the website without using a upstream proxies.
|
||||
- Domain name black and white list, more free to control the way the website is accessed.
|
||||
- Cross-platform, whether you are widows, linux, mac, or even raspberry pie, you can run the proxy very well.
|
||||
- Multi-protocol support, support for HTTP(S), TCP, UDP, Websocket, SOCKS5 proxy.
|
||||
- TCP/UDP port forwarding.
|
||||
- Support intranet penetration, protocol supports TCP and UDP.
|
||||
- SSH relay, HTTP (S), SOCKS5 proxy supports SSH relay, the upper Linux server does not need any server, a local proxy can be happy online.
|
||||
- [KCP](https://github.com/xtaci/kcp-go) protocol support, HTTP(S), SOCKS5, SPS proxy supports KCP protocol to transmit data, reduce latency and improve browsing experience.
|
||||
- Dynamic selection of upstream proxies, through the external API, HTTP (S), SOCKS5, SPS proxies can achieve user-based or IP-based speed limit, connection limit, dynamic access to upstream.
|
||||
- Flexible upstream allocation, HTTP(S), SOCKS5 proxy can implement user- or IP-based speed limit, connection limit, and upper-level through configuration files.
|
||||
- Transparent HTTP (S) proxy, in conjunction with iptables, forwards the outgoing 80, 443 traffic directly to the proxy at the gateway, enabling non-aware intelligent router proxy.
|
||||
- Protocol conversion, which can convert existing HTTP(S) or SOCKS5 or SS proxy into one port and support HTTP(S) and SOCKS5 and SS proxy at the same time. Converted SOCKS5 and SS proxy. If the upstream is SOCKS5 proxy, then UDP is supported. Features while supporting powerful cascading authentication.
|
||||
- Custom underlying encrypted transmission, http(s)\sps\socks proxy can encrypt tcp data via tls standard encryption and kcp protocol on top of tcp, in addition to support custom encryption after tls and kcp, that is Said custom encryption and tls|kcp can be used in combination, the internal AES256 encryption, you only need to define a password when you use it.
|
||||
- Underlying compression efficient transmission, http(s)\sps\socks proxy can encrypt tcp data through custom encryption and tls standard encryption and kcp protocol on tcp, and can also compress data after encryption, that is, compression function And custom encryption and tls|kcp can be used in combination.
|
||||
- Secure DNS proxy, which can secure and prevent pollution DNS queries through encrypted proxy communication between the DNS proxy server provided by the local proxy and the upstream proxy.
|
||||
- Load balancing, high availability, HTTP(S)\SOCKS5\SPS proxies supports upstream load balancing and high availability, and multiple upstream repeat-P parameters can be used.
|
||||
- Specify the egress IP. The HTTP(S)\SOCKS5\SPS\TCP proxy supports the client to connect with the ingress IP, and uses the ingress IP as the egress IP to access the target website. If the ingress IP is an intranet IP, the egress IP does not use the ingress IP.
|
||||
- Support speed limit, HTTP(S)\SOCKS5\SPS\TCP proxy supports speed limit.
|
||||
- SOCKS5 proxies supports cascading certification.
|
||||
- The certificate parameter uses base64 data. By default, the -C, -K parameter is the path of the crt certificate and the key file. If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
- Support client IP black and white list, more secure control of client access to proxy service, if black and white list is set at the same time, then only whitelist is effective. Socks / HTTP(S) / SPS / TCP / UDP / DNS / intranet NAT The bridge/intranet NAT the tbridge and supports the client IP black and white list.
|
||||
- Range ports listen on, HTTP(S)\SOCKS5\SPS\TCP proxy supports port range listening, avoiding starting too many processes and improving performance.
|
||||
|
||||
### Why do you need it?
|
||||
|
||||
- When for some reason we are unable to access our services elsewhere, we can establish a secure tunnel to access our services through multiple connected proxy nodes.
|
||||
- WeChat interface is developed locally for easy debugging.
|
||||
- Remote access to intranet machines.
|
||||
- Play LAN games with your friends.
|
||||
- I used to play only on the LAN, and now I can play anywhere.
|
||||
- Replace the sword inside Netnet, show IP internal Netcom, peanut shell and other tools.
|
||||
- ..
|
||||
|
||||
|
||||
The manual on this page applies to the latest version of goproxy. Other versions may not be applicable. Please use the command according to your own instructions.
|
||||
|
||||
|
||||
### Joining the organization
|
||||
[Click to join the gitter](https://gitter.im/go-proxy/Lobby?utm_source=share-link&utm_medium=link&utm_campaign=share-link)
|
||||
|
||||
[Click to join the TG](https://t.me/snail007_goproxy)
|
||||
|
||||
## Download and install
|
||||
|
||||
### Quick installation
|
||||
|
||||
0. If your VPS is a Linux 64-bit system, you only need to execute the following sentence to complete the automatic installation and configuration.
|
||||
|
||||
Tip: All operations require root privileges.
|
||||
|
||||
The free version performs this:
|
||||
|
||||
```shell
|
||||
curl -L https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/install_auto.sh | bash
|
||||
```
|
||||
|
||||
The commercial version performs this:
|
||||
|
||||
```shell
|
||||
curl -L https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/install_auto_commercial.sh | bash
|
||||
```
|
||||
|
||||
The installation is complete, the configuration directory is /etc/proxy. For more detailed usage, please refer to the manual directory above to learn more about the features you want to use.
|
||||
If the installation fails or your vps is not a linux64-bit system, follow the semi-automatic steps below to install:
|
||||
|
||||
### Manual installation
|
||||
|
||||
1. Download the proxy
|
||||
|
||||
Download address: https://github.com/snail007/goproxy/releases/latest
|
||||
|
||||
Let's take v7.9 as an example. If you have the latest version, please use the latest version of the link. Note that the version number in the download link below is the latest version number.
|
||||
|
||||
The free version performs this:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/v7.9/proxy-linux-amd64.tar.gz
|
||||
```
|
||||
|
||||
The commercial version performs this:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/v7.9/proxy-linux-amd64_commercial.tar.gz
|
||||
```
|
||||
|
||||
2. Download the automatic installation script
|
||||
|
||||
The free version performs this:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/install.sh
|
||||
chmod +x install.sh
|
||||
./install.sh
|
||||
```
|
||||
|
||||
The commercial version performs this:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/install_commercial.sh
|
||||
chmod +x install_commercial.sh
|
||||
./install_commercial.sh
|
||||
```
|
||||
|
||||
## TODO
|
||||
- http,socks proxy multiple upstream load balancing?
|
||||
- http(s) proxy to increase pac support?
|
||||
- Welcome to add group feedback..
|
||||
|
||||
## License
|
||||
Proxy is licensed under GPLv3 license.
|
||||
|
||||
## Contact
|
||||
Official QQ exchange group: 42805407
|
||||
|
||||
## Donation
|
||||
If the proxy helps you solve a lot of problems, you can better support the proxy through the donation below.
|
||||
|
||||
BTC ADDRESS: `1BJcBhGhREiz1q3VTYoiVPuAZy5PGxRG9z`
|
||||
|
||||
<img src="https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/docs/img/btc.png" width="150" height="auto"/>
|
||||
|
||||
ETH ADDRESS: `0x0fA4c567768d2E59E6221152EA52F4842866AFC8`
|
||||
|
||||
<img src="https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/docs/img/eth.png" width="150" height="auto"/>
|
||||
|
||||
### Source code declaration
|
||||
|
||||
The author of this project found that a large number of developers based on the project for secondary development or using a large number of core code of the project without complying with the GPLv3 agreement, which seriously violates the original intention of using the GPLv3 open source agreement in this project. In view of this situation, the project adopts the source. The code delays the release strategy, to a certain extent, to curb these behaviors that do not respect open source and do not respect the labor results of others.
|
||||
This project will continue to update the iterations and continue to release the full platform binary program, providing you with powerful and convenient proxies tools.
|
||||
If you have customized, business needs, please send an email to `[email protected]`
|
||||
|
||||
## Goproxy Manual
|
||||
|
||||
|
||||
## How to Install
|
||||
|
||||
### 1. Linux Install
|
||||
|
||||
[click me get Linux installation](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E4%B8%8B%E8%BD%BD%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
### 2. MacOS Install
|
||||
|
||||
[click me get MacOS installation](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
### 3. Windows Install
|
||||
|
||||
[click me get Windows installation](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
### 4. Others Install
|
||||
|
||||
[click me get Windows installation](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E6%89%8B%E5%8A%A8%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
## Purchase Commercial Edition
|
||||
|
||||
This manual describes the functions, all of which are included in the commercial version; the free version of advanced functional parameters such as authentication is not included;
|
||||
If you encounter some commands when you use the free version to execute some commands, a prompt similar to the following xxx parameter does not exist, indicating that this parameter is a function of the commercial version.
|
||||
`err: unknown long flag '-a'`
|
||||
Comparison between the features of the free version and the commercial version, detailed operations on how to purchase and use the commercial version [please click here to view](https://snail.gitee.io/proxy/page/free_vs_commercial_en/)
|
||||
|
||||
## First Start
|
||||
|
||||
### 1. Environment
|
||||
|
||||
The manual tutorial, the default system is linux, the program is proxy; all operations require root privileges;
|
||||
|
||||
If you are windows, please use the windows version of proxy.exe.
|
||||
|
||||
### 2. Using configuration files
|
||||
|
||||
The next tutorial will introduce the usage method through the command line parameters, or you can get the parameters by reading the configuration file.
|
||||
|
||||
The specific format is to specify the configuration file by the @ symbol, for example: proxy @configfile.txt
|
||||
|
||||
The format in configfile.txt is that the first line is the name of the subcommand, and the second line starts with one parameter per line.
|
||||
|
||||
Format: `parameter Parameter value`, direct write parameter without parameter value, for example: --nolog
|
||||
|
||||
For example, the contents of configfile.txt are as follows:
|
||||
|
||||
```shell
|
||||
Http
|
||||
-t tcp
|
||||
-p :33080
|
||||
--forever
|
||||
```
|
||||
|
||||
### 3. Debug output
|
||||
|
||||
By default, the information output by the log does not include the number of file lines. In some cases, in order to troubleshoot the program, the problem is quickly located.
|
||||
|
||||
You can use the --debug parameter to output the number of lines of code and milliseconds.
|
||||
|
||||
### 4. Using log files
|
||||
|
||||
By default, the log is displayed directly in the console. If you want to save to a file, you can use the --log parameter.
|
||||
|
||||
For example: --log proxy.log, the log will be output to the proxy.log to facilitate troubleshooting.
|
||||
|
||||
|
||||
### 5. Generate the certificate file required for encrypted communication
|
||||
|
||||
The http, tcp, udp proxy process communicates with the upstream. For security, we use encrypted communication. Of course, we can choose not to encrypt the communication. All the communication and the upstream communication in this tutorial are encrypted, and the certificate file is required.
|
||||
|
||||
1. Generate a self-signed certificate and key file with the following command.
|
||||
`proxy keygen -C proxy`
|
||||
The certificate file proxy.crt and the key file proxy.key will be generated under the current program directory.
|
||||
|
||||
2. Use the following command to generate a new certificate using the self-signed certificate proxy.crt and the key file proxy.key: goproxy.crt and goproxy.key.
|
||||
`proxy keygen -s -C proxy -c goproxy`
|
||||
The certificate file goproxy.crt and the key file goproxy.key will be generated under the current program directory.
|
||||
|
||||
3. By default, the domain name inside the certificate is random and can be specified using the `-n test.com` parameter.
|
||||
|
||||
4. More usage: `proxy keygen --help`.
|
||||
|
||||
### 6. Running in the background
|
||||
|
||||
After the proxy is executed by default, you cannot close the command line if you want to keep the proxy running.
|
||||
|
||||
If you want to run the proxy in the background, the command line can be closed, just add the --daemon parameter at the end of the command.
|
||||
|
||||
For example:
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080" --daemon`
|
||||
|
||||
### 7. Guardian running
|
||||
The daemon runs the parameter --forever, for example: `proxy http --forever` ,
|
||||
|
||||
The proxy will fork the child process, and then monitor the child process. If the child process exits abnormally, restart the child process after 5 seconds.
|
||||
|
||||
This parameter is matched with the background running parameter --daemon and log parameter --log, which can guarantee that the proxy will always execute in the background without accidentally exiting.
|
||||
|
||||
And you can see the output log content of the proxy through the log file.
|
||||
|
||||
For example: `proxy http -p ":9090" --forever --log proxy.log --daemon`
|
||||
|
||||
### 8. Security advice
|
||||
|
||||
When the VPS is behind the nat device, the vps network card IP is the intranet IP. At this time, you can use the -g parameter to add the vps external network ip to prevent the infinite loop.
|
||||
|
||||
Suppose your vps external network ip is 23.23.23.23. The following command sets 23.23.23.23 with the -g parameter.
|
||||
|
||||
`proxy http -g "23.23.23.23"`
|
||||
|
||||
### 9. Load balancing and high availability
|
||||
|
||||
The HTTP(S)\SOCKS5\SPS proxy supports upper-level load balancing and high availability, and multiple upstream repeat-P parameters can be used.
|
||||
|
||||
The load balancing policy supports five types, which can be specified by the `--lb-method` parameter:
|
||||
|
||||
Roundrobin used in turn
|
||||
|
||||
Leastconn uses the minimum number of connections
|
||||
|
||||
Leasttime uses the least connection time
|
||||
|
||||
Hash uses a fixed upstream based on the client address
|
||||
|
||||
Weight Select a upstream according to the weight and number of connections of each upstream
|
||||
|
||||
prompt:
|
||||
|
||||
1. The load balancing check interval can be set by `--lb-retrytime` in milliseconds.
|
||||
|
||||
2. The load balancing connection timeout can be set by `--lb-timeout` in milliseconds.
|
||||
|
||||
3. If the load balancing policy is weight, the -P format is: 2.2.2.2: 3880?w=1, where 1 is the weight and an integer greater than 0.
|
||||
|
||||
4. If the load balancing policy is hash, the default is to select the upstream based on the client address. You can select the upstream by using the destination address of the access `--lb-hashtarget`.
|
||||
|
||||
5. The TCP proxies has no parameter `--lb-hashtarget`.
|
||||
|
||||
6. Default is load balancing + high availability mode. If the parameter `--lb-onlyha` is used, only the high availability mode is used, then a node is selected according to the load balancing strategy, and this node will be used until it is not alive, then another node will be selected for using, thus cycling.
|
||||
|
||||
7. If the all nodes are not alive, a random node will be selected for using.
|
||||
|
||||
### 10. Agent springboard jump
|
||||
|
||||
Http (s) agent, SPS agent, intranet penetration, tcp agent support the connection of upstreams through intermediate third-party agents,
|
||||
|
||||
The parameters are: --jumper, all the formats are as follows:
|
||||
|
||||
```text
|
||||
http://username:password@host:port
|
||||
http://host:port
|
||||
https://username:password@host:port
|
||||
https://host:port
|
||||
socks5://username:password@host:port
|
||||
socks5://host:port
|
||||
socks5s://username:password@host:port
|
||||
socks5s://host:port
|
||||
ss://method:password@host:port
|
||||
```
|
||||
|
||||
Http,socks5 represents the normal http and socks5 proxy.
|
||||
|
||||
Https,socks5s represents the http and socks5 agents protected by tls.
|
||||
|
||||
That is http proxy over TLS, socks over TLS.
|
||||
|
||||
### 11. Domain Name Black and White List
|
||||
|
||||
The socks/http(s)/sps proxy supports domain name black and white lists.
|
||||
|
||||
Use the --stop parameter to specify a domain name blacklist file, then the connection will be disconnected when the user connects these domains in the file.
|
||||
|
||||
Specify a domain name whitelist file with the --only parameter, then the connection will be disconnected when the user connects to a domain other than those domains in the file.
|
||||
|
||||
If both --stop and --only are set, then only --only will work.
|
||||
|
||||
The format of the black and white domain name list file is as follows:
|
||||
|
||||
```text
|
||||
**.baidu.com
|
||||
*.taobao.com
|
||||
A.com
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
?.qq.com
|
||||
```
|
||||
|
||||
Description:
|
||||
|
||||
1. One domain name per line, domain name writing supports wildcards `*` and `?`, `*` represents any number of characters, `?` represents an arbitrary character,
|
||||
|
||||
2.`**.baidu.com` Matches no matter how many levels all suffixes are ..baidu.com`.
|
||||
|
||||
3.`*.taobao.com` The matching suffix is the third-level domain name of `.taobao.com`.
|
||||
|
||||
4. It can also be an IP address directly.
|
||||
|
||||
5.`#` at the beginning of the comment.
|
||||
|
||||
### 12. Client IP Blacklist and Whitelist
|
||||
|
||||
socks/http(s)/sps/tcp/udp/dns/ intranet penetration bridge/intranet penetration tbridge, support client IP black and white list.
|
||||
|
||||
Use the --ip-deny parameter to specify a client IP blacklist list file, then the connection will be disconnected when the user's IP is in this file.
|
||||
|
||||
Use the --ip-allow parameter to specify a client IP whitelist file, then the connection will be disconnected when the user's IP is not in the file.
|
||||
|
||||
If both --ip-deny and --ip-allow are set, then only --ip-allow will work.
|
||||
|
||||
The format of the client IP blacklist and whitelist file is as follows:
|
||||
|
||||
```text
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
192.168.1?.*
|
||||
```
|
||||
|
||||
Description:
|
||||
|
||||
1. One domain name per domain, domain name writing supports wildcards `*` and `?`, `*` represents any number of characters, `?` represents an arbitrary character.
|
||||
|
||||
2.`#` at the beginning of the comment.
|
||||
|
||||
### 13. Protocol loading file
|
||||
|
||||
There are many places in the proxy's various proxy functions to set a file. For example: --blocked Specifies a domain name list file that goes directly to the upper level. The parameter value is the path of the file.
|
||||
|
||||
If the parameter supports the protocol loading file, the file path can be not only the file path, but also:
|
||||
|
||||
a. The base64 encoding at the beginning of "base64://" indicates the contents of the above file, for example: base64://ajfpoajsdfa=
|
||||
|
||||
b. "str://" at the beginning of the English comma separated multiple, such as: str://xxx, yyy
|
||||
|
||||
The proxy's blocked, direct, stop, only, hosts, resolve.rules, rewriter.rules, ip.allow, ip.deny files support protocol loading.
|
||||
|
||||
|
||||
### 14.Concurrent client connections
|
||||
|
||||
socks5\sps\http proxies, the parameter that controls the number of concurrent client connections is: `--max-conns-rate`, which controls the maximum number of client connections per second, default: 20, 0 is unlimited
|
||||
|
||||
### 15 Listen on multiple ports
|
||||
|
||||
"tcp / http / socks / sps" supports listen on multiple ports and range ports.
|
||||
Under normal circumstances, it is sufficient to listen on one port, but if you need to listen on multiple ports, the -p parameter is supported.
|
||||
The format is: `-p 0.0.0.0:80,0.0.0.0:443,.0.0.0.0:8000-9000,:5000-6000`, more The bindings can be separated by commas.
|
||||
|
||||
## 1.HTTP Proxies
|
||||
|
||||
### 1.1. Ordinary level HTTP proxy
|
||||
|
||||

|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080"`
|
||||
|
||||
Listen port argument `-p` can be:
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000 and 9001 to 9999, 1002 total ports
|
||||
```
|
||||
|
||||
### 1.2. Ordinary secondary HTTP proxy
|
||||
|
||||

|
||||
|
||||
Use local port 8090, assuming the upstream HTTP proxy is `22.22.22.22:8080`
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" `
|
||||
|
||||
We can also specify the black and white list file of the website domain name, one domain name per line, the matching rule is the rightmost match, for example: baidu.com, the match is *.*.baidu.com, the blacklist domain name goes directly to the upstream agent, whitelist The domain name does not go to the upstream agent.
|
||||
|
||||
`proxy http -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt`
|
||||
|
||||
### 1.3.HTTP secondary agent (encryption)
|
||||
|
||||
> Note: The `proxy.crt` and `proxy.key` used by the secondary proxy should be consistent with the primary proxy.
|
||||
|
||||

|
||||
Level 1 HTTP proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Secondary HTTP proxy (local Linux)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS.
|
||||
|
||||
Secondary HTTP proxy (local windows)
|
||||
`proxy.exe http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then set your windos system, the proxy that needs to go through the proxy Internet program is http mode, the address is: 127.0.0.1, the port is: 8080, the program can access the Internet through vps through the encrypted channel.
|
||||
|
||||
### 1.4.HTTP Level 3 Agent (Encryption)
|
||||

|
||||
Level 1 HTTP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
Secondary HTTP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy http -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 HTTP proxy (local)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then accessing the local port 8080 is to access the proxy port 38080 on the primary HTTP proxy.
|
||||
|
||||
### 1.5.Basic certification
|
||||
For the proxy HTTP protocol, we can perform Basic authentication. The authenticated username and password can be specified on the command line.
|
||||
`proxy http -t tcp -p ":33080" -a "user1:pass1" -a "user2:pass2"`
|
||||
For multiple users, repeat the -a parameter.
|
||||
It can also be placed in a file in the format of a "username:password" and then specified with -F.
|
||||
`proxy http -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
In addition, the http(s) proxy also integrates external HTTP API authentication. We can specify an http url interface address with the --auth-url parameter.
|
||||
Then when there is a user connection, the proxy will request the url in GET mode, and bring the following four parameters. If the HTTP status code 204 is returned, the authentication is successful.
|
||||
In other cases, the authentication failed.
|
||||
For example:
|
||||
`proxy http -t tcp -p ":33080" --auth-url "http://test.com/auth.php"`
|
||||
When the user connects, the proxy will request the url ("http://test.com/auth.php") in GET mode.
|
||||
Take five parameters: user, pass, ip, local_ip, target:
|
||||
Http://test.com/auth.php?user={USER}&pass={PASS}&ip={IP}&local_ip={LOCAL_IP}&target={TARGET}
|
||||
User: username
|
||||
Pass: password
|
||||
Ip: User's IP, for example: 192.168.1.200
|
||||
Local_ip: IP of the server accessed by the user, for example: 3.3.3.3
|
||||
Target: URL accessed by the user, for example: http://demo.com:80/1.html or https://www.baidu.com:80
|
||||
|
||||
If there is no -a or -F or --auth-url parameter, the Basic authentication is turned off.
|
||||
|
||||
### 1.6. HTTP proxy traffic is forced to go to the upper HTTP proxy
|
||||
By default, the proxy will intelligently determine whether a website domain name is inaccessible. If it is not accessible, it will go to the upper level HTTP proxy. With --always, all HTTP proxy traffic can be forced to go to the upper HTTP proxy.
|
||||
`proxy http --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
### 1.7.HTTP(S) via SSH relay
|
||||

|
||||
Description: The principle of ssh transfer is to use the forwarding function of ssh, that is, after you connect to ssh, you can access the target address through ssh proxy.
|
||||
Suppose there is: vps
|
||||
- IP is 2.2.2.2, ssh port is 22, ssh username is: user, ssh user password is: demo
|
||||
- The user's ssh private key name is user.key
|
||||
|
||||
#### *1.7.1 How to ssh username and password*
|
||||
Local HTTP(S) proxy port 28080, executing:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080"`
|
||||
#### *1.7.2 How to ssh username and key*
|
||||
Local HTTP(S) proxy port 28080, executing:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080"`
|
||||
|
||||
### 1.8.KCP protocol transmission
|
||||

|
||||
The KCP protocol requires the --kcp-key parameter to set a password for encrypting and decrypting data.
|
||||
|
||||
Level 1 HTTP proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy http -t kcp -p ":38080" --kcp-key mypassword`
|
||||
|
||||
Secondary HTTP proxy (local Linux)
|
||||
`proxy http -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS, the data is transmitted through the kcp protocol, note that the kcp is the udp protocol, so the firewall needs to release the 380p udp protocol.
|
||||
|
||||
### 1.9 HTTP(S) Reverse Proxy
|
||||

|
||||
The proxy not only supports the proxy setting in other software, but also provides proxy services for other software. It also supports directly parsing the requested website domain name to the proxy listening ip, and then the proxy listens to the 80 and 443 ports, then the proxy will automatically You proxy access to the HTTP(S) website you need to access.
|
||||
|
||||
How to use:
|
||||
On the "last level proxy proxy" machine, because the proxy is to be disguised as all websites, the default HTTP port of the website is 80, HTTPS is 443, and the proxy can listen to ports 80 and 443. Parameters -p multiple addresses with commas segmentation.
|
||||
`proxy http -t tcp -p :80,:443`
|
||||
|
||||
This command starts a proxy agent on the machine, and listens to ports 80 and 443 at the same time. It can be used as a normal proxy, or directly resolve the domain name that needs to be proxyed to the IP of this machine.
|
||||
|
||||
If there is a upstream agent, then refer to the above tutorial to set the upstream, the use is exactly the same.
|
||||
`proxy http -t tcp -p :80,:443 -T tls -P "2.2.2.2:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Note:
|
||||
The DNS resolution result of the server where the proxy is located cannot be affected by the custom resolution, otherwise it will be infinite loop. The proxy proxy should specify the `--dns 8.8.8.8` parameter.
|
||||
|
||||
### 1.10 HTTP(S) Transparent Proxy
|
||||
This mode needs to have a certain network foundation. If the related concepts are not understood, please search for it yourself.
|
||||
Assuming the proxy is now running on the router, the startup command is as follows:
|
||||
`proxy http -t tcp -p :33080 -T tls -P "2.2.2.2:33090" -C proxy.crt -K proxy.key`
|
||||
|
||||
Then add the iptables rule, here are the reference rules:
|
||||
```shell
|
||||
#Upper proxy server IP address:
|
||||
Proxy_server_ip=2.2.2.2
|
||||
|
||||
#路由器Running port for proxy listening:
|
||||
Proxy_local_port=33080
|
||||
|
||||
#The following does not need to be modified
|
||||
#create a new chain named PROXY
|
||||
Iptables -t nat -N PROXY
|
||||
|
||||
# Ignore your PROXY server's addresses
|
||||
# It's very IMPORTANT, just be careful.
|
||||
|
||||
Iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
# Ignore LANs IP address
|
||||
Iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
# Anything to port 80 443 should be redirected to PROXY's local port
|
||||
Iptables -t nat -A PROXY -p tcp --dport 80 -j REDIRECT --to-ports $proxy_local_port
|
||||
Iptables -t nat -A PROXY -p tcp --dport 443 -j REDIRECT --to-ports $proxy_local_port
|
||||
|
||||
# Apply the rules to nat client
|
||||
Iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
# Apply the rules to localhost
|
||||
Iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
- Clear the entire chain iptables -F Chain names such as iptables -t nat -F PROXY
|
||||
- Delete the specified user-defined chain iptables -X chain name such as iptables -t nat -X PROXY
|
||||
- Remove rules from the selected chain iptables -D chain name Rule details such as iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 1.11 Custom DNS
|
||||
--dns-address and --dns-ttl parameters, used to specify the dns (--dns-address) used by the proxy to access the domain name.
|
||||
And the analysis result cache time (--dns-ttl) seconds, to avoid system dns interference to the proxy, in addition to the cache function can also reduce the dns resolution time to improve access speed.
|
||||
For example:
|
||||
`proxy http -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 1.12 Custom encryption
|
||||
The proxy's http(s) proxy can encrypt tcp data via tls standard encryption and kcp protocol on top of tcp, in addition to support customization after tls and kcp.
|
||||
Encryption, that is to say, custom encryption and tls|kcp can be used in combination. The internal use of AES256 encryption, you only need to define a password when you use it.
|
||||
Encryption is divided into two parts, one is whether the local (-z) encryption and decryption, and the other is whether the transmission with the upstream (-Z) is encrypted or decrypted.
|
||||
Custom encryption requires both ends to be proxy. The following two levels and three levels are used as examples:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
### 1.13 Compressed transmission
|
||||
The proxy http(s) proxy can encrypt tcp data through tls standard encryption and kcp protocol on top of tcp, and can also compress data before custom encryption.
|
||||
That is to say, compression and custom encryption and tls|kcp can be used in combination. Compression is divided into two parts, one part is local (-m) compression transmission.
|
||||
Part of it is compressed with the upstream (-M) transmission.
|
||||
Compression requires both sides to be proxy. Compression also protects (encrypted) data to a certain extent. The following uses Level 2 and Level 3 as examples:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
### 1.14 Load Balancing
|
||||
|
||||
The HTTP(S) proxy supports upper-level load balancing, and multiple upstream repeat-P parameters can be used.
|
||||
|
||||
`proxy http --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080`
|
||||
|
||||
### 1.14.1 Setting the retry interval and timeout time
|
||||
|
||||
`proxy http --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp - p :33080`
|
||||
|
||||
### 1.14.2 Setting weights
|
||||
|
||||
`proxy http --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -t tcp - p :33080`
|
||||
|
||||
### 1.14.3 Use the target address to select the upstream
|
||||
|
||||
`proxy http --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp -p :33080`
|
||||
|
||||
### 1.15 Speed limit
|
||||
|
||||
The speed limit is 100K, which can be specified by the `-l` parameter, for example: 100K 2000K 1M . 0 means no limit.
|
||||
|
||||
`proxy http -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 1.16 Specifying Outgoing IP
|
||||
|
||||
The `--bind-listen` parameter can be used to open the client connection with the portal IP, and use the portal IP as the outgoing IP to access the target website. If the incorrect IP is bound, the proxy will not work. At this point, the proxy will try to bind the target without binding the IP, and the log will prompt.
|
||||
|
||||
`proxy http -t tcp -p 2.2.2.2:33080 --bind-listen`
|
||||
|
||||
### 1.17 Certificate parameters use base64 data
|
||||
|
||||
By default, the -C, -K parameter is the path to the crt certificate and the key file.
|
||||
|
||||
If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
|
||||
### 1.18 Intelligent mode
|
||||
Intelligent mode setting, can be one of intelligent|direct|parent.
|
||||
The default is: intelligent.
|
||||
The meaning of each value is as follows:
|
||||
`--intelligent=direct`, the targets in the blocked are not directly connected.
|
||||
`--intelligent=parent`, the target that is not in the direct is going to the higher level.
|
||||
`--intelligent=intelligent`, blocked and direct have no targets, intelligently determine whether to use the upstream access target.
|
||||
|
||||
### 1.19 Help
|
||||
`proxy help http`
|
||||
|
||||
## 2.TCP Proxies
|
||||
|
||||
### 2.1. Ordinary level TCP proxy
|
||||

|
||||
Local execution:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22"`
|
||||
Then access the local port 33080 is to access port 22 of 192.168.22.33.
|
||||
|
||||
The `-p` parameter supports :
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000, 9001 to 9999 for a total of 1002 ports
|
||||
```
|
||||
|
||||
If the number of local listening ports is greater than 1, the corresponding upper port corresponding to the local port will be connected, and the port in `-P` will be ignored.
|
||||
|
||||
If you need a connection from all ports, connect to the upper specified port, you can add the parameter `--lock-port`.
|
||||
|
||||
such as:
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:0"`
|
||||
|
||||
Then the connection of the `33080` port will connect to the `33080` port of 192.168.22.33, and the other ports are similar. The local and upper ports are the same. At this time, the port in the parameter `-P` uses `0`.
|
||||
|
||||
If you want to connect the ports of `33080`, `33081`, etc. to the `22` port of 192.168.22.33, you can add the parameter `--lock-port`.
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:22" --lock-port`
|
||||
|
||||
### 2.2. Ordinary secondary TCP proxy
|
||||

|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
Local execution:
|
||||
`proxy tcp -p ":23080" -T tcp -P "22.22.22.33:33080"`
|
||||
Then access the local port 23080 is to access port 8020 of 22.22.22.33.
|
||||
|
||||
### 2.3. Ordinary three-level TCP proxy
|
||||

|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -p ":38080" -T tcp -P "66.66.66.66:8080"`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy tcp -p ":8080" -T tcp -P "33.33.33.33:28080"`
|
||||
Then access the local port 8080 is to access the port 8080 of 66.66.66.66 through the encrypted TCP tunnel.
|
||||
|
||||
### 2.4. Encrypting secondary TCP proxy
|
||||

|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -t tls -p ":33080" -T tcp -P "127.0.0.1:8080" -C proxy.crt -K proxy.key`
|
||||
Local execution:
|
||||
`proxy tcp -p ":23080" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 23080 is to access the port 8080 of 22.22.22.33 through the encrypted TCP tunnel.
|
||||
|
||||
### 2.5.Encrypting Level 3 TCP Agent
|
||||

|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T tcp -P "66.66.66.66:8080" -C proxy.crt -K proxy.key`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 8080 is to access the port 8080 of 66.66.66.66 through the encrypted TCP tunnel.
|
||||
|
||||
### 2.6 Connecting to a upstream through a proxy
|
||||
Sometimes the network where the proxy is located cannot directly access the external network. You need to use an https or socks5 proxy to access the Internet. Then this time
|
||||
The -J parameter can help you to connect the proxy to the peer-P through the https or socks5 proxy when mapping the proxy tcp port, mapping the external port to the local.
|
||||
The -J parameter format is as follows:
|
||||
|
||||
Https proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Https://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Https://host:port
|
||||
|
||||
Socks5 proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Socks5://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Socks5://host:port
|
||||
|
||||
Host: the IP or domain name of the proxy
|
||||
Port: the port of the proxy
|
||||
|
||||
### 2.7 Specify Outgoing IP
|
||||
When the TCP proxy is a superior type (parameter: -T) is tcp, it supports the specified exit IP. Using the `--bind-listen` parameter, you can open the client to connect with the portal IP, and use the portal IP as the outgoing IP to access the target website. If an incorrect IP is bound, the proxy will not work, the proxy will try to bind the target without binding the IP, and the log will prompt.
|
||||
|
||||
`proxy tcp -p ":33080" -T tcp -P" 192.168.22.33:22" -B`
|
||||
|
||||
### 2.8 Speed limit, connections limit
|
||||
|
||||
The parameter `--max-conns` can limit the maximum number of connections per port.
|
||||
For example, limit the maximum number of connections per port:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --max-conns 1000`
|
||||
The parameter `--rate-limit` can limit the rate of each tcp connection.
|
||||
For example, limit the connection rate of each tcp to 100k/s:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --rate-limit 100k`
|
||||
|
||||
### 2.9 Compressed transmission
|
||||
|
||||
`--c` controls whether to compress transmission between local and client, default false;` --C` controls whether to compress transmission between local and upstream, default false.
|
||||
|
||||
Examples:
|
||||
|
||||
VPS (IP: 22.22.22.33) implementation:
|
||||
`proxy tcp -t tcp --c -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
Local execution:
|
||||
`proxy tcp -t tcp -p ":23080" -T tcp -P "22.22.22.33:33080" --C`
|
||||
|
||||
### 2.10 View Help
|
||||
`proxy help tcp`
|
||||
|
||||
## 3.UDP Proxies
|
||||
|
||||
### 3.1. Ordinary UDP proxy
|
||||

|
||||
Local execution:
|
||||
`proxy udp -p ":5353" -T udp -P "8.8.8.8:53"`
|
||||
Then access the local UDP: 5353 port is to access 8.8.8.8 UDP: 53 port.
|
||||
|
||||
The `-p` parameter supports :
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000, 9001 to 9999 for a total of 1002 ports
|
||||
```
|
||||
|
||||
If the number of local listening ports is greater than 1, the corresponding upper port corresponding to the local port will be connected, and the port in `-P` will be ignored.
|
||||
|
||||
If you need a connection from all ports, connect to the upper specified port, you can add the parameter `--lock-port`.
|
||||
|
||||
such as:
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:0"`
|
||||
|
||||
Then the connection of the `33080` port will connect to the `33080` port of 192.168.22.33, and the other ports are similar. The local and upper ports are the same. At this time, the port in the parameter `-P` uses `0`.
|
||||
|
||||
If you want to connect the ports of `33080`, `33081`, etc. to the `2222` port of 192.168.22.33, you can add the parameter `--lock-port`.
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:2222" --lock-port`
|
||||
|
||||
### 3.2. Ordinary secondary UDP proxy
|
||||

|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -p ":33080" -T udp -P "8.8.8.8:53"`
|
||||
Local execution:
|
||||
`proxy udp -p ":5353" -T tcp -P "22.22.22.33:33080"`
|
||||
Then access the local UDP: 5353 port is through the TCP tunnel, through the VPS access 8.8.8.8 UDP: 53 port.
|
||||
|
||||
### 3.3. Ordinary three-level UDP proxy
|
||||

|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -p ":38080" -T udp -P "8.8.8.8:53"`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy udp -p ":5353" -T tcp -P "33.33.33.33:28080"`
|
||||
Then access to the local 5353 port is through the TCP tunnel, through the VPS to access port 8.8.8.8.
|
||||
|
||||
### 3.4. Encrypting secondary UDP proxy
|
||||

|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -t tls -p ":33080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
Local execution:
|
||||
`proxy udp -p ":5353" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
Then access the local UDP: 5353 port is through the encrypted TCP tunnel, through the VPS access 8.8.8.8 UDP: 53 port.
|
||||
|
||||
### 3.5. Encryption Level 3 UDP Agent
|
||||

|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy udp -p ":5353" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then access the local 5353 port is to access the 8.8.8.8 port 53 through VPS_01 through the encrypted TCP tunnel.
|
||||
|
||||
### 3.6 Specify Outgoing IP
|
||||
When the UDP upstream proxies (parameter: -T) is udp, it supports the specified outgoing IP. Using the `--bind-listen` parameter, you can open the client to connect with the server IP, and use the server IP as the outgoing IP to access the target. If an incorrect IP is bound, the proxy will not work.
|
||||
|
||||
`proxy udp -p ":33080" -T udp -P "192.168.22.33:2222" -B`
|
||||
|
||||
### 3.7 Help
|
||||
`proxy help udp`
|
||||
|
||||
## 4. Expose Intranet
|
||||
|
||||
### 4.1 principle description
|
||||
Intranet penetration, divided into two versions, "multi-link version" and "multiplexed version", generally like a web service, this service is not a long-term connection, it is recommended to use "multi-link version", if it is to keep long The time connection suggests using a "multiplexed version."
|
||||
1. Multi-link version, the corresponding sub-command is tserver, tclient, tbridge.
|
||||
1. Multiplexed version, the corresponding subcommand is server, client, bridge.
|
||||
1. The parameters of the multi-link version and the multiplex version are exactly the same.
|
||||
1. The multiplexed version of the server, client can open the compressed transmission, the parameter is --c.
|
||||
1. server, client either open compression, or not open, can not open only one.
|
||||
|
||||
The following tutorial uses the "multiplexed version" as an example to illustrate how to use it.
|
||||
The intranet penetration consists of three parts: client, server, and bridge; client and server actively connect to the bridge for bridging.
|
||||
|
||||
### 4.2 TCP common usage
|
||||
Background:
|
||||
- Company Machine A provides web service port 80
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
At home, you can access the port 80 of company machine A by accessing port 28080 of the VPS.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.3 WeChat interface local development
|
||||
Background:
|
||||
- Your own notebook provides nginx service port 80
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
Fill in the address in the webpage callback interface configuration of WeChat's development account: http://22.22.22.22/calback.php
|
||||
Then you can access the calback.php under the 80 port of the notebook. If you need to bind the domain name, you can use your own domain name.
|
||||
For example: wx-dev.xxx.com resolves to 22.22.22.22, and then in your own notebook nginx
|
||||
Configure the domain name wx-dev.xxx.com to the specific directory.
|
||||
|
||||
|
||||
Steps:
|
||||
1. Execute on vps to ensure that port 80 of vps is not occupied by other programs.
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":80@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on your laptop
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.4 UDP common usage
|
||||
Background:
|
||||
- Company Machine A provides DNS resolution service, UDP: port 53
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
At home, you can use the company machine A to perform domain name resolution services by setting the local dns to 22.22.22.22.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server --udp -r ":53@:53" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.5 advanced usage one
|
||||
Background:
|
||||
- Company Machine A provides web service port 80
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
In order to be safe, I don't want to have access to the company machine A on the VPS, and I can access the port 28080 of the machine at home.
|
||||
Access to port 80 of company machine A via an encrypted tunnel.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on your home computer
|
||||
`proxy server -r ":28080@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.6 Advanced Usage II
|
||||
Tip:
|
||||
If multiple clients are connected to the same bridge at the same time, you need to specify a different key, which can be set by the --k parameter, and --k can be any unique string.
|
||||
Just be the only one on the same bridge.
|
||||
When the server is connected to the bridge, if there are multiple clients connecting to the same bridge at the same time, you need to use the --k parameter to select the client.
|
||||
Expose multiple ports by repeating the -r parameter. The format of -r is: "local IP: local port @clientHOST:client port".
|
||||
|
||||
Background:
|
||||
- Company Machine A provides web service port 80, ftp service port 21
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
At home, you can access the port 80 of company machine A by accessing port 28080 of the VPS.
|
||||
At home, I can access the 21 port of company machine A by accessing port 29090 of the VPS.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -r ":29090@:21" --k test -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client --k test -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.7.server -r parameter
|
||||
The full format of -r is: `PROTOCOL://LOCAL_IP:LOCAL_PORT@[CLIENT_KEY]CLIENT_LOCAL_HOST:CLIENT_LOCAL_PORT`
|
||||
|
||||
4.7.1. Protocol PROTOCOL: tcp or udp.
|
||||
For example: `-r "udp://:10053@:53" -r "tcp://:10800@:1080" -r ":8080@:80"`
|
||||
If the --udp parameter is specified, PROTOCOL defaults to udp, then:`-r ":8080@:80"` defaults to udp;
|
||||
If the --udp parameter is not specified, PROTOCOL defaults to tcp, then: `-r ":8080@:80"` defaults to tcp;
|
||||
|
||||
4.7.2. CLIENT_KEY: The default is default.
|
||||
For example: -r "udp://:10053@[test1]:53" -r "tcp://:10800@[test2]:1080" -r ":8080@:80"
|
||||
If the --k parameter is specified, such as --k test, then: `-r ":8080@:80"`CLIENT_KEY defaults to test;
|
||||
If the --k parameter is not specified, then: `-r ":8080@:80"`CLIENT_KEY defaults to default;
|
||||
|
||||
4.7.3. LOCAL_IP is empty. The default is: `0.0.0.0`, CLIENT_LOCAL_HOST is empty. The default is: `127.0.0.1`;
|
||||
|
||||
### 4.8.server and client connect bridge through proxy
|
||||
Sometimes the network where the server or client is located cannot directly access the external network. You need to use an https or socks5 proxy to access the Internet. Then this time
|
||||
The -J parameter can help you to connect the server or client to the bridge via https or socks5.
|
||||
The -J parameter format is as follows:
|
||||
|
||||
Https proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Https://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Https://host:port
|
||||
|
||||
Socks5 proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Socks5://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Socks5://host:port
|
||||
|
||||
Host: the IP or domain name of the proxy
|
||||
Port: the port of the proxy
|
||||
|
||||
### 4.9. Expose HTTP service
|
||||
|
||||
Usually the HTTP request client will use the server's ip and port to set the HOST field, but it is not the same as the expected backend actual HOST, which causes tcp to be passed.However, the backend relies on the HOST field to locate the virtual host and it will not work. Now use the `--http-host` parameter to force the HOST field value of the http header to be the actual value of the backend.Domain names and ports can be easily solved. After using the `--http-host` parameter, two headers will be added to the header of each HTTP request. The `X-Forwarded-For` and `X-Real-IP` values are the client IP, so the backend http service can easily obtain the real IP address of the client.
|
||||
|
||||
The format of the `server`-http-host parameter is as follows:
|
||||
|
||||
`--http-host www.test.com:80@2200`, if the server listens to multiple ports, just repeat the `--http-host` parameter to set the HOST for each port.
|
||||
|
||||
Example:
|
||||
|
||||
For example, the client local nginx, 127.0.0.1:80 provides a web service, which is bound to a domain name `local.com`.
|
||||
|
||||
Then the server startup parameters can be as follows:
|
||||
|
||||
`proxy server -P :30000 -r :2500@127.0.0.1:80 --http-host local.com@2500`
|
||||
|
||||
Explanation:
|
||||
|
||||
`-r :2500@127.0.0.1:80` and `--http-host local.com:80@2500` The 2500 port is the port that the server listens locally.
|
||||
|
||||
When the http protocol is used to request the ip:2500 port of the server, the header HOST field of http will be set to `local.com`.
|
||||
|
||||
### 4.10 About traffic statistics
|
||||
If you start a server docking peer separately, it is the proxy-admin control panel. You need to create a new mapping in the upper-level control panel to obtain the ID of the mapping rule.
|
||||
|
||||
Then start the server and add the parameter --server-id=the ID of the mapping rule to count the traffic.
|
||||
|
||||
### 4.11 About p2p
|
||||
Intranet penetration support When the server and client network conditions are met, the server and client are directly connected through p2p. The opening method is:
|
||||
|
||||
When starting the bridge, server, client, add the `--p2p` parameter. The server's -r parameter can be used to enable p2p (ptcp and pudp) for the port.
|
||||
|
||||
If the p2p hole fails between the server and the client, the bridge transfer data is automatically switched.
|
||||
|
||||
### 4.12 Client key whitelist
|
||||
The intranet penetrating bridge can set the client key whitelist. The parameter is --client-keys. The format can be:
|
||||
|
||||
a. File name, file content One client key can only contain the alphanumeric underscore, which is the value of the client startup parameter --k. Only the client key can connect to the whitelist client. The line starting with # is a comment.
|
||||
|
||||
b. The base64 encoding at the beginning of "base64://" is the content of the file described in a above, for example: base64://ajfpoajsdfa=
|
||||
|
||||
c. "str://" multiple keywords separated by a comma at the beginning, such as: str://default,company,school
|
||||
|
||||
The default is empty, allowing all keys.
|
||||
|
||||
### 4.13 Network NAT Type Judgment
|
||||
|
||||
Senat type judgment, easy to check whether the network supports p2p, you can execute: `proxy tools -a nattype`
|
||||
|
||||
### 4.14 Help
|
||||
`proxy help bridge`
|
||||
`proxy help server`
|
||||
`proxy help client`
|
||||
|
||||
## 5.SOCKS5 Proxies
|
||||
prompt:
|
||||
|
||||
SOCKS5 proxy, support CONNECT, UDP protocol, does not support BIND, supports username and password authentication.
|
||||
|
||||
*** If your VPS is Alibaba Cloud, Tencent Cloud is a VPS, if ifconfig can't see your public IP, you can only see the intranet IP, ***
|
||||
|
||||
*** Then you need to add the `-g VPS public network IP` parameter, the UDP function of the SOCKS5 proxy can work normally. ***
|
||||
|
||||
***The udp function of socks5 is turned off by default, and can be turned on by `--udp`. The default is a random port for handshake, and performance can be improved by fixing a port.
|
||||
Set by parameter `--udp-port 0`, `0` represents a free port is randomly selected, or you can manually specify a specific port. ***
|
||||
|
||||
### 5.1. Ordinary SOCKS5 Agent
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080"`
|
||||
|
||||
Listen port argument `-p` can be:
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000 and 9001 to 9999, 1002 total ports
|
||||
```
|
||||
|
||||
### 5.2. Ordinary secondary SOCKS5 agent
|
||||

|
||||
Use local port 8090, assuming the upstream SOCKS5 proxy is `22.22.22.22:8080`
|
||||
`proxy socks -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" `
|
||||
We can also specify the black and white list file of the website domain name, one domain name and one domain name, the matching rule is the rightmost match, for example: baidu.com, the match is *.*.baidu.com, the blacklist domain name domain name goes directly to the upstream agent, white The domain name of the list does not go to the upstream agent; if the domain name is in the blacklist and in the whitelist, the blacklist works.
|
||||
`proxy socks -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt`
|
||||
|
||||
### 5.3. SOCKS Level 2 Agent (Encryption)
|
||||

|
||||
Level 1 SOCKS proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Secondary SOCKS proxy (local Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS.
|
||||
|
||||
Secondary SOCKS proxy (local windows)
|
||||
`proxy.exe socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then set your windos system, the proxy that needs to go through the proxy Internet program is the socks5 mode, the address is: 127.0.0.1, the port is: 8080, the program can access the Internet through vps through the encrypted channel.
|
||||
|
||||
### 5.4. SOCKS Level 3 Agent (Encryption)
|
||||

|
||||
Level 1 SOCKS proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
Secondary SOCKS proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy socks -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 SOCKS proxy (local)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then accessing the local port 8080 is to access the proxy port 38080 on the first-level SOCKS proxy.
|
||||
|
||||
### 5.5. SOCKS proxy traffic is forced to go to the upper level SOCKS proxy
|
||||
By default, the proxy will intelligently determine whether a website domain name is inaccessible. If it is not accessible, it will go to the upstream SOCKS proxy. With --always, all SOCKS proxy traffic can be forced to go to the upper SOCKS proxy.
|
||||
`proxy socks --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
### 5.6. SOCKS via SSH relay
|
||||

|
||||
Description: The principle of ssh transfer is to use the forwarding function of ssh, that is, after you connect to ssh, you can access the target address through ssh proxy.
|
||||
Suppose there is: vps
|
||||
- IP is 2.2.2.2, ssh port is 22, ssh username is: user, ssh user password is: demo
|
||||
- The user's ssh private key name is user.key
|
||||
|
||||
#### *5.6.1 How to ssh username and password*
|
||||
Local SOCKS5 proxy port 28080, execute:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080"`
|
||||
#### *5.6.2 How to ssh username and key*
|
||||
Local SOCKS5 proxy port 28080, execute:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080"`
|
||||
|
||||
Then access the local port 28080 is to access the target address through the VPS.
|
||||
|
||||
### 5.7. Certification
|
||||
For the socks5 proxy protocol, we can perform username and password authentication. The authenticated username and password can be specified on the command line.
|
||||
`proxy socks -t tcp -p ":33080" -a "user1:pass1" -a "user2:pass2"`
|
||||
For multiple users, repeat the -a parameter.
|
||||
It can also be placed in a file in the format of a "username:password" and then specified with -F.
|
||||
`proxy socks -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
In addition, the socks5 agent also integrates external HTTP API authentication. We can specify an http url interface address with the --auth-url parameter.
|
||||
Then when there is a user connection, the proxy will request the url in GET mode, with the following three parameters. If the HTTP status code 204 is returned, the authentication is successful.
|
||||
In other cases, the authentication failed.
|
||||
For example:
|
||||
`proxy socks -t tcp -p ":33080" --auth-url "http://test.com/auth.php"`
|
||||
When the user connects, the proxy will request the url ("http://test.com/auth.php") in GET mode.
|
||||
Bring four parameters: user, pass, ip, local_ip:
|
||||
Http://test.com/auth.php?user={USER}&pass={PASS}&ip={IP}&local_ip={LOCAL_IP}
|
||||
User: username
|
||||
Pass: password
|
||||
Ip: User's IP, for example: 192.168.1.200
|
||||
Local_ip: IP of the server accessed by the user, for example: 3.3.3.3
|
||||
|
||||
If there is no -a or -F or --auth-url parameter, the authentication is turned off.
|
||||
|
||||
### 5.8.KCP protocol transmission
|
||||
The KCP protocol requires the --kcp-key parameter to set a password for encrypting and decrypting data.
|
||||
|
||||
Level 1 HTTP proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy socks -t kcp -p ":38080" --kcp-key mypassword`
|
||||
|
||||
Secondary HTTP proxy (local Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS, the data is transmitted through the kcp protocol.
|
||||
|
||||
notice:
|
||||
|
||||
When using the kcp protocol locally, you need to specify the vps public network IP with -g, and the UDP function of socks5 is fully used. At this time, -g is the IP address in the UDP address returned to the client.
|
||||
|
||||
### 5.9. Custom DNS
|
||||
--dns-address and --dns-ttl parameters, used to specify the dns (--dns-address) used by the proxy to access the domain name.
|
||||
And the analysis result cache time (--dns-ttl) seconds, to avoid system dns interference to the proxy, in addition to the cache function can also reduce the dns resolution time to improve access speed.
|
||||
For example:
|
||||
`proxy socks -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 5.10 Custom Encryption
|
||||
The proxy's socks proxy can encrypt tcp data through tls standard encryption and kcp protocol on top of tcp. In addition, it supports custom encryption after tls and kcp, which means that custom encryption and tls|kcp can be used together. The internal use of AES256 encryption, you only need to define a password when you use it.
|
||||
Encryption is divided into two parts, one is whether the local (-z) encryption and decryption, and the other is whether the transmission with the upstream (-Z) is encrypted or decrypted.
|
||||
|
||||
Custom encryption requires both sides to be proxy.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Secondary instance
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
### 5.11 Compressed transmission
|
||||
The proxy's socks proxy can encrypt tcp data through custom encryption and tls standard encryption and kcp protocol on top of tcp. It can also be used before custom encryption.
|
||||
Compress the data, that is, the compression function and the custom encryption and tls|kcp can be used in combination, and the compression is divided into two parts.
|
||||
Part of it is local (-m) compression transmission, and part is whether the transmission with the upstream (-M) is compressed.
|
||||
|
||||
Compression requires both sides to be proxy, and compression also protects (encrypts) data to some extent.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
### 5.12 Load Balancing
|
||||
|
||||
The SOCKS proxy supports the upper-level load balancing, and multiple upstream repeat-P parameters can be used.
|
||||
|
||||
`proxy socks --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.1 Setting the retry interval and timeout time
|
||||
|
||||
`proxy socks --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.2 Setting weights
|
||||
|
||||
`proxy socks --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.3 Use the target address to select the upstream
|
||||
|
||||
`proxy socks --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.13 Speed limit
|
||||
|
||||
The speed limit is 100K, which can be specified by the `-l` parameter, for example: 100K 2000K 1M . 0 means no limit.
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 5.14 Specifying Outgoing IP
|
||||
|
||||
The `--bind-listen` parameter can be used to open the client connection with the portal IP, and use the portal IP as the outgoing IP to access the target website. If the ingress IP is an intranet IP, the egress IP does not use the ingress IP.
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 --bind-listen`
|
||||
|
||||
### 5.15 Cascade Certification
|
||||
|
||||
SOCKS5 supports cascading authentication, and -A can set upstream authentication information.
|
||||
|
||||
upstream:
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -a user:pass`
|
||||
|
||||
local:
|
||||
|
||||
`proxy socks -T tcp -P 2.2.2.2:33080 -A user:pass -t tcp -p :33080`
|
||||
|
||||
### 5.16 Certificate parameters use base64 data
|
||||
|
||||
By default, the -C, -K parameter is the path to the crt certificate and the key file.
|
||||
|
||||
If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
|
||||
|
||||
### 5.17 Intelligent mode
|
||||
Intelligent mode setting, can be one of intelligent|direct|parent.
|
||||
The default is: intelligent.
|
||||
The meaning of each value is as follows:
|
||||
`--intelligent=direct`, the targets in the blocked are not directly connected.
|
||||
`--intelligent=parent`, the target that is not in the direct is going to the higher level.
|
||||
`--intelligent=intelligent`, blocked and direct have no targets, intelligently determine whether to use the upstream access target.
|
||||
|
||||
### 5.18 Fixed UDP PORT
|
||||
|
||||
By default, the port number of the UDP function of socks5, the proxy is installed in the `rfc1982 draft` request, which is randomly specified during the protocol handshake process and does not need to be specified in advance.
|
||||
|
||||
However, in some cases, you need to fix the UDP function port. You can use the parameter `--udp-port port number` to fix the port number of the UDP function. For example:
|
||||
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080" --udp-port 38080`
|
||||
|
||||
### 5.19 Help
|
||||
`proxy help socks`
|
||||
|
||||
## 6.SPS Protocol Convert
|
||||
|
||||
### 6.1 Function introduction
|
||||
The proxy protocol conversion uses the sps subcommand. The sps itself does not provide the proxy function. It only accepts the proxy request to "convert and forward" to the existing http(s) proxy or the socks5 proxy or ss proxy; the sps can put the existing http(s) proxy or socks5 proxy or ss proxy is converted to a port that supports both http(s) and socks5 and ss proxies, and the http(s) proxy supports forward proxy and reverse proxy (SNI), converted SOCKS5 proxy, UDP function is still supported when the upper level is SOCKS5 or SS; in addition, for the existing http(s) proxy or socks5 proxy, three modes of tls, tcp, and kcp are supported, and chain connection is supported, that is, multiple sps node levels can be supported. The connection builds an encrypted channel.
|
||||
|
||||
The encryption methods supported by the `ss` function are: aes-128-cfb, aes-128-ctr, aes-128-gcm, aes-192-cfb, aes-192-ctr, aes-192-gcm, aes-256- Cfb , aes-256-ctr , aes-256-gcm , bf-cfb , cast5-cfb , chacha20 , chacha20-ietf , chacha20-ietf-poly1305 , des-cfb , rc4-md5 , rc4-md5-6 , salsa20 , Xchacha20
|
||||
|
||||
Listen port argument `-p` can be:
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000 and 9001 to 9999, 1002 total ports
|
||||
```
|
||||
|
||||
notice:
|
||||
|
||||
When using the kcp protocol locally, you need to specify the vps public network IP with -g, and the UDP function of socks5 is fully used. At this time, -g is the IP address in the UDP address returned to the client.
|
||||
|
||||
The udp function of ss is turned off by default and can be turned on by `--ssudp`. The udp function of socks5 is turned off by default and can be turned on by `--udp`, The default is a random port for handshake, and performance can be improved by fixing a port.
|
||||
Set by parameter `--udp-port 0`, `0` represents a free port is randomly selected, or you can manually specify a specific port.
|
||||
|
||||
### 6.2 HTTP(S) to HTTP(S)+SOCKS5+SS
|
||||
Suppose there is already a normal http(s) proxy: 127.0.0.1:8080. Now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss encryption: Aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a tls http(s) proxy: 127.0.0.1:8080. Now we turn it into a normal proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, and tls requires a certificate file. , ss encryption: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S http -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a kcp http(s) proxy (password is: demo123): 127.0.0.1:8080, now we turn it into a normal proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss encryption: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S http -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.3 SOCKS5 to HTTP(S)+SOCKS5+SS
|
||||
Suppose there is already a normal socks5 proxy: 127.0.0.1:8080, now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss encryption: aes-192 -cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S socks -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a tls socks5 proxy: 127.0.0.1:8080, now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, tls requires certificate file, ss encryption Mode: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S socks -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a kcp socks5 proxy (password: demo123): 127.0.0.1:8080, now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss Encryption method: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S socks -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.4 SS to HTTP(S)+SOCKS5+SS
|
||||
SPS upstream and local support ss protocol, the upstream can be SPS or standard ss service.
|
||||
SPS locally provides HTTP(S)\SOCKS5\SPS three defaults. When the upstream is SOCKS5, the converted SOCKS5 and SS support UDP.
|
||||
Suppose there is already a normal SS or SPS proxy (ss is enabled, encryption: aes-256-cfb, password: demo): 127.0.0.1:8080, now we turn it to support both http(s) and socks5 and The ordinary proxy of ss, the converted local port is 18080, the converted ss encryption mode: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S ss -H aes-256-cfb -J pass -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`.
|
||||
|
||||
### 6.5 Chained connection
|
||||

|
||||
The above mentioned multiple sps nodes can be connected to build encrypted channels in a hierarchical connection, assuming the following vps and the home PC.
|
||||
Vps01:2.2.2.2
|
||||
Vps02:3.3.3.3
|
||||
Now we want to use pc and vps01 and vps02 to build an encrypted channel. This example uses tls encryption or kcp. Accessing local 18080 port on the PC is to access the local 8080 port of vps01.
|
||||
First on vps01 (2.2.2.2) we run a locally accessible http(s) proxy and execute:
|
||||
`proxy http -t tcp -p 127.0.0.1:8080`
|
||||
|
||||
Then run a sps node on vps01 (2.2.2.2) and execute:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tls -p :8081 -C proxy.crt -K proxy.key`
|
||||
|
||||
Then run a sps node on vps02 (3.3.3.3) and execute:
|
||||
`proxy sps -S http -T tls -P 2.2.2.2:8081 -t tls -p :8082 -C proxy.crt -K proxy.key`
|
||||
|
||||
Then run a sps node on the pc and execute:
|
||||
`proxy sps -S http -T tls -P 3.3.3.3:8082 -t tcp -p :18080 -C proxy.crt -K proxy.key`
|
||||
|
||||
carry out.
|
||||
|
||||
### 6.6 Authentication
|
||||
Sps supports http(s)\socks5 proxy authentication, which can be cascaded and has four important pieces of information:
|
||||
1: The user sends the authentication information `user-auth`.
|
||||
2: Set the local authentication information `local-auth`.
|
||||
3: Set the connection authentication information 'parent-auth` used by the upstream.
|
||||
4: The authentication information `auth-info-to-parent` that is finally sent to the upstream.
|
||||
Their situation is as follows:
|
||||
|
||||
User-auth | local-auth | parent-auth | auth-info-to-paren
|
||||
| ------ | ------ | ------ | ------
|
||||
| Yes / No | Yes | Yes | From parent-auth
|
||||
| Yes / No | No | Yes | From parent-auth
|
||||
| Yes / No | Yes | No | No
|
||||
| No | No | No | No
|
||||
| Yes | No | No | From user-auth
|
||||
|
||||
For the sps proxy we can perform username and password authentication. The authenticated username and password can be specified on the command line.
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0:0: "`
|
||||
For multiple users, repeat the -a parameter.
|
||||
Can also be placed in a file, the format is one line a `username: password: number of connections: rate: upstream`, and then specified with -F.
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
If the upstream has authentication, the lower level can set the authentication information with the -A parameter, for example:
|
||||
upstream: `proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0: 0:"`
|
||||
Subordinate: `proxy sps -S http -T tcp -P 127.0.0.1:8080 -A "user1:pass1" -t tcp -p ":33080" `
|
||||
|
||||
For more details on certification, please refer to `9.API Certification` and `10.Local Certification`
|
||||
|
||||
### 6.7 Multiple Upstream
|
||||
|
||||
If there are multiple upstreams, they can be specified by multiple -Ps.
|
||||
|
||||
such as:
|
||||
|
||||
`proxy sps -P http://127.0.0.1:3100 -P socks5://127.0.0.1:3200`
|
||||
|
||||
The complete format of `-P` is as follows:
|
||||
|
||||
`protocol://a:[email protected]:33080#1`
|
||||
|
||||
Each section is explained below:
|
||||
|
||||
`protocol://` is the protocol type, possible types and contains the following:
|
||||
|
||||
```text
|
||||
Http is equivalent to -S http -T tcp
|
||||
Https is equivalent to -S http -T tls --parent-tls-single , which is http(s) proxy over TLS
|
||||
Https2 is equivalent to -S http -T tls
|
||||
Socks5 is equivalent to -S socks -T tcp
|
||||
Socks5s is equivalent to -S socks -T tls --parent-tls-single , which is socks over TLS
|
||||
Socks5s2 is equivalent to -S socks -T tls
|
||||
Ss is equivalent to -S ss -T tcp
|
||||
Httpws is equivalent to -S http -T ws
|
||||
Httpwss is equivalent to -S http -T wss
|
||||
Socks5ws is equivalent to -S socks -T ws
|
||||
Socks5wss is equivalent to -S socks -T wss
|
||||
```
|
||||
|
||||
`a:b` is the username and password of the proxy authentication. If it is ss, `a` is the encryption method, `b` is the password, and no username password can be left blank, for example: `http://2.2.2.2:33080` If the username and password are protected, special symbols can be encoded using urlencode.
|
||||
|
||||
`2.2.2.2:33080` is the upstream address, the format is: `IP (or domain name): port `, if the underlying is ws/wss protocol can also bring the path, such as: `2.2.2.2: 33080/ws`;
|
||||
You can also set the `encryption method` and `password` of `ws\wss` by appending the query parameters `m` and `k`, for example: `2.2.2.2:33080/ws?m=aes-192-cfb&k=password`
|
||||
|
||||
`#1` When multiple upper-level load balancing is a weighting strategy, the weights are rarely used.
|
||||
|
||||
### 6.8 Custom Encryption
|
||||
The proxy sps proxy can encrypt tcp data through tls standard encryption and kcp protocol on top of tcp, in addition to support after tls and kcp
|
||||
Custom encryption, that is, custom encryption and tls|kcp can be used in combination, internally using AES256 encryption, only need to define it when using
|
||||
A password can be used, the encryption is divided into two parts, one part is whether the local (-z) encryption and decryption, and the part is the encryption and decryption with the upstream (-Z) transmission.
|
||||
|
||||
Custom encryption requires both sides to be proxy.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Suppose there is already an http(s) proxy: `6.6.6.6:6666`
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
### 6.9 Compressed transmission
|
||||
The proxy sps proxy can encrypt tcp data through custom encryption and tls standard encryption and kcp protocol on top of tcp. It can also be used before custom encryption.
|
||||
Compress the data, that is, the compression function and the custom encryption and tls|kcp can be used in combination, and the compression is divided into two parts.
|
||||
Part of it is local (-m) compression transmission, and part is whether the transmission with the upstream (-M) is compressed.
|
||||
|
||||
Compression requires both sides to be proxy, and compression also protects (encrypts) data to some extent.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
### 6.10 Disabling the protocol
|
||||
By default, SPS supports http(s) and socks5 two proxy protocols. We can disable a protocol by parameter.
|
||||
For example:
|
||||
1. Disable the HTTP(S) proxy function to retain only the SOCKS5 proxy function, parameter: `--disable-http`.
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-http`
|
||||
|
||||
1. Disable the SOCKS5 proxy function to retain only the HTTP(S) proxy function, parameter: `--disable-socks`.
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-socks`
|
||||
|
||||
### 6.11 Speed limit
|
||||
|
||||
Suppose there is a SOCKS5 upstream:
|
||||
|
||||
`proxy socks -p 2.2.2.2:33080 -z password -t tcp`
|
||||
|
||||
SPS lower level, speed limit 100K
|
||||
|
||||
`proxy sps -S socks -P 2.2.2.2:33080 -T tcp -Z password -l 100K -t tcp -p :33080`
|
||||
|
||||
It can be specified by the `-l` parameter, for example: 100K 2000K 1M . 0 means no limit.
|
||||
|
||||
### 6.12 Specifying Outgoing IP
|
||||
|
||||
The `--bind-listen` parameter can be used to open the client connection with the portal IP, and use the portal IP as the outgoing IP to access the target website. If the ingress IP is an intranet IP, the egress IP does not use the ingress IP.
|
||||
|
||||
`proxy sps -S socks -P 2.2.2.2:33080 -T tcp -Z password -l 100K -t tcp --bind-listen -p :33080`
|
||||
|
||||
### 6.13 Certificate parameters use base64 data
|
||||
|
||||
By default, the -C, -K parameter is the path to the crt certificate and the key file.
|
||||
|
||||
If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
|
||||
### 6.14 Independent Service
|
||||
A sps port can complete the full-featured proxy `http\socks\ss` function.
|
||||
The following command is to open the http(s)\ss\socks service with one click, and enable the udp of socks5 and the udp of ss at the same time.
|
||||
`proxy sps -p: 33080 --ssudp --udp --udp-port 0`
|
||||
|
||||
### 6.15 Target Redirection
|
||||
The https(s)\socks5\ss proxy function provided by the sps function, the client connects to the specified "target" through the sps proxy. This "target" is generally a website or an arbitrary tcp address.
|
||||
The website "target" is generally foo.com: 80, foo.com: 443, sps supports the use of the --rewrite parameter to specify a "target" redirection rule file, redirect the target, the client is non-perceived,
|
||||
For example, if you redirect to "target": demo.com:80 to 192.168.0.12:80, then the client visits the website demo.com, in fact, the website service provided by 192.168.0.12.
|
||||
Example of a "target" redirection rule file:
|
||||
|
||||
```text
|
||||
# example
|
||||
Www.a.com:80 10.0.0.2:8080
|
||||
**.b.com:80 10.0.0.2:80
|
||||
192.168.0.11:80 10.0.0.2:8080
|
||||
```
|
||||
|
||||
When sps is an independent service, an additional local socks5 service will be opened to occupy a random port. Now the parameter `--self-port` can be manually specified when needed. The default is 0 to use random.
|
||||
|
||||
### 6.16 Fixed UDP PORT
|
||||
|
||||
By default, the port number of the UDP function of ss's socks5 is specified by the `rfc1982 draft`. It is randomly specified during the protocol handshake process and does not need to be specified in advance.
|
||||
|
||||
However, in some cases, you need to fix the UDP function port. You can fix the port number of the UDP function by the parameter `--udp-port port_number`, for example:
|
||||
|
||||
`proxy sps -t tcp -p "0.0.0.0:38080" --udp-port 38081`
|
||||
|
||||
It should be noted that the ss function of sps also has UDP function, and the UDP port of ss is the same as the tcp port, so avoid the conflict between the UDP port of socks5 and the UDP port of ss.
|
||||
|
||||
To specify a port that is different from the tcp port.
|
||||
|
||||
### 6.17 iptables 透明代理
|
||||
The sps mode supports the iptables transparent forwarding support of the Linux system, which is commonly referred to as the iptables transparent proxy. If a iptables transparent proxy is performed on the gateway device, the device that is connected through the gateway can realize a non-aware proxy.
|
||||
|
||||
Example start command:
|
||||
|
||||
`proxy sps --redir -p :8888 -P httpws: //1.1.1.1:33080`
|
||||
|
||||
Here it is assumed that there is an http superior proxy 1.1.1.1:33080, which uses ws to transmit data.
|
||||
|
||||
Then add iptables rules, here are the reference rules:
|
||||
|
||||
```shell
|
||||
#upstream proxy server IP address:
|
||||
proxy_server_ip = 1.1.1.1
|
||||
|
||||
#Router running proxy listening port:
|
||||
proxy_local_port = 33080
|
||||
|
||||
#There is no need to modify the following
|
||||
#create a new chain named PROXY
|
||||
iptables -t nat -N PROXY
|
||||
|
||||
#Ignore your PROXY server's addresses
|
||||
#It's very IMPORTANT, just be careful。
|
||||
|
||||
iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
#Ignore LANs IP address
|
||||
iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
#Anything to port 80 443 should be redirected to PROXY's local port
|
||||
iptables -t nat -A PROXY -p tcp -j REDIRECT --to-ports $proxy_local_port
|
||||
#Apply the rules to nat client
|
||||
iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
#Apply the rules to localhost
|
||||
iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
|
||||
- Clear the entire chain iptables -F chain name such as iptables -t nat -F PROXY
|
||||
- Delete the specified user-defined chain iptables -X chain name e.g. iptables -t nat -X PROXY
|
||||
- Delete rule from selected chain iptables -D chain name rule details e.g. iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 6.18 Help
|
||||
|
||||
`proxy help sps`
|
||||
|
||||
## 7.KCP Configuration
|
||||
|
||||
### 7.1 Configuration Introduction
|
||||
Many functions of the proxy support the kcp protocol. Any function that uses the kcp protocol supports the configuration parameters described here.
|
||||
Therefore, the KCP configuration parameters are introduced here.
|
||||
|
||||
### 7.2 Detailed configuration
|
||||
There are a total of 17 KCP configuration parameters, you can not set them, they have default values, if for the best effect,
|
||||
You need to configure the parameters according to your own network conditions. Because the kcp configuration is complex, it requires a certain network basics.
|
||||
If you want to get more detailed configuration and explanation of kcp parameters, please search for yourself. The command line name for each parameter, along with the default values and simple function descriptions are as follows:
|
||||
```
|
||||
--kcp-key="secrect" pre-shared secret between client and server
|
||||
--kcp-method="aes" encrypt/decrypt method, can be: aes, aes-128, aes-192, salsa20, blowfish,
|
||||
Twofish, cast5, 3des, tea, xtea, xor, sm4, none
|
||||
--kcp-mode="fast" profiles: fast3, fast2, fast, normal, manual
|
||||
--kcp-mtu=1350 set maximum transmission unit for UDP packets
|
||||
--kcp-sndwnd=1024 set send window size(num of packets)
|
||||
--kcp-rcvwnd=1024 set receive window size(num of packets)
|
||||
--kcp-ds=10 set reed-solomon erasure coding - datashard
|
||||
--kcp-ps=3 set reed-solomon erasure coding - parityshard
|
||||
--kcp-dscp=0 set DSCP(6bit)
|
||||
--kcp-nocomp disable compression
|
||||
--kcp-acknodelay be carefull! flush ack immediately when a packet is received
|
||||
--kcp-nodelay=0 be carefull!
|
||||
--kcp-interval=50 be carefull!
|
||||
--kcp-resend=0 be carefull!
|
||||
--kcp-nc=0 be carefull! no congestion
|
||||
--kcp-sockbuf=4194304 be carefull!
|
||||
--kcp-keepalive=10 be carefull!
|
||||
```
|
||||
Tip:
|
||||
Parameters: -- four fast3, fast2, fast, normal modes in kcp-mode,
|
||||
Equivalent to setting the following four parameters:
|
||||
Normal:`--nodelay=0 --interval=40 --resend=2 --nc=1`
|
||||
Fast :`--nodelay=0 --interval=30 --resend=2 --nc=1`
|
||||
Fast2:`--nodelay=1 --interval=20 --resend=2 --nc=1`
|
||||
Fast3:`--nodelay=1 --interval=10 --resend=2 --nc=1`
|
||||
|
||||
## 8. Security DNS
|
||||
|
||||
### 8.1 Introduction
|
||||
DNS is known as the service provided by UDP port 53, but with the development of the network, some well-known DNS servers also support TCP mode dns query, such as Google's 8.8.8.8, the DNS anti-pollution server principle of the proxy is to start a proxy DNS proxy locally. Server, which uses TCP to perform dns query through the upstream agent. If it communicates with the upstream agent, it can perform secure and pollution-free DNS resolution. It also supports independent services, concurrent parsing, and enhanced enhanced hosts file function to support flexible concurrent parsing and forwarding.
|
||||
|
||||
Dns resolution order:
|
||||
1. Use the parameter --hosts to parse.
|
||||
2. If the domain name to be resolved is not found in 1, it is parsed using the parameter --forward rule.
|
||||
3. The domain name to be resolved is not found in 1 and 2, and the default --default parsing is used. The default default behavior parameter values are three: proxy, direct, and system.
|
||||
The three parameter values are explained as follows:
|
||||
Proxy: The domain name is resolved by the dns server specified by the -q parameter.
|
||||
Direct: Connect to the dns server specified by the -q parameter to resolve the domain name through the local network.
|
||||
System: resolves the domain name through the system dns.
|
||||
|
||||
Tip:
|
||||
The host file format specified by the --hosts parameter is the same as the system hosts file, and the domain name supports wildcards. You can refer to the hosts file.
|
||||
The parsing forwarding rule file specified by the --forward parameter can be referenced to the resolve.rules file. The domain name supports wildcards. It supports multiple dns servers for each domain name to be parsed concurrently. Whoever resolves the fastest resolution will use the resolution result.
|
||||
The -q parameter can specify multiple remote dns servers to perform concurrent parsing. Whoever resolves the fastest parsing success, the default is: 1.1.1.1, 8.8.8.8, 9.9.9.9, multiple comma-separated,
|
||||
For example, you can also bring ports: 1.1.1.1, 8.8.8.8#53, 9.9.9.9
|
||||
|
||||
If you are a standalone service, you don't need a upstream:
|
||||
Can perform:
|
||||
`proxy dns --default system -p :5353`
|
||||
Or
|
||||
`proxy dns --default direct -p :5353`
|
||||
|
||||
### 8.2 Example of use
|
||||
|
||||
#### 8.2.1 Normal HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
Local execution:
|
||||
`proxy dns -S http -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides DNS resolution.
|
||||
|
||||
#### 8.2.2 Ordinary SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
Local execution:
|
||||
`proxy dns -S socks -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides DNS resolution.
|
||||
|
||||
#### 8.2.3 TLS encrypted HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy http -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S http -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.4 TLS-encrypted SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy socks -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S socks -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.5 KCP encrypted HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy http -t kcp -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S http -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.6 KCP encrypted SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy socks -t kcp -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S socks -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.7 Custom encrypted HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy http -t tcp -p :33080 -z password`
|
||||
Local execution:
|
||||
`proxy dns -S http -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.8 Custom encrypted SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy socks -t kcp -p :33080 -z password`
|
||||
Local execution:
|
||||
`proxy dns -S socks -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
## 9.API Authentication
|
||||
|
||||
The proxy's http(s)/socks5/sps proxy function supports user-to-agent access via the API.
|
||||
|
||||
### What can I do through the API?
|
||||
|
||||
- User dimension, which controls the single connection rate and controls the maximum number of connections.
|
||||
- IP dimension, which controls the single connection rate and controls the maximum number of connections.
|
||||
- Dynamic upstream, can dynamically obtain its upstream from the API according to the user or client IP, and support http(s)/socks5/ss upstream.
|
||||
- Authenticate every connection, regardless of whether client authentication is required.
|
||||
- Cache authentication results, time can be set to reduce API pressure.
|
||||
|
||||
#### Specific use
|
||||
The proxy's http(s)/socks5/sps proxy API function is controlled by three parameters: `--auth-url` and `--auth-nouser` and `--auth-cache`.
|
||||
The parameter `--auth-url` is the HTTP API interface address. When the client connects, the proxy will request the url in GET mode, with the following parameters. If the HTTP status code 204 is returned, the authentication is successful. In other cases, the authentication fails.
|
||||
|
||||
An example of a complete request API:
|
||||
`http://test.com/auth.php?user=a&pass=b&client_addr=127.0.0.1:49892&local_addr=127.0.0.1:8100&target=http%3A%2F%2Fwww.baidu.com&service=http&sps=0`
|
||||
|
||||
#### Parameter Description
|
||||
`user and pass` When the proxy turns on authentication, here is the username and password provided by the client.
|
||||
`client_addr` The address used by the client to access the proxy, format IP: port.
|
||||
`local_addr` The proxy address accessed by the client, format IP: port.
|
||||
`service` Proxy type, divided into: http, socks.
|
||||
Whether the `sps` proxy is provided by sps, 1: yes, 0: no.
|
||||
`target` The target to be accessed by the client. If it is an http(s) proxy, the target is the specific url accessed; if it is a socks5 proxy, the target is empty.
|
||||
|
||||
#### Example
|
||||
Suppose --auth-url http://127.0.0.1:333/auth.php points to a php interface address.
|
||||
The contents of auth.php are as follows:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#all users and password
|
||||
$alluser=[
|
||||
"user1"=>"pass1",
|
||||
"user2"=>"pass2",
|
||||
"user3"=>"pass3",
|
||||
"user4"=>"pass4",
|
||||
];
|
||||
$proxy_ip=$_GET['local_addr'];
|
||||
$user_ip=$_GET['client_addr'];
|
||||
$service=$_GET['service'];
|
||||
$is_sps=$_GET['sps']=='1';
|
||||
$user=$_GET['user'];
|
||||
$pass=$_GET['pass'];
|
||||
$target=$_GET['target'];
|
||||
|
||||
//business checking
|
||||
//....
|
||||
$ok=false;
|
||||
foreach ($alluser as $dbuser => $dbpass) {
|
||||
if ($user==$dbuser&&$pass==$dbpass){
|
||||
$ok=true;
|
||||
break;
|
||||
}
|
||||
}
|
||||
|
||||
//set the authentication result
|
||||
if($ok){
|
||||
header("userconns:1000");
|
||||
header("ipconns:2000");
|
||||
header("userrate:3000");
|
||||
header("iprate:8000");
|
||||
header("UPSTREAM:http://127.0.0.1:3500?parent-type=tcp");
|
||||
header("HTTP/1.1 204 No Content");
|
||||
}
|
||||
```
|
||||
|
||||
#### Explanation
|
||||
Userconns: The maximum number of connections for the user, not limited to 0 or not set this header.
|
||||
Ipcons: The maximum number of connections for the user IP, not limited to 0 or not set this header.
|
||||
Userrate: User's single TCP connection rate limit, in bytes/second, is not limited to 0 or does not set this header.
|
||||
Iprate: The single TCP connection rate limit of the user IP, in bytes/second, not limited to 0 or not set this header.
|
||||
Upstream: The upstream used, not empty, or not set this header.
|
||||
|
||||
#### Tips
|
||||
1. By default, `--auth-url` is required to provide the user name and password. If you do not need the client to provide the username and password, and authenticate, you can add `--auth-nouser`. The visit will still access the authentication address `--auth-url` for authentication. Only the $user authentication username and the $pass authentication password received in the php interface are empty when client didn't send username and password.
|
||||
2. Connection limit priority: User authentication file limit - "File ip.limit limit -" API user limit - "API IP limit -" command line global connection limit.
|
||||
3. Rate Limit Priority: User Authentication File Rate Limit - "File ip.limit Rate Limit -" API User Rate Limit - "API IP Rate Limit - "Command Line Global Rate Limit.
|
||||
3. The upstream obtains the priority: the upstream of the user authentication file - the file ip.limit upstream-"API upstream-" command line specifies the upstream.
|
||||
4.`--auth-cache` authentication cache, cache the authentication result for a certain period of time, improve performance, reduce the pressure on the authentication interface, --auth-cache unit seconds, default 0, set 0 to close the cache.
|
||||
|
||||
#### upstream detailed description
|
||||
|
||||
1. When the parameter `sps` is 0.
|
||||
When the service is http, upstream only supports http(s) proxy, and does not support authentication. If authentication is required, it can be replaced by sps. Format:
|
||||
`http://127.0.0.1:3100?argk=argv`
|
||||
When the service is a socks, the upstream only supports the socks5 proxy. The format is:
|
||||
`socks5://127.0.0.1:3100?argk=argv`
|
||||
|
||||
Explanation: `http://`,`socks5://` is fixed, `127.0.0.1:3100` is the address of the upstream
|
||||
|
||||
2. When `sps` is 1.
|
||||
Upstream supports socks5, http(s) proxy, support authentication, format: `protocol://a:b@2.2.2.2:33080?argk=argv`, please refer to SPS chapter for details, **multiple upstreams** , the description of the `-P` parameter.
|
||||
3. Parameters, `?` followed by `argk=argv` are parameters: parameter name = parameter value, multiple parameters are connected with `&`.
|
||||
All the supported parameters are as follows, and the meaning of the command line with the same name is the same.
|
||||
1. parent-type : upper-level transport type, support tcp, tls, ws, wss
|
||||
2. parent-ws-method: The encryption method of the upper-level ws transmission type, the supported value is the same as the value range supported by the command line.
|
||||
3. parent-ws-password: The upper-level ws transmission type encryption password, the alphanumeric password
|
||||
4. parent-tls-single : Whether the upper-level tls transport type is a one-way tls, which can be: true | false
|
||||
5. timeout : timeout for establishing tcp connection, number, in milliseconds
|
||||
6. ca : The base64-encoded string of the upper-level tls transport type ca certificate file.
|
||||
7. cert : The base64 encoded string of the higher level tls transport type certificate file.
|
||||
8. key : The base64 encoded string of the higher-level tls transport type certificate key file.
|
||||
|
||||
### Traffic report / Traffic limit / Traffic statistics
|
||||
|
||||
The proxy's http (s) / socks5 / sps / tcp / udp proxy function supports traffic reporting. You can set an http interface address through the parameter `--traffic-url`.
|
||||
The proxy will report the traffic used for this connection to this address.Specifically, the proxy sends an HTTP to GET request to the HTTP URL address set by `--traffic-url`.
|
||||
There are two reporting modes, which can be specified by the `--traffic-mode` parameter. It can be reported in the normal mode or in the fast mode.
|
||||
|
||||
1. Report in `normal` normal mode
|
||||
When the connection is released, the proxy will report the traffic used for this connection to this `--traffic-url` address.
|
||||
|
||||
2. Report in `fast` mode
|
||||
For each connection that has been established, the proxy will `timely` report the traffic generated by this connection to this` --traffic-url` address.
|
||||
`Timing` defaults to 5 seconds, and you can modify` Timing` to the appropriate number of seconds via the parameter `--traffic-interval`.
|
||||
|
||||
The traffic reporting function combined with the above API authentication function can control the user's traffic usage in real time. The traffic is reported to the interface. The interface writes the traffic data to the database, and then the authentication API queries the database to determine the traffic usage and determine whether the user can be successfully authenticated.
|
||||
|
||||
The following is a complete URL request example:
|
||||
|
||||
`http://127.0.0.1:33088/user/traffic?bytes=337&client_addr=127.0.0.1%3A51035&id=http&server_addr =127.0.0.1%3A33088&target_addr=myip.ipip.net%3A80&username=a`
|
||||
|
||||
Request parameter description:
|
||||
id: service id flag.
|
||||
server_addr: proxies's address requested by the client, format: IP: port.
|
||||
client_addr: client address, format: IP: port.
|
||||
target_addr: target address, format: "IP: port", when tcp / udp proxy, this is empty.
|
||||
User name: proxy authentication user name, this is empty when tcp / udp proxy.
|
||||
bytes: the number of traffic bytes used by the user.
|
||||
|
||||
#### Tips
|
||||
|
||||
The `--traffic-url` URL must response the HTTP status code` 204`. Only when the traffic is reported will the report be considered successful, and if it response other status codes, it will be considered that the reported traffic failed, and the log will be output.
|
||||
|
||||
#### traffic flow
|
||||
|
||||

|
||||
|
||||
|
||||
### Disconnect the user's connection
|
||||
|
||||
The proxy's http (s) / socks5 / sps proxy function supports a control interface, which can be specified by the parameter --control-url http interface address,
|
||||
Then the proxy will interval send all the usernames or client IPs currently connected to the proxy to this URL. Specifically, the proxy sends an HTTP to POST request to the HTTP URL address set by --control-url.
|
||||
|
||||
`interval` defaults to 30 seconds, this value can be modified via the --control-sleep parameter.
|
||||
|
||||
When the user expires, or the user's traffic has been used up, the authentication API can only control the user cannot create a new connection, but the connection with the proxy has been established and the connection cannot be immediately disconnected.
|
||||
Then this problem can be solved through the control interface. The control interface will return the content through the control interface in the slowest `interval` time, and the end is invalid when the user establishes the connection.
|
||||
|
||||
#### Request Description
|
||||
|
||||
The proxy sends an HTTP POST request to the control interface URL. There are two fields in the form data: user and ip.
|
||||
|
||||
user: the user name currently connected to the proxy, multiple are separated by commas, for example: user1, user2
|
||||
|
||||
ip: The IP address of the client currently connected to the proxy, multiple are separated by commas, for example: 1.1.1.1, 2.2.2.2
|
||||
|
||||
#### Response Data Description
|
||||
|
||||
The data returned by the control interface is invalid user and IP, the format is a json object data, there are two fields user and ip.
|
||||
|
||||
For example: {"user": "a, b", "ip": ""}
|
||||
|
||||
user: the user name currently connected to the proxy, multiple are separated by commas, not left blank, for example: user1, user2
|
||||
|
||||
ip: The ip address of the client currently connected to the proxy. Multiple are separated by commas and not left blank.
|
||||
|
||||
The connection between the returned user and ip will be disconnected by proxy.
|
||||
|
||||
#### Example
|
||||
Suppose --control-url `http://127.0.0.1:33088/user/control.php` points to a PHP interface address.
|
||||
The content of control.php is as follows:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#revcieve proxy post data
|
||||
$userArr=explode(",",$_POST['user']);
|
||||
$ipArr=$_GET['ip'];
|
||||
|
||||
//invalid users array
|
||||
$badUsers=[];
|
||||
|
||||
foreach ($userArr as $user) {
|
||||
//logic business, push invalid user into $badUsers
|
||||
$badUsers[]=$user;
|
||||
}
|
||||
$data=["user"=>implode(","$badUsers),"ip"=>""];
|
||||
|
||||
echo json_encode($data);
|
||||
```
|
||||
|
||||
|
||||
## 10. Authentication
|
||||
|
||||
The proxy http(s)/socks5/sps proxy function supports the user to access the proxy pair through the configuration file, and supports the http(s) proxy ``Proxy Basic proxy authentication` and the socks5 proxy authentication.
|
||||
|
||||
### start using
|
||||
The proxy's http(s)/socks5/sps proxy function can pass
|
||||
`--auth-file`, `--max-conns`, `--ip-limit`, `--rate-limit`, `-a` These five parameters control.
|
||||
|
||||
#### Detailed explanation of parameters
|
||||
|
||||
##### `--auth-file`
|
||||
The authenticated user name and password file. This parameter specifies a file, one line per rule, in the format: "username: password: number of connections: rate: upstream".
|
||||
`Connection number` is the maximum number of connections for the user. The 'rate' is the maximum speed of each tcp connection of the user. The unit is: byte/second. The upper level is the upper level used by the user.
|
||||
Not only can the authenticated user be set by `--auth-file`, but also the `-a` parameter can be set directly. Multiple users can repeat multiple `-a` parameters.
|
||||
For example: `proxy http -a a:b:0:0: -a c:d:0:0:`
|
||||
|
||||
Example explanation:
|
||||
For example: `user:pass:100:10240:http://192.168.1.1:3100`
|
||||
`user` is the authentication username
|
||||
`pass` is the authentication user password (cannot contain a colon:)
|
||||
`100` is the maximum number of connections for this user, not limited to write 0
|
||||
`10240` is the rate limit of this user's single tcp connection, the unit is: byte / sec, no limit write 0
|
||||
`http://192.168.1.1:3100` is the upstream used by this user, no space is left blank
|
||||
|
||||
##### `--max-conns`
|
||||
Limit the maximum number of global connections for the proxy service, a number, 0 is unrestricted, default is 0.
|
||||
|
||||
##### `--ip-limit`
|
||||
Controls the number of connections and connection rate of the client IP. This parameter specifies a file, one rule per line, and the beginning of # is gaze.
|
||||
The sample file ip.limit, the rule format is as follows:
|
||||
`127.0.0.1:100:10240:http://192.168.1.1:3100`
|
||||
Rule interpretation:
|
||||
`127.0.0.1` is the IP to be restricted
|
||||
`100` is the maximum number of connections for this IP, not limited to write 0
|
||||
`10240` is the rate limit of IP single tcp connection, the unit is: byte / s, no limit write 0
|
||||
`http://192.168.1.1:3100` is the upstream used by this IP, and it is not left blank.
|
||||
|
||||
##### `--rate-limit`
|
||||
Limit the speed of each tcp connection of the service, for example: 100K 2000K 1M . 0 means unlimited, default 0.
|
||||
|
||||
## 11. Cluster
|
||||
|
||||
The proxy supports the cluster management. The proxy is installed on each machine node as an agent, with the control panel [`proxyadmin cluster edition`] (https://github.com/snail007/proxy-admin-cluster) Unified management of proxy services on massive machines.
|
||||
|
||||
If the proxy is to be run as an agent, assume that the cluster port address of the control panel is: `1.1.1.1: 55333`.
|
||||
|
||||
The command example is as follows:
|
||||
|
||||
`proxy agent -k xxx -c 1.1.1.1:55333 -i test`
|
||||
|
||||
Command explanation:
|
||||
|
||||
agent: is a function parameter, which means running agent mode.
|
||||
|
||||
-k : The encryption and decryption key for communication with `proxyadmin cluster edition`. This key is set in the configuration file of` proxyadmin cluster edition`.
|
||||
|
||||
-c : The cluster port address of `proxyadmin cluster edition`, format: IP:port.
|
||||
|
||||
-i : The unique identifier of the agent ensures that each agent is different. The "unique identifier" specified here is used when adding a node to the control panel. The IP is filled with this "unique identifier".
|
||||
If -i is not specified, the default is empty, and the control panel adds the IP field to fill in: the agent's internet IP.
|
||||
|
||||
-u: proxy parameter, empty by default. You can specify an agent, and the agent will communicate with the cluster through this agent.
|
||||
The format is the same as that of `--jumper`. For details, please refer to the `--jumper` part of the manual.
|
||||
|
||||
notice:
|
||||
|
||||
When the client service is configured in the control panel, all nodes use the same key, which leads to only one client working. To solve this problem,
|
||||
Client service parameters can use placeholders: `{AGENT_ID}` to refer to the agent’s id as the client’s key, so as to ensure that each client has a unique key.
|
||||
|
||||
For example, client service parameters:
|
||||
|
||||
`client -T tcp -P 1.1.1.1:30000 --k {AGENT_ID}`
|
||||
@@ -0,0 +1,2151 @@
|
||||
## 赞助商广告
|
||||
<a href="https://www.huobi.bi/zh-cn/topic/invited/?invite_code=qpi54">
|
||||
<img width="auto" height="100" src="/doc/images/zanzhu-1.png"/>
|
||||
</a>
|
||||
|
||||
## GOPROXY简介
|
||||
<img src="https://cdn.jsdelivr.net/gh/snail007/goproxy@master/doc/images/logo.jpg" width="200" height="auto"/>
|
||||
一款轻量级、功能强大、高性能的http代理、https代理、socks5代理、内网穿透代理服务器、ss代理、游戏盾、游戏代理,支持API代理认证。websocke代理、tcp代理、udp代理、socket代理、高防服务器。支持正向代理、反向代理、透明代理、TCP内网穿透、UDP内网穿透、HTTP内网穿透、HTTPS内网穿透、https代理负载均衡、http代理负载均衡、socks5代理负载均衡、socket代理负载均衡、ss代理负载均衡、TCP/UDP端口映射、SSH中转、TLS加密传输、协议转换、防污染DNS代理,限速,限连接数。官方QQ交流群: 42805407。
|
||||
|
||||
---
|
||||
|
||||
[](https://github.com/snail007/goproxy/) []() [](https://github.com/snail007/goproxy/releases) [](https://github.com/snail007/goproxy/releases)
|
||||
|
||||
---
|
||||
### [点击我观看视频教程](https://space.bilibili.com/472844633)
|
||||
- [下载地址](https://github.com/snail007/goproxy/releases)
|
||||
- [官方手册(国外)](https://snail007.github.io/goproxy/manual/zh/)
|
||||
- [官方手册(国内)](https://snail.gitee.io/proxy/manual/zh/)
|
||||
- [桌面版,控制面板ProxyAdmin](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md)
|
||||
- [安卓全局代理版](https://github.com/snail007/goproxy-ss-plugin-android)
|
||||
- [安卓全能代理版](https://github.com/snail007/goproxy-android)
|
||||
- [安卓内网穿透客户端](https://github.com/snail007/lanass)
|
||||
- [SDK](https://github.com/snail007/goproxy-sdk)
|
||||
- [GORPOXY实战教程](https://snail.gitee.io/proxy/)
|
||||
- [免费版VS商业版(安装、激活)](https://snail.gitee.io/proxy/page/free_vs_commercial/)
|
||||
|
||||
## 国内下载
|
||||
|
||||
请在github的下载链接前面加上: `https://mirrors.host900.com/` 。
|
||||
|
||||
比如`v10.4`的github下载链接是:
|
||||
|
||||
`https://github.com/snail007/goproxy/releases/download/v10.4/proxy-linux-amd64.tar.gz`
|
||||
|
||||
那么国内下载地址就是:
|
||||
|
||||
`https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/v10.4/proxy-linux-amd64.tar.gz`
|
||||
|
||||
此地址也适用于wget,curl直接命令行下载。
|
||||
|
||||
## ProxyAdmin介绍预览(这不是goproxy,是控制面板友情链接;安装使用goproxy请往下看,谢谢!)
|
||||
`ProxyAdmin` 是强大的代理服务工具 snail007/goproxy 的控制面板,运行了它,一秒让你的服务器变为强大的代理服务器,友好的交互界面,小白也能轻松上手,让你用起来得心应手,心情舒畅。
|
||||
|
||||

|
||||
|
||||
### goproxy能干什么?
|
||||
- 链式代理,程序本身可以作为一级代理,如果设置了上级代理那么可以作为二级代理,乃至N级代理。
|
||||
- 通讯加密,如果程序不是一级代理,而且上级代理也是本程序,那么可以加密和上级代理之间的通讯,采用底层tls高强度加密,安全无特征。
|
||||
- 智能HTTP代理,HTTPS代理,SOCKS5代理,会自动判断访问的网站是否屏蔽,如果被屏蔽那么就会使用上级代理(前提是配置了上级代理)访问网站;如果访问的网站没有被屏蔽,为了加速访问,代理会直接访问网站,不使用上级代理。
|
||||
- 域名黑白名单,更加自由的控制网站的访问方式。
|
||||
- 跨平台性,无论你是widows,linux,还是mac,甚至是树莓派,都可以很好的运行proxy。
|
||||
- 多协议支持,支持HTTP(S),TCP,UDP,Websocket,SOCKS5代理。
|
||||
- TCP/UDP端口转发。
|
||||
- 游戏盾,游戏代理,高防服务器。
|
||||
- 内网穿透,P2P传输,协议支持TCP和UDP,针对HTTP的优化穿透。
|
||||
- SSH中转,HTTP(S),SOCKS5代理支持SSH中转,上级Linux服务器不需要任何服务端,本地一个proxy即可开心上网。
|
||||
- [KCP](https://github.com/xtaci/kcp-go)协议支持,HTTP(S),SOCKS5代理支持KCP协议传输数据,降低延迟,提升浏览体验。
|
||||
- 动态选择上级代理,通过外部API,HTTP(S),SOCKS5,SPS代理可以实现基于用户或者IP的限速,连接数限制,动态获取上级。
|
||||
- 灵活的上级分配,HTTP(S),SOCKS5,SPS代理可以通过配置文件实现基于用户或者IP的限速,连接数限制,指定上级。
|
||||
- 反向代理,支持直接把域名解析到proxy监听的ip,然后proxy就会帮你代理访问需要访问的HTTP(S)网站。
|
||||
- 透明HTTP(S)代理,配合iptables,在网关直接把出去的80,443方向的流量转发到proxy,就能实现无感知的智能路由器代理。
|
||||
- 协议转换,可以把已经存在的HTTP(S)或SOCKS5或SS代理转换为一个端口同时支持HTTP(S)和SOCKS5和SS代理,转换后的SOCKS5和SS代理如果上级是SOCKS5代理,那么支持UDP功能,同时支持强大的级联认证功能。
|
||||
- 自定义底层加密传输,http(s)\sps\socks代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行自定义加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义一个密码即可。
|
||||
- 底层压缩高效传输,http(s)\sps\socks代理在tcp之上可以通过自定义加密和tls标准加密以及kcp协议加密tcp数据,在加密之后还可以对数据进行压缩,也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的。
|
||||
- 安全的DNS代理,可以通过本地的proxy提供的DNS代理服务器与上级代理加密通讯实现安全防污染的DNS查询。
|
||||
- 负载均衡,高可用,HTTP(S)\SOCKS5\SPS代理支持上级负载均衡和高可用,多个上级重复-P参数即可。
|
||||
- 指定出口IP,HTTP(S)\SOCKS5\SPS代理支持客户端用入口IP连接过来的,就用入口IP作为出口IP访问目标网站的功能。如果入口IP是内网IP,出口IP不会使用入口IP
|
||||
- 支持限速,HTTP(S)\SOCKS5\SPS\TCP代理支持限速。
|
||||
- 支持限连接数,HTTP(S)\SOCKS5\SPS\TCP代理支持限连接数。
|
||||
- SOCKS5代理支持级联认证。
|
||||
- 证书参数使用base64数据,默认情况下-C,-K参数是crt证书和key文件的路径,如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
- 支持客户端IP黑白名单,更加安全的控制客户端对代理服务的访问,如果黑白名单同时设置,那么只有白名单生效。socks/http(s)/sps/tcp/udp/dns/内网穿透bridge/内网穿透tbridge,都支持客户端IP黑白名单。
|
||||
- 端口范围批量监听,HTTP(S)\SOCKS5\SPS\TCP代理支持指定端口范围监听,避免启动过多进程,提高性能。
|
||||
|
||||
### 为什么需要它?
|
||||
|
||||
- 当由于某某原因,我们不能访问我们在其它地方的服务,我们可以通过多个相连的proxy节点建立起一个安全的隧道访问我们的服务。
|
||||
- 微信接口本地开发,方便调试。
|
||||
- 远程访问内网机器。
|
||||
- 和小伙伴一起玩局域网游戏。
|
||||
- 以前只能在局域网玩的,现在可以在任何地方玩。
|
||||
- 替代圣剑内网通,显IP内网通,花生壳之类的工具。
|
||||
- 有大量IP资源,想变现,对外提供IP代理服务。
|
||||
- 有大量拨号VPS,想对外提供IP代理服务。
|
||||
- 公司安全要求,审计员工对互联网的访问。
|
||||
- 想要一个高性能稳定的,认证功能齐全的代理服务。
|
||||
- 想一个固定入口,实现动态IP出口。
|
||||
- ..。
|
||||
|
||||
|
||||
本页手册适用于最新版goproxy,其他版本可能有的地方不再适用,请自己根据命令帮助使用。
|
||||
|
||||
|
||||
### 加入组织
|
||||
[点击加入交流组织gitter](https://gitter.im/go-proxy/Lobby?utm_source=share-link&utm_medium=link&utm_campaign=share-link)
|
||||
|
||||
[点击加入交流组织TG](https://t.me/snail007_goproxy)
|
||||
|
||||
## 下载安装 goproxy
|
||||
|
||||
### 快速安装 goproxy
|
||||
|
||||
如果你的VPS是linux64位的系统,那么只需要执行下面一句,就可以完成自动安装和配置.
|
||||
|
||||
提示:所有操作需要root权限。
|
||||
|
||||
免费版执行这个:
|
||||
|
||||
```shell
|
||||
curl -L https://mirrors.host900.com/https://github.com/snail007/goproxy/blob/master/install_auto.sh | bash
|
||||
```
|
||||
|
||||
商业版执行这个:
|
||||
|
||||
```shell
|
||||
curl -L https://mirrors.host900.com/https://github.com/snail007/goproxy/blob/master/install_auto_commercial.sh | bash
|
||||
```
|
||||
|
||||
安装完成,配置目录是/etc/proxy,更详细的使用方法请参考上面的手册目录,进一步了解你想要使用的功能。
|
||||
如果安装失败或者你的vps不是linux64位系统,请按照下面的半自动步骤安装:
|
||||
|
||||
### 手动安装 goproxy
|
||||
|
||||
1.下载goproxy
|
||||
|
||||
根据你的平台和CPU类型选择,下载地址: https://github.com/snail007/goproxy/releases ,
|
||||
|
||||
这里以 `proxy-linux-amd64.tar.gz` `v10.4` 为例,具体使用的时候,请根据你的平台和CPU类型选择具体文件名称.
|
||||
|
||||
免费版执行这个:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/v10.4/proxy-linux-amd64.tar.gz
|
||||
```
|
||||
|
||||
商业版执行这个:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/v10.4/proxy-linux-amd64_commercial.tar.gz
|
||||
```
|
||||
|
||||
2.下载自动安装脚本
|
||||
|
||||
免费版执行这个:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/install.sh
|
||||
chmod +x install.sh
|
||||
./install.sh
|
||||
```
|
||||
|
||||
商业版执行这个:
|
||||
|
||||
```shell
|
||||
cd /root/proxy/
|
||||
wget https://mirrors.host900.com/https://raw.githubusercontent.com/snail007/goproxy/master/install_commercial.sh
|
||||
chmod +x install_commercial.sh
|
||||
./install_commercial.sh
|
||||
```
|
||||
|
||||
## TODO
|
||||
- http,socks代理多个上级负载均衡?
|
||||
- http(s)代理增加pac支持?
|
||||
- 欢迎加群反馈..。
|
||||
|
||||
## License
|
||||
Proxy is licensed under GPLv3 license。
|
||||
|
||||
## Contact
|
||||
官方QQ交流群: 42805407
|
||||
|
||||
## Donation
|
||||
如果proxy帮助你解决了很多问题,你可以通过下面的捐赠更好的支持proxy。
|
||||
<img src="/doc/images/alipay.jpg" width="200" height="auto"/>
|
||||
<img src="/doc/images/wxpay.jpg" width="200" height="auto"/>
|
||||
|
||||
### 源代码申明
|
||||
|
||||
本项目作者发现大量的开发者基于本项目进行二次开发或使用大量本项目核心代码而不遵循GPLv3协议,这严重违背了本项目使用GPLv3开源协议的初衷,鉴于这种情况,本项目采取源代码延迟发布策略,在一定程度上遏制这些不尊重开源,不尊重他人劳动成果的行为。
|
||||
本项目会持续更新迭代,持续发布全平台的二进制程序,给大家提供强大便捷的代理工具。
|
||||
如果你有定制,商业需求请发邮件至`arraykeys@gmail.com`
|
||||
|
||||
## goproxy使用手册
|
||||
|
||||
|
||||
## 如何安装
|
||||
|
||||
### 1. Linux安装
|
||||
|
||||
[点击查看Linux安装教程](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E4%B8%8B%E8%BD%BD%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
### 2. 苹果Mac系统安装
|
||||
|
||||
[点击查看苹果Mac系统安装教程](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
### 3. Windows安装
|
||||
|
||||
为了方便操作,推荐Windows用户使用proxy-admin面板,[点击查看Windows安装教程](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
当然你也可以使用命令行goproxy[点击查看手动安装](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E6%89%8B%E5%8A%A8%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
### 4. 其它平台安装
|
||||
|
||||
[点击查看其它安装教程](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E6%89%8B%E5%8A%A8%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
## 免费版、商业版说明
|
||||
|
||||
本手册描述功能,`proxyadmin商业版`和`goproxy商业版`全部包含;认证等高级功能参数免费版和VIP控制面板不包含;
|
||||
|
||||
如果您用`goproxy免费版`执行某些命令或者`proxyadmin 免费版`、`proxyadmin VIP版`服务启动失败的时候遇到,类似如下xxx参数不存在的提示,说明这个参数是商业版的功能,您需要下载并购买商业版授权才能使用.
|
||||
` err : unknown short flag '-a'`
|
||||
|
||||
以下软件都是相互独立使用,没有依赖关系,需要购买的也是分别单独购买使用。
|
||||
|
||||
软件名称 | 免费版功能 | 商业版功能 | 购买使用 | 特点 | 传送门
|
||||
:----------- | :---: | :---: | :---: | :---: | :---:
|
||||
proxyadmin 免费版 | √ | x | x| Web界面操作,支持Linux,Windows,macOS,免费使用,服务数量有限制,适合个人,小白和白嫖党 | [下载安装](https://github.com/snail007/proxy_admin_free)
|
||||
proxyadmin VIP版 | √ | x | √| Web界面操作,支持更多平台,功能和免费版一样,服务数量无限制,适合个体户或者小集体 | [下载安装](https://github.com/snail007/proxy-admin-vip)
|
||||
proxyadmin 商业版 | √ | √ | √|Web界面操作,支持更多平台,无限制,适合集体或公司对外提供服务 | [下载安装](https://github.com/snail007/proxy-admin-commercial)
|
||||
proxyadmin 集群版| √ | √ | √|Web界面操作,支持Linux,Windows,macOS,无限制,配合`goproxy 商业版`,可以实现以组为单位,管理海量机器上的proxy服务,适合有大量机器的集体或公司对外提供服务 | [下载安装](https://github.com/snail007/proxy-admin-cluster)
|
||||
goproxy 免费版 | √ | x | x|命令行操作,全平台支持,免费使用,稳定且灵活,适合一切熟悉命令行的大佬或集体或公司白嫖,自用或者大规模部署对外服务 | [下载安装](https://github.com/snail007/goproxy)
|
||||
goproxy 商业版| √ | √ | √|命令行操作,全平台支持,稳定且灵活,适合集体或公司大规模部署对外提供服务 | [下载安装](https://github.com/snail007/goproxy)
|
||||
|
||||
关于免费版功能和商业版功能对比请看这里,[`免费版`和`商业版`功能对比](https://snail.gitee.io/proxy/page/free_vs_commercial/).
|
||||
|
||||
[商业版激活绑定教程](https://snail.gitee.io/proxy/page/free_vs_commercial/)
|
||||
|
||||
提示:
|
||||
|
||||
**免费和付费软件均没有额外技术支持,不按着手册操作的一切问题请自行解决。付费软件免费享有`手册功能`使用指导和`首次安装配置`指导。**
|
||||
|
||||
## FAQ
|
||||
|
||||
[别点我](https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/)
|
||||
|
||||
## 首次使用必看,谢谢!!!
|
||||
|
||||
### 1. 环境
|
||||
|
||||
该手册教程,默认系统是linux,程序是proxy;所有操作需要root权限;
|
||||
|
||||
如果你的是windows,请使用windows版本的proxy.exe即可。
|
||||
|
||||
### 2. 使用配置文件
|
||||
|
||||
接下来的教程都是通过命令行参数介绍使用方法,也可以通过读取配置文件获取参数。
|
||||
|
||||
具体格式是通过@符号指定配置文件,例如:proxy @configfile.txt
|
||||
|
||||
configfile.txt里面的格式是,第一行是子命令名称,第二行开始一行一个参数,
|
||||
|
||||
格式:`参数 参数值`,没有参数值的直接写参数,比如:--nolog
|
||||
|
||||
比如configfile.txt内容如下:
|
||||
|
||||
```shell
|
||||
http
|
||||
-t tcp
|
||||
-p :33080
|
||||
--forever
|
||||
```
|
||||
|
||||
### 3. 调试输出
|
||||
|
||||
默认情况下,日志输出的信息不包含文件行数,某些情况下为了排除程序问题,快速定位问题,
|
||||
|
||||
可以使用--debug参数,输出代码行数和毫秒时间。
|
||||
|
||||
### 4. 使用日志文件
|
||||
|
||||
默认情况下,日志是直接在控制台显示出来的,如果要保存到文件,可以使用--log参数,
|
||||
|
||||
比如: --log proxy.log,日志就会输出到proxy.log方便排除问题。
|
||||
|
||||
|
||||
### 5. 生成加密通讯需要的证书文件
|
||||
|
||||
http(s)代理、tcp代理、udp代理、socks5代理、内网穿透等功能和上级通讯的时候,为了安全我们采用TLS加密通讯,当然可以选择不加密通信通讯,本教程所有和上级通讯都采用加密,需要证书文件。
|
||||
|
||||
***所有端必须使用相同的proxy.crt和proxy.key***
|
||||
|
||||
1.通过下面的命令生成自签名的证书和key文件。
|
||||
`proxy keygen -C proxy`
|
||||
会在当前程序目录下面生成证书文件proxy.crt和key文件proxy.key。
|
||||
|
||||
2.通过下面的命令生,使用自签名证书proxy.crt和key文件proxy.key签发新证书:goproxy.crt和goproxy.key。
|
||||
`proxy keygen -s -C proxy -c goproxy`
|
||||
会在当前程序目录下面生成证书文件goproxy.crt和key文件goproxy.key。
|
||||
|
||||
3.默认情况下证书的里面的域名是随机的,可以使用`-n test.com`参数指定。
|
||||
|
||||
4.更多用法:`proxy keygen --help`。
|
||||
|
||||
### 6. 后台运行
|
||||
|
||||
默认执行proxy之后,如果要保持proxy运行,不能关闭命令行。
|
||||
|
||||
如果想在后台运行proxy,命令行可以关闭,只需要在命令最后加上--daemon参数即可。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080" --daemon`
|
||||
|
||||
### 7. 守护运行
|
||||
守护运行参数--forever,比如: `proxy http --forever` ,
|
||||
|
||||
proxy会fork子进程,然后监控子进程,如果子进程异常退出,5秒后重启子进程。
|
||||
|
||||
该参数配合后台运行参数--daemon和日志参数--log,可以保障proxy一直在后台执行不会因为意外退出,
|
||||
|
||||
而且可以通过日志文件看到proxy的输出日志内容。
|
||||
|
||||
比如: `proxy http -p ":9090" --forever --log proxy.log --daemon`
|
||||
|
||||
### 8. 安全建议
|
||||
|
||||
当VPS在nat设备后面,vps上网卡IP都是内网IP,这个时候可以通过-g参数添加vps的外网ip防止死循环。
|
||||
|
||||
假设你的vps外网ip是23.23.23.23,下面命令通过-g参数设置23.23.23.23
|
||||
|
||||
`proxy http -g "23.23.23.23"`
|
||||
|
||||
### 9. 负载均衡和高可用
|
||||
|
||||
HTTP(S)\SOCKS5\SPS\TCP代理支持上级负载均衡和高可用,多个上级重复-P参数即可。
|
||||
|
||||
负载均衡策略支持5种,可以通过`--lb-method`参数指定:
|
||||
|
||||
roundrobin 轮流使用
|
||||
|
||||
leastconn 使用最小连接数的
|
||||
|
||||
leasttime 使用连接时间最小的
|
||||
|
||||
hash 使用根据客户端地址计算出一个固定上级
|
||||
|
||||
weight 根据每个上级的权重和连接数情况,选择出一个上级
|
||||
|
||||
提示:
|
||||
|
||||
1.负载均衡检查时间间隔可以通过`--lb-retrytime`设置,单位毫秒
|
||||
|
||||
2.负载均衡连接超时时间可以通过`--lb-timeout`设置,单位毫秒
|
||||
|
||||
3.如果负载均衡策略是权重(weight),-P格式为:2.2.2.2:3880?w=1,1就是权重,大于0的整数。
|
||||
|
||||
4.如果负载均衡策略是hash,默认是根据客户端地址选择上级,可以通过开关`--lb-hashtarget`使用访问的目标地址选择上级。
|
||||
|
||||
5.TCP代理没有参数`--lb-hashtarget`.
|
||||
|
||||
6.默认是负载均衡+高可用模式,如果使用了参数`--lb-onlyha`就只使用高可用模式,依据负载均衡策略选择一个节点,之后就一直使用这个节点,直到这个节点不再存活,那么会依据负载均衡策略再选择一个节点使用,以此循环.
|
||||
|
||||
7.如果检查节点全部不再存活,那么每次连接都会随机选取一个节点使用.
|
||||
|
||||
### 10. 代理跳板跳转
|
||||
|
||||
http(s)代理,SPS代理,内网穿透,tcp代理都支持通过中间第三方代理连接上级,
|
||||
|
||||
参数是:--jumper,所有格式如下:
|
||||
|
||||
```text
|
||||
http://username:password@host:port
|
||||
http://host:port
|
||||
https://username:password@host:port
|
||||
https://host:port
|
||||
socks5://username:password@host:port
|
||||
socks5://host:port
|
||||
socks5s://username:password@host:port
|
||||
socks5s://host:port
|
||||
ss://method:password@host:port
|
||||
```
|
||||
|
||||
http,socks5代表的是普通的http和socks5代理。
|
||||
|
||||
https,socks5s代表的是通过tls保护的http和socks5代理,
|
||||
|
||||
也就是http代理 over TLS , socks over TLS。
|
||||
|
||||
### 11. 域名黑白名单
|
||||
|
||||
socks/http(s)/sps代理都支持域名黑白名单。
|
||||
|
||||
用--stop参数指定一个域名黑名单列表文件,那么当用户连接文件里面这些域名的时候连接就会被断开。
|
||||
|
||||
用--only参数指定一个域名白名单列表文件,那么当用户连接文件里面这些域名之外的域名的时候连接就会被断开。
|
||||
|
||||
如果同时设置了--stop和--only,那么只有--only会起作用。
|
||||
|
||||
黑白域名名单文件内容格式如下:
|
||||
|
||||
```text
|
||||
**.baidu.com
|
||||
*.taobao.com
|
||||
a.com
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
?.qq.com
|
||||
```
|
||||
|
||||
说明:
|
||||
|
||||
1.一行一个域名,域名写法支持通配符`*`和`?`,`*`代表任意个字符,`?`代表一个任意字符,
|
||||
|
||||
2.`**.baidu.com` 匹配无论是多少级所有后缀是`.baidu.com`的域名。
|
||||
|
||||
3.`*.taobao.com` 匹配后缀是`.taobao.com`的三级域名。
|
||||
|
||||
4.还可以直接是IP地址。
|
||||
|
||||
5.`#`开头的为注释。
|
||||
|
||||
### 12. 客户端IP黑白名单
|
||||
|
||||
socks/http(s)/sps/tcp/udp/dns/内网穿透bridge/内网穿透tbridge,都支持客户端IP黑白名单。
|
||||
|
||||
用--ip-deny参数指定一个客户端IP黑名单列表文件,那么当用户的IP在这个文件里面的时候连接就会被断开。
|
||||
|
||||
用--ip-allow参数指定一个客户端IP白名单列表文件,那么当用户的IP不在这个文件里面的时候连接就会被断开。
|
||||
|
||||
如果同时设置了--ip-deny和--ip-allow,那么只有--ip-allow会起作用。
|
||||
|
||||
客户端IP黑白名单文件内容格式如下:
|
||||
|
||||
```text
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
192.168.1?.*
|
||||
```
|
||||
|
||||
说明:
|
||||
|
||||
1.一行一个域名,域名写法支持通配符`*`和`?`,`*`代表任意个字符,`?`代表一个任意字符。
|
||||
|
||||
2.`#`开头的为注释。
|
||||
|
||||
### 13. 协议加载文件
|
||||
|
||||
proxy的各种代理功能里面很多地方都有参数设置一个文件,比如:--blocked 指定一个直接走上级的域名列表文件,参数值是文件的路径,
|
||||
|
||||
如果参数支持协议加载文件,那么文件路径不仅可以是文件路径,还可以是:
|
||||
|
||||
a.“base64://”开头的base64编码的上面说明的文件内容,比如:base64://ajfpoajsdfa=
|
||||
|
||||
b.”str://“开头的英文逗号分割的多个,比如:str://xxx,yyy
|
||||
|
||||
proxy的blocked,direct,stop,only,hosts,resolve.rules,rewriter.rules,ip.allow,ip.deny 文件支持协议加载。
|
||||
|
||||
### 14. 客户端并发连接数
|
||||
|
||||
socks5\sps\http代理,控制客户端并发连接数参数是:`--max-conns-rate`,控制每秒客户端的最大连接数,默认20, 0为不限制.
|
||||
|
||||
### 15 监听多个端口
|
||||
|
||||
`tcp/http/socks/sps`支持同时监听多个端口以及范围端口。
|
||||
一般情况下监听一个端口就可以,不过如果需要同时监听多个两个端口,或者范围端口,那么-p参数是支持的,
|
||||
格式是:`-p 0.0.0.0:80,0.0.0.0:443,0.0.0.0:8000-9000,:5000-6000`,多个绑定用逗号分隔即可。
|
||||
|
||||
## 1.HTTP代理
|
||||
|
||||
### 1.1.普通一级HTTP代理
|
||||
|
||||
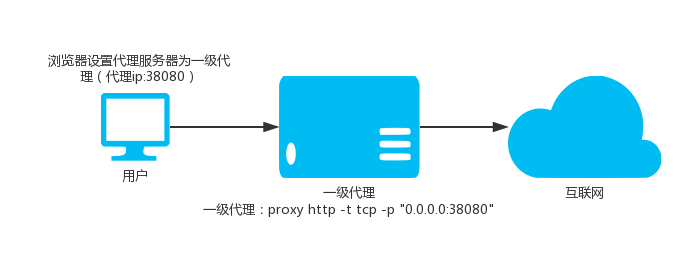
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080"`
|
||||
|
||||
-p参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
### 1.2.普通二级HTTP代理
|
||||
|
||||
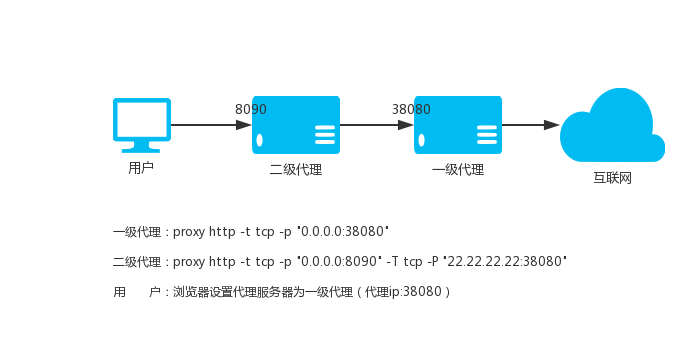
|
||||
|
||||
使用本地端口8090,假设上级HTTP代理是`22.22.22.22:8080`
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" `
|
||||
|
||||
我们还可以指定网站域名的黑白名单文件,一行一个域名,匹配规则是最右匹配,比如:baidu.com,匹配的是*.*.baidu.com,黑名单的域名直接走上级代理,白名单的域名不走上级代理。
|
||||
|
||||
`proxy http -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt`
|
||||
|
||||
### 1.3.HTTP二级代理(加密)
|
||||
|
||||
> 注意: 后面二级代理使用的`proxy.crt`和`proxy.key`应与一级代理一致
|
||||
|
||||
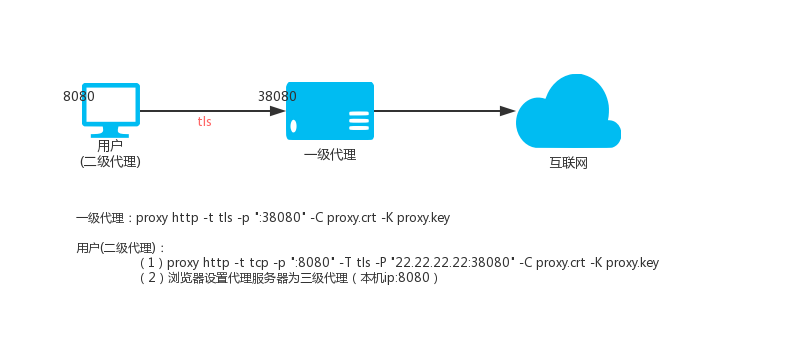
|
||||
一级HTTP代理(VPS,IP:22.22.22.22)
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
二级HTTP代理(本地Linux)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080。
|
||||
|
||||
二级HTTP代理(本地windows)
|
||||
`proxy.exe http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
然后设置你的windos系统中,需要通过代理上网的程序的代理为http模式,地址为:127.0.0.1,端口为:8080,程序即可通过加密通道通过vps上网。
|
||||
|
||||
### 1.4.HTTP三级代理(加密)
|
||||

|
||||
一级HTTP代理VPS_01,IP:22.22.22.22
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
二级HTTP代理VPS_02,IP:33.33.33.33
|
||||
`proxy http -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
三级HTTP代理(本地)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地的8080端口就是访问一级HTTP代理上面的代理端口38080。
|
||||
|
||||
### 1.5.Basic认证,API认证
|
||||
|
||||
请参考`9.API认证` 和 `10.本地认证`
|
||||
|
||||
### 1.6.HTTP代理流量强制走上级HTTP代理
|
||||
默认情况下,proxy会智能判断一个网站域名是否无法访问,如果无法访问才走上级HTTP代理.通过--always可以使全部HTTP代理流量强制走上级HTTP代理。
|
||||
`proxy http --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
### 1.7.HTTP(S)通过SSH中转
|
||||
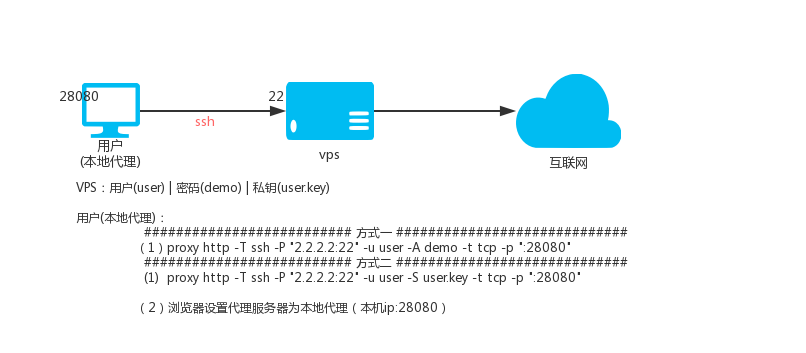
|
||||
说明:ssh中转的原理是利用了ssh的转发功能,就是你连接上ssh之后,可以通过ssh代理访问目标地址。
|
||||
假设有:vps
|
||||
- IP是2.2.2.2, ssh端口是22, ssh用户名是:user, ssh用户密码是:demo
|
||||
- 用户user的ssh私钥名称是user.key
|
||||
|
||||
#### *1.7.1 ssh用户名和密码的方式*
|
||||
本地HTTP(S)代理28080端口,执行:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080"`
|
||||
#### *1.7.2 ssh用户名和密钥的方式*
|
||||
本地HTTP(S)代理28080端口,执行:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080"`
|
||||
|
||||
### 1.8.KCP协议传输
|
||||
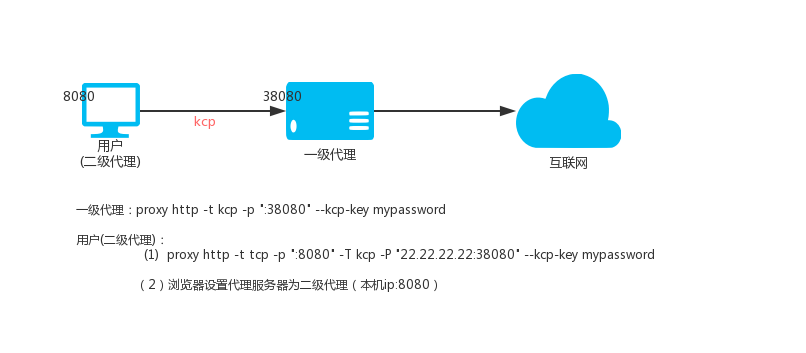
|
||||
KCP协议需要--kcp-key参数设置一个密码用于加密解密数据
|
||||
|
||||
一级HTTP代理(VPS,IP:22.22.22.22)
|
||||
`proxy http -t kcp -p ":38080" --kcp-key mypassword`
|
||||
|
||||
二级HTTP代理(本地Linux)
|
||||
`proxy http -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080,数据通过kcp协议传输,注意kcp走的是udp协议协议,所以防火墙需放开38080的udp协议。
|
||||
|
||||
### 1.9 HTTP(S)反向代理
|
||||
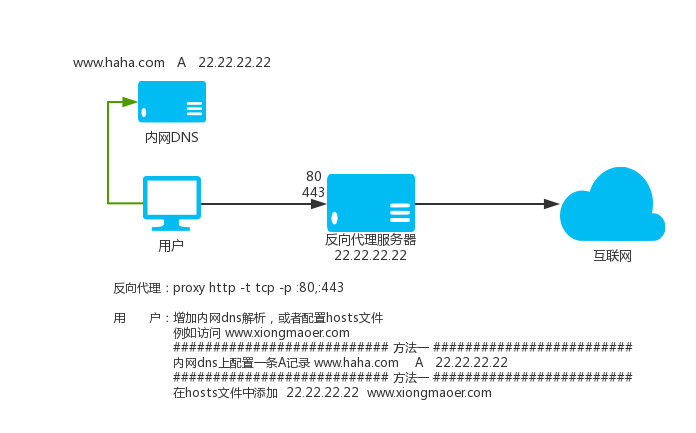
|
||||
proxy不仅支持在其他软件里面通过设置代理的方式,为其他软件提供代理服务,而且支持直接把请求的网站域名解析到proxy监听的ip上,然后proxy监听80和443端口,那么proxy就会自动为你代理访问需要访问的HTTP(S)网站。
|
||||
|
||||
使用方式:
|
||||
在"最后一级proxy代理"的机器上,因为proxy要伪装成所有网站,网站默认的端口HTTP是80,HTTPS是443,让proxy监听80和443端口即可.参数-p多个地址用逗号分割。
|
||||
`proxy http -t tcp -p :80,:443`
|
||||
|
||||
这个命令就在机器上启动了一个proxy代理,同时监听80和443端口,既可以当作普通的代理使用,也可以直接把需要代理的域名解析到这个机器的IP上。
|
||||
|
||||
如果有上级代理那么参照上面教程设置上级即可,使用方式完全一样。
|
||||
`proxy http -t tcp -p :80,:443 -T tls -P "2.2.2.2:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
注意:
|
||||
proxy所在的服务器的DNS解析结果不能受到自定义的解析影响,不然就死循环了,proxy代理最好指定`--dns 8.8.8.8`参数。
|
||||
|
||||
### 1.10 HTTP(S)透明代理
|
||||
该模式需要具有一定的网络基础,相关概念不懂的请自行搜索解决。
|
||||
假设proxy现在在路由器上运行,启动命令如下:
|
||||
`proxy http -t tcp -p :33080 -T tls -P "2.2.2.2:33090" -C proxy.crt -K proxy.key`
|
||||
|
||||
然后添加iptables规则,下面是参考规则:
|
||||
```shell
|
||||
#上级proxy服务端服务器IP地址:
|
||||
proxy_server_ip=2.2.2.2
|
||||
|
||||
#路由器运行proxy监听的端口:
|
||||
proxy_local_port=33080
|
||||
|
||||
#下面的就不用修改了
|
||||
#create a new chain named PROXY
|
||||
iptables -t nat -N PROXY
|
||||
|
||||
# Ignore your PROXY server's addresses
|
||||
# It's very IMPORTANT, just be careful。
|
||||
|
||||
iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
# Ignore LANs IP address
|
||||
iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
# Anything to port 80 443 should be redirected to PROXY's local port
|
||||
iptables -t nat -A PROXY -p tcp --dport 80 -j REDIRECT --to-ports $proxy_local_port
|
||||
iptables -t nat -A PROXY -p tcp --dport 443 -j REDIRECT --to-ports $proxy_local_port
|
||||
|
||||
# Apply the rules to nat client
|
||||
iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
# Apply the rules to localhost
|
||||
iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
- 清空整个链 iptables -F 链名比如iptables -t nat -F PROXY
|
||||
- 删除指定的用户自定义链 iptables -X 链名 比如 iptables -t nat -X PROXY
|
||||
- 从所选链中删除规则 iptables -D 链名 规则详情 比如 iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 1.11 自定义DNS
|
||||
--dns-address和--dns-ttl参数,用于自己指定proxy访问域名的时候使用的dns(--dns-address)
|
||||
以及解析结果缓存时间(--dns-ttl)秒数,避免系统dns对proxy的干扰,另外缓存功能还能减少dns解析时间提高访问速度。
|
||||
比如:
|
||||
`proxy http -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 1.12 自定义加密
|
||||
proxy的http(s)代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行自定义
|
||||
加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义一个密码即可,
|
||||
加密分为两个部分,一部分是本地(-z)是否加密解密,一部分是与上级(-Z)传输是否加密解密。
|
||||
自定义加密要求两端都是proxy才可以,下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
本地二级执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
本地三级执行:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
### 1.13 压缩传输
|
||||
proxy的http(s)代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,在自定义加密之前还可以对数据进行压缩,
|
||||
也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的,压缩分为两个部分,一部分是本地(-m)是否压缩传输,
|
||||
一部分是与上级(-M)传输是否压缩。
|
||||
压缩要求两端都是proxy才可以,压缩也在一定程度上保护了(加密)数据,下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
本地二级执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
本地三级执行:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
### 1.14 负载均衡
|
||||
|
||||
HTTP(S)代理支持上级负载均衡,多个上级重复-P参数即可。
|
||||
|
||||
`proxy http --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080`
|
||||
|
||||
### 1.14.1 设置重试间隔和超时时间
|
||||
|
||||
`proxy http --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp -p :33080`
|
||||
|
||||
### 1.14.2 设置权重
|
||||
|
||||
`proxy http --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -t tcp -p :33080`
|
||||
|
||||
### 1.14.3 使用目标地址选择上级
|
||||
|
||||
`proxy http --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp -p :33080`
|
||||
|
||||
### 1.15 限速
|
||||
|
||||
限速100K,通过`-l`参数即可指定,比如:100K 2000K 1M . 0意味着无限制。
|
||||
|
||||
`proxy http -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 1.16 指定出口IP
|
||||
|
||||
`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy http -t tcp -p :33080 --bind-listen`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy http -t tcp -p 5.5.5.5:6666 --bind-listen`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy http -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 1.17 证书参数使用base64数据
|
||||
|
||||
默认情况下-C,-K参数是crt证书和key文件的路径,
|
||||
|
||||
如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
|
||||
### 1.18 智能模式
|
||||
智能模式设置,可以是intelligent|direct|parent三者之一。
|
||||
默认是:intelligent。
|
||||
每个值的含义如下:
|
||||
`--intelligent=direct`,不在blocked里面的目标都直连。
|
||||
`--intelligent=parent`,不在direct里面的目标都走上级。
|
||||
`--intelligent=intelligent`,blocked和direct里面都没有的目标,智能判断是否使用上级访问目标。
|
||||
|
||||
### 1.19 查看帮助
|
||||
`proxy help http`
|
||||
|
||||
## 2.TCP代理
|
||||
|
||||
### 2.1 普通一级TCP代理
|
||||
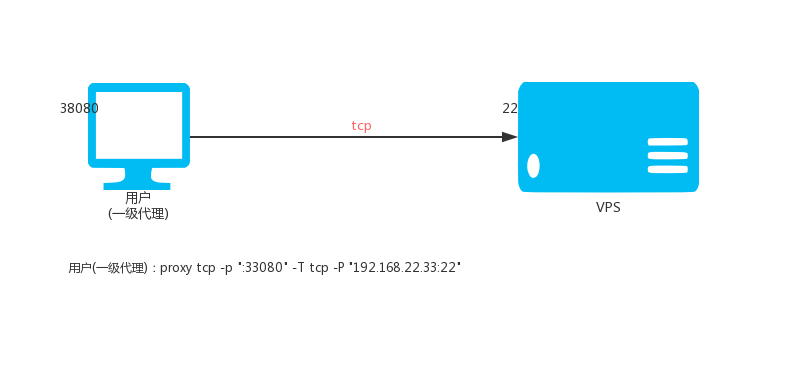
|
||||
本地执行:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22"`
|
||||
那么访问本地33080端口就是访问192.168.22.33的22端口。
|
||||
|
||||
`-p`参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
如果本地监听端口数量大于1,那么将会连接与本地端口一致的对应上级端口,忽略`-P`里面的端口。
|
||||
|
||||
如果需要所有端口进来的连接,都连接到上级指定端口,可以加上参数`--lock-port`。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:0"`
|
||||
|
||||
那么`33080`端口进来的连接,将会连接192.168.22.33的`33080`端口,其它端口以此类推,本地和上级端口一致,此时参数`-P`里面的端口用`0`。
|
||||
|
||||
如果想无论是`33080`,`33081`等端口进来的连接都连接到192.168.22.33的`22`端口,可以加上参数`--lock-port`
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:22" --lock-port`
|
||||
|
||||
|
||||
### 2.2 普通二级TCP代理
|
||||
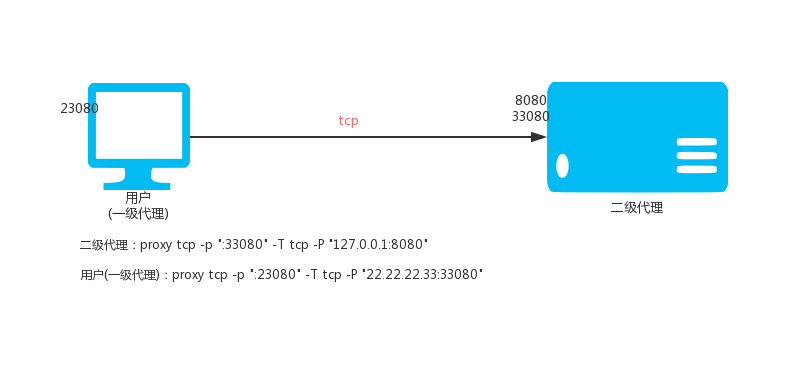
|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
本地执行:
|
||||
`proxy tcp -p ":23080" -T tcp -P "22.22.22.33:33080"`
|
||||
那么访问本地23080端口就是访问22.22.22.33的8080端口。
|
||||
|
||||
### 2.3 普通三级TCP代理
|
||||
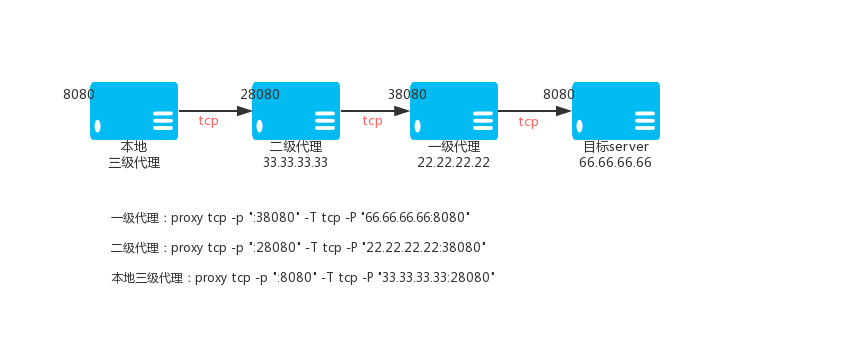
|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -p ":38080" -T tcp -P "66.66.66.66:8080"`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
三级TCP代理(本地)
|
||||
`proxy tcp -p ":8080" -T tcp -P "33.33.33.33:28080"`
|
||||
那么访问本地8080端口就是通过加密TCP隧道访问66.66.66.66的8080端口。
|
||||
|
||||
### 2.4 加密二级TCP代理
|
||||
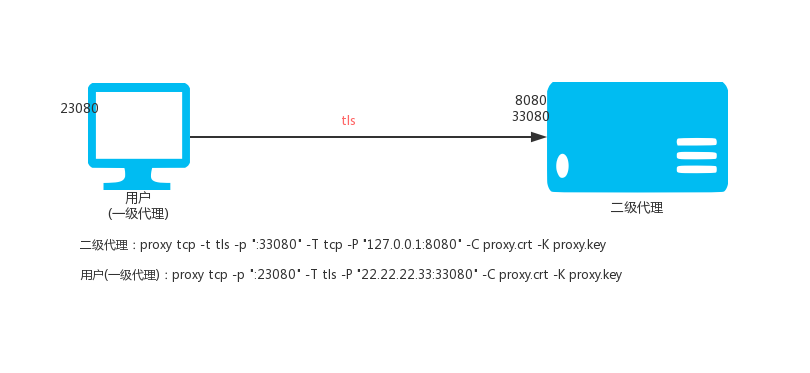
|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -t tls -p ":33080" -T tcp -P "127.0.0.1:8080" -C proxy.crt -K proxy.key`
|
||||
本地执行:
|
||||
`proxy tcp -p ":23080" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地23080端口就是通过加密TCP隧道访问22.22.22.33的8080端口。
|
||||
|
||||
### 2.5 加密三级TCP代理
|
||||
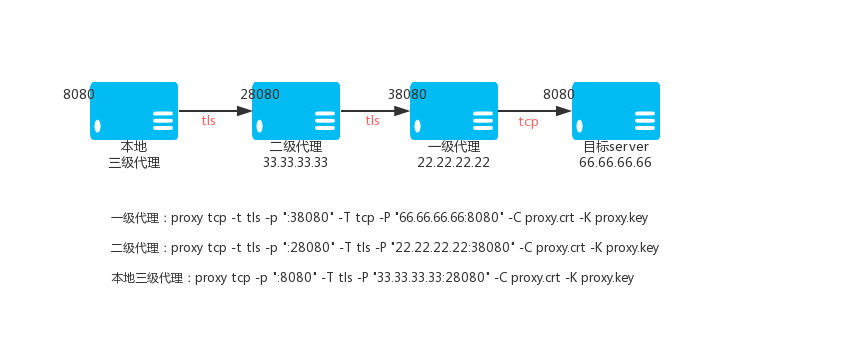
|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T tcp -P "66.66.66.66:8080" -C proxy.crt -K proxy.key`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
三级TCP代理(本地)
|
||||
`proxy tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地8080端口就是通过加密TCP隧道访问66.66.66.66的8080端口。
|
||||
|
||||
### 2.6 通过代理连接上级
|
||||
有时候proxy所在的网络不能直接访问外网,需要通过一个https或者socks5代理才能上网,那么这个时候
|
||||
-J参数就可以帮助你让proxy的tcp端口映射的时候通过https或者socks5代理去连接上级-P,将外部端口映射到本地。
|
||||
-J参数格式如下:
|
||||
|
||||
https代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
https://username:password@host:port
|
||||
代理不需要认证
|
||||
https://host:port
|
||||
|
||||
socks5代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
socks5://username:password@host:port
|
||||
代理不需要认证
|
||||
socks5://host:port
|
||||
|
||||
host:代理的IP或者域名
|
||||
port:代理的端口
|
||||
|
||||
### 2.7 指定出口IP
|
||||
|
||||
当TCP代理当上级类型(参数:-T)是tcp当时候,支持指定`出口IP`。`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy tcp -t tcp -p :33080 --bind-listen -T tcp -P 2.2.2.2:3322`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy tcp -t tcp -p 5.5.5.5:6666 --bind-listen -T tcp -P 2.2.2.2:3322`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy tcp -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888 -T tcp -P 2.2.2.2:3322`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 2.8 限速,限制连接数
|
||||
|
||||
参数`--max-conns`可以限制每个端口的最大连接数。
|
||||
比如限制每个端口最多1000个连接数:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --max-conns 1000`
|
||||
参数`--rate-limit`可以限制每个tcp连接的速率。
|
||||
比如限制每个tcp连接速率为100k/s:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --rate-limit 100k`
|
||||
|
||||
### 2.9 压缩传输
|
||||
|
||||
`--c`控制本地和客户端之间是否压缩传输,默认false;`--C`控制本地和上级之间是否压缩传输,默认false。
|
||||
|
||||
示例:
|
||||
|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -t tcp --c -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
本地执行:
|
||||
`proxy tcp -t tcp -p ":23080" -T tcp -P "22.22.22.33:33080" --C`
|
||||
|
||||
### 2.10 查看帮助
|
||||
`proxy help tcp`
|
||||
|
||||
## 3.UDP代理
|
||||
|
||||
### 3.1.普通一级UDP代理
|
||||
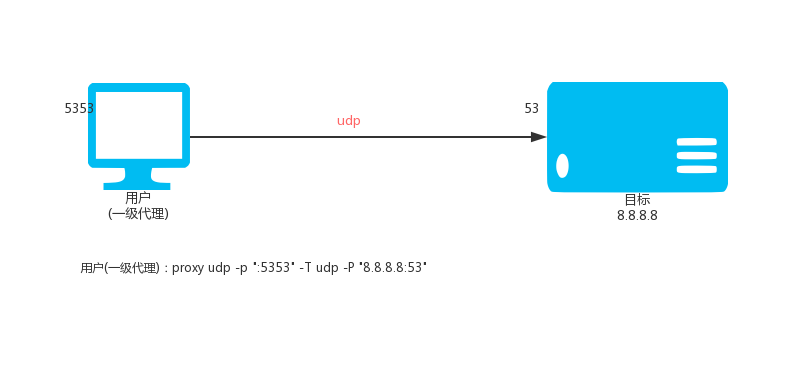
|
||||
本地执行:
|
||||
`proxy udp -p ":5353" -T udp -P "8.8.8.8:53"`
|
||||
那么访问本地UDP:5353端口就是访问8.8.8.8的UDP:53端口。
|
||||
|
||||
`-p`参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
如果本地监听端口数量大于1,那么将会连接与本地端口一致的对应上级端口,忽略`-P`里面的端口。
|
||||
|
||||
如果需要所有端口进来的连接,都连接到上级指定端口,可以加上参数`--lock-port`。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:0"`
|
||||
|
||||
那么`33080`端口进来的连接,将会连接192.168.22.33的`33080`端口,其它端口以此类推,本地和上级端口一致,此时参数`-P`里面的端口用`0`。
|
||||
|
||||
如果想无论是`33080`,`33081`等端口进来的连接都连接到192.168.22.33的`2222`端口,可以加上参数`--lock-port`
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:2222" --lock-port`
|
||||
|
||||
### 3.2.普通二级UDP代理
|
||||
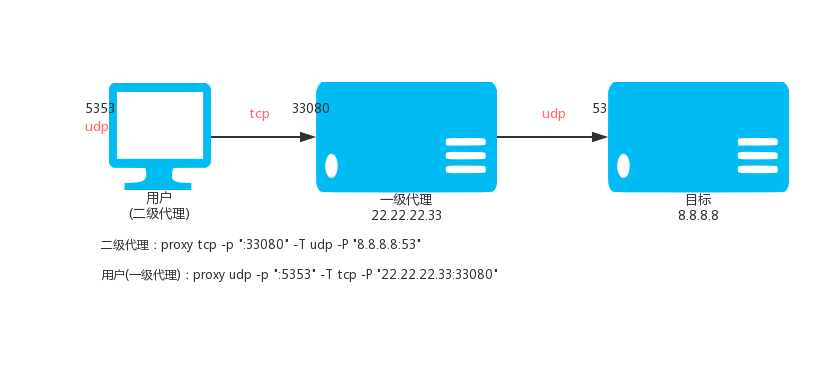
|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -p ":33080" -T udp -P "8.8.8.8:53"`
|
||||
本地执行:
|
||||
`proxy udp -p ":5353" -T tcp -P "22.22.22.33:33080"`
|
||||
那么访问本地UDP:5353端口就是通过TCP隧道,通过VPS访问8.8.8.8的UDP:53端口。
|
||||
|
||||
### 3.3.普通三级UDP代理
|
||||
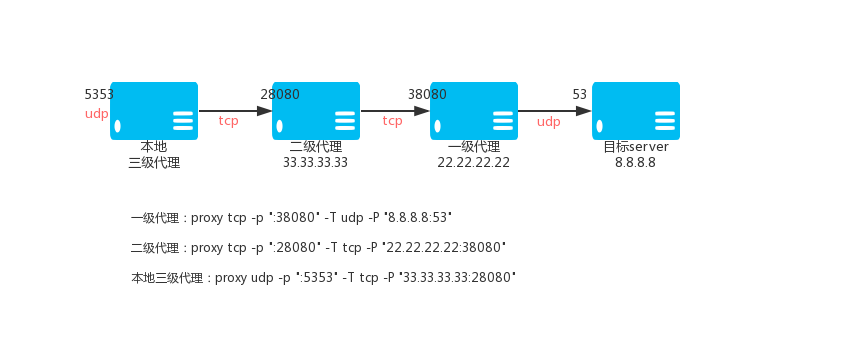
|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -p ":38080" -T udp -P "8.8.8.8:53"`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
三级TCP代理(本地)
|
||||
`proxy udp -p ":5353" -T tcp -P "33.33.33.33:28080"`
|
||||
那么访问本地5353端口就是通过TCP隧道,通过VPS访问8.8.8.8的53端口。
|
||||
|
||||
### 3.4.加密二级UDP代理
|
||||
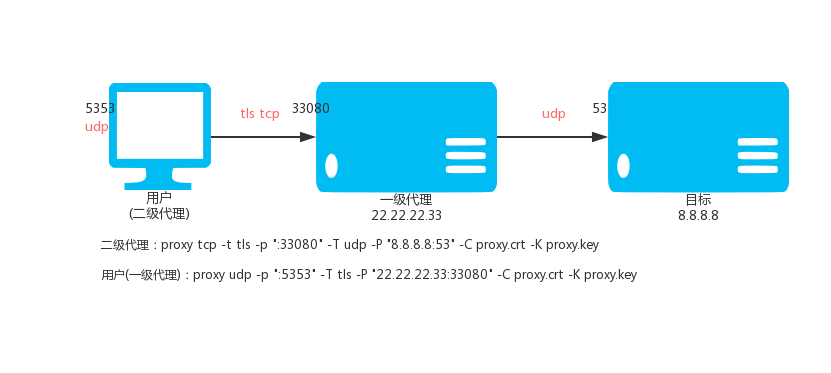
|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -t tls -p ":33080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
本地执行:
|
||||
`proxy udp -p ":5353" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地UDP:5353端口就是通过加密TCP隧道,通过VPS访问8.8.8.8的UDP:53端口。
|
||||
|
||||
### 3.5.加密三级UDP代理
|
||||
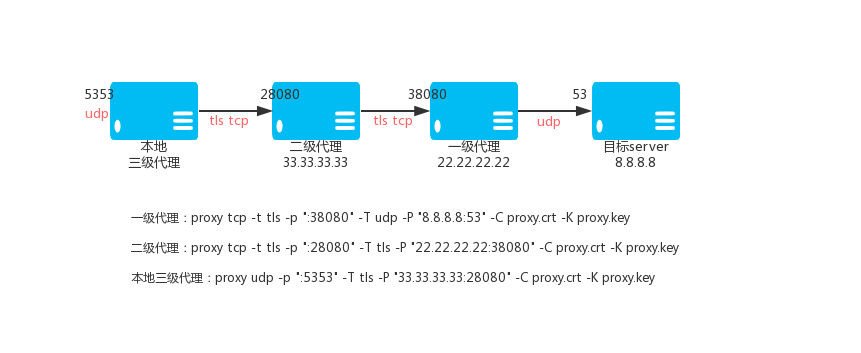
|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
三级TCP代理(本地)
|
||||
`proxy udp -p ":5353" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地5353端口就是通过加密TCP隧道,通过VPS_01访问8.8.8.8的53端口。
|
||||
|
||||
### 3.6 指定出口IP
|
||||
|
||||
当UDP代理当上级类型(参数:-T)是udp当时候,支持指定`出口IP`。使用`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
`proxy udp -p ":33080" -T udp -P "192.168.22.33:2222" -B`
|
||||
|
||||
### 3.7 查看帮助
|
||||
`proxy help udp`
|
||||
|
||||
## 4.内网穿透
|
||||
### 4.1、原理说明
|
||||
内网穿透,分为两个版本,“多链接版本”和“多路复用版本”,一般像web服务这种不是长时间连接的服务建议用“多链接版本”,如果是要保持长时间连接建议使用“多路复用版本”。
|
||||
1. 多链接版本,对应的子命令是tserver,tclient,tbridge。
|
||||
1. 多路复用版本,对应的子命令是server,client,bridge。
|
||||
1. 多链接版本和多路复用版本的参数和使用方式完全一样。
|
||||
1. 多路复用版本的server,client可以开启压缩传输,参数是--c。
|
||||
1. server,client要么都开启压缩,要么都不开启,不能只开一个。
|
||||
|
||||
下面的教程以“多路复用版本”为例子,说明使用方法。
|
||||
内网穿透由三部分组成:client端,server端,bridge端;client和server主动连接bridge端进行桥接。
|
||||
|
||||
### 4.2、TCP普通用法
|
||||
背景:
|
||||
- 公司机器A提供了web服务80端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在家里能够通过访问VPS的28080端口访问到公司机器A的80端口
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.3、微信接口本地开发
|
||||
背景:
|
||||
- 自己的笔记本提供了nginx服务80端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在微信的开发帐号的网页回调接口配置里面填写地址:http://22.22.22.22/calback.php
|
||||
然后就可以访问到笔记本的80端口下面的calback.php,如果需要绑定域名,可以用自己的域名
|
||||
比如:wx-dev.xxx.com解析到22.22.22.22,然后在自己笔记本的nginx里
|
||||
配置域名wx-dev.xxx.com到具体的目录即可。
|
||||
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行,确保vps的80端口没被其它程序占用。
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":80@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在自己笔记本上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.4、UDP普通用法
|
||||
背景:
|
||||
- 公司机器A提供了DNS解析服务,UDP:53端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在家里能够通过设置本地dns为22.22.22.22,使用公司机器A进行域名解析服务。
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server --udp -r ":53@:53" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.5、高级用法一
|
||||
背景:
|
||||
- 公司机器A提供了web服务80端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
为了安全,不想在VPS上能够访问到公司机器A,在家里能够通过访问本机的28080端口,
|
||||
通过加密隧道访问到公司机器A的80端口。
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在家里电脑上执行
|
||||
`proxy server -r ":28080@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.6、高级用法二
|
||||
提示:
|
||||
如果同时有多个client连接到同一个bridge,需要指定不同的key,可以通过--k参数设定,--k可以是任意唯一字符串,
|
||||
只要在同一个bridge上唯一即可。
|
||||
server连接到bridge的时候,如果同时有多个client连接到同一个bridge,需要使用--k参数选择client。
|
||||
暴露多个端口重复-r参数即可.-r格式是:"本地IP:本地端口@clientHOST:client端口"。
|
||||
|
||||
背景:
|
||||
- 公司机器A提供了web服务80端口,ftp服务21端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在家里能够通过访问VPS的28080端口访问到公司机器A的80端口
|
||||
在家里能够通过访问VPS的29090端口访问到公司机器A的21端口
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -r ":29090@:21" --k test -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client --k test -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.7.server的-r参数
|
||||
-r完整格式是:`PROTOCOL://LOCAL_IP:LOCAL_PORT@[CLIENT_KEY]CLIENT_LOCAL_HOST:CLIENT_LOCAL_PORT`
|
||||
|
||||
4.7.1.协议PROTOCOL:tcp、udp、ptcp、pudp。
|
||||
比如: `-r "udp://:10053@:53" -r "tcp://:10800@:1080" -r ":8080@:80"`
|
||||
如果指定了--udp参数,PROTOCOL默认为udp,那么:`-r ":8080@:80"`默认为udp;
|
||||
如果没有指定--udp参数,PROTOCOL默认为tcp,那么:`-r ":8080@:80"`默认为tcp;
|
||||
|
||||
4.7.2.CLIENT_KEY:默认是default。
|
||||
比如: -r "udp://:10053@[test1]:53" -r "tcp://:10800@[test2]:1080" -r ":8080@:80"
|
||||
如果指定了--k参数,比如--k test,那么:`-r ":8080@:80"`CLIENT_KEY默认为test;
|
||||
如果没有指定--k参数,那么:`-r ":8080@:80"`CLIENT_KEY默认为default;
|
||||
|
||||
4.7.3.LOCAL_IP为空默认是:`0.0.0.0`,CLIENT_LOCAL_HOST为空默认是:`127.0.0.1`;
|
||||
|
||||
### 4.8.server和client通过代理连接bridge
|
||||
有时候server或者client所在的网络不能直接访问外网,需要通过一个https或者socks5代理才能上网,那么这个时候
|
||||
-J参数就可以帮助你让server或者client通过https或者socks5代理去连接bridge。
|
||||
-J参数格式如下:
|
||||
|
||||
https代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
https://username:password@host:port
|
||||
代理不需要认证
|
||||
https://host:port
|
||||
|
||||
socks5代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
socks5://username:password@host:port
|
||||
代理不需要认证
|
||||
socks5://host:port
|
||||
|
||||
host:代理的IP或者域名
|
||||
port:代理的端口
|
||||
|
||||
### 4.9.内网穿透HTTP服务
|
||||
|
||||
通常HTTP请求客户端会使用server的ip和端口去设置HOST字段,但是与期望的后端实际HOST不一样,这样就造成了tcp是通的, 但后端依赖HOST字段定位虚拟主机就不能工作.现在用`--http-host`参数强制设置http头部的HOST字段值为后端实际的域名和端口即可轻松解决,另外使用了`--http-host`参数之后,会在每个HTTP请求的头部增加两个头部 `X-Forwarded-For` 和 `X-Real-IP` 值是客户端IP, 这样后端http服务就能方便的获取用户端真实IP地址。
|
||||
|
||||
`server`的--http-host参数格式如下:
|
||||
|
||||
`--http-host www.test.com:80@2200`,如果server监听多个端口,只需要重复`--http-host`参数设置每个端口的HOST即可。
|
||||
|
||||
实例:
|
||||
|
||||
比如client本地nginx,127.0.0.1:80提供了web服务,其中绑定了一个域名`local.com`。
|
||||
|
||||
那么server的启动参数可以如下:
|
||||
|
||||
`proxy server -P :30000 -r :2500@127.0.0.1:80 --http-host local.com@2500`
|
||||
|
||||
解释:
|
||||
|
||||
`-r :2500@127.0.0.1:80` 和 `--http-host local.com:80@2500` 里面的2500端口是server本地监听的端口
|
||||
|
||||
当使用http协议请求server的ip:2500端口的时候,http的头部HOST字段就会被设置为`local.com`。
|
||||
|
||||
另外只有设置了`--http-host`参数
|
||||
|
||||
|
||||
### 4.10 关于流量统计
|
||||
|
||||
如果单独启动一个server对接上级是proxy-admin控制面板,需要在上级控制面板里面新建一个映射,获得个映射规则的ID,
|
||||
|
||||
然后启动server的时候加上参数 --server-id=映射规则的ID 才能统计到流量。
|
||||
|
||||
### 4.11 关于p2p
|
||||
内网穿透支持在server和client网络情况满足的情况下,server和client之间通过p2p直接连接,开启方法是:
|
||||
|
||||
在启动bridge,server,client到时候都加上`--p2p`参数即可。server的-r参数可以针对端口是否启用p2p(ptcp和pudp)。
|
||||
|
||||
如果server和client之间p2p打洞失败,那么会自动切换使用bridge中转传输数据。
|
||||
|
||||
### 4.12 客户端key白名单
|
||||
内网穿透bridge可以设置客户端key白名单,参数是--client-keys,格式可以是:
|
||||
|
||||
a.文件名,文件内容一行一个客户端key只能包含数字字母下划线,也就是客户端启动参数--k的值,只有客户端key在此白名单的客户端才能连接。# 开头的行,为注释。
|
||||
|
||||
b.“base64://”开头的base64编码的上面a说明的文件内容,比如:base64://ajfpoajsdfa=
|
||||
|
||||
c.”str://“开头的英文逗号分割的多个key,比如:str://default,company,school
|
||||
|
||||
默认是空,允许所有key。
|
||||
|
||||
### 4.13 网络NAT类型判断
|
||||
|
||||
nat类型判断,方便查看网络是否支持p2p,可以执行:`proxy tools -a nattype`
|
||||
|
||||
### 4.14 查看帮助
|
||||
`proxy help bridge`
|
||||
`proxy help server`
|
||||
`proxy help client`
|
||||
|
||||
## 5.SOCKS5代理
|
||||
提示:
|
||||
|
||||
SOCKS5代理,支持CONNECT,UDP协议,不支持BIND,支持用户名密码认证。
|
||||
|
||||
***如果你的VPS是阿里云,腾讯云这种VPS,就是ifconfig看不见你的公网IP,只能看见内网IP,***
|
||||
|
||||
***那么需要加上`-g VPS公网IP`参数,SOCKS5代理的UDP功能才能正常工作。***
|
||||
|
||||
***socks5的udp功能默认关闭,可以通过--udp开启,默认是握手随机端口,可以通过固定一个端口提高性能,
|
||||
通过参数--udp-port 0设置,0代表随机选择一个空闲端口,也可以手动指定一个具体端口。***
|
||||
|
||||
### 5.1 普通SOCKS5代理
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080" --udp-port 0 --udp`
|
||||
|
||||
-p参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
### 5.2.普通二级SOCKS5代理
|
||||
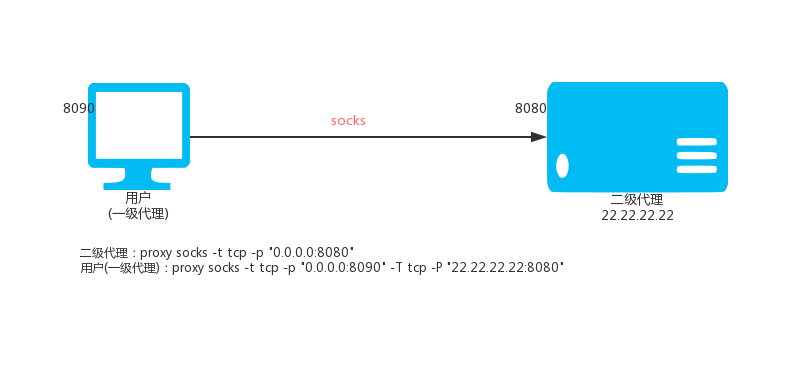
|
||||
使用本地端口8090,假设上级SOCKS5代理是`22.22.22.22:8080`
|
||||
`proxy socks -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" --udp-port 0 --udp`
|
||||
我们还可以指定网站域名的黑白名单文件,一行一个域名,匹配规则是最右匹配,比如:baidu.com,匹配的是*.*.baidu.com,黑名单的域名域名直接走上级代理,白名单的域名不走上级代理;如果域名即在黑名单又在白名单中,那么黑名单起作用。
|
||||
`proxy socks -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt --udp-port 0 --udp`
|
||||
|
||||
### 5.3.SOCKS二级代理(加密)
|
||||
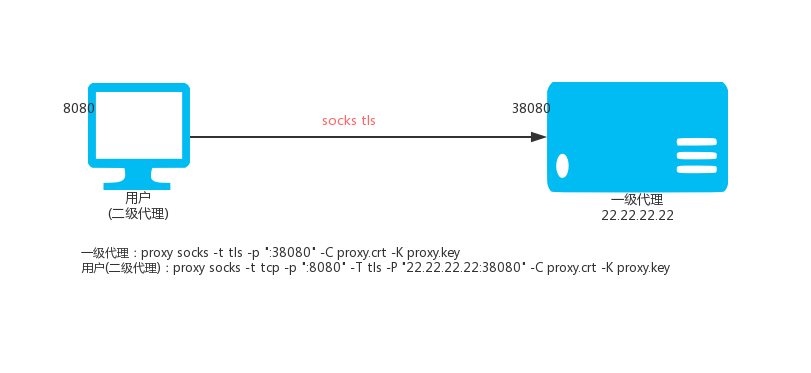
|
||||
一级SOCKS代理(VPS,IP:22.22.22.22)
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
|
||||
二级SOCKS代理(本地Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080。
|
||||
|
||||
二级SOCKS代理(本地windows)
|
||||
`proxy.exe socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
然后设置你的windos系统中,需要通过代理上网的程序的代理为socks5模式,地址为:127.0.0.1,端口为:8080,程序即可通过加密通道通过vps上网。
|
||||
|
||||
### 5.4.SOCKS三级代理(加密)
|
||||
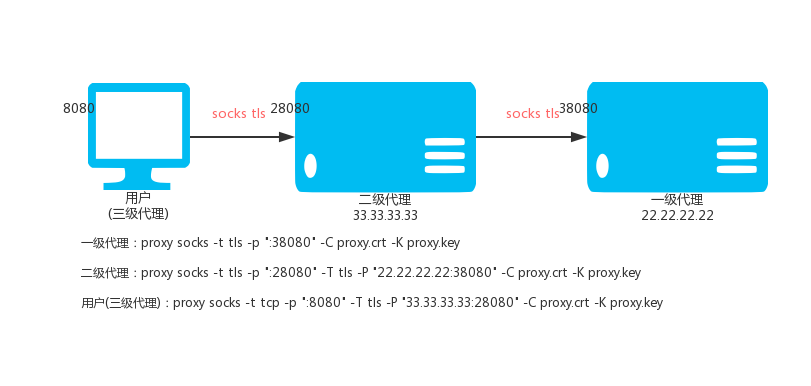
|
||||
一级SOCKS代理VPS_01,IP:22.22.22.22
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
二级SOCKS代理VPS_02,IP:33.33.33.33
|
||||
`proxy socks -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
三级SOCKS代理(本地)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
那么访问本地的8080端口就是访问一级SOCKS代理上面的代理端口38080。
|
||||
|
||||
### 5.5.SOCKS代理流量强制走上级SOCKS代理
|
||||
默认情况下,proxy会智能判断一个网站域名是否无法访问,如果无法访问才走上级SOCKS代理.通过--always可以使全部SOCKS代理流量强制走上级SOCKS代理。
|
||||
`proxy socks --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
|
||||
### 5.6.SOCKS通过SSH中转
|
||||
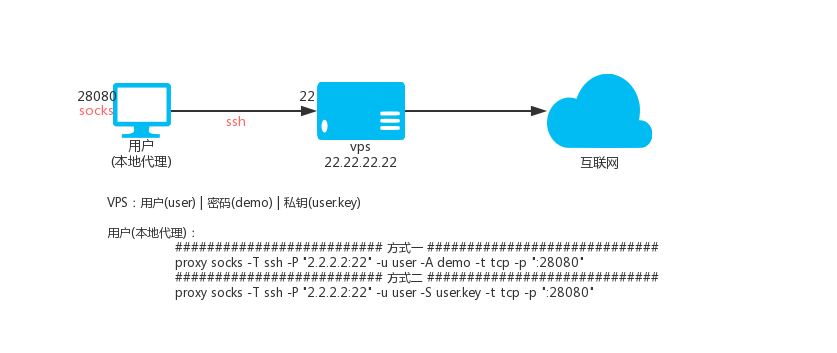
|
||||
说明:ssh中转的原理是利用了ssh的转发功能,就是你连接上ssh之后,可以通过ssh代理访问目标地址。
|
||||
假设有:vps
|
||||
- IP是2.2.2.2, ssh端口是22, ssh用户名是:user, ssh用户密码是:demo
|
||||
- 用户user的ssh私钥名称是user.key
|
||||
|
||||
#### *5.6.1 ssh用户名和密码的方式*
|
||||
本地SOCKS5代理28080端口,执行:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080" --udp-port 0 --udp`
|
||||
#### *5.6.2 ssh用户名和密钥的方式*
|
||||
本地SOCKS5代理28080端口,执行:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080" --udp-port 0 --udp`
|
||||
|
||||
那么访问本地的28080端口就是通过VPS访问目标地址。
|
||||
|
||||
### 5.7.认证
|
||||
对于socks5代理协议我们可以进行用户名密码认证,认证的用户名和密码可以在命令行指定
|
||||
`proxy socks -t tcp -p ":33080" -a "user1:pass1" -a "user2:pass2"`
|
||||
多个用户,重复-a参数即可。
|
||||
也可以放在文件中,格式是一行一个"用户名:密码",然后用-F指定。
|
||||
`proxy socks -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
### 5.8.KCP协议传输
|
||||
KCP协议需要--kcp-key参数设置一个密码用于加密解密数据
|
||||
|
||||
一级HTTP代理(VPS,IP:22.22.22.22)
|
||||
`proxy socks -t kcp -p ":38080" --kcp-key mypassword -g 22.22.22.22`
|
||||
|
||||
二级HTTP代理(本地Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080,数据通过kcp协议传输。
|
||||
|
||||
提示:
|
||||
|
||||
当本地使用kcp协议时,需要用-g指定vps公网IP,socks5的UDP功能才能正常使用.这时-g是返回给客户端的UDP地址中的IP地址.
|
||||
|
||||
### 5.9.自定义DNS
|
||||
--dns-address和--dns-ttl参数,用于自己指定proxy访问域名的时候使用的dns(--dns-address)
|
||||
以及解析结果缓存时间(--dns-ttl)秒数,避免系统dns对proxy的干扰,另外缓存功能还能减少dns解析时间提高访问速度。
|
||||
比如:
|
||||
`proxy socks -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 5.10 自定义加密
|
||||
proxy的socks代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行自定义加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义一个密码即可,
|
||||
加密分为两个部分,一部分是本地(-z)是否加密解密,一部分是与上级(-Z)传输是否加密解密。
|
||||
|
||||
自定义加密要求两端都是proxy才可以。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
本地二级执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
本地三级执行:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
### 5.11 压缩传输
|
||||
proxy的socks代理在tcp之上可以通过自定义加密和tls标准加密以及kcp协议加密tcp数据,在自定义加密之前还可以
|
||||
对数据进行压缩,也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的,压缩分为两个部分,
|
||||
一部分是本地(-m)是否压缩传输,一部分是与上级(-M)传输是否压缩。
|
||||
|
||||
压缩要求两端都是proxy才可以,压缩也在一定程度上保护了(加密)数据。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
本地二级执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
本地三级执行:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
### 5.12 负载均衡
|
||||
|
||||
SOCKS代理支持上级负载均衡,多个上级重复-P参数即可。
|
||||
|
||||
`proxy socks --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.1 设置重试间隔和超时时间
|
||||
|
||||
`proxy socks --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.2 设置权重
|
||||
|
||||
`proxy socks --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.3 使用目标地址选择上级
|
||||
|
||||
`proxy socks --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.13 限速
|
||||
|
||||
限速100K,通过`-l`参数即可指定,比如:100K 2000K 1M . 0意味着无限制。
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 5.14 指定出口IP
|
||||
|
||||
`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy socks -t tcp -p :33080 --bind-listen`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy socks -t tcp -p 5.5.5.5:6666 --bind-listen`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy socks -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 5.15 级联认证
|
||||
|
||||
SOCKS5支持级联认证,-A可以设置上级认证信息。
|
||||
|
||||
上级:
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -a user:pass`
|
||||
|
||||
本地:
|
||||
|
||||
`proxy socks -T tcp -P 2.2.2.2:33080 -A user:pass -t tcp -p :33080`
|
||||
|
||||
请更多认证细节,请参考`9.API认证` 和 `10.本地认证`
|
||||
|
||||
### 5.16 证书参数使用base64数据
|
||||
|
||||
默认情况下-C,-K参数是crt证书和key文件的路径,
|
||||
|
||||
如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
|
||||
|
||||
### 5.17 智能模式
|
||||
智能模式设置,可以是intelligent|direct|parent三者之一。
|
||||
默认是:intelligent。
|
||||
每个值的含义如下:
|
||||
`--intelligent=direct`,不在blocked里面的目标都直连。
|
||||
`--intelligent=parent`,不在direct里面的目标都走上级。
|
||||
`--intelligent=intelligent`,blocked和direct里面都没有的目标,智能判断是否使用上级访问目标。
|
||||
|
||||
### 5.18 固定UDP功能端口
|
||||
|
||||
默认情况下socks5的UDP功能的端口号,proxy是按着`rfc1982草案`要求,使用协议握手过程中随机指定,不需要提前指定。
|
||||
|
||||
但是某些情况下,需要固定UDP功能端口,可以通过参数`--udp-port 端口号`用来固定UDP功能的端口号,比如:
|
||||
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080" --udp-port 38080`
|
||||
|
||||
### 5.19 查看帮助
|
||||
`proxy help socks`
|
||||
|
||||
## 6.SPS协议转换
|
||||
|
||||
### 6.1 功能介绍
|
||||
代理协议转换使用的是sps子命令,sps可以把已经存在的http(s)代理或者socks5代理或ss代理转换为一个端口同时支持http(s)和socks5和ss的代理,而且http(s)代理支持正向代理和反向代理(SNI),当上级是SOCKS5时,转换后的SOCKS5或者SS代理仍然支持UDP功能;另外对于已经存在的http(s)代理或者socks5代理,支持tls、tcp、kcp三种模式,支持链式连接,也就是可以多个sps结点层级连接构建加密通道。
|
||||
|
||||
`ss`功能支持的加密方法为:aes-128-cfb , aes-128-ctr , aes-128-gcm , aes-192-cfb , aes-192-ctr , aes-192-gcm , aes-256-cfb , aes-256-ctr , aes-256-gcm , bf-cfb , cast5-cfb , chacha20 , chacha20-ietf , chacha20-ietf-poly1305 , des-cfb , rc4-md5 , rc4-md5-6 , salsa20 , xchacha20
|
||||
|
||||
本地监听端口-p参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
提示:
|
||||
|
||||
当本地使用kcp协议时,需要用-g指定vps公网IP,socks5的UDP功能才能正常使用.这时-g是返回给客户端的UDP地址中的IP地址.
|
||||
|
||||
ss的udp功能默认关闭,可以通过--ssudp开启。socks5的udp功能默认关闭,可以通过--udp开启,默认是握手随机端口,可以通过固定一个端口提高性能,
|
||||
通过参数--udp-port 0设置,0代表随机选择一个空闲端口,也可以手动指定一个具体端口。
|
||||
|
||||
### 6.2 HTTP(S)转HTTP(S)+SOCKS5+SS
|
||||
转换后的SOCKS5或者SS代理不具备UDP功能。
|
||||
假设已经存在一个普通的http(s)代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个tls的http(s)代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,tls需要证书文件,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S http -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个kcp的http(s)代理(密码是:demo123):127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S http -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.3 SOCKS5转HTTP(S)+SOCKS5+SS
|
||||
如果上级是SOCKS5而且支持UDP功能,那么转换后的SOCKS5或者SS代理仍然支持UDP功能。
|
||||
假设已经存在一个普通的socks5代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S socks -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个tls的socks5代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,tls需要证书文件,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S socks -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个kcp的socks5代理(密码是:demo123):127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S socks -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.4 SS转HTTP(S)+SOCKS5+SS
|
||||
SPS上级和本地支持ss协议,上级可以是SPS或者标准的ss服务,转换后的SOCKS5或者SS代理不具备UDP功能。
|
||||
假设已经存在一个普通的SS或者SPS代理(开启了ss,加密方式:aes-256-cfb,密码:demo):127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,转换后的ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S ss -H aes-256-cfb -J pass -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`。
|
||||
|
||||
### 6.5 链式连接
|
||||
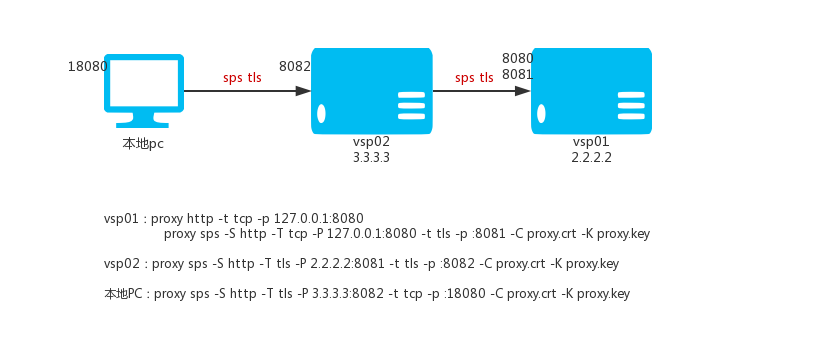
|
||||
上面提过多个sps结点可以层级连接构建加密通道,假设有如下vps和家里的pc电脑。
|
||||
vps01:2.2.2.2
|
||||
vps02:3.3.3.3
|
||||
现在我们想利用pc和vps01和vps02构建一个加密通道,本例子用tls加密也可以用kcp,在pc上访问本地18080端口就是访问vps01的本地8080端口。
|
||||
首先在vps01(2.2.2.2)上我们运行一个只有本地可以访问的http(s)代理,执行:
|
||||
`proxy http -t tcp -p 127.0.0.1:8080`
|
||||
|
||||
然后在vps01(2.2.2.2)上运行一个sps结点,执行:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tls -p :8081 -C proxy.crt -K proxy.key`
|
||||
|
||||
然后在vps02(3.3.3.3)上运行一个sps结点,执行:
|
||||
`proxy sps -S http -T tls -P 2.2.2.2:8081 -t tls -p :8082 -C proxy.crt -K proxy.key`
|
||||
|
||||
然后在pc上运行一个sps结点,执行:
|
||||
`proxy sps -S http -T tls -P 3.3.3.3:8082 -t tcp -p :18080 -C proxy.crt -K proxy.key`
|
||||
|
||||
完成。
|
||||
|
||||
### 6.6 认证功能
|
||||
sps支持http(s)\socks5代理认证,可以级联认证,有四个重要的信息:
|
||||
1:用户发送认证信息`user-auth`。
|
||||
2:设置的本地认证信息`local-auth`。
|
||||
3:设置的连接上级使用的认证信息`parent-auth`。
|
||||
4:最终发送给上级的认证信息`auth-info-to-parent`。
|
||||
他们的情况关系如下:
|
||||
|
||||
| user-auth | local-auth | parent-auth | auth-info-to-paren
|
||||
| ------ | ------ | ------ | ------
|
||||
| 有/没有 | 有 | 有 | 来自parent-auth
|
||||
| 有/没有 | 没有 | 有 | 来自parent-auth
|
||||
| 有/没有 | 有 | 没有 | 无
|
||||
| 没有 | 没有 | 没有 | 无
|
||||
| 有 | 没有 | 没有 | 来自user-auth
|
||||
|
||||
对于sps代理我们可以进行用户名密码认证,认证的用户名和密码可以在命令行指定
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0:0:"`
|
||||
多个用户,重复-a参数即可。
|
||||
也可以放在文件中,格式是一行一个`用户名:密码:连接数:速率:上级`,然后用-F指定。
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
如果上级有认证,下级可以通过-A参数设置认证信息,比如:
|
||||
上级:`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0:0:"`
|
||||
下级:`proxy sps -S http -T tcp -P 127.0.0.1:8080 -A "user1:pass1" -t tcp -p ":33080" `
|
||||
|
||||
请更多认证细节,请参考`9.API认证` 和 `10.本地认证`
|
||||
|
||||
### 6.7 多个上级
|
||||
|
||||
如果存在多个上级,可以通过多个-P指定。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy sps -P http://127.0.0.1:3100 -P socks5://127.0.0.1:3200`
|
||||
|
||||
`-P`完整格式如下:
|
||||
|
||||
`protocol://a:b@2.2.2.2:33080#1`
|
||||
|
||||
下面对每部分进行解释:
|
||||
|
||||
`protocol://` 是协议类型,可能的类型以及含有如下:
|
||||
|
||||
```text
|
||||
http 等价于 -S http -T tcp
|
||||
https 等价于 -S http -T tls --parent-tls-single , 也就是http(s)代理 over TLS
|
||||
https2 等价于 -S http -T tls
|
||||
socks5 等价于 -S socks -T tcp
|
||||
socks5s 等价于 -S socks -T tls --parent-tls-single , 也就是socks over TLS
|
||||
socks5s2 等价于 -S socks -T tls
|
||||
ss 等价于 -S ss -T tcp
|
||||
httpws 等价于 -S http -T ws
|
||||
httpwss 等价于 -S http -T wss
|
||||
socks5ws 等价于 -S socks -T ws
|
||||
socks5wss 等价于 -S socks -T wss
|
||||
```
|
||||
|
||||
`a:b`是代理认证的用户名密码,如果是ss,`a`是加密方法,`b`是密码,没有用户名密码可以留空比如:`http://2.2.2.2:33080`,如果用户名和密码保护特殊符号可以使用urlencode进行编码。
|
||||
|
||||
`2.2.2.2:33080`是上级地址,格式是:`IP(或域名):端口`,如果底层是ws/wss协议还可以带上路径,比如:`2.2.2.2:33080/ws`;
|
||||
还能通过附加查询参数`m`和`k`设置`ws\wss`的`加密方法`和`密码`,比如:`2.2.2.2:33080/ws?m=aes-192-cfb&k=password`
|
||||
|
||||
`#1`多个上级的负载均衡是权重策略时候,设置的权重,很少用到。
|
||||
|
||||
### 6.8 自定义加密
|
||||
proxy的sps代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行
|
||||
自定义加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义
|
||||
一个密码即可,加密分为两个部分,一部分是本地(-z)是否加密解密,一部分是与上级(-Z)传输是否加密解密。
|
||||
|
||||
自定义加密要求两端都是proxy才可以。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
假设已经存在一个http(s)代理:`6.6.6.6:6666`
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
本地二级执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
本地三级执行:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
### 6.9 压缩传输
|
||||
proxy的sps代理在tcp之上可以通过自定义加密和tls标准加密以及kcp协议加密tcp数据,在自定义加密之前还可以
|
||||
对数据进行压缩,也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的,压缩分为两个部分,
|
||||
一部分是本地(-m)是否压缩传输,一部分是与上级(-M)传输是否压缩。
|
||||
|
||||
压缩要求两端都是proxy才可以,压缩也在一定程度上保护了(加密)数据。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
本地二级执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
本地三级执行:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
### 6.10 禁用协议
|
||||
SPS默认情况下一个端口支持http(s)和socks5两种代理协议,我们可以通过参数禁用某个协议
|
||||
比如:
|
||||
1.禁用HTTP(S)代理功能只保留SOCKS5代理功能,参数:`--disable-http`。
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-http`
|
||||
|
||||
1.禁用SOCKS5代理功能只保留HTTP(S)代理功能,参数:`--disable-socks`。
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-socks`
|
||||
|
||||
### 6.11 限速
|
||||
|
||||
假设存在SOCKS5上级:
|
||||
|
||||
`proxy socks -p 2.2.2.2:33080 -z password -t tcp`
|
||||
|
||||
sps下级,限速100K
|
||||
|
||||
`proxy sps -S socks -P 2.2.2.2:33080 -T tcp -Z password -l 100K -t tcp -p :33080`
|
||||
|
||||
通过`-l`参数即可指定,比如:100K 2000K 1M . 0意味着无限制。
|
||||
|
||||
### 6.12 指定出口IP
|
||||
|
||||
`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy sps -t tcp -p :33080 --bind-listen`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy sps -t tcp -p 5.5.5.5:6666 --bind-listen`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy sps -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 6.13 证书参数使用base64数据
|
||||
|
||||
默认情况下-C,-K参数是crt证书和key文件的路径,
|
||||
|
||||
如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
|
||||
### 6.14 独立服务
|
||||
sps一个端口可完成完整功能的代理`http(s)\socks\ss`功能。
|
||||
下面这个命令,就是一键开启http(s)\ss\socks服务,同时开启socks5的udp和ss的udp功能。
|
||||
`proxy sps -p :33080 --ssudp --udp --udp-port 0`
|
||||
|
||||
### 6.15 目标重定向
|
||||
sps功能提供的http(s)\socks5\ss代理功能,客户端通过sps代理去连接指定的“目标”,这个“目标”一般是网站也可能是任意的tcp地址,
|
||||
网站”目标“一般是foo.com:80,foo.com:443,sps支持使用--rewrite参数指定一个“目标”重定向规则文件,对目标进行重定向,客户端是无感知的,
|
||||
比如你对“目标”:demo.com:80重定向到192.168.0.12:80,那么客户端访问网站demo.com,其实访问的是192.168.0.12提供的网站服务。
|
||||
“目标”重定向规则文件示例:
|
||||
|
||||
```text
|
||||
# example
|
||||
www.a.com:80 10.0.0.2:8080
|
||||
**.b.com:80 10.0.0.2:80
|
||||
192.168.0.11:80 10.0.0.2:8080
|
||||
```
|
||||
|
||||
### 6.16 固定UDP功能端口
|
||||
|
||||
默认情况下sps的socks5的UDP功能的端口号是按着`rfc1982草案`要求,使用协议握手过程中随机指定,不需要提前指定。
|
||||
|
||||
但是某些情况下,需要固定UDP功能端口,可以通过参数`--udp-port 端口号`用来固定UDP功能的端口号,比如:
|
||||
|
||||
`proxy sps -t tcp -p "0.0.0.0:38080" --udp-port 38081`
|
||||
|
||||
需要注意的是,sps的ss功能也有UDP功能,而且ss的UDP端口和tcp端口是一样的,所以要避免socks5的UDP端口和ss的UDP端口冲突,
|
||||
|
||||
要指定和tcp端口不一样的端口。
|
||||
|
||||
### 6.17 iptables 透明代理
|
||||
sps模式支持Linux系统的iptables转发支持,也就是通常所说的iptables透明代理,如果在网关设备上进行iptables透明代理,那么对通过网关联网的设备就能实现无感知的代理。
|
||||
|
||||
启动命令实例:
|
||||
|
||||
`proxy sps --redir -p :8888 -P httpws://1.1.1.1:33080`
|
||||
|
||||
这里假设存在一个http的上级代理1.1.1.1:33080,使用ws传输数据。
|
||||
|
||||
然后添加iptables规则,下面是参考规则:
|
||||
```shell
|
||||
#上级proxy服务端服务器IP地址:
|
||||
proxy_server_ip=1.1.1.1
|
||||
|
||||
#路由器运行proxy监听的端口:
|
||||
proxy_local_port=33080
|
||||
|
||||
#下面的就不用修改了
|
||||
#create a new chain named PROXY
|
||||
iptables -t nat -N PROXY
|
||||
|
||||
# Ignore your PROXY server's addresses
|
||||
# It's very IMPORTANT, just be careful。
|
||||
|
||||
iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
# Ignore LANs IP address
|
||||
iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
# Anything to port 80 443 should be redirected to PROXY's local port
|
||||
iptables -t nat -A PROXY -p tcp -j REDIRECT --to-ports $proxy_local_port
|
||||
# Apply the rules to nat client
|
||||
iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
# Apply the rules to localhost
|
||||
iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
- 清空整个链 iptables -F 链名比如iptables -t nat -F PROXY
|
||||
- 删除指定的用户自定义链 iptables -X 链名 比如 iptables -t nat -X PROXY
|
||||
- 从所选链中删除规则 iptables -D 链名 规则详情 比如 iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 6.18 查看帮助
|
||||
|
||||
`proxy help sps`
|
||||
|
||||
## 7.KCP配置
|
||||
|
||||
### 7.1 配置介绍
|
||||
proxy的很多功能都支持kcp协议,凡是使用了kcp协议的功能都支持这里介绍的配置参数。
|
||||
所以这里统一对KCP配置参数进行介绍。
|
||||
|
||||
### 7.2 详细配置
|
||||
所有的KCP配置参数共有17个,你可以都不用设置,他们都有默认值,如果为了或者最好的效果,
|
||||
就需要自己根据自己根据网络情况对参数进行配置。由于kcp配置很复杂需要一定的网络基础知识,
|
||||
如果想获得kcp参数更详细的配置和解说,请自行搜索。每个参数的命令行名称以及默认值和简单的功能说明如下:
|
||||
```
|
||||
--kcp-key="secrect" pre-shared secret between client and server
|
||||
--kcp-method="aes" encrypt/decrypt method, can be: aes, aes-128, aes-192, salsa20, blowfish,
|
||||
twofish, cast5, 3des, tea, xtea, xor, sm4, none
|
||||
--kcp-mode="fast" profiles: fast3, fast2, fast, normal, manual
|
||||
--kcp-mtu=1350 set maximum transmission unit for UDP packets
|
||||
--kcp-sndwnd=1024 set send window size(num of packets)
|
||||
--kcp-rcvwnd=1024 set receive window size(num of packets)
|
||||
--kcp-ds=10 set reed-solomon erasure coding - datashard
|
||||
--kcp-ps=3 set reed-solomon erasure coding - parityshard
|
||||
--kcp-dscp=0 set DSCP(6bit)
|
||||
--kcp-nocomp disable compression
|
||||
--kcp-acknodelay be carefull! flush ack immediately when a packet is received
|
||||
--kcp-nodelay=0 be carefull!
|
||||
--kcp-interval=50 be carefull!
|
||||
--kcp-resend=0 be carefull!
|
||||
--kcp-nc=0 be carefull! no congestion
|
||||
--kcp-sockbuf=4194304 be carefull!
|
||||
--kcp-keepalive=10 be carefull!
|
||||
```
|
||||
提示:
|
||||
参数:--kcp-mode中的四种fast3, fast2, fast, normal模式,
|
||||
相当于设置了下面四个参数:
|
||||
normal:`--nodelay=0 --interval=40 --resend=2 --nc=1`
|
||||
fast :`--nodelay=0 --interval=30 --resend=2 --nc=1`
|
||||
fast2:`--nodelay=1 --interval=20 --resend=2 --nc=1`
|
||||
fast3:`--nodelay=1 --interval=10 --resend=2 --nc=1`
|
||||
|
||||
## 8.安全DNS
|
||||
|
||||
### 8.1 介绍
|
||||
众所周知DNS是UDP端口53提供的服务,但是随着网络的发展一些知名DNS服务器也支持TCP方式dns查询,比如谷歌的8.8.8.8,proxy的DNS防污染服务器原理就是在本地启动一个proxy的DNS代理服务器,它用TCP的方式通过上级代理进行dns查询。如果它和上级代理通讯采用加密的方式,那么就可以进行安全无污染的DNS解析,还支持独立服务,并发解析,支持增强的hosts文件功能支持灵活的并发解析转发。
|
||||
|
||||
dns解析顺序:
|
||||
1.使用参数--hosts解析。
|
||||
2.要解析的域名在1中没有找到,就使用参数--forward规则解析。
|
||||
3.要解析的域名在1和2中都没有找到,就使用默认--default解析,--default默认行为参数值有三种:proxy,direct,system。
|
||||
三种参数值解释如下:
|
||||
proxy:通过上级去连接-q参数指定的dns服务器去解析域名。
|
||||
direct:通过本地网络去连接-q参数指定的dns服务器去解析域名。
|
||||
system:通过系统dns去解析域名。
|
||||
|
||||
提示:
|
||||
--hosts 参数指定的host文件格式和系统hosts文件一致,而且域名支持通配符,可以参考hosts文件。
|
||||
--forward 参数指定的解析转发规则文件,格式可以参考resolve.rules文件,域名支持通配符,支持为每个域名指定多个dns服务器并发解析,谁最快解析成功就用谁的解析结果。
|
||||
-q 参数可以指定多个远程dns服务器,执行并发解析谁最快解析成功就用谁的解析结果,默认是:1.1.1.1,8.8.8.8,9.9.9.9,多个用逗号分割,
|
||||
比如还可以带端口:1.1.1.1,8.8.8.8#53,9.9.9.9
|
||||
|
||||
如果独立服务,不需要上级:
|
||||
可以执行:
|
||||
`proxy dns --default system -p :5353`
|
||||
or
|
||||
`proxy dns --default direct -p :5353`
|
||||
|
||||
### 8.2 使用示例
|
||||
|
||||
#### 8.2.1 普通HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
本地执行:
|
||||
`proxy dns -S http -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了DNS解析功能。
|
||||
|
||||
#### 8.2.2 普通SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
本地执行:
|
||||
`proxy dns -S socks -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了DNS解析功能。
|
||||
|
||||
#### 8.2.3 TLS加密的HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy http -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S http -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.4 TLS加密的SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy socks -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S socks -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.5 KCP加密的HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy http -t kcp -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S http -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.6 KCP加密的SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy socks -t kcp -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S socks -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.7 自定义加密的HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy http -t tcp -p :33080 -z password`
|
||||
本地执行:
|
||||
`proxy dns -S http -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.8 自定义加密的SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy socks -t kcp -p :33080 -z password`
|
||||
本地执行:
|
||||
`proxy dns -S socks -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
## 9.API认证,限速,控制连接数,限流量
|
||||
|
||||
proxy的http(s)/socks5/sps代理功能,支持通过API控制用户对代理对访问。
|
||||
|
||||
### 通过API可以干什么?
|
||||
|
||||
- 用户维度,控制单个连接速率,控制最大连接数。
|
||||
- IP维度,控制单个连接速率,控制最大连接数。
|
||||
- 动态上级,可以根据用户或者客户端IP,动态的从API获取其上级,支持http(s)/socks5/ss上级。
|
||||
- 认证每一个连接,无论是否要求客户端认证。
|
||||
- 缓存认证结果,时间可以设置,减轻API压力。
|
||||
|
||||
#### 具体使用
|
||||
proxy的http(s)/socks5/sps代理API功能,通过`--auth-url`和`--auth-nouser`和`--auth-cache`三个参数控制。
|
||||
参数`--auth-url`是HTTP API接口地址,客户端连接的时候,proxy会GET方式请求这url,带上下面参数,如果返回HTTP状态码204,代表认证成功,其它情况认为认证失败。
|
||||
|
||||
一个完整的请求API的示例:
|
||||
`http://test.com/auth.php?user=a&pass=b&client_addr=127.0.0.1:49892&local_addr=127.0.0.1:8100&target=http%3A%2F%2Fwww.baidu.com&service=http&sps=0`
|
||||
|
||||
#### 参数说明
|
||||
`user和pass` 当代理开启了认证功能,这里就是客户端提供的用户名和密码。
|
||||
`client_addr` 客户端访问代理时的用的地址,格式IP:端口。
|
||||
`local_addr` 客户端访问的代理地址,格式IP:端口。
|
||||
`service` 代理类型,分为:http、socks。
|
||||
`sps` 代理是否是sps提供的,1:是,0:否。
|
||||
`target` 客户端要访问的目标,如果是http(s)代理,target是访问的具体url;如果是socks5代理,target是空。
|
||||
|
||||
#### 示例
|
||||
假设--auth-url http://127.0.0.1:333/auth.php 指向了一个php接口地址.
|
||||
auth.php内容如下:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#设置所有的用户名密码,前面是用户名,后面是对应密码
|
||||
$alluser=[
|
||||
"user1"=>"pass1",
|
||||
"user2"=>"pass2",
|
||||
"user3"=>"pass3",
|
||||
"user4"=>"pass4",
|
||||
];
|
||||
$proxy_ip=$_GET['local_addr'];
|
||||
$user_ip=$_GET['client_addr'];
|
||||
$service=$_GET['service'];
|
||||
$is_sps=$_GET['sps']=='1';
|
||||
$user=$_GET['user'];
|
||||
$pass=$_GET['pass'];
|
||||
$target=$_GET['target'];
|
||||
//业务逻辑判断
|
||||
//....
|
||||
$ok=false;
|
||||
foreach ($alluser as $dbuser => $dbpass) {
|
||||
if ($user==$dbuser&&$pass==$dbpass){
|
||||
$ok=true;
|
||||
break;
|
||||
}
|
||||
}
|
||||
//设置认证结果
|
||||
if($ok){
|
||||
header("userconns:1000");
|
||||
header("ipconns:2000");
|
||||
header("userrate:3000");
|
||||
header("iprate:8000");
|
||||
header("UPSTREAM:http://127.0.0.1:3500?parent-type=tcp");
|
||||
header("HTTP/1.1 204 No Content");
|
||||
}
|
||||
```
|
||||
|
||||
#### 解释
|
||||
userconns:用户的最大连接数,不限制为0或者不设置这个头部。
|
||||
ipconns:用户IP的最大连接数,不限制为0或者不设置这个头部。
|
||||
userrate:用户的单个TCP连接速率限制,单位:字节/秒,不限制为0或者不设置这个头部。
|
||||
iprate:用户IP的单个TCP连接速率限制,单位:字节/秒,不限制为0或者不设置这个头部。
|
||||
upstream:使用的上级,没有为空,或者不设置这个头部。
|
||||
|
||||
#### 提示
|
||||
1.默认情况下,设置了`--auth-url`是强制要求客户端提供用户名和密码的;如果不需要强制要求客户端提供用户名密码,并认证,可以加上`--auth-nouser`,每次访问仍然会访问认证地址`--auth-url`进行认证,当客户端没有发生认证信息当时候,php接口里面接收的$user认证用户名和$pass认证密码都为空。
|
||||
2.连接数限制优先级:用户认证文件连接数限制-》文件ip.limit连接数限制-》API用户连接数限制-》API的IP连接数限制-》命令行全局连接数限制。
|
||||
3.速率限制优先级:用户认证文件速率限制-》文件ip.limit速率限制-》API用户速率限制-》API的IP速率限制-》命令行全局速率限制。
|
||||
3.上级获取优先级:用户认证文件的upstream-》文件ip.limit的upstream-》API的upstream-》命令行指定的上级。
|
||||
4.`--auth-cache`认证缓存,对认证结果缓存一定时间,提升性能,降低认证接口压力,--auth-cache 单位秒,默认0, 设置0是关闭缓存。
|
||||
|
||||
#### upstream详细说明
|
||||
|
||||
1.当参数`sps`是0的时候。
|
||||
service是http时,upstream只支持http(s)代理,不支持认证,如需要认证可以用sps代替,格式:
|
||||
`http://127.0.0.1:3100?argk=argv`
|
||||
service是socks时,upstream只支持socks5代理,格式:
|
||||
`socks5://127.0.0.1:3100?argk=argv`
|
||||
|
||||
解释:`http://`,`socks5://` 是固定的,`127.0.0.1:3100`是上级的地址
|
||||
|
||||
2.当`sps`是1的时候。
|
||||
upstream支持socks5、http(s)代理,支持认证,格式:`protocol://a:b@2.2.2.2:33080?argk=argv`,具体介绍请参考SPS章节的,**多个上级**,`-P`参数的说明。
|
||||
3.参数,`?`后面`argk=argv`是参数:参数名称=参数值,多个参数用`&`连接。
|
||||
支持的所有参数如下,和命令行同名参数意义一致。
|
||||
1. parent-type : 上级底层传输类型,支持 tcp,tls,ws,wss。
|
||||
2. parent-ws-method : 上级底层ws传输类型的加密方法,支持的值和命令行支持的值范围一样。
|
||||
3. parent-ws-password : 上级底层ws传输类型的加密密码,数字字母组成的密码。
|
||||
4. parent-tls-single : 上级底层tls传输类型是否是单向tls,可以是:true | false。
|
||||
5. timeout : 建立tcp连接的超时时间,数字,单位毫秒。
|
||||
6. ca : 上级底层tls传输类型的ca证书文件经过base64编码后的字符串。
|
||||
7. cert : 上级底层tls传输类型的证书文件经过base64编码后的字符串。
|
||||
8. key : 上级底层tls传输类型的证书密钥文件经过base64编码后的字符串。
|
||||
|
||||
### 流量上报/流量统计/流量限制
|
||||
|
||||
proxy的http(s)/socks5/sps/tcp/udp代理功能支持流量上报,可以通过参数`--traffic-url`设置一个http接口地址。
|
||||
proxy会把连接使用的流量上报到这个地址,具体情况是,proxy发送一个HTTP到GET请求到`--traffic-url`设置的HTTP URL地址.
|
||||
上报模式有两种,可以通过`--traffic-mode`参数指定,可以是`normal`普通模式上报,也可以是`fast`快速模式上报。
|
||||
1. `normal`普通模式上报
|
||||
当连接释放时,proxy会把此次连接使用的流量上报到这个`--traffic-url`地址.
|
||||
2. `fast`快速模式上报
|
||||
对已经建立的每个连接,proxy会`定时`把这个连接产生的流量上报到这个这个`--traffic-url`地址.
|
||||
`定时`默认是5秒,可以通过参数`--traffic-interval`修改`定时`为合适的秒数。
|
||||
流量上报功能结合上面的API认证功能可以实现实时控制用户的流量使用,流量统计,流量限制;流量上报到接口,接口把流量数据写入数据库,然后认证API查询数据库判断用户或者IP流量使用情况,用来确定用户是否可以认证成功.
|
||||
|
||||
下面是一个完整的URL请求实例:
|
||||
|
||||
`http://127.0.0.1:33088/user/traffic?bytes=337&client_addr=127.0.0.1%3A51035&id=http&server_addr=127.0.0.1%3A33088&target_addr=myip.ipip.net%3A80&username=a`
|
||||
|
||||
请求参数说明:
|
||||
id: 服务id标志.
|
||||
server_addr: 客户端请求的代理地址,格式: `IP:端口`.
|
||||
client_addr: 客户端地址,格式: `IP:端口`.
|
||||
target_addr: 目标地址,格式: `IP:端口`,tcp/udp代理时,这个是空.
|
||||
username: 代理认证用户名,tcp/udp代理时,这个是空.
|
||||
bytes: 此次使用的流量字节数.
|
||||
|
||||
#### 提示
|
||||
|
||||
访问的`--traffic-url`地址接口必须返回HTTP状态码`204`,流量上报才认为上报成功,返回其它状态码将认为上报流量失败,会输出相关日志。
|
||||
|
||||
#### 流量上报原理
|
||||
|
||||
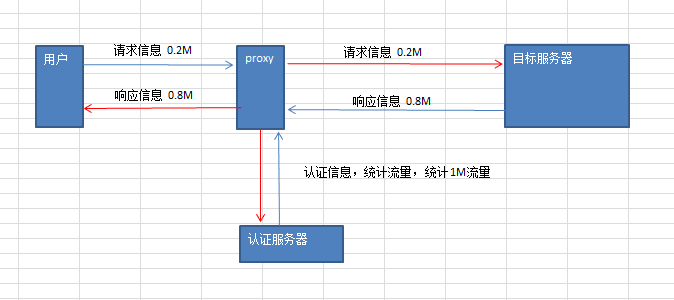
|
||||
|
||||
### 主动断开用户连接
|
||||
|
||||
proxy的http(s)/socks5/sps代理功能支持`控制接口`,可以通过参数`--control-url`指定的http接口地址,
|
||||
那么proxy就会`定期`的把当前连接到proxy的全部用户名或客户端IP发送到此URL,具体情况是,proxy发送一个HTTP的POST请求到`--control-url`设置的HTTP URL地址.`定期`默认是30秒,可以通过`--control-sleep`参数修改此值。
|
||||
当用户过期,或者用户流量已经用完,通过认证API只能控制用户不能新建连接,但是已经和proxy建立当连接没法立刻断开,
|
||||
那么通过控制接口可以解决这个问题,控制接口会在最慢`定期`时间内通过控制接口返回的内容,结束已经无效的用户建立的连接。
|
||||
|
||||
#### 控制接口请求说明
|
||||
|
||||
proxy会向控制接口URL发送一个HTTP POST请求,表单数据中有两个字段:user和ip。
|
||||
|
||||
user:当前连接到proxy的用户名,多个使用英文逗号分割,比如:user1,user2
|
||||
|
||||
ip:当前连接到proxy的客户端ip地址,多个使用英文逗号分割,比如:1.1.1.1,2.2.2.2
|
||||
|
||||
#### 控制接口返回数据说明
|
||||
|
||||
控制接口返回的数据是无效的用户和IP,格式是一个json对象数据,有两个字段user和ip。
|
||||
|
||||
比如:{"user":"a,b","ip":""}
|
||||
|
||||
user:当前连接到proxy的用户名,多个使用英文逗号分割,没有留空,比如:user1,user2
|
||||
|
||||
ip:当前连接到proxy的客户端ip地址,多个使用英文逗号分割,没有留空,比如:1.1.1.1,2.2.2.2
|
||||
|
||||
返回的用户和ip已经建立的连接会被proxy断开。
|
||||
|
||||
#### 示例
|
||||
假设--control-url `http://127.0.0.1:33088/user/control.php` 指向了一个php接口地址.
|
||||
control.php内容如下:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#接收proxy post过来的数据
|
||||
$userArr=explode(",",$_POST['user']);
|
||||
$ipArr=$_GET['ip'];
|
||||
|
||||
//无效用户列表
|
||||
$badUsers=[];
|
||||
|
||||
foreach ($userArr as $user) {
|
||||
//逻辑判断用户$user是否无效,如果无效就放入$badUsers
|
||||
$badUsers[]=$user;
|
||||
}
|
||||
$data=["user"=>implode(","$badUsers),"ip"=>""];
|
||||
|
||||
echo json_encode($data);
|
||||
```
|
||||
|
||||
### 使用代理
|
||||
|
||||
http(s)/socks5/sps认证API(`--auth-url`)、控制API(`--control-url`)、流量上报API(`--traffic-url`)三个地址的访问,支持通过代理访问,参数是:`--auth-proxy`,格式和`--jumper`格式一致,详细详细请参考`--jumper`。
|
||||
|
||||
## 10.本地认证,限速,控制连接数
|
||||
|
||||
proxy的http(s)/socks5/sps代理功能,支持通过配置文件控制用户对代理对访问,支持开启http(s)代理``Proxy Basic 代理认证`,socks5代理认证。
|
||||
|
||||
### 开始使用
|
||||
proxy的http(s)/socks5/sps代理功能可以通过
|
||||
`--auth-file`,`--max-conns`,`--ip-limit`,`--rate-limit`,`-a`这五个参数控制。
|
||||
|
||||
#### 参数详细解释
|
||||
|
||||
##### `--auth-file`
|
||||
认证的用户名和密码文件,该参数指定一个文件,一行一条规则,格式是:"用户名:密码:连接数:速率:上级"。
|
||||
`连接数`是用户最大连接数,`速率`是用户每个tcp连接最大速度,单位是:字节/秒,`上级`是用户使用的上级。
|
||||
不仅可以通过`--auth-file`设置认证用户,也可以直接用`-a`参数设置,多个用户就重复多个`-a`参数即可。
|
||||
比如:`proxy http -a a:b:0:0: -a c:d:0:0:`
|
||||
|
||||
实例解释:
|
||||
比如:`user:pass:100:10240:http://192.168.1.1:3100`
|
||||
`user`是认证用户名
|
||||
`pass`是认证用户密码(不能包含冒号:)
|
||||
`100`是这个用户的最大连接数,不限制写0
|
||||
`10240`是这个用户单个tcp连接的速率限制,单位是:字节/秒,不限制写0
|
||||
`http://192.168.1.1:3100`是这个用户使用的上级,没有就留空
|
||||
|
||||
##### `--max-conns`
|
||||
限制代理服务的全局最大连接数,一个数字,0为不限制,默认0。
|
||||
|
||||
##### `--ip-limit`
|
||||
控制客户端IP的连接数和连接速率,该参数指定一个文件,一行一条规则,#开头的是注视。
|
||||
示例文件ip.limit,规则格式如下:
|
||||
`127.0.0.1:100:10240:http://192.168.1.1:3100`
|
||||
规则解释:
|
||||
`127.0.0.1`是要限制的IP
|
||||
`100`是这个IP的最大连接数,不限制写0
|
||||
`10240`是IP单个tcp连接的速率限制,单位是:字节/s,不限制写0
|
||||
`http://192.168.1.1:3100`是这个IP使用的上级,没有就留空
|
||||
|
||||
##### `--rate-limit`
|
||||
限制服务的每一个tcp连接的速度,比如:100K 2000K 1M . 0意味着无限制,默认0。
|
||||
|
||||
## 11.集群管理
|
||||
|
||||
proxy支持集群管理功能,此时proxy安装在每个机器节点上作为agent,配合控制面板[`proxyadmin集群版`](https://github.com/snail007/proxy-admin-cluster),就能够实现统一管理海量机器上的proxy服务。
|
||||
|
||||
proxy如果要作为agent运行,假设控制面板的集群端口地址是:`1.1.1.1:55333`.
|
||||
|
||||
命令示例如下:
|
||||
|
||||
`proxy agent -k xxx -c 1.1.1.1:55333 -i test`
|
||||
|
||||
命令解释:
|
||||
|
||||
agent : 是功能参数,表示运行agent模式。
|
||||
|
||||
-k :和`proxyadmin集群版`通讯加密解密的密钥,这个密钥是在`proxyadmin集群版`的配置文件里面设置的。
|
||||
|
||||
-c :`proxyadmin集群版`的集群端口地址,格式:IP:端口。
|
||||
|
||||
-i : agent唯一标识,保证每个agent的都不一样,此处指定的`唯一标识`,在控制面板添加节点的时候用到,IP一栏填写这个`唯一标识`。
|
||||
如果-i不指定,默认是空,控制面板添加节点的时候IP一栏填写:agent的出口IP。
|
||||
|
||||
-u: 代理参数,默认是空。可以指定一个代理,agent会通过这个代理与cluster通讯。
|
||||
格式和`--jumper`格式一致,详细情况请参考手册中`--jumper`部分。
|
||||
|
||||
提示:
|
||||
|
||||
1.当控制面板里面配置了client服务,那么所有节点都使用相同都key那么就导致,只有一个client可以工作,为了解决这个问题,
|
||||
client服务参数里面可以通过使用占位符:`{AGENT_ID}`引用agent的id当作client的key,这样就可以保证每个客户端都有唯一的key。
|
||||
|
||||
比如client服务参数:
|
||||
|
||||
`client -T tcp -P 1.1.1.1:30000 --k {AGENT_ID}`
|
||||
|
||||
2.如果使用了代理参数`-u`,务必设置唯一标示参数`-i`,不然cluster无法区分不同的agent,agent将不能正常工作。
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1,4833 @@
|
||||
0rz.tw
|
||||
0to255.com
|
||||
0zz0.com
|
||||
1-apple.com.tw
|
||||
1000dosok.ru
|
||||
1000giri.net
|
||||
1024.inc.gs
|
||||
10conditionsoflove.com
|
||||
10musume.com
|
||||
10youtube.com
|
||||
123cha.com
|
||||
123rf.com
|
||||
123sdfsdfsdfsd.ru
|
||||
12bet.com
|
||||
12vpn.com
|
||||
141hongkong.com
|
||||
1688.com.au
|
||||
173ng.com
|
||||
177wyt.com
|
||||
17t17p.com
|
||||
1800flowers.com
|
||||
18onlygirls.com
|
||||
18virginsex.com
|
||||
1984bbs.com
|
||||
1984bbs.org
|
||||
1998cdp.org
|
||||
1bao.org
|
||||
1eew.com
|
||||
1pondo.tv
|
||||
2-hand.info
|
||||
2000fun.com
|
||||
2008xianzhang.info
|
||||
213.so
|
||||
21andy.com
|
||||
21sextury.com
|
||||
228.net.tw
|
||||
24smile.org
|
||||
2cat.twbbs.org
|
||||
2shared.com
|
||||
301works.org
|
||||
315lz.com
|
||||
32red.com
|
||||
343dy.net
|
||||
365singles.com.ar
|
||||
36rain.com
|
||||
3a5a.com
|
||||
3boys2girls.com
|
||||
3ren.ca
|
||||
3suisses.fr
|
||||
3tui.net
|
||||
4bluestones.biz
|
||||
4chan.org
|
||||
4everproxy.com
|
||||
4life.com
|
||||
4proxy.de
|
||||
4shared.com
|
||||
4sq.com
|
||||
4sqi.net
|
||||
4tube.com
|
||||
51.ca
|
||||
5278.cc
|
||||
5i01.com
|
||||
5isotoi5.org
|
||||
5maodang.com
|
||||
6-4.net
|
||||
64museum.org
|
||||
64tianwang.com
|
||||
64wiki.com
|
||||
666kb.com
|
||||
6park.com
|
||||
6v6dota.com
|
||||
7capture.com
|
||||
7cow.com
|
||||
8-d.com
|
||||
84000.co
|
||||
85cc.net
|
||||
85st.com
|
||||
881903.com
|
||||
888.com
|
||||
89-64.org
|
||||
8news.com.tw
|
||||
9001700.com
|
||||
908taiwan.org
|
||||
91porn.com
|
||||
92ccav.com
|
||||
9bis.com
|
||||
9bis.net
|
||||
9to5mac.com
|
||||
a-normal-day.com
|
||||
a5.com.ru
|
||||
aamacau.com
|
||||
aarki.net
|
||||
abc.com.py
|
||||
abc.pp.ru
|
||||
abc.xyz
|
||||
abchinese.com
|
||||
abercrombie.com
|
||||
abitno.linpie.com
|
||||
ablwang.com
|
||||
aboluowang.com
|
||||
aboutgfw.com
|
||||
ac.jiruan.net
|
||||
accounts.blogger.com
|
||||
acgkj.com
|
||||
actimes.com.au
|
||||
aculo.us
|
||||
adblockplus.org
|
||||
addictedtocoffee.de
|
||||
addthis.com
|
||||
admob.com
|
||||
adult-empire.com
|
||||
adult.friendfinder.com
|
||||
adultfriendfinder.com
|
||||
adultkeep.net
|
||||
advanscene.com
|
||||
advertfan.com
|
||||
aenhancers.com
|
||||
af.mil
|
||||
agoogleaday.com
|
||||
ahcdn.com
|
||||
aiph.net
|
||||
aisex.com
|
||||
ait.org.tw
|
||||
aiweiwei.com
|
||||
aiweiweiblog.com
|
||||
ajaxplorer.info
|
||||
ajsands.com
|
||||
akamai.net
|
||||
akamaihd.net
|
||||
akiba-online.com
|
||||
aktifhaber.com
|
||||
al-qimmah.net
|
||||
alabout.com
|
||||
alarabiya.net
|
||||
alasbarricadas.org
|
||||
aldi.co.uk
|
||||
aldi.us
|
||||
alexlur.org
|
||||
alien-ufos.com
|
||||
aliengu.com
|
||||
aliorbank.pl
|
||||
alkasir.com
|
||||
all-that-is-interesting.com
|
||||
allaboutalpha.com
|
||||
allasians.com
|
||||
allgirlsallowed.org
|
||||
alliance.org.hk
|
||||
allinfa.com
|
||||
allinfo.com
|
||||
alllaw.com
|
||||
allmovie.com
|
||||
allmusic.com
|
||||
allonlinux.free.fr
|
||||
allproducts.com.tw
|
||||
alphaporno.com
|
||||
alternate-tools.com
|
||||
altrec.com
|
||||
alvinalexander.com
|
||||
alwaysdata.com
|
||||
alwaysdata.net
|
||||
am730.com.hk
|
||||
amakings.com
|
||||
amateurhomevids.com
|
||||
amateursexy.net
|
||||
amazon.com
|
||||
amazonaws.com
|
||||
ameblo.jp
|
||||
americangreencard.com
|
||||
americorps.gov
|
||||
amiblockedornot.com
|
||||
amnesty.ca
|
||||
amnesty.org
|
||||
amnesty.org.au
|
||||
amnesty.org.il
|
||||
amnesty.org.pl
|
||||
amnesty.org.ru
|
||||
amnesty.org.uk
|
||||
amnestyusa.org
|
||||
amnyemachen.org
|
||||
amoiist.com
|
||||
ampproject.org
|
||||
amtrak.com
|
||||
amusingplanet.com
|
||||
amzs.me
|
||||
ana.co.jp
|
||||
analyze-v.com
|
||||
anchorfree.com
|
||||
ancsconf.org
|
||||
andfaraway.net
|
||||
android-x86.org
|
||||
android.com
|
||||
angel-live.com
|
||||
angularjs.org
|
||||
animalpolitico.com
|
||||
animecrazy.net
|
||||
animeshippuuden.com
|
||||
aniscartujo.com
|
||||
anobii.com
|
||||
anontext.com
|
||||
anonym.to
|
||||
anonymitynetwork.com
|
||||
anonymizer.com
|
||||
anonymouse.org
|
||||
anpopo.com
|
||||
answering-islam.org
|
||||
antd.org
|
||||
anthonycalzadilla.com
|
||||
antidrm.hpg.ig.com.br
|
||||
antiwave.net
|
||||
anying.ca
|
||||
anysex.com
|
||||
aobo.com.au
|
||||
aolchannels.aol.com
|
||||
aolnews.com
|
||||
aomiwang.com
|
||||
apetube.com
|
||||
api.linksalpha.com
|
||||
api.mobilepicture.com
|
||||
api.path.com
|
||||
api.proxlet.com
|
||||
api.supertweet.net
|
||||
apiary.io
|
||||
apidocs.linksalpha.com
|
||||
apigee.com
|
||||
app.box.com
|
||||
app.heywire.com
|
||||
app.hkatvnews.com
|
||||
appannie.com
|
||||
appleactionews.com
|
||||
appledaily.com
|
||||
appledaily.com.hk
|
||||
appledaily.com.tw
|
||||
apps.admob.com
|
||||
apps.hloli.net
|
||||
appspot.com
|
||||
aprs.net
|
||||
ar.hao123.com
|
||||
arabic-keyboard.org
|
||||
archdaily.net
|
||||
archive.is
|
||||
archive.org
|
||||
archlinuxarm.org
|
||||
arctosia.com
|
||||
areca-backup.org
|
||||
arlingtoncemetery.mil
|
||||
army.mil
|
||||
art-or-porn.com
|
||||
artifacts.com.tw
|
||||
artsy.net
|
||||
artwitter.com
|
||||
arzon.jp
|
||||
asahichinese.com
|
||||
asana.com
|
||||
asdfg.jp
|
||||
asg.to
|
||||
asiaharvest.org
|
||||
asianews.it
|
||||
asianspiss.com
|
||||
asianwomensfilm.de
|
||||
askstudent.com
|
||||
askynz.net
|
||||
assembla.com
|
||||
assembly.com
|
||||
assets-yammer.com
|
||||
astonmartinnews.com
|
||||
astrill.com
|
||||
atc.org.au
|
||||
atchinese.com
|
||||
atdmt.com
|
||||
atgfw.org
|
||||
ath.cx
|
||||
atj.org.tw
|
||||
atlaspost.com
|
||||
atnext.com
|
||||
augsburger-allgemeine.de
|
||||
auth.keyhole.com
|
||||
autoblog.com
|
||||
av100fun.com
|
||||
avaaz.org
|
||||
avast.com
|
||||
avdb.in
|
||||
avdb.tv
|
||||
avery.com
|
||||
avidemux.org
|
||||
avito.ru
|
||||
avnoma.com
|
||||
avoision.com
|
||||
avval.ir
|
||||
awardwinningfjords.com
|
||||
axureformac.com
|
||||
azerbaycan.tv
|
||||
azubu.tv
|
||||
bab-ul-islam.net
|
||||
babynet.com.hk
|
||||
backblaze.com
|
||||
backchina.com
|
||||
backpackers.com.tw
|
||||
backpage.com
|
||||
backtotiananmen.com
|
||||
badassjs.com
|
||||
badjojo.com
|
||||
badoo.com
|
||||
baidu.jp
|
||||
baixing.me
|
||||
bajarfacebook.com
|
||||
bajaryoutube.com
|
||||
balatarin.com
|
||||
ballpure.com
|
||||
bananaman.kir.jp
|
||||
bananarepublic.com
|
||||
bankmillennium.pl
|
||||
bannedbook.org
|
||||
barenakedislam.com
|
||||
barnabu.co.uk
|
||||
barracudanetworks.com
|
||||
basetimesheightdividedby2.com
|
||||
bayvoice.net
|
||||
bb.ttv.com.tw
|
||||
bbc.co
|
||||
bbc.co.uk
|
||||
bbc.com
|
||||
bbc.in
|
||||
bbcchinese.com
|
||||
bbci.co.uk
|
||||
bbg.gov
|
||||
bbs-tw.com
|
||||
bbs.cantonese.asia
|
||||
bbs.ecstart.com
|
||||
bbs.hanminzu.org
|
||||
bbs.kimy.com.tw
|
||||
bbs.morbell.com
|
||||
bbs.mychat.to
|
||||
bbs.ozchinese.com
|
||||
bbs.qmzdd.com
|
||||
bbs.sina.com
|
||||
bbs.skykiwi.com
|
||||
bbs.soul-plus.net
|
||||
bbs.tuitui.info
|
||||
bbsfeed.com
|
||||
bbsland.com
|
||||
bbsone.com
|
||||
bbtoystore.com
|
||||
bcast.co.nz
|
||||
bcc.com.tw
|
||||
bcchinese.net
|
||||
bd.zhe.la
|
||||
bdsmvideos.net
|
||||
beaconevents.com
|
||||
beanstalkapp.com
|
||||
bebo.com
|
||||
beeg.com
|
||||
behindkink.com
|
||||
beijing1989.com
|
||||
beijingspring.com
|
||||
benjaminste.in
|
||||
benjerry.com
|
||||
berlintwitterwall.com
|
||||
berm.co.nz
|
||||
beslist.nl
|
||||
bestadbid.com
|
||||
bestforchina.org
|
||||
bestgore.com
|
||||
bestofyoutube.com
|
||||
bestvpn.com
|
||||
bestvpnservice.com
|
||||
bestvpnusa.com
|
||||
bet365.com
|
||||
beta.iset.com.tw
|
||||
beta.usejump.com
|
||||
betbase1.info
|
||||
betfair.com
|
||||
betfair.com.au
|
||||
betternet.co
|
||||
bettween.com
|
||||
betvictor.com
|
||||
bewww.net
|
||||
beyondfirewall.com
|
||||
bfnn.org
|
||||
bfsh.hk
|
||||
bhg.com
|
||||
biantailajiao.com
|
||||
biantailajiao.in
|
||||
biblesforamerica.org
|
||||
bic2011.org
|
||||
big.az
|
||||
bigcommerce.com
|
||||
bigfools.com
|
||||
bignews.org
|
||||
bigsound.org
|
||||
bigtits.com
|
||||
bigtitstokyo.com
|
||||
bill.zhong.pp.ru
|
||||
bill2-software.com
|
||||
billypan.com
|
||||
billywr.com
|
||||
binaryage.com
|
||||
bind2.com
|
||||
bintray.com
|
||||
bipic.net
|
||||
birdsontwitter.com
|
||||
bit.ly
|
||||
bitbucket.org
|
||||
bitcointalk.org
|
||||
bitly.com
|
||||
bitshare.com
|
||||
bizhat.com
|
||||
bjnewlife.org
|
||||
bjs.com
|
||||
bjzc.org
|
||||
blinkx.com
|
||||
blinw.com
|
||||
blip.tv
|
||||
blockcn.com
|
||||
blockedsiteaccess.com
|
||||
blog.birdhouseapp.com
|
||||
blog.bitly.com
|
||||
blog.boxcar.io
|
||||
blog.com
|
||||
blog.conviso.com.br
|
||||
blog.davidziegler.net
|
||||
blog.dayoneapp.com
|
||||
blog.de
|
||||
blog.dribbble.com
|
||||
blog.exblog.co.jp
|
||||
blog.excite.co.jp
|
||||
blog.expofutures.com
|
||||
blog.fizzik.com
|
||||
blog.foolsmountain.com
|
||||
blog.gowalla.com
|
||||
blog.hotpotato.com
|
||||
blog.ifttt.com
|
||||
blog.instagram.com
|
||||
blog.instapaper.com
|
||||
blog.iphone-dev.org
|
||||
blog.istef.info
|
||||
blog.jackjia.com
|
||||
blog.joeyrobert.org
|
||||
blog.jp
|
||||
blog.kangye.org
|
||||
blog.kickstarter.com
|
||||
blog.kl.am
|
||||
blog.klip.me
|
||||
blog.lester850.info
|
||||
blog.lightbox.com
|
||||
blog.mongodb.org
|
||||
blog.openinkpot.org
|
||||
blog.palm.com
|
||||
blog.path.com
|
||||
blog.pathtosharepoint.com
|
||||
blog.pentalogic.net
|
||||
blog.pikchur.com
|
||||
blog.pilotmoon.com
|
||||
blog.qooza.hk
|
||||
blog.ranxiang.com
|
||||
blog.rockmelt.com
|
||||
blog.romanandreg.com
|
||||
blog.sina.com.tw
|
||||
blog.sogoo.org
|
||||
blog.sparrowmailapp.com
|
||||
blog.summify.com
|
||||
blog.syx86.cn
|
||||
blog.syx86.com
|
||||
blog.taragana.com
|
||||
blog.tiney.com
|
||||
blog.topify.com
|
||||
blog.trello.com
|
||||
blog.usa.gov
|
||||
blog.webmproject.org
|
||||
blog.wenweipo.com
|
||||
blog.writelonger.com
|
||||
blog.xuite.net
|
||||
blog.youthwant.com.tw
|
||||
blog.youxu.info
|
||||
blogblog.com
|
||||
blogcatalog.com
|
||||
blogcdn.com
|
||||
blogcity.me
|
||||
blogger.com
|
||||
blogger.com.br
|
||||
blogimg.jp
|
||||
bloglines.com
|
||||
bloglovin.com
|
||||
blogs.icerocket.com
|
||||
blogs.tampabay.com
|
||||
blogs.yahoo.co.jp
|
||||
blogsky.com
|
||||
blogsmithmedia.com
|
||||
blogspot.ca
|
||||
blogspot.ch
|
||||
blogspot.cl
|
||||
blogspot.co.id
|
||||
blogspot.co.ke
|
||||
blogspot.co.uk
|
||||
blogspot.co.za
|
||||
blogspot.com
|
||||
blogspot.com.br
|
||||
blogspot.com.co
|
||||
blogspot.com.es
|
||||
blogspot.com.ng
|
||||
blogspot.com.tr
|
||||
blogspot.cz
|
||||
blogspot.de
|
||||
blogspot.dk
|
||||
blogspot.fi
|
||||
blogspot.hk
|
||||
blogspot.hu
|
||||
blogspot.in
|
||||
blogspot.jp
|
||||
blogspot.kr
|
||||
blogspot.mx
|
||||
blogspot.no
|
||||
blogspot.ro
|
||||
blogspot.ru
|
||||
blogspot.sg
|
||||
blogspot.tw
|
||||
blogtd.net
|
||||
blogtd.org
|
||||
bloodshed.net
|
||||
bloomberg.cn
|
||||
bloomberg.com
|
||||
bloomberg.com.br
|
||||
bloomberg.de
|
||||
bloombergbusiness.com
|
||||
bloombergview.com
|
||||
bloomfortune.com
|
||||
bloomingdales.com
|
||||
blueangellive.com
|
||||
bnrmetal.com
|
||||
boardreader.com
|
||||
bobsredmill.com
|
||||
bobulate.com
|
||||
bod.asia
|
||||
bodog88.com
|
||||
bolin.netfirms.com
|
||||
bomnegocio.com
|
||||
bonbonme.com
|
||||
bond-adventures.com
|
||||
bondageco.com
|
||||
bonjourlesgeeks.com
|
||||
boobstagram.com
|
||||
book.com.tw
|
||||
bookbrowse.com
|
||||
books.com.tw
|
||||
bookshelfporn.com
|
||||
bootstrapcdn.com
|
||||
bot.nu
|
||||
botanwang.com
|
||||
botonestwitter.com
|
||||
bowenpress.com
|
||||
box.com
|
||||
box.net
|
||||
boxcdn.net
|
||||
boxpn.com
|
||||
boxun.com
|
||||
boxun.tv
|
||||
boxunblog.com
|
||||
boxunclub.com
|
||||
boyfriendtv.com
|
||||
boysfood.com
|
||||
boysmaster.com
|
||||
br.hao123.com
|
||||
br.st
|
||||
bralio.com
|
||||
branch.com
|
||||
brandonhutchinson.com
|
||||
braumeister.org
|
||||
bravoerotica.com
|
||||
bravoteens.com
|
||||
bravotube.net
|
||||
brazzers.com
|
||||
break.com
|
||||
breakingtweets.com
|
||||
breakwall.net
|
||||
briefdream.com
|
||||
brightkite.com
|
||||
briian.com
|
||||
brizzly.com
|
||||
broadbook.com
|
||||
broadpressinc.com
|
||||
brokebackasians.com
|
||||
browserscope.org
|
||||
brucewang.net
|
||||
brutaltgp.com
|
||||
bt95.com
|
||||
btdigg.org
|
||||
btspread.com
|
||||
btunnel.com
|
||||
budaedu.org
|
||||
buddhistchannel.tv
|
||||
buff.ly
|
||||
bugclub.org
|
||||
bulbous.freeserve.co.uk
|
||||
bullog.org
|
||||
bullogger.com
|
||||
bullogs.com
|
||||
bunbunhk.com
|
||||
busayari.com
|
||||
businessinsider.com
|
||||
businessinsider.com.au
|
||||
businesstimes.com.cn
|
||||
businessweek.com
|
||||
busytrade.com
|
||||
buugaa.com
|
||||
buzzhand.com
|
||||
buzztter.com
|
||||
buzzurl.jp
|
||||
bwsj.hk
|
||||
bx.tl
|
||||
bypassthe.net
|
||||
c-and-a.com
|
||||
c-est-simple.com
|
||||
c-spanvideo.org
|
||||
c1521.biz.tm
|
||||
c1522.mooo.com
|
||||
cablenews.i-cable.com
|
||||
cachvaofacebook.com
|
||||
cacnw.com
|
||||
cactusvpn.com
|
||||
caf.fr
|
||||
cafepress.com
|
||||
cafepress.com.au
|
||||
cahr.org.tw
|
||||
calameo.com
|
||||
calebelston.com
|
||||
calgarysun.com
|
||||
cam4.com
|
||||
cam4.jp
|
||||
cam4.sg
|
||||
cambio.com
|
||||
camdough.com
|
||||
cameleo.ru
|
||||
camfrog.com
|
||||
cams.com
|
||||
cams.org.sg
|
||||
canadameet.com
|
||||
canoe.ca
|
||||
canyu.org
|
||||
cao.im
|
||||
caobian.info
|
||||
caochangqing.com
|
||||
carabinasypistolas.com
|
||||
cardinalkungfoundation.org
|
||||
cargill.com
|
||||
cargurus.com
|
||||
cari.com.my
|
||||
carmotorshow.com
|
||||
cartoonmovement.com
|
||||
casatibet.org.mx
|
||||
casinobellini.com
|
||||
casinoking.com
|
||||
casinoriva.com
|
||||
caspion.com
|
||||
cat-world.com.au
|
||||
catcatbox.com
|
||||
catch22.net
|
||||
catfightpayperview.xxx
|
||||
cathnews.com
|
||||
catholic.org.hk
|
||||
catholic.org.tw
|
||||
cathvoice.org.tw
|
||||
cattt.com
|
||||
cbc.ca
|
||||
cbs.ntu.edu.tw
|
||||
cbsnews.com
|
||||
cbtc.org.hk
|
||||
ccavtop10.com
|
||||
ccdtr.org
|
||||
ccim.org
|
||||
cclife.org
|
||||
ccthere.com
|
||||
cctongbao.com
|
||||
ccue.ca
|
||||
ccue.com
|
||||
cdbook.org
|
||||
cdd.me
|
||||
cdef.org
|
||||
cdig.info
|
||||
cdjp.org
|
||||
cdn.embedly.com
|
||||
cdn.optimizely.com
|
||||
cdn.printfriendly.com
|
||||
cdn.softlayer.net
|
||||
cdn.sstatic.net
|
||||
cdn.staticstuff.net
|
||||
cdn.v2ex.com
|
||||
cdnews.com.tw
|
||||
cdninstagram.com
|
||||
cdp.sinica.edu.tw
|
||||
cdp1989.org
|
||||
cdp1998.org
|
||||
cdp2006.org
|
||||
cdpa.url.tw
|
||||
cdpeu.org
|
||||
cdpusa.org
|
||||
cdpweb.org
|
||||
cdpwu.org
|
||||
cduniverse.com
|
||||
cdw.com
|
||||
cecc.gov
|
||||
celebritymovieblog.com
|
||||
cellulo.info
|
||||
cenci.tk
|
||||
cenews.eu
|
||||
centralnation.com
|
||||
centurys.net
|
||||
certificate-transparency.org
|
||||
certificate.revocationcheck.com
|
||||
cfhks.org.hk
|
||||
cftfc.com
|
||||
cgdepot.org
|
||||
cgst.edu
|
||||
ch.shvoong.com
|
||||
chacha.com
|
||||
chandoo.org
|
||||
change.org
|
||||
changp.com
|
||||
chaos.e-spacy.com
|
||||
chapm25.com
|
||||
charter.com
|
||||
chaturbate.com
|
||||
chengmingmag.com
|
||||
chenguangcheng.com
|
||||
chenpokong.com
|
||||
cherrysave.com
|
||||
chevronwp7.com
|
||||
chhongbi.org
|
||||
chicagoncmtv.com
|
||||
china-labour.org.hk
|
||||
china-week.com
|
||||
china101.com
|
||||
china18.org
|
||||
china21.com
|
||||
china21.org
|
||||
china5000.us
|
||||
chinaaffairs.org
|
||||
chinaaid.me
|
||||
chinaaid.net
|
||||
chinaaid.org
|
||||
chinaaid.us
|
||||
chinabuye.com
|
||||
chinachange.org
|
||||
chinachannel.hk
|
||||
chinacomments.org
|
||||
chinadigitaltimes.net
|
||||
chinaeweekly.com
|
||||
chinafreepress.org
|
||||
chinagate.com
|
||||
chinageeks.org
|
||||
chinagfw.org
|
||||
chinagreenparty.org
|
||||
chinahorizon.org
|
||||
chinahush.com
|
||||
chinainperspective.com
|
||||
chinainperspective.net
|
||||
chinainperspective.org
|
||||
chinainterimgov.org
|
||||
chinalaborwatch.org
|
||||
chinalawandpolicy.com
|
||||
chinalawtranslate.com
|
||||
chinamule.com
|
||||
chinamz.org
|
||||
chinapress.com.my
|
||||
chinarightsia.org
|
||||
chinasocialdemocraticparty.com
|
||||
chinasoul.org
|
||||
chinatimes.com
|
||||
chinatown.com.au
|
||||
chinatweeps.com
|
||||
chinaway.org
|
||||
chinaworker.info
|
||||
chinaxchina.com
|
||||
chinayouth.org.hk
|
||||
chinayuanmin.org
|
||||
chinese-hermit.net
|
||||
chinese-memorial.org
|
||||
chinese.engadget.com
|
||||
chinese.net.au
|
||||
chinese.rfi.fr
|
||||
chinese.rnw.nl
|
||||
chinese.soifind.com
|
||||
chinesedaily.com
|
||||
chinesedailynews.com
|
||||
chinesefriendfinders.com
|
||||
chinesen.de
|
||||
chinesenewsnet.com
|
||||
chinesepen.org
|
||||
chinesetalks.net
|
||||
chingcheong.com
|
||||
chinman.net
|
||||
chithu.org
|
||||
chn.chosun.com
|
||||
chrdnet.com
|
||||
chrispederick.com
|
||||
chrispederick.net
|
||||
christianstudy.com
|
||||
christiantimes.org.hk
|
||||
christusrex.org
|
||||
chrlawyers.hk
|
||||
chrlcg-hk.org
|
||||
chrome.angrybirds.com
|
||||
chrome.com
|
||||
chromeadblock.com
|
||||
chromeexperiments.com
|
||||
chromercise.com
|
||||
chromium.org
|
||||
chubun.com
|
||||
chuizi.net
|
||||
cineastentreff.de
|
||||
cipherdyne.org
|
||||
circleofmoms.com
|
||||
circlethebayfortibet.org
|
||||
citizenlab.org
|
||||
citizenscommission.hk
|
||||
citizensradio.org
|
||||
city365.ca
|
||||
city9x.com
|
||||
citysearch.com
|
||||
civicparty.hk
|
||||
civilhrfront.org
|
||||
civiliangunner.com
|
||||
civilmedia.tw
|
||||
cjb.net
|
||||
ck101.com
|
||||
cl.d0z.net
|
||||
cl.ly
|
||||
cl.ufree.org
|
||||
classicalguitarblog.net
|
||||
classically.me
|
||||
classicscore.hut2.ru
|
||||
classmarker.com
|
||||
clb.org.hk
|
||||
clearclips.com
|
||||
clearharmony.net
|
||||
clearwisdom.net
|
||||
click.xda-developers.com
|
||||
clientsfromhell.net
|
||||
cling.omy.sg
|
||||
clinica-tibet.ru
|
||||
clip.dj
|
||||
clipfish.de
|
||||
cliphunter.com
|
||||
cloudflare.com
|
||||
cloudfront.com
|
||||
cloudfront.net
|
||||
club1069.com
|
||||
cmi.org.tw
|
||||
cmoinc.org
|
||||
cms.gov
|
||||
cmule.com
|
||||
cmule.org
|
||||
cn.calameo.com
|
||||
cn.dayabook.com
|
||||
cn.fmnnow.com
|
||||
cn.giganews.com
|
||||
cn.ibtimes.com
|
||||
cn.reuters.com
|
||||
cn.streetvoice.com
|
||||
cn.uncyclopedia.wikia.com
|
||||
cn.voa.mobi
|
||||
cn2.streetvoice.com
|
||||
cn6.eu
|
||||
cna.com
|
||||
cna.com.tw
|
||||
cnavista.com.tw
|
||||
cnd.org
|
||||
cnn.com
|
||||
cochina.co
|
||||
cochina.org
|
||||
cocoa.zonble.net
|
||||
cocoapods.org
|
||||
cocolog-nifty.com
|
||||
code1984.com
|
||||
codeboxapp.com
|
||||
codeshare.io
|
||||
codeskulptor.org
|
||||
colgate.com
|
||||
collateralmurder.com
|
||||
collateralmurder.org
|
||||
collegefashion.net
|
||||
colormyfacebook.com
|
||||
comefromchina.com
|
||||
commandarms.com
|
||||
commentshk.com
|
||||
commercebank.com
|
||||
compileheart.com
|
||||
connect.facebook.net
|
||||
connectedchina.reuters.com
|
||||
conoyo.com
|
||||
contactmagazine.net
|
||||
contests.twilio.com
|
||||
convio.net
|
||||
coobai.com
|
||||
coobay.com
|
||||
cookingtothegoodlife.com
|
||||
cool18.com
|
||||
coolaler.com
|
||||
coolder.com
|
||||
coolloud.org.tw
|
||||
coolncute.com
|
||||
corumcollege.com
|
||||
cosmiq.de
|
||||
costumesupercenter.com
|
||||
cotweet.com
|
||||
couchdbwiki.com
|
||||
coupang.com
|
||||
couverturefacebook.com
|
||||
coveringweb.com
|
||||
cpj.org
|
||||
cracked.com
|
||||
crackle.com
|
||||
crackle.com.ar
|
||||
crackle.com.br
|
||||
crackle.com.co
|
||||
crackle.com.mx
|
||||
crackle.com.ve
|
||||
crashlytics.com
|
||||
crchina.org
|
||||
crd-net.org
|
||||
creaders.net
|
||||
crocoguide.com
|
||||
crossthewall.net
|
||||
crowy.net
|
||||
csdparty.com
|
||||
css.pixnet.in
|
||||
csuchen.de
|
||||
ctfriend.net
|
||||
ctheroux.com
|
||||
cthlo.github.io
|
||||
ctitv.com.tw
|
||||
cts.com.tw
|
||||
cubicle17.com
|
||||
cuhkacs.org
|
||||
cuihua.org
|
||||
cuiweiping.net
|
||||
cultpens.com
|
||||
culture.tw
|
||||
cumlouder.com
|
||||
curvefish.com
|
||||
cvs.com
|
||||
cw.com.tw
|
||||
cwahi.net
|
||||
cyberghost.natado.com
|
||||
cyberghostvpn.com
|
||||
cylex.de
|
||||
cynscribe.com
|
||||
cytode.us
|
||||
d20pfsrd.com
|
||||
dabr.co.uk
|
||||
dabr.me
|
||||
dabr.mobi
|
||||
dadazim.com
|
||||
dadi360.com
|
||||
dafagood.com
|
||||
dafahao.com
|
||||
dailidaili.com
|
||||
dailymotion.com
|
||||
dailynews.sina.com
|
||||
dajiyuan.com
|
||||
dajiyuan.eu
|
||||
dajusha.baywords.com
|
||||
dalailama.com
|
||||
dalailama.ru
|
||||
dalailamaprotesters.info
|
||||
dalailamavisit.org.nz
|
||||
dalailamaworld.com
|
||||
dalianmeng.org
|
||||
daliulian.org
|
||||
dallasobserver.com
|
||||
danawa.com
|
||||
dancingbear.com
|
||||
danke4china.net
|
||||
danwei.org
|
||||
daolan.net
|
||||
darpa.mil
|
||||
dastrassi.org
|
||||
data-vocabulary.org
|
||||
date.fm
|
||||
datpiff.com
|
||||
david-kilgour.com
|
||||
davidslog.com
|
||||
daxa.cn
|
||||
dayaarmongol.ning.com
|
||||
daylife.com
|
||||
dcard.tw
|
||||
dcmilitary.com
|
||||
ddc.com.tw
|
||||
ddfnetwork.com
|
||||
ddhw.com
|
||||
ddoo.cc
|
||||
de-sci.org
|
||||
deck.ly
|
||||
default.secureserver.net
|
||||
definebabe.com
|
||||
delcamp.net
|
||||
delcampe.net
|
||||
deletefacebook.com
|
||||
delicious.com
|
||||
demo.opera-mini.net
|
||||
democrats.org
|
||||
derekhsu.homeip.net
|
||||
desc.se
|
||||
descargaryoutube.com
|
||||
designerol.com
|
||||
designyoutube.com
|
||||
desipapa.com
|
||||
destiny.xfiles.to
|
||||
destroy-china.jp
|
||||
destroytwitter.com
|
||||
deutsche-welle.de
|
||||
dev102.com
|
||||
developer.android.com
|
||||
developers.box.net
|
||||
deviantart.com
|
||||
deviantart.net
|
||||
devio.us
|
||||
devpn.com
|
||||
dfanning.com
|
||||
dfas.mil
|
||||
dharamsalanet.com
|
||||
dhl.de
|
||||
diaoyuislands.org
|
||||
digicert.com
|
||||
digiland.tw
|
||||
digitalnomadsproject.org
|
||||
digitalocean.com
|
||||
diigo.com
|
||||
dimitrik.free.fr
|
||||
dingoonity.org
|
||||
dinside.no
|
||||
dipity.com
|
||||
directcreative.com
|
||||
directlyrics.com
|
||||
diretta.it
|
||||
dirty.ru
|
||||
discogs.com
|
||||
discuss.com.hk
|
||||
dish.com
|
||||
disneyrollergirl.net
|
||||
disp.cc
|
||||
dit-inc.us
|
||||
dizhidizhi.com
|
||||
dizhuzhishang.com
|
||||
djangosnippets.org
|
||||
djorz.com
|
||||
dl-laby.jp
|
||||
dl.box.net
|
||||
dl.dropboxusercontent.com
|
||||
dlsite.com
|
||||
dmcdn.net
|
||||
dmm.co.jp
|
||||
dmm.com
|
||||
dns2go.com
|
||||
dnscrypt.org
|
||||
dnsimple.com
|
||||
dnssec.net
|
||||
do.co
|
||||
docker.com
|
||||
docs.chef.io
|
||||
docs.docker.com
|
||||
documentingreality.com
|
||||
dogfartnetwork.com
|
||||
dojin.com
|
||||
dok-forum.net
|
||||
dolc.de
|
||||
dolf.org.hk
|
||||
dollf.com
|
||||
domain.club.tw
|
||||
domain4ik.ru
|
||||
domainhelp.search.com
|
||||
domains.googlesyndication.com
|
||||
dongde.com
|
||||
dongtaiwang.com
|
||||
dongtaiwang.net
|
||||
dongyangjing.com
|
||||
dontfilter.us
|
||||
dontmovetochina.com
|
||||
dotheyfolloweachother.com
|
||||
dotnettwitter.com
|
||||
dotplane.com
|
||||
dotsub.com
|
||||
dotup.org
|
||||
doubleaf.com
|
||||
doubleclick.com
|
||||
doubleclick.net
|
||||
dougscripts.com
|
||||
dowei.org
|
||||
down4youtube.com
|
||||
downfacebook.com
|
||||
download.aircrack-ng.org
|
||||
download.ithome.com.tw
|
||||
doxygen.org
|
||||
dphk.org
|
||||
dpp.org.tw
|
||||
dracoola.org
|
||||
dragtimes.com
|
||||
draw.io
|
||||
drdobbs.com
|
||||
dreamcheeky.com
|
||||
dreammask.org
|
||||
drepung.org
|
||||
drewolanoff.com
|
||||
drgan.net
|
||||
dribbble.com
|
||||
dropbox.com
|
||||
dropboxstatic.com
|
||||
dropboxusercontent.com
|
||||
droplr.com
|
||||
drsunacademy.com
|
||||
drtuber.com
|
||||
dscn.info
|
||||
dslr-forum.de
|
||||
dtiblog.com
|
||||
dtic.mil
|
||||
dtiserv2.com
|
||||
duck.hk
|
||||
duckduckgo.com
|
||||
duckload.com
|
||||
duckmylife.com
|
||||
duga.jp
|
||||
duihua.org
|
||||
duihuahrjournal.org
|
||||
duoweitimes.com
|
||||
duping.net
|
||||
duplicati.com
|
||||
dupola.com
|
||||
dupola.net
|
||||
dupont.com
|
||||
dvorak.org
|
||||
dw-world.com
|
||||
dw-world.de
|
||||
dw.com
|
||||
dw.de
|
||||
dwheeler.com
|
||||
dwnews.com
|
||||
dwnews.net
|
||||
dy24k.info
|
||||
dynawebinc.com
|
||||
dyndns.org
|
||||
dz3w.com
|
||||
dzze.com
|
||||
e-classical.com.tw
|
||||
e-gold.com
|
||||
e-hentai.org
|
||||
e-info.org.tw
|
||||
e-shop.gr
|
||||
e-traderland.net
|
||||
e-travel.com
|
||||
e123.hk
|
||||
e15.cz
|
||||
eamonnbrennan.com
|
||||
earthcam.com
|
||||
earthquake.usgs.gov
|
||||
eastturkestan.com
|
||||
eastturkistan-gov.org
|
||||
eastturkistan.net
|
||||
eastturkistangovernmentinexile.us
|
||||
easybranches.com
|
||||
easybytez.com
|
||||
easyca.ca
|
||||
easypic.com
|
||||
ebony-beauty.com
|
||||
ebookbrowse.com
|
||||
ebookee.com
|
||||
echofon.com
|
||||
ecministry.net
|
||||
econ.st
|
||||
economist.com
|
||||
ecsm.vs.com
|
||||
edgecastcdn.net
|
||||
edgesuite.net
|
||||
edicypages.com
|
||||
edigitalsurvey.com
|
||||
editmysite.com
|
||||
edoors.com
|
||||
edubridge.com
|
||||
eevpn.com
|
||||
efcc.org.hk
|
||||
efksoft.com
|
||||
efmoe.com
|
||||
efukt.com
|
||||
egyig.com
|
||||
eic-av.com
|
||||
eksisozluk.com
|
||||
electionsmeter.com
|
||||
electrical-engineering-portal.com
|
||||
elementaryos.org
|
||||
elgoog.im
|
||||
eloqua.com
|
||||
elotrolado.net
|
||||
elpais.com
|
||||
elpais.com.co
|
||||
elpais.com.uy
|
||||
eltondisney.com
|
||||
emacsblog.org
|
||||
embedly.com
|
||||
embr.in
|
||||
emgn.com
|
||||
emgog.com
|
||||
emory.edu
|
||||
emule-ed2k.com
|
||||
emuparadise.me
|
||||
en.favotter.net
|
||||
en.hao123.com
|
||||
enewstree.com
|
||||
enfal.de
|
||||
engadget.com
|
||||
englishforeveryone.org
|
||||
englishfromengland.co.uk
|
||||
englishtown.com
|
||||
enormego.com
|
||||
entermap.com
|
||||
entnt.com
|
||||
eogli.org
|
||||
episcopalchurch.org
|
||||
epoch-archive.com
|
||||
epochtimes-bg.com
|
||||
epochtimes-romania.com
|
||||
epochtimes.co.id
|
||||
epochtimes.co.il
|
||||
epochtimes.co.kr
|
||||
epochtimes.com
|
||||
epochtimes.com.au
|
||||
epochtimes.com.br
|
||||
epochtimes.com.tw
|
||||
epochtimes.com.ua
|
||||
epochtimes.de
|
||||
epochtimes.fr
|
||||
epochtimes.ie
|
||||
epochtimes.jp
|
||||
epochtimes.ru
|
||||
epochtimes.se
|
||||
epochtimestr.com
|
||||
epochweekly.com
|
||||
equestriadaily.com
|
||||
equinenow.com
|
||||
erabaru.net
|
||||
eraysoft.com.tr
|
||||
erepublik.com
|
||||
erights.net
|
||||
eriversoft.com
|
||||
erktv.com
|
||||
ernestmandel.org
|
||||
ero-video.net
|
||||
eroharuhi.net
|
||||
eroprofile.com
|
||||
eroshinbo.com
|
||||
eroticsaloon.net
|
||||
esky.pl
|
||||
eslite.com
|
||||
esmas.com
|
||||
etaa.org.au
|
||||
etaiwannews.com
|
||||
etizer.org
|
||||
etools.ncol.com
|
||||
etracker.com
|
||||
ettoday.net
|
||||
eucasino.com
|
||||
eukhost.com
|
||||
eulam.com
|
||||
eurekavpt.com
|
||||
europages.fr
|
||||
evchk.wikia.com
|
||||
eventbrite.com
|
||||
eventful.com
|
||||
evernote.com
|
||||
everyday-carry.com
|
||||
everythingtwitter.com
|
||||
exblog.jp
|
||||
excelforum.com
|
||||
expatshield.com
|
||||
expedia.com
|
||||
expekt.com
|
||||
experts-univers.com
|
||||
exploader.net
|
||||
expressvpn.com
|
||||
extmatrix.com
|
||||
extrapetite.com
|
||||
extremetube.com
|
||||
eyespirit.info
|
||||
eyevio.jp
|
||||
eyny.com
|
||||
ezpc.tk
|
||||
ezpeer.com
|
||||
fabric.io
|
||||
facebook.com
|
||||
facebook.com.bd
|
||||
facebook.com.br
|
||||
facebook.com.mx
|
||||
facebook.net
|
||||
facebookquotes4u.com
|
||||
faceless.me
|
||||
facesofnyfw.com
|
||||
facesoftibetanselfimmolators.info
|
||||
fail.hk
|
||||
faithfuleye.com
|
||||
faiththedog.info
|
||||
fakku.net
|
||||
falsefire.com
|
||||
falun-co.org
|
||||
falun-ny.net
|
||||
falunart.org
|
||||
falunasia.info
|
||||
falundafa-dc.org
|
||||
falundafa-florida.org
|
||||
falundafa-nc.org
|
||||
falundafa.org
|
||||
falundafamuseum.org
|
||||
falungong.org.uk
|
||||
falunhr.org
|
||||
faluninfo.net
|
||||
falunpilipinas.net
|
||||
falunworld.net
|
||||
familyfed.org
|
||||
famunion.com
|
||||
fan-qiang.com
|
||||
fangbinxing.com
|
||||
fangeming.com
|
||||
fanglizhi.info
|
||||
fangong.org
|
||||
fangongheike.com
|
||||
fanqianghou.com
|
||||
fanqiangyakexi.net
|
||||
fanswong.com
|
||||
fanyue.info
|
||||
fapdu.com
|
||||
farwestchina.com
|
||||
fashionhotbox.com
|
||||
fashionpulis.com
|
||||
fastly.net
|
||||
fastpic.ru
|
||||
faststone.org
|
||||
favorious.com
|
||||
favotter.net
|
||||
favstar.fm
|
||||
fawanghuihui.org
|
||||
faydao.com
|
||||
fb.com
|
||||
fb.me
|
||||
fbcdn.net
|
||||
fbsbx.com
|
||||
fc2.com
|
||||
fc2blog.net
|
||||
fc2blog.us
|
||||
fc2china.com
|
||||
fdc89.jp
|
||||
feathersite.com
|
||||
feedblitz.com
|
||||
feedbooks.mobi
|
||||
feedburner.com
|
||||
feedly.com
|
||||
feeds.feedburner.com
|
||||
feeds.fileforum.com
|
||||
feeds2.feedburner.com
|
||||
feedsportal.com
|
||||
feedzshare.com
|
||||
feelssh.com
|
||||
feer.com
|
||||
feitian-california.org
|
||||
feitianacademy.org
|
||||
felixcat.net
|
||||
feministteacher.com
|
||||
fengzhenghu.com
|
||||
ff.im
|
||||
fflick.com
|
||||
fgmtv.net
|
||||
fgmtv.org
|
||||
fiberprox.eu
|
||||
filefactory.com
|
||||
fileflyer.com
|
||||
files2me.com
|
||||
fileserve.com
|
||||
fillthesquare.org
|
||||
filterbypass.me
|
||||
filthdump.com
|
||||
fimes.gr
|
||||
finalion.jp
|
||||
financetwitter.com
|
||||
findbook.tw
|
||||
findmespot.com
|
||||
fingerdaily.com
|
||||
finler.net
|
||||
fireofliberty.org
|
||||
firstfivefollowers.com
|
||||
firstmerit.com
|
||||
flagsonline.it
|
||||
flamefans.com
|
||||
flashscore.com
|
||||
flecheinthepeche.fr
|
||||
fleshbot.com
|
||||
flexibits.com
|
||||
flickr.com
|
||||
flickrhivemind.net
|
||||
flightcaster.com
|
||||
flipboard.com
|
||||
flirt.com
|
||||
fmnnow.com
|
||||
fnac.es
|
||||
fnacspectacles.com
|
||||
focustaiwan.tw
|
||||
focusvpn.com
|
||||
fofg.org
|
||||
fofldfradio.org
|
||||
fooooo.com
|
||||
footwiball.com
|
||||
forexpf.ru
|
||||
forgeofempires.com
|
||||
forum.baby-kingdom.com
|
||||
forum.cyberctm.com
|
||||
forum.idsam.com
|
||||
forum.iset.com.tw
|
||||
forum.my903.com
|
||||
forum.mymaji.com
|
||||
forum.omy.sg
|
||||
forum.palmislife.com
|
||||
forum.setty.com.tw
|
||||
forum.sina.com.hk
|
||||
forum.slime.com.tw
|
||||
forum.tvb.com
|
||||
forum4hk.com
|
||||
forums.freenas.org
|
||||
fotop.net
|
||||
fourface.nodesnoop.com
|
||||
fourthinternational.org
|
||||
foxdie.us
|
||||
foxgay.com
|
||||
foxsub.com
|
||||
foxtang.com
|
||||
fpmt-osel.org
|
||||
fpmt.org
|
||||
fpmt.tw
|
||||
fpmtmexico.org
|
||||
fqok.org
|
||||
fqrouter.com
|
||||
fr-online.de
|
||||
franceculture.fr
|
||||
franklc.com
|
||||
freakshare.com
|
||||
fredwilson.vc
|
||||
free-gate.org
|
||||
free-hada-now.org
|
||||
free-proxyserver.com
|
||||
free-ssh.com
|
||||
free.fr
|
||||
free4u.com.ar
|
||||
freealim.com
|
||||
freebase.com
|
||||
freechal.com
|
||||
freechina.net
|
||||
freedl.org
|
||||
freedom-ip.com
|
||||
freedomcollection.org
|
||||
freedomhouse.org
|
||||
freeforums.org
|
||||
freegao.com
|
||||
freehostia.com
|
||||
freelancer.com
|
||||
freelotto.com
|
||||
freeman2.com
|
||||
freemoren.com
|
||||
freemorenews.com
|
||||
freenet-china.org
|
||||
freenetproject.org
|
||||
freenewscn.com
|
||||
freeoda.com
|
||||
freeones.com
|
||||
freeopenvpn.com
|
||||
freeoz.org
|
||||
freepik.com
|
||||
freepornofreeporn.com
|
||||
freesafeip.com
|
||||
freessh.us
|
||||
freetibet.net
|
||||
freetibet.org
|
||||
freetibetanheroes.org
|
||||
freevpn.nl
|
||||
freewallpaper4.me
|
||||
freewebs.com
|
||||
freewebsubmission.com
|
||||
freeweibo.com
|
||||
freexinwen.com
|
||||
freeyellow.com
|
||||
freeyoutubeproxy.net
|
||||
frequency.com
|
||||
friendfeed-media.com
|
||||
friendfeed.com
|
||||
friends-of-tibet.org
|
||||
friendscout24.de
|
||||
friendsoftibet.org
|
||||
fring.com
|
||||
fringenetwork.com
|
||||
fromchinatousa.net
|
||||
frommel.net
|
||||
frontlinedefenders.org
|
||||
fscked.org
|
||||
fsdn.com
|
||||
fsurf.com
|
||||
ftchinese.com
|
||||
fucd.com
|
||||
fuckcnnic.net
|
||||
fucked-tube.com
|
||||
fuckgfw.com
|
||||
fuckgfw.org
|
||||
fulue.com
|
||||
funf.tw
|
||||
funny-games.biz
|
||||
funp.com
|
||||
funp.com.tw
|
||||
fuq.com
|
||||
furhhdl.org
|
||||
furinkan.com
|
||||
furl.net
|
||||
futurechinaforum.org
|
||||
futureme.org
|
||||
futuremessage.org
|
||||
fux.com
|
||||
fuyin.net
|
||||
fw.cm
|
||||
fxnetworks.com
|
||||
fzh999.com
|
||||
fzh999.net
|
||||
fzlm.com
|
||||
g-cash.biz
|
||||
g.co
|
||||
g.e-hentai.org
|
||||
gabocorp.com
|
||||
gaeproxy.com
|
||||
gaforum.org
|
||||
galenwu.com
|
||||
game735.com
|
||||
gamebase.com.tw
|
||||
gamefans.com
|
||||
gamejolt.com
|
||||
gamer.com.tw
|
||||
gamerseden.kir.jp
|
||||
gamez.com.tw
|
||||
gamousa.com
|
||||
gandi.net
|
||||
ganges.com
|
||||
gaoming.net
|
||||
gaopi.net
|
||||
gaozhisheng.net
|
||||
gaozhisheng.org
|
||||
gappp.org
|
||||
gardennetworks.com
|
||||
gardennetworks.org
|
||||
garena.tw
|
||||
gartlive.com
|
||||
gates.com
|
||||
gather.com
|
||||
gaymap.cc
|
||||
gaytube.com
|
||||
gazetapraca.pl
|
||||
gazotube.com
|
||||
gcc.org.hk
|
||||
gclooney.com
|
||||
gcpnews.com
|
||||
gcr.io
|
||||
gdbt.net
|
||||
gdzf.org
|
||||
geek-art.net
|
||||
geekerhome.com
|
||||
geekmade.co.uk
|
||||
geekmanuals.com
|
||||
gelbooru.com
|
||||
generesis.com
|
||||
gentlecuff.com
|
||||
genuitec.com
|
||||
geocities.co.jp
|
||||
geocities.com
|
||||
geocities.jp
|
||||
geohot.com
|
||||
geometrictools.com
|
||||
georgiapower.com
|
||||
get-digital-help.com
|
||||
get-tune.net
|
||||
getchu.com
|
||||
getcloudapp.com
|
||||
getcomposer.org
|
||||
getfoxyproxy.org
|
||||
getfreedur.com
|
||||
getgom.com
|
||||
getiton.com
|
||||
getjetso.com
|
||||
getlantern.org
|
||||
getnarrative.com
|
||||
getonfacebook.com
|
||||
getprismatic.com
|
||||
getsmartlinks.com
|
||||
getsocialscope.com
|
||||
getuploader.com
|
||||
getyouram.com
|
||||
gfw.org.ua
|
||||
ggpht.com
|
||||
ggssl.com
|
||||
ghconduit.com
|
||||
ghost.org
|
||||
ghut.org
|
||||
giga-web.jp
|
||||
gigacircle.com
|
||||
gigporno.ru
|
||||
giltcity.com
|
||||
gimpshop.com
|
||||
gioco.it
|
||||
girisfacebook.com
|
||||
girlbanker.com
|
||||
girlfriendvideos.com
|
||||
gist.github.com
|
||||
git-scm.com
|
||||
gitbooks.io
|
||||
github.com
|
||||
github.io
|
||||
githubapp.com
|
||||
githubusercontent.com
|
||||
gittigidiyor.com
|
||||
givemesomethingtoread.com
|
||||
gizlen.net
|
||||
glennhilton.com
|
||||
global-ssl.fastly.net
|
||||
global.hkepc.com
|
||||
global.ssl.fastly.net
|
||||
globaldelight.com
|
||||
globaljihad.net
|
||||
globalmediaoutreach.com
|
||||
globalmuseumoncommunism.org
|
||||
globalrescue.hopto.org
|
||||
globalrescue.net
|
||||
globalvoicesonline.org
|
||||
glock.com
|
||||
gloryhole.com
|
||||
glue-static.s3-external-3.amazonaws.com
|
||||
gmail.com
|
||||
gmhz.org
|
||||
gmiddle.com
|
||||
gmiddle.net
|
||||
gmll.org
|
||||
gmodules.com
|
||||
gmozomg.izihost.org
|
||||
gnci.org.hk
|
||||
gnuradio.org
|
||||
go-pki.com
|
||||
goagent.biz
|
||||
goagentplus.com
|
||||
god.tv
|
||||
godaddy.com
|
||||
godfootsteps.org
|
||||
godsdirectcontact.com
|
||||
godsdirectcontact.info
|
||||
godsdirectcontact.org
|
||||
godsdirectcontact.org.tw
|
||||
gohappy.com.tw
|
||||
gokbayrak.com
|
||||
golan.org
|
||||
golang.org
|
||||
goldbet.com
|
||||
goldbetsports.com
|
||||
goldenfrog.com
|
||||
goldenmelody.com.tw
|
||||
goldwave.com
|
||||
golem.de
|
||||
gongm.in
|
||||
gongmeng.info
|
||||
gongminliliang.com
|
||||
gongwt.com
|
||||
goo.gl
|
||||
good.gd
|
||||
goodreaders.com
|
||||
goodreads.com
|
||||
goodshow.tw
|
||||
goodthaigirl.com
|
||||
goodtv.com.tw
|
||||
goodtv.tv
|
||||
goofind.com
|
||||
google-analytics.com
|
||||
google-cardboard.com
|
||||
google.ae
|
||||
google.am
|
||||
google.as
|
||||
google.at
|
||||
google.az
|
||||
google.ba
|
||||
google.be
|
||||
google.bg
|
||||
google.bi
|
||||
google.bs
|
||||
google.ca
|
||||
google.cd
|
||||
google.cg
|
||||
google.ch
|
||||
google.ci
|
||||
google.cl
|
||||
google.co.bw
|
||||
google.co.ck
|
||||
google.co.cr
|
||||
google.co.hu
|
||||
google.co.id
|
||||
google.co.il
|
||||
google.co.in
|
||||
google.co.jp
|
||||
google.co.ke
|
||||
google.co.kr
|
||||
google.co.ls
|
||||
google.co.ma
|
||||
google.co.nz
|
||||
google.co.th
|
||||
google.co.ug
|
||||
google.co.uk
|
||||
google.co.uz
|
||||
google.co.ve
|
||||
google.co.vi
|
||||
google.co.zm
|
||||
google.com
|
||||
google.com.af
|
||||
google.com.ag
|
||||
google.com.ar
|
||||
google.com.au
|
||||
google.com.bd
|
||||
google.com.bh
|
||||
google.com.bo
|
||||
google.com.br
|
||||
google.com.bz
|
||||
google.com.co
|
||||
google.com.cu
|
||||
google.com.do
|
||||
google.com.ec
|
||||
google.com.eg
|
||||
google.com.et
|
||||
google.com.gi
|
||||
google.com.gt
|
||||
google.com.hk
|
||||
google.com.jm
|
||||
google.com.ly
|
||||
google.com.mt
|
||||
google.com.mx
|
||||
google.com.my
|
||||
google.com.na
|
||||
google.com.nf
|
||||
google.com.ni
|
||||
google.com.np
|
||||
google.com.om
|
||||
google.com.pa
|
||||
google.com.pe
|
||||
google.com.ph
|
||||
google.com.pk
|
||||
google.com.pr
|
||||
google.com.py
|
||||
google.com.sa
|
||||
google.com.sb
|
||||
google.com.sg
|
||||
google.com.sv
|
||||
google.com.tj
|
||||
google.com.tr
|
||||
google.com.tw
|
||||
google.com.ua
|
||||
google.com.uy
|
||||
google.com.vc
|
||||
google.com.vn
|
||||
google.de
|
||||
google.dj
|
||||
google.dk
|
||||
google.dm
|
||||
google.es
|
||||
google.fi
|
||||
google.fm
|
||||
google.fr
|
||||
google.gl
|
||||
google.gm
|
||||
google.gr
|
||||
google.hn
|
||||
google.hr
|
||||
google.ht
|
||||
google.ie
|
||||
google.is
|
||||
google.it
|
||||
google.jo
|
||||
google.kg
|
||||
google.kz
|
||||
google.li
|
||||
google.lk
|
||||
google.lt
|
||||
google.lu
|
||||
google.lv
|
||||
google.mn
|
||||
google.ms
|
||||
google.mu
|
||||
google.mw
|
||||
google.nl
|
||||
google.no
|
||||
google.nu
|
||||
google.off.ai
|
||||
google.org
|
||||
google.pl
|
||||
google.pn
|
||||
google.pt
|
||||
google.ro
|
||||
google.ru
|
||||
google.rw
|
||||
google.sc
|
||||
google.se
|
||||
google.sh
|
||||
google.sk
|
||||
google.sm
|
||||
google.sn
|
||||
google.tm
|
||||
google.to
|
||||
google.tp
|
||||
google.tt
|
||||
google.vg
|
||||
google.vu
|
||||
google.ws
|
||||
googleadservices.com
|
||||
googleapis.com
|
||||
googleapps.com
|
||||
googleartproject.com
|
||||
googlecode.com
|
||||
googlecommerce.com
|
||||
googledomains.com
|
||||
googledrive.com
|
||||
googleearth.com
|
||||
googlegroups.com
|
||||
googlehosted.com
|
||||
googlelabs.com
|
||||
googlemail.com
|
||||
googlemashups.com
|
||||
googlepages.com
|
||||
googleplus.com
|
||||
googlesile.com
|
||||
googlesource.com
|
||||
googlestore.com
|
||||
googlesyndication.com
|
||||
googletagmanager.com
|
||||
googletagservices.com
|
||||
googleusercontent.com
|
||||
googlevideo.com
|
||||
googlewave.com
|
||||
gopetition.com
|
||||
goproxing.com
|
||||
gospelherald.com
|
||||
gospelherald.com.hk
|
||||
gosurf.asia
|
||||
gotgayporn.com
|
||||
gotovim.ru
|
||||
gotw.ca
|
||||
gov.tw
|
||||
governmentjobs.com
|
||||
gpass1.com
|
||||
gplusexpertise.com
|
||||
gqueues.com
|
||||
grandtrial.org
|
||||
grangorz.org
|
||||
graphis.ne.jp
|
||||
gratka.pl
|
||||
gravatar.com
|
||||
graylog2.org
|
||||
greasespot.net
|
||||
great-firewall.com
|
||||
great-roc.org
|
||||
greatfire.org
|
||||
greatfirewall.biz
|
||||
greatfirewallofchina.net
|
||||
greatfirewallofchina.org
|
||||
greatroc.org
|
||||
greatroc.tw
|
||||
greatzhonghua.org
|
||||
greenparty.org.tw
|
||||
greenpeace.com.tw
|
||||
greenpeace.org
|
||||
greenvpn.net
|
||||
group-facials.com
|
||||
gs-discuss.com
|
||||
gstatic.com
|
||||
gtricks.com
|
||||
gu-chu-sum.org
|
||||
guancha.org
|
||||
guardster.com
|
||||
guide-twitter.com
|
||||
guishan.org
|
||||
guitarlist.net
|
||||
gumtree.com
|
||||
gun-world.net
|
||||
gunsamerica.com
|
||||
gunsandammo.com
|
||||
guomin.us
|
||||
gutefrage.net
|
||||
gutteruncensored.com
|
||||
gvlib.com
|
||||
gvm.com.tw
|
||||
gvt0.com
|
||||
gvt1.com
|
||||
gvt2.com
|
||||
gvt3.com
|
||||
gyalwarinpoche.com
|
||||
gyatsostudio.com
|
||||
gzm.tv
|
||||
gzone-anime.info
|
||||
gzoo.org
|
||||
h-china.org
|
||||
h1n1china.org
|
||||
h2porn.com
|
||||
hacken.cc
|
||||
hacking-facebook.com
|
||||
hackmyfacebook.com
|
||||
hackthatphone.net
|
||||
hahlo.com
|
||||
hakkatv.org.tw
|
||||
hanunyi.com
|
||||
happi-game-center.com
|
||||
haproxy.org
|
||||
hardsextube.com
|
||||
harley-davidson.com
|
||||
harunyahya.com
|
||||
hasaowall.com
|
||||
have8.com
|
||||
haxx.se
|
||||
hbogo.com
|
||||
hd1080.org
|
||||
hdtvb.net
|
||||
heartyit.com
|
||||
heatsale.com
|
||||
hecaitou.net
|
||||
hechaji.com
|
||||
heeact.edu.tw
|
||||
hegre-art.com
|
||||
heix.pp.ru
|
||||
heiyo.info
|
||||
helloandroid.com
|
||||
hellonewyork.us
|
||||
helloqueer.com
|
||||
hellotxt.com
|
||||
hellouk.org
|
||||
help.linksalpha.com
|
||||
help.opera.com
|
||||
help.trello.com
|
||||
helpeachpeople.com
|
||||
helplinfen.com
|
||||
helpster.de
|
||||
helpzhuling.org
|
||||
hen.bao.li
|
||||
hentaimedia.com
|
||||
hentaitube.tv
|
||||
hentaivideoworld.com
|
||||
heqinglian.net
|
||||
here4news.com
|
||||
heritage.org
|
||||
hersheys.com
|
||||
heungkongdiscuss.com
|
||||
hexieshe.com
|
||||
hexxeh.net
|
||||
heyzo.com
|
||||
hgseav.com
|
||||
hidden-advent.org
|
||||
hide.me
|
||||
hidecloud.com
|
||||
hideipvpn.com
|
||||
hideman.net
|
||||
hideme.be
|
||||
hidemyass.com
|
||||
hidemyipaddress.org
|
||||
hideweb.org
|
||||
higfw.com
|
||||
highcharts.com
|
||||
highrockmedia.com
|
||||
hihiforum.com
|
||||
hihistory.net
|
||||
hiitch.com
|
||||
hikinggfw.org
|
||||
hilive.tv
|
||||
himalayan-foundation.org
|
||||
himalayanglacier.com
|
||||
himemix.com
|
||||
himemix.net
|
||||
hipmunk.com
|
||||
hizb-ut-tahrir.info
|
||||
hizb-ut-tahrir.org
|
||||
hizbuttahrir.org
|
||||
hjclub.info
|
||||
hk-pub.com
|
||||
hk.geocities.com
|
||||
hk.gradconnection.com
|
||||
hk.jiepang.com
|
||||
hk32168.com
|
||||
hkatvnews.com
|
||||
hkbc.net
|
||||
hkbf.org
|
||||
hkchurch.org
|
||||
hkdailynews.com.hk
|
||||
hkday.net
|
||||
hkej.com
|
||||
hkepc.com
|
||||
hkfreezone.com
|
||||
hkfront.org
|
||||
hkg.westkit.net
|
||||
hkgolden.com
|
||||
hkgreenradio.org
|
||||
hkheadline.com
|
||||
hkhkhk.com
|
||||
hkjc.com
|
||||
hkjp.easyweb.hk
|
||||
hkjp.org
|
||||
hkptu.org
|
||||
hkreporter.com
|
||||
hkreporter.loved.hk
|
||||
hkupop.hku.hk
|
||||
hkwcc.org.hk
|
||||
hkzone.org
|
||||
hmv.com
|
||||
hnjhj.com
|
||||
hocusfoc.us
|
||||
hola.com
|
||||
hola.org
|
||||
hollisterco.com
|
||||
holyspiritspeaks.org
|
||||
holz.byethost8.com
|
||||
home.sina.com
|
||||
home.so-net.net.tw
|
||||
homedepot.com
|
||||
homeip.net
|
||||
homemademoviez.com
|
||||
homeperversion.com
|
||||
homeservershow.com
|
||||
hometeenmovs.com
|
||||
hongkongfp.com
|
||||
hongmeimei.com
|
||||
hongzhi.li
|
||||
hootsuite.com
|
||||
hot-sex-tube.com
|
||||
hotfile.com
|
||||
hotfrog.com.tw
|
||||
hotgamesforgirls.com
|
||||
hotgoo.com
|
||||
hotpornshow.com
|
||||
hotpot.hk
|
||||
hotshame.com
|
||||
hotspotshield.com
|
||||
hottystop.com
|
||||
hougaige.com
|
||||
howtodownloadmusicfromyoutube.com
|
||||
howtoforge.com
|
||||
howtogeek.com
|
||||
hqcdp.org
|
||||
hqmovies.com
|
||||
hrblock.com
|
||||
hrcchina.org
|
||||
hrcir.com
|
||||
hrea.org
|
||||
hrichina.org
|
||||
hrw.org
|
||||
hsbc.com.hk
|
||||
hsjp.net
|
||||
hsselite.com
|
||||
hstern.net
|
||||
hstt.net
|
||||
ht.ly
|
||||
htkou.net
|
||||
htl.li
|
||||
html.it
|
||||
html5rocks.com
|
||||
htmldog.com
|
||||
htxt.it
|
||||
hua-yue.net
|
||||
huaglad.com
|
||||
huanghuagang.org
|
||||
huaren.us
|
||||
huaxia-news.com
|
||||
huaxiabao.org
|
||||
huaxin.ph
|
||||
hudatoriq.web.id
|
||||
hugoroy.eu
|
||||
huhaitai.com
|
||||
huhamhire.com
|
||||
hulkshare.com
|
||||
hulu.com
|
||||
huluim.com
|
||||
humanrightsbriefing.org
|
||||
hung-ya.com
|
||||
hungerstrikeforaids.org
|
||||
huping.net
|
||||
hussytube.com
|
||||
hutianyi.net
|
||||
hutong9.net
|
||||
huyandex.com
|
||||
hwayue.org.tw
|
||||
hwinfo.com
|
||||
hxwq.org
|
||||
hybrid-analysis.com
|
||||
hyperrate.com
|
||||
hypeshell.com
|
||||
i-cable.com
|
||||
i-sux.com
|
||||
i1.hk
|
||||
i2p2.de
|
||||
i2runner.com
|
||||
ialmostlaugh.com
|
||||
ianslive.in
|
||||
iask.bz
|
||||
iask.ca
|
||||
iata.org
|
||||
ibiblio.org
|
||||
iblist.com
|
||||
iblogserv-f.net
|
||||
ibros.org
|
||||
icams.com
|
||||
icij.org
|
||||
icl-fi.org
|
||||
iconfactory.com
|
||||
iconpaper.org
|
||||
icu-project.org
|
||||
id.hao123.com
|
||||
idemocracy.asia
|
||||
identi.ca
|
||||
idesktop.tv
|
||||
idiomconnection.com
|
||||
idlcoyote.com
|
||||
idol-blog.com
|
||||
idouga.com
|
||||
idreamx.com
|
||||
idv.tw
|
||||
ieasynews.net
|
||||
ied2k.net
|
||||
if.ttt
|
||||
ifan.cz.cc
|
||||
ifanqiang.com
|
||||
ifanr.com
|
||||
ifcss.org
|
||||
ifjc.org
|
||||
ifreewares.com
|
||||
ift.tt
|
||||
ifttt.com
|
||||
igfw.net
|
||||
igmg.de
|
||||
ignitedetroit.net
|
||||
igossip.com
|
||||
igotmail.com.tw
|
||||
igvita.com
|
||||
ihakka.net
|
||||
iicns.com
|
||||
ilgiornale.it
|
||||
illusionfactory.com
|
||||
ilove80.be
|
||||
ilovelongtoes.com
|
||||
im.tv
|
||||
im88.tw
|
||||
imagefap.com
|
||||
imageflea.com
|
||||
imagenparaelfacebook.com
|
||||
imageoptim.com
|
||||
imageshack.us
|
||||
imagevenue.com
|
||||
imagezilla.net
|
||||
imb.org
|
||||
imdb.com
|
||||
img.dlsite.jp
|
||||
img.ly
|
||||
imgix.net
|
||||
imgur.com
|
||||
imkev.com
|
||||
imlive.com
|
||||
immigration.gov.tw
|
||||
immoral.jp
|
||||
impact.org.au
|
||||
in-disguise.com
|
||||
incloak.com
|
||||
incredibox.fr
|
||||
indeed.co.uk
|
||||
independent.ie
|
||||
index.hu
|
||||
indiaglitz.com
|
||||
indiemerch.com
|
||||
infinitylist.com
|
||||
info-graf.fr
|
||||
informer.com
|
||||
infradead.org
|
||||
initiativesforchina.org
|
||||
inkui.com
|
||||
inmediahk.net
|
||||
inmoment.com
|
||||
innermongolia.org
|
||||
insidefacebook.com
|
||||
instaforex.com
|
||||
instagram.com
|
||||
institut-tibetain.org
|
||||
intelius.com
|
||||
intellectuapp.com
|
||||
interestinglaugh.com
|
||||
interfaceaddiction.com
|
||||
internationalrivers.org
|
||||
internet.org
|
||||
internetdefenseleague.org
|
||||
internetfreedom.org
|
||||
internetpopculture.com
|
||||
intertwitter.com
|
||||
inxian.com
|
||||
ipcf.org.tw
|
||||
iphider.org
|
||||
iphone4hongkong.com
|
||||
iphonehacks.com
|
||||
iphonenews.cc
|
||||
iphonix.fr
|
||||
ipicture.ru
|
||||
ipjetable.net
|
||||
ipobar.com
|
||||
ippotv.com
|
||||
ipredator.se
|
||||
iptorrents.com
|
||||
iptv.com.tw
|
||||
ipvanish.com
|
||||
iredmail.org
|
||||
iridiumcao.info
|
||||
ironbigfools.compython.net
|
||||
ironfx.com
|
||||
ironicsoftware.com
|
||||
ironpython.net
|
||||
irr.ru
|
||||
is.gd
|
||||
isaacmao.com
|
||||
isgreat.org
|
||||
iskcondesiretree.com
|
||||
iskconsandton.co.za
|
||||
islam.org.hk
|
||||
islamhouse.com
|
||||
islamicawakening.com
|
||||
islamicity.com
|
||||
islamtoday.net
|
||||
ismaelan.com
|
||||
ismprofessional.net
|
||||
isohunt.com
|
||||
israbox.com
|
||||
istars.co.nz
|
||||
istockphoto.com
|
||||
isunaffairs.com
|
||||
isuntv.com
|
||||
itaboo.info
|
||||
ithelp.ithome.com.tw
|
||||
its.caltech.edu
|
||||
itshidden.com
|
||||
itweet.net
|
||||
iu45.com
|
||||
iuhrdf.org
|
||||
iuksky.com
|
||||
iverycd.com
|
||||
ixiaa.com
|
||||
ixquick-proxy.com
|
||||
ixquick.com
|
||||
ixxx.com
|
||||
iyouport.com
|
||||
izaobao.us
|
||||
izles.net
|
||||
izlesem.org
|
||||
izlesene.com
|
||||
j.mp
|
||||
jackinthebox.com
|
||||
jaidefinichon.com
|
||||
jalan.net
|
||||
jamaat.org
|
||||
jams.kir.jp
|
||||
japan-whores.com
|
||||
japanesesportcars.com
|
||||
japanfirst.asianfreeforum.com
|
||||
jappydolls.net
|
||||
javbus.com
|
||||
javfor.me
|
||||
javhub.net
|
||||
javlibrary.com
|
||||
javpee.com
|
||||
javseeds.com
|
||||
jayparkinsonmd.com
|
||||
jazztel.com
|
||||
jbtalks.cc
|
||||
jbtalks.com
|
||||
jbtalks.my
|
||||
jdwsy.com
|
||||
jeanyim.com
|
||||
jetstar.com
|
||||
jetztspielen.de
|
||||
jeuxvideo.com
|
||||
jgoodies.com
|
||||
jiaoyou8.com
|
||||
jiehua.cz
|
||||
jieshibaobao.com
|
||||
jigong1024.com
|
||||
jihadology.net
|
||||
jimoparty.com
|
||||
jinbushe.org
|
||||
jingpin.org
|
||||
jitouch.com
|
||||
jitsuroku.kir.jp
|
||||
jizzhut.com
|
||||
jjgirls.com
|
||||
jkb.cc
|
||||
jkforum.net
|
||||
joachims.org
|
||||
jobso.tv
|
||||
joeedelman.com
|
||||
journalchretien.net
|
||||
journalofdemocracy.org
|
||||
jp-sex.com
|
||||
jp.hao123.com
|
||||
jpl.nasa.gov
|
||||
jpopforum.net
|
||||
jshint.com
|
||||
juegosdefacebook.com
|
||||
juliepost.com
|
||||
juliereyc.com
|
||||
jumav.com
|
||||
junauza.com
|
||||
junefourth-20.net
|
||||
justfreevpn.com
|
||||
justpaste.it
|
||||
justtristan.com
|
||||
juyuange.org
|
||||
juziyue.com
|
||||
jwmusic.org
|
||||
jwpcdn.com
|
||||
jyxf.net
|
||||
jyzj.waqn.com
|
||||
k2.xrea.com
|
||||
ka-wai.com
|
||||
kagyuoffice.org
|
||||
kagyuoffice.org.tw
|
||||
kaiyuan.de
|
||||
kakao.com
|
||||
kanzhongguo.com
|
||||
kanzhongguo.eu
|
||||
kaotic.com
|
||||
karayou.com
|
||||
kat.cr
|
||||
kat.ph
|
||||
kcoolonline.com
|
||||
kcsoftwares.com
|
||||
kebrum.com
|
||||
kechara.com
|
||||
keepandshare.com
|
||||
keepvid.com
|
||||
keepyoutube.com
|
||||
kendincos.net
|
||||
kenengba.com
|
||||
keontech.net
|
||||
kepard.com
|
||||
keurig.com
|
||||
khabdha.org
|
||||
khmusic.com.tw
|
||||
kickyoutube.com
|
||||
killwall.com
|
||||
kineox.free.fr
|
||||
kingdomsalvation.org
|
||||
kinghost.com
|
||||
kinghost.com.br
|
||||
kinghost.net
|
||||
kingstone.com.tw
|
||||
kissyoutube.com
|
||||
kiwi.kz
|
||||
kkbobo.com
|
||||
klip.me
|
||||
klmty.net
|
||||
kmart.com
|
||||
kmt.org.tw
|
||||
knightmaster.kir.jp
|
||||
knowledgerush.com
|
||||
kobo.com
|
||||
kodingen.com
|
||||
kokoro.kir.jp
|
||||
kompozer.net
|
||||
konami.jp
|
||||
koolsolutions.com
|
||||
koornk.com
|
||||
korea-twitter.com
|
||||
kproxy.com
|
||||
kraftrecipes.com
|
||||
kt.kcome.org
|
||||
ktzhk.com
|
||||
kui.name
|
||||
kuliwang.com
|
||||
kun.im
|
||||
kurashsultan.com
|
||||
kurtmunger.com
|
||||
kusocity.com
|
||||
kuvia.eu
|
||||
kwcg.ca
|
||||
kwongwah.com.my
|
||||
kyohk.net
|
||||
kzeng.info
|
||||
la-forum.org
|
||||
labanquepostale.fr
|
||||
labiennale.org
|
||||
ladbrokes.com
|
||||
lagrandeepoque.com
|
||||
lagranepoca.com
|
||||
lalulalu.com
|
||||
lamayeshe.com
|
||||
lamenhu.com
|
||||
lancome.com
|
||||
laogai.org
|
||||
laomiu.com
|
||||
laonanren.com
|
||||
laoyang.info
|
||||
laptoplockdown.com
|
||||
laqingdan.net
|
||||
larsgeorge.com
|
||||
lastcombat.com
|
||||
lastfm.es
|
||||
lastpass.com
|
||||
lataayoutube.com
|
||||
latelinenews.com
|
||||
latibet.org
|
||||
latimesblogs.latimes.com
|
||||
lazarsearlymusic.com
|
||||
lebo.tv
|
||||
leecheukyan.org
|
||||
leedeelive.com
|
||||
legacy.com
|
||||
legaltech.law.com
|
||||
leggycash.com
|
||||
leirentv.ca
|
||||
leisurecafe.ca
|
||||
lematin.ch
|
||||
lemonde.fr
|
||||
lenwhite.com
|
||||
lerosua.org
|
||||
lesoir.be
|
||||
lesscss.org
|
||||
letscorp.net
|
||||
lezcuties.com
|
||||
lian86.com
|
||||
liansi.org
|
||||
lianyue.net
|
||||
liaowangxizang.net
|
||||
lib.virginia.edu
|
||||
liberal.org.hk
|
||||
libertytimes.com.tw
|
||||
library.usc.cuhk.edu.hk
|
||||
librodetwitter.com
|
||||
licdn.com
|
||||
lich355.megabyet.net
|
||||
lidecheng.com
|
||||
life.fly4ever.me
|
||||
lifemiles.com
|
||||
like-facebook.com
|
||||
limiao.net
|
||||
line.me
|
||||
line.naver.jp
|
||||
linglingfa.com
|
||||
lingvodics.com
|
||||
linkedin.com
|
||||
linkideo.com
|
||||
links.org.au
|
||||
linksalpha.com
|
||||
linode.com
|
||||
linux-engineer.net
|
||||
linuxcommand.org
|
||||
linuxconfig.org
|
||||
linuxquestions.org
|
||||
linuxreviews.org
|
||||
linuxtoy.org
|
||||
lipuman.com
|
||||
list.ly
|
||||
listentoyoutube.com
|
||||
listorious.com
|
||||
lists.debian.org
|
||||
lists.w3.org
|
||||
lists.webmproject.org
|
||||
lithium.com
|
||||
littlebigdetails.com
|
||||
liu.lu
|
||||
liudejun.com
|
||||
liuhanyu.com
|
||||
liujianshu.com
|
||||
liuxiaotong.com
|
||||
livedoor.jp
|
||||
liveleak.com
|
||||
livestation.com
|
||||
livestream.com
|
||||
livetv.sx
|
||||
livevideo.com
|
||||
livingonline.us
|
||||
livingstream.com
|
||||
lizhizhuangbi.com
|
||||
lkcn.net
|
||||
llnwd.net
|
||||
load.to
|
||||
local.com
|
||||
localhost.com
|
||||
localpresshk.com
|
||||
locanto.com
|
||||
lockdown.com
|
||||
lockestek.com
|
||||
locu.com
|
||||
lofi.e-hentai.org
|
||||
log.riku.me
|
||||
logbot.net
|
||||
logiqx.com
|
||||
logme.in
|
||||
logmein.com
|
||||
logmike.com
|
||||
loiclemeur.com
|
||||
london.neighborhoodr.com
|
||||
longhair.hk
|
||||
longtermly.net
|
||||
lookatgame.com
|
||||
lookingglasstheatre.org
|
||||
lookpic.com
|
||||
looktoronto.com
|
||||
lorealparisusa.com
|
||||
lotsawahouse.org
|
||||
lotuslight.org.tw
|
||||
loudtwitter.com
|
||||
lovequicksilver.com
|
||||
loxber.com
|
||||
lpsg.com
|
||||
lrfz.com
|
||||
lrip.org
|
||||
lsd.org.hk
|
||||
lsforum.net
|
||||
lsm.org
|
||||
lsmchinese.org
|
||||
lsmkorean.org
|
||||
lsmradio.com
|
||||
lsxszzg.com
|
||||
ltn.com.tw
|
||||
luke54.org
|
||||
luntan.zaobao.com
|
||||
lupm.org
|
||||
lushstories.com
|
||||
luxebc.com
|
||||
lvhai.org
|
||||
lvv2.com
|
||||
lyfhk.net
|
||||
lyrics5.com
|
||||
lyricsquote.com
|
||||
m-sport.co.uk
|
||||
m-team.cc
|
||||
m.googlemail.com
|
||||
m.oulove.org
|
||||
m.plixi.com
|
||||
m.slandr.net
|
||||
m.tweete.net
|
||||
m3.com
|
||||
m88a.com
|
||||
ma.hao123.com
|
||||
mac.com
|
||||
macauslot.com
|
||||
maccosmetics.com
|
||||
macgamestore.com
|
||||
macrovpn.com
|
||||
macys.com
|
||||
mad-ar.ch
|
||||
maddw.com
|
||||
madmenunbuttoned.com
|
||||
madthumbs.com
|
||||
magazines.com
|
||||
magazines.sina.com.tw
|
||||
magiccloak.net
|
||||
maiio.net
|
||||
mail-archive.com
|
||||
mailchimp.com
|
||||
maiplus.com
|
||||
makemymood.com
|
||||
makeuseof.com
|
||||
makzhou.warehouse333.com
|
||||
malaysiakini.com
|
||||
mango.pl
|
||||
manhub.com
|
||||
maniash.com
|
||||
mansion.com
|
||||
mansionpoker.com
|
||||
marc.info
|
||||
marco.org
|
||||
marguerite.su
|
||||
marines.mil
|
||||
marinsm.com
|
||||
markacadey.net
|
||||
market.android.com
|
||||
markmail.org
|
||||
markmilian.com
|
||||
mars99.com
|
||||
martau.com
|
||||
martincartoons.com
|
||||
martsangkagyuofficial.org
|
||||
maruta.be
|
||||
marxist.com
|
||||
marxist.net
|
||||
marxists.org
|
||||
mash.to
|
||||
mashable.com
|
||||
matainja.com
|
||||
match.com
|
||||
mathiew-badimon.com
|
||||
matsushimakaede.com
|
||||
maturejp.com
|
||||
maxgif.com
|
||||
maybelline.com
|
||||
mayimayi.com
|
||||
mcadforums.com
|
||||
mcfog.com
|
||||
mcreasite.com
|
||||
md-t.org
|
||||
mediafire.com
|
||||
mediafreakcity.com
|
||||
mediawiki.org
|
||||
meetav.com
|
||||
meeticaffinity.fr
|
||||
meetup.com
|
||||
mefeedia.com
|
||||
megaporn.com
|
||||
megaproxy.com
|
||||
megarotic.com
|
||||
megaupload.com
|
||||
megavideo.com
|
||||
megurineluka.com
|
||||
meirixiaochao.com
|
||||
melhoresdoyoutube.com
|
||||
melon-peach.com
|
||||
memehk.com
|
||||
memrijttm.org
|
||||
menover30.com
|
||||
menupages.com
|
||||
merit-times.com.tw
|
||||
mesotw.com
|
||||
metacafe.com
|
||||
metarthunter.com
|
||||
meteorshowersonline.com
|
||||
metro.taipei
|
||||
metrolife.ca
|
||||
meyou.jp
|
||||
mfxmedia.com
|
||||
mgoon.com
|
||||
mgstage.com
|
||||
mh4u.org
|
||||
mhradio.org
|
||||
michaelanti.com
|
||||
michaelmarketl.com
|
||||
middle-way.net
|
||||
mihk.hk
|
||||
mihr.com
|
||||
mihua.org
|
||||
mike.cz.cc
|
||||
milph.net
|
||||
milsurps.com
|
||||
mimivip.com
|
||||
mimivv.com
|
||||
mindbodygreen.com
|
||||
mindrolling.org
|
||||
minergate.com
|
||||
minghui-a.org
|
||||
minghui-b.org
|
||||
minghui-school.org
|
||||
minghui.org
|
||||
minghui.tv
|
||||
mingjinglishi.com
|
||||
mingjingnews.com
|
||||
mingjingtimes.com
|
||||
mingpao.com
|
||||
mingpaocanada.com
|
||||
mingpaomonthly.com
|
||||
mingpaonews.com
|
||||
mingpaony.com
|
||||
mingpaosf.com
|
||||
mingpaotor.com
|
||||
mingpaovan.com
|
||||
mingshengbao.com
|
||||
minhhue.net
|
||||
minidaili.com
|
||||
minilua.com
|
||||
minimalmac.com
|
||||
mininova.org
|
||||
ministrybooks.org
|
||||
minus.com
|
||||
minzhuhua.net
|
||||
minzhuzhanxian.com
|
||||
minzhuzhongguo.org
|
||||
miroguide.com
|
||||
mirrorbooks.com
|
||||
mitbbs.ca
|
||||
mitbbs.com
|
||||
mitsuran.kir.jp
|
||||
mixedmedialabs.com
|
||||
mixero.com
|
||||
mixpod.com
|
||||
mixx.com
|
||||
mizzmona.com
|
||||
mjlsh.usc.cuhk.edu.hk
|
||||
mk5000.com
|
||||
mlcool.com
|
||||
mmaaxx.com
|
||||
mmgp.ru
|
||||
mmmca.com
|
||||
mobatek.net
|
||||
mobile.de
|
||||
mobile01.com
|
||||
mobileways.de
|
||||
moby.to
|
||||
mobypicture.com
|
||||
mockable.io
|
||||
modedamour.com
|
||||
modfetish.com
|
||||
modivideo.com
|
||||
modmyi.com
|
||||
mog.com
|
||||
molihua.org
|
||||
mondex.org
|
||||
monitorchina.org
|
||||
monlamit.org
|
||||
moonbbs.com
|
||||
mooo.com
|
||||
mopo.de
|
||||
morazzia.com
|
||||
morningsun.org
|
||||
motherearthliving.com
|
||||
motor4ik.ru
|
||||
mousebreaker.com
|
||||
movabletype.com
|
||||
movements.org
|
||||
moviefap.com
|
||||
moxa.com
|
||||
moztw.org
|
||||
mp3buscador.com
|
||||
mp3ye.eu
|
||||
mpettis.com
|
||||
mpfinance.com
|
||||
mpinews.com
|
||||
mps.it
|
||||
mrdoob.com
|
||||
mrgreen.com
|
||||
mrtweet.com
|
||||
msguancha.com
|
||||
msn.com.tw
|
||||
mthruf.com
|
||||
mtw.tl
|
||||
muchosucko.com
|
||||
mullvad.net
|
||||
multiplayerforums.com
|
||||
multiply.com
|
||||
multiproxy.org
|
||||
multiupload.com
|
||||
mummysgold.com
|
||||
mundofacebook.com
|
||||
muouju.com
|
||||
murmur.tw
|
||||
musavat.com
|
||||
muselinks.co.jp
|
||||
musicade.net
|
||||
muzi.com
|
||||
muzi.net
|
||||
muzu.tv
|
||||
mvd.ru
|
||||
mx981.com
|
||||
mxplayer.j2inter.com
|
||||
my-addr.com
|
||||
my-private-network.co.uk
|
||||
my-proxy.com
|
||||
my.opera.com
|
||||
myactimes.com
|
||||
myaudiocast.com
|
||||
myav.com.tw
|
||||
mybloggertricks.com
|
||||
myca168.com
|
||||
mychinamyhome.com
|
||||
mycould.com
|
||||
mydish.com
|
||||
myeasytv.com
|
||||
myeclipseide.com
|
||||
myequil.com
|
||||
myforum.com.hk
|
||||
myforum.com.uk
|
||||
myfreepaysite.com
|
||||
myfreshnet.com
|
||||
myiphide.com
|
||||
mylust.com
|
||||
myopenid.com
|
||||
myparagliding.com
|
||||
mypopescu.com
|
||||
myshare.url.com.tw
|
||||
mysinablog.com
|
||||
mysocialpoint.com
|
||||
myspace.com
|
||||
mywot.com
|
||||
naacoalition.org
|
||||
naitik.net
|
||||
nakido.com
|
||||
name.com
|
||||
namsisi.com
|
||||
nanyang.com
|
||||
nanyang.com.my
|
||||
nanyangpost.com
|
||||
nanzao.com
|
||||
naol.ca
|
||||
national-lottery.co.uk
|
||||
nationalrail.co.uk
|
||||
naughtyamerica.com
|
||||
navicat.com
|
||||
navigeaters.com
|
||||
navy.mil
|
||||
nbc.com
|
||||
nccwatch.org.tw
|
||||
nch.com.tw
|
||||
ncn.org
|
||||
nde.de
|
||||
ndr.de
|
||||
ne.jp
|
||||
ned.org
|
||||
nekoslovakia.net
|
||||
nelnet.com
|
||||
nemesis2.qx.net
|
||||
netbirds.com
|
||||
netcolony.com
|
||||
netflix.com
|
||||
netme.cc
|
||||
network54.com
|
||||
networkedblogs.com
|
||||
neverforget8964.org
|
||||
new-3lunch.net
|
||||
new-akiba.com
|
||||
newcenturymc.com
|
||||
newcenturynews.com
|
||||
newchen.com
|
||||
newgrounds.com
|
||||
newipnow.com
|
||||
newlandmagazine.com.au
|
||||
newmobilelife.com
|
||||
newnews.ca
|
||||
news.atebits.com
|
||||
news.bbc.co.uk
|
||||
news.cnyes.com
|
||||
news.dartlang.org
|
||||
news.ghostery.com
|
||||
news.msn.com.tw
|
||||
news.now.com
|
||||
news.omy.sg
|
||||
news.sina.com.hk
|
||||
news.sina.com.tw
|
||||
news.sinchew.com.my
|
||||
news.singtao.ca
|
||||
news100.com.tw
|
||||
newsancai.com
|
||||
newscn.org
|
||||
newsextube.org
|
||||
newsforums.bbc.co.uk
|
||||
newsminer.com
|
||||
newspeak.cc
|
||||
newstapa.org
|
||||
newstarnet.com
|
||||
newtaiwan.com.tw
|
||||
newtalk.tw
|
||||
newyorktimes.com
|
||||
nexon.com
|
||||
nexon.net
|
||||
next11.co.jp
|
||||
nextbigfuture.com
|
||||
nextmedia.com
|
||||
nexton-net.jp
|
||||
nexttv.com.tw
|
||||
nf.id.au
|
||||
nga.mil
|
||||
ngensis.com
|
||||
ngrok.com
|
||||
nhentai.net
|
||||
nic.cz.cc
|
||||
nichegalz.com
|
||||
nicotwitter.com
|
||||
nicovideo.jp
|
||||
nighost.org
|
||||
ninecommentaries.com
|
||||
ninjacloak.com
|
||||
nintendium.com
|
||||
niusnews.com
|
||||
njactb.org
|
||||
njuice.com
|
||||
nlfreevpn.com
|
||||
nlog.cc
|
||||
nn.ru
|
||||
nobel.se
|
||||
nobelprize.org
|
||||
noblecasino.com
|
||||
nobodycanstop.us
|
||||
nokogiri.org
|
||||
nokola.com
|
||||
noobbox.com
|
||||
norbulingka.org
|
||||
nordstrom.com
|
||||
nordstromimage.com
|
||||
notes.alexdong.com
|
||||
novelasia.com
|
||||
nowfoods.com
|
||||
nownews.com
|
||||
nowtorrents.com
|
||||
noypf.com
|
||||
npa.go.jp
|
||||
nps.gov
|
||||
nrk.no
|
||||
nsc.gov.tw
|
||||
nsfwyoutube.com
|
||||
ntd.tv
|
||||
ntdtv.ca
|
||||
ntdtv.co
|
||||
ntdtv.com
|
||||
ntdtv.jp
|
||||
ntdtv.org
|
||||
ntdtv.ru
|
||||
nubiles.net
|
||||
nuexpo.com
|
||||
nurgo-software.com
|
||||
nuuvem.com
|
||||
nuvid.com
|
||||
nuzcom.com
|
||||
nuzzel.com
|
||||
nvquan.org
|
||||
nwtca.org
|
||||
nxgx.com
|
||||
ny.visiontimes.com
|
||||
nyaa.se
|
||||
nydus.ca
|
||||
nylon-angel.com
|
||||
nylonstockingsonline.com
|
||||
nysingtao.com
|
||||
nyt.com
|
||||
nytco.com
|
||||
nytimes.com
|
||||
nytimg.com
|
||||
nzchinese.net.nz
|
||||
o2online.de
|
||||
oakland.edu
|
||||
oasic.net
|
||||
observechina.net
|
||||
obutu.com
|
||||
ocaspro.com
|
||||
oclp.hk
|
||||
ocreampies.com
|
||||
ocsp.digicert.com
|
||||
october-review.org
|
||||
offbeatchina.com
|
||||
officeoftibet.com
|
||||
ogaoga.org
|
||||
ohayoutube.com
|
||||
oi.com.br
|
||||
oikos.com.tw
|
||||
oiktv.com
|
||||
oizoblog.com
|
||||
ojogos.com.br
|
||||
okayfreedom.com
|
||||
okk.tw
|
||||
okta.com
|
||||
old-cat.net
|
||||
old.honeynet.org
|
||||
old.nabble.com
|
||||
olivegarden.com
|
||||
oloadcdn.net
|
||||
olumpo.com
|
||||
olx.com.ve
|
||||
olx.ph
|
||||
olympicwatch.org
|
||||
omandaily.om
|
||||
omgili.com
|
||||
omnitalk.com
|
||||
omnitalk.org
|
||||
on.cc
|
||||
one.xthost.info
|
||||
onedrive.live.com
|
||||
onion.city
|
||||
online.hk
|
||||
onlinecha.com
|
||||
onmoon.com
|
||||
onmoon.net
|
||||
onthehunt.com
|
||||
ontrac.com
|
||||
ookla.com
|
||||
ooo-sex.com
|
||||
oopsforum.com
|
||||
open-consoles-news.com
|
||||
open.com.hk
|
||||
opendemocracy.net
|
||||
openid.net
|
||||
openleaks.org
|
||||
openload.co
|
||||
openvpn.net
|
||||
openwall.com
|
||||
openwebster.com
|
||||
opml.radiotime.com
|
||||
opnir.com
|
||||
optus.com.au
|
||||
orchidbbs.com
|
||||
organharvestinvestigation.net
|
||||
orgfree.com
|
||||
orient-doll.com
|
||||
orientaldaily.com.my
|
||||
orientaldaily.on.cc
|
||||
orkut.com
|
||||
orn.jp
|
||||
orzdream.com
|
||||
orzistic.org
|
||||
osaka69.com
|
||||
osfoora.com
|
||||
osikko.jp
|
||||
osmdroid.net
|
||||
oss.sonatype.org
|
||||
ostraining.com
|
||||
ottawasun.com
|
||||
otto.de
|
||||
our-twitter.com
|
||||
ourdearamy.com
|
||||
oursogo.com
|
||||
oursteps.com.au
|
||||
overlapr.com
|
||||
overplay.net
|
||||
ow.ly
|
||||
owind.com
|
||||
owl.li
|
||||
oxid.it
|
||||
oyax.com
|
||||
ozchinese.com
|
||||
ozyoyo.com
|
||||
p-cdn.com
|
||||
p.twipple.jp
|
||||
pachosting.com
|
||||
pacificpoker.com
|
||||
packages.debian.org
|
||||
packetix.net
|
||||
paddle.com
|
||||
padhuskitchen.com
|
||||
padmanet.com
|
||||
page2rss.com
|
||||
pagodabox.com
|
||||
paid2youtube.com
|
||||
paint.net
|
||||
palacemoon.com
|
||||
palevo.com
|
||||
paljorpublications.com
|
||||
palmbeachpost.com
|
||||
paltalk.com
|
||||
pandora.com
|
||||
pandora.tv
|
||||
panlon.com
|
||||
panluan.net
|
||||
panoramio.com
|
||||
pao-pao.net
|
||||
paper-replika.com
|
||||
paper.li
|
||||
paperb.us
|
||||
parade.com
|
||||
paradisepoker.com
|
||||
parislemon.com
|
||||
parkansky.com
|
||||
partycasino.com
|
||||
partypoker.com
|
||||
passion.com
|
||||
passiontimes.hk
|
||||
pastebin.com
|
||||
pastie.org
|
||||
pbs.org
|
||||
pbwiki.com
|
||||
pbworks.com
|
||||
pbxes.com
|
||||
pbxes.org
|
||||
pcdiscuss.com
|
||||
pcdvd.com.tw
|
||||
pchome.com.tw
|
||||
pcij.org
|
||||
pct.org.tw
|
||||
pdetails.com
|
||||
pdproxy.com
|
||||
pds.nasa.gov
|
||||
peace.ca
|
||||
peacefire.org
|
||||
peacehall.com
|
||||
pearlher.org
|
||||
peeasian.com
|
||||
peerfly.com
|
||||
peerpong.com
|
||||
peggo.co
|
||||
pekingduck.org
|
||||
pen.io
|
||||
penchinese.com
|
||||
penchinese.net
|
||||
penchinese.org
|
||||
pengyulong.com
|
||||
penisbot.com
|
||||
penthouse.com
|
||||
penthousebabesworld.com
|
||||
peopo.org
|
||||
percy.in
|
||||
perfectgirls.net
|
||||
perfectmoney.is
|
||||
perfectvpn.net
|
||||
perfspot.com
|
||||
perlhowto.com
|
||||
persecutionblog.com
|
||||
pfizer.com
|
||||
phapluan.org
|
||||
phayul.com
|
||||
philborges.com
|
||||
philly.com
|
||||
phncdn.com
|
||||
phonesat.org
|
||||
photo.utom.us
|
||||
photobucket.com
|
||||
photodharma.net
|
||||
photofocus.com
|
||||
photos.dailyme.com
|
||||
phuquocservices.com
|
||||
picidae.net
|
||||
picsee.net
|
||||
picturedip.com
|
||||
pictures.playboy.com
|
||||
picturesocial.com
|
||||
pidown.com
|
||||
pigav.com
|
||||
pign.net
|
||||
pimg.tw
|
||||
pimpmyip.com
|
||||
pin6.com
|
||||
pinboard.in
|
||||
ping.fm
|
||||
pingtest.net
|
||||
pinimg.com
|
||||
pinknews.co.uk
|
||||
pinoy-n.com
|
||||
pinporn.com
|
||||
pinterest.com
|
||||
pioneer-worker.forums-free.com
|
||||
piposay.com
|
||||
piraattilahti.org
|
||||
piring.com
|
||||
pixelqi.com
|
||||
pixnet.net
|
||||
pk.com
|
||||
placemix.com
|
||||
planetsuzy.org
|
||||
playboy.com
|
||||
playpcesor.com
|
||||
plays.com.tw
|
||||
playvid.com
|
||||
plm.org.hk
|
||||
plunder.com
|
||||
plurk.com
|
||||
plurktop.mmdays.com
|
||||
plus28.com
|
||||
plusbb.com
|
||||
pmates.com
|
||||
po2b.com
|
||||
pocketcalculatorshow.com
|
||||
podcastblaster.com
|
||||
podictionary.com
|
||||
poker.betfair.com
|
||||
pokerbooksdvd.com
|
||||
pokerstars.com
|
||||
pokerstars.net
|
||||
pokervideo4u.com
|
||||
politicalchina.org
|
||||
politicalconsultation.org
|
||||
polysolve.com
|
||||
popapp.in
|
||||
popularpages.net
|
||||
popvote.hk
|
||||
popyard.com
|
||||
popyard.org
|
||||
porn-star.com
|
||||
porn.com
|
||||
porn2.com
|
||||
pornbase.org
|
||||
pornerbros.com
|
||||
pornhd.com
|
||||
pornhome.com
|
||||
pornhost.com
|
||||
pornhub.com
|
||||
pornhublive.com
|
||||
pornmm.net
|
||||
pornoxo.com
|
||||
pornrapidshare.com
|
||||
pornstarclub.com
|
||||
porntube.com
|
||||
porntubecdn.com
|
||||
porntubenews.com
|
||||
pornvisit.com
|
||||
portablevpn.nl
|
||||
pose.com
|
||||
post.anyu.org
|
||||
post.ly
|
||||
post76.com
|
||||
post852.com
|
||||
postadult.com
|
||||
posterous.com
|
||||
potora.jp
|
||||
power.com
|
||||
powerapple.com
|
||||
powercx.com
|
||||
powerpointninja.com
|
||||
prayforchina.net
|
||||
premeforwindows7.com
|
||||
premierinconline.com
|
||||
presentationzen.com
|
||||
prestige-av.com
|
||||
prestigecasino.com
|
||||
prisoneralert.com
|
||||
pritunl.com
|
||||
privacybox.de
|
||||
privacyprotector.eu
|
||||
private.com
|
||||
privateinternetaccess.com
|
||||
privatepaste.com
|
||||
privatetunnel.com
|
||||
privatevoyeur.com
|
||||
privoxy.org
|
||||
procopytips.com
|
||||
proctoru.com
|
||||
profitcentr.com
|
||||
programastwitter.com
|
||||
prosiben.de
|
||||
protv.ro
|
||||
provideocoalition.com
|
||||
proxay.co.uk
|
||||
proxfree.com
|
||||
proxifier.com
|
||||
proxite.net
|
||||
proxite.us
|
||||
proxlet.com
|
||||
proxomitron.info
|
||||
proxpn.biz
|
||||
proxpn.com
|
||||
proxpn.org
|
||||
proxy.googlezip.net
|
||||
proxy.org
|
||||
proxy4free.com
|
||||
proxypy.net
|
||||
proxyroad.com
|
||||
proxysite.com
|
||||
proxyunblocker.org
|
||||
prozz.net
|
||||
psblog.name
|
||||
psd-tutorials.de
|
||||
psiphon.ca
|
||||
psiphon.civisec.org
|
||||
pso2.jp
|
||||
pts.org.tw
|
||||
ptt.cc
|
||||
pubu.com.tw
|
||||
puffinbrowser.com
|
||||
puffstore.com
|
||||
pullfolio.com
|
||||
punyu.com
|
||||
purchasefollowersontwitter.com
|
||||
pure18.com
|
||||
pureconcepts.net
|
||||
pureinsight.org
|
||||
purepdf.com
|
||||
purevpn.com
|
||||
puritan.com
|
||||
purseblog.com
|
||||
pussy.org
|
||||
putlocker.com
|
||||
putty.org
|
||||
puttycm.free.fr
|
||||
puuko.com
|
||||
pwc.com
|
||||
pwned.com
|
||||
pypi.python.org
|
||||
python.com
|
||||
python.com.tw
|
||||
qanote.com
|
||||
qi-gong.me
|
||||
qidian.ca
|
||||
qienkuen.org
|
||||
qiwen.lu
|
||||
qkshare.com
|
||||
qoos.com
|
||||
qq.co.za
|
||||
qstatus.com
|
||||
qt.io
|
||||
qtrac.eu
|
||||
qtweeter.com
|
||||
quadedge.com
|
||||
quanzi.com.au
|
||||
quitccp.net
|
||||
quitccp.org
|
||||
quora.com
|
||||
quran.com
|
||||
qusi8.net
|
||||
qvodzy.org
|
||||
qxbbs.org
|
||||
raaga.com
|
||||
rabota.ru
|
||||
radicalparty.org
|
||||
radiko.jp
|
||||
radioaustralia.net.au
|
||||
radiohilight.net
|
||||
radiovaticana.org
|
||||
radiovncr.com
|
||||
rael.org
|
||||
raidcall.com
|
||||
raidcall.com.tw
|
||||
raidtalk.com.tw
|
||||
rangzen.com
|
||||
rangzen.net
|
||||
rangzen.org
|
||||
ranyunfei.com
|
||||
rapbull.net
|
||||
rapidgator.net
|
||||
rapidshare8.com
|
||||
rapidsharedata.com
|
||||
raspberrypi.org
|
||||
rbs.com
|
||||
rcinet.ca
|
||||
rconversation.blogs.com
|
||||
rd.com
|
||||
rd.io
|
||||
rdio.com
|
||||
read100.com
|
||||
readingtimes.com.tw
|
||||
readmoo.com
|
||||
realcourage.org
|
||||
realhomesex.net
|
||||
realitykings.com
|
||||
realraptalk.com
|
||||
recaptcha.net
|
||||
recordhistory.org
|
||||
redbox.com
|
||||
redchinacn.org
|
||||
redmondpie.com
|
||||
redtube.com
|
||||
referer.us
|
||||
refinery29.com
|
||||
reflectivecode.com
|
||||
rekrytointipalvelut.info
|
||||
relakks.com
|
||||
relaxbbs.com
|
||||
releaseinternational.org
|
||||
religioustolerance.org
|
||||
renminbao.com
|
||||
rense.com
|
||||
renyurenquan.org
|
||||
repo.scala-sbt.org
|
||||
repo.typesafe.com
|
||||
repo1.maven.org
|
||||
research.jmsc.hku.hk
|
||||
ressim.net
|
||||
retaildesignblog.net
|
||||
retweeteffect.com
|
||||
retweetist.com
|
||||
retweetrank.com
|
||||
reuters.com
|
||||
reviewcentre.com
|
||||
reviveourhearts.com
|
||||
revleft.com
|
||||
revver.com
|
||||
rfa.org
|
||||
rfachina.com
|
||||
rfamobile.org
|
||||
rferl.org
|
||||
rfi.fr
|
||||
rfi.my
|
||||
rhcloud.com
|
||||
rian.ru
|
||||
ricardo.ch
|
||||
rigpa.org
|
||||
riitek.com
|
||||
riku.me
|
||||
rileyguide.com
|
||||
ringcentral.com
|
||||
ritouki.jp
|
||||
rlwlw.com
|
||||
rmjdw.com
|
||||
rnw.nl
|
||||
robtex.com
|
||||
robustnessiskey.com
|
||||
rocmp.org
|
||||
rojo.com
|
||||
roksa.pl
|
||||
ronjoneswriter.com
|
||||
roodo.com
|
||||
rosechina.net
|
||||
rotten.com
|
||||
rottetstudio.com
|
||||
routledge.com
|
||||
rsf-chinese.org
|
||||
rsf.org
|
||||
rssmeme.com
|
||||
rtbot.net
|
||||
rthk.hk
|
||||
rthk.hk.edgesuite.net
|
||||
rthk.org.hk
|
||||
rti.org.tw
|
||||
rtl.de
|
||||
ruanyifeng.com
|
||||
rubyfortune.com
|
||||
runningonjuice.com
|
||||
rushbee.com
|
||||
rutube.ru
|
||||
rutwitter.com
|
||||
ruyiseek.com
|
||||
rxhj.net
|
||||
s-cute.com
|
||||
s-dragon.org
|
||||
s.xiaod.in
|
||||
s1heng.com
|
||||
s3-eu-west-1.amazonaws.com
|
||||
s3.amazonaws.com
|
||||
s4miniarchive.com
|
||||
s8forum.com
|
||||
sa.hao123.com
|
||||
sacom.hk
|
||||
sadpanda.us
|
||||
sadyoutube.com
|
||||
safeforwork.net
|
||||
safeway.com
|
||||
sai-zen-sen.jp
|
||||
saiq.me
|
||||
sakuralive.com
|
||||
salegamez.cc
|
||||
salvation.org.hk
|
||||
samair.ru
|
||||
sambhota.org
|
||||
sammyjs.org
|
||||
samsoff.es
|
||||
sandnoble.com
|
||||
sankaizok.com
|
||||
sanmin.com.tw
|
||||
sapikachu.net
|
||||
savemedia.com
|
||||
savetibet.de
|
||||
savetibet.fr
|
||||
savetibet.nl
|
||||
savetibet.org
|
||||
savetibet.ru
|
||||
savevid.com
|
||||
saveyoutube.com
|
||||
savings.com
|
||||
say2.info
|
||||
sbnation.com
|
||||
sbobet.com
|
||||
sbs.com.au
|
||||
scala-sbt.org
|
||||
scalatest.org
|
||||
scasino.com
|
||||
schema.org
|
||||
scholarships.com
|
||||
schooltunnel.net
|
||||
sciencemag.org
|
||||
scim.ag
|
||||
scmp.com
|
||||
scmpchinese.com
|
||||
scorecardresearch.com
|
||||
scribd.com
|
||||
scriptspot.com
|
||||
se-duc-tive.com
|
||||
seamless.com
|
||||
seapuff.com
|
||||
searchtruth.com
|
||||
seattlecoffeegear.com
|
||||
secretchina.com
|
||||
secretgarden.no
|
||||
secretsline.biz
|
||||
secure.freeyellow.com
|
||||
secure.wikimedia.org
|
||||
securitykiss.com
|
||||
seesmic.com
|
||||
seevpn.com
|
||||
seezone.net
|
||||
sejie.com
|
||||
sendoid.com
|
||||
sendspace.com
|
||||
sendvid.com
|
||||
sensortower.com
|
||||
sephora.com
|
||||
service.urchin.com
|
||||
sesawe.net
|
||||
sesawe.org
|
||||
sethwklein.net
|
||||
sevenload.com
|
||||
sex-11.com
|
||||
sex.com
|
||||
sex3.com
|
||||
sex8.cc
|
||||
sexandsubmission.com
|
||||
sexbot.com
|
||||
sexdelivery.com
|
||||
sexfind.com
|
||||
sexhu.com
|
||||
sexhuang.com
|
||||
sexinsex.net
|
||||
sextracker.com
|
||||
sextube.com
|
||||
sextvx.com
|
||||
sexu.com
|
||||
sexy.com
|
||||
sf.net
|
||||
sfileydy.com
|
||||
sftuk.org
|
||||
sh3lls.net
|
||||
sha7.info
|
||||
shadow.ma
|
||||
shadowsocks.org
|
||||
shahamat-english.com
|
||||
shambhalasun.com
|
||||
shangfang.org
|
||||
shapeservices.com
|
||||
shapeservices.net
|
||||
share.ovi.com
|
||||
share.skype.com
|
||||
share.youthwant.com.tw
|
||||
sharebee.com
|
||||
sharecool.org
|
||||
sharenxs.com
|
||||
sharkdolphin.com
|
||||
sharpdaily.com.hk
|
||||
sharpdaily.hk
|
||||
sharpdaily.tw
|
||||
shat-tibet.com
|
||||
shaunthesheep.com
|
||||
sheikyermami.com
|
||||
shellfire.de
|
||||
shellmix.com
|
||||
shenshou.org
|
||||
shenyun.com
|
||||
shenyunperformingarts.org
|
||||
shenzhoufilm.com
|
||||
sherdog.com
|
||||
shifeike.blog125.fc2blog.net
|
||||
shinychan.com
|
||||
shipcamouflage.com
|
||||
shitaotv.org
|
||||
shixiao.org
|
||||
shizhao.org
|
||||
shkspr.mobi
|
||||
shodanhq.com
|
||||
shop2000.com.tw
|
||||
shopping.com
|
||||
shoprite.com
|
||||
showbiz.omy.sg
|
||||
showtime.jp
|
||||
shutterstock.com
|
||||
shwchurch3.com
|
||||
si.wsj.net
|
||||
sickfacebook.com
|
||||
sidelinesnews.com
|
||||
sidelinessportseatery.com
|
||||
simboli-facebook.com
|
||||
simbolostwitter.com
|
||||
simplecd.org
|
||||
simpleproductivityblog.com
|
||||
sin1.g.adnxs.com
|
||||
singaporepools.com.sg
|
||||
singtao.com
|
||||
singyoutube.com
|
||||
sino-monthly.com
|
||||
sinoants.com
|
||||
sinocast.com
|
||||
sinocism.com
|
||||
sinomontreal.ca
|
||||
sinonet.ca
|
||||
sinopitt.info
|
||||
sinoquebec.com
|
||||
sipml5.org
|
||||
sirina.tv
|
||||
sis.xxx
|
||||
sis001.com
|
||||
sis001.us
|
||||
site90.net
|
||||
sitebro.tw
|
||||
sitefile.org
|
||||
sitekreator.com
|
||||
siteks.uk.to
|
||||
sitemaps.org
|
||||
sitetag.us
|
||||
skimtube.com
|
||||
skybet.com
|
||||
skyhighpremium.com
|
||||
skype.com
|
||||
skyvegas.com
|
||||
slack-files.com
|
||||
slack-msgs.com
|
||||
slack.com
|
||||
slacker.com
|
||||
slashdot.org
|
||||
slavasoft.com
|
||||
slaytizle.com
|
||||
slheng.com
|
||||
slickvpn.com
|
||||
slideshare.net
|
||||
slinkset.com
|
||||
slutload.com
|
||||
slyuser.com
|
||||
smarthosts.googlecode.com
|
||||
smchbooks.com
|
||||
smhric.org
|
||||
snagajob.com
|
||||
snapchat.com
|
||||
snaptu.com
|
||||
sndcdn.com
|
||||
sneakme.net
|
||||
snooper.co.uk
|
||||
snowlionpub.com
|
||||
snowpear.com
|
||||
so-ga.net
|
||||
so-news.com
|
||||
sobees.com
|
||||
soc.mil
|
||||
socialwhale.com
|
||||
sockslist.net
|
||||
sod.co.jp
|
||||
soft4fun.net
|
||||
softether-download.com
|
||||
softether.co.jp
|
||||
softether.org
|
||||
softwarebychuck.com
|
||||
softwaredownload.gitbooks.io
|
||||
sogclub.com
|
||||
sogrady.me
|
||||
soh.tw
|
||||
sohcradio.com
|
||||
sohfrance.org
|
||||
sokamonline.com
|
||||
solopeliculasgratis.com
|
||||
solozorro.tk
|
||||
somee.com
|
||||
songjianjun.com
|
||||
sonidodelaesperanza.org
|
||||
sopcast.com
|
||||
sopcast.org
|
||||
sorting-algorithms.com
|
||||
soubory.com
|
||||
soumo.info
|
||||
soundcloud.com
|
||||
soundofhope.kr
|
||||
soundofhope.org
|
||||
soup.io
|
||||
soupofmedia.com
|
||||
sourceforge.net
|
||||
southnews.com.tw
|
||||
sowers.org.hk
|
||||
space-scape.com
|
||||
spankbang.com
|
||||
spankwire.com
|
||||
spapps.co
|
||||
spb.com
|
||||
speakerdeck.com
|
||||
speckleapp.com
|
||||
speedpluss.org
|
||||
spencertipping.com
|
||||
spike.com
|
||||
spinejs.com
|
||||
spoiledvirgins.com
|
||||
spoilertv.com
|
||||
sportingbet.com
|
||||
sports.williamhill.com
|
||||
sportsmansoutdoorsuperstore.com
|
||||
spotflux.com
|
||||
spotify.com
|
||||
springboardplatform.com
|
||||
sprinklr.com
|
||||
sproutcore.com
|
||||
spysurfing.com
|
||||
squarespace.com
|
||||
srcf.ucam.org
|
||||
ssense.com
|
||||
ssh91.com
|
||||
ssl-images-amazon.com
|
||||
sstatic.net
|
||||
ssyoutube.com
|
||||
stackfile.com
|
||||
stackoverflow.com
|
||||
standupfortibet.org
|
||||
stanford.edu
|
||||
starp2p.com
|
||||
startpage.com
|
||||
state168.com
|
||||
static.apple.nextmedia.com
|
||||
static.byhours.com
|
||||
static.digg.com
|
||||
staticflickr.com
|
||||
status.twhirl.org
|
||||
stc.com.sa
|
||||
steampowered.com
|
||||
steel-storm.com
|
||||
stepmania.com
|
||||
steves-digicams.com
|
||||
sthoo.com
|
||||
stickam.com
|
||||
stickeraction.com
|
||||
stileproject.com
|
||||
stirileprotv.ro
|
||||
stltoday.com
|
||||
stonegames.net
|
||||
stoneip.info
|
||||
stopchildpornonfacebook.com
|
||||
stoptibetcrisis.net
|
||||
storagenewsletter.com
|
||||
storify.com
|
||||
storm.mg
|
||||
stoweboyd.com
|
||||
stranabg.com
|
||||
streamie.org
|
||||
streamingthe.net
|
||||
streamtwitter.com
|
||||
strongvpn.com
|
||||
strongwindpress.com
|
||||
student.tw
|
||||
studentsforafreetibet.org
|
||||
stuffimreading.com
|
||||
stuffimreading.net
|
||||
stumbleupon.com
|
||||
stupidbeauty.com
|
||||
stupidvideos.com
|
||||
subacme.rerouted.org
|
||||
subito.it
|
||||
sublimetext.com
|
||||
submitexpress.com
|
||||
sufeng.org
|
||||
sugarsync.com
|
||||
summify.com
|
||||
sumrando.com
|
||||
sun1911.com
|
||||
sunporno.com
|
||||
suoluo.org
|
||||
superdrug.com
|
||||
superpages.com
|
||||
supertweet.net
|
||||
suprememastertv.com
|
||||
surfeasy.com
|
||||
surfeasy.com.au
|
||||
surfert.nl
|
||||
surrenderat20.net
|
||||
susjed.com
|
||||
suumo.jp
|
||||
suyangg.com
|
||||
svwind.com
|
||||
swagbucks.com
|
||||
sweux.com
|
||||
swift-tools.net
|
||||
sydneytoday.com
|
||||
sylfoundation.org
|
||||
symauth.com
|
||||
symcb.com
|
||||
symcd.com
|
||||
syncback.com
|
||||
sysadmin1138.net
|
||||
sysresccd.org
|
||||
sytes.net
|
||||
szbbs.net
|
||||
szetowah.org.hk
|
||||
t-shirt.pl
|
||||
t.co
|
||||
t.huhaitai.com
|
||||
t.kun.im
|
||||
t.orzdream.com
|
||||
t35.com
|
||||
t66y.com
|
||||
t88.ca
|
||||
taa-usa.org
|
||||
taaze.tw
|
||||
tablesgenerator.com
|
||||
tabtter.jp
|
||||
tacem.org
|
||||
taedp.org.tw
|
||||
tafaward.com
|
||||
tafm.org.tw
|
||||
tagwalk.com
|
||||
tagxedo.com
|
||||
tahr.org.tw
|
||||
taipei.gov.tw
|
||||
taipeisociety.org
|
||||
taiwan-sex.com
|
||||
taiwanbible.com
|
||||
taiwandaily.net
|
||||
taiwanheart.ning.com
|
||||
taiwankiss.com
|
||||
taiwannation.50webs.com
|
||||
taiwannation.com
|
||||
taiwannation.com.tw
|
||||
taiwannews.com.tw
|
||||
taiwanonline.cc
|
||||
taiwantp.net
|
||||
taiwantt.org.tw
|
||||
taiwanus.net
|
||||
taiwanyes.com
|
||||
taiwanyes.ning.com
|
||||
taiyangbao.ca
|
||||
talk853.com
|
||||
talkboxapp.com
|
||||
tamiaode.tk
|
||||
tanc.org
|
||||
tangben.com
|
||||
taoism.net
|
||||
taolun.info
|
||||
taosl.net
|
||||
tap11.com
|
||||
tapbots.com
|
||||
target.com
|
||||
tarr.uspto.gov
|
||||
taup.net
|
||||
taup.org.tw
|
||||
taweet.com
|
||||
tbpic.info
|
||||
tbsec.org
|
||||
tbsn.org
|
||||
tbsseattle.org
|
||||
tccwonline.org
|
||||
tcewf.org
|
||||
tchrd.org
|
||||
tcno.net
|
||||
td.org
|
||||
tdesktop.com
|
||||
teamamericany.com
|
||||
teamseesmic.com
|
||||
teashark.com
|
||||
tech2.in.com
|
||||
techcrunch.com
|
||||
techlifeweb.com
|
||||
techparaiso.com
|
||||
teck.in
|
||||
teensinasia.com
|
||||
tehran.ir
|
||||
telecomspace.com
|
||||
telegram.me
|
||||
telegram.org
|
||||
telegraph.co.uk
|
||||
telelistas.net
|
||||
tenacy.com
|
||||
test.com
|
||||
tetronics.com
|
||||
tew.org
|
||||
tfbnw.net
|
||||
th.hao123.com
|
||||
the-sun.on.cc
|
||||
theampfactory.com
|
||||
theappleblog.com
|
||||
theatrum-belli.com
|
||||
thebcomplex.com
|
||||
theblaze.com
|
||||
theblemish.com
|
||||
thebobs.com
|
||||
thebodyshop-usa.com
|
||||
thecheeky.com
|
||||
thechinabeat.org
|
||||
thechinastory.org
|
||||
thecoveteur.com
|
||||
thedailywh.at
|
||||
thedieline.com
|
||||
thediplomat.com
|
||||
thedw.us
|
||||
theepochtimes.com
|
||||
thefacebook.com
|
||||
thefourtheye.in
|
||||
thefrontier.hk
|
||||
thegatesnotes.com
|
||||
thegioitinhoc.vn
|
||||
thegreatcourses.com
|
||||
theguardian.co
|
||||
theguardian.com
|
||||
thehots.info
|
||||
thehousenews.com
|
||||
thehun.net
|
||||
thehungrydudes.com
|
||||
theinitium.com
|
||||
theinternetwishlist.com
|
||||
thelifeyoucansave.com
|
||||
thelius.org
|
||||
thenational.ae
|
||||
thenewslens.com
|
||||
thenorthface.com
|
||||
thepetitionsite.com
|
||||
thepiratebay.org
|
||||
thepiratebay.se
|
||||
theqii.info
|
||||
thereallove.kr
|
||||
therock.net.nz
|
||||
thesartorialist.com
|
||||
thesnippetapp.com
|
||||
thespeeder.com
|
||||
thestandnews.com
|
||||
thetibetconnection.org
|
||||
thetibetmuseum.org
|
||||
thetibetpost.com
|
||||
thetrotskymovie.com
|
||||
thetruthaboutcars.com
|
||||
thevivekspot.com
|
||||
thewgo.org
|
||||
thinkingtaiwan.com
|
||||
thisav.com
|
||||
thisiswhyyouarefat.com
|
||||
thkphoto.com
|
||||
thomasbernhard.org
|
||||
threatchaos.com
|
||||
throughnightsfire.com
|
||||
thumbr.io
|
||||
thumbzilla.com
|
||||
thywords.com
|
||||
tiananmenmother.org
|
||||
tiananmenuniv.com
|
||||
tiananmenuniv.net
|
||||
tiandixing.org
|
||||
tianhuayuan.com
|
||||
tianlawoffice.com
|
||||
tiantibooks.org
|
||||
tianzhu.org
|
||||
tiava.com
|
||||
tibet-foundation.org
|
||||
tibet-house-trust.co.uk
|
||||
tibet-info.net
|
||||
tibet-initiative.de
|
||||
tibet-munich.de
|
||||
tibet.a.se
|
||||
tibet.at
|
||||
tibet.ca
|
||||
tibet.com
|
||||
tibet.fr
|
||||
tibet.net
|
||||
tibet.nu
|
||||
tibet.org
|
||||
tibet.org.tw
|
||||
tibetaid.org
|
||||
tibetalk.com
|
||||
tibetan-alliance.org
|
||||
tibetanarts.org
|
||||
tibetanculture.org
|
||||
tibetanpaintings.com
|
||||
tibetanphotoproject.com
|
||||
tibetanwomen.org
|
||||
tibetanyouthcongress.org
|
||||
tibetcharity.dk
|
||||
tibetcharity.in
|
||||
tibetcity.com
|
||||
tibetcollection.com
|
||||
tibetcorps.org
|
||||
tibetfocus.com
|
||||
tibetfund.org
|
||||
tibethouse.jp
|
||||
tibethouse.org
|
||||
tibethouse.us
|
||||
tibetjustice.org
|
||||
tibetmuseum.org
|
||||
tibetnetwork.org
|
||||
tibetoffice.ch
|
||||
tibetoffice.com.au
|
||||
tibetoffice.org
|
||||
tibetonline.com
|
||||
tibetonline.tv
|
||||
tibetoralhistory.org
|
||||
tibetrelieffund.co.uk
|
||||
tibetsites.com
|
||||
tibetsun.com
|
||||
tibettimes.net
|
||||
tibetwrites.org
|
||||
tidyread.com
|
||||
tiffanyarment.com
|
||||
timdir.com
|
||||
time.com
|
||||
times.hinet.net
|
||||
timsah.com
|
||||
tintuc101.com
|
||||
tiny.cc
|
||||
tinychat.com
|
||||
tinymce.com
|
||||
tinypaste.com
|
||||
tinypic.com
|
||||
tinysubversions.com
|
||||
tistory.com
|
||||
tjholowaychuk.com
|
||||
tkcs-collins.com
|
||||
tkforum.tk
|
||||
tl.gd
|
||||
tldp.org
|
||||
tmagazine.com
|
||||
tmi.me
|
||||
tnaflix.com
|
||||
tnews.cc
|
||||
tnp.org
|
||||
togetter.com
|
||||
tokfm.pl
|
||||
tokyo-247.com
|
||||
tokyo-hot.com
|
||||
tokyo-porn-tube.com
|
||||
tokyo-tube.com
|
||||
tokyocn.com
|
||||
tomayko.com
|
||||
toms.com
|
||||
tomsc.com
|
||||
tono-oka.jp
|
||||
tonyyan.net
|
||||
toodoc.com
|
||||
toom.kir.jp
|
||||
toonel.net
|
||||
top81.ws
|
||||
topchinesenews.com
|
||||
topic.youthwant.com.tw
|
||||
topnews.in
|
||||
topshare.us
|
||||
topshareware.com
|
||||
topstyle4.com
|
||||
topsy.com
|
||||
toptip.ca
|
||||
tor.blingblingsquad.net
|
||||
tor.updatestar.com
|
||||
tora.to
|
||||
torontosun.com
|
||||
torproject.org
|
||||
torproject.us
|
||||
torrentcrazy.com
|
||||
torrentkitty.com
|
||||
torrentprivacy.com
|
||||
torrentproject.se
|
||||
torrenty.org
|
||||
torrentz.eu
|
||||
torvpn.com
|
||||
tosh.comedycentral.com
|
||||
toshiba.com
|
||||
touch99.com
|
||||
toukoucity.to
|
||||
toutfr.com
|
||||
toypark.in
|
||||
toytractorshow.com
|
||||
tparents.org
|
||||
tpi.org.tw
|
||||
tr.im
|
||||
traffichaus.com
|
||||
trans.wenweipo.com
|
||||
transgressionism.org
|
||||
transparency.org
|
||||
travelinlocal.com
|
||||
treemall.com.tw
|
||||
trendhunter.com
|
||||
trendsmap.com
|
||||
trialofccp.org
|
||||
trickfacebook.com
|
||||
tricksfacebook.com
|
||||
tripadvisor.in
|
||||
tripod.com
|
||||
trojmiasto.pl
|
||||
trouw.nl
|
||||
trovit.fr
|
||||
trovit.it
|
||||
trt.net.tr
|
||||
trtc.com.tw
|
||||
trucchifacebook.com
|
||||
trulyergonomic.com
|
||||
trustedbi.com
|
||||
truth101.co.tv
|
||||
truthcn.com
|
||||
truveo.com
|
||||
try.dartlang.org
|
||||
tsctv.net
|
||||
tsdr.uspto.gov
|
||||
tsemtulku.com
|
||||
tsquare.tv
|
||||
tsu.co
|
||||
tsu.org.tw
|
||||
tsunagarumon.com
|
||||
tsuru-bird.net
|
||||
tt-rss.org
|
||||
tt1069.com
|
||||
tt48.tumblr.com
|
||||
tttan.com
|
||||
tu8964.com
|
||||
tuanzt.com
|
||||
tubaholic.com
|
||||
tube.com
|
||||
tube8.com
|
||||
tube911.com
|
||||
tubecao.com
|
||||
tubegals.com
|
||||
tubeislam.com
|
||||
tubepornclassic.com
|
||||
tubewolf.com
|
||||
tui.orzdream.com
|
||||
tuidang.net
|
||||
tuidang.org
|
||||
tuitwit.com
|
||||
tumblr.awflasher.com
|
||||
tumblr.com
|
||||
tumblweed.org
|
||||
tumutanzi.com
|
||||
tunein.com
|
||||
tunnelbear.com
|
||||
tuo8.hk
|
||||
tuo8.org
|
||||
turansam.org
|
||||
turbobit.net
|
||||
turbohide.com
|
||||
turbotwitter.com
|
||||
turningtorso.com
|
||||
turntable.fm
|
||||
tushycash.com
|
||||
tusjuegosparafacebook.com
|
||||
tuxtraining.com
|
||||
tuzaijidi.com
|
||||
tv-intros.com
|
||||
tv.com
|
||||
tv.com.pk
|
||||
tv.nu
|
||||
tv.on.cc
|
||||
tvanouvelles.ca
|
||||
tvants.com
|
||||
tvb.com
|
||||
tvboxnow.com
|
||||
tvider.com
|
||||
tvunetworks.com
|
||||
tw-npo.org
|
||||
tw.gigacircle.com
|
||||
tw.hao123.com
|
||||
tw.jiepang.com
|
||||
tw.streetvoice.com
|
||||
tw.voa.mobi
|
||||
tw01.org
|
||||
twa.sh
|
||||
twaitter.com
|
||||
twapperkeeper.com
|
||||
twaud.io
|
||||
twavtv.com
|
||||
twbbs.net.tw
|
||||
twbbs.org
|
||||
twbbs.tw
|
||||
twblogger.com
|
||||
tweepguide.com
|
||||
tweeplike.me
|
||||
tweepmag.com
|
||||
tweepml.org
|
||||
tweetbackup.com
|
||||
tweetboard.com
|
||||
tweetboner.biz
|
||||
tweetdeck.com
|
||||
tweete.net
|
||||
tweetedtimes.com
|
||||
tweetmeme.com
|
||||
tweetmylast.fm
|
||||
tweetphoto.com
|
||||
tweetrans.com
|
||||
tweetree.com
|
||||
tweets.seraph.me
|
||||
tweettunnel.com
|
||||
tweetvalue.com
|
||||
tweetwally.com
|
||||
tweetymail.com
|
||||
twenga.fr
|
||||
twerkingbutt.com
|
||||
twftp.org
|
||||
twibase.com
|
||||
twibble.de
|
||||
twibbon.com
|
||||
twibs.com
|
||||
twicsy.com
|
||||
twiends.com
|
||||
twifan.com
|
||||
twiffo.com
|
||||
twiggit.org
|
||||
twilightsex.com
|
||||
twillo.com
|
||||
twilog.org
|
||||
twimbow.com
|
||||
twimg.com
|
||||
twimg.edgesuite.net
|
||||
twindexx.com
|
||||
twip.me
|
||||
twipple.jp
|
||||
twishort.com
|
||||
twistar.cc
|
||||
twister.net.co
|
||||
twisterio.com
|
||||
twisternow.com
|
||||
twistory.net
|
||||
twit2d.com
|
||||
twitbrowser.net
|
||||
twitcause.com
|
||||
twitch.tv
|
||||
twitgether.com
|
||||
twitgoo.com
|
||||
twitiq.com
|
||||
twitlonger.com
|
||||
twitmania.com
|
||||
twitoaster.com
|
||||
twitonmsn.com
|
||||
twitpic.com
|
||||
twitreferral.com
|
||||
twitstat.com
|
||||
twittanic.com
|
||||
twittbot.net
|
||||
twitter-icon.com
|
||||
twitter.com
|
||||
twitter.com.au
|
||||
twitter.jp
|
||||
twitter4j.org
|
||||
twittercentral.com.br
|
||||
twittercounter.com
|
||||
twitterfall.com
|
||||
twitterfeed.com
|
||||
twittergadget.com
|
||||
twitterkr.com
|
||||
twittermail.com
|
||||
twittertim.es
|
||||
twitterwall.me
|
||||
twitthat.com
|
||||
twitturk.com
|
||||
twitturly.com
|
||||
twitvid.com
|
||||
twitzap.com
|
||||
twiyia.com
|
||||
twotwitter.com
|
||||
twreg.info
|
||||
twstar.net
|
||||
twt.fm
|
||||
twt.tl
|
||||
twtkr.com
|
||||
twtr2src.ogaoga.org
|
||||
twtrland.com
|
||||
twttr.com
|
||||
twurl.nl
|
||||
twyac.org
|
||||
twylah.com
|
||||
tycool.com
|
||||
tynsoe.org
|
||||
typekit.net
|
||||
typepad.com
|
||||
typesafe.com
|
||||
tzangms.com
|
||||
ub0.cc
|
||||
uberproxy.net
|
||||
ubervu.com
|
||||
ubnt.com
|
||||
ubuntu.com
|
||||
ucdc1998.org
|
||||
ucoz.com
|
||||
uderzo.it
|
||||
udn.com
|
||||
udn.com.tw
|
||||
uforadio.com.tw
|
||||
ufreevpn.com
|
||||
ugo.com
|
||||
uhaul.com
|
||||
uhrp.org
|
||||
uighur.nl
|
||||
uighurbiz.net
|
||||
uinyan.tumblr.com
|
||||
ukchinese.com
|
||||
ukliferadio.co.uk
|
||||
ulike.net
|
||||
ulozto.cz
|
||||
ulozto.net
|
||||
ultrareach.net
|
||||
ultrasurf.us
|
||||
ultrasurfing.com
|
||||
ultravpn.fr
|
||||
ultraxs.com
|
||||
umich.edu
|
||||
unblock-us.com
|
||||
unblock.cn.com
|
||||
unblocksit.es
|
||||
unblockthatsite.net
|
||||
unblockyoutube.co.uk
|
||||
unblockyoutube.com
|
||||
uncyclomedia.org
|
||||
uncyclopedia.info
|
||||
uncyclopedia.tw
|
||||
underwoodammo.com
|
||||
unholyknight.com
|
||||
uni-due.de
|
||||
uni.cc
|
||||
unicode.org
|
||||
unification.net
|
||||
unification.org.tw
|
||||
uninstallapp.org
|
||||
uniteddaily.com.my
|
||||
unix100.com
|
||||
unknownspace.org
|
||||
unodedos.com
|
||||
unpo.org
|
||||
uocn.org
|
||||
upholdjustice.org
|
||||
upload.wikimedia.org
|
||||
upload4u.info
|
||||
uploaded.net
|
||||
uploaded.to
|
||||
uploadstation.com
|
||||
uproxy.org
|
||||
upwill.org
|
||||
ur7s.com
|
||||
urbanoutfitters.com
|
||||
urlborg.com
|
||||
urlparser.com
|
||||
us.to
|
||||
usacn.com
|
||||
usaip.eu
|
||||
usaupload.net
|
||||
users.skynet.be
|
||||
usfk.mil
|
||||
usinfo.state.gov
|
||||
usma.edu
|
||||
usmc.mil
|
||||
usmgtcg.ning.com
|
||||
ussearch.com
|
||||
ustream.tv
|
||||
ustwrap.info
|
||||
usus.cc
|
||||
uushare.com
|
||||
uwants.com
|
||||
uwants.net
|
||||
uyghur-j.org
|
||||
uyghuramerican.org
|
||||
uyghurcanadiansociety.org
|
||||
uyghurcongress.org
|
||||
uyghurensemble.co.uk
|
||||
uyghurpen.org
|
||||
uyghurpress.com
|
||||
uygur.fc2web.com
|
||||
uygur.org
|
||||
uymaarip.com
|
||||
uyttt.com
|
||||
v-state.org
|
||||
v2ex.com
|
||||
v70.us
|
||||
v7976888.info
|
||||
vaayoo.com
|
||||
value-domain.com
|
||||
van001.com
|
||||
van698.com
|
||||
vanilla-jp.com
|
||||
vanpeople.com
|
||||
vansky.com
|
||||
vapurl.com
|
||||
varnish-cache.org
|
||||
vatn.org
|
||||
vcf-online.org
|
||||
vcfbuilder.org
|
||||
vds.rightster.com
|
||||
vectorstock.com
|
||||
veempiire.com
|
||||
vegasred.com
|
||||
vegorpedersen.com
|
||||
velkaepocha.sk
|
||||
venbbs.com
|
||||
venchina.com
|
||||
ventureswell.com
|
||||
veoh.com
|
||||
verizon.net
|
||||
verticalresponse.com
|
||||
verybs.com
|
||||
vesti.ru
|
||||
vevo.com
|
||||
vft.com.tw
|
||||
viamichelin.com
|
||||
viber.com
|
||||
victorinox.com
|
||||
video.aol.ca
|
||||
video.aol.co.uk
|
||||
video.aol.com
|
||||
video.ap.org
|
||||
video.fdbox.com
|
||||
video.foxbusiness.com
|
||||
video.tiscali.it
|
||||
video2brain.com
|
||||
videobam.com
|
||||
videodetective.com
|
||||
videomega.tv
|
||||
videomo.com
|
||||
videopediaworld.com
|
||||
videosdeyoutube.com
|
||||
vidoemo.com
|
||||
vidoevo.com
|
||||
viemo.com
|
||||
views.fm
|
||||
vikeng.info
|
||||
viki.com
|
||||
villagevoice.com
|
||||
vimeo.com
|
||||
vimeocdn.com
|
||||
vimgolf.com
|
||||
vimperator.org
|
||||
vincnd.com
|
||||
vine.co
|
||||
vineapp.com
|
||||
vinniev.com
|
||||
visibletweets.com
|
||||
vivatube.com
|
||||
vjmedia.com.hk
|
||||
vllcs.org
|
||||
vlog.xuite.net
|
||||
vmixcore.com
|
||||
vn.hao123.com
|
||||
voa.gov
|
||||
voacantonese.com
|
||||
voachinese.com
|
||||
voachineseblog.com
|
||||
voafanti.com
|
||||
voagd.com
|
||||
voanews.com
|
||||
voatibetan.com
|
||||
vocn.tv
|
||||
voicetube.tw
|
||||
vongutenberg.com
|
||||
vot.org
|
||||
vouchercodes.co.uk
|
||||
vovo2000.com
|
||||
vovokan.com
|
||||
vox-cdn.com
|
||||
voy.com
|
||||
vpnbook.com
|
||||
vpncup.com
|
||||
vpnfire.com
|
||||
vpngate.jp
|
||||
vpngate.net
|
||||
vpnpop.com
|
||||
vpnpronet.com
|
||||
vpnreviewz.com
|
||||
vporn.com
|
||||
vtunnel.com
|
||||
vuku.ru
|
||||
vworldc.com
|
||||
w.idaiwan.com
|
||||
w.org
|
||||
w3schools.com
|
||||
waffle1999.com
|
||||
wahas.com
|
||||
waigaobu.com
|
||||
waikeung.org
|
||||
waiwaier.com
|
||||
wallornot.org
|
||||
wallpapercasa.com
|
||||
wan-press.org
|
||||
wanderinghorse.net
|
||||
wangafu.net
|
||||
wangjinbo.org
|
||||
wanglixiong.com
|
||||
wango.org
|
||||
wangruoshui.net
|
||||
wangruowang.org
|
||||
want-daily.com
|
||||
wantchinatimes.com
|
||||
wantyoutube.com
|
||||
wapedia.mobi
|
||||
waselpro.com
|
||||
washeng.net
|
||||
watchinese.com
|
||||
watchmygf.net
|
||||
wattpad.com
|
||||
wav.tv
|
||||
wdf5.com
|
||||
wearehairy.com
|
||||
wearn.com
|
||||
web2project.net
|
||||
webbang.net
|
||||
webcams.com
|
||||
webevader.org
|
||||
webfee.tk
|
||||
webjb.org
|
||||
weblagu.com
|
||||
webmproject.org
|
||||
webnode.com
|
||||
webrtc.org
|
||||
webrush.net
|
||||
webs-tv.net
|
||||
webs.com
|
||||
webshots.com
|
||||
websitepulse.com
|
||||
websnapr.com
|
||||
webwarper.net
|
||||
webworkerdaily.com
|
||||
webzen.com
|
||||
weeewooo.net
|
||||
weekmag.info
|
||||
wefacebook.com
|
||||
wefightcensorship.org
|
||||
wefong.com
|
||||
wehaslinks.com
|
||||
weiboleak.com
|
||||
weigegebyc.dreamhosters.com
|
||||
weijingsheng.org
|
||||
weiming.info
|
||||
weiquanwang.org
|
||||
weisuo.ws
|
||||
wellplacedpixels.com
|
||||
welovecock.com
|
||||
wemigrate.org
|
||||
wen.ru
|
||||
wengewang.com
|
||||
wengewang.org
|
||||
wenhui.ch
|
||||
wenku.com
|
||||
wenxuecity.com
|
||||
wenyunchao.com
|
||||
wepn.info
|
||||
westca.com
|
||||
westernshugdensociety.org
|
||||
westernwolves.com
|
||||
westhost.com
|
||||
westkit.net
|
||||
westpoint.edu
|
||||
westword.com
|
||||
wet123.com
|
||||
wetplace.com
|
||||
wetpussygames.com
|
||||
wetransfer.com
|
||||
wexiaobo.org
|
||||
wezhiyong.org
|
||||
wezone.net
|
||||
wforum.com
|
||||
whatblocked.com
|
||||
whatbrowser.org
|
||||
whendidyoujointwitter.com
|
||||
whereiswerner.com
|
||||
wheretowatch.com
|
||||
whippedass.com
|
||||
whitebear.freebearblog.org
|
||||
who.is
|
||||
whoownsfacebook.com
|
||||
whotalking.com
|
||||
whydidyoubuymethat.com
|
||||
whylover.com
|
||||
whyx.org
|
||||
wifemovies.net
|
||||
wiki.cnitter.com
|
||||
wiki.gamerp.jp
|
||||
wiki.jqueryui.com
|
||||
wiki.moegirl.org
|
||||
wiki.oauth.net
|
||||
wiki.phonegap.com
|
||||
wikibooks.org
|
||||
wikidata.org
|
||||
wikidot.com
|
||||
wikileaks.ch
|
||||
wikileaks.de
|
||||
wikileaks.eu
|
||||
wikileaks.lu
|
||||
wikileaks.org
|
||||
wikileaks.pl
|
||||
wikilivres.info
|
||||
wikimapia.org
|
||||
wikimedia.org
|
||||
wikimedia.org.mo
|
||||
wikimediafoundation.org
|
||||
wikinews.org
|
||||
wikipedia.com
|
||||
wikipedia.org
|
||||
wikiquote.org
|
||||
wikisource.org
|
||||
wikiversity.org
|
||||
wikivoyage.org
|
||||
wikiwiki.jp
|
||||
wiksa.com
|
||||
wiktionary.org
|
||||
wildammo.com
|
||||
wiley.com
|
||||
williamhillpoker.com
|
||||
willw.net
|
||||
windowsmedia.com
|
||||
windowsphoneme.com
|
||||
wingamestore.com
|
||||
winnipegsun.com
|
||||
winwhispers.info
|
||||
wiredbytes.com
|
||||
wiredpen.com
|
||||
wireshark.org
|
||||
wisdompubs.org
|
||||
wisevid.com
|
||||
wistia.com
|
||||
wistia.net
|
||||
withgoogle.com
|
||||
witnessleeteaching.com
|
||||
witopia.net
|
||||
wiwo.de
|
||||
wixoo.com
|
||||
wlx.sowiki.net
|
||||
wmmail.ru
|
||||
wn.com
|
||||
wnacg.com
|
||||
wo.tc
|
||||
woeser.com
|
||||
woesermiddle-way.net
|
||||
wolfax.com
|
||||
womanwithin.com
|
||||
womensrightsofchina.org
|
||||
wonderlandads.com
|
||||
woopie.jp
|
||||
woopie.tv
|
||||
wordboner.com
|
||||
wordpress.com
|
||||
wordsandturds.com
|
||||
workatruna.com
|
||||
workerdemo.org.hk
|
||||
workersthebig.net
|
||||
worldcat.org
|
||||
worldjournal.com
|
||||
worldmarket.com
|
||||
worldnews01.com
|
||||
worstthingieverate.com
|
||||
wow-life.net
|
||||
wowlegacy.ml
|
||||
woxinghuiguo.com
|
||||
wozy.in
|
||||
wp.com
|
||||
wpmudev.org
|
||||
wpoforum.com
|
||||
wqlhw.com
|
||||
wqyd.org
|
||||
wrangl.com
|
||||
wrchina.org
|
||||
wretch.cc
|
||||
writelonger.com
|
||||
writer.zoho.com
|
||||
wsgzao.github.io
|
||||
wsj.com
|
||||
wsj.net
|
||||
wsjemail.com
|
||||
wtfpeople.com
|
||||
wuala.com
|
||||
wuerkaixi.com
|
||||
wufi.org.tw
|
||||
wufoo.com
|
||||
wuguoguang.com
|
||||
wujie.net
|
||||
wujieliulan.com
|
||||
wukangrui.net
|
||||
wwitv.com
|
||||
www.agoogleaday.com
|
||||
www.alliance.org.hk
|
||||
www.blogger.com
|
||||
www.chromeexperiments.com
|
||||
www.chromercise.com
|
||||
www.dartlang.org
|
||||
www.data-vocabulary.org
|
||||
www.emailintervention.com
|
||||
www.feedburner.com
|
||||
www.googlechinawebmaster.com
|
||||
www.googleinsidesearch.com
|
||||
www.googlemashups.com
|
||||
www.googlepreview.com
|
||||
www.googletagservices.com
|
||||
www.googlezeitgeist.com
|
||||
www.gosetsuden.jp
|
||||
www.minghui.org
|
||||
www.smhric.org
|
||||
www.teachparentstech.org
|
||||
www.textcube.com
|
||||
www.thegobridgeoglepuzzle.com
|
||||
www.thegooglepuzzle.com
|
||||
www.waveprotocol.org
|
||||
www.webm-ccl.org
|
||||
www.webmproject.org
|
||||
www.youtube-nocookie.com
|
||||
www2.ohchr.org
|
||||
www2.rocketbbs.com
|
||||
wzyboy.im
|
||||
x-art.com
|
||||
x-berry.com
|
||||
x-wall.org
|
||||
x.xcity.jp
|
||||
x1949x.com
|
||||
x365x.com
|
||||
xa.yimg.com
|
||||
xanga.com
|
||||
xbabe.com
|
||||
xbookcn.com
|
||||
xcafe.in
|
||||
xcritic.com
|
||||
xfm.pp.ru
|
||||
xgmyd.com
|
||||
xhamster.com
|
||||
xhcdn.com
|
||||
xianqiao.net
|
||||
xiaochuncnjp.com
|
||||
xiaohexie.com
|
||||
xiaolan.me
|
||||
xiaoma.org
|
||||
xiezhua.com
|
||||
xiezi.us
|
||||
xihua.es
|
||||
xing.com
|
||||
xinhuanet.org
|
||||
xinmiao.com.hk
|
||||
xinqimeng.over-blog.com
|
||||
xinsheng.net
|
||||
xinshijue.com
|
||||
xinyubbs.net
|
||||
xiongpian.com
|
||||
xite.ws
|
||||
xizang-zhiye.org
|
||||
xjp.cc
|
||||
xlfmwz.info
|
||||
xmbs.jp
|
||||
xml-training-guide.com
|
||||
xmovies.com
|
||||
xmusic.fm
|
||||
xnxx.com
|
||||
xpdo.net
|
||||
xpud.org
|
||||
xrentdvd.com
|
||||
xskywalker.com
|
||||
xtube.com
|
||||
xuchao.net
|
||||
xuchao.org
|
||||
xuzhiyong.net
|
||||
xuzhuoer.com
|
||||
xvedios.com
|
||||
xvideos.com
|
||||
xvideos.es
|
||||
xxbbx.com
|
||||
xxeronetxx.info
|
||||
xxx.com
|
||||
xxx.com.au
|
||||
xxxx.com.au
|
||||
xxxymovies.com
|
||||
xys.dxiong.com
|
||||
xys.org
|
||||
xysblogs.org
|
||||
xyy69.com
|
||||
xyy69.info
|
||||
yahoo.com
|
||||
yahoo.com.hk
|
||||
yahoo.com.tw
|
||||
yakbutterblues.com
|
||||
yam.com
|
||||
yangjianli.com
|
||||
yasni.co.uk
|
||||
yasukuni.or.jp
|
||||
ydy.com
|
||||
yeelou.com
|
||||
yeeyan.org
|
||||
yeeyi.com
|
||||
yegle.net
|
||||
yepi.com
|
||||
yes123.com.tw
|
||||
yesasia.com
|
||||
yesasia.com.hk
|
||||
yfrog.com
|
||||
yhcw.net
|
||||
yi.org
|
||||
yibada.com
|
||||
yibaochina.com
|
||||
yidio.com
|
||||
yilubbs.com
|
||||
yipub.com
|
||||
yobt.com
|
||||
yobt.tv
|
||||
yogichen.org
|
||||
yong.hu
|
||||
yorkbbs.ca
|
||||
youjizz.com
|
||||
youjizzlive.com
|
||||
youmaker.com
|
||||
youngfatties.com
|
||||
youngliving.com
|
||||
youpai.org
|
||||
youporn.com
|
||||
youporngay.com
|
||||
your-freedom.net
|
||||
yourepeat.com
|
||||
yourlisten.com
|
||||
yourlust.com
|
||||
yousendit.com
|
||||
youthbao.com
|
||||
youthnetradio.org
|
||||
youtu.be
|
||||
youtube-mp3.com
|
||||
youtube-nocookie.com
|
||||
youtube.com
|
||||
youtube.com.br
|
||||
youtube.com.my
|
||||
youtubecn.com
|
||||
youversion.com
|
||||
youxu.info
|
||||
ysku.in
|
||||
yslang.com
|
||||
ytht.net
|
||||
ytimg.com
|
||||
yuanming.net
|
||||
yuming.flnet.org
|
||||
yunchao.net
|
||||
yuvutu.com
|
||||
yvesgeleyn.com
|
||||
yx51.net
|
||||
yyets.com
|
||||
yyii.org
|
||||
yymaya.com
|
||||
yzzk.com
|
||||
zacebook.com
|
||||
zagat.com
|
||||
zain.com
|
||||
zalando.es
|
||||
zannel.com
|
||||
zaobao.com
|
||||
zaobao.com.sg
|
||||
zaozon.com
|
||||
zap.co.il
|
||||
zarias.com
|
||||
zattoo.com
|
||||
zaubacorp.com
|
||||
zaurus.org.uk
|
||||
zdassets.com
|
||||
zdnet.com.tw
|
||||
zdnet.fr
|
||||
zekamashi.net
|
||||
zend.com
|
||||
zend2.com
|
||||
zengjinyan.org
|
||||
zensur.freerk.com
|
||||
zeutch.com
|
||||
zfreet.com
|
||||
zgzcjj.net
|
||||
zh-tw.justin.tv
|
||||
zh.netlog.com
|
||||
zh.pokerstrategy.com
|
||||
zh.uncyclopedia.wikia.com
|
||||
zhanbin.net
|
||||
zhangboli.net
|
||||
zhangtianliang.com
|
||||
zhao.jinhai.de
|
||||
zhenghui.org
|
||||
zhengjian.org
|
||||
zhengwunet.org
|
||||
zhenlibu.info
|
||||
zhenxiang.biz
|
||||
zhibo5.com
|
||||
zhinengluyou.com
|
||||
zhongguo.ca
|
||||
zhongguorenquan.org
|
||||
zhongguotese.net
|
||||
zhongmeng.org
|
||||
zhreader.com
|
||||
zhufeng.me
|
||||
zhuichaguoji.org
|
||||
ziddu.com
|
||||
zideo.nl
|
||||
zillionk.com
|
||||
zinio.com
|
||||
ziplib.com
|
||||
ziporn.com
|
||||
zkaip.com
|
||||
zlib.net
|
||||
zomobo.net
|
||||
zonaeuropa.com
|
||||
zootool.com
|
||||
zoozle.net
|
||||
zozotown.com
|
||||
zshare.net
|
||||
zsrhao.com
|
||||
zuo.la
|
||||
zuobiao.me
|
||||
zuola.com
|
||||
zvereff.com
|
||||
zyzc9.com
|
||||
zzcartoon.com
|
||||
@@ -0,0 +1,144 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"io/ioutil"
|
||||
"log"
|
||||
"os"
|
||||
"proxy/services"
|
||||
"proxy/utils"
|
||||
|
||||
kingpin "gopkg.in/alecthomas/kingpin.v2"
|
||||
)
|
||||
|
||||
var (
|
||||
app *kingpin.Application
|
||||
service *services.ServiceItem
|
||||
)
|
||||
|
||||
func initConfig() (err error) {
|
||||
//keygen
|
||||
if len(os.Args) > 1 {
|
||||
if os.Args[1] == "keygen" {
|
||||
utils.Keygen()
|
||||
os.Exit(0)
|
||||
}
|
||||
}
|
||||
args := services.Args{}
|
||||
//define args
|
||||
tcpArgs := services.TCPArgs{}
|
||||
httpArgs := services.HTTPArgs{}
|
||||
tunnelServerArgs := services.TunnelServerArgs{}
|
||||
tunnelClientArgs := services.TunnelClientArgs{}
|
||||
tunnelBridgeArgs := services.TunnelBridgeArgs{}
|
||||
udpArgs := services.UDPArgs{}
|
||||
|
||||
//build srvice args
|
||||
app = kingpin.New("proxy", "happy with proxy")
|
||||
app.Author("snail").Version(APP_VERSION)
|
||||
args.Parent = app.Flag("parent", "parent address, such as: \"23.32.32.19:28008\"").Default("").Short('P').String()
|
||||
args.Local = app.Flag("local", "local ip:port to listen").Short('p').Default(":33080").String()
|
||||
certTLS := app.Flag("cert", "cert file for tls").Short('C').Default("proxy.crt").String()
|
||||
keyTLS := app.Flag("key", "key file for tls").Short('K').Default("proxy.key").String()
|
||||
|
||||
//########http#########
|
||||
http := app.Command("http", "proxy on http mode")
|
||||
httpArgs.LocalType = http.Flag("local-type", "parent protocol type <tls|tcp>").Default("tcp").Short('t').Enum("tls", "tcp")
|
||||
httpArgs.ParentType = http.Flag("parent-type", "parent protocol type <tls|tcp>").Short('T').Enum("tls", "tcp")
|
||||
httpArgs.Always = http.Flag("always", "always use parent proxy").Default("false").Bool()
|
||||
httpArgs.Timeout = http.Flag("timeout", "tcp timeout milliseconds when connect to real server or parent proxy").Default("2000").Int()
|
||||
httpArgs.HTTPTimeout = http.Flag("http-timeout", "check domain if blocked , http request timeout milliseconds when connect to host").Default("3000").Int()
|
||||
httpArgs.Interval = http.Flag("interval", "check domain if blocked every interval seconds").Default("10").Int()
|
||||
httpArgs.Blocked = http.Flag("blocked", "blocked domain file , one domain each line").Default("blocked").Short('b').String()
|
||||
httpArgs.Direct = http.Flag("direct", "direct domain file , one domain each line").Default("direct").Short('d').String()
|
||||
httpArgs.AuthFile = http.Flag("auth-file", "http basic auth file,\"username:password\" each line in file").Short('F').String()
|
||||
httpArgs.Auth = http.Flag("auth", "http basic auth username and password, mutiple user repeat -a ,such as: -a user1:pass1 -a user2:pass2").Short('a').Strings()
|
||||
httpArgs.PoolSize = http.Flag("pool-size", "conn pool size , which connect to parent proxy, zero: means turn off pool").Short('L').Default("20").Int()
|
||||
httpArgs.CheckParentInterval = http.Flag("check-parent-interval", "check if proxy is okay every interval seconds,zero: means no check").Short('I').Default("3").Int()
|
||||
|
||||
//########tcp#########
|
||||
tcp := app.Command("tcp", "proxy on tcp mode")
|
||||
tcpArgs.Timeout = tcp.Flag("timeout", "tcp timeout milliseconds when connect to real server or parent proxy").Short('t').Default("2000").Int()
|
||||
tcpArgs.ParentType = tcp.Flag("parent-type", "parent protocol type <tls|tcp|udp>").Short('T').Enum("tls", "tcp", "udp")
|
||||
tcpArgs.IsTLS = tcp.Flag("tls", "proxy on tls mode").Default("false").Bool()
|
||||
tcpArgs.PoolSize = tcp.Flag("pool-size", "conn pool size , which connect to parent proxy, zero: means turn off pool").Short('L').Default("20").Int()
|
||||
tcpArgs.CheckParentInterval = tcp.Flag("check-parent-interval", "check if proxy is okay every interval seconds,zero: means no check").Short('I').Default("3").Int()
|
||||
|
||||
//########udp#########
|
||||
udp := app.Command("udp", "proxy on udp mode")
|
||||
udpArgs.Timeout = udp.Flag("timeout", "tcp timeout milliseconds when connect to parent proxy").Short('t').Default("2000").Int()
|
||||
udpArgs.ParentType = udp.Flag("parent-type", "parent protocol type <tls|tcp|udp>").Short('T').Enum("tls", "tcp", "udp")
|
||||
udpArgs.PoolSize = udp.Flag("pool-size", "conn pool size , which connect to parent proxy, zero: means turn off pool").Short('L').Default("20").Int()
|
||||
udpArgs.CheckParentInterval = udp.Flag("check-parent-interval", "check if proxy is okay every interval seconds,zero: means no check").Short('I').Default("3").Int()
|
||||
|
||||
//########tunnel-server#########
|
||||
tunnelServer := app.Command("tserver", "proxy on tunnel server mode")
|
||||
tunnelServerArgs.Timeout = tunnelServer.Flag("timeout", "tcp timeout with milliseconds").Short('t').Default("2000").Int()
|
||||
tunnelServerArgs.IsUDP = tunnelServer.Flag("udp", "proxy on udp tunnel server mode").Default("false").Bool()
|
||||
tunnelServerArgs.Key = tunnelServer.Flag("k", "key same with client").Default("default").String()
|
||||
|
||||
//########tunnel-client#########
|
||||
tunnelClient := app.Command("tclient", "proxy on tunnel client mode")
|
||||
tunnelClientArgs.Timeout = tunnelClient.Flag("timeout", "tcp timeout with milliseconds").Short('t').Default("2000").Int()
|
||||
tunnelClientArgs.IsUDP = tunnelClient.Flag("udp", "proxy on udp tunnel client mode").Default("false").Bool()
|
||||
tunnelClientArgs.Key = tunnelClient.Flag("k", "key same with server").Default("default").String()
|
||||
|
||||
//########tunnel-bridge#########
|
||||
tunnelBridge := app.Command("tbridge", "proxy on tunnel bridge mode")
|
||||
tunnelBridgeArgs.Timeout = tunnelBridge.Flag("timeout", "tcp timeout with milliseconds").Short('t').Default("2000").Int()
|
||||
|
||||
kingpin.MustParse(app.Parse(os.Args[1:]))
|
||||
|
||||
if *certTLS != "" && *keyTLS != "" {
|
||||
args.CertBytes, args.KeyBytes = tlsBytes(*certTLS, *keyTLS)
|
||||
}
|
||||
|
||||
//common args
|
||||
httpArgs.Args = args
|
||||
tcpArgs.Args = args
|
||||
udpArgs.Args = args
|
||||
tunnelBridgeArgs.Args = args
|
||||
tunnelClientArgs.Args = args
|
||||
tunnelServerArgs.Args = args
|
||||
|
||||
poster()
|
||||
//regist services and run service
|
||||
serviceName := kingpin.MustParse(app.Parse(os.Args[1:]))
|
||||
services.Regist("http", services.NewHTTP(), httpArgs)
|
||||
services.Regist("tcp", services.NewTCP(), tcpArgs)
|
||||
services.Regist("udp", services.NewUDP(), udpArgs)
|
||||
services.Regist("tserver", services.NewTunnelServer(), tunnelServerArgs)
|
||||
services.Regist("tclient", services.NewTunnelClient(), tunnelClientArgs)
|
||||
services.Regist("tbridge", services.NewTunnelBridge(), tunnelBridgeArgs)
|
||||
service, err = services.Run(serviceName)
|
||||
if err != nil {
|
||||
log.Fatalf("run service [%s] fail, ERR:%s", service, err)
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func poster() {
|
||||
fmt.Printf(`
|
||||
######## ######## ####### ## ## ## ##
|
||||
## ## ## ## ## ## ## ## ## ##
|
||||
## ## ## ## ## ## ## ## ####
|
||||
######## ######## ## ## ### ##
|
||||
## ## ## ## ## ## ## ##
|
||||
## ## ## ## ## ## ## ##
|
||||
## ## ## ####### ## ## ##
|
||||
|
||||
v%s`+" by snail , blog : http://www.host900.com/\n\n", APP_VERSION)
|
||||
}
|
||||
func tlsBytes(cert, key string) (certBytes, keyBytes []byte) {
|
||||
certBytes, err := ioutil.ReadFile(cert)
|
||||
if err != nil {
|
||||
log.Fatalf("err : %s", err)
|
||||
return
|
||||
}
|
||||
keyBytes, err = ioutil.ReadFile(key)
|
||||
if err != nil {
|
||||
log.Fatalf("err : %s", err)
|
||||
return
|
||||
}
|
||||
return
|
||||
}
|
||||
@@ -0,0 +1,456 @@
|
||||
07073.com
|
||||
10010.com
|
||||
100ye.com
|
||||
114la.com
|
||||
115.com
|
||||
120ask.com
|
||||
126.com
|
||||
126.net
|
||||
1616.net
|
||||
163.com
|
||||
17173.com
|
||||
1778.com
|
||||
178.com
|
||||
17u.com
|
||||
19lou.com
|
||||
1o26.com
|
||||
1ting.com
|
||||
21cn.com
|
||||
2345.com
|
||||
265.com
|
||||
265g.com
|
||||
28.com
|
||||
28tui.com
|
||||
2hua.com
|
||||
2mdn.net
|
||||
315che.com
|
||||
3366.com
|
||||
360buy.com
|
||||
360buyimg.com
|
||||
360doc.com
|
||||
36kr.com
|
||||
39.net
|
||||
3dmgame.com
|
||||
4399.com
|
||||
4738.com
|
||||
500wan.com
|
||||
51.com
|
||||
51.la
|
||||
5173.com
|
||||
51auto.com
|
||||
51buy.com
|
||||
51cto.com
|
||||
51fanli.com
|
||||
51job.com
|
||||
52kmh.com
|
||||
52pk.net
|
||||
52tlbb.com
|
||||
53kf.com
|
||||
55bbs.com
|
||||
55tuan.com
|
||||
56.com
|
||||
58.com
|
||||
591hx.com
|
||||
5d6d.net
|
||||
61.com
|
||||
70e.com
|
||||
777wyx.com
|
||||
778669.com
|
||||
7c.com
|
||||
7k7k.com
|
||||
88db.com
|
||||
91.com
|
||||
99bill.com
|
||||
a135.net
|
||||
abang.com
|
||||
abchina.com
|
||||
ad1111.com
|
||||
admin5.com
|
||||
adnxs.com
|
||||
adobe.com
|
||||
adroll.com
|
||||
ads8.com
|
||||
adsame.com
|
||||
adsonar.com
|
||||
adtechus.com
|
||||
aibang.com
|
||||
aifang.com
|
||||
aili.com
|
||||
aipai.com
|
||||
aizhan.com
|
||||
ali213.net
|
||||
alibaba.com
|
||||
alicdn.com
|
||||
aliexpress.com
|
||||
alimama.com
|
||||
alipay.com
|
||||
alipayobjects.com
|
||||
alisoft.com
|
||||
alivv.com
|
||||
aliyun.com
|
||||
allyes.com
|
||||
amazon.com
|
||||
anjuke.com
|
||||
anzhi.com
|
||||
aol.com
|
||||
apple.com
|
||||
arpg2.com
|
||||
atdmt.com
|
||||
b2b168.com
|
||||
babytree.com
|
||||
baidu.com
|
||||
baihe.com
|
||||
baixing.com
|
||||
bankcomm.com
|
||||
baomihua.com
|
||||
bdimg.com
|
||||
bdstatic.com
|
||||
bendibao.com
|
||||
betrad.com
|
||||
bilibili.tv
|
||||
bing.com
|
||||
bitauto.com
|
||||
blog.163.com
|
||||
blogchina.com
|
||||
blueidea.com
|
||||
bluekai.com
|
||||
booksky.org
|
||||
caixin.com
|
||||
ccb.com
|
||||
ccidnet.com
|
||||
cctv*.com
|
||||
china.com
|
||||
chinabyte.com
|
||||
chinahr.com
|
||||
chinanews.com
|
||||
chinaw3.com
|
||||
chinaz.com
|
||||
chuangelm.com
|
||||
ci123.com
|
||||
cmbchina.com
|
||||
cnbeta.com
|
||||
cnblogs.com
|
||||
cncn.com
|
||||
cnhubei.com
|
||||
cnki.net
|
||||
cnmo.com
|
||||
cnxad.com
|
||||
cnzz.com
|
||||
cocoren.com
|
||||
compete.com
|
||||
comsenz.com
|
||||
coo8.com
|
||||
cqnews.net
|
||||
crsky.com
|
||||
csdn.net
|
||||
ct10000.com
|
||||
ctrip.com
|
||||
dangdang.com
|
||||
daqi.com
|
||||
dayoo.com
|
||||
dbank.com
|
||||
ddmap.com
|
||||
dedecms.com
|
||||
dh818.com
|
||||
diandian.com
|
||||
dianping.com
|
||||
discuz.net
|
||||
doc88.com
|
||||
docin.com
|
||||
donews.com
|
||||
dospy.com
|
||||
douban.com
|
||||
douban.fm
|
||||
doubleclick.com
|
||||
doubleclick.net
|
||||
duba.net
|
||||
duote.com
|
||||
duowan.com
|
||||
dzwww.com
|
||||
eastday.com
|
||||
eastmoney.com
|
||||
ebay.com
|
||||
elong.com
|
||||
ename.net
|
||||
etao.com
|
||||
exam8.com
|
||||
eye.rs
|
||||
fantong.com
|
||||
fastcdn.com
|
||||
fblife.com
|
||||
fengniao.com
|
||||
fenzhi.com
|
||||
flickr.com
|
||||
fobshanghai.com
|
||||
ftuan.com
|
||||
funshion.com
|
||||
fx120.net
|
||||
game3737.com
|
||||
gamersky.com
|
||||
gamestlbb.com
|
||||
gamesville.com
|
||||
ganji.com
|
||||
gfan.com
|
||||
gongchang.com
|
||||
google-analytics.com
|
||||
gougou.com
|
||||
gtimg.com
|
||||
hao123.com
|
||||
haodf.com
|
||||
harrenmedianetwork.com
|
||||
hc360.com
|
||||
hefei.cc
|
||||
hf365.com
|
||||
hiapk.com
|
||||
hichina.com
|
||||
homeinns.com
|
||||
hotsales.net
|
||||
house365.com
|
||||
huaban.com
|
||||
huanqiu.com
|
||||
hudong.com
|
||||
hupu.com
|
||||
iask.com
|
||||
iciba.com
|
||||
icson.com
|
||||
ifeng.com
|
||||
iloveyouxi.com
|
||||
im286.com
|
||||
imanhua.com
|
||||
img.cctvpic.com
|
||||
imrworldwide.com
|
||||
invitemedia.com
|
||||
ip138.com
|
||||
ipinyou.com
|
||||
iqilu.com
|
||||
iqiyi.com
|
||||
irs01.com
|
||||
irs01.net
|
||||
it168.com
|
||||
iteye.com
|
||||
iyaya.com
|
||||
jb51.net
|
||||
jiathis.com
|
||||
jiayuan.com
|
||||
jing.fm
|
||||
jinti.com
|
||||
jqw.com
|
||||
jumei.com
|
||||
jxedt.com
|
||||
jysq.net
|
||||
kaixin001.com
|
||||
kandian.com
|
||||
kdnet.net
|
||||
kimiss.com
|
||||
ku6.com
|
||||
ku6cdn.com
|
||||
ku6img.com
|
||||
kuaidi100.com
|
||||
kugou.com
|
||||
l99.com
|
||||
lady8844.com
|
||||
lafaso.com
|
||||
lashou.com
|
||||
legolas-media.com
|
||||
lehecai.com
|
||||
leho.com
|
||||
letv.com
|
||||
liebiao.com
|
||||
lietou.com
|
||||
linezing.com
|
||||
linkedin.com
|
||||
live.com
|
||||
longhoo.net
|
||||
lusongsong.com
|
||||
lxdns.com
|
||||
lycos.com
|
||||
lygo.com
|
||||
m18.com
|
||||
m1905.com
|
||||
made-in-china.com
|
||||
makepolo.com
|
||||
mangocity.com
|
||||
manzuo.com
|
||||
mapbar.com
|
||||
mathtag.com
|
||||
mediaplex.com
|
||||
mediav.com
|
||||
meilele.com
|
||||
meilishuo.com
|
||||
meishichina.com
|
||||
meituan.com
|
||||
meizu.com
|
||||
miaozhen.com
|
||||
microsoft.com
|
||||
miercn.com
|
||||
mlt01.com
|
||||
mmcdn.cn
|
||||
mmstat.com
|
||||
mnwan.com
|
||||
mogujie.com
|
||||
mookie1.com
|
||||
moonbasa.com
|
||||
mop.com
|
||||
mosso.com
|
||||
mplife.com
|
||||
msn.com
|
||||
mtime.com
|
||||
mumayi.com
|
||||
mydrivers.com
|
||||
net114.com
|
||||
netease.com
|
||||
newsmth.net
|
||||
nipic.com
|
||||
nowec.com
|
||||
nuomi.com
|
||||
oadz.com
|
||||
oeeee.com
|
||||
onetad.com
|
||||
onlinedown.net
|
||||
onlylady.com
|
||||
oschina.net
|
||||
otwan.com
|
||||
paipai.com
|
||||
paypal.com
|
||||
pchome.net
|
||||
pcpop.com
|
||||
pengyou.com
|
||||
php100.com
|
||||
phpwind.net
|
||||
pingan.com
|
||||
pixlr.com
|
||||
pp.cc
|
||||
ppstream.com
|
||||
pptv.com
|
||||
ptlogin2.qq.com
|
||||
pubmatic.com
|
||||
q150.com
|
||||
qianlong.com
|
||||
qidian.com
|
||||
qingdaonews.com
|
||||
qire123.com
|
||||
qiushibaike.com
|
||||
qiyou.com
|
||||
qjy168.com
|
||||
qq.com
|
||||
qq937.com
|
||||
qstatic.com
|
||||
quantserve.com
|
||||
qunar.com
|
||||
rakuten.co.jp
|
||||
readnovel.com
|
||||
renren.com
|
||||
rtbidder.net
|
||||
scanscout.com
|
||||
scorecardresearch.com
|
||||
sdo.com
|
||||
seowhy.com
|
||||
serving-sys.com
|
||||
sf-express.com
|
||||
shangdu.com
|
||||
si.kz
|
||||
sina.com
|
||||
sinahk.net
|
||||
sinajs.com
|
||||
smzdm.com
|
||||
snyu.com
|
||||
sodu.org
|
||||
sogou.com
|
||||
sohu.com
|
||||
soku.com
|
||||
sootoo.com
|
||||
soso.com
|
||||
soufun.com
|
||||
sourceforge.net
|
||||
staticsdo.com
|
||||
stockstar.com
|
||||
sttlbb.com
|
||||
suning.com
|
||||
szhome.com
|
||||
sznews.com
|
||||
tangdou.com
|
||||
tanx.com
|
||||
tao123.com
|
||||
taobao.com
|
||||
taobaocdn.com
|
||||
tbcdn.cn
|
||||
tdimg.com
|
||||
tenpay.com
|
||||
tgbus.com
|
||||
theplanet.com
|
||||
thethirdmedia.com
|
||||
tiancity.com
|
||||
tianji.com
|
||||
tiao8.info
|
||||
tiexue.net
|
||||
titan24.com
|
||||
tmall.com
|
||||
tom.com
|
||||
toocle.com
|
||||
tremormedia.com
|
||||
tuan800.com
|
||||
tudou.com
|
||||
tudouui.com
|
||||
tui18.com
|
||||
tuniu.com
|
||||
twcczhu.com
|
||||
u17.com
|
||||
ucjoy.com
|
||||
ulink.cc
|
||||
uniontoufang.com
|
||||
up2c.com
|
||||
uuu9.com
|
||||
uuzu.com
|
||||
vancl.com
|
||||
verycd.com
|
||||
vipshop.com
|
||||
vizu.com
|
||||
vjia.com
|
||||
weibo.com
|
||||
weiphone.com
|
||||
west263.com
|
||||
whlongda.com
|
||||
wrating.com
|
||||
wumii.com
|
||||
xiami.com
|
||||
xiaomi.com
|
||||
xiazaiba.com
|
||||
xici.net
|
||||
xinhuanet.com
|
||||
xinnet.com
|
||||
xitek.com
|
||||
xiu.com
|
||||
xunlei.com
|
||||
xyxy.net
|
||||
yahoo.co.jp
|
||||
yahoo.com
|
||||
yaolan.com
|
||||
yesky.com
|
||||
yieldmanager.com
|
||||
yihaodian.com
|
||||
yingjiesheng.com
|
||||
yinyuetai.com
|
||||
yiqifa.com
|
||||
ykimg.com
|
||||
ynet.com
|
||||
yoka.com
|
||||
yolk7.com
|
||||
youboy.com
|
||||
youdao.com
|
||||
yougou.com
|
||||
youku.com
|
||||
youshang.com
|
||||
yupoo.com
|
||||
yxlady.com
|
||||
yyets.com
|
||||
zhaodao123.com
|
||||
zhaopin.com
|
||||
zhenai.com
|
||||
zhibo8.cc
|
||||
zhihu.com
|
||||
zhubajie.com
|
||||
zongheng.com
|
||||
zoosnet.net
|
||||
zqgame.com
|
||||
ztgame.com
|
||||
zx915.com
|
||||

|
After Width: | Height: | Size: 94 KiB |

|
After Width: | Height: | Size: 26 KiB |

|
After Width: | Height: | Size: 32 KiB |

|
After Width: | Height: | Size: 12 KiB |

|
After Width: | Height: | Size: 39 KiB |

|
After Width: | Height: | Size: 34 KiB |

|
After Width: | Height: | Size: 18 KiB |

|
After Width: | Height: | Size: 22 KiB |

|
After Width: | Height: | Size: 25 KiB |

|
After Width: | Height: | Size: 29 KiB |

|
After Width: | Height: | Size: 25 KiB |

|
After Width: | Height: | Size: 30 KiB |

|
After Width: | Height: | Size: 119 KiB |

|
After Width: | Height: | Size: 18 KiB |

|
After Width: | Height: | Size: 24 KiB |

|
After Width: | Height: | Size: 19 KiB |

|
After Width: | Height: | Size: 25 KiB |

|
After Width: | Height: | Size: 24 KiB |

|
After Width: | Height: | Size: 14 KiB |

|
After Width: | Height: | Size: 17 KiB |

|
After Width: | Height: | Size: 22 KiB |

|
After Width: | Height: | Size: 19 KiB |

|
After Width: | Height: | Size: 25 KiB |

|
After Width: | Height: | Size: 3.5 KiB |

|
After Width: | Height: | Size: 13 KiB |

|
After Width: | Height: | Size: 20 KiB |

|
After Width: | Height: | Size: 23 KiB |

|
After Width: | Height: | Size: 22 KiB |

|
After Width: | Height: | Size: 26 KiB |

|
After Width: | Height: | Size: 24 KiB |

|
After Width: | Height: | Size: 33 KiB |

|
After Width: | Height: | Size: 26 KiB |
@@ -0,0 +1,7 @@
|
||||
# alpine, busybox, scratch
|
||||
FROM scratch
|
||||
COPY proxy /
|
||||
COPY Shanghai /etc/localtime/
|
||||
COPY ca-certificates.crt /etc/ssl/certs/
|
||||
ENTRYPOINT ["/proxy"]
|
||||
CMD ["--version"]
|
||||
@@ -0,0 +1,21 @@
|
||||
#!/bin/bash
|
||||
set -e
|
||||
ver=$1
|
||||
if [ -z "$ver" ]; then
|
||||
echo -e "example:\n./build.sh 10.0"
|
||||
exit
|
||||
fi
|
||||
CLEAN="goproxy proxy"
|
||||
rm -rf $CLEAN
|
||||
mkdir goproxy
|
||||
|
||||
cd goproxy
|
||||
wget https://mirrors.host900.com/snail007/goproxy/proxy-linux-amd64.tar.gz
|
||||
tar zxf proxy-linux-amd64.tar.gz
|
||||
mv proxy ../
|
||||
cd ..
|
||||
|
||||
docker build --no-cache -t snail007/goproxy:v$ver .
|
||||
docker tag snail007/goproxy:v$ver snail007/goproxy:latest
|
||||
docker images
|
||||
rm -rf $CLEAN
|
||||
@@ -0,0 +1,3260 @@
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIH0zCCBbugAwIBAgIIXsO3pkN/pOAwDQYJKoZIhvcNAQEFBQAwQjESMBAGA1UE
|
||||
AwwJQUNDVlJBSVoxMRAwDgYDVQQLDAdQS0lBQ0NWMQ0wCwYDVQQKDARBQ0NWMQsw
|
||||
CQYDVQQGEwJFUzAeFw0xMTA1MDUwOTM3MzdaFw0zMDEyMzEwOTM3MzdaMEIxEjAQ
|
||||
BgNVBAMMCUFDQ1ZSQUlaMTEQMA4GA1UECwwHUEtJQUNDVjENMAsGA1UECgwEQUND
|
||||
VjELMAkGA1UEBhMCRVMwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQCb
|
||||
qau/YUqXry+XZpp0X9DZlv3P4uRm7x8fRzPCRKPfmt4ftVTdFXxpNRFvu8gMjmoY
|
||||
HtiP2Ra8EEg2XPBjs5BaXCQ316PWywlxufEBcoSwfdtNgM3802/J+Nq2DoLSRYWo
|
||||
G2ioPej0RGy9ocLLA76MPhMAhN9KSMDjIgro6TenGEyxCQ0jVn8ETdkXhBilyNpA
|
||||
lHPrzg5XPAOBOp0KoVdDaaxXbXmQeOW1tDvYvEyNKKGno6e6Ak4l0Squ7a4DIrhr
|
||||
IA8wKFSVf+DuzgpmndFALW4ir50awQUZ0m/A8p/4e7MCQvtQqR0tkw8jq8bBD5L/
|
||||
0KIV9VMJcRz/RROE5iZe+OCIHAr8Fraocwa48GOEAqDGWuzndN9wrqODJerWx5eH
|
||||
k6fGioozl2A3ED6XPm4pFdahD9GILBKfb6qkxkLrQaLjlUPTAYVtjrs78yM2x/47
|
||||
4KElB0iryYl0/wiPgL/AlmXz7uxLaL2diMMxs0Dx6M/2OLuc5NF/1OVYm3z61PMO
|
||||
m3WR5LpSLhl+0fXNWhn8ugb2+1KoS5kE3fj5tItQo05iifCHJPqDQsGH+tUtKSpa
|
||||
cXpkatcnYGMN285J9Y0fkIkyF/hzQ7jSWpOGYdbhdQrqeWZ2iE9x6wQl1gpaepPl
|
||||
uUsXQA+xtrn13k/c4LOsOxFwYIRKQ26ZIMApcQrAZQIDAQABo4ICyzCCAscwfQYI
|
||||
KwYBBQUHAQEEcTBvMEwGCCsGAQUFBzAChkBodHRwOi8vd3d3LmFjY3YuZXMvZmls
|
||||
ZWFkbWluL0FyY2hpdm9zL2NlcnRpZmljYWRvcy9yYWl6YWNjdjEuY3J0MB8GCCsG
|
||||
AQUFBzABhhNodHRwOi8vb2NzcC5hY2N2LmVzMB0GA1UdDgQWBBTSh7Tj3zcnk1X2
|
||||
VuqB5TbMjB4/vTAPBgNVHRMBAf8EBTADAQH/MB8GA1UdIwQYMBaAFNKHtOPfNyeT
|
||||
VfZW6oHlNsyMHj+9MIIBcwYDVR0gBIIBajCCAWYwggFiBgRVHSAAMIIBWDCCASIG
|
||||
CCsGAQUFBwICMIIBFB6CARAAQQB1AHQAbwByAGkAZABhAGQAIABkAGUAIABDAGUA
|
||||
cgB0AGkAZgBpAGMAYQBjAGkA8wBuACAAUgBhAO0AegAgAGQAZQAgAGwAYQAgAEEA
|
||||
QwBDAFYAIAAoAEEAZwBlAG4AYwBpAGEAIABkAGUAIABUAGUAYwBuAG8AbABvAGcA
|
||||
7QBhACAAeQAgAEMAZQByAHQAaQBmAGkAYwBhAGMAaQDzAG4AIABFAGwAZQBjAHQA
|
||||
cgDzAG4AaQBjAGEALAAgAEMASQBGACAAUQA0ADYAMAAxADEANQA2AEUAKQAuACAA
|
||||
QwBQAFMAIABlAG4AIABoAHQAdABwADoALwAvAHcAdwB3AC4AYQBjAGMAdgAuAGUA
|
||||
czAwBggrBgEFBQcCARYkaHR0cDovL3d3dy5hY2N2LmVzL2xlZ2lzbGFjaW9uX2Mu
|
||||
aHRtMFUGA1UdHwROMEwwSqBIoEaGRGh0dHA6Ly93d3cuYWNjdi5lcy9maWxlYWRt
|
||||
aW4vQXJjaGl2b3MvY2VydGlmaWNhZG9zL3JhaXphY2N2MV9kZXIuY3JsMA4GA1Ud
|
||||
DwEB/wQEAwIBBjAXBgNVHREEEDAOgQxhY2N2QGFjY3YuZXMwDQYJKoZIhvcNAQEF
|
||||
BQADggIBAJcxAp/n/UNnSEQU5CmH7UwoZtCPNdpNYbdKl02125DgBS4OxnnQ8pdp
|
||||
D70ER9m+27Up2pvZrqmZ1dM8MJP1jaGo/AaNRPTKFpV8M9xii6g3+CfYCS0b78gU
|
||||
JyCpZET/LtZ1qmxNYEAZSUNUY9rizLpm5U9EelvZaoErQNV/+QEnWCzI7UiRfD+m
|
||||
AM/EKXMRNt6GGT6d7hmKG9Ww7Y49nCrADdg9ZuM8Db3VlFzi4qc1GwQA9j9ajepD
|
||||
vV+JHanBsMyZ4k0ACtrJJ1vnE5Bc5PUzolVt3OAJTS+xJlsndQAJxGJ3KQhfnlms
|
||||
tn6tn1QwIgPBHnFk/vk4CpYY3QIUrCPLBhwepH2NDd4nQeit2hW3sCPdK6jT2iWH
|
||||
7ehVRE2I9DZ+hJp4rPcOVkkO1jMl1oRQQmwgEh0q1b688nCBpHBgvgW1m54ERL5h
|
||||
I6zppSSMEYCUWqKiuUnSwdzRp+0xESyeGabu4VXhwOrPDYTkF7eifKXeVSUG7szA
|
||||
h1xA2syVP1XgNce4hL60Xc16gwFy7ofmXx2utYXGJt/mwZrpHgJHnyqobalbz+xF
|
||||
d3+YJ5oyXSrjhO7FmGYvliAd3djDJ9ew+f7Zfc3Qn48LFFhRny+Lwzgt3uiP1o2H
|
||||
pPVWQxaZLPSkVrQ0uGE3ycJYgBugl6H8WY3pEfbRD0tVNEYqi4Y7
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFgzCCA2ugAwIBAgIPXZONMGc2yAYdGsdUhGkHMA0GCSqGSIb3DQEBCwUAMDsx
|
||||
CzAJBgNVBAYTAkVTMREwDwYDVQQKDAhGTk1ULVJDTTEZMBcGA1UECwwQQUMgUkFJ
|
||||
WiBGTk1ULVJDTTAeFw0wODEwMjkxNTU5NTZaFw0zMDAxMDEwMDAwMDBaMDsxCzAJ
|
||||
BgNVBAYTAkVTMREwDwYDVQQKDAhGTk1ULVJDTTEZMBcGA1UECwwQQUMgUkFJWiBG
|
||||
Tk1ULVJDTTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBALpxgHpMhm5/
|
||||
yBNtwMZ9HACXjywMI7sQmkCpGreHiPibVmr75nuOi5KOpyVdWRHbNi63URcfqQgf
|
||||
BBckWKo3Shjf5TnUV/3XwSyRAZHiItQDwFj8d0fsjz50Q7qsNI1NOHZnjrDIbzAz
|
||||
WHFctPVrbtQBULgTfmxKo0nRIBnuvMApGGWn3v7v3QqQIecaZ5JCEJhfTzC8PhxF
|
||||
tBDXaEAUwED653cXeuYLj2VbPNmaUtu1vZ5Gzz3rkQUCwJaydkxNEJY7kvqcfw+Z
|
||||
374jNUUeAlz+taibmSXaXvMiwzn15Cou08YfxGyqxRxqAQVKL9LFwag0Jl1mpdIC
|
||||
IfkYtwb1TplvqKtMUejPUBjFd8g5CSxJkjKZqLsXF3mwWsXmo8RZZUc1g16p6DUL
|
||||
mbvkzSDGm0oGObVo/CK67lWMK07q87Hj/LaZmtVC+nFNCM+HHmpxffnTtOmlcYF7
|
||||
wk5HlqX2doWjKI/pgG6BU6VtX7hI+cL5NqYuSf+4lsKMB7ObiFj86xsc3i1w4peS
|
||||
MKGJ47xVqCfWS+2QrYv6YyVZLag13cqXM7zlzced0ezvXg5KkAYmY6252TUtB7p2
|
||||
ZSysV4999AeU14ECll2jB0nVetBX+RvnU0Z1qrB5QstocQjpYL05ac70r8NWQMet
|
||||
UqIJ5G+GR4of6ygnXYMgrwTJbFaai0b1AgMBAAGjgYMwgYAwDwYDVR0TAQH/BAUw
|
||||
AwEB/zAOBgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFPd9xf3E6Jobd2Sn9R2gzL+H
|
||||
YJptMD4GA1UdIAQ3MDUwMwYEVR0gADArMCkGCCsGAQUFBwIBFh1odHRwOi8vd3d3
|
||||
LmNlcnQuZm5tdC5lcy9kcGNzLzANBgkqhkiG9w0BAQsFAAOCAgEAB5BK3/MjTvDD
|
||||
nFFlm5wioooMhfNzKWtN/gHiqQxjAb8EZ6WdmF/9ARP67Jpi6Yb+tmLSbkyU+8B1
|
||||
RXxlDPiyN8+sD8+Nb/kZ94/sHvJwnvDKuO+3/3Y3dlv2bojzr2IyIpMNOmqOFGYM
|
||||
LVN0V2Ue1bLdI4E7pWYjJ2cJj+F3qkPNZVEI7VFY/uY5+ctHhKQV8Xa7pO6kO8Rf
|
||||
77IzlhEYt8llvhjho6Tc+hj507wTmzl6NLrTQfv6MooqtyuGC2mDOL7Nii4LcK2N
|
||||
JpLuHvUBKwrZ1pebbuCoGRw6IYsMHkCtA+fdZn71uSANA+iW+YJF1DngoABd15jm
|
||||
fZ5nc8OaKveri6E6FO80vFIOiZiaBECEHX5FaZNXzuvO+FB8TxxuBEOb+dY7Ixjp
|
||||
6o7RTUaN8Tvkasq6+yO3m/qZASlaWFot4/nUbQ4mrcFuNLwy+AwF+mWj2zs3gyLp
|
||||
1txyM/1d8iC9djwj2ij3+RvrWWTV3F9yfiD8zYm1kGdNYno/Tq0dwzn+evQoFt9B
|
||||
9kiABdcPUXmsEKvU7ANm5mqwujGSQkBqvjrTcuFqN1W8rB2Vt2lh8kORdOag0wok
|
||||
RqEIr9baRRmW1FMdW4R58MD3R++Lj8UGrp1MYp3/RgT408m2ECVAdf4WqslKYIYv
|
||||
uu8wd+RU4riEmViAqhOLUTpPSPaLtrM=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFuzCCA6OgAwIBAgIIVwoRl0LE48wwDQYJKoZIhvcNAQELBQAwazELMAkGA1UE
|
||||
BhMCSVQxDjAMBgNVBAcMBU1pbGFuMSMwIQYDVQQKDBpBY3RhbGlzIFMucC5BLi8w
|
||||
MzM1ODUyMDk2NzEnMCUGA1UEAwweQWN0YWxpcyBBdXRoZW50aWNhdGlvbiBSb290
|
||||
IENBMB4XDTExMDkyMjExMjIwMloXDTMwMDkyMjExMjIwMlowazELMAkGA1UEBhMC
|
||||
SVQxDjAMBgNVBAcMBU1pbGFuMSMwIQYDVQQKDBpBY3RhbGlzIFMucC5BLi8wMzM1
|
||||
ODUyMDk2NzEnMCUGA1UEAwweQWN0YWxpcyBBdXRoZW50aWNhdGlvbiBSb290IENB
|
||||
MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAp8bEpSmkLO/lGMWwUKNv
|
||||
UTufClrJwkg4CsIcoBh/kbWHuUA/3R1oHwiD1S0eiKD4j1aPbZkCkpAW1V8IbInX
|
||||
4ay8IMKx4INRimlNAJZaby/ARH6jDuSRzVju3PvHHkVH3Se5CAGfpiEd9UEtL0z9
|
||||
KK3giq0itFZljoZUj5NDKd45RnijMCO6zfB9E1fAXdKDa0hMxKufgFpbOr3JpyI/
|
||||
gCczWw63igxdBzcIy2zSekciRDXFzMwujt0q7bd9Zg1fYVEiVRvjRuPjPdA1Yprb
|
||||
rxTIW6HMiRvhMCb8oJsfgadHHwTrozmSBp+Z07/T6k9QnBn+locePGX2oxgkg4YQ
|
||||
51Q+qDp2JE+BIcXjDwL4k5RHILv+1A7TaLndxHqEguNTVHnd25zS8gebLra8Pu2F
|
||||
be8lEfKXGkJh90qX6IuxEAf6ZYGyojnP9zz/GPvG8VqLWeICrHuS0E4UT1lF9gxe
|
||||
KF+w6D9Fz8+vm2/7hNN3WpVvrJSEnu68wEqPSpP4RCHiMUVhUE4Q2OM1fEwZtN4F
|
||||
v6MGn8i1zeQf1xcGDXqVdFUNaBr8EBtiZJ1t4JWgw5QHVw0U5r0F+7if5t+L4sbn
|
||||
fpb2U8WANFAoWPASUHEXMLrmeGO89LKtmyuy/uE5jF66CyCU3nuDuP/jVo23Eek7
|
||||
jPKxwV2dpAtMK9myGPW1n0sCAwEAAaNjMGEwHQYDVR0OBBYEFFLYiDrIn3hm7Ynz
|
||||
ezhwlMkCAjbQMA8GA1UdEwEB/wQFMAMBAf8wHwYDVR0jBBgwFoAUUtiIOsifeGbt
|
||||
ifN7OHCUyQICNtAwDgYDVR0PAQH/BAQDAgEGMA0GCSqGSIb3DQEBCwUAA4ICAQAL
|
||||
e3KHwGCmSUyIWOYdiPcUZEim2FgKDk8TNd81HdTtBjHIgT5q1d07GjLukD0R0i70
|
||||
jsNjLiNmsGe+b7bAEzlgqqI0JZN1Ut6nna0Oh4lScWoWPBkdg/iaKWW+9D+a2fDz
|
||||
WochcYBNy+A4mz+7+uAwTc+G02UQGRjRlwKxK3JCaKygvU5a2hi/a5iB0P2avl4V
|
||||
SM0RFbnAKVy06Ij3Pjaut2L9HmLecHgQHEhb2rykOLpn7VU+Xlff1ANATIGk0k9j
|
||||
pwlCCRT8AKnCgHNPLsBA2RF7SOp6AsDT6ygBJlh0wcBzIm2Tlf05fbsq4/aC4yyX
|
||||
X04fkZT6/iyj2HYauE2yOE+b+h1IYHkm4vP9qdCa6HCPSXrW5b0KDtst842/6+Ok
|
||||
fcvHlXHo2qN8xcL4dJIEG4aspCJTQLas/kx2z/uUMsA1n3Y/buWQbqCmJqK4LL7R
|
||||
K4X9p2jIugErsWx0Hbhzlefut8cl8ABMALJ+tguLHPPAUJ4lueAI3jZm/zel0btU
|
||||
ZCzJJ7VLkn5l/9Mt4blOvH+kQSGQQXemOR/qnuOf0GZvBeyqdn6/axag67XH/JJU
|
||||
LysRJyU3eExRarDzzFhdFPFqSBX/wge2sY0PjlxQRrM9vwGYT7JZVEc+NHt4bVaT
|
||||
LnPqZih4zR0Uv6CPLy64Lo7yFIrM6bV8+2ydDKXhlg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDTDCCAjSgAwIBAgIId3cGJyapsXwwDQYJKoZIhvcNAQELBQAwRDELMAkGA1UE
|
||||
BhMCVVMxFDASBgNVBAoMC0FmZmlybVRydXN0MR8wHQYDVQQDDBZBZmZpcm1UcnVz
|
||||
dCBDb21tZXJjaWFsMB4XDTEwMDEyOTE0MDYwNloXDTMwMTIzMTE0MDYwNlowRDEL
|
||||
MAkGA1UEBhMCVVMxFDASBgNVBAoMC0FmZmlybVRydXN0MR8wHQYDVQQDDBZBZmZp
|
||||
cm1UcnVzdCBDb21tZXJjaWFsMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKC
|
||||
AQEA9htPZwcroRX1BiLLHwGy43NFBkRJLLtJJRTWzsO3qyxPxkEylFf6EqdbDuKP
|
||||
Hx6GGaeqtS25Xw2Kwq+FNXkyLbscYjfysVtKPcrNcV/pQr6U6Mje+SJIZMblq8Yr
|
||||
ba0F8PrVC8+a5fBQpIs7R6UjW3p6+DM/uO+Zl+MgwdYoic+U+7lF7eNAFxHUdPAL
|
||||
MeIrJmqbTFeurCA+ukV6BfO9m2kVrn1OIGPENXY6BwLJN/3HR+7o8XYdcxXyl6S1
|
||||
yHp52UKqK39c/s4mT6NmgTWvRLpUHhwwMmWd5jyTXlBOeuM61G7MGvv50jeuJCqr
|
||||
VwMiKA1JdX+3KNp1v47j3A55MQIDAQABo0IwQDAdBgNVHQ4EFgQUnZPGU4teyq8/
|
||||
nx4P5ZmVvCT2lI8wDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYwDQYJ
|
||||
KoZIhvcNAQELBQADggEBAFis9AQOzcAN/wr91LoWXym9e2iZWEnStB03TX8nfUYG
|
||||
XUPGhi4+c7ImfU+TqbbEKpqrIZcUsd6M06uJFdhrJNTxFq7YpFzUf1GO7RgBsZNj
|
||||
vbz4YYCanrHOQnDiqX0GJX0nof5v7LMeJNrjS1UaADs1tDvZ110w/YETifLCBivt
|
||||
Z8SOyUOyXGsViQK8YvxO8rUzqrJv0wqiUOP2O+guRMLbZjipM1ZI8W0bM40NjD9g
|
||||
N53Tym1+NH4Nn3J2ixufcv1SNUFFApYvHLKac0khsUlHRUe072o0EclNmsxZt9YC
|
||||
nlpOZbWUrhvfKbAW8b8Angc6F2S1BLUjIZkKlTuXfO8=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDTDCCAjSgAwIBAgIIfE8EORzUmS0wDQYJKoZIhvcNAQEFBQAwRDELMAkGA1UE
|
||||
BhMCVVMxFDASBgNVBAoMC0FmZmlybVRydXN0MR8wHQYDVQQDDBZBZmZpcm1UcnVz
|
||||
dCBOZXR3b3JraW5nMB4XDTEwMDEyOTE0MDgyNFoXDTMwMTIzMTE0MDgyNFowRDEL
|
||||
MAkGA1UEBhMCVVMxFDASBgNVBAoMC0FmZmlybVRydXN0MR8wHQYDVQQDDBZBZmZp
|
||||
cm1UcnVzdCBOZXR3b3JraW5nMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKC
|
||||
AQEAtITMMxcua5Rsa2FSoOujz3mUTOWUgJnLVWREZY9nZOIG41w3SfYvm4SEHi3y
|
||||
YJ0wTsyEheIszx6e/jarM3c1RNg1lho9Nuh6DtjVR6FqaYvZ/Ls6rnla1fTWcbua
|
||||
kCNrmreIdIcMHl+5ni36q1Mr3Lt2PpNMCAiMHqIjHNRqrSK6mQEubWXLviRmVSRL
|
||||
QESxG9fhwoXA3hA/Pe24/PHxI1Pcv2WXb9n5QHGNfb2V1M6+oF4nI979ptAmDgAp
|
||||
6zxG8D1gvz9Q0twmQVGeFDdCBKNwV6gbh+0t+nvujArjqWaJGctB+d1ENmHP4ndG
|
||||
yH329JKBNv3bNPFyfvMMFr20FQIDAQABo0IwQDAdBgNVHQ4EFgQUBx/S55zawm6i
|
||||
QLSwelAQUHTEyL0wDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYwDQYJ
|
||||
KoZIhvcNAQEFBQADggEBAIlXshZ6qML91tmbmzTCnLQyFE2npN/svqe++EPbkTfO
|
||||
tDIuUFUaNU52Q3Eg75N3ThVwLofDwR1t3Mu1J9QsVtFSUzpE0nPIxBsFZVpikpzu
|
||||
QY0x2+c06lkh1QF612S4ZDnNye2v7UsDSKegmQGA3GWjNq5lWUhPgkvIZfFXHeVZ
|
||||
Lgo/bNjR9eUJtGxUAArgFU2HdW23WJZa3W3SAKD0m0i+wzekujbgfIeFlxoVot4u
|
||||
olu9rxj5kFDNcFn4J2dHy8egBzp90SxdbBk6ZrV9/ZFvgrG+CJPbFEfxojfHRZ48
|
||||
x3evZKiT3/Zpg4Jg8klCNO1aAFSFHBY2kgxc+qatv9s=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFRjCCAy6gAwIBAgIIbYwURrGmCu4wDQYJKoZIhvcNAQEMBQAwQTELMAkGA1UE
|
||||
BhMCVVMxFDASBgNVBAoMC0FmZmlybVRydXN0MRwwGgYDVQQDDBNBZmZpcm1UcnVz
|
||||
dCBQcmVtaXVtMB4XDTEwMDEyOTE0MTAzNloXDTQwMTIzMTE0MTAzNlowQTELMAkG
|
||||
A1UEBhMCVVMxFDASBgNVBAoMC0FmZmlybVRydXN0MRwwGgYDVQQDDBNBZmZpcm1U
|
||||
cnVzdCBQcmVtaXVtMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAxBLf
|
||||
qV/+Qd3d9Z+K4/as4Tx4mrzY8H96oDMq3I0gW64tb+eT2TZwamjPjlGjhVtnBKAQ
|
||||
JG9dKILBl1fYSCkTtuG+kU3fhQxTGJoeJKJPj/CihQvL9Cl/0qRY7iZNyaqoe5rZ
|
||||
+jjeRFcV5fiMyNlI4g0WJx0eyIOFJbe6qlVBzAMiSy2RjYvmia9mx+n/K+k8rNrS
|
||||
s8PhaJyJ+HoAVt70VZVs+7pk3WKL3wt3MutizCaam7uqYoNMtAZ6MMgpv+0GTZe5
|
||||
HMQxK9VfvFMSF5yZVylmd2EhMQcuJUmdGPLu8ytxjLW6OQdJd/zvLpKQBY0tL3d7
|
||||
70O/Nbua2Plzpyzy0FfuKE4mX4+QaAkvuPjcBukumj5Rp9EixAqnOEhss/n/fauG
|
||||
V+O61oV4d7pD6kh/9ti+I20ev9E2bFhc8e6kGVQa9QPSdubhjL08s9NIS+LI+H+S
|
||||
qHZGnEJlPqQewQcDWkYtuJfzt9WyVSHvutxMAJf7FJUnM7/oQ0dG0giZFmA7mn7S
|
||||
5u046uwBHjxIVkkJx0w3AJ6IDsBz4W9m6XJHMD4Q5QsDyZpCAGzFlH5hxIrff4Ia
|
||||
C1nEWTJ3s7xgaVY5/bQGeyzWZDbZvUjthB9+pSKPKrhC9IK31FOQeE4tGv2Bb0TX
|
||||
OwF0lkLgAOIua+rF7nKsu7/+6qqo+Nz2snmKtmcCAwEAAaNCMEAwHQYDVR0OBBYE
|
||||
FJ3AZ6YMItkm9UWrpmVSESfYRaxjMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/
|
||||
BAQDAgEGMA0GCSqGSIb3DQEBDAUAA4ICAQCzV00QYk465KzquByvMiPIs0laUZx2
|
||||
KI15qldGF9X1Uva3ROgIRL8YhNILgM3FEv0AVQVhh0HctSSePMTYyPtwni94loMg
|
||||
Nt58D2kTiKV1NpgIpsbfrM7jWNa3Pt668+s0QNiigfV4Py/VpfzZotReBA4Xrf5B
|
||||
8OWycvpEgjNC6C1Y91aMYj+6QrCcDFx+LmUmXFNPALJ4fqENmS2NuB2OosSw/WDQ
|
||||
MKSOyARiqcTtNd56l+0OOF6SL5Nwpamcb6d9Ex1+xghIsV5n61EIJenmJWtSKZGc
|
||||
0jlzCFfemQa0W50QBuHCAKi4HEoCChTQwUHK+4w1IX2COPKpVJEZNZOUbWo6xbLQ
|
||||
u4mGk+ibyQ86p3q4ofB4Rvr8Ny/lioTz3/4E2aFooC8k4gmVBtWVyuEklut89pMF
|
||||
u+1z6S3RdTnX5yTb2E5fQ4+e0BQ5v1VwSJlXMbSc7kqYA5YwH2AG7hsj/oFgIxpH
|
||||
YoWlzBk0gG+zrBrjn/B7SK3VAdlntqlyk+otZrWyuOQ9PLLvTIzq6we/qzWaVYa8
|
||||
GKa1qF60g2xraUDTn9zxw2lrueFtCfTxqlB2Cnp9ehehVZZCmTEJ3WARjQUwfuaO
|
||||
RtGdFNrHF+QFlozEJLUbzxQHskD4o55BhrwE0GuWyCqANP2/7waj3VjFhT0+j/6e
|
||||
KeC2uAloGRwYQw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIB/jCCAYWgAwIBAgIIdJclisc/elQwCgYIKoZIzj0EAwMwRTELMAkGA1UEBhMC
|
||||
VVMxFDASBgNVBAoMC0FmZmlybVRydXN0MSAwHgYDVQQDDBdBZmZpcm1UcnVzdCBQ
|
||||
cmVtaXVtIEVDQzAeFw0xMDAxMjkxNDIwMjRaFw00MDEyMzExNDIwMjRaMEUxCzAJ
|
||||
BgNVBAYTAlVTMRQwEgYDVQQKDAtBZmZpcm1UcnVzdDEgMB4GA1UEAwwXQWZmaXJt
|
||||
VHJ1c3QgUHJlbWl1bSBFQ0MwdjAQBgcqhkjOPQIBBgUrgQQAIgNiAAQNMF4bFZ0D
|
||||
0KF5Nbc6PJJ6yhUczWLznCZcBz3lVPqj1swS6vQUX+iOGasvLkjmrBhDeKzQN8O9
|
||||
ss0s5kfiGuZjuD0uL3jET9v0D6RoTFVya5UdThhClXjMNzyR4ptlKymjQjBAMB0G
|
||||
A1UdDgQWBBSaryl6wBE1NSZRMADDav5A1a7WPDAPBgNVHRMBAf8EBTADAQH/MA4G
|
||||
A1UdDwEB/wQEAwIBBjAKBggqhkjOPQQDAwNnADBkAjAXCfOHiFBar8jAQr9HX/Vs
|
||||
aobgxCd05DhT1wV/GzTjxi+zygk8N53X57hG8f2h4nECMEJZh0PUUd+60wkyWs6I
|
||||
flc9nF9Ca/UHLbXwgpP5WW+uZPpY5Yse42O+tYHNbwKMeQ==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDQTCCAimgAwIBAgITBmyfz5m/jAo54vB4ikPmljZbyjANBgkqhkiG9w0BAQsF
|
||||
ADA5MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6
|
||||
b24gUm9vdCBDQSAxMB4XDTE1MDUyNjAwMDAwMFoXDTM4MDExNzAwMDAwMFowOTEL
|
||||
MAkGA1UEBhMCVVMxDzANBgNVBAoTBkFtYXpvbjEZMBcGA1UEAxMQQW1hem9uIFJv
|
||||
b3QgQ0EgMTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBALJ4gHHKeNXj
|
||||
ca9HgFB0fW7Y14h29Jlo91ghYPl0hAEvrAIthtOgQ3pOsqTQNroBvo3bSMgHFzZM
|
||||
9O6II8c+6zf1tRn4SWiw3te5djgdYZ6k/oI2peVKVuRF4fn9tBb6dNqcmzU5L/qw
|
||||
IFAGbHrQgLKm+a/sRxmPUDgH3KKHOVj4utWp+UhnMJbulHheb4mjUcAwhmahRWa6
|
||||
VOujw5H5SNz/0egwLX0tdHA114gk957EWW67c4cX8jJGKLhD+rcdqsq08p8kDi1L
|
||||
93FcXmn/6pUCyziKrlA4b9v7LWIbxcceVOF34GfID5yHI9Y/QCB/IIDEgEw+OyQm
|
||||
jgSubJrIqg0CAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMC
|
||||
AYYwHQYDVR0OBBYEFIQYzIU07LwMlJQuCFmcx7IQTgoIMA0GCSqGSIb3DQEBCwUA
|
||||
A4IBAQCY8jdaQZChGsV2USggNiMOruYou6r4lK5IpDB/G/wkjUu0yKGX9rbxenDI
|
||||
U5PMCCjjmCXPI6T53iHTfIUJrU6adTrCC2qJeHZERxhlbI1Bjjt/msv0tadQ1wUs
|
||||
N+gDS63pYaACbvXy8MWy7Vu33PqUXHeeE6V/Uq2V8viTO96LXFvKWlJbYK8U90vv
|
||||
o/ufQJVtMVT8QtPHRh8jrdkPSHCa2XV4cdFyQzR1bldZwgJcJmApzyMZFo6IQ6XU
|
||||
5MsI+yMRQ+hDKXJioaldXgjUkK642M4UwtBV8ob2xJNDd2ZhwLnoQdeXeGADbkpy
|
||||
rqXRfboQnoZsG4q5WTP468SQvvG5
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFQTCCAymgAwIBAgITBmyf0pY1hp8KD+WGePhbJruKNzANBgkqhkiG9w0BAQwF
|
||||
ADA5MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6
|
||||
b24gUm9vdCBDQSAyMB4XDTE1MDUyNjAwMDAwMFoXDTQwMDUyNjAwMDAwMFowOTEL
|
||||
MAkGA1UEBhMCVVMxDzANBgNVBAoTBkFtYXpvbjEZMBcGA1UEAxMQQW1hem9uIFJv
|
||||
b3QgQ0EgMjCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAK2Wny2cSkxK
|
||||
gXlRmeyKy2tgURO8TW0G/LAIjd0ZEGrHJgw12MBvIITplLGbhQPDW9tK6Mj4kHbZ
|
||||
W0/jTOgGNk3Mmqw9DJArktQGGWCsN0R5hYGCrVo34A3MnaZMUnbqQ523BNFQ9lXg
|
||||
1dKmSYXpN+nKfq5clU1Imj+uIFptiJXZNLhSGkOQsL9sBbm2eLfq0OQ6PBJTYv9K
|
||||
8nu+NQWpEjTj82R0Yiw9AElaKP4yRLuH3WUnAnE72kr3H9rN9yFVkE8P7K6C4Z9r
|
||||
2UXTu/Bfh+08LDmG2j/e7HJV63mjrdvdfLC6HM783k81ds8P+HgfajZRRidhW+me
|
||||
z/CiVX18JYpvL7TFz4QuK/0NURBs+18bvBt+xa47mAExkv8LV/SasrlX6avvDXbR
|
||||
8O70zoan4G7ptGmh32n2M8ZpLpcTnqWHsFcQgTfJU7O7f/aS0ZzQGPSSbtqDT6Zj
|
||||
mUyl+17vIWR6IF9sZIUVyzfpYgwLKhbcAS4y2j5L9Z469hdAlO+ekQiG+r5jqFoz
|
||||
7Mt0Q5X5bGlSNscpb/xVA1wf+5+9R+vnSUeVC06JIglJ4PVhHvG/LopyboBZ/1c6
|
||||
+XUyo05f7O0oYtlNc/LMgRdg7c3r3NunysV+Ar3yVAhU/bQtCSwXVEqY0VThUWcI
|
||||
0u1ufm8/0i2BWSlmy5A5lREedCf+3euvAgMBAAGjQjBAMA8GA1UdEwEB/wQFMAMB
|
||||
Af8wDgYDVR0PAQH/BAQDAgGGMB0GA1UdDgQWBBSwDPBMMPQFWAJI/TPlUq9LhONm
|
||||
UjANBgkqhkiG9w0BAQwFAAOCAgEAqqiAjw54o+Ci1M3m9Zh6O+oAA7CXDpO8Wqj2
|
||||
LIxyh6mx/H9z/WNxeKWHWc8w4Q0QshNabYL1auaAn6AFC2jkR2vHat+2/XcycuUY
|
||||
+gn0oJMsXdKMdYV2ZZAMA3m3MSNjrXiDCYZohMr/+c8mmpJ5581LxedhpxfL86kS
|
||||
k5Nrp+gvU5LEYFiwzAJRGFuFjWJZY7attN6a+yb3ACfAXVU3dJnJUH/jWS5E4ywl
|
||||
7uxMMne0nxrpS10gxdr9HIcWxkPo1LsmmkVwXqkLN1PiRnsn/eBG8om3zEK2yygm
|
||||
btmlyTrIQRNg91CMFa6ybRoVGld45pIq2WWQgj9sAq+uEjonljYE1x2igGOpm/Hl
|
||||
urR8FLBOybEfdF849lHqm/osohHUqS0nGkWxr7JOcQ3AWEbWaQbLU8uz/mtBzUF+
|
||||
fUwPfHJ5elnNXkoOrJupmHN5fLT0zLm4BwyydFy4x2+IoZCn9Kr5v2c69BoVYh63
|
||||
n749sSmvZ6ES8lgQGVMDMBu4Gon2nL2XA46jCfMdiyHxtN/kHNGfZQIG6lzWE7OE
|
||||
76KlXIx3KadowGuuQNKotOrN8I1LOJwZmhsoVLiJkO/KdYE+HvJkJMcYr07/R54H
|
||||
9jVlpNMKVv/1F2Rs76giJUmTtt8AF9pYfl3uxRuw0dFfIRDH+fO6AgonB8Xx1sfT
|
||||
4PsJYGw=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIBtjCCAVugAwIBAgITBmyf1XSXNmY/Owua2eiedgPySjAKBggqhkjOPQQDAjA5
|
||||
MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6b24g
|
||||
Um9vdCBDQSAzMB4XDTE1MDUyNjAwMDAwMFoXDTQwMDUyNjAwMDAwMFowOTELMAkG
|
||||
A1UEBhMCVVMxDzANBgNVBAoTBkFtYXpvbjEZMBcGA1UEAxMQQW1hem9uIFJvb3Qg
|
||||
Q0EgMzBZMBMGByqGSM49AgEGCCqGSM49AwEHA0IABCmXp8ZBf8ANm+gBG1bG8lKl
|
||||
ui2yEujSLtf6ycXYqm0fc4E7O5hrOXwzpcVOho6AF2hiRVd9RFgdszflZwjrZt6j
|
||||
QjBAMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgGGMB0GA1UdDgQWBBSr
|
||||
ttvXBp43rDCGB5Fwx5zEGbF4wDAKBggqhkjOPQQDAgNJADBGAiEA4IWSoxe3jfkr
|
||||
BqWTrBqYaGFy+uGh0PsceGCmQ5nFuMQCIQCcAu/xlJyzlvnrxir4tiz+OpAUFteM
|
||||
YyRIHN8wfdVoOw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIB8jCCAXigAwIBAgITBmyf18G7EEwpQ+Vxe3ssyBrBDjAKBggqhkjOPQQDAzA5
|
||||
MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6b24g
|
||||
Um9vdCBDQSA0MB4XDTE1MDUyNjAwMDAwMFoXDTQwMDUyNjAwMDAwMFowOTELMAkG
|
||||
A1UEBhMCVVMxDzANBgNVBAoTBkFtYXpvbjEZMBcGA1UEAxMQQW1hem9uIFJvb3Qg
|
||||
Q0EgNDB2MBAGByqGSM49AgEGBSuBBAAiA2IABNKrijdPo1MN/sGKe0uoe0ZLY7Bi
|
||||
9i0b2whxIdIA6GO9mif78DluXeo9pcmBqqNbIJhFXRbb/egQbeOc4OO9X4Ri83Bk
|
||||
M6DLJC9wuoihKqB1+IGuYgbEgds5bimwHvouXKNCMEAwDwYDVR0TAQH/BAUwAwEB
|
||||
/zAOBgNVHQ8BAf8EBAMCAYYwHQYDVR0OBBYEFNPsxzplbszh2naaVvuc84ZtV+WB
|
||||
MAoGCCqGSM49BAMDA2gAMGUCMDqLIfG9fhGt0O9Yli/W651+kI0rz2ZVwyzjKKlw
|
||||
CkcO8DdZEv8tmZQoTipPNU0zWgIxAOp1AE47xDqUEpHJWEadIRNyp4iciuRMStuW
|
||||
1KyLa2tJElMzrdfkviT8tQp21KW8EA==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDdzCCAl+gAwIBAgIIXDPLYixfszIwDQYJKoZIhvcNAQELBQAwPDEeMBwGA1UE
|
||||
AwwVQXRvcyBUcnVzdGVkUm9vdCAyMDExMQ0wCwYDVQQKDARBdG9zMQswCQYDVQQG
|
||||
EwJERTAeFw0xMTA3MDcxNDU4MzBaFw0zMDEyMzEyMzU5NTlaMDwxHjAcBgNVBAMM
|
||||
FUF0b3MgVHJ1c3RlZFJvb3QgMjAxMTENMAsGA1UECgwEQXRvczELMAkGA1UEBhMC
|
||||
REUwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCVhTuXbyo7LjvPpvMp
|
||||
Nb7PGKw+qtn4TaA+Gke5vJrf8v7MPkfoepbCJI419KkM/IL9bcFyYie96mvr54rM
|
||||
VD6QUM+A1JX76LWC1BTFtqlVJVfbsVD2sGBkWXppzwO3bw2+yj5vdHLqqjAqc2K+
|
||||
SZFhyBH+DgMq92og3AIVDV4VavzjgsG1xZ1kCWyjWZgHJ8cblithdHFsQ/H3NYkQ
|
||||
4J7sVaE3IqKHBAUsR320HLliKWYoyrfhk/WklAOZuXCFteZI6o1Q/NnezG8HDt0L
|
||||
cp2AMBYHlT8oDv3FdU9T1nSatCQujgKRz3bFmx5VdJx4IbHwLfELn8LVlhgf8FQi
|
||||
eowHAgMBAAGjfTB7MB0GA1UdDgQWBBSnpQaxLKYJYO7Rl+lwrrw7GWzbITAPBgNV
|
||||
HRMBAf8EBTADAQH/MB8GA1UdIwQYMBaAFKelBrEspglg7tGX6XCuvDsZbNshMBgG
|
||||
A1UdIAQRMA8wDQYLKwYBBAGwLQMEAQEwDgYDVR0PAQH/BAQDAgGGMA0GCSqGSIb3
|
||||
DQEBCwUAA4IBAQAmdzTblEiGKkGdLD4GkGDEjKwLVLgfuXvTBznk+j57sj1O7Z8j
|
||||
vZfza1zv7v1Apt+hk6EKhqzvINB5Ab149xnYJDE0BAGmuhWawyfc2E8PzBhj/5kP
|
||||
DpFrdRbhIfzYJsdHt6bPWHJxfrrhTZVHO8mvbaG0weyJ9rQPOLXiZNwlz6bb65pc
|
||||
maHFCN795trV1lpFDMS3wrUU77QR/w4VtfX128a961qn8FYiqTxlVMYVqL2Gns2D
|
||||
lmh6cYGJ4Qvh6hEbaAjMaZ7snkGeRDImeuKHCnE96+RapNLbxc3G3mB/ufNPRJLv
|
||||
KrcYPqcZ2Qt9sTdBQrC6YB3y/gkRsPCHe6ed
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIGFDCCA/ygAwIBAgIIU+w77vuySF8wDQYJKoZIhvcNAQEFBQAwUTELMAkGA1UE
|
||||
BhMCRVMxQjBABgNVBAMMOUF1dG9yaWRhZCBkZSBDZXJ0aWZpY2FjaW9uIEZpcm1h
|
||||
cHJvZmVzaW9uYWwgQ0lGIEE2MjYzNDA2ODAeFw0wOTA1MjAwODM4MTVaFw0zMDEy
|
||||
MzEwODM4MTVaMFExCzAJBgNVBAYTAkVTMUIwQAYDVQQDDDlBdXRvcmlkYWQgZGUg
|
||||
Q2VydGlmaWNhY2lvbiBGaXJtYXByb2Zlc2lvbmFsIENJRiBBNjI2MzQwNjgwggIi
|
||||
MA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDKlmuO6vj78aI14H9M2uDDUtd9
|
||||
thDIAl6zQyrET2qyyhxdKJp4ERppWVevtSBC5IsP5t9bpgOSL/UR5GLXMnE42QQM
|
||||
cas9UX4PB99jBVzpv5RvwSmCwLTaUbDBPLutN0pcyvFLNg4kq7/DhHf9qFD0sefG
|
||||
L9ItWY16Ck6WaVICqjaY7Pz6FIMMNx/Jkjd/14Et5cS54D40/mf0PmbR0/RAz15i
|
||||
NA9wBj4gGFrO93IbJWyTdBSTo3OxDqqHECNZXyAFGUftaI6SEspd/NYrspI8IM/h
|
||||
X68gvqB2f3bl7BqGYTM+53u0P6APjqK5am+5hyZvQWyIplD9amML9ZMWGxmPsu2b
|
||||
m8mQ9QEM3xk9Dz44I8kvjwzRAv4bVdZO0I08r0+k8/6vKtMFnXkIoctXMbScyJCy
|
||||
Z/QYFpM6/EfY0XiWMR+6KwxfXZmtY4laJCB22N/9q06mIqqdXuYnin1oKaPnirja
|
||||
EbsXLZmdEyRG98Xi2J+Of8ePdG1asuhy9azuJBCtLxTa/y2aRnFHvkLfuwHb9H/T
|
||||
KI8xWVvTyQKmtFLKbpf7Q8UIJm+K9Lv9nyiqDdVF8xM6HdjAeI9BZzwelGSuewvF
|
||||
6NkBiDkal4ZkQdU7hwxu+g/GvUgUvzlN1J5Bto+WHWOWk9mVBngxaJ43BjuAiUVh
|
||||
OSPHG0SjFeUc+JIwuwIDAQABo4HvMIHsMBIGA1UdEwEB/wQIMAYBAf8CAQEwDgYD
|
||||
VR0PAQH/BAQDAgEGMB0GA1UdDgQWBBRlzeurNR4APn7VdMActHNHDhpkLzCBpgYD
|
||||
VR0gBIGeMIGbMIGYBgRVHSAAMIGPMC8GCCsGAQUFBwIBFiNodHRwOi8vd3d3LmZp
|
||||
cm1hcHJvZmVzaW9uYWwuY29tL2NwczBcBggrBgEFBQcCAjBQHk4AUABhAHMAZQBv
|
||||
ACAAZABlACAAbABhACAAQgBvAG4AYQBuAG8AdgBhACAANAA3ACAAQgBhAHIAYwBl
|
||||
AGwAbwBuAGEAIAAwADgAMAAxADcwDQYJKoZIhvcNAQEFBQADggIBABd9oPm03cXF
|
||||
661LJLWhAqvdpYhKsg9VSytXjDvlMd3+xDLx51tkljYyGOylMnfX40S2wBEqgLk9
|
||||
am58m9Ot/MPWo+ZkKXzR4Tgegiv/J2Wv+xYVxC5xhOW1//qkR71kMrv2JYSiJ0L1
|
||||
ILDCExARzRAVukKQKtJE4ZYm6zFIEv0q2skGz3QeqUvVhyj5eTSSPi5E6PaPT481
|
||||
PyWzOdxjKpBrIF/EUhJOlywqrJ2X3kjyo2bbwtKDlaZmp54lD+kLM5FlClrD2VQS
|
||||
3a/DTg4fJl4N3LON7NWBcN7STyQF82xO9UxJZo3R/9ILJUFI/lGExkKvgATP0H5k
|
||||
SeTy36LssUzAKh3ntLFlosS88Zj0qnAHY7S42jtM+kAiMFsRpvAFDsYCA0irhpuF
|
||||
3dvd6qJ2gHN99ZwExEWN57kci57q13XRcrHedUTnQn3iV2t93Jm8PYMo6oCTjcVM
|
||||
ZcFwgbg4/EMxsvYDNEeyrPsiBsse3RdHHF9mudMaotoRsaS8I8nkvof/uZS2+F0g
|
||||
StRf571oe2XyFR7SOqkt6dhrJKyXWERHrVkY8SFlcN7ONGCoQPHzPKTDKCOM/icz
|
||||
Q0CgFzzr6juwcqajuUpLXhZI9LK8yIySxZ2frHI2vDSANGupi5LAuBft7HZT9SQB
|
||||
jLMi6Et8Vcad+qMUu2WFbm5PEn4KPJ2V
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDdzCCAl+gAwIBAgIEAgAAuTANBgkqhkiG9w0BAQUFADBaMQswCQYDVQQGEwJJ
|
||||
RTESMBAGA1UEChMJQmFsdGltb3JlMRMwEQYDVQQLEwpDeWJlclRydXN0MSIwIAYD
|
||||
VQQDExlCYWx0aW1vcmUgQ3liZXJUcnVzdCBSb290MB4XDTAwMDUxMjE4NDYwMFoX
|
||||
DTI1MDUxMjIzNTkwMFowWjELMAkGA1UEBhMCSUUxEjAQBgNVBAoTCUJhbHRpbW9y
|
||||
ZTETMBEGA1UECxMKQ3liZXJUcnVzdDEiMCAGA1UEAxMZQmFsdGltb3JlIEN5YmVy
|
||||
VHJ1c3QgUm9vdDCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAKMEuyKr
|
||||
mD1X6CZymrV51Cni4eiVgLGw41uOKymaZN+hXe2wCQVt2yguzmKiYv60iNoS6zjr
|
||||
IZ3AQSsBUnuId9Mcj8e6uYi1agnnc+gRQKfRzMpijS3ljwumUNKoUMMo6vWrJYeK
|
||||
mpYcqWe4PwzV9/lSEy/CG9VwcPCPwBLKBsua4dnKM3p31vjsufFoREJIE9LAwqSu
|
||||
XmD+tqYF/LTdB1kC1FkYmGP1pWPgkAx9XbIGevOF6uvUA65ehD5f/xXtabz5OTZy
|
||||
dc93Uk3zyZAsuT3lySNTPx8kmCFcB5kpvcY67Oduhjprl3RjM71oGDHweI12v/ye
|
||||
jl0qhqdNkNwnGjkCAwEAAaNFMEMwHQYDVR0OBBYEFOWdWTCCR1jMrPoIVDaGezq1
|
||||
BE3wMBIGA1UdEwEB/wQIMAYBAf8CAQMwDgYDVR0PAQH/BAQDAgEGMA0GCSqGSIb3
|
||||
DQEBBQUAA4IBAQCFDF2O5G9RaEIFoN27TyclhAO992T9Ldcw46QQF+vaKSm2eT92
|
||||
9hkTI7gQCvlYpNRhcL0EYWoSihfVCr3FvDB81ukMJY2GQE/szKN+OMY3EU/t3Wgx
|
||||
jkzSswF07r51XgdIGn9w/xZchMB5hbgF/X++ZRGjD8ACtPhSNzkE1akxehi/oCr0
|
||||
Epn3o0WC4zxe9Z2etciefC7IpJ5OCBRLbf1wbWsaY71k5h+3zvDyny67G7fyUIhz
|
||||
ksLi4xaNmjICq44Y3ekQEe5+NauQrz4wlHrQMz2nZQ/1/I6eYs9HRCwBXbsdtTLS
|
||||
R9I4LtD+gdwyah617jzV/OeBHRnDJELqYzmp
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFWTCCA0GgAwIBAgIBAjANBgkqhkiG9w0BAQsFADBOMQswCQYDVQQGEwJOTzEd
|
||||
MBsGA1UECgwUQnV5cGFzcyBBUy05ODMxNjMzMjcxIDAeBgNVBAMMF0J1eXBhc3Mg
|
||||
Q2xhc3MgMiBSb290IENBMB4XDTEwMTAyNjA4MzgwM1oXDTQwMTAyNjA4MzgwM1ow
|
||||
TjELMAkGA1UEBhMCTk8xHTAbBgNVBAoMFEJ1eXBhc3MgQVMtOTgzMTYzMzI3MSAw
|
||||
HgYDVQQDDBdCdXlwYXNzIENsYXNzIDIgUm9vdCBDQTCCAiIwDQYJKoZIhvcNAQEB
|
||||
BQADggIPADCCAgoCggIBANfHXvfBB9R3+0Mh9PT1aeTuMgHbo4Yf5FkNuud1g1Lr
|
||||
6hxhFUi7HQfKjK6w3Jad6sNgkoaCKHOcVgb/S2TwDCo3SbXlzwx87vFKu3MwZfPV
|
||||
L4O2fuPn9Z6rYPnT8Z2SdIrkHJasW4DptfQxh6NR/Md+oW+OU3fUl8FVM5I+GC91
|
||||
1K2GScuVr1QGbNgGE41b/+EmGVnAJLqBcXmQRFBoJJRfuLMR8SlBYaNByyM21cHx
|
||||
MlAQTn/0hpPshNOOvEu/XAFOBz3cFIqUCqTqc/sLUegTBxj6DvEr0VQVfTzh97QZ
|
||||
QmdiXnfgolXsttlpF9U6r0TtSsWe5HonfOV116rLJeffawrbD02TTqigzXsu8lkB
|
||||
arcNuAeBfos4GzjmCleZPe4h6KP1DBbdi+w0jpwqHAAVF41og9JwnxgIzRFo1clr
|
||||
Us3ERo/ctfPYV3Me6ZQ5BL/T3jjetFPsaRyifsSP5BtwrfKi+fv3FmRmaZ9JUaLi
|
||||
FRhnBkp/1Wy1TbMz4GHrXb7pmA8y1x1LPC5aAVKRCfLf6o3YBkBjqhHk/sM3nhRS
|
||||
P/TizPJhk9H9Z2vXUq6/aKtAQ6BXNVN48FP4YUIHZMbXb5tMOA1jrGKvNouicwoN
|
||||
9SG9dKpN6nIDSdvHXx1iY8f93ZHsM+71bbRuMGjeyNYmsHVee7QHIJihdjK4TWxP
|
||||
AgMBAAGjQjBAMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFMmAd+BikoL1Rpzz
|
||||
uvdMw964o605MA4GA1UdDwEB/wQEAwIBBjANBgkqhkiG9w0BAQsFAAOCAgEAU18h
|
||||
9bqwOlI5LJKwbADJ784g7wbylp7ppHR/ehb8t/W2+xUbP6umwHJdELFx7rxP462s
|
||||
A20ucS6vxOOto70MEae0/0qyexAQH6dXQbLArvQsWdZHEIjzIVEpMMpghq9Gqx3t
|
||||
OluwlN5E40EIosHsHdb9T7bWR9AUC8rmyrV7d35BH16Dx7aMOZawP5aBQW9gkOLo
|
||||
+fsicdl9sz1Gv7SEr5AcD48Saq/v7h56rgJKihcrdv6sVIkkLE8/trKnToyokZf7
|
||||
KcZ7XC25y2a2t6hbElGFtQl+Ynhw/qlqYLYdDnkM/crqJIByw5c/8nerQyIKx+u2
|
||||
DISCLIBrQYoIwOula9+ZEsuK1V6ADJHgJgg2SMX6OBE1/yWDLfJ6v9r9jv6ly0Us
|
||||
H8SIU653DtmadsWOLB2jutXsMq7Aqqz30XpN69QH4kj3Io6wpJ9qzo6ysmD0oyLQ
|
||||
I+uUWnpp3Q+/QFesa1lQ2aOZ4W7+jQF5JyMV3pKdewlNWudLSDBaGOYKbeaP4NK7
|
||||
5t98biGCwWg5TbSYWGZizEqQXsP6JwSxeRV0mcy+rSDeJmAc61ZRpqPq5KM/p/9h
|
||||
3PFaTWwyI0PurKju7koSCTxdccK+efrCh2gdC/1cacwG0Jp9VJkqyTkaGa9LKkPz
|
||||
Y11aWOIv4x3kqdbQCtCev9eBCfHJxyYNrJgWVqA=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFWTCCA0GgAwIBAgIBAjANBgkqhkiG9w0BAQsFADBOMQswCQYDVQQGEwJOTzEd
|
||||
MBsGA1UECgwUQnV5cGFzcyBBUy05ODMxNjMzMjcxIDAeBgNVBAMMF0J1eXBhc3Mg
|
||||
Q2xhc3MgMyBSb290IENBMB4XDTEwMTAyNjA4Mjg1OFoXDTQwMTAyNjA4Mjg1OFow
|
||||
TjELMAkGA1UEBhMCTk8xHTAbBgNVBAoMFEJ1eXBhc3MgQVMtOTgzMTYzMzI3MSAw
|
||||
HgYDVQQDDBdCdXlwYXNzIENsYXNzIDMgUm9vdCBDQTCCAiIwDQYJKoZIhvcNAQEB
|
||||
BQADggIPADCCAgoCggIBAKXaCpUWUOOV8l6ddjEGMnqb8RB2uACatVI2zSRHsJ8Y
|
||||
ZLya9vrVediQYkwiL944PdbgqOkcLNt4EemOaFEVcsfzM4fkoF0LXOBXByow9c3E
|
||||
N3coTRiR5r/VUv1xLXA+58bEiuPwKAv0dpihi4dVsjoT/Lc+JzeOIuOoTyrvYLs9
|
||||
tznDDgFHmV0ST9tD+leh7fmdvhFHJlsTmKtdFoqwNxxXnUX/iJY2v7vKB3tvh2PX
|
||||
0DJq1l1sDPGzbjniazEuOQAnFN44wOwZZoYS6J1yFhNkUsepNxz9gjDthBgd9K5c
|
||||
/3ATAOux9TN6S9ZV+AWNS2mw9bMoNlwUxFFzTWsL8TQH2xc519woe2v1n/MuwU8X
|
||||
KhDzzMro6/1rqy6any2CbgTUUgGTLT2G/H783+9CHaZr77kgxve9oKeV/afmiSTY
|
||||
zIw0bOIjL9kSGiG5VZFvC5F5GQytQIgLcOJ60g7YaEi7ghM5EFjp2CoHxhLbWNvS
|
||||
O1UQRwUVZ2J+GGOmRj8JDlQyXr8NYnon74Do29lLBlo3WiXQCBJ31G8JUJc9yB3D
|
||||
34xFMFbG02SrZvPAXpacw8Tvw3xrizp5f7NJzz3iiZ+gMEuFuZyUJHmPfWupRWgP
|
||||
K9Dx2hzLabjKSWJtyNBjYt1gD1iqj6G8BaVmos8bdrKEZLFMOVLAMLrwjEsCsLa3
|
||||
AgMBAAGjQjBAMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFEe4zf/lb+74suwv
|
||||
Tg75JbCOPGvDMA4GA1UdDwEB/wQEAwIBBjANBgkqhkiG9w0BAQsFAAOCAgEAACAj
|
||||
QTUEkMJAYmDv4jVM1z+s4jSQuKFvdvoWFqRINyzpkMLyPPgKn9iB5btb2iUspKdV
|
||||
cSQy9sgL8rxq+JOssgfCX5/bzMiKqr5qb+FJEMwx14C7u8jYog5kV+qi9cKpMRXS
|
||||
IGrs/CIBKM+GuIAeqcwRpTzyFrNHnfzSgCHEy9BHcEGhyoMZCCxt8l13nIoUE9Q2
|
||||
HJLw5QY33KbmkJs4j1xrG0aGQ0JfPgEHU1RdZX33inOhmlRaHylDFCfChQ+1iHsa
|
||||
O5S3HWCntZznKWlXWpuTekMwGwPXYshApqr8ZORK15FTAaggiG6cX0S5y2CBNOxv
|
||||
033aSF/rtJC8LakcC6wc1aJoIIAE1vyxjy+7SjENSoYc6+I2KSb12tjE8nVhz36u
|
||||
dmNKekBlk4f4HoCMhuWG1o8O/FMsYOgWYRqiPkN7zTlgVGr18okmAWiDSKIz6MkE
|
||||
kbIRNBE+6tBDGR8Dk5AM/1E9V/RBbuHLoL7ryWPNbczk+DaqaJ3tvV2XcEQNtg41
|
||||
3OEMXbugUZTLfhbrES+jkkXITHHZvMmZUldGL1DPvTVp9D0VzgalLA8+9oG6lLvD
|
||||
u79leNKGef9JOxqDDPDeeOzI8k1MGt6CKfjBWtrt7uYnXuhF0J0cUahoq0Tj0Itq
|
||||
4/g7u9xN12TyUb7mqqta6THuBrxzvxNiCp/HuZc=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFaTCCA1GgAwIBAgIJAJK4iNuwisFjMA0GCSqGSIb3DQEBCwUAMFIxCzAJBgNV
|
||||
BAYTAlNLMRMwEQYDVQQHEwpCcmF0aXNsYXZhMRMwEQYDVQQKEwpEaXNpZyBhLnMu
|
||||
MRkwFwYDVQQDExBDQSBEaXNpZyBSb290IFIyMB4XDTEyMDcxOTA5MTUzMFoXDTQy
|
||||
MDcxOTA5MTUzMFowUjELMAkGA1UEBhMCU0sxEzARBgNVBAcTCkJyYXRpc2xhdmEx
|
||||
EzARBgNVBAoTCkRpc2lnIGEucy4xGTAXBgNVBAMTEENBIERpc2lnIFJvb3QgUjIw
|
||||
ggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQCio8QACdaFXS1tFPbCw3Oe
|
||||
NcJxVX6B+6tGUODBfEl45qt5WDza/3wcn9iXAng+a0EE6UG9vgMsRfYvZNSrXaNH
|
||||
PWSb6WiaxswbP7q+sos0Ai6YVRn8jG+qX9pMzk0DIaPY0jSTVpbLTAwAFjxfGs3I
|
||||
x2ymrdMxp7zo5eFm1tL7A7RBZckQrg4FY8aAamkw/dLukO8NJ9+flXP04SXabBbe
|
||||
QTg06ov80egEFGEtQX6sx3dOy1FU+16SGBsEWmjGycT6txOgmLcRK7fWV8x8nhfR
|
||||
yyX+hk4kLlYMeE2eARKmK6cBZW58Yh2EhN/qwGu1pSqVg8NTEQxzHQuyRpDRQjrO
|
||||
QG6Vrf/GlK1ul4SOfW+eioANSW1z4nuSHsPzwfPrLgVv2RvPN3YEyLRa5Beny912
|
||||
H9AZdugsBbPWnDTYltxhh5EF5EQIM8HauQhl1K6yNg3ruji6DOWbnuuNZt2Zz9aJ
|
||||
QfYEkoopKW1rOhzndX0CcQ7zwOe9yxndnWCywmZgtrEE7snmhrmaZkCo5xHtgUUD
|
||||
i/ZnWejBBhG93c+AAk9lQHhcR1DIm+YfgXvkRKhbhZri3lrVx/k6RGZL5DJUfORs
|
||||
nLMOPReisjQS1n6yqEm70XooQL6iFh/f5DcfEXP7kAplQ6INfPgGAVUzfbANuPT1
|
||||
rqVCV3w2EYx7XsQDnYx5nQIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1Ud
|
||||
DwEB/wQEAwIBBjAdBgNVHQ4EFgQUtZn4r7CU9eMg1gqtzk5WpC5uQu0wDQYJKoZI
|
||||
hvcNAQELBQADggIBACYGXnDnZTPIgm7ZnBc6G3pmsgH2eDtpXi/q/075KMOYKmFM
|
||||
tCQSin1tERT3nLXK5ryeJ45MGcipvXrA1zYObYVybqjGom32+nNjf7xueQgcnYqf
|
||||
GopTpti72TVVsRHFqQOzVju5hJMiXn7B9hJSi+osZ7z+Nkz1uM/Rs0mSO9MpDpkb
|
||||
lvdhuDvEK7Z4bLQjb/D907JedR+Zlais9trhxTF7+9FGs9K8Z7RiVLoJ92Owk6Ka
|
||||
+elSLotgEqv89WBW7xBci8QaQtyDW2QOy7W81k/BfDxujRNt+3vrMNDcTa/F1bal
|
||||
TFtxyegxvug4BkihGuLq0t4SOVga/4AOgnXmt8kHbA7v/zjxmHHEt38OFdAlab0i
|
||||
nSvtBfZGR6ztwPDUO+Ls7pZbkBNOHlY667DvlruWIxG68kOGdGSVyCh13x01utI3
|
||||
gzhTODY7z2zp+WsO0PsE6E9312UBeIYMej4hYvF/Y3EMyZ9E26gnonW+boE+18Dr
|
||||
G5gPcFw0sorMwIUY6256s/daoQe/qUKS82Ail+QUoQebTnbAjn39pCXHR+3/H3Os
|
||||
zMOl6W8KjptlwlCFtaOgUxLMVYdh84GuEEZhvUQhuMI9dM9+JDX6HAcOmz0iyu8x
|
||||
L4ysEr3vQCj8KWefshNPZiTEUxnpHikV7+ZtsH8tZ/3zbBt1RqPlShfppNcL
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFjTCCA3WgAwIBAgIEGErM1jANBgkqhkiG9w0BAQsFADBWMQswCQYDVQQGEwJD
|
||||
TjEwMC4GA1UECgwnQ2hpbmEgRmluYW5jaWFsIENlcnRpZmljYXRpb24gQXV0aG9y
|
||||
aXR5MRUwEwYDVQQDDAxDRkNBIEVWIFJPT1QwHhcNMTIwODA4MDMwNzAxWhcNMjkx
|
||||
MjMxMDMwNzAxWjBWMQswCQYDVQQGEwJDTjEwMC4GA1UECgwnQ2hpbmEgRmluYW5j
|
||||
aWFsIENlcnRpZmljYXRpb24gQXV0aG9yaXR5MRUwEwYDVQQDDAxDRkNBIEVWIFJP
|
||||
T1QwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDXXWvNED8fBVnVBU03
|
||||
sQ7smCuOFR36k0sXgiFxEFLXUWRwFsJVaU2OFW2fvwwbwuCjZ9YMrM8irq93VCpL
|
||||
TIpTUnrD7i7es3ElweldPe6hL6P3KjzJIx1qqx2hp/Hz7KDVRM8Vz3IvHWOX6Jn5
|
||||
/ZOkVIBMUtRSqy5J35DNuF++P96hyk0g1CXohClTt7GIH//62pCfCqktQT+x8Rgp
|
||||
7hZZLDRJGqgG16iI0gNyejLi6mhNbiyWZXvKWfry4t3uMCz7zEasxGPrb382KzRz
|
||||
EpR/38wmnvFyXVBlWY9ps4deMm/DGIq1lY+wejfeWkU7xzbh72fROdOXW3NiGUgt
|
||||
hxwG+3SYIElz8AXSG7Ggo7cbcNOIabla1jj0Ytwli3i/+Oh+uFzJlU9fpy25IGvP
|
||||
a931DfSCt/SyZi4QKPaXWnuWFo8BGS1sbn85WAZkgwGDg8NNkt0yxoekN+kWzqot
|
||||
aK8KgWU6cMGbrU1tVMoqLUuFG7OA5nBFDWteNfB/O7ic5ARwiRIlk9oKmSJgamNg
|
||||
TnYGmE69g60dWIolhdLHZR4tjsbftsbhf4oEIRUpdPA+nJCdDC7xij5aqgwJHsfV
|
||||
PKPtl8MeNPo4+QgO48BdK4PRVmrJtqhUUy54Mmc9gn900PvhtgVguXDbjgv5E1hv
|
||||
cWAQUhC5wUEJ73IfZzF4/5YFjQIDAQABo2MwYTAfBgNVHSMEGDAWgBTj/i39KNAL
|
||||
tbq2osS/BqoFjJP7LzAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIBBjAd
|
||||
BgNVHQ4EFgQU4/4t/SjQC7W6tqLEvwaqBYyT+y8wDQYJKoZIhvcNAQELBQADggIB
|
||||
ACXGumvrh8vegjmWPfBEp2uEcwPenStPuiB/vHiyz5ewG5zz13ku9Ui20vsXiObT
|
||||
ej/tUxPQ4i9qecsAIyjmHjdXNYmEwnZPNDatZ8POQQaIxffu2Bq41gt/UP+TqhdL
|
||||
jOztUmCypAbqTuv0axn96/Ua4CUqmtzHQTb3yHQFhDmVOdYLO6Qn+gjYXB74BGBS
|
||||
ESgoA//vU2YApUo0FmZ8/Qmkrp5nGm9BC2sGE5uPhnEFtC+NiWYzKXZUmhH4J/qy
|
||||
P5Hgzg0b8zAarb8iXRvTvyUFTeGSGn+ZnzxEk8rUQElsgIfXBDrDMlI1Dlb4pd19
|
||||
xIsNER9Tyx6yF7Zod1rg1MvIB671Oi6ON7fQAUtDKXeMOZePglr4UeWJoBjnaH9d
|
||||
Ci77o0cOPaYjesYBx4/IXr9tgFa+iiS6M+qf4TIRnvHST4D2G0CvOJ4RUHlzEhLN
|
||||
5mydLIhyPDCBBpEi6lmt2hkuIsKNuYyH4Ga8cyNfIWRjgEj1oDwYPZTISEEdQLpe
|
||||
/v5WOaHIz16eGWRGENoXkbcFgKyLmZJ956LYBws2J+dIeWCKw9cTXPhyQN9Ky8+Z
|
||||
AAoACxGV2lZFA4gKn2fQ1XmxqI1AbQ3CekD6819kR5LLU7m7Wc5P/dAVUwHY3+vZ
|
||||
5nbv0CO7O6l5s9UCKc2Jo5YPSjXnTkLAdc0Hz+Ys63su
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEHTCCAwWgAwIBAgIQToEtioJl4AsC7j41AkblPTANBgkqhkiG9w0BAQUFADCB
|
||||
gTELMAkGA1UEBhMCR0IxGzAZBgNVBAgTEkdyZWF0ZXIgTWFuY2hlc3RlcjEQMA4G
|
||||
A1UEBxMHU2FsZm9yZDEaMBgGA1UEChMRQ09NT0RPIENBIExpbWl0ZWQxJzAlBgNV
|
||||
BAMTHkNPTU9ETyBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTAeFw0wNjEyMDEwMDAw
|
||||
MDBaFw0yOTEyMzEyMzU5NTlaMIGBMQswCQYDVQQGEwJHQjEbMBkGA1UECBMSR3Jl
|
||||
YXRlciBNYW5jaGVzdGVyMRAwDgYDVQQHEwdTYWxmb3JkMRowGAYDVQQKExFDT01P
|
||||
RE8gQ0EgTGltaXRlZDEnMCUGA1UEAxMeQ09NT0RPIENlcnRpZmljYXRpb24gQXV0
|
||||
aG9yaXR5MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA0ECLi3LjkRv3
|
||||
UcEbVASY06m/weaKXTuH+7uIzg3jLz8GlvCiKVCZrts7oVewdFFxze1CkU1B/qnI
|
||||
2GqGd0S7WWaXUF601CxwRM/aN5VCaTwwxHGzUvAhTaHYujl8HJ6jJJ3ygxaYqhZ8
|
||||
Q5sVW7euNJH+1GImGEaaP+vB+fGQV+useg2L23IwambV4EajcNxo2f8ESIl33rXp
|
||||
+2dtQem8Ob0y2WIC8bGoPW43nOIv4tOiJovGuFVDiOEjPqXSJDlqR6sA1KGzqSX+
|
||||
DT+nHbrTUcELpNqsOO9VUCQFZUaTNE8tja3G1CEZ0o7KBWFxB3NH5YoZEr0ETc5O
|
||||
nKVIrLsm9wIDAQABo4GOMIGLMB0GA1UdDgQWBBQLWOWLxkwVN6RAqTCpIb5HNlpW
|
||||
/zAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB/zBJBgNVHR8EQjBAMD6g
|
||||
PKA6hjhodHRwOi8vY3JsLmNvbW9kb2NhLmNvbS9DT01PRE9DZXJ0aWZpY2F0aW9u
|
||||
QXV0aG9yaXR5LmNybDANBgkqhkiG9w0BAQUFAAOCAQEAPpiem/Yb6dc5t3iuHXIY
|
||||
SdOH5EOC6z/JqvWote9VfCFSZfnVDeFs9D6Mk3ORLgLETgdxb8CPOGEIqB6BCsAv
|
||||
IC9Bi5HcSEW88cbeunZrM8gALTFGTO3nnc+IlP8zwFboJIYmuNg4ON8qa90SzMc/
|
||||
RxdMosIGlgnW2/4/PEZB31jiVg88O8EckzXZOFKs7sjsLjBOlDW0JB9LeGna8gI4
|
||||
zJVSk/BwJVmcIGfE7vmLV2H0knZ9P4SNVbfo5azV8fUZVqZa+5Acr5Pr5RzUZ5dd
|
||||
BA6+C4OmF4O5MBKgxTMVBbkN+8cFduPYSo38NBejxiEovjBFMR7HeL5YYTisO+IB
|
||||
ZQ==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICiTCCAg+gAwIBAgIQH0evqmIAcFBUTAGem2OZKjAKBggqhkjOPQQDAzCBhTEL
|
||||
MAkGA1UEBhMCR0IxGzAZBgNVBAgTEkdyZWF0ZXIgTWFuY2hlc3RlcjEQMA4GA1UE
|
||||
BxMHU2FsZm9yZDEaMBgGA1UEChMRQ09NT0RPIENBIExpbWl0ZWQxKzApBgNVBAMT
|
||||
IkNPTU9ETyBFQ0MgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMDgwMzA2MDAw
|
||||
MDAwWhcNMzgwMTE4MjM1OTU5WjCBhTELMAkGA1UEBhMCR0IxGzAZBgNVBAgTEkdy
|
||||
ZWF0ZXIgTWFuY2hlc3RlcjEQMA4GA1UEBxMHU2FsZm9yZDEaMBgGA1UEChMRQ09N
|
||||
T0RPIENBIExpbWl0ZWQxKzApBgNVBAMTIkNPTU9ETyBFQ0MgQ2VydGlmaWNhdGlv
|
||||
biBBdXRob3JpdHkwdjAQBgcqhkjOPQIBBgUrgQQAIgNiAAQDR3svdcmCFYX7deSR
|
||||
FtSrYpn1PlILBs5BAH+X4QokPB0BBO490o0JlwzgdeT6+3eKKvUDYEs2ixYjFq0J
|
||||
cfRK9ChQtP6IHG4/bC8vCVlbpVsLM5niwz2J+Wos77LTBumjQjBAMB0GA1UdDgQW
|
||||
BBR1cacZSBm8nZ3qQUfflMRId5nTeTAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/
|
||||
BAUwAwEB/zAKBggqhkjOPQQDAwNoADBlAjEA7wNbeqy3eApyt4jf/7VGFAkK+qDm
|
||||
fQjGGoe9GKhzvSbKYAydzpmfz1wPMOG+FDHqAjAU9JM8SaczepBGR7NjfRObTrdv
|
||||
GDeAU/7dIOA1mjbRxwG55tzd8/8dLDoWV9mSOdY=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF2DCCA8CgAwIBAgIQTKr5yttjb+Af907YWwOGnTANBgkqhkiG9w0BAQwFADCB
|
||||
hTELMAkGA1UEBhMCR0IxGzAZBgNVBAgTEkdyZWF0ZXIgTWFuY2hlc3RlcjEQMA4G
|
||||
A1UEBxMHU2FsZm9yZDEaMBgGA1UEChMRQ09NT0RPIENBIExpbWl0ZWQxKzApBgNV
|
||||
BAMTIkNPTU9ETyBSU0EgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMTAwMTE5
|
||||
MDAwMDAwWhcNMzgwMTE4MjM1OTU5WjCBhTELMAkGA1UEBhMCR0IxGzAZBgNVBAgT
|
||||
EkdyZWF0ZXIgTWFuY2hlc3RlcjEQMA4GA1UEBxMHU2FsZm9yZDEaMBgGA1UEChMR
|
||||
Q09NT0RPIENBIExpbWl0ZWQxKzApBgNVBAMTIkNPTU9ETyBSU0EgQ2VydGlmaWNh
|
||||
dGlvbiBBdXRob3JpdHkwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQCR
|
||||
6FSS0gpWsawNJN3Fz0RndJkrN6N9I3AAcbxT38T6KhKPS38QVr2fcHK3YX/JSw8X
|
||||
pz3jsARh7v8Rl8f0hj4K+j5c+ZPmNHrZFGvnnLOFoIJ6dq9xkNfs/Q36nGz637CC
|
||||
9BR++b7Epi9Pf5l/tfxnQ3K9DADWietrLNPtj5gcFKt+5eNu/Nio5JIk2kNrYrhV
|
||||
/erBvGy2i/MOjZrkm2xpmfh4SDBF1a3hDTxFYPwyllEnvGfDyi62a+pGx8cgoLEf
|
||||
Zd5ICLqkTqnyg0Y3hOvozIFIQ2dOciqbXL1MGyiKXCJ7tKuY2e7gUYPDCUZObT6Z
|
||||
+pUX2nwzV0E8jVHtC7ZcryxjGt9XyD+86V3Em69FmeKjWiS0uqlWPc9vqv9JWL7w
|
||||
qP/0uK3pN/u6uPQLOvnoQ0IeidiEyxPx2bvhiWC4jChWrBQdnArncevPDt09qZah
|
||||
SL0896+1DSJMwBGB7FY79tOi4lu3sgQiUpWAk2nojkxl8ZEDLXB0AuqLZxUpaVIC
|
||||
u9ffUGpVRr+goyhhf3DQw6KqLCGqR84onAZFdr+CGCe01a60y1Dma/RMhnEw6abf
|
||||
Fobg2P9A3fvQQoh/ozM6LlweQRGBY84YcWsr7KaKtzFcOmpH4MN5WdYgGq/yapiq
|
||||
crxXStJLnbsQ/LBMQeXtHT1eKJ2czL+zUdqnR+WEUwIDAQABo0IwQDAdBgNVHQ4E
|
||||
FgQUu69+Aj36pvE8hI6t7jiY7NkyMtQwDgYDVR0PAQH/BAQDAgEGMA8GA1UdEwEB
|
||||
/wQFMAMBAf8wDQYJKoZIhvcNAQEMBQADggIBAArx1UaEt65Ru2yyTUEUAJNMnMvl
|
||||
wFTPoCWOAvn9sKIN9SCYPBMtrFaisNZ+EZLpLrqeLppysb0ZRGxhNaKatBYSaVqM
|
||||
4dc+pBroLwP0rmEdEBsqpIt6xf4FpuHA1sj+nq6PK7o9mfjYcwlYRm6mnPTXJ9OV
|
||||
2jeDchzTc+CiR5kDOF3VSXkAKRzH7JsgHAckaVd4sjn8OoSgtZx8jb8uk2Intzna
|
||||
FxiuvTwJaP+EmzzV1gsD41eeFPfR60/IvYcjt7ZJQ3mFXLrrkguhxuhoqEwWsRqZ
|
||||
CuhTLJK7oQkYdQxlqHvLI7cawiiFwxv/0Cti76R7CZGYZ4wUAc1oBmpjIXUDgIiK
|
||||
boHGhfKppC3n9KUkEEeDys30jXlYsQab5xoq2Z0B15R97QNKyvDb6KkBPvVWmcke
|
||||
jkk9u+UJueBPSZI9FoJAzMxZxuY67RIuaTxslbH9qh17f4a+Hg4yRvv7E491f0yL
|
||||
S0Zj/gA0QHDBw7mh3aZw4gSzQbzpgJHqZJx64SIDqZxubw5lT2yHh17zbqD5daWb
|
||||
QOhTsiedSrnAdyGN/4fy3ryM7xfft0kL0fJuMAsaDk527RH89elWsn2/x20Kk4yl
|
||||
0MC2Hb46TpSi125sC8KKfPog88Tk5c0NqMuRkrF8hey1FGlmDoLnzc7ILaZRfyHB
|
||||
NVOFBkpdn627G190
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDqDCCApCgAwIBAgIJAP7c4wEPyUj/MA0GCSqGSIb3DQEBBQUAMDQxCzAJBgNV
|
||||
BAYTAkZSMRIwEAYDVQQKDAlEaGlteW90aXMxETAPBgNVBAMMCENlcnRpZ25hMB4X
|
||||
DTA3MDYyOTE1MTMwNVoXDTI3MDYyOTE1MTMwNVowNDELMAkGA1UEBhMCRlIxEjAQ
|
||||
BgNVBAoMCURoaW15b3RpczERMA8GA1UEAwwIQ2VydGlnbmEwggEiMA0GCSqGSIb3
|
||||
DQEBAQUAA4IBDwAwggEKAoIBAQDIaPHJ1tazNHUmgh7stL7qXOEm7RFHYeGifBZ4
|
||||
QCHkYJ5ayGPhxLGWkv8YbWkj4Sti993iNi+RB7lIzw7sebYs5zRLcAglozyHGxny
|
||||
gQcPOJAZ0xH+hrTy0V4eHpbNgGzOOzGTtvKg0KmVEn2lmsxryIRWijOp5yIVUxbw
|
||||
zBfsV1/pogqYCd7jX5xv3EjjhQsVWqa6n6xI4wmy9/Qy3l40vhx4XUJbzg4ij02Q
|
||||
130yGLMLLGq/jj8UEYkgDncUtT2UCIf3JR7VsmAA7G8qKCVuKj4YYxclPz5EIBb2
|
||||
JsglrgVKtOdjLPOMFlN+XPsRGgjBRmKfIrjxwo1p3Po6WAbfAgMBAAGjgbwwgbkw
|
||||
DwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUGu3+QTmQtCRZvgHyUtVF9lo53BEw
|
||||
ZAYDVR0jBF0wW4AUGu3+QTmQtCRZvgHyUtVF9lo53BGhOKQ2MDQxCzAJBgNVBAYT
|
||||
AkZSMRIwEAYDVQQKDAlEaGlteW90aXMxETAPBgNVBAMMCENlcnRpZ25hggkA/tzj
|
||||
AQ/JSP8wDgYDVR0PAQH/BAQDAgEGMBEGCWCGSAGG+EIBAQQEAwIABzANBgkqhkiG
|
||||
9w0BAQUFAAOCAQEAhQMeknH2Qq/ho2Ge6/PAD/Kl1NqV5ta+aDY9fm4fTIrv0Q8h
|
||||
bV6lUmPOEvjvKtpv6zf+EwLHyzs+ImvaYS5/1HI93TDhHkxAGYwP15zRgzB7mFnc
|
||||
fca5DClMoTOi62c6ZYTTluLtdkVwj7Ur3vkj1kluPBS1xp81HlDQwY9qcEQCYsuu
|
||||
HWhBp6pX6FOqB9IG9tUUBguRA3UsbHK1YZWaDYu5Def131TN3ubY1gkIl2PlwS6w
|
||||
t0QmwCbAr1UwnjvVNioZBPRcHv/PLLf/0P2HQBHVESO7SMAhqaQoLf0V+LBOK/Qw
|
||||
WyH8EZE0vkHve52Xdf+XlcCWWC/qu0bXu+TZLg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFkjCCA3qgAwIBAgIBATANBgkqhkiG9w0BAQsFADBaMQswCQYDVQQGEwJGUjET
|
||||
MBEGA1UEChMKQ2VydGlub21pczEXMBUGA1UECxMOMDAwMiA0MzM5OTg5MDMxHTAb
|
||||
BgNVBAMTFENlcnRpbm9taXMgLSBSb290IENBMB4XDTEzMTAyMTA5MTcxOFoXDTMz
|
||||
MTAyMTA5MTcxOFowWjELMAkGA1UEBhMCRlIxEzARBgNVBAoTCkNlcnRpbm9taXMx
|
||||
FzAVBgNVBAsTDjAwMDIgNDMzOTk4OTAzMR0wGwYDVQQDExRDZXJ0aW5vbWlzIC0g
|
||||
Um9vdCBDQTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBANTMCQosP5L2
|
||||
fxSeC5yaah1AMGT9qt8OHgZbn1CF6s2Nq0Nn3rD6foCWnoR4kkjW4znuzuRZWJfl
|
||||
LieY6pOod5tK8O90gC3rMB+12ceAnGInkYjwSond3IjmFPnVAy//ldu9n+ws+hQV
|
||||
WZUKxkd8aRi5pwP5ynapz8dvtF4F/u7BUrJ1Mofs7SlmO/NKFoL21prbcpjp3vDF
|
||||
TKWrteoB4owuZH9kb/2jJZOLyKIOSY008B/sWEUuNKqEUL3nskoTuLAPrjhdsKkb
|
||||
5nPJWqHZZkCqqU2mNAKthH6yI8H7KsZn9DS2sJVqM09xRLWtwHkziOC/7aOgFLSc
|
||||
CbAK42C++PhmiM1b8XcF4LVzbsF9Ri6OSyemzTUK/eVNfaoqoynHWmgE6OXWk6Ri
|
||||
wsXm9E/G+Z8ajYJJGYrKWUM66A0ywfRMEwNvbqY/kXPLynNvEiCL7sCCeN5LLsJJ
|
||||
wx3tFvYk9CcbXFcx3FXuqB5vbKziRcxXV4p1VxngtViZSTYxPDMBbRZKzbgqg4SG
|
||||
m/lg0h9tkQPTYKbVPZrdd5A9NaSfD171UkRpucC63M9933zZxKyGIjK8e2uR73r4
|
||||
F2iw4lNVYC2vPsKD2NkJK/DAZNuHi5HMkesE/Xa0lZrmFAYb1TQdvtj/dBxThZng
|
||||
WVJKYe2InmtJiUZ+IFrZ50rlau7SZRFDAgMBAAGjYzBhMA4GA1UdDwEB/wQEAwIB
|
||||
BjAPBgNVHRMBAf8EBTADAQH/MB0GA1UdDgQWBBTvkUz1pcMw6C8I6tNxIqSSaHh0
|
||||
2TAfBgNVHSMEGDAWgBTvkUz1pcMw6C8I6tNxIqSSaHh02TANBgkqhkiG9w0BAQsF
|
||||
AAOCAgEAfj1U2iJdGlg+O1QnurrMyOMaauo++RLrVl89UM7g6kgmJs95Vn6RHJk/
|
||||
0KGRHCwPT5iVWVO90CLYiF2cN/z7ZMF4jIuaYAnq1fohX9B0ZedQxb8uuQsLrbWw
|
||||
F6YSjNRieOpWauwK0kDDPAUwPk2Ut59KA9N9J0u2/kTO+hkzGm2kQtHdzMjI1xZS
|
||||
g081lLMSVX3l4kLr5JyTCcBMWwerx20RoFAXlCOotQqSD7J6wWAsOMwaplv/8gzj
|
||||
qh8c3LigkyfeY+N/IZ865Z764BNqdeuWXGKRlI5nU7aJ+BIJy29SWwNyhlCVCNSN
|
||||
h4YVH5Uk2KRvms6knZtt0rJ2BobGVgjF6wnaNsIbW0G+YSrjcOa4pvi2WsS9Iff/
|
||||
ql+hbHY5ZtbqTFXhADObE5hjyW/QASAJN1LnDE8+zbz1X5YnpyACleAu6AdBBR8V
|
||||
btaw5BngDwKTACdyxYvRVB9dSsNAl35VpnzBMwQUAR1JIGkLGZOdblgi90AMRgwj
|
||||
Y/M50n92Uaf0yKHxDHYiI0ZSKS3io0EHVmmY0gUJvGnHWmHNj4FgFU2A3ZDifcRQ
|
||||
8ow7bkrHxuaAKzyBvBGAFhAn1/DNP3nMcyrDflOR1m749fPH0FFNjkulW+YZFzvW
|
||||
gQncItzujrnEj1PhZ7szuIgVRs/taTX/dQ1G885x4cVrhkIGuUE=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDkjCCAnqgAwIBAgIRAIW9S/PY2uNp9pTXX8OlRCMwDQYJKoZIhvcNAQEFBQAw
|
||||
PTELMAkGA1UEBhMCRlIxETAPBgNVBAoTCENlcnRwbHVzMRswGQYDVQQDExJDbGFz
|
||||
cyAyIFByaW1hcnkgQ0EwHhcNOTkwNzA3MTcwNTAwWhcNMTkwNzA2MjM1OTU5WjA9
|
||||
MQswCQYDVQQGEwJGUjERMA8GA1UEChMIQ2VydHBsdXMxGzAZBgNVBAMTEkNsYXNz
|
||||
IDIgUHJpbWFyeSBDQTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBANxQ
|
||||
ltAS+DXSCHh6tlJw/W/uz7kRy1134ezpfgSN1sxvc0NXYKwzCkTsA18cgCSR5aiR
|
||||
VhKC9+Ar9NuuYS6JEI1rbLqzAr3VNsVINyPi8Fo3UjMXEuLRYE2+L0ER4/YXJQyL
|
||||
kcAbmXuZVg2v7tK8R1fjeUl7NIknJITesezpWE7+Tt9avkGtrAjFGA7v0lPubNCd
|
||||
EgETjdyAYveVqUSISnFOYFWe2yMZeVYHDD9jC1yw4r5+FfyUM1hBOHTE4Y+L3yas
|
||||
H7WLO7dDWWuwJKZtkIvEcupdM5i3y95ee++U8Rs+yskhwcWYAqqi9lt3m/V+llU0
|
||||
HGdpwPFC40es/CgcZlUCAwEAAaOBjDCBiTAPBgNVHRMECDAGAQH/AgEKMAsGA1Ud
|
||||
DwQEAwIBBjAdBgNVHQ4EFgQU43Mt38sOKAze3bOkynm4jrvoMIkwEQYJYIZIAYb4
|
||||
QgEBBAQDAgEGMDcGA1UdHwQwMC4wLKAqoCiGJmh0dHA6Ly93d3cuY2VydHBsdXMu
|
||||
Y29tL0NSTC9jbGFzczIuY3JsMA0GCSqGSIb3DQEBBQUAA4IBAQCnVM+IRBnL39R/
|
||||
AN9WM2K191EBkOvDP9GIROkkXe/nFL0gt5o8AP5tn9uQ3Nf0YtaLcF3n5QRIqWh8
|
||||
yfFC82x/xXp8HVGIutIKPidd3i1RTtMTZGnkLuPT55sJmabglZvOGtd/vjzOUrMR
|
||||
FcEPF80Du5wlFbqidon8BvEY0JNLDnyCt6X09l/+7UCmnYR0ObncHoUW2ikbhiMA
|
||||
ybuJfm6AiB4vFLQDJKgybwOaRywwvlbGp0ICcBvqQNi6BQNwB6SW//1IMwrh3KWB
|
||||
kJtN3X3n57LNXMhqlfil9o3EXXgIvnsG1knPGTZQIy4I5p4FTUcY1Rbpsda2ENW7
|
||||
l7+ijrRU
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDuzCCAqOgAwIBAgIDBETAMA0GCSqGSIb3DQEBBQUAMH4xCzAJBgNVBAYTAlBM
|
||||
MSIwIAYDVQQKExlVbml6ZXRvIFRlY2hub2xvZ2llcyBTLkEuMScwJQYDVQQLEx5D
|
||||
ZXJ0dW0gQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkxIjAgBgNVBAMTGUNlcnR1bSBU
|
||||
cnVzdGVkIE5ldHdvcmsgQ0EwHhcNMDgxMDIyMTIwNzM3WhcNMjkxMjMxMTIwNzM3
|
||||
WjB+MQswCQYDVQQGEwJQTDEiMCAGA1UEChMZVW5pemV0byBUZWNobm9sb2dpZXMg
|
||||
Uy5BLjEnMCUGA1UECxMeQ2VydHVtIENlcnRpZmljYXRpb24gQXV0aG9yaXR5MSIw
|
||||
IAYDVQQDExlDZXJ0dW0gVHJ1c3RlZCBOZXR3b3JrIENBMIIBIjANBgkqhkiG9w0B
|
||||
AQEFAAOCAQ8AMIIBCgKCAQEA4/t9o3K6wvDJFIf1awFO4W5AB7ptJ11/91sts1rH
|
||||
UV+rpDKmYYe2bg+G0jACl/jXaVehGDldamR5xgFZrDwxSjh80gTSSyjoIF87B6LM
|
||||
TXPb865Px1bVWqeWifrzq2jUI4ZZJ88JJ7ysbnKDHDBy3+Ci6dLhdHUZvSqeexVU
|
||||
BBvXQzmtVSjF4hq79MDkrjhJM8x2hZ85RdKknvISjFH4fOQtf/WsX+sWn7Et0brM
|
||||
kUJ3TCXJkDhv2/DM+44el1k+1WBO5gUo7Ul5E0u6SNsv+XLTOcr+H9g0cvW0QM8x
|
||||
AcPs3hEtF10fuFDRXhmnad4HMyjKUJX5p1TLVIZQRan5SQIDAQABo0IwQDAPBgNV
|
||||
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBQIds3LB/8k9sXN7buQvOKEN0Z19zAOBgNV
|
||||
HQ8BAf8EBAMCAQYwDQYJKoZIhvcNAQEFBQADggEBAKaorSLOAT2mo/9i0Eidi15y
|
||||
sHhE49wcrwn9I0j6vSrEuVUEtRCjjSfeC4Jj0O7eDDd5QVsisrCaQVymcODU0HfL
|
||||
I9MA4GxWL+FpDQ3Zqr8hgVDZBqWo/5U30Kr+4rP1mS1FhIrlQgnXdAIv94nYmem8
|
||||
J9RHjboNRhx3zxSkHLmkMcScKHQDNP8zGSal6Q10tz6XxnboJ5ajZt3hrvJBW8qY
|
||||
VoNzcOSGGtIxQbovvi0TWnZvTuhOgQ4/WwMioBK+ZlgRSssDxLQqKi2WF+A5VLxI
|
||||
03YnnZotBqbJ7DnSq9ufmgsnAjUpsUCV5/nonFWIGUbWtzT1fs45mtk48VH3Tyw=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF0jCCA7qgAwIBAgIQIdbQSk8lD8kyN/yqXhKN6TANBgkqhkiG9w0BAQ0FADCB
|
||||
gDELMAkGA1UEBhMCUEwxIjAgBgNVBAoTGVVuaXpldG8gVGVjaG5vbG9naWVzIFMu
|
||||
QS4xJzAlBgNVBAsTHkNlcnR1bSBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTEkMCIG
|
||||
A1UEAxMbQ2VydHVtIFRydXN0ZWQgTmV0d29yayBDQSAyMCIYDzIwMTExMDA2MDgz
|
||||
OTU2WhgPMjA0NjEwMDYwODM5NTZaMIGAMQswCQYDVQQGEwJQTDEiMCAGA1UEChMZ
|
||||
VW5pemV0byBUZWNobm9sb2dpZXMgUy5BLjEnMCUGA1UECxMeQ2VydHVtIENlcnRp
|
||||
ZmljYXRpb24gQXV0aG9yaXR5MSQwIgYDVQQDExtDZXJ0dW0gVHJ1c3RlZCBOZXR3
|
||||
b3JrIENBIDIwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQC9+Xj45tWA
|
||||
DGSdhhuWZGc/IjoedQF97/tcZ4zJzFxrqZHmuULlIEub2pt7uZld2ZuAS9eEQCsn
|
||||
0+i6MLs+CRqnSZXvK0AkwpfHp+6bJe+oCgCXhVqqndwpyeI1B+twTUrWwbNWuKFB
|
||||
OJvR+zF/j+Bf4bE/D44WSWDXBo0Y+aomEKsq09DRZ40bRr5HMNUuctHFY9rnY3lE
|
||||
fktjJImGLjQ/KUxSiyqnwOKRKIm5wFv5HdnnJ63/mgKXwcZQkpsCLL2puTRZCr+E
|
||||
Sv/f/rOf69me4Jgj7KZrdxYq28ytOxykh9xGc14ZYmhFV+SQgkK7QtbwYeDBoz1m
|
||||
o130GO6IyY0XRSmZMnUCMe4pJshrAua1YkV/NxVaI2iJ1D7eTiew8EAMvE0Xy02i
|
||||
sx7QBlrd9pPPV3WZ9fqGGmd4s7+W/jTcvedSVuWz5XV710GRBdxdaeOVDUO5/IOW
|
||||
OZV7bIBaTxNyxtd9KXpEulKkKtVBRgkg/iKgtlswjbyJDNXXcPiHUv3a76xRLgez
|
||||
Tv7QCdpw75j6VuZt27VXS9zlLCUVyJ4ueE742pyehizKV/Ma5ciSixqClnrDvFAS
|
||||
adgOWkaLOusm+iPJtrCBvkIApPjW/jAux9JG9uWOdf3yzLnQh1vMBhBgu4M1t15n
|
||||
3kfsmUjxpKEV/q2MYo45VU85FrmxY53/twIDAQABo0IwQDAPBgNVHRMBAf8EBTAD
|
||||
AQH/MB0GA1UdDgQWBBS2oVQ5AsOgP46KvPrU+Bym0ToO/TAOBgNVHQ8BAf8EBAMC
|
||||
AQYwDQYJKoZIhvcNAQENBQADggIBAHGlDs7k6b8/ONWJWsQCYftMxRQXLYtPU2sQ
|
||||
F/xlhMcQSZDe28cmk4gmb3DWAl45oPePq5a1pRNcgRRtDoGCERuKTsZPpd1iHkTf
|
||||
CVn0W3cLN+mLIMb4Ck4uWBzrM9DPhmDJ2vuAL55MYIR4PSFk1vtBHxgP58l1cb29
|
||||
XN40hz5BsA72udY/CROWFC/emh1auVbONTqwX3BNXuMp8SMoclm2q8KMZiYcdywm
|
||||
djWLKKdpoPk79SPdhRB0yZADVpHnr7pH1BKXESLjokmUbOe3lEu6LaTaM4tMpkT/
|
||||
WjzGHWTYtTHkpjx6qFcL2+1hGsvxznN3Y6SHb0xRONbkX8eftoEq5IVIeVheO/jb
|
||||
AoJnwTnbw3RLPTYe+SmTiGhbqEQZIfCn6IENLOiTNrQ3ssqwGyZ6miUfmpqAnksq
|
||||
P/ujmv5zMnHCnsZy4YpoJ/HkD7TETKVhk/iXEAcqMCWpuchxuO9ozC1+9eB+D4Ko
|
||||
b7a6bINDd82Kkhehnlt4Fj1F4jNy3eFmypnTycUm/Q1oBEauttmbjL4ZvrHG8hnj
|
||||
XALKLNhvSgfZyTXaQHXyxKcZb55CEJh15pWLYLztxRLXis7VmFxWlgPF7ncGNf/P
|
||||
5O4/E2Hu29othfDNrp2yGAlFw5Khchf8R7agCyzxxN5DaAhqXzvwdmP7zAYspsbi
|
||||
DrW5viSP
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIHTzCCBTegAwIBAgIJAKPaQn6ksa7aMA0GCSqGSIb3DQEBBQUAMIGuMQswCQYD
|
||||
VQQGEwJFVTFDMEEGA1UEBxM6TWFkcmlkIChzZWUgY3VycmVudCBhZGRyZXNzIGF0
|
||||
IHd3dy5jYW1lcmZpcm1hLmNvbS9hZGRyZXNzKTESMBAGA1UEBRMJQTgyNzQzMjg3
|
||||
MRswGQYDVQQKExJBQyBDYW1lcmZpcm1hIFMuQS4xKTAnBgNVBAMTIENoYW1iZXJz
|
||||
IG9mIENvbW1lcmNlIFJvb3QgLSAyMDA4MB4XDTA4MDgwMTEyMjk1MFoXDTM4MDcz
|
||||
MTEyMjk1MFowga4xCzAJBgNVBAYTAkVVMUMwQQYDVQQHEzpNYWRyaWQgKHNlZSBj
|
||||
dXJyZW50IGFkZHJlc3MgYXQgd3d3LmNhbWVyZmlybWEuY29tL2FkZHJlc3MpMRIw
|
||||
EAYDVQQFEwlBODI3NDMyODcxGzAZBgNVBAoTEkFDIENhbWVyZmlybWEgUy5BLjEp
|
||||
MCcGA1UEAxMgQ2hhbWJlcnMgb2YgQ29tbWVyY2UgUm9vdCAtIDIwMDgwggIiMA0G
|
||||
CSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQCvAMtwNyuAWko6bHiUfaN/Gh/2NdW9
|
||||
28sNRHI+JrKQUrpjOyhYb6WzbZSm891kDFX29ufyIiKAXuFixrYp4YFs8r/lfTJq
|
||||
VKAyGVn+H4vXPWCGhSRv4xGzdz4gljUha7MI2XAuZPeEklPWDrCQiorjh40G072Q
|
||||
DuKZoRuGDtqaCrsLYVAGUvGef3bsyw/QHg3PmTA9HMRFEFis1tPo1+XqxQEHd9ZR
|
||||
5gN/ikilTWh1uem8nk4ZcfUyS5xtYBkL+8ydddy/Js2Pk3g5eXNeJQ7KXOt3EgfL
|
||||
ZEFHcpOrUMPrCXZkNNI5t3YRCQ12RcSprj1qr7V9ZS+UWBDsXHyvfuK2GNnQm05a
|
||||
Sd+pZgvMPMZ4fKecHePOjlO+Bd5gD2vlGts/4+EhySnB8esHnFIbAURRPHsl18Tl
|
||||
UlRdJQfKFiC4reRB7noI/plvg6aRArBsNlVq5331lubKgdaX8ZSD6e2wsWsSaR6s
|
||||
+12pxZjptFtYer49okQ6Y1nUCyXeG0+95QGezdIp1Z8XGQpvvwyQ0wlf2eOKNcx5
|
||||
Wk0ZN5K3xMGtr/R5JJqyAQuxr1yW84Ay+1w9mPGgP0revq+ULtlVmhduYJ1jbLhj
|
||||
ya6BXBg14JC7vjxPNyK5fuvPnnchpj04gftI2jE9K+OJ9dC1vX7gUMQSibMjmhAx
|
||||
hduub+84Mxh2EQIDAQABo4IBbDCCAWgwEgYDVR0TAQH/BAgwBgEB/wIBDDAdBgNV
|
||||
HQ4EFgQU+SSsD7K1+HnA+mCIG8TZTQKeFxkwgeMGA1UdIwSB2zCB2IAU+SSsD7K1
|
||||
+HnA+mCIG8TZTQKeFxmhgbSkgbEwga4xCzAJBgNVBAYTAkVVMUMwQQYDVQQHEzpN
|
||||
YWRyaWQgKHNlZSBjdXJyZW50IGFkZHJlc3MgYXQgd3d3LmNhbWVyZmlybWEuY29t
|
||||
L2FkZHJlc3MpMRIwEAYDVQQFEwlBODI3NDMyODcxGzAZBgNVBAoTEkFDIENhbWVy
|
||||
ZmlybWEgUy5BLjEpMCcGA1UEAxMgQ2hhbWJlcnMgb2YgQ29tbWVyY2UgUm9vdCAt
|
||||
IDIwMDiCCQCj2kJ+pLGu2jAOBgNVHQ8BAf8EBAMCAQYwPQYDVR0gBDYwNDAyBgRV
|
||||
HSAAMCowKAYIKwYBBQUHAgEWHGh0dHA6Ly9wb2xpY3kuY2FtZXJmaXJtYS5jb20w
|
||||
DQYJKoZIhvcNAQEFBQADggIBAJASryI1wqM58C7e6bXpeHxIvj99RZJe6dqxGfwW
|
||||
PJ+0W2aeaufDuV2I6A+tzyMP3iU6XsxPpcG1Lawk0lgH3qLPaYRgM+gQDROpI9CF
|
||||
5Y57pp49chNyM/WqfcZjHwj0/gF/JM8rLFQJ3uIrbZLGOU8W6jx+ekbURWpGqOt1
|
||||
glanq6B8aBMz9p0w8G8nOSQjKpD9kCk18pPfNKXG9/jvjA9iSnyu0/VU+I22mlaH
|
||||
FoI6M6taIgj3grrqLuBHmrS1RaMFO9ncLkVAO+rcf+g769HsJtg1pDDFOqxXnrN2
|
||||
pSB7+R5KBWIBpih1YJeSDW4+TTdDDZIVnBgizVGZoCkaPF+KMjNbMMeJL0eYD6MD
|
||||
xvbxrN8y8NmBGuScvfaAFPDRLLmF9dijscilIeUcE5fuDr3fKanvNFNb0+RqE4QG
|
||||
tjICxFKuItLcsiFCGtpA8CnJ7AoMXOLQusxI0zcKzBIKinmwPQN/aUv0NCB9szTq
|
||||
jktk9T79syNnFQ0EuPAtwQlRPLJsFfClI9eDdOTlLsn+mCdCxqvGnrDQWzilm1De
|
||||
fhiYtUU79nm06PcaewaD+9CL2rvHvRirCG88gGtAPxkZumWK5r7VXNM21+9AUiRg
|
||||
OGcEMeyP84LG3rlV8zsxkVrctQgVrXYlCg17LofiDKYGvCYQbTed7N14jHyAxfDZ
|
||||
d0jQ
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEMjCCAxqgAwIBAgIBATANBgkqhkiG9w0BAQUFADB7MQswCQYDVQQGEwJHQjEb
|
||||
MBkGA1UECAwSR3JlYXRlciBNYW5jaGVzdGVyMRAwDgYDVQQHDAdTYWxmb3JkMRow
|
||||
GAYDVQQKDBFDb21vZG8gQ0EgTGltaXRlZDEhMB8GA1UEAwwYQUFBIENlcnRpZmlj
|
||||
YXRlIFNlcnZpY2VzMB4XDTA0MDEwMTAwMDAwMFoXDTI4MTIzMTIzNTk1OVowezEL
|
||||
MAkGA1UEBhMCR0IxGzAZBgNVBAgMEkdyZWF0ZXIgTWFuY2hlc3RlcjEQMA4GA1UE
|
||||
BwwHU2FsZm9yZDEaMBgGA1UECgwRQ29tb2RvIENBIExpbWl0ZWQxITAfBgNVBAMM
|
||||
GEFBQSBDZXJ0aWZpY2F0ZSBTZXJ2aWNlczCCASIwDQYJKoZIhvcNAQEBBQADggEP
|
||||
ADCCAQoCggEBAL5AnfRu4ep2hxxNRUSOvkbIgwadwSr+GB+O5AL686tdUIoWMQua
|
||||
BtDFcCLNSS1UY8y2bmhGC1Pqy0wkwLxyTurxFa70VJoSCsN6sjNg4tqJVfMiWPPe
|
||||
3M/vg4aijJRPn2jymJBGhCfHdr/jzDUsi14HZGWCwEiwqJH5YZ92IFCokcdmtet4
|
||||
YgNW8IoaE+oxox6gmf049vYnMlhvB/VruPsUK6+3qszWY19zjNoFmag4qMsXeDZR
|
||||
rOme9Hg6jc8P2ULimAyrL58OAd7vn5lJ8S3frHRNG5i1R8XlKdH5kBjHYpy+g8cm
|
||||
ez6KJcfA3Z3mNWgQIJ2P2N7Sw4ScDV7oL8kCAwEAAaOBwDCBvTAdBgNVHQ4EFgQU
|
||||
oBEKIz6W8Qfs4q8p74Klf9AwpLQwDgYDVR0PAQH/BAQDAgEGMA8GA1UdEwEB/wQF
|
||||
MAMBAf8wewYDVR0fBHQwcjA4oDagNIYyaHR0cDovL2NybC5jb21vZG9jYS5jb20v
|
||||
QUFBQ2VydGlmaWNhdGVTZXJ2aWNlcy5jcmwwNqA0oDKGMGh0dHA6Ly9jcmwuY29t
|
||||
b2RvLm5ldC9BQUFDZXJ0aWZpY2F0ZVNlcnZpY2VzLmNybDANBgkqhkiG9w0BAQUF
|
||||
AAOCAQEACFb8AvCb6P+k+tZ7xkSAzk/ExfYAWMymtrwUSWgEdujm7l3sAg9g1o1Q
|
||||
GE8mTgHj5rCl7r+8dFRBv/38ErjHT1r0iWAFf2C3BUrz9vHCv8S5dIa2LX1rzNLz
|
||||
Rt0vxuBqw8M0Ayx9lt1awg6nCpnBBYurDC/zXDrPbDdVCYfeU0BsWO/8tqtlbgT2
|
||||
G9w84FoVxp7Z8VlIMCFlA2zs6SFz7JsDoeA3raAVGI/6ugLOpyypEBMs1OUIJqsi
|
||||
l2D4kF501KKaU73yqWjgom7C12yxow+ev+to51byrvLjKzg6CYG1a4XXvi3tPxq3
|
||||
smPi9WIsgtRqAEFQ8TmDn5XpNpaYbg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDoTCCAomgAwIBAgILBAAAAAABD4WqLUgwDQYJKoZIhvcNAQEFBQAwOzEYMBYG
|
||||
A1UEChMPQ3liZXJ0cnVzdCwgSW5jMR8wHQYDVQQDExZDeWJlcnRydXN0IEdsb2Jh
|
||||
bCBSb290MB4XDTA2MTIxNTA4MDAwMFoXDTIxMTIxNTA4MDAwMFowOzEYMBYGA1UE
|
||||
ChMPQ3liZXJ0cnVzdCwgSW5jMR8wHQYDVQQDExZDeWJlcnRydXN0IEdsb2JhbCBS
|
||||
b290MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA+Mi8vRRQZhP/8NN5
|
||||
7CPytxrHjoXxEnOmGaoQ25yiZXRadz5RfVb23CO21O1fWLE3TdVJDm71aofW0ozS
|
||||
J8bi/zafmGWgE07GKmSb1ZASzxQG9Dvj1Ci+6A74q05IlG2OlTEQXO2iLb3VOm2y
|
||||
HLtgwEZLAfVJrn5GitB0jaEMAs7u/OePuGtm839EAL9mJRQr3RAwHQeWP032a7iP
|
||||
t3sMpTjr3kfb1V05/Iin89cqdPHoWqI7n1C6poxFNcJQZZXcY4Lv3b93TZxiyWNz
|
||||
FtApD0mpSPCzqrdsxacwOUBdrsTiXSZT8M4cIwhhqJQZugRiQOwfOHB3EgZxpzAY
|
||||
XSUnpQIDAQABo4GlMIGiMA4GA1UdDwEB/wQEAwIBBjAPBgNVHRMBAf8EBTADAQH/
|
||||
MB0GA1UdDgQWBBS2CHsNesysIEyGVjJez6tuhS1wVzA/BgNVHR8EODA2MDSgMqAw
|
||||
hi5odHRwOi8vd3d3Mi5wdWJsaWMtdHJ1c3QuY29tL2NybC9jdC9jdHJvb3QuY3Js
|
||||
MB8GA1UdIwQYMBaAFLYIew16zKwgTIZWMl7Pq26FLXBXMA0GCSqGSIb3DQEBBQUA
|
||||
A4IBAQBW7wojoFROlZfJ+InaRcHUowAl9B8Tq7ejhVhpwjCt2BWKLePJzYFa+HMj
|
||||
Wqd8BfP9IjsO0QbE2zZMcwSO5bAi5MXzLqXZI+O4Tkogp24CJJ8iYGd7ix1yCcUx
|
||||
XOl5n4BHPa2hCwcUPUf/A2kaDAtE52Mlp3+yybh2hO0j9n0Hq0V+09+zv+mKts2o
|
||||
omcrUtW3ZfA5TGOgkXmTUg9U3YO7n9GPp1Nzw8v/MOx8BLjYRB+TX3EJIrduPuoc
|
||||
A06dGiBh+4E37F78CkWr1+cXVdCg6mCbpvbjjFspwgZgFJ0tl0ypkxWdYcQBX0jW
|
||||
WL1WMRJOEcgh4LMRkWXbtKaIOM5V
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEMzCCAxugAwIBAgIDCYPzMA0GCSqGSIb3DQEBCwUAME0xCzAJBgNVBAYTAkRF
|
||||
MRUwEwYDVQQKDAxELVRydXN0IEdtYkgxJzAlBgNVBAMMHkQtVFJVU1QgUm9vdCBD
|
||||
bGFzcyAzIENBIDIgMjAwOTAeFw0wOTExMDUwODM1NThaFw0yOTExMDUwODM1NTha
|
||||
ME0xCzAJBgNVBAYTAkRFMRUwEwYDVQQKDAxELVRydXN0IEdtYkgxJzAlBgNVBAMM
|
||||
HkQtVFJVU1QgUm9vdCBDbGFzcyAzIENBIDIgMjAwOTCCASIwDQYJKoZIhvcNAQEB
|
||||
BQADggEPADCCAQoCggEBANOySs96R+91myP6Oi/WUEWJNTrGa9v+2wBoqOADER03
|
||||
UAifTUpolDWzU9GUY6cgVq/eUXjsKj3zSEhQPgrfRlWLJ23DEE0NkVJD2IfgXU42
|
||||
tSHKXzlABF9bfsyjxiupQB7ZNoTWSPOSHjRGICTBpFGOShrvUD9pXRl/RcPHAY9R
|
||||
ySPocq60vFYJfxLLHLGvKZAKyVXMD9O0Gu1HNVpK7ZxzBCHQqr0ME7UAyiZsxGsM
|
||||
lFqVlNpQmvH/pStmMaTJOKDfHR+4CS7zp+hnUquVH+BGPtikw8paxTGA6Eian5Rp
|
||||
/hnd2HN8gcqW3o7tszIFZYQ05ub9VxC1X3a/L7AQDcUCAwEAAaOCARowggEWMA8G
|
||||
A1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFP3aFMSfMN4hvR5COfyrYyNJ4PGEMA4G
|
||||
A1UdDwEB/wQEAwIBBjCB0wYDVR0fBIHLMIHIMIGAoH6gfIZ6bGRhcDovL2RpcmVj
|
||||
dG9yeS5kLXRydXN0Lm5ldC9DTj1ELVRSVVNUJTIwUm9vdCUyMENsYXNzJTIwMyUy
|
||||
MENBJTIwMiUyMDIwMDksTz1ELVRydXN0JTIwR21iSCxDPURFP2NlcnRpZmljYXRl
|
||||
cmV2b2NhdGlvbmxpc3QwQ6BBoD+GPWh0dHA6Ly93d3cuZC10cnVzdC5uZXQvY3Js
|
||||
L2QtdHJ1c3Rfcm9vdF9jbGFzc18zX2NhXzJfMjAwOS5jcmwwDQYJKoZIhvcNAQEL
|
||||
BQADggEBAH+X2zDI36ScfSF6gHDOFBJpiBSVYEQBrLLpME+bUMJm2H6NMLVwMeni
|
||||
acfzcNsgFYbQDfC+rAF1hM5+n02/t2A7nPPKHeJeaNijnZflQGDSNiH+0LS4F9p0
|
||||
o3/U37CYAqxva2ssJSRyoWXuJVrl5jLn8t+rSfrzkGkj2wTZ51xY/GXUl77M/C4K
|
||||
zCUqNQT4YJEVdT1B/yMfGchs64JTBKbkTCJNjYy6zltz7GRUUG3RnFX7acM2w4y8
|
||||
PIWmawomDeCTmGCufsYkl4phX5GOZpIJhzbNi5stPvZR1FDUWSi9g/LMKHtThm3Y
|
||||
Johw1+qRzT65ysCQblrGXnRl11z+o+I=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEQzCCAyugAwIBAgIDCYP0MA0GCSqGSIb3DQEBCwUAMFAxCzAJBgNVBAYTAkRF
|
||||
MRUwEwYDVQQKDAxELVRydXN0IEdtYkgxKjAoBgNVBAMMIUQtVFJVU1QgUm9vdCBD
|
||||
bGFzcyAzIENBIDIgRVYgMjAwOTAeFw0wOTExMDUwODUwNDZaFw0yOTExMDUwODUw
|
||||
NDZaMFAxCzAJBgNVBAYTAkRFMRUwEwYDVQQKDAxELVRydXN0IEdtYkgxKjAoBgNV
|
||||
BAMMIUQtVFJVU1QgUm9vdCBDbGFzcyAzIENBIDIgRVYgMjAwOTCCASIwDQYJKoZI
|
||||
hvcNAQEBBQADggEPADCCAQoCggEBAJnxhDRwui+3MKCOvXwEz75ivJn9gpfSegpn
|
||||
ljgJ9hBOlSJzmY3aFS3nBfwZcyK3jpgAvDw9rKFs+9Z5JUut8Mxk2og+KbgPCdM0
|
||||
3TP1YtHhzRnp7hhPTFiu4h7WDFsVWtg6uMQYZB7jM7K1iXdODL/ZlGsTl28So/6Z
|
||||
qQTMFexgaDbtCHu39b+T7WYxg4zGcTSHThfqr4uRjRxWQa4iN1438h3Z0S0NL2lR
|
||||
p75mpoo6Kr3HGrHhFPC+Oh25z1uxav60sUYgovseO3Dvk5h9jHOW8sXvhXCtKSb8
|
||||
HgQ+HKDYD8tSg2J87otTlZCpV6LqYQXY+U3EJ/pure3511H3a6UCAwEAAaOCASQw
|
||||
ggEgMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFNOUikxiEyoZLsyvcop9Ntea
|
||||
HNxnMA4GA1UdDwEB/wQEAwIBBjCB3QYDVR0fBIHVMIHSMIGHoIGEoIGBhn9sZGFw
|
||||
Oi8vZGlyZWN0b3J5LmQtdHJ1c3QubmV0L0NOPUQtVFJVU1QlMjBSb290JTIwQ2xh
|
||||
c3MlMjAzJTIwQ0ElMjAyJTIwRVYlMjAyMDA5LE89RC1UcnVzdCUyMEdtYkgsQz1E
|
||||
RT9jZXJ0aWZpY2F0ZXJldm9jYXRpb25saXN0MEagRKBChkBodHRwOi8vd3d3LmQt
|
||||
dHJ1c3QubmV0L2NybC9kLXRydXN0X3Jvb3RfY2xhc3NfM19jYV8yX2V2XzIwMDku
|
||||
Y3JsMA0GCSqGSIb3DQEBCwUAA4IBAQA07XtaPKSUiO8aEXUHL7P+PPoeUSbrh/Yp
|
||||
3uDx1MYkCenBz1UbtDDZzhr+BlGmFaQt77JLvyAoJUnRpjZ3NOhk31KxEcdzes05
|
||||
nsKtjHEh8lprr988TlWvsoRlFIm5d8sqMb7Po23Pb0iUMkZv53GMoKaEGTcH8gNF
|
||||
CSuGdXzfX2lXANtu2KZyIktQ1HWYVt+3GP9DQ1CuekR78HlR10M9p9OB0/DJT7na
|
||||
xpeG0ILD5EJt/rDiZE4OJudANCa1CInXCGNjOCd1HjPqbqjdn5lPdE2BiYBL3ZqX
|
||||
KVwvvoFBuYz/6n1gBp7N1z3TLqMVvKjmJuVvw9y4AyHqnxbxLFS1
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDSjCCAjKgAwIBAgIQRK+wgNajJ7qJMDmGLvhAazANBgkqhkiG9w0BAQUFADA/
|
||||
MSQwIgYDVQQKExtEaWdpdGFsIFNpZ25hdHVyZSBUcnVzdCBDby4xFzAVBgNVBAMT
|
||||
DkRTVCBSb290IENBIFgzMB4XDTAwMDkzMDIxMTIxOVoXDTIxMDkzMDE0MDExNVow
|
||||
PzEkMCIGA1UEChMbRGlnaXRhbCBTaWduYXR1cmUgVHJ1c3QgQ28uMRcwFQYDVQQD
|
||||
Ew5EU1QgUm9vdCBDQSBYMzCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEB
|
||||
AN+v6ZdQCINXtMxiZfaQguzH0yxrMMpb7NnDfcdAwRgUi+DoM3ZJKuM/IUmTrE4O
|
||||
rz5Iy2Xu/NMhD2XSKtkyj4zl93ewEnu1lcCJo6m67XMuegwGMoOifooUMM0RoOEq
|
||||
OLl5CjH9UL2AZd+3UWODyOKIYepLYYHsUmu5ouJLGiifSKOeDNoJjj4XLh7dIN9b
|
||||
xiqKqy69cK3FCxolkHRyxXtqqzTWMIn/5WgTe1QLyNau7Fqckh49ZLOMxt+/yUFw
|
||||
7BZy1SbsOFU5Q9D8/RhcQPGX69Wam40dutolucbY38EVAjqr2m7xPi71XAicPNaD
|
||||
aeQQmxkqtilX4+U9m5/wAl0CAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNV
|
||||
HQ8BAf8EBAMCAQYwHQYDVR0OBBYEFMSnsaR7LHH62+FLkHX/xBVghYkQMA0GCSqG
|
||||
SIb3DQEBBQUAA4IBAQCjGiybFwBcqR7uKGY3Or+Dxz9LwwmglSBd49lZRNI+DT69
|
||||
ikugdB/OEIKcdBodfpga3csTS7MgROSR6cz8faXbauX+5v3gTt23ADq1cEmv8uXr
|
||||
AvHRAosZy5Q6XkjEGB5YGV8eAlrwDPGxrancWYaLbumR9YbK+rlmM6pZW87ipxZz
|
||||
R8srzJmwN0jP41ZL9c8PDHIyh8bwRLtTcm1D9SZImlJnt1ir/md2cXjbDaJWFBM5
|
||||
JDGFoqgCWjBH4d1QB7wCCZAA62RjYJsWvIjJEubSfZGL+T0yjWW06XyxV3bqxbYo
|
||||
Ob8VZRzI9neWagqNdwvYkQsEjgfbKbYK7p2CNTUQ
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDnzCCAoegAwIBAgIBJjANBgkqhkiG9w0BAQUFADBxMQswCQYDVQQGEwJERTEc
|
||||
MBoGA1UEChMTRGV1dHNjaGUgVGVsZWtvbSBBRzEfMB0GA1UECxMWVC1UZWxlU2Vj
|
||||
IFRydXN0IENlbnRlcjEjMCEGA1UEAxMaRGV1dHNjaGUgVGVsZWtvbSBSb290IENB
|
||||
IDIwHhcNOTkwNzA5MTIxMTAwWhcNMTkwNzA5MjM1OTAwWjBxMQswCQYDVQQGEwJE
|
||||
RTEcMBoGA1UEChMTRGV1dHNjaGUgVGVsZWtvbSBBRzEfMB0GA1UECxMWVC1UZWxl
|
||||
U2VjIFRydXN0IENlbnRlcjEjMCEGA1UEAxMaRGV1dHNjaGUgVGVsZWtvbSBSb290
|
||||
IENBIDIwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCrC6M14IspFLEU
|
||||
ha88EOQ5bzVdSq7d6mGNlUn0b2SjGmBmpKlAIoTZ1KXleJMOaAGtuU1cOs7TuKhC
|
||||
QN/Po7qCWWqSG6wcmtoIKyUn+WkjR/Hg6yx6m/UTAtB+NHzCnjwAWav12gz1Mjwr
|
||||
rFDa1sPeg5TKqAyZMg4ISFZbavva4VhYAUlfckE8FQYBjl2tqriTtM2e66foai1S
|
||||
NNs671x1Udrb8zH57nGYMsRUFUQM+ZtV7a3fGAigo4aKSe5TBY8ZTNXeWHmb0moc
|
||||
QqvF1afPaA+W5OFhmHZhyJF81j4A4pFQh+GdCuatl9Idxjp9y7zaAzTVjlsB9WoH
|
||||
txa2bkp/AgMBAAGjQjBAMB0GA1UdDgQWBBQxw3kbuvVT1xfgiXotF2wKsyudMzAP
|
||||
BgNVHRMECDAGAQH/AgEFMA4GA1UdDwEB/wQEAwIBBjANBgkqhkiG9w0BAQUFAAOC
|
||||
AQEAlGRZrTlk5ynrE/5aw4sTV8gEJPB0d8Bg42f76Ymmg7+Wgnxu1MM9756Abrsp
|
||||
tJh6sTtU6zkXR34ajgv8HzFZMQSyzhfzLMdiNlXiItiJVbSYSKpk+tYcNthEeFpa
|
||||
IzpXl/V6ME+un2pMSyuOoAPjPuCp1NJ70rOo4nI8rZ7/gFnkm0W09juwzTkZmDLl
|
||||
6iFhkOQxIY40sfcvNUqFENrnijchvllj4PKFiDFT1FQUhXB59C4Gdyd1Lx+4ivn+
|
||||
xbrYNuSD7Odlt79jWvNGr4GUN9RBjNYj1h7P9WgbRGOiWrqnNVmh5XAFmw4jV5mU
|
||||
Cm26OWMohpLzGITY+9HPBVZkVw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDtzCCAp+gAwIBAgIQDOfg5RfYRv6P5WD8G/AwOTANBgkqhkiG9w0BAQUFADBl
|
||||
MQswCQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3
|
||||
d3cuZGlnaWNlcnQuY29tMSQwIgYDVQQDExtEaWdpQ2VydCBBc3N1cmVkIElEIFJv
|
||||
b3QgQ0EwHhcNMDYxMTEwMDAwMDAwWhcNMzExMTEwMDAwMDAwWjBlMQswCQYDVQQG
|
||||
EwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3d3cuZGlnaWNl
|
||||
cnQuY29tMSQwIgYDVQQDExtEaWdpQ2VydCBBc3N1cmVkIElEIFJvb3QgQ0EwggEi
|
||||
MA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCtDhXO5EOAXLGH87dg+XESpa7c
|
||||
JpSIqvTO9SA5KFhgDPiA2qkVlTJhPLWxKISKityfCgyDF3qPkKyK53lTXDGEKvYP
|
||||
mDI2dsze3Tyoou9q+yHyUmHfnyDXH+Kx2f4YZNISW1/5WBg1vEfNoTb5a3/UsDg+
|
||||
wRvDjDPZ2C8Y/igPs6eD1sNuRMBhNZYW/lmci3Zt1/GiSw0r/wty2p5g0I6QNcZ4
|
||||
VYcgoc/lbQrISXwxmDNsIumH0DJaoroTghHtORedmTpyoeb6pNnVFzF1roV9Iq4/
|
||||
AUaG9ih5yLHa5FcXxH4cDrC0kqZWs72yl+2qp/C3xag/lRbQ/6GW6whfGHdPAgMB
|
||||
AAGjYzBhMA4GA1UdDwEB/wQEAwIBhjAPBgNVHRMBAf8EBTADAQH/MB0GA1UdDgQW
|
||||
BBRF66Kv9JLLgjEtUYunpyGd823IDzAfBgNVHSMEGDAWgBRF66Kv9JLLgjEtUYun
|
||||
pyGd823IDzANBgkqhkiG9w0BAQUFAAOCAQEAog683+Lt8ONyc3pklL/3cmbYMuRC
|
||||
dWKuh+vy1dneVrOfzM4UKLkNl2BcEkxY5NM9g0lFWJc1aRqoR+pWxnmrEthngYTf
|
||||
fwk8lOa4JiwgvT2zKIn3X/8i4peEH+ll74fg38FnSbNd67IJKusm7Xi+fT8r87cm
|
||||
NW1fiQG2SVufAQWbqz0lwcy2f8Lxb4bG+mRo64EtlOtCt/qMHt1i8b5QZ7dsvfPx
|
||||
H2sMNgcWfzd8qVttevESRmCD1ycEvkvOl77DZypoEd+A5wwzZr8TDRRu838fYxAe
|
||||
+o0bJW1sj6W3YQGx0qMmoRBxna3iw/nDmVG3KwcIzi7mULKn+gpFL6Lw8g==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDljCCAn6gAwIBAgIQC5McOtY5Z+pnI7/Dr5r0SzANBgkqhkiG9w0BAQsFADBl
|
||||
MQswCQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3
|
||||
d3cuZGlnaWNlcnQuY29tMSQwIgYDVQQDExtEaWdpQ2VydCBBc3N1cmVkIElEIFJv
|
||||
b3QgRzIwHhcNMTMwODAxMTIwMDAwWhcNMzgwMTE1MTIwMDAwWjBlMQswCQYDVQQG
|
||||
EwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3d3cuZGlnaWNl
|
||||
cnQuY29tMSQwIgYDVQQDExtEaWdpQ2VydCBBc3N1cmVkIElEIFJvb3QgRzIwggEi
|
||||
MA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQDZ5ygvUj82ckmIkzTz+GoeMVSA
|
||||
n61UQbVH35ao1K+ALbkKz3X9iaV9JPrjIgwrvJUXCzO/GU1BBpAAvQxNEP4Htecc
|
||||
biJVMWWXvdMX0h5i89vqbFCMP4QMls+3ywPgym2hFEwbid3tALBSfK+RbLE4E9Hp
|
||||
EgjAALAcKxHad3A2m67OeYfcgnDmCXRwVWmvo2ifv922ebPynXApVfSr/5Vh88lA
|
||||
bx3RvpO704gqu52/clpWcTs/1PPRCv4o76Pu2ZmvA9OPYLfykqGxvYmJHzDNw6Yu
|
||||
YjOuFgJ3RFrngQo8p0Quebg/BLxcoIfhG69Rjs3sLPr4/m3wOnyqi+RnlTGNAgMB
|
||||
AAGjQjBAMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgGGMB0GA1UdDgQW
|
||||
BBTOw0q5mVXyuNtgv6l+vVa1lzan1jANBgkqhkiG9w0BAQsFAAOCAQEAyqVVjOPI
|
||||
QW5pJ6d1Ee88hjZv0p3GeDgdaZaikmkuOGybfQTUiaWxMTeKySHMq2zNixya1r9I
|
||||
0jJmwYrA8y8678Dj1JGG0VDjA9tzd29KOVPt3ibHtX2vK0LRdWLjSisCx1BL4Gni
|
||||
lmwORGYQRI+tBev4eaymG+g3NJ1TyWGqolKvSnAWhsI6yLETcDbYz+70CjTVW0z9
|
||||
B5yiutkBclzzTcHdDrEcDcRjvq30FPuJ7KJBDkzMyFdA0G4Dqs0MjomZmWzwPDCv
|
||||
ON9vvKO+KSAnq3T/EyJ43pdSVR6DtVQgA+6uwE9W3jfMw3+qBCe703e4YtsXfJwo
|
||||
IhNzbM8m9Yop5w==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICRjCCAc2gAwIBAgIQC6Fa+h3foLVJRK/NJKBs7DAKBggqhkjOPQQDAzBlMQsw
|
||||
CQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3d3cu
|
||||
ZGlnaWNlcnQuY29tMSQwIgYDVQQDExtEaWdpQ2VydCBBc3N1cmVkIElEIFJvb3Qg
|
||||
RzMwHhcNMTMwODAxMTIwMDAwWhcNMzgwMTE1MTIwMDAwWjBlMQswCQYDVQQGEwJV
|
||||
UzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3d3cuZGlnaWNlcnQu
|
||||
Y29tMSQwIgYDVQQDExtEaWdpQ2VydCBBc3N1cmVkIElEIFJvb3QgRzMwdjAQBgcq
|
||||
hkjOPQIBBgUrgQQAIgNiAAQZ57ysRGXtzbg/WPuNsVepRC0FFfLvC/8QdJ+1YlJf
|
||||
Zn4f5dwbRXkLzMZTCp2NXQLZqVneAlr2lSoOjThKiknGvMYDOAdfVdp+CW7if17Q
|
||||
RSAPWXYQ1qAk8C3eNvJsKTmjQjBAMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/
|
||||
BAQDAgGGMB0GA1UdDgQWBBTL0L2p4ZgFUaFNN6KDec6NHSrkhDAKBggqhkjOPQQD
|
||||
AwNnADBkAjAlpIFFAmsSS3V0T8gj43DydXLefInwz5FyYZ5eEJJZVrmDxxDnOOlY
|
||||
JjZ91eQ0hjkCMHw2U/Aw5WJjOpnitqM7mzT6HtoQknFekROn3aRukswy1vUhZscv
|
||||
6pZjamVFkpUBtA==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDrzCCApegAwIBAgIQCDvgVpBCRrGhdWrJWZHHSjANBgkqhkiG9w0BAQUFADBh
|
||||
MQswCQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3
|
||||
d3cuZGlnaWNlcnQuY29tMSAwHgYDVQQDExdEaWdpQ2VydCBHbG9iYWwgUm9vdCBD
|
||||
QTAeFw0wNjExMTAwMDAwMDBaFw0zMTExMTAwMDAwMDBaMGExCzAJBgNVBAYTAlVT
|
||||
MRUwEwYDVQQKEwxEaWdpQ2VydCBJbmMxGTAXBgNVBAsTEHd3dy5kaWdpY2VydC5j
|
||||
b20xIDAeBgNVBAMTF0RpZ2lDZXJ0IEdsb2JhbCBSb290IENBMIIBIjANBgkqhkiG
|
||||
9w0BAQEFAAOCAQ8AMIIBCgKCAQEA4jvhEXLeqKTTo1eqUKKPC3eQyaKl7hLOllsB
|
||||
CSDMAZOnTjC3U/dDxGkAV53ijSLdhwZAAIEJzs4bg7/fzTtxRuLWZscFs3YnFo97
|
||||
nh6Vfe63SKMI2tavegw5BmV/Sl0fvBf4q77uKNd0f3p4mVmFaG5cIzJLv07A6Fpt
|
||||
43C/dxC//AH2hdmoRBBYMql1GNXRor5H4idq9Joz+EkIYIvUX7Q6hL+hqkpMfT7P
|
||||
T19sdl6gSzeRntwi5m3OFBqOasv+zbMUZBfHWymeMr/y7vrTC0LUq7dBMtoM1O/4
|
||||
gdW7jVg/tRvoSSiicNoxBN33shbyTApOB6jtSj1etX+jkMOvJwIDAQABo2MwYTAO
|
||||
BgNVHQ8BAf8EBAMCAYYwDwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUA95QNVbR
|
||||
TLtm8KPiGxvDl7I90VUwHwYDVR0jBBgwFoAUA95QNVbRTLtm8KPiGxvDl7I90VUw
|
||||
DQYJKoZIhvcNAQEFBQADggEBAMucN6pIExIK+t1EnE9SsPTfrgT1eXkIoyQY/Esr
|
||||
hMAtudXH/vTBH1jLuG2cenTnmCmrEbXjcKChzUyImZOMkXDiqw8cvpOp/2PV5Adg
|
||||
06O/nVsJ8dWO41P0jmP6P6fbtGbfYmbW0W5BjfIttep3Sp+dWOIrWcBAI+0tKIJF
|
||||
PnlUkiaY4IBIqDfv8NZ5YBberOgOzW6sRBc4L0na4UU+Krk2U886UAb3LujEV0ls
|
||||
YSEY1QSteDwsOoBrp+uvFRTp2InBuThs4pFsiv9kuXclVzDAGySj4dzp30d8tbQk
|
||||
CAUw7C29C79Fv1C5qfPrmAESrciIxpg0X40KPMbp1ZWVbd4=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDjjCCAnagAwIBAgIQAzrx5qcRqaC7KGSxHQn65TANBgkqhkiG9w0BAQsFADBh
|
||||
MQswCQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3
|
||||
d3cuZGlnaWNlcnQuY29tMSAwHgYDVQQDExdEaWdpQ2VydCBHbG9iYWwgUm9vdCBH
|
||||
MjAeFw0xMzA4MDExMjAwMDBaFw0zODAxMTUxMjAwMDBaMGExCzAJBgNVBAYTAlVT
|
||||
MRUwEwYDVQQKEwxEaWdpQ2VydCBJbmMxGTAXBgNVBAsTEHd3dy5kaWdpY2VydC5j
|
||||
b20xIDAeBgNVBAMTF0RpZ2lDZXJ0IEdsb2JhbCBSb290IEcyMIIBIjANBgkqhkiG
|
||||
9w0BAQEFAAOCAQ8AMIIBCgKCAQEAuzfNNNx7a8myaJCtSnX/RrohCgiN9RlUyfuI
|
||||
2/Ou8jqJkTx65qsGGmvPrC3oXgkkRLpimn7Wo6h+4FR1IAWsULecYxpsMNzaHxmx
|
||||
1x7e/dfgy5SDN67sH0NO3Xss0r0upS/kqbitOtSZpLYl6ZtrAGCSYP9PIUkY92eQ
|
||||
q2EGnI/yuum06ZIya7XzV+hdG82MHauVBJVJ8zUtluNJbd134/tJS7SsVQepj5Wz
|
||||
tCO7TG1F8PapspUwtP1MVYwnSlcUfIKdzXOS0xZKBgyMUNGPHgm+F6HmIcr9g+UQ
|
||||
vIOlCsRnKPZzFBQ9RnbDhxSJITRNrw9FDKZJobq7nMWxM4MphQIDAQABo0IwQDAP
|
||||
BgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIBhjAdBgNVHQ4EFgQUTiJUIBiV
|
||||
5uNu5g/6+rkS7QYXjzkwDQYJKoZIhvcNAQELBQADggEBAGBnKJRvDkhj6zHd6mcY
|
||||
1Yl9PMWLSn/pvtsrF9+wX3N3KjITOYFnQoQj8kVnNeyIv/iPsGEMNKSuIEyExtv4
|
||||
NeF22d+mQrvHRAiGfzZ0JFrabA0UWTW98kndth/Jsw1HKj2ZL7tcu7XUIOGZX1NG
|
||||
Fdtom/DzMNU+MeKNhJ7jitralj41E6Vf8PlwUHBHQRFXGU7Aj64GxJUTFy8bJZ91
|
||||
8rGOmaFvE7FBcf6IKshPECBV1/MUReXgRPTqh5Uykw7+U0b6LJ3/iyK5S9kJRaTe
|
||||
pLiaWN0bfVKfjllDiIGknibVb63dDcY3fe0Dkhvld1927jyNxF1WW6LZZm6zNTfl
|
||||
MrY=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICPzCCAcWgAwIBAgIQBVVWvPJepDU1w6QP1atFcjAKBggqhkjOPQQDAzBhMQsw
|
||||
CQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3d3cu
|
||||
ZGlnaWNlcnQuY29tMSAwHgYDVQQDExdEaWdpQ2VydCBHbG9iYWwgUm9vdCBHMzAe
|
||||
Fw0xMzA4MDExMjAwMDBaFw0zODAxMTUxMjAwMDBaMGExCzAJBgNVBAYTAlVTMRUw
|
||||
EwYDVQQKEwxEaWdpQ2VydCBJbmMxGTAXBgNVBAsTEHd3dy5kaWdpY2VydC5jb20x
|
||||
IDAeBgNVBAMTF0RpZ2lDZXJ0IEdsb2JhbCBSb290IEczMHYwEAYHKoZIzj0CAQYF
|
||||
K4EEACIDYgAE3afZu4q4C/sLfyHS8L6+c/MzXRq8NOrexpu80JX28MzQC7phW1FG
|
||||
fp4tn+6OYwwX7Adw9c+ELkCDnOg/QW07rdOkFFk2eJ0DQ+4QE2xy3q6Ip6FrtUPO
|
||||
Z9wj/wMco+I+o0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIBhjAd
|
||||
BgNVHQ4EFgQUs9tIpPmhxdiuNkHMEWNpYim8S8YwCgYIKoZIzj0EAwMDaAAwZQIx
|
||||
AK288mw/EkrRLTnDCgmXc/SINoyIJ7vmiI1Qhadj+Z4y3maTD/HMsQmP3Wyr+mt/
|
||||
oAIwOWZbwmSNuJ5Q3KjVSaLtx9zRSX8XAbjIho9OjIgrqJqpisXRAL34VOKa5Vt8
|
||||
sycX
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDxTCCAq2gAwIBAgIQAqxcJmoLQJuPC3nyrkYldzANBgkqhkiG9w0BAQUFADBs
|
||||
MQswCQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3
|
||||
d3cuZGlnaWNlcnQuY29tMSswKQYDVQQDEyJEaWdpQ2VydCBIaWdoIEFzc3VyYW5j
|
||||
ZSBFViBSb290IENBMB4XDTA2MTExMDAwMDAwMFoXDTMxMTExMDAwMDAwMFowbDEL
|
||||
MAkGA1UEBhMCVVMxFTATBgNVBAoTDERpZ2lDZXJ0IEluYzEZMBcGA1UECxMQd3d3
|
||||
LmRpZ2ljZXJ0LmNvbTErMCkGA1UEAxMiRGlnaUNlcnQgSGlnaCBBc3N1cmFuY2Ug
|
||||
RVYgUm9vdCBDQTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAMbM5XPm
|
||||
+9S75S0tMqbf5YE/yc0lSbZxKsPVlDRnogocsF9ppkCxxLeyj9CYpKlBWTrT3JTW
|
||||
PNt0OKRKzE0lgvdKpVMSOO7zSW1xkX5jtqumX8OkhPhPYlG++MXs2ziS4wblCJEM
|
||||
xChBVfvLWokVfnHoNb9Ncgk9vjo4UFt3MRuNs8ckRZqnrG0AFFoEt7oT61EKmEFB
|
||||
Ik5lYYeBQVCmeVyJ3hlKV9Uu5l0cUyx+mM0aBhakaHPQNAQTXKFx01p8VdteZOE3
|
||||
hzBWBOURtCmAEvF5OYiiAhF8J2a3iLd48soKqDirCmTCv2ZdlYTBoSUeh10aUAsg
|
||||
EsxBu24LUTi4S8sCAwEAAaNjMGEwDgYDVR0PAQH/BAQDAgGGMA8GA1UdEwEB/wQF
|
||||
MAMBAf8wHQYDVR0OBBYEFLE+w2kD+L9HAdSYJhoIAu9jZCvDMB8GA1UdIwQYMBaA
|
||||
FLE+w2kD+L9HAdSYJhoIAu9jZCvDMA0GCSqGSIb3DQEBBQUAA4IBAQAcGgaX3Nec
|
||||
nzyIZgYIVyHbIUf4KmeqvxgydkAQV8GK83rZEWWONfqe/EW1ntlMMUu4kehDLI6z
|
||||
eM7b41N5cdblIZQB2lWHmiRk9opmzN6cN82oNLFpmyPInngiK3BD41VHMWEZ71jF
|
||||
hS9OMPagMRYjyOfiZRYzy78aG6A9+MpeizGLYAiJLQwGXFK3xPkKmNEVX58Svnw2
|
||||
Yzi9RKR/5CYrCsSXaQ3pjOLAEFe4yHYSkVXySGnYvCoCWw9E1CAx2/S6cCZdkGCe
|
||||
vEsXCS+0yx5DaMkHJ8HSXPfqIbloEpw8nL+e/IBcm2PN7EeqJSdnoDfzAIJ9VNep
|
||||
+OkuE6N36B9K
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFkDCCA3igAwIBAgIQBZsbV56OITLiOQe9p3d1XDANBgkqhkiG9w0BAQwFADBi
|
||||
MQswCQYDVQQGEwJVUzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3
|
||||
d3cuZGlnaWNlcnQuY29tMSEwHwYDVQQDExhEaWdpQ2VydCBUcnVzdGVkIFJvb3Qg
|
||||
RzQwHhcNMTMwODAxMTIwMDAwWhcNMzgwMTE1MTIwMDAwWjBiMQswCQYDVQQGEwJV
|
||||
UzEVMBMGA1UEChMMRGlnaUNlcnQgSW5jMRkwFwYDVQQLExB3d3cuZGlnaWNlcnQu
|
||||
Y29tMSEwHwYDVQQDExhEaWdpQ2VydCBUcnVzdGVkIFJvb3QgRzQwggIiMA0GCSqG
|
||||
SIb3DQEBAQUAA4ICDwAwggIKAoICAQC/5pBzaN675F1KPDAiMGkz7MKnJS7JIT3y
|
||||
ithZwuEppz1Yq3aaza57G4QNxDAf8xukOBbrVsaXbR2rsnnyyhHS5F/WBTxSD1If
|
||||
xp4VpX6+n6lXFllVcq9ok3DCsrp1mWpzMpTREEQQLt+C8weE5nQ7bXHiLQwb7iDV
|
||||
ySAdYyktzuxeTsiT+CFhmzTrBcZe7FsavOvJz82sNEBfsXpm7nfISKhmV1efVFiO
|
||||
DCu3T6cw2Vbuyntd463JT17lNecxy9qTXtyOj4DatpGYQJB5w3jHtrHEtWoYOAMQ
|
||||
jdjUN6QuBX2I9YI+EJFwq1WCQTLX2wRzKm6RAXwhTNS8rhsDdV14Ztk6MUSaM0C/
|
||||
CNdaSaTC5qmgZ92kJ7yhTzm1EVgX9yRcRo9k98FpiHaYdj1ZXUJ2h4mXaXpI8OCi
|
||||
EhtmmnTK3kse5w5jrubU75KSOp493ADkRSWJtppEGSt+wJS00mFt6zPZxd9LBADM
|
||||
fRyVw4/3IbKyEbe7f/LVjHAsQWCqsWMYRJUadmJ+9oCw++hkpjPRiQfhvbfmQ6QY
|
||||
uKZ3AeEPlAwhHbJUKSWJbOUOUlFHdL4mrLZBdd56rF+NP8m800ERElvlEFDrMcXK
|
||||
chYiCd98THU/Y+whX8QgUWtvsauGi0/C1kVfnSD8oR7FwI+isX4KJpn15GkvmB0t
|
||||
9dmpsh3lGwIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIB
|
||||
hjAdBgNVHQ4EFgQU7NfjgtJxXWRM3y5nP+e6mK4cD08wDQYJKoZIhvcNAQEMBQAD
|
||||
ggIBALth2X2pbL4XxJEbw6GiAI3jZGgPVs93rnD5/ZpKmbnJeFwMDF/k5hQpVgs2
|
||||
SV1EY+CtnJYYZhsjDT156W1r1lT40jzBQ0CuHVD1UvyQO7uYmWlrx8GnqGikJ9yd
|
||||
+SeuMIW59mdNOj6PWTkiU0TryF0Dyu1Qen1iIQqAyHNm0aAFYF/opbSnr6j3bTWc
|
||||
fFqK1qI4mfN4i/RN0iAL3gTujJtHgXINwBQy7zBZLq7gcfJW5GqXb5JQbZaNaHqa
|
||||
sjYUegbyJLkJEVDXCLG4iXqEI2FCKeWjzaIgQdfRnGTZ6iahixTXTBmyUEFxPT9N
|
||||
cCOGDErcgdLMMpSEDQgJlxxPwO5rIHQw0uA5NBCFIRUBCOhVMt5xSdkoF1BN5r5N
|
||||
0XWs0Mr7QbhDparTwwVETyw2m+L64kW4I1NsBm9nVX9GtUw/bihaeSbSpKhil9Ie
|
||||
4u1Ki7wb/UdKDd9nZn6yW0HQO+T0O/QEY+nvwlQAUaCKKsnOeMzV6ocEGLPOr0mI
|
||||
r/OSmbaz5mEP0oUA51Aa5BuVnRmhuZyxm7EAHu/QD09CbMkKvO5D+jpxpchNJqU1
|
||||
/YldvIViHTLSoCtU7ZpXwdv6EM8Zt4tKG48BtieVU+i2iW1bvGjUI+iLUaJW+fCm
|
||||
gKDWHrO8Dw9TdSmq6hN35N6MgSGtBxBHEa2HPQfRdbzP82Z+
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIGSzCCBDOgAwIBAgIIamg+nFGby1MwDQYJKoZIhvcNAQELBQAwgbIxCzAJBgNV
|
||||
BAYTAlRSMQ8wDQYDVQQHDAZBbmthcmExQDA+BgNVBAoMN0UtVHXEn3JhIEVCRyBC
|
||||
aWxpxZ9pbSBUZWtub2xvamlsZXJpIHZlIEhpem1ldGxlcmkgQS7Fni4xJjAkBgNV
|
||||
BAsMHUUtVHVncmEgU2VydGlmaWthc3lvbiBNZXJrZXppMSgwJgYDVQQDDB9FLVR1
|
||||
Z3JhIENlcnRpZmljYXRpb24gQXV0aG9yaXR5MB4XDTEzMDMwNTEyMDk0OFoXDTIz
|
||||
MDMwMzEyMDk0OFowgbIxCzAJBgNVBAYTAlRSMQ8wDQYDVQQHDAZBbmthcmExQDA+
|
||||
BgNVBAoMN0UtVHXEn3JhIEVCRyBCaWxpxZ9pbSBUZWtub2xvamlsZXJpIHZlIEhp
|
||||
em1ldGxlcmkgQS7Fni4xJjAkBgNVBAsMHUUtVHVncmEgU2VydGlmaWthc3lvbiBN
|
||||
ZXJrZXppMSgwJgYDVQQDDB9FLVR1Z3JhIENlcnRpZmljYXRpb24gQXV0aG9yaXR5
|
||||
MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEA4vU/kwVRHoViVF56C/UY
|
||||
B4Oufq9899SKa6VjQzm5S/fDxmSJPZQuVIBSOTkHS0vdhQd2h8y/L5VMzH2nPbxH
|
||||
D5hw+IyFHnSOkm0bQNGZDbt1bsipa5rAhDGvykPL6ys06I+XawGb1Q5KCKpbknSF
|
||||
Q9OArqGIW66z6l7LFpp3RMih9lRozt6Plyu6W0ACDGQXwLWTzeHxE2bODHnv0ZEo
|
||||
q1+gElIwcxmOj+GMB6LDu0rw6h8VqO4lzKRG+Bsi77MOQ7osJLjFLFzUHPhdZL3D
|
||||
k14opz8n8Y4e0ypQBaNV2cvnOVPAmJ6MVGKLJrD3fY185MaeZkJVgkfnsliNZvcH
|
||||
fC425lAcP9tDJMW/hkd5s3kc91r0E+xs+D/iWR+V7kI+ua2oMoVJl0b+SzGPWsut
|
||||
dEcf6ZG33ygEIqDUD13ieU/qbIWGvaimzuT6w+Gzrt48Ue7LE3wBf4QOXVGUnhMM
|
||||
ti6lTPk5cDZvlsouDERVxcr6XQKj39ZkjFqzAQqptQpHF//vkUAqjqFGOjGY5RH8
|
||||
zLtJVor8udBhmm9lbObDyz51Sf6Pp+KJxWfXnUYTTjF2OySznhFlhqt/7x3U+Lzn
|
||||
rFpct1pHXFXOVbQicVtbC/DP3KBhZOqp12gKY6fgDT+gr9Oq0n7vUaDmUStVkhUX
|
||||
U8u3Zg5mTPj5dUyQ5xJwx0UCAwEAAaNjMGEwHQYDVR0OBBYEFC7j27JJ0JxUeVz6
|
||||
Jyr+zE7S6E5UMA8GA1UdEwEB/wQFMAMBAf8wHwYDVR0jBBgwFoAULuPbsknQnFR5
|
||||
XPonKv7MTtLoTlQwDgYDVR0PAQH/BAQDAgEGMA0GCSqGSIb3DQEBCwUAA4ICAQAF
|
||||
Nzr0TbdF4kV1JI+2d1LoHNgQk2Xz8lkGpD4eKexd0dCrfOAKkEh47U6YA5n+KGCR
|
||||
HTAduGN8qOY1tfrTYXbm1gdLymmasoR6d5NFFxWfJNCYExL/u6Au/U5Mh/jOXKqY
|
||||
GwXgAEZKgoClM4so3O0409/lPun++1ndYYRP0lSWE2ETPo+Aab6TR7U1Q9Jauz1c
|
||||
77NCR807VRMGsAnb/WP2OogKmW9+4c4bU2pEZiNRCHu8W1Ki/QY3OEBhj0qWuJA3
|
||||
+GbHeJAAFS6LrVE1Uweoa2iu+U48BybNCAVwzDk/dr2l02cmAYamU9JgO3xDf1WK
|
||||
vJUawSg5TB9D0pH0clmKuVb8P7Sd2nCcdlqMQ1DujjByTd//SffGqWfZbawCEeI6
|
||||
FiWnWAjLb1NBnEg4R2gz0dfHj9R0IdTDBZB6/86WiLEVKV0jq9BgoRJP3vQXzTLl
|
||||
yb/IQ639Lo7xr+L0mPoSHyDYwKcMhcWQ9DstliaxLL5Mq+ux0orJ23gTDx4JnW2P
|
||||
AJ8C2sH6H3p6CcRK5ogql5+Ji/03X186zjhZhkuvcQu02PJwT58yE+Owp1fl2tpD
|
||||
y4Q08ijE6m30Ku/Ba3ba+367hTzSU8JNvnHhRdH9I2cNE3X7z2VnIp2usAnRCf8d
|
||||
NL/+I5c30jn6PQ0GC7TbO6Orb1wdtn7os4I07QZcJA==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFVjCCBD6gAwIBAgIQ7is969Qh3hSoYqwE893EATANBgkqhkiG9w0BAQUFADCB
|
||||
8zELMAkGA1UEBhMCRVMxOzA5BgNVBAoTMkFnZW5jaWEgQ2F0YWxhbmEgZGUgQ2Vy
|
||||
dGlmaWNhY2lvIChOSUYgUS0wODAxMTc2LUkpMSgwJgYDVQQLEx9TZXJ2ZWlzIFB1
|
||||
YmxpY3MgZGUgQ2VydGlmaWNhY2lvMTUwMwYDVQQLEyxWZWdldSBodHRwczovL3d3
|
||||
dy5jYXRjZXJ0Lm5ldC92ZXJhcnJlbCAoYykwMzE1MDMGA1UECxMsSmVyYXJxdWlh
|
||||
IEVudGl0YXRzIGRlIENlcnRpZmljYWNpbyBDYXRhbGFuZXMxDzANBgNVBAMTBkVD
|
||||
LUFDQzAeFw0wMzAxMDcyMzAwMDBaFw0zMTAxMDcyMjU5NTlaMIHzMQswCQYDVQQG
|
||||
EwJFUzE7MDkGA1UEChMyQWdlbmNpYSBDYXRhbGFuYSBkZSBDZXJ0aWZpY2FjaW8g
|
||||
KE5JRiBRLTA4MDExNzYtSSkxKDAmBgNVBAsTH1NlcnZlaXMgUHVibGljcyBkZSBD
|
||||
ZXJ0aWZpY2FjaW8xNTAzBgNVBAsTLFZlZ2V1IGh0dHBzOi8vd3d3LmNhdGNlcnQu
|
||||
bmV0L3ZlcmFycmVsIChjKTAzMTUwMwYDVQQLEyxKZXJhcnF1aWEgRW50aXRhdHMg
|
||||
ZGUgQ2VydGlmaWNhY2lvIENhdGFsYW5lczEPMA0GA1UEAxMGRUMtQUNDMIIBIjAN
|
||||
BgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAsyLHT+KXQpWIR4NA9h0X84NzJB5R
|
||||
85iKw5K4/0CQBXCHYMkAqbWUZRkiFRfCQ2xmRJoNBD45b6VLeqpjt4pEndljkYRm
|
||||
4CgPukLjbo73FCeTae6RDqNfDrHrZqJyTxIThmV6PttPB/SnCWDaOkKZx7J/sxaV
|
||||
HMf5NLWUhdWZXqBIoH7nF2W4onW4HvPlQn2v7fOKSGRdghST2MDk/7NQcvJ29rNd
|
||||
QlB50JQ+awwAvthrDk4q7D7SzIKiGGUzE3eeml0aE9jD2z3Il3rucO2n5nzbcc8t
|
||||
lGLfbdb1OL4/pYUKGbio2Al1QnDE6u/LDsg0qBIimAy4E5S2S+zw0JDnJwIDAQAB
|
||||
o4HjMIHgMB0GA1UdEQQWMBSBEmVjX2FjY0BjYXRjZXJ0Lm5ldDAPBgNVHRMBAf8E
|
||||
BTADAQH/MA4GA1UdDwEB/wQEAwIBBjAdBgNVHQ4EFgQUoMOLRKo3pUW/l4Ba0fF4
|
||||
opvpXY0wfwYDVR0gBHgwdjB0BgsrBgEEAfV4AQMBCjBlMCwGCCsGAQUFBwIBFiBo
|
||||
dHRwczovL3d3dy5jYXRjZXJ0Lm5ldC92ZXJhcnJlbDA1BggrBgEFBQcCAjApGidW
|
||||
ZWdldSBodHRwczovL3d3dy5jYXRjZXJ0Lm5ldC92ZXJhcnJlbCAwDQYJKoZIhvcN
|
||||
AQEFBQADggEBAKBIW4IB9k1IuDlVNZyAelOZ1Vr/sXE7zDkJlF7W2u++AVtd0x7Y
|
||||
/X1PzaBB4DSTv8vihpw3kpBWHNzrKQXlxJ7HNd+KDM3FIUPpqojlNcAZQmNaAl6k
|
||||
SBg6hW/cnbw/nZzBh7h6YQjpdwt/cKt63dmXLGQehb+8dJahw3oS7AwaboMMPOhy
|
||||
Rp/7SNVel+axofjk70YllJyJ22k4vuxcDlbHZVHlUIiIv0LVKz3l+bqeLrPK9HOS
|
||||
Agu+TGbrIP65y7WZf+a2E/rKS03Z7lNGBjvGTq2TWoF+bCpLagVFjPIhpDGQh2xl
|
||||
nJ2lYJU6Un/10asIbvPuW/mIPX64b24D5EI=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEAzCCAuugAwIBAgIQVID5oHPtPwBMyonY43HmSjANBgkqhkiG9w0BAQUFADB1
|
||||
MQswCQYDVQQGEwJFRTEiMCAGA1UECgwZQVMgU2VydGlmaXRzZWVyaW1pc2tlc2t1
|
||||
czEoMCYGA1UEAwwfRUUgQ2VydGlmaWNhdGlvbiBDZW50cmUgUm9vdCBDQTEYMBYG
|
||||
CSqGSIb3DQEJARYJcGtpQHNrLmVlMCIYDzIwMTAxMDMwMTAxMDMwWhgPMjAzMDEy
|
||||
MTcyMzU5NTlaMHUxCzAJBgNVBAYTAkVFMSIwIAYDVQQKDBlBUyBTZXJ0aWZpdHNl
|
||||
ZXJpbWlza2Vza3VzMSgwJgYDVQQDDB9FRSBDZXJ0aWZpY2F0aW9uIENlbnRyZSBS
|
||||
b290IENBMRgwFgYJKoZIhvcNAQkBFglwa2lAc2suZWUwggEiMA0GCSqGSIb3DQEB
|
||||
AQUAA4IBDwAwggEKAoIBAQDIIMDs4MVLqwd4lfNE7vsLDP90jmG7sWLqI9iroWUy
|
||||
euuOF0+W2Ap7kaJjbMeMTC55v6kF/GlclY1i+blw7cNRfdCT5mzrMEvhvH2/UpvO
|
||||
bntl8jixwKIy72KyaOBhU8E2lf/slLo2rpwcpzIP5Xy0xm90/XsY6KxX7QYgSzIw
|
||||
WFv9zajmofxwvI6Sc9uXp3whrj3B9UiHbCe9nyV0gVWw93X2PaRka9ZP585ArQ/d
|
||||
MtO8ihJTmMmJ+xAdTX7Nfh9WDSFwhfYggx/2uh8Ej+p3iDXE/+pOoYtNP2MbRMNE
|
||||
1CV2yreN1x5KZmTNXMWcg+HCCIia7E6j8T4cLNlsHaFLAgMBAAGjgYowgYcwDwYD
|
||||
VR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFBLyWj7qVhy/
|
||||
zQas8fElyalL1BSZMEUGA1UdJQQ+MDwGCCsGAQUFBwMCBggrBgEFBQcDAQYIKwYB
|
||||
BQUHAwMGCCsGAQUFBwMEBggrBgEFBQcDCAYIKwYBBQUHAwkwDQYJKoZIhvcNAQEF
|
||||
BQADggEBAHv25MANqhlHt01Xo/6tu7Fq1Q+e2+RjxY6hUFaTlrg4wCQiZrxTFGGV
|
||||
v9DHKpY5P30osxBAIWrEr7BSdxjhlthWXePdNl4dp1BUoMUq5KqMlIpPnTX/dqQG
|
||||
E5Gion0ARD9V04I8GtVbvFZMIi5GQ4okQC3zErg7cBqklrkar4dBGmoYDQZPxz5u
|
||||
uSlNDUmJEYcyW+ZLBMjkXOZ0c5RdFpgTlf7727FE5TpwrDdr5rMzcijJs1eg9gIW
|
||||
iAYLtqZLICjU3j2LrTcFU3T+bsy8QxdxXvnFzBqpYe73dgzzcvRyrc9yAjYHR8/v
|
||||
GVCJYMzpJJUPwssd8m92kMfMdcGWxZ0=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEKjCCAxKgAwIBAgIEOGPe+DANBgkqhkiG9w0BAQUFADCBtDEUMBIGA1UEChML
|
||||
RW50cnVzdC5uZXQxQDA+BgNVBAsUN3d3dy5lbnRydXN0Lm5ldC9DUFNfMjA0OCBp
|
||||
bmNvcnAuIGJ5IHJlZi4gKGxpbWl0cyBsaWFiLikxJTAjBgNVBAsTHChjKSAxOTk5
|
||||
IEVudHJ1c3QubmV0IExpbWl0ZWQxMzAxBgNVBAMTKkVudHJ1c3QubmV0IENlcnRp
|
||||
ZmljYXRpb24gQXV0aG9yaXR5ICgyMDQ4KTAeFw05OTEyMjQxNzUwNTFaFw0yOTA3
|
||||
MjQxNDE1MTJaMIG0MRQwEgYDVQQKEwtFbnRydXN0Lm5ldDFAMD4GA1UECxQ3d3d3
|
||||
LmVudHJ1c3QubmV0L0NQU18yMDQ4IGluY29ycC4gYnkgcmVmLiAobGltaXRzIGxp
|
||||
YWIuKTElMCMGA1UECxMcKGMpIDE5OTkgRW50cnVzdC5uZXQgTGltaXRlZDEzMDEG
|
||||
A1UEAxMqRW50cnVzdC5uZXQgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkgKDIwNDgp
|
||||
MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEArU1LqRKGsuqjIAcVFmQq
|
||||
K0vRvwtKTY7tgHalZ7d4QMBzQshowNtTK91euHaYNZOLGp18EzoOH1u3Hs/lJBQe
|
||||
sYGpjX24zGtLA/ECDNyrpUAkAH90lKGdCCmziAv1h3edVc3kw37XamSrhRSGlVuX
|
||||
MlBvPci6Zgzj/L24ScF2iUkZ/cCovYmjZy/Gn7xxGWC4LeksyZB2ZnuU4q941mVT
|
||||
XTzWnLLPKQP5L6RQstRIzgUyVYr9smRMDuSYB3Xbf9+5CFVghTAp+XtIpGmG4zU/
|
||||
HoZdenoVve8AjhUiVBcAkCaTvA5JaJG/+EfTnZVCwQ5N328mz8MYIWJmQ3DW1cAH
|
||||
4QIDAQABo0IwQDAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB/zAdBgNV
|
||||
HQ4EFgQUVeSB0RGAvtiJuQijMfmhJAkWuXAwDQYJKoZIhvcNAQEFBQADggEBADub
|
||||
j1abMOdTmXx6eadNl9cZlZD7Bh/KM3xGY4+WZiT6QBshJ8rmcnPyT/4xmf3IDExo
|
||||
U8aAghOY+rat2l098c5u9hURlIIM7j+VrxGrD9cv3h8Dj1csHsm7mhpElesYT6Yf
|
||||
zX1XEC+bBAlahLVu2B064dae0Wx5XnkcFMXj0EyTO2U87d89vqbllRrDtRnDvV5b
|
||||
u/8j72gZyxKTJ1wDLW8w0B62GqzeWvfRqqgnpv55gcR5mTNXuhKwqeBCbJPKVt7+
|
||||
bYQLCIt+jerXmCHG8+c8eS9enNFMFY3h7CI3zJpDC5fcgJCNs2ebb0gIFVbPv/Er
|
||||
fF6adulZkMV8gzURZVE=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEkTCCA3mgAwIBAgIERWtQVDANBgkqhkiG9w0BAQUFADCBsDELMAkGA1UEBhMC
|
||||
VVMxFjAUBgNVBAoTDUVudHJ1c3QsIEluYy4xOTA3BgNVBAsTMHd3dy5lbnRydXN0
|
||||
Lm5ldC9DUFMgaXMgaW5jb3Jwb3JhdGVkIGJ5IHJlZmVyZW5jZTEfMB0GA1UECxMW
|
||||
KGMpIDIwMDYgRW50cnVzdCwgSW5jLjEtMCsGA1UEAxMkRW50cnVzdCBSb290IENl
|
||||
cnRpZmljYXRpb24gQXV0aG9yaXR5MB4XDTA2MTEyNzIwMjM0MloXDTI2MTEyNzIw
|
||||
NTM0MlowgbAxCzAJBgNVBAYTAlVTMRYwFAYDVQQKEw1FbnRydXN0LCBJbmMuMTkw
|
||||
NwYDVQQLEzB3d3cuZW50cnVzdC5uZXQvQ1BTIGlzIGluY29ycG9yYXRlZCBieSBy
|
||||
ZWZlcmVuY2UxHzAdBgNVBAsTFihjKSAyMDA2IEVudHJ1c3QsIEluYy4xLTArBgNV
|
||||
BAMTJEVudHJ1c3QgUm9vdCBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTCCASIwDQYJ
|
||||
KoZIhvcNAQEBBQADggEPADCCAQoCggEBALaVtkNC+sZtKm9I35RMOVcF7sN5EUFo
|
||||
Nu3s/poBj6E4KPz3EEZmLk0eGrEaTsbRwJWIsMn/MYszA9u3g3s+IIRe7bJWKKf4
|
||||
4LlAcTfFy0cOlypowCKVYhXbR9n10Cv/gkvJrT7eTNuQgFA/CYqEAOwwCj0Yzfv9
|
||||
KlmaI5UXLEWeH25DeW0MXJj+SKfFI0dcXv1u5x609mhF0YaDW6KKjbHjKYD+JXGI
|
||||
rb68j6xSlkuqUY3kEzEZ6E5Nn9uss2rVvDlUccp6en+Q3X0dgNmBu1kmwhH+5pPi
|
||||
94DkZfs0Nw4pgHBNrziGLp5/V6+eF67rHMsoIV+2HNjnogQi+dPa2MsCAwEAAaOB
|
||||
sDCBrTAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB/zArBgNVHRAEJDAi
|
||||
gA8yMDA2MTEyNzIwMjM0MlqBDzIwMjYxMTI3MjA1MzQyWjAfBgNVHSMEGDAWgBRo
|
||||
kORnpKZTgMeGZqTx90tD+4S9bTAdBgNVHQ4EFgQUaJDkZ6SmU4DHhmak8fdLQ/uE
|
||||
vW0wHQYJKoZIhvZ9B0EABBAwDhsIVjcuMTo0LjADAgSQMA0GCSqGSIb3DQEBBQUA
|
||||
A4IBAQCT1DCw1wMgKtD5Y+iRDAUgqV8ZyntyTtSx29CW+1RaGSwMCPeyvIWonX9t
|
||||
O1KzKtvn1ISMY/YPyyYBkVBs9F8U4pN0wBOeMDpQ47RgxRzwIkSNcUesyBrJ6Zua
|
||||
AGAT/3B+XxFNSRuzFVJ7yVTav52Vr2ua2J7p8eRDjeIRRDq/r72DQnNSi6q7pynP
|
||||
9WQcCk3RvKqsnyrQ/39/2n3qse0wJcGE2jTSW3iDVuycNsMm4hH2Z0kdkquM++v/
|
||||
eu6FSqdQgPCnXEqULl8FmTxSQeDNtGPPAUO6nIPcj2A781q0tHuu2guQOHXvgR1m
|
||||
0vdXcDazv/wor3ElhVsT/h5/WrQ8
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIC+TCCAoCgAwIBAgINAKaLeSkAAAAAUNCR+TAKBggqhkjOPQQDAzCBvzELMAkG
|
||||
A1UEBhMCVVMxFjAUBgNVBAoTDUVudHJ1c3QsIEluYy4xKDAmBgNVBAsTH1NlZSB3
|
||||
d3cuZW50cnVzdC5uZXQvbGVnYWwtdGVybXMxOTA3BgNVBAsTMChjKSAyMDEyIEVu
|
||||
dHJ1c3QsIEluYy4gLSBmb3IgYXV0aG9yaXplZCB1c2Ugb25seTEzMDEGA1UEAxMq
|
||||
RW50cnVzdCBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5IC0gRUMxMB4XDTEy
|
||||
MTIxODE1MjUzNloXDTM3MTIxODE1NTUzNlowgb8xCzAJBgNVBAYTAlVTMRYwFAYD
|
||||
VQQKEw1FbnRydXN0LCBJbmMuMSgwJgYDVQQLEx9TZWUgd3d3LmVudHJ1c3QubmV0
|
||||
L2xlZ2FsLXRlcm1zMTkwNwYDVQQLEzAoYykgMjAxMiBFbnRydXN0LCBJbmMuIC0g
|
||||
Zm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxMzAxBgNVBAMTKkVudHJ1c3QgUm9vdCBD
|
||||
ZXJ0aWZpY2F0aW9uIEF1dGhvcml0eSAtIEVDMTB2MBAGByqGSM49AgEGBSuBBAAi
|
||||
A2IABIQTydC6bUF74mzQ61VfZgIaJPRbiWlH47jCffHyAsWfoPZb1YsGGYZPUxBt
|
||||
ByQnoaD41UcZYUx9ypMn6nQM72+WCf5j7HBdNq1nd67JnXxVRDqiY1Ef9eNi1KlH
|
||||
Bz7MIKNCMEAwDgYDVR0PAQH/BAQDAgEGMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0O
|
||||
BBYEFLdj5xrdjekIplWDpOBqUEFlEUJJMAoGCCqGSM49BAMDA2cAMGQCMGF52OVC
|
||||
R98crlOZF7ZvHH3hvxGU0QOIdeSNiaSKd0bebWHvAvX7td/M/k7//qnmpwIwW5nX
|
||||
hTcGtXsI/esni0qU+eH6p44mCOh8kmhtc9hvJqwhAriZtyZBWyVgrtBIGu4G
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEPjCCAyagAwIBAgIESlOMKDANBgkqhkiG9w0BAQsFADCBvjELMAkGA1UEBhMC
|
||||
VVMxFjAUBgNVBAoTDUVudHJ1c3QsIEluYy4xKDAmBgNVBAsTH1NlZSB3d3cuZW50
|
||||
cnVzdC5uZXQvbGVnYWwtdGVybXMxOTA3BgNVBAsTMChjKSAyMDA5IEVudHJ1c3Qs
|
||||
IEluYy4gLSBmb3IgYXV0aG9yaXplZCB1c2Ugb25seTEyMDAGA1UEAxMpRW50cnVz
|
||||
dCBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5IC0gRzIwHhcNMDkwNzA3MTcy
|
||||
NTU0WhcNMzAxMjA3MTc1NTU0WjCBvjELMAkGA1UEBhMCVVMxFjAUBgNVBAoTDUVu
|
||||
dHJ1c3QsIEluYy4xKDAmBgNVBAsTH1NlZSB3d3cuZW50cnVzdC5uZXQvbGVnYWwt
|
||||
dGVybXMxOTA3BgNVBAsTMChjKSAyMDA5IEVudHJ1c3QsIEluYy4gLSBmb3IgYXV0
|
||||
aG9yaXplZCB1c2Ugb25seTEyMDAGA1UEAxMpRW50cnVzdCBSb290IENlcnRpZmlj
|
||||
YXRpb24gQXV0aG9yaXR5IC0gRzIwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEK
|
||||
AoIBAQC6hLZy254Ma+KZ6TABp3bqMriVQRrJ2mFOWHLP/vaCeb9zYQYKpSfYs1/T
|
||||
RU4cctZOMvJyig/3gxnQaoCAAEUesMfnmr8SVycco2gvCoe9amsOXmXzHHfV1IWN
|
||||
cCG0szLni6LVhjkCsbjSR87kyUnEO6fe+1R9V77w6G7CebI6C1XiUJgWMhNcL3hW
|
||||
wcKUs/Ja5CeanyTXxuzQmyWC48zCxEXFjJd6BmsqEZ+pCm5IO2/b1BEZQvePB7/1
|
||||
U1+cPvQXLOZprE4yTGJ36rfo5bs0vBmLrpxR57d+tVOxMyLlbc9wPBr64ptntoP0
|
||||
jaWvYkxN4FisZDQSA/i2jZRjJKRxAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAP
|
||||
BgNVHRMBAf8EBTADAQH/MB0GA1UdDgQWBBRqciZ60B7vfec7aVHUbI2fkBJmqzAN
|
||||
BgkqhkiG9w0BAQsFAAOCAQEAeZ8dlsa2eT8ijYfThwMEYGprmi5ZiXMRrEPR9RP/
|
||||
jTkrwPK9T3CMqS/qF8QLVJ7UG5aYMzyorWKiAHarWWluBh1+xLlEjZivEtRh2woZ
|
||||
Rkfz6/djwUAFQKXSt/S1mja/qYh2iARVBCuch38aNzx+LaUa2NSJXsq9rD1s2G2v
|
||||
1fN2D807iDginWyTmsQ9v4IbZT+mD12q/OWyFcq1rca8PdCE6OoGcrBNOTJ4vz4R
|
||||
nAuknZoh8/CbCzB428Hch0P+vGOaysXCHMnHjf87ElgI5rY97HosTvuDls4MPGmH
|
||||
VHOkc8KT/1EQrBVUAdj8BbGJoX90g5pJ19xOe4pIb4tF9g==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDVDCCAjygAwIBAgIDAjRWMA0GCSqGSIb3DQEBBQUAMEIxCzAJBgNVBAYTAlVT
|
||||
MRYwFAYDVQQKEw1HZW9UcnVzdCBJbmMuMRswGQYDVQQDExJHZW9UcnVzdCBHbG9i
|
||||
YWwgQ0EwHhcNMDIwNTIxMDQwMDAwWhcNMjIwNTIxMDQwMDAwWjBCMQswCQYDVQQG
|
||||
EwJVUzEWMBQGA1UEChMNR2VvVHJ1c3QgSW5jLjEbMBkGA1UEAxMSR2VvVHJ1c3Qg
|
||||
R2xvYmFsIENBMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA2swYYzD9
|
||||
9BcjGlZ+W988bDjkcbd4kdS8odhM+KhDtgPpTSEHCIjaWC9mOSm9BXiLnTjoBbdq
|
||||
fnGk5sRgprDvgOSJKA+eJdbtg/OtppHHmMlCGDUUna2YRpIuT8rxh0PBFpVXLVDv
|
||||
iS2Aelet8u5fa9IAjbkU+BQVNdnARqN7csiRv8lVK83Qlz6cJmTM386DGXHKTubU
|
||||
1XupGc1V3sjs0l44U+VcT4wt/lAjNvxm5suOpDkZALeVAjmRCw7+OC7RHQWa9k0+
|
||||
bw8HHa8sHo9gOeL6NlMTOdReJivbPagUvTLrGAMoUgRx5aszPeE4uwc2hGKceeoW
|
||||
MPRfwCvocWvk+QIDAQABo1MwUTAPBgNVHRMBAf8EBTADAQH/MB0GA1UdDgQWBBTA
|
||||
ephojYn7qwVkDBF9qn1luMrMTjAfBgNVHSMEGDAWgBTAephojYn7qwVkDBF9qn1l
|
||||
uMrMTjANBgkqhkiG9w0BAQUFAAOCAQEANeMpauUvXVSOKVCUn5kaFOSPeCpilKIn
|
||||
Z57QzxpeR+nBsqTP3UEaBU6bS+5Kb1VSsyShNwrrZHYqLizz/Tt1kL/6cdjHPTfS
|
||||
tQWVYrmm3ok9Nns4d0iXrKYgjy6myQzCsplFAMfOEVEiIuCl6rYVSAlk6l5PdPcF
|
||||
PseKUgzbFbS9bZvlxrFUaKnjaZC2mqUPuLk/IH2uSrW4nOQdtqvmlKXBx4Ot2/Un
|
||||
hw4EbNX/3aBd7YdStysVAq45pmp06drE57xNNB6pXE0zX5IJL4hmXXeXxx12E6nV
|
||||
5fEWCRE11azbJHFwLJhWC9kXtNHjUStedejV0NxPNO3CBWaAocvmMw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDfDCCAmSgAwIBAgIQGKy1av1pthU6Y2yv2vrEoTANBgkqhkiG9w0BAQUFADBY
|
||||
MQswCQYDVQQGEwJVUzEWMBQGA1UEChMNR2VvVHJ1c3QgSW5jLjExMC8GA1UEAxMo
|
||||
R2VvVHJ1c3QgUHJpbWFyeSBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTAeFw0wNjEx
|
||||
MjcwMDAwMDBaFw0zNjA3MTYyMzU5NTlaMFgxCzAJBgNVBAYTAlVTMRYwFAYDVQQK
|
||||
Ew1HZW9UcnVzdCBJbmMuMTEwLwYDVQQDEyhHZW9UcnVzdCBQcmltYXJ5IENlcnRp
|
||||
ZmljYXRpb24gQXV0aG9yaXR5MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKC
|
||||
AQEAvrgVe//UfH1nrYNke8hCUy3f9oQIIGHWAVlqnEQRr+92/ZV+zmEwu3qDXwK9
|
||||
AWbK7hWNb6EwnL2hhZ6UOvNWiAAxz9juapYC2e0DjPt1befquFUWBRaa9OBesYjA
|
||||
ZIVcFU2Ix7e64HXprQU9nceJSOC7KMgD4TCTZF5SwFlwIjVXiIrxlQqD17wxcwE0
|
||||
7e9GceBrAqg1cmuXm2bgyxx5X9gaBGgeRwLmnWDiNpcB3841kt++Z8dtd1k7j53W
|
||||
kBWUvEI0EME5+bEnPn7WinXFsq+W06Lem+SYvn3h6YGttm/81w7a4DSwDRp35+MI
|
||||
mO9Y+pyEtzavwt+s0vQQBnBxNQIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4G
|
||||
A1UdDwEB/wQEAwIBBjAdBgNVHQ4EFgQULNVQQZcVi/CPNmFbSvtr2ZnJM5IwDQYJ
|
||||
KoZIhvcNAQEFBQADggEBAFpwfyzdtzRP9YZRqSa+S7iq8XEN3GHHoOo0Hnp3DwQ1
|
||||
6CePbJC/kRYkRj5KTs4rFtULUh38H2eiAkUxT87z+gOneZ1TatnaYzr4gNfTmeGl
|
||||
4b7UVXGYNTq+k+qurUKykG/g/CFNNWMziUnWm07Kx+dOCQD32sfvmWKZd7aVIl6K
|
||||
oKv0uHiYyjgZmclynnjNS6yvGaBzEi38wkG6gZHaFloxt/m0cYASSJlyc1pZU8Fj
|
||||
UjPtp8nSOQJw+uCxQmYpqptR7TBUIhRf2asdweSU8Pj1K/fqynhG1riR/aYNKxoU
|
||||
AT6A8EKglQdebc3MS6RFjasS6LPeWuWgfOgPIh1a6Vk=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICrjCCAjWgAwIBAgIQPLL0SAoA4v7rJDteYD7DazAKBggqhkjOPQQDAzCBmDEL
|
||||
MAkGA1UEBhMCVVMxFjAUBgNVBAoTDUdlb1RydXN0IEluYy4xOTA3BgNVBAsTMChj
|
||||
KSAyMDA3IEdlb1RydXN0IEluYy4gLSBGb3IgYXV0aG9yaXplZCB1c2Ugb25seTE2
|
||||
MDQGA1UEAxMtR2VvVHJ1c3QgUHJpbWFyeSBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0
|
||||
eSAtIEcyMB4XDTA3MTEwNTAwMDAwMFoXDTM4MDExODIzNTk1OVowgZgxCzAJBgNV
|
||||
BAYTAlVTMRYwFAYDVQQKEw1HZW9UcnVzdCBJbmMuMTkwNwYDVQQLEzAoYykgMjAw
|
||||
NyBHZW9UcnVzdCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxNjA0BgNV
|
||||
BAMTLUdlb1RydXN0IFByaW1hcnkgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkgLSBH
|
||||
MjB2MBAGByqGSM49AgEGBSuBBAAiA2IABBWx6P0DFUPlrOuHNxFi79KDNlJ9RVcL
|
||||
So17VDs6bl8VAsBQps8lL33KSLjHUGMcKiEIfJo22Av+0SbFWDEwKCXzXV2juLal
|
||||
tJLtbCyf691DiaI8S0iRHVDsJt/WYC69IaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAO
|
||||
BgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFBVfNVdRVfslsq0DafwBo/q+EVXVMAoG
|
||||
CCqGSM49BAMDA2cAMGQCMGSWWaboCd6LuvpaiIjwH5HTRqjySkwCY/tsXzjbLkGT
|
||||
qQ7mndwxHLKgpxgceeHHNgIwOlavmnRs9vuD4DPTCF+hnMJbn0bWtsuRBmOiBucz
|
||||
rD6ogRLQy7rQkgu2npaqBA+K
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIID/jCCAuagAwIBAgIQFaxulBmyeUtB9iepwxgPHzANBgkqhkiG9w0BAQsFADCB
|
||||
mDELMAkGA1UEBhMCVVMxFjAUBgNVBAoTDUdlb1RydXN0IEluYy4xOTA3BgNVBAsT
|
||||
MChjKSAyMDA4IEdlb1RydXN0IEluYy4gLSBGb3IgYXV0aG9yaXplZCB1c2Ugb25s
|
||||
eTE2MDQGA1UEAxMtR2VvVHJ1c3QgUHJpbWFyeSBDZXJ0aWZpY2F0aW9uIEF1dGhv
|
||||
cml0eSAtIEczMB4XDTA4MDQwMjAwMDAwMFoXDTM3MTIwMTIzNTk1OVowgZgxCzAJ
|
||||
BgNVBAYTAlVTMRYwFAYDVQQKEw1HZW9UcnVzdCBJbmMuMTkwNwYDVQQLEzAoYykg
|
||||
MjAwOCBHZW9UcnVzdCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxNjA0
|
||||
BgNVBAMTLUdlb1RydXN0IFByaW1hcnkgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkg
|
||||
LSBHMzCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBANziXmJYHTNXOTIz
|
||||
+uvLh4yn1ErdBojqZI4xmKU4kB6Yzy5jK/BGvESyiaHAKAxJcCGVn2TAppMSAmUm
|
||||
hsalifD614SgcK9PGpc/BkTVyetyEH3kMSj7HGHmKAdEc5IiaacDiGydY8hS2pgn
|
||||
5whMcD60yRLBxWeDXTPzAxHsatBT4tG6NmCUgLthY2xbF37fQJQeqw3CIShwiP/W
|
||||
JmxsYAQlTlV+fe+/lEjetx3dcI0FX4ilm/LC7urRQEFtYjgdVgbFA0dRIBn8exAL
|
||||
DmKudlW/X3e+PkkBUz2YJQN2JFodtNuJ6nnltrM7P7pMKEF/BqxqjsHQ9gUdfeZC
|
||||
huOl1UcCAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYw
|
||||
HQYDVR0OBBYEFMR5yo6hTgMdHNxr2zFblD4/MH8tMA0GCSqGSIb3DQEBCwUAA4IB
|
||||
AQAtxRPPVoB7eni9n64smefv2t+UXglpp+duaIy9cr5HqQ6XErhK8WTTOd8lNNTB
|
||||
zU6B8A8ExCSzNJbGpqow32hhc9f5joWJ7w5elShKKiePEI4ufIbEAp7aDHdlDkQN
|
||||
kv39sxY2+hENHYwOB4lqKVb3cvTdFZx3NWZXqxNT2I7BQMXXExZacse3aQHEerGD
|
||||
AWh9jUGhlBjBJVz88P6DAod8DQ3PLghcSkANPuyBYeYk28rgDi0Hsj5W3I31QYUH
|
||||
SJsMC8tJP33st/3LjWeJGqvtux6jAAgIFyqCXDFdRootD4abdNlF+9RAsXqqaC2G
|
||||
spki4cErx5z481+oghLrGREt
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFaDCCA1CgAwIBAgIBATANBgkqhkiG9w0BAQUFADBFMQswCQYDVQQGEwJVUzEW
|
||||
MBQGA1UEChMNR2VvVHJ1c3QgSW5jLjEeMBwGA1UEAxMVR2VvVHJ1c3QgVW5pdmVy
|
||||
c2FsIENBMB4XDTA0MDMwNDA1MDAwMFoXDTI5MDMwNDA1MDAwMFowRTELMAkGA1UE
|
||||
BhMCVVMxFjAUBgNVBAoTDUdlb1RydXN0IEluYy4xHjAcBgNVBAMTFUdlb1RydXN0
|
||||
IFVuaXZlcnNhbCBDQTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAKYV
|
||||
VaCjxuAfjJ0hUNfBvitbtaSeodlyWL0AG0y/YckUHUWCq8YdgNY96xCcOq9tJPi8
|
||||
cQGeBvV8Xx7BDlXKg5pZMK4ZyzBIle0iN430SppyZj6tlcDgFgDgEB8rMQ7XlFTT
|
||||
QjOgNB0eRXbdT8oYN+yFFXoZCPzVx5zw8qkuEKmS5j1YPakWaDwvdSEYfyh3peFh
|
||||
F7em6fgemdtzbvQKoiFs7tqqhZJmr/Z6a4LauiIINQ/PQvE1+mrufislzDoR5G2v
|
||||
c7J2Ha3QsnhnGqQ5HFELZ1aD/ThdDc7d8Lsrlh/eezJS/R27tQahsiFepdaVaH/w
|
||||
mZ7cRQg+59IJDTWU3YBOU5fXtQlEIGQWFwMCTFMNaN7VqnJNk22CDtucvc+081xd
|
||||
VHppCZbW2xHBjXWotM85yM48vCR85mLK4b19p71XZQvk/iXttmkQ3CgaRr0BHdCX
|
||||
teGYO8A3ZNY9lO4L4fUorgtWv3GLIylBjobFS1J72HGrH4oVpjuDWtdYAVHGTEHZ
|
||||
f9hBZ3KiKN9gg6meyHv8U3NyWfWTehd2Ds735VzZC1U0oqpbtWpU5xPKV+yXbfRe
|
||||
Bi9Fi1jUIxaS5BZuKGNZMN9QAZxjiRqf2xeUgnA3wySemkfWWspOqGmJch+RbNt+
|
||||
nhutxx9z3SxPGWX9f5NAEC7S8O08ni4oPmkmM8V7AgMBAAGjYzBhMA8GA1UdEwEB
|
||||
/wQFMAMBAf8wHQYDVR0OBBYEFNq7LqqwDLiIJlF0XG0D08DYj3rWMB8GA1UdIwQY
|
||||
MBaAFNq7LqqwDLiIJlF0XG0D08DYj3rWMA4GA1UdDwEB/wQEAwIBhjANBgkqhkiG
|
||||
9w0BAQUFAAOCAgEAMXjmx7XfuJRAyXHEqDXsRh3ChfMoWIawC/yOsjmPRFWrZIRc
|
||||
aanQmjg8+uUfNeVE44B5lGiku8SfPeE0zTBGi1QrlaXv9z+ZhP015s8xxtxqv6fX
|
||||
IwjhmF7DWgh2qaavdy+3YL1ERmrvl/9zlcGO6JP7/TG37FcREUWbMPEaiDnBTzyn
|
||||
ANXH/KttgCJwpQzgXQQpAvvLoJHRfNbDflDVnVi+QTjruXU8FdmbyUqDWcDaU/0z
|
||||
uzYYm4UPFd3uLax2k7nZAY1IEKj79TiG8dsKxr2EoyNB3tZ3b4XUhRxQ4K5RirqN
|
||||
Pnbiucon8l+f725ZDQbYKxek0nxru18UGkiPGkzns0ccjkxFKyDuSN/n3QmOGKja
|
||||
QI2SJhFTYXNd673nxE0pN2HrrDktZy4W1vUAg4WhzH92xH3kt0tm7wNFYGm2DFKW
|
||||
koRepqO1pD4r2czYG0eq8kTaT/kD6PAUyz/zg97QwVTjt+gKN02LIFkDMBmhLMi9
|
||||
ER/frslKxfMnZmaGrGiR/9nmUxwPi1xpZQomyB40w11Re9epnAahNt3ViZS82eQt
|
||||
DF4JbAiXfKM9fJP/P6EUp8+1Xevb2xzEdt+Iub1FBZUbrvxGakyvSOPOrg/Sfuvm
|
||||
bJxPgWp6ZKy7PtXny3YuxadIwVyQD8vIP/rmMuGNG2+k5o7Y+SlIis5z/iw=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFbDCCA1SgAwIBAgIBATANBgkqhkiG9w0BAQUFADBHMQswCQYDVQQGEwJVUzEW
|
||||
MBQGA1UEChMNR2VvVHJ1c3QgSW5jLjEgMB4GA1UEAxMXR2VvVHJ1c3QgVW5pdmVy
|
||||
c2FsIENBIDIwHhcNMDQwMzA0MDUwMDAwWhcNMjkwMzA0MDUwMDAwWjBHMQswCQYD
|
||||
VQQGEwJVUzEWMBQGA1UEChMNR2VvVHJ1c3QgSW5jLjEgMB4GA1UEAxMXR2VvVHJ1
|
||||
c3QgVW5pdmVyc2FsIENBIDIwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoIC
|
||||
AQCzVFLByT7y2dyxUxpZKeexw0Uo5dfR7cXFS6GqdHtXr0om/Nj1XqduGdt0DE81
|
||||
WzILAePb63p3NeqqWuDW6KFXlPCQo3RWlEQwAx5cTiuFJnSCegx2oG9NzkEtoBUG
|
||||
FF+3Qs17j1hhNNwqCPkuwwGmIkQcTAeC5lvO0Ep8BNMZcyfwqph/Lq9O64ceJHdq
|
||||
XbboW0W63MOhBW9Wjo8QJqVJwy7XQYci4E+GymC16qFjwAGXEHm9ADwSbSsVsaxL
|
||||
se4YuU6W3Nx2/zu+z18DwPw76L5GG//aQMJS9/7jOvdqdzXQ2o3rXhhqMcceujwb
|
||||
KNZrVMaqW9eiLBsZzKIC9ptZvTdrhrVtgrrY6slWvKk2WP0+GfPtDCapkzj4T8Fd
|
||||
IgbQl+rhrcZV4IErKIM6+vR7IVEAvlI4zs1meaj0gVbi0IMJR1FbUGrP20gaXT73
|
||||
y/Zl92zxlfgCOzJWgjl6W70viRu/obTo/3+NjN8D8WBOWBFM66M/ECuDmgFz2ZRt
|
||||
hAAnZqzwcEAJQpKtT5MNYQlRJNiS1QuUYbKHsu3/mjX/hVTK7URDrBs8FmtISgoc
|
||||
QIgfksILAAX/8sgCSqSqqcyZlpwvWOB94b67B9xfBHJcMTTD7F8t4D1kkCLm0ey4
|
||||
Lt1ZrtmhN79UNdxzMk+MBB4zsslG8dhcyFVQyWi9qLo2CQIDAQABo2MwYTAPBgNV
|
||||
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBR281Xh+qQ2+/CfXGJx7Tz0RzgQKzAfBgNV
|
||||
HSMEGDAWgBR281Xh+qQ2+/CfXGJx7Tz0RzgQKzAOBgNVHQ8BAf8EBAMCAYYwDQYJ
|
||||
KoZIhvcNAQEFBQADggIBAGbBxiPz2eAubl/oz66wsCVNK/g7WJtAJDday6sWSf+z
|
||||
dXkzoS9tcBc0kf5nfo/sm+VegqlVHy/c1FEHEv6sFj4sNcZj/NwQ6w2jqtB8zNHQ
|
||||
L1EuxBRa3ugZ4T7GzKQp5y6EqgYweHZUcyiYWTjgAA1i00J9IZ+uPTqM1fp3DRgr
|
||||
Fg5fNuH8KrUwJM/gYwx7WBr+mbpCErGR9Hxo4sjoryzqyX6uuyo9DRXcNJW2GHSo
|
||||
ag/HtPQTxORb7QrSpJdMKu0vbBKJPfEncKpqA1Ihn0CoZ1Dy81of398j9tx4TuaY
|
||||
T1U6U+Pv8vSfx3zYWK8pIpe44L2RLrB27FcRz+8pRPPphXpgY+RdM4kX2TGq2tbz
|
||||
GDVyz4crL2MjhF2EjD9XoIj8mZEoJmmZ1I+XRL6O1UixpCgp8RW04eWe3fiPpm8m
|
||||
1wk8OhwRDqZsN/etRIcsKMfYdIKz0G9KV7s1KSegi+ghp4dkNl3M2Basx7InQJJV
|
||||
OCiNUW7dFGdTbHFcJoRNdVq2fmBWqU2t+5sel/MN2dKXVHfaPRK34B7vCAas+YWH
|
||||
6aLcr34YEoP9VhdBLtUpgn2Z9DH2canPLAEnpQW5qrJITirvn5NSUZU8UnOOVkwX
|
||||
QMAJKOSLakhT2+zNVVXxxvjpoixMptEmX36vWkzaH6byHCx+rgIW0lbQL1dTR+iS
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIB4TCCAYegAwIBAgIRKjikHJYKBN5CsiilC+g0mAIwCgYIKoZIzj0EAwIwUDEk
|
||||
MCIGA1UECxMbR2xvYmFsU2lnbiBFQ0MgUm9vdCBDQSAtIFI0MRMwEQYDVQQKEwpH
|
||||
bG9iYWxTaWduMRMwEQYDVQQDEwpHbG9iYWxTaWduMB4XDTEyMTExMzAwMDAwMFoX
|
||||
DTM4MDExOTAzMTQwN1owUDEkMCIGA1UECxMbR2xvYmFsU2lnbiBFQ0MgUm9vdCBD
|
||||
QSAtIFI0MRMwEQYDVQQKEwpHbG9iYWxTaWduMRMwEQYDVQQDEwpHbG9iYWxTaWdu
|
||||
MFkwEwYHKoZIzj0CAQYIKoZIzj0DAQcDQgAEuMZ5049sJQ6fLjkZHAOkrprlOQcJ
|
||||
FspjsbmG+IpXwVfOQvpzofdlQv8ewQCybnMO/8ch5RikqtlxP6jUuc6MHaNCMEAw
|
||||
DgYDVR0PAQH/BAQDAgEGMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFFSwe61F
|
||||
uOJAf/sKbvu+M8k8o4TVMAoGCCqGSM49BAMCA0gAMEUCIQDckqGgE6bPA7DmxCGX
|
||||
kPoUVy0D7O48027KqGx2vKLeuwIgJ6iFJzWbVsaj8kfSt24bAgAXqmemFZHe+pTs
|
||||
ewv4n4Q=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICHjCCAaSgAwIBAgIRYFlJ4CYuu1X5CneKcflK2GwwCgYIKoZIzj0EAwMwUDEk
|
||||
MCIGA1UECxMbR2xvYmFsU2lnbiBFQ0MgUm9vdCBDQSAtIFI1MRMwEQYDVQQKEwpH
|
||||
bG9iYWxTaWduMRMwEQYDVQQDEwpHbG9iYWxTaWduMB4XDTEyMTExMzAwMDAwMFoX
|
||||
DTM4MDExOTAzMTQwN1owUDEkMCIGA1UECxMbR2xvYmFsU2lnbiBFQ0MgUm9vdCBD
|
||||
QSAtIFI1MRMwEQYDVQQKEwpHbG9iYWxTaWduMRMwEQYDVQQDEwpHbG9iYWxTaWdu
|
||||
MHYwEAYHKoZIzj0CAQYFK4EEACIDYgAER0UOlvt9Xb/pOdEh+J8LttV7HpI6SFkc
|
||||
8GIxLcB6KP4ap1yztsyX50XUWPrRd21DosCHZTQKH3rd6zwzocWdTaRvQZU4f8ke
|
||||
hOvRnkmSh5SHDDqFSmafnVmTTZdhBoZKo0IwQDAOBgNVHQ8BAf8EBAMCAQYwDwYD
|
||||
VR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUPeYpSJvqB8ohREom3m7e0oPQn1kwCgYI
|
||||
KoZIzj0EAwMDaAAwZQIxAOVpEslu28YxuglB4Zf4+/2a4n0Sye18ZNPLBSWLVtmg
|
||||
515dTguDnFt2KaAJJiFqYgIwcdK1j1zqO+F4CYWodZI7yFz9SO8NdCKoCOJuxUnO
|
||||
xwy8p2Fp8fc74SrL+SvzZpA3
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDdTCCAl2gAwIBAgILBAAAAAABFUtaw5QwDQYJKoZIhvcNAQEFBQAwVzELMAkG
|
||||
A1UEBhMCQkUxGTAXBgNVBAoTEEdsb2JhbFNpZ24gbnYtc2ExEDAOBgNVBAsTB1Jv
|
||||
b3QgQ0ExGzAZBgNVBAMTEkdsb2JhbFNpZ24gUm9vdCBDQTAeFw05ODA5MDExMjAw
|
||||
MDBaFw0yODAxMjgxMjAwMDBaMFcxCzAJBgNVBAYTAkJFMRkwFwYDVQQKExBHbG9i
|
||||
YWxTaWduIG52LXNhMRAwDgYDVQQLEwdSb290IENBMRswGQYDVQQDExJHbG9iYWxT
|
||||
aWduIFJvb3QgQ0EwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQDaDuaZ
|
||||
jc6j40+Kfvvxi4Mla+pIH/EqsLmVEQS98GPR4mdmzxzdzxtIK+6NiY6arymAZavp
|
||||
xy0Sy6scTHAHoT0KMM0VjU/43dSMUBUc71DuxC73/OlS8pF94G3VNTCOXkNz8kHp
|
||||
1Wrjsok6Vjk4bwY8iGlbKk3Fp1S4bInMm/k8yuX9ifUSPJJ4ltbcdG6TRGHRjcdG
|
||||
snUOhugZitVtbNV4FpWi6cgKOOvyJBNPc1STE4U6G7weNLWLBYy5d4ux2x8gkasJ
|
||||
U26Qzns3dLlwR5EiUWMWea6xrkEmCMgZK9FGqkjWZCrXgzT/LCrBbBlDSgeF59N8
|
||||
9iFo7+ryUp9/k5DPAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNVHRMBAf8E
|
||||
BTADAQH/MB0GA1UdDgQWBBRge2YaRQ2XyolQL30EzTSo//z9SzANBgkqhkiG9w0B
|
||||
AQUFAAOCAQEA1nPnfE920I2/7LqivjTFKDK1fPxsnCwrvQmeU79rXqoRSLblCKOz
|
||||
yj1hTdNGCbM+w6DjY1Ub8rrvrTnhQ7k4o+YviiY776BQVvnGCv04zcQLcFGUl5gE
|
||||
38NflNUVyRRBnMRddWQVDf9VMOyGj/8N7yy5Y0b2qvzfvGn9LhJIZJrglfCm7ymP
|
||||
AbEVtQwdpf5pLGkkeB6zpxxxYu7KyJesF12KwvhHhm4qxFYxldBniYUr+WymXUad
|
||||
DKqC5JlR3XC321Y9YeRq4VzW9v493kHMB65jUr9TU/Qr6cf9tveCX4XSQRjbgbME
|
||||
HMUfpIBvFSDJ3gyICh3WZlXi/EjJKSZp4A==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDujCCAqKgAwIBAgILBAAAAAABD4Ym5g0wDQYJKoZIhvcNAQEFBQAwTDEgMB4G
|
||||
A1UECxMXR2xvYmFsU2lnbiBSb290IENBIC0gUjIxEzARBgNVBAoTCkdsb2JhbFNp
|
||||
Z24xEzARBgNVBAMTCkdsb2JhbFNpZ24wHhcNMDYxMjE1MDgwMDAwWhcNMjExMjE1
|
||||
MDgwMDAwWjBMMSAwHgYDVQQLExdHbG9iYWxTaWduIFJvb3QgQ0EgLSBSMjETMBEG
|
||||
A1UEChMKR2xvYmFsU2lnbjETMBEGA1UEAxMKR2xvYmFsU2lnbjCCASIwDQYJKoZI
|
||||
hvcNAQEBBQADggEPADCCAQoCggEBAKbPJA6+Lm8omUVCxKs+IVSbC9N/hHD6ErPL
|
||||
v4dfxn+G07IwXNb9rfF73OX4YJYJkhD10FPe+3t+c4isUoh7SqbKSaZeqKeMWhG8
|
||||
eoLrvozps6yWJQeXSpkqBy+0Hne/ig+1AnwblrjFuTosvNYSuetZfeLQBoZfXklq
|
||||
tTleiDTsvHgMCJiEbKjNS7SgfQx5TfC4LcshytVsW33hoCmEofnTlEnLJGKRILzd
|
||||
C9XZzPnqJworc5HGnRusyMvo4KD0L5CLTfuwNhv2GXqF4G3yYROIXJ/gkwpRl4pa
|
||||
zq+r1feqCapgvdzZX99yqWATXgAByUr6P6TqBwMhAo6CygPCm48CAwEAAaOBnDCB
|
||||
mTAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUm+IH
|
||||
V2ccHsBqBt5ZtJot39wZhi4wNgYDVR0fBC8wLTAroCmgJ4YlaHR0cDovL2NybC5n
|
||||
bG9iYWxzaWduLm5ldC9yb290LXIyLmNybDAfBgNVHSMEGDAWgBSb4gdXZxwewGoG
|
||||
3lm0mi3f3BmGLjANBgkqhkiG9w0BAQUFAAOCAQEAmYFThxxol4aR7OBKuEQLq4Gs
|
||||
J0/WwbgcQ3izDJr86iw8bmEbTUsp9Z8FHSbBuOmDAGJFtqkIk7mpM0sYmsL4h4hO
|
||||
291xNBrBVNpGP+DTKqttVCL1OmLNIG+6KYnX3ZHu01yiPqFbQfXf5WRDLenVOavS
|
||||
ot+3i9DAgBkcRcAtjOj4LaR0VknFBbVPFd5uRHg5h6h+u/N5GJG79G+dwfCMNYxd
|
||||
AfvDbbnvRG15RjF+Cv6pgsH/76tuIMRQyV+dTZsXjAzlAcmgQWpzU/qlULRuJQ/7
|
||||
TBj0/VLZjmmx6BEP3ojY+x1J96relc8geMJgEtslQIxq/H5COEBkEveegeGTLg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDXzCCAkegAwIBAgILBAAAAAABIVhTCKIwDQYJKoZIhvcNAQELBQAwTDEgMB4G
|
||||
A1UECxMXR2xvYmFsU2lnbiBSb290IENBIC0gUjMxEzARBgNVBAoTCkdsb2JhbFNp
|
||||
Z24xEzARBgNVBAMTCkdsb2JhbFNpZ24wHhcNMDkwMzE4MTAwMDAwWhcNMjkwMzE4
|
||||
MTAwMDAwWjBMMSAwHgYDVQQLExdHbG9iYWxTaWduIFJvb3QgQ0EgLSBSMzETMBEG
|
||||
A1UEChMKR2xvYmFsU2lnbjETMBEGA1UEAxMKR2xvYmFsU2lnbjCCASIwDQYJKoZI
|
||||
hvcNAQEBBQADggEPADCCAQoCggEBAMwldpB5BngiFvXAg7aEyiie/QV2EcWtiHL8
|
||||
RgJDx7KKnQRfJMsuS+FggkbhUqsMgUdwbN1k0ev1LKMPgj0MK66X17YUhhB5uzsT
|
||||
gHeMCOFJ0mpiLx9e+pZo34knlTifBtc+ycsmWQ1z3rDI6SYOgxXG71uL0gRgykmm
|
||||
KPZpO/bLyCiR5Z2KYVc3rHQU3HTgOu5yLy6c+9C7v/U9AOEGM+iCK65TpjoWc4zd
|
||||
QQ4gOsC0p6Hpsk+QLjJg6VfLuQSSaGjlOCZgdbKfd/+RFO+uIEn8rUAVSNECMWEZ
|
||||
XriX7613t2Saer9fwRPvm2L7DWzgVGkWqQPabumDk3F2xmmFghcCAwEAAaNCMEAw
|
||||
DgYDVR0PAQH/BAQDAgEGMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFI/wS3+o
|
||||
LkUkrk1Q+mOai97i3Ru8MA0GCSqGSIb3DQEBCwUAA4IBAQBLQNvAUKr+yAzv95ZU
|
||||
RUm7lgAJQayzE4aGKAczymvmdLm6AC2upArT9fHxD4q/c2dKg8dEe3jgr25sbwMp
|
||||
jjM5RcOO5LlXbKr8EpbsU8Yt5CRsuZRj+9xTaGdWPoO4zzUhw8lo/s7awlOqzJCK
|
||||
6fBdRoyV3XpYKBovHd7NADdBj+1EbddTKJd+82cEHhXXipa0095MJ6RMG3NzdvQX
|
||||
mcIfeg7jLQitChws/zyrVQ4PkX4268NXSb7hLi18YIvDQVETI53O9zJrlAGomecs
|
||||
Mx86OyXShkDOOyyGeMlhLxS67ttVb9+E7gUJTb0o2HLO02JQZR7rkpeDMdmztcpH
|
||||
WD9f
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIHSTCCBTGgAwIBAgIJAMnN0+nVfSPOMA0GCSqGSIb3DQEBBQUAMIGsMQswCQYD
|
||||
VQQGEwJFVTFDMEEGA1UEBxM6TWFkcmlkIChzZWUgY3VycmVudCBhZGRyZXNzIGF0
|
||||
IHd3dy5jYW1lcmZpcm1hLmNvbS9hZGRyZXNzKTESMBAGA1UEBRMJQTgyNzQzMjg3
|
||||
MRswGQYDVQQKExJBQyBDYW1lcmZpcm1hIFMuQS4xJzAlBgNVBAMTHkdsb2JhbCBD
|
||||
aGFtYmVyc2lnbiBSb290IC0gMjAwODAeFw0wODA4MDExMjMxNDBaFw0zODA3MzEx
|
||||
MjMxNDBaMIGsMQswCQYDVQQGEwJFVTFDMEEGA1UEBxM6TWFkcmlkIChzZWUgY3Vy
|
||||
cmVudCBhZGRyZXNzIGF0IHd3dy5jYW1lcmZpcm1hLmNvbS9hZGRyZXNzKTESMBAG
|
||||
A1UEBRMJQTgyNzQzMjg3MRswGQYDVQQKExJBQyBDYW1lcmZpcm1hIFMuQS4xJzAl
|
||||
BgNVBAMTHkdsb2JhbCBDaGFtYmVyc2lnbiBSb290IC0gMjAwODCCAiIwDQYJKoZI
|
||||
hvcNAQEBBQADggIPADCCAgoCggIBAMDfVtPkOpt2RbQT2//BthmLN0EYlVJH6xed
|
||||
KYiONWwGMi5HYvNJBL99RDaxccy9Wglz1dmFRP+RVyXfXjaOcNFccUMd2drvXNL7
|
||||
G706tcuto8xEpw2uIRU/uXpbknXYpBI4iRmKt4DS4jJvVpyR1ogQC7N0ZJJ0YPP2
|
||||
zxhPYLIj0Mc7zmFLmY/CDNBAspjcDahOo7kKrmCgrUVSY7pmvWjg+b4aqIG7HkF4
|
||||
ddPB/gBVsIdU6CeQNR1MM62X/JcumIS/LMmjv9GYERTtY/jKmIhYF5ntRQOXfjyG
|
||||
HoiMvvKRhI9lNNgATH23MRdaKXoKGCQwoze1eqkBfSbW+Q6OWfH9GzO1KTsXO0G2
|
||||
Id3UwD2ln58fQ1DJu7xsepeY7s2MH/ucUa6LcL0nn3HAa6x9kGbo1106DbDVwo3V
|
||||
yJ2dwW3Q0L9R5OP4wzg2rtandeavhENdk5IMagfeOx2YItaswTXbo6Al/3K1dh3e
|
||||
beksZixShNBFks4c5eUzHdwHU1SjqoI7mjcv3N2gZOnm3b2u/GSFHTynyQbehP9r
|
||||
6GsaPMWis0L7iwk+XwhSx2LE1AVxv8Rk5Pihg+g+EpuoHtQ2TS9x9o0o9oOpE9Jh
|
||||
wZG7SMA0j0GMS0zbaRL/UJScIINZc+18ofLx/d33SdNDWKBWY8o9PeU1VlnpDsog
|
||||
zCtLkykPAgMBAAGjggFqMIIBZjASBgNVHRMBAf8ECDAGAQH/AgEMMB0GA1UdDgQW
|
||||
BBS5CcqcHtvTbDprru1U8VuTBjUuXjCB4QYDVR0jBIHZMIHWgBS5CcqcHtvTbDpr
|
||||
ru1U8VuTBjUuXqGBsqSBrzCBrDELMAkGA1UEBhMCRVUxQzBBBgNVBAcTOk1hZHJp
|
||||
ZCAoc2VlIGN1cnJlbnQgYWRkcmVzcyBhdCB3d3cuY2FtZXJmaXJtYS5jb20vYWRk
|
||||
cmVzcykxEjAQBgNVBAUTCUE4Mjc0MzI4NzEbMBkGA1UEChMSQUMgQ2FtZXJmaXJt
|
||||
YSBTLkEuMScwJQYDVQQDEx5HbG9iYWwgQ2hhbWJlcnNpZ24gUm9vdCAtIDIwMDiC
|
||||
CQDJzdPp1X0jzjAOBgNVHQ8BAf8EBAMCAQYwPQYDVR0gBDYwNDAyBgRVHSAAMCow
|
||||
KAYIKwYBBQUHAgEWHGh0dHA6Ly9wb2xpY3kuY2FtZXJmaXJtYS5jb20wDQYJKoZI
|
||||
hvcNAQEFBQADggIBAICIf3DekijZBZRG/5BXqfEv3xoNa/p8DhxJJHkn2EaqbylZ
|
||||
UohwEurdPfWbU1Rv4WCiqAm57OtZfMY18dwY6fFn5a+6ReAJ3spED8IXDneRRXoz
|
||||
X1+WLGiLwUePmJs9wOzL9dWCkoQ10b42OFZyMVtHLaoXpGNR6woBrX/sdZ7LoR/x
|
||||
fxKxueRkf2fWIyr0uDldmOghp+G9PUIadJpwr2hsUF1Jz//7Dl3mLEfXgTpZALVz
|
||||
a2Mg9jFFCDkO9HB+QHBaP9BrQql0PSgvAm11cpUJjUhjxsYjV5KTXjXBjfkK9yyd
|
||||
Yhz2rXzdpjEetrHHfoUm+qRqtdpjMNHvkzeyZi99Bffnt0uYlDXA2TopwZ2yUDMd
|
||||
SqlapskD7+3056huirRXhOukP9DuqqqHW2Pok+JrqNS4cnhrG+055F3Lm6qH1U9O
|
||||
AP7Zap88MQ8oAgF9mOinsKJknnn4SPIVqczmyETrP3iZ8ntxPjzxmKfFGBI/5rso
|
||||
M0LpRQp8bfKGeS/Fghl9CYl8slR2iK7ewfPM4W7bMdaTrpmg7yVqc5iJWzouE4ge
|
||||
v8CSlDQb4ye3ix5vQv/n6TebUB0tovkC7stYWDpxvGjjqsGvHCgfotwjZT+B6q6Z
|
||||
09gwzxMNTxXJhLynSC34MCN32EZLeW32jO06f2ARePTpm67VVMB0gNELQp/B
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEADCCAuigAwIBAgIBADANBgkqhkiG9w0BAQUFADBjMQswCQYDVQQGEwJVUzEh
|
||||
MB8GA1UEChMYVGhlIEdvIERhZGR5IEdyb3VwLCBJbmMuMTEwLwYDVQQLEyhHbyBE
|
||||
YWRkeSBDbGFzcyAyIENlcnRpZmljYXRpb24gQXV0aG9yaXR5MB4XDTA0MDYyOTE3
|
||||
MDYyMFoXDTM0MDYyOTE3MDYyMFowYzELMAkGA1UEBhMCVVMxITAfBgNVBAoTGFRo
|
||||
ZSBHbyBEYWRkeSBHcm91cCwgSW5jLjExMC8GA1UECxMoR28gRGFkZHkgQ2xhc3Mg
|
||||
MiBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTCCASAwDQYJKoZIhvcNAQEBBQADggEN
|
||||
ADCCAQgCggEBAN6d1+pXGEmhW+vXX0iG6r7d/+TvZxz0ZWizV3GgXne77ZtJ6XCA
|
||||
PVYYYwhv2vLM0D9/AlQiVBDYsoHUwHU9S3/Hd8M+eKsaA7Ugay9qK7HFiH7Eux6w
|
||||
wdhFJ2+qN1j3hybX2C32qRe3H3I2TqYXP2WYktsqbl2i/ojgC95/5Y0V4evLOtXi
|
||||
EqITLdiOr18SPaAIBQi2XKVlOARFmR6jYGB0xUGlcmIbYsUfb18aQr4CUWWoriMY
|
||||
avx4A6lNf4DD+qta/KFApMoZFv6yyO9ecw3ud72a9nmYvLEHZ6IVDd2gWMZEewo+
|
||||
YihfukEHU1jPEX44dMX4/7VpkI+EdOqXG68CAQOjgcAwgb0wHQYDVR0OBBYEFNLE
|
||||
sNKR1EwRcbNhyz2h/t2oatTjMIGNBgNVHSMEgYUwgYKAFNLEsNKR1EwRcbNhyz2h
|
||||
/t2oatTjoWekZTBjMQswCQYDVQQGEwJVUzEhMB8GA1UEChMYVGhlIEdvIERhZGR5
|
||||
IEdyb3VwLCBJbmMuMTEwLwYDVQQLEyhHbyBEYWRkeSBDbGFzcyAyIENlcnRpZmlj
|
||||
YXRpb24gQXV0aG9yaXR5ggEAMAwGA1UdEwQFMAMBAf8wDQYJKoZIhvcNAQEFBQAD
|
||||
ggEBADJL87LKPpH8EsahB4yOd6AzBhRckB4Y9wimPQoZ+YeAEW5p5JYXMP80kWNy
|
||||
OO7MHAGjHZQopDH2esRU1/blMVgDoszOYtuURXO1v0XJJLXVggKtI3lpjbi2Tc7P
|
||||
TMozI+gciKqdi0FuFskg5YmezTvacPd+mSYgFFQlq25zheabIZ0KbIIOqPjCDPoQ
|
||||
HmyW74cNxA9hi63ugyuV+I6ShHI56yDqg+2DzZduCLzrTia2cyvk0/ZM/iZx4mER
|
||||
dEr/VxqHD3VILs9RaRegAhJhldXRQLIQTO7ErBBDpqWeCtWVYpoNz4iCxTIM5Cuf
|
||||
ReYNnyicsbkqWletNw+vHX/bvZ8=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDxTCCAq2gAwIBAgIBADANBgkqhkiG9w0BAQsFADCBgzELMAkGA1UEBhMCVVMx
|
||||
EDAOBgNVBAgTB0FyaXpvbmExEzARBgNVBAcTClNjb3R0c2RhbGUxGjAYBgNVBAoT
|
||||
EUdvRGFkZHkuY29tLCBJbmMuMTEwLwYDVQQDEyhHbyBEYWRkeSBSb290IENlcnRp
|
||||
ZmljYXRlIEF1dGhvcml0eSAtIEcyMB4XDTA5MDkwMTAwMDAwMFoXDTM3MTIzMTIz
|
||||
NTk1OVowgYMxCzAJBgNVBAYTAlVTMRAwDgYDVQQIEwdBcml6b25hMRMwEQYDVQQH
|
||||
EwpTY290dHNkYWxlMRowGAYDVQQKExFHb0RhZGR5LmNvbSwgSW5jLjExMC8GA1UE
|
||||
AxMoR28gRGFkZHkgUm9vdCBDZXJ0aWZpY2F0ZSBBdXRob3JpdHkgLSBHMjCCASIw
|
||||
DQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAL9xYgjx+lk09xvJGKP3gElY6SKD
|
||||
E6bFIEMBO4Tx5oVJnyfq9oQbTqC023CYxzIBsQU+B07u9PpPL1kwIuerGVZr4oAH
|
||||
/PMWdYA5UXvl+TW2dE6pjYIT5LY/qQOD+qK+ihVqf94Lw7YZFAXK6sOoBJQ7Rnwy
|
||||
DfMAZiLIjWltNowRGLfTshxgtDj6AozO091GB94KPutdfMh8+7ArU6SSYmlRJQVh
|
||||
GkSBjCypQ5Yj36w6gZoOKcUcqeldHraenjAKOc7xiID7S13MMuyFYkMlNAJWJwGR
|
||||
tDtwKj9useiciAF9n9T521NtYJ2/LOdYq7hfRvzOxBsDPAnrSTFcaUaz4EcCAwEA
|
||||
AaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYE
|
||||
FDqahQcQZyi27/a9BUFuIMGU2g/eMA0GCSqGSIb3DQEBCwUAA4IBAQCZ21151fmX
|
||||
WWcDYfF+OwYxdS2hII5PZYe096acvNjpL9DbWu7PdIxztDhC2gV7+AJ1uP2lsdeu
|
||||
9tfeE8tTEH6KRtGX+rcuKxGrkLAngPnon1rpN5+r5N9ss4UXnT3ZJE95kTXWXwTr
|
||||
gIOrmgIttRD02JDHBHNA7XIloKmf7J6raBKZV8aPEjoJpL1E/QYVN8Gb5DKj7Tjo
|
||||
2GTzLH4U/ALqn83/B2gX2yKQOC16jdFU8WnjXzPKej17CuPKf1855eJ1usV2GDPO
|
||||
LPAvTK33sefOT6jEm0pUBsV/fdUID+Ic/n4XuKxe9tQWskMJDE32p2u0mYRlynqI
|
||||
4uJEvlz36hz1
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICwzCCAkqgAwIBAgIBADAKBggqhkjOPQQDAjCBqjELMAkGA1UEBhMCR1IxDzAN
|
||||
BgNVBAcTBkF0aGVuczFEMEIGA1UEChM7SGVsbGVuaWMgQWNhZGVtaWMgYW5kIFJl
|
||||
c2VhcmNoIEluc3RpdHV0aW9ucyBDZXJ0LiBBdXRob3JpdHkxRDBCBgNVBAMTO0hl
|
||||
bGxlbmljIEFjYWRlbWljIGFuZCBSZXNlYXJjaCBJbnN0aXR1dGlvbnMgRUNDIFJv
|
||||
b3RDQSAyMDE1MB4XDTE1MDcwNzEwMzcxMloXDTQwMDYzMDEwMzcxMlowgaoxCzAJ
|
||||
BgNVBAYTAkdSMQ8wDQYDVQQHEwZBdGhlbnMxRDBCBgNVBAoTO0hlbGxlbmljIEFj
|
||||
YWRlbWljIGFuZCBSZXNlYXJjaCBJbnN0aXR1dGlvbnMgQ2VydC4gQXV0aG9yaXR5
|
||||
MUQwQgYDVQQDEztIZWxsZW5pYyBBY2FkZW1pYyBhbmQgUmVzZWFyY2ggSW5zdGl0
|
||||
dXRpb25zIEVDQyBSb290Q0EgMjAxNTB2MBAGByqGSM49AgEGBSuBBAAiA2IABJKg
|
||||
QehLgoRc4vgxEZmGZE4JJS+dQS8KrjVPdJWyUWRrjWvmP3CV8AVER6ZyOFB2lQJa
|
||||
jq4onvktTpnvLEhvTCUp6NFxW98dwXU3tNf6e3pCnGoKVlp8aQuqgAkkbH7BRqNC
|
||||
MEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFLQi
|
||||
C4KZJAEOnLvkDv2/+5cgk5kqMAoGCCqGSM49BAMCA2cAMGQCMGfOFmI4oqxiRaep
|
||||
lSTAGiecMjvAwNW6qef4BENThe5SId6d9SWDPp5YSy/XZxMOIQIwBeF1Ad5o7Sof
|
||||
TUwJCA3sS61kFyjndc5FZXIhF8siQQ6ME5g4mlRtm8rifOoCWCKR
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEMTCCAxmgAwIBAgIBADANBgkqhkiG9w0BAQUFADCBlTELMAkGA1UEBhMCR1Ix
|
||||
RDBCBgNVBAoTO0hlbGxlbmljIEFjYWRlbWljIGFuZCBSZXNlYXJjaCBJbnN0aXR1
|
||||
dGlvbnMgQ2VydC4gQXV0aG9yaXR5MUAwPgYDVQQDEzdIZWxsZW5pYyBBY2FkZW1p
|
||||
YyBhbmQgUmVzZWFyY2ggSW5zdGl0dXRpb25zIFJvb3RDQSAyMDExMB4XDTExMTIw
|
||||
NjEzNDk1MloXDTMxMTIwMTEzNDk1MlowgZUxCzAJBgNVBAYTAkdSMUQwQgYDVQQK
|
||||
EztIZWxsZW5pYyBBY2FkZW1pYyBhbmQgUmVzZWFyY2ggSW5zdGl0dXRpb25zIENl
|
||||
cnQuIEF1dGhvcml0eTFAMD4GA1UEAxM3SGVsbGVuaWMgQWNhZGVtaWMgYW5kIFJl
|
||||
c2VhcmNoIEluc3RpdHV0aW9ucyBSb290Q0EgMjAxMTCCASIwDQYJKoZIhvcNAQEB
|
||||
BQADggEPADCCAQoCggEBAKlTAOMupvaO+mDYLZU++CwqVE7NuYRhlFhPjz2L5EPz
|
||||
dYmNUeTDN9KKiE15HrcS3UN4SoqS5tdI1Q+kOilENbgH9mgdVc04UfCMJDGFr4PJ
|
||||
fel3r+0ae50X+bOdOFAPplp5kYCvN66m0zH7tSYJnTxa71HFK9+WXesyHgLacEns
|
||||
bgzImjeN9/E2YEsmLIKe0HjzDQ9jpFEw4fkrJxIH2Oq9GGKYsFk3fb7u8yBRQlqD
|
||||
75O6aRXxYp2fmTmCobd0LovUxQt7L/DICto9eQqakxylKHJzkUOap9FNhYS5qXSP
|
||||
FEDH3N6sQWRstBmbAmNtJGSPRLIl6s5ddAxjMlyNh+UCAwEAAaOBiTCBhjAPBgNV
|
||||
HRMBAf8EBTADAQH/MAsGA1UdDwQEAwIBBjAdBgNVHQ4EFgQUppFC/RNhSiOeCKQp
|
||||
5dgTBCPuQSUwRwYDVR0eBEAwPqA8MAWCAy5ncjAFggMuZXUwBoIELmVkdTAGggQu
|
||||
b3JnMAWBAy5ncjAFgQMuZXUwBoEELmVkdTAGgQQub3JnMA0GCSqGSIb3DQEBBQUA
|
||||
A4IBAQAf73lB4XtuP7KMhjdCSk4cNx6NZrokgclPEg8hwAOXhiVtXdMiKahsog2p
|
||||
6z0GW5k6x8zDmjR/qw7IThzh+uTczQ2+vyT+bOdrwg3IBp5OjWEopmr95fZi6hg8
|
||||
TqBTnbI6nOulnJEWtk2C4AwFSKls9cz4y51JtPACpf1wA+2KIaWuE4ZJwzNzvoc7
|
||||
dIsXRSZMFpGD/md9zU1jZ/rzAxKWeAaNsWftjj++n08C9bMJL/NMh98qy5V8Acys
|
||||
Nnq/onN694/BtZqhFLKPM58N7yLcZnuEvUUXBj08yrl3NI/K6s8/MT7jiOOASSXI
|
||||
l7WdmplNsDz4SgCbZN2fOUvRJ9e4
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIGCzCCA/OgAwIBAgIBADANBgkqhkiG9w0BAQsFADCBpjELMAkGA1UEBhMCR1Ix
|
||||
DzANBgNVBAcTBkF0aGVuczFEMEIGA1UEChM7SGVsbGVuaWMgQWNhZGVtaWMgYW5k
|
||||
IFJlc2VhcmNoIEluc3RpdHV0aW9ucyBDZXJ0LiBBdXRob3JpdHkxQDA+BgNVBAMT
|
||||
N0hlbGxlbmljIEFjYWRlbWljIGFuZCBSZXNlYXJjaCBJbnN0aXR1dGlvbnMgUm9v
|
||||
dENBIDIwMTUwHhcNMTUwNzA3MTAxMTIxWhcNNDAwNjMwMTAxMTIxWjCBpjELMAkG
|
||||
A1UEBhMCR1IxDzANBgNVBAcTBkF0aGVuczFEMEIGA1UEChM7SGVsbGVuaWMgQWNh
|
||||
ZGVtaWMgYW5kIFJlc2VhcmNoIEluc3RpdHV0aW9ucyBDZXJ0LiBBdXRob3JpdHkx
|
||||
QDA+BgNVBAMTN0hlbGxlbmljIEFjYWRlbWljIGFuZCBSZXNlYXJjaCBJbnN0aXR1
|
||||
dGlvbnMgUm9vdENBIDIwMTUwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoIC
|
||||
AQDC+Kk/G4n8PDwEXT2QNrCROnk8ZlrvbTkBSRq0t89/TSNTt5AA4xMqKKYx8ZEA
|
||||
4yjsriFBzh/a/X0SWwGDD7mwX5nh8hKDgE0GPt+sr+ehiGsxr/CL0BgzuNtFajT0
|
||||
AoAkKAoCFZVedioNmToUW/bLy1O8E00BiDeUJRtCvCLYjqOWXjrZMts+6PAQZe10
|
||||
4S+nfK8nNLspfZu2zwnI5dMK/IhlZXQK3HMcXM1AsRzUtoSMTFDPaI6oWa7CJ06C
|
||||
ojXdFPQf/7J31Ycvqm59JCfnxssm5uX+Zwdj2EUN3TpZZTlYepKZcj2chF6IIbjV
|
||||
9Cz82XBST3i4vTwri5WY9bPRaM8gFH5MXF/ni+X1NYEZN9cRCLdmvtNKzoNXADrD
|
||||
gfgXy5I2XdGj2HUb4Ysn6npIQf1FGQatJ5lOwXBH3bWfgVMS5bGMSF0xQxfjjMZ6
|
||||
Y5ZLKTBOhE5iGV48zpeQpX8B653g+IuJ3SWYPZK2fu/Z8VFRfS0myGlZYeCsargq
|
||||
NhEEelC9MoS+L9xy1dcdFkfkR2YgP/SWxa+OAXqlD3pk9Q0Yh9muiNX6hME6wGko
|
||||
LfINaFGq46V3xqSQDqE3izEjR8EJCOtu93ib14L8hCCZSRm2Ekax+0VVFqmjZayc
|
||||
Bw/qa9wfLgZy7IaIEuQt218FL+TwA9MmM+eAws1CoRc0CwIDAQABo0IwQDAPBgNV
|
||||
HRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIBBjAdBgNVHQ4EFgQUcRVnyMjJvXVd
|
||||
ctA4GGqd83EkVAswDQYJKoZIhvcNAQELBQADggIBAHW7bVRLqhBYRjTyYtcWNl0I
|
||||
XtVsyIe9tC5G8jH4fOpCtZMWVdyhDBKg2mF+D1hYc2Ryx+hFjtyp8iY/xnmMsVMI
|
||||
M4GwVhO+5lFc2JsKT0ucVlMC6U/2DWDqTUJV6HwbISHTGzrMd/K4kPFox/la/vot
|
||||
9L/J9UUbzjgQKjeKeaO04wlshYaT/4mWJ3iBj2fjRnRUjtkNaeJK9E10A/+yd+2V
|
||||
Z5fkscWrv2oj6NSU4kQoYsRL4vDY4ilrGnB+JGGTe08DMiUNRSQrlrRGar9KC/ea
|
||||
j8GsGsVn82800vpzY4zvFrCopEYq+OsS7HK07/grfoxSwIuEVPkvPuNVqNxmsdnh
|
||||
X9izjFk0WaSrT2y7HxjbdavYy5LNlDhhDgcGH0tGEPEVvo2FXDtKK4F5D7Rpn0lQ
|
||||
l033DlZdwJVqwjbDG2jJ9SrcR5q+ss7FJej6A7na+RZukYT1HCjI/CbM1xyQVqdf
|
||||
bzoEvM14iQuODy+jqk+iGxI9FghAD/FGTNeqewjBCvVtJ94Cj8rDtSvK6evIIVM4
|
||||
pcw72Hc3MKJP2W/R8kCtQXoXxdZKNYm3QdV8hn9VTYNKpXMgwDqvkPGaJI7ZjnHK
|
||||
e7iG2rKPmT4dEw0SEe7Uq/DpFXYC5ODfqiAeW2GFZECpkJcNrVPSWh2HagCXZWK0
|
||||
vm9qp/UsQu0yrbYhnr68
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDMDCCAhigAwIBAgICA+gwDQYJKoZIhvcNAQEFBQAwRzELMAkGA1UEBhMCSEsx
|
||||
FjAUBgNVBAoTDUhvbmdrb25nIFBvc3QxIDAeBgNVBAMTF0hvbmdrb25nIFBvc3Qg
|
||||
Um9vdCBDQSAxMB4XDTAzMDUxNTA1MTMxNFoXDTIzMDUxNTA0NTIyOVowRzELMAkG
|
||||
A1UEBhMCSEsxFjAUBgNVBAoTDUhvbmdrb25nIFBvc3QxIDAeBgNVBAMTF0hvbmdr
|
||||
b25nIFBvc3QgUm9vdCBDQSAxMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKC
|
||||
AQEArP84tulmAknjorThkPlAj3n54r15/gK97iSSHSL22oVyaf7XPwnU3ZG1ApzQ
|
||||
jVrhVcNQhrkpJsLj2aDxaQMoIIBFIi1WpztUlVYiWR8o3x8gPW2iNr4joLFutbEn
|
||||
PzlTCeqrauh0ssJlXI6/fMN4hM2eFvz1Lk8gKgifd/PFHsSaUmYeSF7jEAaPIpjh
|
||||
ZY4bXSNmO7ilMlHIhqqhqZ5/dpTCpmy3QfDVyAY45tQM4vM7TG1QjMSDJ8EThFk9
|
||||
nnV0ttgCXjqQesBCNnLsak3c78QA3xMYV18meMjWCnl3v/evt3a5pQuEF10Q6m/h
|
||||
q5URX208o1xNg1vysxmKgIsLhwIDAQABoyYwJDASBgNVHRMBAf8ECDAGAQH/AgED
|
||||
MA4GA1UdDwEB/wQEAwIBxjANBgkqhkiG9w0BAQUFAAOCAQEADkbVPK7ih9legYsC
|
||||
mEEIjEy82tvuJxuC52pF7BaLT4Wg87JwvVqWuspube5Gi27nKi6Wsxkz67SfqLI3
|
||||
7piol7Yutmcn1KZJ/RyTZXaeQi/cImyaT/JaFTmxcdcrUehtHJjA2Sr0oYJ71clB
|
||||
oiMBdDhViw+5LmeiIAQ32pwL0xch4I+XeTRvhEgCIDMb5jREn5Fw9IBehEPCKdJs
|
||||
EhTkYY2sEJCehFC78JZvRZ+K88psT/oROhUVRsPNH4NbLUES7VBnQRM9IauUiqpO
|
||||
fMGx+6fWtScvl6tu4B3i0RwsH0Ti/L6RoZz71ilTc4afU9hDDl3WY4JxHYB0yvbi
|
||||
AmvZWg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFazCCA1OgAwIBAgIRAIIQz7DSQONZRGPgu2OCiwAwDQYJKoZIhvcNAQELBQAw
|
||||
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
|
||||
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTUwNjA0MTEwNDM4
|
||||
WhcNMzUwNjA0MTEwNDM4WjBPMQswCQYDVQQGEwJVUzEpMCcGA1UEChMgSW50ZXJu
|
||||
ZXQgU2VjdXJpdHkgUmVzZWFyY2ggR3JvdXAxFTATBgNVBAMTDElTUkcgUm9vdCBY
|
||||
MTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAK3oJHP0FDfzm54rVygc
|
||||
h77ct984kIxuPOZXoHj3dcKi/vVqbvYATyjb3miGbESTtrFj/RQSa78f0uoxmyF+
|
||||
0TM8ukj13Xnfs7j/EvEhmkvBioZxaUpmZmyPfjxwv60pIgbz5MDmgK7iS4+3mX6U
|
||||
A5/TR5d8mUgjU+g4rk8Kb4Mu0UlXjIB0ttov0DiNewNwIRt18jA8+o+u3dpjq+sW
|
||||
T8KOEUt+zwvo/7V3LvSye0rgTBIlDHCNAymg4VMk7BPZ7hm/ELNKjD+Jo2FR3qyH
|
||||
B5T0Y3HsLuJvW5iB4YlcNHlsdu87kGJ55tukmi8mxdAQ4Q7e2RCOFvu396j3x+UC
|
||||
B5iPNgiV5+I3lg02dZ77DnKxHZu8A/lJBdiB3QW0KtZB6awBdpUKD9jf1b0SHzUv
|
||||
KBds0pjBqAlkd25HN7rOrFleaJ1/ctaJxQZBKT5ZPt0m9STJEadao0xAH0ahmbWn
|
||||
OlFuhjuefXKnEgV4We0+UXgVCwOPjdAvBbI+e0ocS3MFEvzG6uBQE3xDk3SzynTn
|
||||
jh8BCNAw1FtxNrQHusEwMFxIt4I7mKZ9YIqioymCzLq9gwQbooMDQaHWBfEbwrbw
|
||||
qHyGO0aoSCqI3Haadr8faqU9GY/rOPNk3sgrDQoo//fb4hVC1CLQJ13hef4Y53CI
|
||||
rU7m2Ys6xt0nUW7/vGT1M0NPAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNV
|
||||
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBR5tFnme7bl5AFzgAiIyBpY9umbbjANBgkq
|
||||
hkiG9w0BAQsFAAOCAgEAVR9YqbyyqFDQDLHYGmkgJykIrGF1XIpu+ILlaS/V9lZL
|
||||
ubhzEFnTIZd+50xx+7LSYK05qAvqFyFWhfFQDlnrzuBZ6brJFe+GnY+EgPbk6ZGQ
|
||||
3BebYhtF8GaV0nxvwuo77x/Py9auJ/GpsMiu/X1+mvoiBOv/2X/qkSsisRcOj/KK
|
||||
NFtY2PwByVS5uCbMiogziUwthDyC3+6WVwW6LLv3xLfHTjuCvjHIInNzktHCgKQ5
|
||||
ORAzI4JMPJ+GslWYHb4phowim57iaztXOoJwTdwJx4nLCgdNbOhdjsnvzqvHu7Ur
|
||||
TkXWStAmzOVyyghqpZXjFaH3pO3JLF+l+/+sKAIuvtd7u+Nxe5AW0wdeRlN8NwdC
|
||||
jNPElpzVmbUq4JUagEiuTDkHzsxHpFKVK7q4+63SM1N95R1NbdWhscdCb+ZAJzVc
|
||||
oyi3B43njTOQ5yOf+1CceWxG1bQVs5ZufpsMljq4Ui0/1lvh+wjChP4kqKOJ2qxq
|
||||
4RgqsahDYVvTH9w7jXbyLeiNdd8XM2w9U/t7y0Ff/9yi0GE44Za4rF2LN9d11TPA
|
||||
mRGunUHBcnWEvgJBQl9nJEiU0Zsnvgc/ubhPgXRR4Xq37Z0j4r7g1SgEEzwxA57d
|
||||
emyPxgcYxn/eR44/KJ4EBs+lVDR3veyJm+kXQ99b21/+jh5Xos1AnX5iItreGCc=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFYDCCA0igAwIBAgIQCgFCgAAAAUUjyES1AAAAAjANBgkqhkiG9w0BAQsFADBK
|
||||
MQswCQYDVQQGEwJVUzESMBAGA1UEChMJSWRlblRydXN0MScwJQYDVQQDEx5JZGVu
|
||||
VHJ1c3QgQ29tbWVyY2lhbCBSb290IENBIDEwHhcNMTQwMTE2MTgxMjIzWhcNMzQw
|
||||
MTE2MTgxMjIzWjBKMQswCQYDVQQGEwJVUzESMBAGA1UEChMJSWRlblRydXN0MScw
|
||||
JQYDVQQDEx5JZGVuVHJ1c3QgQ29tbWVyY2lhbCBSb290IENBIDEwggIiMA0GCSqG
|
||||
SIb3DQEBAQUAA4ICDwAwggIKAoICAQCnUBneP5k91DNG8W9RYYKyqU+PZ4ldhNlT
|
||||
3Qwo2dfw/66VQ3KZ+bVdfIrBQuExUHTRgQ18zZshq0PirK1ehm7zCYofWjK9ouuU
|
||||
+ehcCuz/mNKvcbO0U59Oh++SvL3sTzIwiEsXXlfEU8L2ApeN2WIrvyQfYo3fw7gp
|
||||
S0l4PJNgiCL8mdo2yMKi1CxUAGc1bnO/AljwpN3lsKImesrgNqUZFvX9t++uP0D1
|
||||
bVoE/c40yiTcdCMbXTMTEl3EASX2MN0CXZ/g1Ue9tOsbobtJSdifWwLziuQkkORi
|
||||
T0/Br4sOdBeo0XKIanoBScy0RnnGF7HamB4HWfp1IYVl3ZBWzvurpWCdxJ35UrCL
|
||||
vYf5jysjCiN2O/cz4ckA82n5S6LgTrx+kzmEB/dEcH7+B1rlsazRGMzyNeVJSQjK
|
||||
Vsk9+w8YfYs7wRPCTY/JTw436R+hDmrfYi7LNQZReSzIJTj0+kuniVyc0uMNOYZK
|
||||
dHzVWYfCP04MXFL0PfdSgvHqo6z9STQaKPNBiDoT7uje/5kdX7rL6B7yuVBgwDHT
|
||||
c+XvvqDtMwt0viAgxGds8AgDelWAf0ZOlqf0Hj7h9tgJ4TNkK2PXMl6f+cB7D3hv
|
||||
l7yTmvmcEpB4eoCHFddydJxVdHixuuFucAS6T6C6aMN7/zHwcz09lCqxC0EOoP5N
|
||||
iGVreTO01wIDAQABo0IwQDAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB
|
||||
/zAdBgNVHQ4EFgQU7UQZwNPwBovupHu+QucmVMiONnYwDQYJKoZIhvcNAQELBQAD
|
||||
ggIBAA2ukDL2pkt8RHYZYR4nKM1eVO8lvOMIkPkp165oCOGUAFjvLi5+U1KMtlwH
|
||||
6oi6mYtQlNeCgN9hCQCTrQ0U5s7B8jeUeLBfnLOic7iPBZM4zY0+sLj7wM+x8uwt
|
||||
LRvM7Kqas6pgghstO8OEPVeKlh6cdbjTMM1gCIOQ045U8U1mwF10A0Cj7oV+wh93
|
||||
nAbowacYXVKV7cndJZ5t+qntozo00Fl72u1Q8zW/7esUTTHHYPTa8Yec4kjixsU3
|
||||
+wYQ+nVZZjFHKdp2mhzpgq7vmrlR94gjmmmVYjzlVYA211QC//G5Xc7UI2/YRYRK
|
||||
W2XviQzdFKcgyxilJbQN+QHwotL0AMh0jqEqSI5l2xPE4iUXfeu+h1sXIFRRk0pT
|
||||
AwvsXcoz7WL9RccvW9xYoIA55vrX/hMUpu09lEpCdNTDd1lzzY9GvlU47/rokTLq
|
||||
l1gEIt44w8y8bckzOmoKaT+gyOpyj4xjhiO9bTyWnpXgSUyqorkqG5w2gXjtw+hG
|
||||
4iZZRHUe2XWJUc0QhJ1hYMtd+ZciTY6Y5uN/9lu7rs3KSoFrXgvzUeF0K+l+J6fZ
|
||||
mUlO+KWA2yUPHGNiiskzZ2s8EIPGrd6ozRaOjfAHN3Gf8qv8QfXBi+wAN10J5U6A
|
||||
7/qxXDgGpRtK4dw4LTzcqx+QGtVKnO7RcGzM7vRX+Bi6hG6H
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFZjCCA06gAwIBAgIQCgFCgAAAAUUjz0Z8AAAAAjANBgkqhkiG9w0BAQsFADBN
|
||||
MQswCQYDVQQGEwJVUzESMBAGA1UEChMJSWRlblRydXN0MSowKAYDVQQDEyFJZGVu
|
||||
VHJ1c3QgUHVibGljIFNlY3RvciBSb290IENBIDEwHhcNMTQwMTE2MTc1MzMyWhcN
|
||||
MzQwMTE2MTc1MzMyWjBNMQswCQYDVQQGEwJVUzESMBAGA1UEChMJSWRlblRydXN0
|
||||
MSowKAYDVQQDEyFJZGVuVHJ1c3QgUHVibGljIFNlY3RvciBSb290IENBIDEwggIi
|
||||
MA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQC2IpT8pEiv6EdrCvsnduTyP4o7
|
||||
ekosMSqMjbCpwzFrqHd2hCa2rIFCDQjrVVi7evi8ZX3yoG2LqEfpYnYeEe4IFNGy
|
||||
RBb06tD6Hi9e28tzQa68ALBKK0CyrOE7S8ItneShm+waOh7wCLPQ5CQ1B5+ctMlS
|
||||
bdsHyo+1W/CD80/HLaXIrcuVIKQxKFdYWuSNG5qrng0M8gozOSI5Cpcu81N3uURF
|
||||
/YTLNiCBWS2ab21ISGHKTN9T0a9SvESfqy9rg3LvdYDaBjMbXcjaY8ZNzaxmMc3R
|
||||
3j6HEDbhuaR672BQssvKplbgN6+rNBM5Jeg5ZuSYeqoSmJxZZoY+rfGwyj4GD3vw
|
||||
EUs3oERte8uojHH01bWRNszwFcYr3lEXsZdMUD2xlVl8BX0tIdUAvwFnol57plzy
|
||||
9yLxkA2T26pEUWbMfXYD62qoKjgZl3YNa4ph+bz27nb9cCvdKTz4Ch5bQhyLVi9V
|
||||
GxyhLrXHFub4qjySjmm2AcG1hp2JDws4lFTo6tyePSW8Uybt1as5qsVATFSrsrTZ
|
||||
2fjXctscvG29ZV/viDUqZi/u9rNl8DONfJhBaUYPQxxp+pu10GFqzcpL2UyQRqsV
|
||||
WaFHVCkugyhfHMKiq3IXAAaOReyL4jM9f9oZRORicsPfIsbyVtTdX5Vy7W1f90gD
|
||||
W/3FKqD2cyOEEBsB5wIDAQABo0IwQDAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/
|
||||
BAUwAwEB/zAdBgNVHQ4EFgQU43HgntinQtnbcZFrlJPrw6PRFKMwDQYJKoZIhvcN
|
||||
AQELBQADggIBAEf63QqwEZE4rU1d9+UOl1QZgkiHVIyqZJnYWv6IAcVYpZmxI1Qj
|
||||
t2odIFflAWJBF9MJ23XLblSQdf4an4EKwt3X9wnQW3IV5B4Jaj0z8yGa5hV+rVHV
|
||||
DRDtfULAj+7AmgjVQdZcDiFpboBhDhXAuM/FSRJSzL46zNQuOAXeNf0fb7iAaJg9
|
||||
TaDKQGXSc3z1i9kKlT/YPyNtGtEqJBnZhbMX73huqVjRI9PHE+1yJX9dsXNw0H8G
|
||||
lwmEKYBhHfpe/3OsoOOJuBxxFcbeMX8S3OFtm6/n6J91eEyrRjuazr8FGF1NFTwW
|
||||
mhlQBJqymm9li1JfPFgEKCXAZmExfrngdbkaqIHWchezxQMxNRF4eKLg6TCMf4Df
|
||||
WN88uieW4oA0beOY02QnrEh+KHdcxiVhJfiFDGX6xDIvpZgF5PgLZxYWxoK4Mhn5
|
||||
+bl53B/N66+rDt0b20XkeucC4pVd/GnwU2lhlXV5C15V5jgclKlZM57IcXR5f1GJ
|
||||
tshquDDIajjDbp7hNxbqBWJMWxJH7ae0s1hWx0nzfxJoCTFx8G34Tkf71oXuxVhA
|
||||
GaQdp/lLQzfcaFpPz+vCZHTetBXZ9FRUGi8c15dxVJCO2SCdUyt/q4/i6jC8UDfv
|
||||
8Ue1fXwsBOxonbRJRBD0ckscZOf85muQ3Wl9af0AVqW3rLatt8o+Ae+c
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF8TCCA9mgAwIBAgIQALC3WhZIX7/hy/WL1xnmfTANBgkqhkiG9w0BAQsFADA4
|
||||
MQswCQYDVQQGEwJFUzEUMBIGA1UECgwLSVpFTlBFIFMuQS4xEzARBgNVBAMMCkl6
|
||||
ZW5wZS5jb20wHhcNMDcxMjEzMTMwODI4WhcNMzcxMjEzMDgyNzI1WjA4MQswCQYD
|
||||
VQQGEwJFUzEUMBIGA1UECgwLSVpFTlBFIFMuQS4xEzARBgNVBAMMCkl6ZW5wZS5j
|
||||
b20wggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDJ03rKDx6sp4boFmVq
|
||||
scIbRTJxldn+EFvMr+eleQGPicPK8lVx93e+d5TzcqQsRNiekpsUOqHnJJAKClaO
|
||||
xdgmlOHZSOEtPtoKct2jmRXagaKH9HtuJneJWK3W6wyyQXpzbm3benhB6QiIEn6H
|
||||
LmYRY2xU+zydcsC8Lv/Ct90NduM61/e0aL6i9eOBbsFGb12N4E3GVFWJGjMxCrFX
|
||||
uaOKmMPsOzTFlUFpfnXCPCDFYbpRR6AgkJOhkEvzTnyFRVSa0QUmQbC1TR0zvsQD
|
||||
yCV8wXDbO/QJLVQnSKwv4cSsPsjLkkxTOTcj7NMB+eAJRE1NZMDhDVqHIrytG6P+
|
||||
JrUV86f8hBnp7KGItERphIPzidF0BqnMC9bC3ieFUCbKF7jJeodWLBoBHmy+E60Q
|
||||
rLUk9TiRodZL2vG70t5HtfG8gfZZa88ZU+mNFctKy6lvROUbQc/hhqfK0GqfvEyN
|
||||
BjNaooXlkDWgYlwWTvDjovoDGrQscbNYLN57C9saD+veIR8GdwYDsMnvmfzAuU8L
|
||||
hij+0rnq49qlw0dpEuDb8PYZi+17cNcC1u2HGCgsBCRMd+RIihrGO5rUD8r6ddIB
|
||||
QFqNeb+Lz0vPqhbBleStTIo+F5HUsWLlguWABKQDfo2/2n+iD5dPDNMN+9fR5XJ+
|
||||
HMh3/1uaD7euBUbl8agW7EekFwIDAQABo4H2MIHzMIGwBgNVHREEgagwgaWBD2lu
|
||||
Zm9AaXplbnBlLmNvbaSBkTCBjjFHMEUGA1UECgw+SVpFTlBFIFMuQS4gLSBDSUYg
|
||||
QTAxMzM3MjYwLVJNZXJjLlZpdG9yaWEtR2FzdGVpeiBUMTA1NSBGNjIgUzgxQzBB
|
||||
BgNVBAkMOkF2ZGEgZGVsIE1lZGl0ZXJyYW5lbyBFdG9yYmlkZWEgMTQgLSAwMTAx
|
||||
MCBWaXRvcmlhLUdhc3RlaXowDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMC
|
||||
AQYwHQYDVR0OBBYEFB0cZQ6o8iV7tJHP5LGx5r1VdGwFMA0GCSqGSIb3DQEBCwUA
|
||||
A4ICAQB4pgwWSp9MiDrAyw6lFn2fuUhfGI8NYjb2zRlrrKvV9pF9rnHzP7MOeIWb
|
||||
laQnIUdCSnxIOvVFfLMMjlF4rJUT3sb9fbgakEyrkgPH7UIBzg/YsfqikuFgba56
|
||||
awmqxinuaElnMIAkejEWOVt+8Rwu3WwJrfIxwYJOubv5vr8qhT/AQKM6WfxZSzwo
|
||||
JNu0FXWuDYi6LnPAvViH5ULy617uHjAimcs30cQhbIHsvm0m5hzkQiCeR7Csg1lw
|
||||
LDXWrzY0tM07+DKo7+N4ifuNRSzanLh+QBxh5z6ikixL8s36mLYp//Pye6kfLqCT
|
||||
VyvehQP5aTfLnnhqBbTFMXiJ7HqnheG5ezzevh55hM6fcA5ZwjUukCox2eRFekGk
|
||||
LhObNA5me0mrZJfQRsN5nXJQY6aYWwa9SG3YOYNw6DXwBdGqvOPbyALqfP2C2sJb
|
||||
UjWumDqtujWTI6cfSN01RpiyEGjkpTHCClguGYEQyVB1/OpaFs4R1+7vUIgtYf8/
|
||||
QnMFlEPVjjxOAToZpR9GTnfQXeWBIiGH/pR9hNiTrdZoQ0iy2+tzJOeRf1SktoA+
|
||||
naM8THLCV8Sg1Mw4J87VBp6iSNnpn86CcDaTmjvfliHjWbcM2pE38P1ZWrOZyGls
|
||||
QyYBNWNgVYkDOnXYukrZVP/u3oDYLdE41V4tC5h9Pmzb/CaIxw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFwzCCA6ugAwIBAgIUCn6m30tEntpqJIWe5rgV0xZ/u7EwDQYJKoZIhvcNAQEL
|
||||
BQAwRjELMAkGA1UEBhMCTFUxFjAUBgNVBAoMDUx1eFRydXN0IFMuQS4xHzAdBgNV
|
||||
BAMMFkx1eFRydXN0IEdsb2JhbCBSb290IDIwHhcNMTUwMzA1MTMyMTU3WhcNMzUw
|
||||
MzA1MTMyMTU3WjBGMQswCQYDVQQGEwJMVTEWMBQGA1UECgwNTHV4VHJ1c3QgUy5B
|
||||
LjEfMB0GA1UEAwwWTHV4VHJ1c3QgR2xvYmFsIFJvb3QgMjCCAiIwDQYJKoZIhvcN
|
||||
AQEBBQADggIPADCCAgoCggIBANeFl78RmOnwYoNMPIf5U2o3C/IPPIfOb9wmKb3F
|
||||
ibrJgz337spbxm1Jc7TJRqMbNBM/wYlFV/TZsfs2ZUv7COJIcRHIbjuend+JZTem
|
||||
hfY7RBi2xjcwYkSSl2l9QjAk5A0MiWtj3sXh306pFGxT4GHO9hcvHTy95iJMHZP1
|
||||
EMShduxq3sVs35a0VkBCwGKSMKEtFZSg0iAGCW5qbeXrt77U8PEVfIvmTroTzEsn
|
||||
Xpk8F12PgX8zPU/TPxvsXD/wPEx1bvKm1Z3aLQdjAsZy6ZS8TEmVT4hSyNvoaYL4
|
||||
zDRbIvCGp4m9SAptZoFtyMhk+wHh9OHe2Z7d21vUKpkmFRseTJIpgp7VkoGSQXAZ
|
||||
96Tlk0u8d2cx3Rz9MXANF5kM+Qw5GSoXtTBxVdUPrljhPS80m8+f9niFwpN6cj5m
|
||||
j5wWEWCPnolvZ77gR1o7DJpni89Gxq44o/KnvObWhWszJHAiS8sIm7vI+AIpHb4g
|
||||
DEa/a4ebsypmQjVGbKq6rfmYe+lQVRQxv7HaLe2ArWgk+2mr2HETMOZns4dA/Yl+
|
||||
8kPREd8vZS9kzl8UubG/Mb2HeFpZZYiq/FkySIbWTLkpS5XTdvN3JW1CHDiDTf2j
|
||||
X5t/Lax5Gw5CMZdjpPuKadUiDTSQMC6otOBttpSsvItO13D8xTiOZCXhTTmQzsmH
|
||||
hFhxAgMBAAGjgagwgaUwDwYDVR0TAQH/BAUwAwEB/zBCBgNVHSAEOzA5MDcGByuB
|
||||
KwEBAQowLDAqBggrBgEFBQcCARYeaHR0cHM6Ly9yZXBvc2l0b3J5Lmx1eHRydXN0
|
||||
Lmx1MA4GA1UdDwEB/wQEAwIBBjAfBgNVHSMEGDAWgBT/GCh2+UgFLKGu8SsbK7JT
|
||||
+Et8szAdBgNVHQ4EFgQU/xgodvlIBSyhrvErGyuyU/hLfLMwDQYJKoZIhvcNAQEL
|
||||
BQADggIBAGoZFO1uecEsh9QNcH7X9njJCwROxLHOk3D+sFTAMs2ZMGQXvw/l4jP9
|
||||
BzZAcg4atmpZ1gDlaCDdLnINH2pkMSCEfUmmWjfrRcmF9dTHF5kH5ptV5AzoqbTO
|
||||
jFu1EVzPig4N1qx3gf4ynCSecs5U89BvolbW7MM3LGVYvlcAGvI1+ut7MV3CwRI9
|
||||
loGIlonBWVx65n9wNOeD4rHh4bhY79SV5GCc8JaXcozrhAIuZY+kt9J/Z93I055c
|
||||
qqmkoCUUBpvsT34tC38ddfEz2O3OuHVtPlu5mB0xDVbYQw8wkbIEa91WvpWAVWe+
|
||||
2M2D2RjuLg+GLZKecBPs3lHJQ3gCpU3I+V/EkVhGFndadKpAvAefMLmx9xIX3eP/
|
||||
JEAdemrRTxgKqpAd60Ae36EeRJIQmvKN4dFLRp7oRUKX6kWZ8+xm1QL68qZKJKre
|
||||
zrnK+T+Tb/mjuuqlPpmt/f97mfVl7vBZKGfXkJWkE4SphMHozs51k2MavDzq1WQf
|
||||
LSoSOcbDWjLtR5EWDrw4wVDej8oqkDQc7kGUnF4ZLvhFSZl0kbAEb+MEWrGrKqv+
|
||||
x9CWttrhSmQGbmBNvUJO/3jaJMobtNeWOWyu8Q6qp31IiyBMz2TWuJdGsE7RKlY6
|
||||
oJO9r4Ak4Ap+58rVyuiFVdw2KuGUaJPHZnJED4AhMmwlxyOAgwrr
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIECjCCAvKgAwIBAgIJAMJ+QwRORz8ZMA0GCSqGSIb3DQEBCwUAMIGCMQswCQYD
|
||||
VQQGEwJIVTERMA8GA1UEBwwIQnVkYXBlc3QxFjAUBgNVBAoMDU1pY3Jvc2VjIEx0
|
||||
ZC4xJzAlBgNVBAMMHk1pY3Jvc2VjIGUtU3ppZ25vIFJvb3QgQ0EgMjAwOTEfMB0G
|
||||
CSqGSIb3DQEJARYQaW5mb0BlLXN6aWduby5odTAeFw0wOTA2MTYxMTMwMThaFw0y
|
||||
OTEyMzAxMTMwMThaMIGCMQswCQYDVQQGEwJIVTERMA8GA1UEBwwIQnVkYXBlc3Qx
|
||||
FjAUBgNVBAoMDU1pY3Jvc2VjIEx0ZC4xJzAlBgNVBAMMHk1pY3Jvc2VjIGUtU3pp
|
||||
Z25vIFJvb3QgQ0EgMjAwOTEfMB0GCSqGSIb3DQEJARYQaW5mb0BlLXN6aWduby5o
|
||||
dTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAOn4j/NjrdqG2KfgQvvP
|
||||
kd6mJviZpWNwrZuuyjNAfW2WbqEORO7hE52UQlKavXWFdCyoDh2Tthi3jCyoz/tc
|
||||
cbna7P7ofo/kLx2yqHWH2Leh5TvPmUpG0IMZfcChEhyVbUr02MelTTMuhTlAdX4U
|
||||
fIASmFDHQWe4oIBhVKZsTh/gnQ4H6cm6M+f+wFUoLAKApxn1ntxVUwOXewdI/5n7
|
||||
N4okxFnMUBBjjqqpGrCEGob5X7uxUG6k0QrM1XF+H6cbfPVTbiJfyyvm1HxdrtbC
|
||||
xkzlBQHZ7Vf8wSN5/PrIJIOV87VqUQHQd9bpEqH5GoP7ghu5sJf0dgYzQ0mg/wu1
|
||||
+rUCAwEAAaOBgDB+MA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgEGMB0G
|
||||
A1UdDgQWBBTLD8bfQkPMPcu1SCOhGnqmKrs0aDAfBgNVHSMEGDAWgBTLD8bfQkPM
|
||||
Pcu1SCOhGnqmKrs0aDAbBgNVHREEFDASgRBpbmZvQGUtc3ppZ25vLmh1MA0GCSqG
|
||||
SIb3DQEBCwUAA4IBAQDJ0Q5eLtXMs3w+y/w9/w0olZMEyL/azXm4Q5DwpL7v8u8h
|
||||
mLzU1F0G9u5C7DBsoKqpyvGvivo/C3NqPuouQH4frlRheesuCDfXI/OMn74dseGk
|
||||
ddug4lQUsbocKaQY9hK6ohQU4zE1yED/t+AFdlfBHFny+L/k7SViXITwfn4fs775
|
||||
tyERzAMBVnCnEJIeGzSBHq2cGsMEPO0CYdYeBvNfOofyK/FFh+U9rNHHV4S9a67c
|
||||
2Pm2G2JwCz02yULyMtd6YebS2z3PyKnJm9zbWETXbzivf3jTo60adbocwTZ8jx5t
|
||||
HMN1Rq41Bab2XD0h7lbwyYIiLXpUq3DDfSJlgnCW
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEFTCCAv2gAwIBAgIGSUEs5AAQMA0GCSqGSIb3DQEBCwUAMIGnMQswCQYDVQQG
|
||||
EwJIVTERMA8GA1UEBwwIQnVkYXBlc3QxFTATBgNVBAoMDE5ldExvY2sgS2Z0LjE3
|
||||
MDUGA1UECwwuVGFuw7pzw610dsOhbnlraWFkw7NrIChDZXJ0aWZpY2F0aW9uIFNl
|
||||
cnZpY2VzKTE1MDMGA1UEAwwsTmV0TG9jayBBcmFueSAoQ2xhc3MgR29sZCkgRsWR
|
||||
dGFuw7pzw610dsOhbnkwHhcNMDgxMjExMTUwODIxWhcNMjgxMjA2MTUwODIxWjCB
|
||||
pzELMAkGA1UEBhMCSFUxETAPBgNVBAcMCEJ1ZGFwZXN0MRUwEwYDVQQKDAxOZXRM
|
||||
b2NrIEtmdC4xNzA1BgNVBAsMLlRhbsO6c8OtdHbDoW55a2lhZMOzayAoQ2VydGlm
|
||||
aWNhdGlvbiBTZXJ2aWNlcykxNTAzBgNVBAMMLE5ldExvY2sgQXJhbnkgKENsYXNz
|
||||
IEdvbGQpIEbFkXRhbsO6c8OtdHbDoW55MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8A
|
||||
MIIBCgKCAQEAxCRec75LbRTDofTjl5Bu0jBFHjzuZ9lk4BqKf8owyoPjIMHj9DrT
|
||||
lF8afFttvzBPhCf2nx9JvMaZCpDyD/V/Q4Q3Y1GLeqVw/HpYzY6b7cNGbIRwXdrz
|
||||
AZAj/E4wqX7hJ2Pn7WQ8oLjJM2P+FpD/sLj916jAwJRDC7bVWaaeVtAkH3B5r9s5
|
||||
VA1lddkVQZQBr17s9o3x/61k/iCa11zr/qYfCGSji3ZVrR47KGAuhyXoqq8fxmRG
|
||||
ILdwfzzeSNuWU7c5d+Qa4scWhHaXWy+7GRWF+GmF9ZmnqfI0p6m2pgP8b4Y9VHx2
|
||||
BJtr+UBdADTHLpl1neWIA6pN+APSQnbAGwIDAKiLo0UwQzASBgNVHRMBAf8ECDAG
|
||||
AQH/AgEEMA4GA1UdDwEB/wQEAwIBBjAdBgNVHQ4EFgQUzPpnk/C2uNClwB7zU/2M
|
||||
U9+D15YwDQYJKoZIhvcNAQELBQADggEBAKt/7hwWqZw8UQCgwBEIBaeZ5m8BiFRh
|
||||
bvG5GK1Krf6BQCOUL/t1fC8oS2IkgYIL9WHxHG64YTjrgfpioTtaYtOUZcTh5m2C
|
||||
+C8lcLIhJsFyUR+MLMOEkMNaj7rP9KdlpeuY0fsFskZ1FSNqb4VjMIDw1Z4fKRzC
|
||||
bLBQWV2QWzuoDTDPv31/zvGdg73JRm4gpvlhUbohL3u+pRVjodSVh/GeufOJ8z2F
|
||||
uLjbvrW5KfnaNwUASZQDhETnv0Mxz3WLJdH0pmT1kvarBes96aULNmLazAZfNou2
|
||||
XjG4Kvte9nHfRCaexOYNkbQudZWAUWpLMKawYqGT8ZvYzsRjdT9ZR7E=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIID5jCCAs6gAwIBAgIQV8szb8JcFuZHFhfjkDFo4DANBgkqhkiG9w0BAQUFADBi
|
||||
MQswCQYDVQQGEwJVUzEhMB8GA1UEChMYTmV0d29yayBTb2x1dGlvbnMgTC5MLkMu
|
||||
MTAwLgYDVQQDEydOZXR3b3JrIFNvbHV0aW9ucyBDZXJ0aWZpY2F0ZSBBdXRob3Jp
|
||||
dHkwHhcNMDYxMjAxMDAwMDAwWhcNMjkxMjMxMjM1OTU5WjBiMQswCQYDVQQGEwJV
|
||||
UzEhMB8GA1UEChMYTmV0d29yayBTb2x1dGlvbnMgTC5MLkMuMTAwLgYDVQQDEydO
|
||||
ZXR3b3JrIFNvbHV0aW9ucyBDZXJ0aWZpY2F0ZSBBdXRob3JpdHkwggEiMA0GCSqG
|
||||
SIb3DQEBAQUAA4IBDwAwggEKAoIBAQDkvH6SMG3G2I4rC7xGzuAnlt7e+foS0zwz
|
||||
c7MEL7xxjOWftiJgPl9dzgn/ggwbmlFQGiaJ3dVhXRncEg8tCqJDXRfQNJIg6nPP
|
||||
OCwGJgl6cvf6UDL4wpPTaaIjzkGxzOTVHzbRijr4jGPiFFlp7Q3Tf2vouAPlT2rl
|
||||
mGNpSAW+Lv8ztumXWWn4Zxmuk2GWRBXTcrA/vGp97Eh/jcOrqnErU2lBUzS1sLnF
|
||||
BgrEsEX1QV1uiUV7PTsmjHTC5dLRfbIR1PtYMiKagMnc/Qzpf14Dl847ABSHJ3A4
|
||||
qY5usyd2mFHgBeMhqxrVhSI8KbWaFsWAqPS7azCPL0YCorEMIuDTAgMBAAGjgZcw
|
||||
gZQwHQYDVR0OBBYEFCEwyfsA106Y2oeqKtCnLrFAMadMMA4GA1UdDwEB/wQEAwIB
|
||||
BjAPBgNVHRMBAf8EBTADAQH/MFIGA1UdHwRLMEkwR6BFoEOGQWh0dHA6Ly9jcmwu
|
||||
bmV0c29sc3NsLmNvbS9OZXR3b3JrU29sdXRpb25zQ2VydGlmaWNhdGVBdXRob3Jp
|
||||
dHkuY3JsMA0GCSqGSIb3DQEBBQUAA4IBAQC7rkvnt1frf6ott3NHhWrB5KUd5Oc8
|
||||
6fRZZXe1eltajSU24HqXLjjAV2CDmAaDn7l2em5Q4LqILPxFzBiwmZVRDuwduIj/
|
||||
h1AcgsLj4DKAv6ALR8jDMe+ZZzKATxcheQxpXN5eNK4CtSbqUN9/GGUsyfJj4akH
|
||||
/nxxH2szJGoeBfcFaMBqEssuXmHLrijTfsK0ZpEmXzwuJF/LWA/rKOyvEZbz3Htv
|
||||
wKeI8lN3s2Berq4o2jUsbzRF0ybh3uxbTydrFny9RAQYgrOJeRcQcT16ohZO9QHN
|
||||
pGxlaKFJdlxDydi8NmdspZS11My5vWo1ViHe2MPr+8ukYEywVaCge1ey
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIID8TCCAtmgAwIBAgIQQT1yx/RrH4FDffHSKFTfmjANBgkqhkiG9w0BAQUFADCB
|
||||
ijELMAkGA1UEBhMCQ0gxEDAOBgNVBAoTB1dJU2VLZXkxGzAZBgNVBAsTEkNvcHly
|
||||
aWdodCAoYykgMjAwNTEiMCAGA1UECxMZT0lTVEUgRm91bmRhdGlvbiBFbmRvcnNl
|
||||
ZDEoMCYGA1UEAxMfT0lTVEUgV0lTZUtleSBHbG9iYWwgUm9vdCBHQSBDQTAeFw0w
|
||||
NTEyMTExNjAzNDRaFw0zNzEyMTExNjA5NTFaMIGKMQswCQYDVQQGEwJDSDEQMA4G
|
||||
A1UEChMHV0lTZUtleTEbMBkGA1UECxMSQ29weXJpZ2h0IChjKSAyMDA1MSIwIAYD
|
||||
VQQLExlPSVNURSBGb3VuZGF0aW9uIEVuZG9yc2VkMSgwJgYDVQQDEx9PSVNURSBX
|
||||
SVNlS2V5IEdsb2JhbCBSb290IEdBIENBMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8A
|
||||
MIIBCgKCAQEAy0+zAJs9Nt350UlqaxBJH+zYK7LG+DKBKUOVTJoZIyEVRd7jyBxR
|
||||
VVuuk+g3/ytr6dTqvirdqFEr12bDYVxgAsj1znJ7O7jyTmUIms2kahnBAbtzptf2
|
||||
w93NvKSLtZlhuAGio9RN1AU9ka34tAhxZK9w8RxrfvbDd50kc3vkDIzh2TbhmYsF
|
||||
mQvtRTEJysIA2/dyoJaqlYfQjse2YXMNdmaM3Bu0Y6Kff5MTMPGhJ9vZ/yxViJGg
|
||||
4E8HsChWjBgbl0SOid3gF27nKu+POQoxhILYQBRJLnpB5Kf+42TMwVlxSywhp1t9
|
||||
4B3RLoGbw9ho972WG6xwsRYUC9tguSYBBQIDAQABo1EwTzALBgNVHQ8EBAMCAYYw
|
||||
DwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUswN+rja8sHnR3JQmthG+IbJphpQw
|
||||
EAYJKwYBBAGCNxUBBAMCAQAwDQYJKoZIhvcNAQEFBQADggEBAEuh/wuHbrP5wUOx
|
||||
SPMowB0uyQlB+pQAHKSkq0lPjz0e701vvbyk9vImMMkQyh2I+3QZH4VFvbBsUfk2
|
||||
ftv1TDI6QU9bR8/oCy22xBmddMVHxjtqD6wU2zz0c5ypBd8A3HR4+vg1YFkCExh8
|
||||
vPtNsCBtQ7tgMHpnM1zFmdH4LTlSc/uMqpclXHLZCB6rTjzjgTGfA6b7wP4piFXa
|
||||
hNVQA7bihKOmNqoROgHhGEvWRGizPflTdISzRpFGlgC3gCy24eMQ4tui5yiPAZZi
|
||||
Fj4A4xylNoEYokxSdsARo27mHbrjWr42U8U+dY+GaSlYU7Wcu2+fXMUY7N0v4ZjJ
|
||||
/L7fCg0=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDtTCCAp2gAwIBAgIQdrEgUnTwhYdGs/gjGvbCwDANBgkqhkiG9w0BAQsFADBt
|
||||
MQswCQYDVQQGEwJDSDEQMA4GA1UEChMHV0lTZUtleTEiMCAGA1UECxMZT0lTVEUg
|
||||
Rm91bmRhdGlvbiBFbmRvcnNlZDEoMCYGA1UEAxMfT0lTVEUgV0lTZUtleSBHbG9i
|
||||
YWwgUm9vdCBHQiBDQTAeFw0xNDEyMDExNTAwMzJaFw0zOTEyMDExNTEwMzFaMG0x
|
||||
CzAJBgNVBAYTAkNIMRAwDgYDVQQKEwdXSVNlS2V5MSIwIAYDVQQLExlPSVNURSBG
|
||||
b3VuZGF0aW9uIEVuZG9yc2VkMSgwJgYDVQQDEx9PSVNURSBXSVNlS2V5IEdsb2Jh
|
||||
bCBSb290IEdCIENBMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA2Be3
|
||||
HEokKtaXscriHvt9OO+Y9bI5mE4nuBFde9IllIiCFSZqGzG7qFshISvYD06fWvGx
|
||||
WuR51jIjK+FTzJlFXHtPrby/h0oLS5daqPZI7H17Dc0hBt+eFf1Biki3IPShehtX
|
||||
1F1Q/7pn2COZH8g/497/b1t3sWtuuMlk9+HKQUYOKXHQuSP8yYFfTvdv37+ErXNk
|
||||
u7dCjmn21HYdfp2nuFeKUWdy19SouJVUQHMD9ur06/4oQnc/nSMbsrY9gBQHTC5P
|
||||
99UKFg29ZkM3fiNDecNAhvVMKdqOmq0NpQSHiB6F4+lT1ZvIiwNjeOvgGUpuuy9r
|
||||
M2RYk61pv48b74JIxwIDAQABo1EwTzALBgNVHQ8EBAMCAYYwDwYDVR0TAQH/BAUw
|
||||
AwEB/zAdBgNVHQ4EFgQUNQ/INmNe4qPs+TtmFc5RUuORmj0wEAYJKwYBBAGCNxUB
|
||||
BAMCAQAwDQYJKoZIhvcNAQELBQADggEBAEBM+4eymYGQfp3FsLAmzYh7KzKNbrgh
|
||||
cViXfa43FK8+5/ea4n32cZiZBKpDdHij40lhPnOMTZTg+XHEthYOU3gf1qKHLwI5
|
||||
gSk8rxWYITD+KJAAjNHhy/peyP34EEY7onhCkRd0VQreUGdNZtGn//3ZwLWoo4rO
|
||||
ZvUPQ82nK1d7Y0Zqqi5S2PTt4W2tKZB4SLrhI6qjiey1q5bAtEuiHZeeevJuQHHf
|
||||
aPFlTc58Bd9TZaml8LGXBHAVRgOY1NK/VLSgWH1Sb9pWJmLU2NuJMW8c8CLC02Ic
|
||||
Nc1MaRVUGpCY3useX8p3x8uOPUNpnJpY0CQ73xtAln41rYHHTnG6iBM=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF0DCCBLigAwIBAgIEOrZQizANBgkqhkiG9w0BAQUFADB/MQswCQYDVQQGEwJC
|
||||
TTEZMBcGA1UEChMQUXVvVmFkaXMgTGltaXRlZDElMCMGA1UECxMcUm9vdCBDZXJ0
|
||||
aWZpY2F0aW9uIEF1dGhvcml0eTEuMCwGA1UEAxMlUXVvVmFkaXMgUm9vdCBDZXJ0
|
||||
aWZpY2F0aW9uIEF1dGhvcml0eTAeFw0wMTAzMTkxODMzMzNaFw0yMTAzMTcxODMz
|
||||
MzNaMH8xCzAJBgNVBAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBMaW1pdGVkMSUw
|
||||
IwYDVQQLExxSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5MS4wLAYDVQQDEyVR
|
||||
dW9WYWRpcyBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5MIIBIjANBgkqhkiG
|
||||
9w0BAQEFAAOCAQ8AMIIBCgKCAQEAv2G1lVO6V/z68mcLOhrfEYBklbTRvM16z/Yp
|
||||
li4kVEAkOPcahdxYTMukJ0KX0J+DisPkBgNbAKVRHnAEdOLB1Dqr1607BxgFjv2D
|
||||
rOpm2RgbaIr1VxqYuvXtdj182d6UajtLF8HVj71lODqV0D1VNk7feVcxKh7YWWVJ
|
||||
WCCYfqtffp/p1k3sg3Spx2zY7ilKhSoGFPlU5tPaZQeLYzcS19Dsw3sgQUSj7cug
|
||||
F+FxZc4dZjH3dgEZyH0DWLaVSR2mEiboxgx24ONmy+pdpibu5cxfvWenAScOospU
|
||||
xbF6lR1xHkopigPcakXBpBlebzbNw6Kwt/5cOOJSvPhEQ+aQuwIDAQABo4ICUjCC
|
||||
Ak4wPQYIKwYBBQUHAQEEMTAvMC0GCCsGAQUFBzABhiFodHRwczovL29jc3AucXVv
|
||||
dmFkaXNvZmZzaG9yZS5jb20wDwYDVR0TAQH/BAUwAwEB/zCCARoGA1UdIASCAREw
|
||||
ggENMIIBCQYJKwYBBAG+WAABMIH7MIHUBggrBgEFBQcCAjCBxxqBxFJlbGlhbmNl
|
||||
IG9uIHRoZSBRdW9WYWRpcyBSb290IENlcnRpZmljYXRlIGJ5IGFueSBwYXJ0eSBh
|
||||
c3N1bWVzIGFjY2VwdGFuY2Ugb2YgdGhlIHRoZW4gYXBwbGljYWJsZSBzdGFuZGFy
|
||||
ZCB0ZXJtcyBhbmQgY29uZGl0aW9ucyBvZiB1c2UsIGNlcnRpZmljYXRpb24gcHJh
|
||||
Y3RpY2VzLCBhbmQgdGhlIFF1b1ZhZGlzIENlcnRpZmljYXRlIFBvbGljeS4wIgYI
|
||||
KwYBBQUHAgEWFmh0dHA6Ly93d3cucXVvdmFkaXMuYm0wHQYDVR0OBBYEFItLbe3T
|
||||
KbkGGew5Oanwl4Rqy+/fMIGuBgNVHSMEgaYwgaOAFItLbe3TKbkGGew5Oanwl4Rq
|
||||
y+/foYGEpIGBMH8xCzAJBgNVBAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBMaW1p
|
||||
dGVkMSUwIwYDVQQLExxSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5MS4wLAYD
|
||||
VQQDEyVRdW9WYWRpcyBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5ggQ6tlCL
|
||||
MA4GA1UdDwEB/wQEAwIBBjANBgkqhkiG9w0BAQUFAAOCAQEAitQUtf70mpKnGdSk
|
||||
fnIYj9lofFIk3WdvOXrEql494liwTXCYhGHoG+NpGA7O+0dQoE7/8CQfvbLO9Sf8
|
||||
7C9TqnN7Az10buYWnuulLsS/VidQK2K6vkscPFVcQR0kvoIgR13VRH56FmjffU1R
|
||||
cHhXHTMe/QKZnAzNCgVPx7uOpHX6Sm2xgI4JVrmcGmD+XcHXetwReNDWXcG31a0y
|
||||
mQM6isxUJTkxgXsTIlG6Rmyhu576BGxJJnSP0nPrzDCi5upZIof4l/UO/erMkqQW
|
||||
xFIY6iHOsfHmhIHluqmGKPJDWl0Snawe2ajlCmqnf6CHKc/yiU3U7MXi5nrQNiOK
|
||||
SnQ2+Q==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFYDCCA0igAwIBAgIUeFhfLq0sGUvjNwc1NBMotZbUZZMwDQYJKoZIhvcNAQEL
|
||||
BQAwSDELMAkGA1UEBhMCQk0xGTAXBgNVBAoTEFF1b1ZhZGlzIExpbWl0ZWQxHjAc
|
||||
BgNVBAMTFVF1b1ZhZGlzIFJvb3QgQ0EgMSBHMzAeFw0xMjAxMTIxNzI3NDRaFw00
|
||||
MjAxMTIxNzI3NDRaMEgxCzAJBgNVBAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBM
|
||||
aW1pdGVkMR4wHAYDVQQDExVRdW9WYWRpcyBSb290IENBIDEgRzMwggIiMA0GCSqG
|
||||
SIb3DQEBAQUAA4ICDwAwggIKAoICAQCgvlAQjunybEC0BJyFuTHK3C3kEakEPBtV
|
||||
wedYMB0ktMPvhd6MLOHBPd+C5k+tR4ds7FtJwUrVu4/sh6x/gpqG7D0DmVIB0jWe
|
||||
rNrwU8lmPNSsAgHaJNM7qAJGr6Qc4/hzWHa39g6QDbXwz8z6+cZM5cOGMAqNF341
|
||||
68Xfuw6cwI2H44g4hWf6Pser4BOcBRiYz5P1sZK0/CPTz9XEJ0ngnjybCKOLXSoh
|
||||
4Pw5qlPafX7PGglTvF0FBM+hSo+LdoINofjSxxR3W5A2B4GbPgb6Ul5jxaYA/qXp
|
||||
UhtStZI5cgMJYr2wYBZupt0lwgNm3fME0UDiTouG9G/lg6AnhF4EwfWQvTA9xO+o
|
||||
abw4m6SkltFi2mnAAZauy8RRNOoMqv8hjlmPSlzkYZqn0ukqeI1RPToV7qJZjqlc
|
||||
3sX5kCLliEVx3ZGZbHqfPT2YfF72vhZooF6uCyP8Wg+qInYtyaEQHeTTRCOQiJ/G
|
||||
KubX9ZqzWB4vMIkIG1SitZgj7Ah3HJVdYdHLiZxfokqRmu8hqkkWCKi9YSgxyXSt
|
||||
hfbZxbGL0eUQMk1fiyA6PEkfM4VZDdvLCXVDaXP7a3F98N/ETH3Goy7IlXnLc6KO
|
||||
Tk0k+17kBL5yG6YnLUlamXrXXAkgt3+UuU/xDRxeiEIbEbfnkduebPRq34wGmAOt
|
||||
zCjvpUfzUwIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIB
|
||||
BjAdBgNVHQ4EFgQUo5fW816iEOGrRZ88F2Q87gFwnMwwDQYJKoZIhvcNAQELBQAD
|
||||
ggIBABj6W3X8PnrHX3fHyt/PX8MSxEBd1DKquGrX1RUVRpgjpeaQWxiZTOOtQqOC
|
||||
MTaIzen7xASWSIsBx40Bz1szBpZGZnQdT+3Btrm0DWHMY37XLneMlhwqI2hrhVd2
|
||||
cDMT/uFPpiN3GPoajOi9ZcnPP/TJF9zrx7zABC4tRi9pZsMbj/7sPtPKlL92CiUN
|
||||
qXsCHKnQO18LwIE6PWThv6ctTr1NxNgpxiIY0MWscgKCP6o6ojoilzHdCGPDdRS5
|
||||
YCgtW2jgFqlmgiNR9etT2DGbe+m3nUvriBbP+V04ikkwj+3x6xn0dxoxGE1nVGwv
|
||||
b2X52z3sIexe9PSLymBlVNFxZPT5pqOBMzYzcfCkeF9OrYMh3jRJjehZrJ3ydlo2
|
||||
8hP0r+AJx2EqbPfgna67hkooby7utHnNkDPDs3b69fBsnQGQ+p6Q9pxyz0fawx/k
|
||||
NSBT8lTR32GDpgLiJTjehTItXnOQUl1CxM49S+H5GYQd1aJQzEH7QRTDvdbJWqNj
|
||||
ZgKAvQU6O0ec7AAmTPWIUb+oI38YB7AL7YsmoWTTYUrrXJ/es69nA7Mf3W1daWhp
|
||||
q1467HxpvMc7hU6eFbm0FU/DlXpY18ls6Wy58yljXrQs8C097Vpl4KlbQMJImYFt
|
||||
nh8GKjwStIsPm6Ik8KaN1nrgS7ZklmOVhMJKzRwuJIczYOXD
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFtzCCA5+gAwIBAgICBQkwDQYJKoZIhvcNAQEFBQAwRTELMAkGA1UEBhMCQk0x
|
||||
GTAXBgNVBAoTEFF1b1ZhZGlzIExpbWl0ZWQxGzAZBgNVBAMTElF1b1ZhZGlzIFJv
|
||||
b3QgQ0EgMjAeFw0wNjExMjQxODI3MDBaFw0zMTExMjQxODIzMzNaMEUxCzAJBgNV
|
||||
BAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBMaW1pdGVkMRswGQYDVQQDExJRdW9W
|
||||
YWRpcyBSb290IENBIDIwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQCa
|
||||
GMpLlA0ALa8DKYrwD4HIrkwZhR0In6spRIXzL4GtMh6QRr+jhiYaHv5+HBg6XJxg
|
||||
Fyo6dIMzMH1hVBHL7avg5tKifvVrbxi3Cgst/ek+7wrGsxDp3MJGF/hd/aTa/55J
|
||||
WpzmM+Yklvc/ulsrHHo1wtZn/qtmUIttKGAr79dgw8eTvI02kfN/+NsRE8Scd3bB
|
||||
rrcCaoF6qUWD4gXmuVbBlDePSHFjIuwXZQeVikvfj8ZaCuWw419eaxGrDPmF60Tp
|
||||
+ARz8un+XJiM9XOva7R+zdRcAitMOeGylZUtQofX1bOQQ7dsE/He3fbE+Ik/0XX1
|
||||
ksOR1YqI0JDs3G3eicJlcZaLDQP9nL9bFqyS2+r+eXyt66/3FsvbzSUr5R/7mp/i
|
||||
Ucw6UwxI5g69ybR2BlLmEROFcmMDBOAENisgGQLodKcftslWZvB1JdxnwQ5hYIiz
|
||||
PtGo/KPaHbDRsSNU30R2be1B2MGyIrZTHN81Hdyhdyox5C315eXbyOD/5YDXC2Og
|
||||
/zOhD7osFRXql7PSorW+8oyWHhqPHWykYTe5hnMz15eWniN9gqRMgeKh0bpnX5UH
|
||||
oycR7hYQe7xFSkyyBNKr79X9DFHOUGoIMfmR2gyPZFwDwzqLID9ujWc9Otb+fVuI
|
||||
yV77zGHcizN300QyNQliBJIWENieJ0f7OyHj+OsdWwIDAQABo4GwMIGtMA8GA1Ud
|
||||
EwEB/wQFMAMBAf8wCwYDVR0PBAQDAgEGMB0GA1UdDgQWBBQahGK8SEwzJQTU7tD2
|
||||
A8QZRtGUazBuBgNVHSMEZzBlgBQahGK8SEwzJQTU7tD2A8QZRtGUa6FJpEcwRTEL
|
||||
MAkGA1UEBhMCQk0xGTAXBgNVBAoTEFF1b1ZhZGlzIExpbWl0ZWQxGzAZBgNVBAMT
|
||||
ElF1b1ZhZGlzIFJvb3QgQ0EgMoICBQkwDQYJKoZIhvcNAQEFBQADggIBAD4KFk2f
|
||||
BluornFdLwUvZ+YTRYPENvbzwCYMDbVHZF34tHLJRqUDGCdViXh9duqWNIAXINzn
|
||||
g/iN/Ae42l9NLmeyhP3ZRPx3UIHmfLTJDQtyU/h2BwdBR5YM++CCJpNVjP4iH2Bl
|
||||
fF/nJrP3MpCYUNQ3cVX2kiF495V5+vgtJodmVjB3pjd4M1IQWK4/YY7yarHvGH5K
|
||||
WWPKjaJW1acvvFYfzznB4vsKqBUsfU16Y8Zsl0Q80m/DShcK+JDSV6IZUaUtl0Ha
|
||||
B0+pUNqQjZRG4T7wlP0QADj1O+hA4bRuVhogzG9Yje0uRY/W6ZM/57Es3zrWIozc
|
||||
hLsib9D45MY56QSIPMO661V6bYCZJPVsAfv4l7CUW+v90m/xd2gNNWQjrLhVoQPR
|
||||
TUIZ3Ph1WVaj+ahJefivDrkRoHy3au000LYmYjgahwz46P0u05B/B5EqHdZ+XIWD
|
||||
mbA4CD/pXvk1B+TJYm5Xf6dQlfe6yJvmjqIBxdZmv3lh8zwc4bmCXF2gw+nYSL0Z
|
||||
ohEUGW6yhhtoPkg3Goi3XZZenMfvJ2II4pEZXNLxId26F0KCl3GBUzGpn/Z9Yr9y
|
||||
4aOTHcyKJloJONDO1w2AFrR4pTqHTI2KpdVGl/IsELm8VCLAAVBpQ570su9t+Oza
|
||||
8eOx79+Rj1QqCyXBJhnEUhAFZdWCEOrCMc0u
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFYDCCA0igAwIBAgIURFc0JFuBiZs18s64KztbpybwdSgwDQYJKoZIhvcNAQEL
|
||||
BQAwSDELMAkGA1UEBhMCQk0xGTAXBgNVBAoTEFF1b1ZhZGlzIExpbWl0ZWQxHjAc
|
||||
BgNVBAMTFVF1b1ZhZGlzIFJvb3QgQ0EgMiBHMzAeFw0xMjAxMTIxODU5MzJaFw00
|
||||
MjAxMTIxODU5MzJaMEgxCzAJBgNVBAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBM
|
||||
aW1pdGVkMR4wHAYDVQQDExVRdW9WYWRpcyBSb290IENBIDIgRzMwggIiMA0GCSqG
|
||||
SIb3DQEBAQUAA4ICDwAwggIKAoICAQChriWyARjcV4g/Ruv5r+LrI3HimtFhZiFf
|
||||
qq8nUeVuGxbULX1QsFN3vXg6YOJkApt8hpvWGo6t/x8Vf9WVHhLL5hSEBMHfNrMW
|
||||
n4rjyduYNM7YMxcoRvynyfDStNVNCXJJ+fKH46nafaF9a7I6JaltUkSs+L5u+9ym
|
||||
c5GQYaYDFCDy54ejiK2toIz/pgslUiXnFgHVy7g1gQyjO/Dh4fxaXc6AcW34Sas+
|
||||
O7q414AB+6XrW7PFXmAqMaCvN+ggOp+oMiwMzAkd056OXbxMmO7FGmh77FOm6RQ1
|
||||
o9/NgJ8MSPsc9PG/Srj61YxxSscfrf5BmrODXfKEVu+lV0POKa2Mq1W/xPtbAd0j
|
||||
IaFYAI7D0GoT7RPjEiuA3GfmlbLNHiJuKvhB1PLKFAeNilUSxmn1uIZoL1NesNKq
|
||||
IcGY5jDjZ1XHm26sGahVpkUG0CM62+tlXSoREfA7T8pt9DTEceT/AFr2XK4jYIVz
|
||||
8eQQsSWu1ZK7E8EM4DnatDlXtas1qnIhO4M15zHfeiFuuDIIfR0ykRVKYnLP43eh
|
||||
vNURG3YBZwjgQQvD6xVu+KQZ2aKrr+InUlYrAoosFCT5v0ICvybIxo/gbjh9Uy3l
|
||||
7ZizlWNof/k19N+IxWA1ksB8aRxhlRbQ694Lrz4EEEVlWFA4r0jyWbYW8jwNkALG
|
||||
cC4BrTwV1wIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIB
|
||||
BjAdBgNVHQ4EFgQU7edvdlq/YOxJW8ald7tyFnGbxD0wDQYJKoZIhvcNAQELBQAD
|
||||
ggIBAJHfgD9DCX5xwvfrs4iP4VGyvD11+ShdyLyZm3tdquXK4Qr36LLTn91nMX66
|
||||
AarHakE7kNQIXLJgapDwyM4DYvmL7ftuKtwGTTwpD4kWilhMSA/ohGHqPHKmd+RC
|
||||
roijQ1h5fq7KpVMNqT1wvSAZYaRsOPxDMuHBR//47PERIjKWnML2W2mWeyAMQ0Ga
|
||||
W/ZZGYjeVYg3UQt4XAoeo0L9x52ID8DyeAIkVJOviYeIyUqAHerQbj5hLja7NQ4n
|
||||
lv1mNDthcnPxFlxHBlRJAHpYErAK74X9sbgzdWqTHBLmYF5vHX/JHyPLhGGfHoJE
|
||||
+V+tYlUkmlKY7VHnoX6XOuYvHxHaU4AshZ6rNRDbIl9qxV6XU/IyAgkwo1jwDQHV
|
||||
csaxfGl7w/U2Rcxhbl5MlMVerugOXou/983g7aEOGzPuVBj+D77vfoRrQ+NwmNtd
|
||||
dbINWQeFFSM51vHfqSYP1kjHs6Yi9TM3WpVHn3u6GBVv/9YUZINJ0gpnIdsPNWNg
|
||||
KCLjsZWDzYWm3S8P52dSbrsvhXz1SnPnxT7AvSESBT/8twNJAlvIJebiVDj1eYeM
|
||||
HVOyToV7BjjHLPj4sHKNJeV3UvQDHEimUF+IIDBu8oJDqz2XhOdT+yHBTw8imoa4
|
||||
WSr2Rz0ZiC3oheGe7IUIarFsNMkd7EgrO3jtZsSOeWmD3n+M
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIGnTCCBIWgAwIBAgICBcYwDQYJKoZIhvcNAQEFBQAwRTELMAkGA1UEBhMCQk0x
|
||||
GTAXBgNVBAoTEFF1b1ZhZGlzIExpbWl0ZWQxGzAZBgNVBAMTElF1b1ZhZGlzIFJv
|
||||
b3QgQ0EgMzAeFw0wNjExMjQxOTExMjNaFw0zMTExMjQxOTA2NDRaMEUxCzAJBgNV
|
||||
BAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBMaW1pdGVkMRswGQYDVQQDExJRdW9W
|
||||
YWRpcyBSb290IENBIDMwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDM
|
||||
V0IWVJzmmNPTTe7+7cefQzlKZbPoFog02w1ZkXTPkrgEQK0CSzGrvI2RaNggDhoB
|
||||
4hp7Thdd4oq3P5kazethq8Jlph+3t723j/z9cI8LoGe+AaJZz3HmDyl2/7FWeUUr
|
||||
H556VOijKTVopAFPD6QuN+8bv+OPEKhyq1hX51SGyMnzW9os2l2ObjyjPtr7guXd
|
||||
8lyyBTNvijbO0BNO/79KDDRMpsMhvVAEVeuxu537RR5kFd5VAYwCdrXLoT9Cabwv
|
||||
vWhDFlaJKjdhkf2mrk7AyxRllDdLkgbvBNDInIjbC3uBr7E9KsRlOni27tyAsdLT
|
||||
mZw67mtaa7ONt9XOnMK+pUsvFrGeaDsGb659n/je7Mwpp5ijJUMv7/FfJuGITfhe
|
||||
btfZFG4ZM2mnO4SJk8RTVROhUXhA+LjJou57ulJCg54U7QVSWllWp5f8nT8KKdjc
|
||||
T5EOE7zelaTfi5m+rJsziO+1ga8bxiJTyPbH7pcUsMV8eFLI8M5ud2CEpukqdiDt
|
||||
WAEXMJPpGovgc2PZapKUSU60rUqFxKMiMPwJ7Wgic6aIDFUhWMXhOp8q3crhkODZ
|
||||
c6tsgLjoC2SToJyMGf+z0gzskSaHirOi4XCPLArlzW1oUevaPwV/izLmE1xr/l9A
|
||||
4iLItLRkT9a6fUg+qGkM17uGcclzuD87nSVL2v9A6wIDAQABo4IBlTCCAZEwDwYD
|
||||
VR0TAQH/BAUwAwEB/zCB4QYDVR0gBIHZMIHWMIHTBgkrBgEEAb5YAAMwgcUwgZMG
|
||||
CCsGAQUFBwICMIGGGoGDQW55IHVzZSBvZiB0aGlzIENlcnRpZmljYXRlIGNvbnN0
|
||||
aXR1dGVzIGFjY2VwdGFuY2Ugb2YgdGhlIFF1b1ZhZGlzIFJvb3QgQ0EgMyBDZXJ0
|
||||
aWZpY2F0ZSBQb2xpY3kgLyBDZXJ0aWZpY2F0aW9uIFByYWN0aWNlIFN0YXRlbWVu
|
||||
dC4wLQYIKwYBBQUHAgEWIWh0dHA6Ly93d3cucXVvdmFkaXNnbG9iYWwuY29tL2Nw
|
||||
czALBgNVHQ8EBAMCAQYwHQYDVR0OBBYEFPLAE+CCQz777i9nMpY1XNu4ywLQMG4G
|
||||
A1UdIwRnMGWAFPLAE+CCQz777i9nMpY1XNu4ywLQoUmkRzBFMQswCQYDVQQGEwJC
|
||||
TTEZMBcGA1UEChMQUXVvVmFkaXMgTGltaXRlZDEbMBkGA1UEAxMSUXVvVmFkaXMg
|
||||
Um9vdCBDQSAzggIFxjANBgkqhkiG9w0BAQUFAAOCAgEAT62gLEz6wPJv92ZVqyM0
|
||||
7ucp2sNbtrCD2dDQ4iH782CnO11gUyeim/YIIirnv6By5ZwkajGxkHon24QRiSem
|
||||
d1o417+shvzuXYO8BsbRd2sPbSQvS3pspweWyuOEn62Iix2rFo1bZhfZFvSLgNLd
|
||||
+LJ2w/w4E6oM3kJpK27zPOuAJ9v1pkQNn1pVWQvVDVJIxa6f8i+AxeoyUDUSly7B
|
||||
4f/xI4hROJ/yZlZ25w9Rl6VSDE1JUZU2Pb+iSwwQHYaZTKrzchGT5Or2m9qoXadN
|
||||
t54CrnMAyNojA+j56hl0YgCUyyIgvpSnWbWCar6ZeXqp8kokUvd0/bpO5qgdAm6x
|
||||
DYBEwa7TIzdfu4V8K5Iu6H6li92Z4b8nby1dqnuH/grdS/yO9SbkbnBCbjPsMZ57
|
||||
k8HkyWkaPcBrTiJt7qtYTcbQQcEr6k8Sh17rRdhs9ZgC06DYVYoGmRmioHfRMJ6s
|
||||
zHXug/WwYjnPbFfiTNKRCw51KBuav/0aQ/HKd/s7j2G4aSgWQgRecCocIdiP4b0j
|
||||
Wy10QJLZYxkNc91pvGJHvOB0K7Lrfb5BG7XARsWhIstfTsEokt4YutUqKLsRixeT
|
||||
mJlglFwjz1onl14LBQaTNx47aTbrqZ5hHY8y2o4M1nQ+ewkk2gF3R8Q7zTSMmfXK
|
||||
4SVhM7JZG+Ju1zdXtg2pEto=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFYDCCA0igAwIBAgIULvWbAiin23r/1aOp7r0DoM8Sah0wDQYJKoZIhvcNAQEL
|
||||
BQAwSDELMAkGA1UEBhMCQk0xGTAXBgNVBAoTEFF1b1ZhZGlzIExpbWl0ZWQxHjAc
|
||||
BgNVBAMTFVF1b1ZhZGlzIFJvb3QgQ0EgMyBHMzAeFw0xMjAxMTIyMDI2MzJaFw00
|
||||
MjAxMTIyMDI2MzJaMEgxCzAJBgNVBAYTAkJNMRkwFwYDVQQKExBRdW9WYWRpcyBM
|
||||
aW1pdGVkMR4wHAYDVQQDExVRdW9WYWRpcyBSb290IENBIDMgRzMwggIiMA0GCSqG
|
||||
SIb3DQEBAQUAA4ICDwAwggIKAoICAQCzyw4QZ47qFJenMioKVjZ/aEzHs286IxSR
|
||||
/xl/pcqs7rN2nXrpixurazHb+gtTTK/FpRp5PIpM/6zfJd5O2YIyC0TeytuMrKNu
|
||||
FoM7pmRLMon7FhY4futD4tN0SsJiCnMK3UmzV9KwCoWdcTzeo8vAMvMBOSBDGzXR
|
||||
U7Ox7sWTaYI+FrUoRqHe6okJ7UO4BUaKhvVZR74bbwEhELn9qdIoyhA5CcoTNs+c
|
||||
ra1AdHkrAj80//ogaX3T7mH1urPnMNA3I4ZyYUUpSFlob3emLoG+B01vr87ERROR
|
||||
FHAGjx+f+IdpsQ7vw4kZ6+ocYfx6bIrc1gMLnia6Et3UVDmrJqMz6nWB2i3ND0/k
|
||||
A9HvFZcba5DFApCTZgIhsUfei5pKgLlVj7WiL8DWM2fafsSntARE60f75li59wzw
|
||||
eyuxwHApw0BiLTtIadwjPEjrewl5qW3aqDCYz4ByA4imW0aucnl8CAMhZa634Ryl
|
||||
sSqiMd5mBPfAdOhx3v89WcyWJhKLhZVXGqtrdQtEPREoPHtht+KPZ0/l7DxMYIBp
|
||||
VzgeAVuNVejH38DMdyM0SXV89pgR6y3e7UEuFAUCf+D+IOs15xGsIs5XPd7JMG0Q
|
||||
A4XN8f+MFrXBsj6IbGB/kE+V9/YtrQE5BwT6dYB9v0lQ7e/JxHwc64B+27bQ3RP+
|
||||
ydOc17KXqQIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIB
|
||||
BjAdBgNVHQ4EFgQUxhfQvKjqAkPyGwaZXSuQILnXnOQwDQYJKoZIhvcNAQELBQAD
|
||||
ggIBADRh2Va1EodVTd2jNTFGu6QHcrxfYWLopfsLN7E8trP6KZ1/AvWkyaiTt3px
|
||||
KGmPc+FSkNrVvjrlt3ZqVoAh313m6Tqe5T72omnHKgqwGEfcIHB9UqM+WXzBusnI
|
||||
FUBhynLWcKzSt/Ac5IYp8M7vaGPQtSCKFWGafoaYtMnCdvvMujAWzKNhxnQT5Wvv
|
||||
oxXqA/4Ti2Tk08HS6IT7SdEQTXlm66r99I0xHnAUrdzeZxNMgRVhvLfZkXdxGYFg
|
||||
u/BYpbWcC/ePIlUnwEsBbTuZDdQdm2NnL9DuDcpmvJRPpq3t/O5jrFc/ZSXPsoaP
|
||||
0Aj/uHYUbt7lJ+yreLVTubY/6CD50qi+YUbKh4yE8/nxoGibIh6BJpsQBJFxwAYf
|
||||
3KDTuVan45gtf4Od34wrnDKOMpTwATwiKp9Dwi7DmDkHOHv8XgBCH/MyJnmDhPbl
|
||||
8MFREsALHgQjDFSlTC9JxUrRtm5gDWv8a4uFJGS3iQ6rJUdbPM9+Sb3H6QrG2vd+
|
||||
DhcI00iX0HGS8A85PjRqHH3Y8iKuu2n0M7SmSFXRDw4m6Oy2Cy2nhTXN/VnIn9HN
|
||||
PlopNLk9hM6xZdRZkZFWdSHBd575euFgndOtBBj0fOtek49TSiIp+EgrPk2GrFt/
|
||||
ywaZWWDYWGWVjUTR939+J399roD1B0y2PpxxVJkES/1Y+Zj0
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDcjCCAlqgAwIBAgIUPopdB+xV0jLVt+O2XwHrLdzk1uQwDQYJKoZIhvcNAQEL
|
||||
BQAwUTELMAkGA1UEBhMCUEwxKDAmBgNVBAoMH0tyYWpvd2EgSXpiYSBSb3psaWN6
|
||||
ZW5pb3dhIFMuQS4xGDAWBgNVBAMMD1NaQUZJUiBST09UIENBMjAeFw0xNTEwMTkw
|
||||
NzQzMzBaFw0zNTEwMTkwNzQzMzBaMFExCzAJBgNVBAYTAlBMMSgwJgYDVQQKDB9L
|
||||
cmFqb3dhIEl6YmEgUm96bGljemVuaW93YSBTLkEuMRgwFgYDVQQDDA9TWkFGSVIg
|
||||
Uk9PVCBDQTIwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQC3vD5QqEvN
|
||||
QLXOYeeWyrSh2gwisPq1e3YAd4wLz32ohswmUeQgPYUM1ljj5/QqGJ3a0a4m7utT
|
||||
3PSQ1hNKDJA8w/Ta0o4NkjrcsbH/ON7Dui1fgLkCvUqdGw+0w8LBZwPd3BucPbOw
|
||||
3gAeqDRHu5rr/gsUvTaE2g0gv/pby6kWIK05YO4vdbbnl5z5Pv1+TW9NL++IDWr6
|
||||
3fE9biCloBK0TXC5ztdyO4mTp4CEHCdJckm1/zuVnsHMyAHs6A6KCpbns6aH5db5
|
||||
BSsNl0BwPLqsdVqc1U2dAgrSS5tmS0YHF2Wtn2yIANwiieDhZNRnvDF5YTy7ykHN
|
||||
XGoAyDw4jlivAgMBAAGjQjBAMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQD
|
||||
AgEGMB0GA1UdDgQWBBQuFqlKGLXLzPVvUPMjX/hd56zwyDANBgkqhkiG9w0BAQsF
|
||||
AAOCAQEAtXP4A9xZWx126aMqe5Aosk3AM0+qmrHUuOQn/6mWmc5G4G18TKI4pAZw
|
||||
8PRBEew/R40/cof5O/2kbytTAOD/OblqBw7rHRz2onKQy4I9EYKL0rufKq8h5mOG
|
||||
nXkZ7/e7DDWQw4rtTw/1zBLZpD67oPwglV9PJi8RI4NOdQcPv5vRtB3pEAT+ymCP
|
||||
oky4rc/hkA/NrgrHXXu3UNLUYfrVFdvXn4dRVOul4+vJhaAlIDf7js4MNIThPIGy
|
||||
d05DpYhfhmehPea0XGG2Ptv+tyjFogeutcrKjSoS75ftwjCkySp6+/NNIxuZMzSg
|
||||
LvWpCz/UXeHPhJ/iGcJfitYgHuNztw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDbTCCAlWgAwIBAgIBATANBgkqhkiG9w0BAQUFADBYMQswCQYDVQQGEwJKUDEr
|
||||
MCkGA1UEChMiSmFwYW4gQ2VydGlmaWNhdGlvbiBTZXJ2aWNlcywgSW5jLjEcMBoG
|
||||
A1UEAxMTU2VjdXJlU2lnbiBSb290Q0ExMTAeFw0wOTA0MDgwNDU2NDdaFw0yOTA0
|
||||
MDgwNDU2NDdaMFgxCzAJBgNVBAYTAkpQMSswKQYDVQQKEyJKYXBhbiBDZXJ0aWZp
|
||||
Y2F0aW9uIFNlcnZpY2VzLCBJbmMuMRwwGgYDVQQDExNTZWN1cmVTaWduIFJvb3RD
|
||||
QTExMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA/XeqpRyQBTvLTJsz
|
||||
i1oURaTnkBbR31fSIRCkF/3frNYfp+TbfPfs37gD2pRY/V1yfIw/XwFndBWW4wI8
|
||||
h9uuywGOwvNmxoVF9ALGOrVisq/6nL+k5tSAMJjzDbaTj6nU2DbysPyKyiyhFTOV
|
||||
MdrAG/LuYpmGYz+/3ZMqg6h2uRMft85OQoWPIucuGvKVCbIFtUROd6EgvanyTgp9
|
||||
UK31BQ1FT0Zx/Sg+U/sE2C3XZR1KG/rPO7AxmjVuyIsG0wCR8pQIZUyxNAYAeoni
|
||||
8McDWc/V1uinMrPmmECGxc0nEovMe863ETxiYAcjPitAbpSACW22s293bzUIUPsC
|
||||
h8U+iQIDAQABo0IwQDAdBgNVHQ4EFgQUW/hNT7KlhtQ60vFjmqC+CfZXt94wDgYD
|
||||
VR0PAQH/BAQDAgEGMA8GA1UdEwEB/wQFMAMBAf8wDQYJKoZIhvcNAQEFBQADggEB
|
||||
AKChOBZmLqdWHyGcBvod7bkixTgm2E5P7KN/ed5GIaGHd48HCJqypMWvDzKYC3xm
|
||||
KbabfSVSSUOrTC4rbnpwrxYO4wJs+0LmGJ1F2FXI6Dvd5+H0LgscNFxsWEr7jIhQ
|
||||
X5Ucv+2rIrVls4W6ng+4reV6G4pQOh29Dbx7VFALuUKvVaAYga1lme++5Jy/xIWr
|
||||
QbJUb9wlze144o4MjQlJ3WN7WmmWAiGovVJZ6X01y8hSyn+B/tlr0/cR7SXf+Of5
|
||||
pPpyl4RTDaXQMhhRdlkUbA/r7F+AjHVDg8OFmP9Mni0N5HeDk061lgeLKBObjBmN
|
||||
QSdJQO7e5iNEOdyhIta6A/I=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDuDCCAqCgAwIBAgIQDPCOXAgWpa1Cf/DrJxhZ0DANBgkqhkiG9w0BAQUFADBI
|
||||
MQswCQYDVQQGEwJVUzEgMB4GA1UEChMXU2VjdXJlVHJ1c3QgQ29ycG9yYXRpb24x
|
||||
FzAVBgNVBAMTDlNlY3VyZVRydXN0IENBMB4XDTA2MTEwNzE5MzExOFoXDTI5MTIz
|
||||
MTE5NDA1NVowSDELMAkGA1UEBhMCVVMxIDAeBgNVBAoTF1NlY3VyZVRydXN0IENv
|
||||
cnBvcmF0aW9uMRcwFQYDVQQDEw5TZWN1cmVUcnVzdCBDQTCCASIwDQYJKoZIhvcN
|
||||
AQEBBQADggEPADCCAQoCggEBAKukgeWVzfX2FI7CT8rU4niVWJxB4Q2ZQCQXOZEz
|
||||
Zum+4YOvYlyJ0fwkW2Gz4BERQRwdbvC4u/jep4G6pkjGnx29vo6pQT64lO0pGtSO
|
||||
0gMdA+9tDWccV9cGrcrI9f4Or2YlSASWC12juhbDCE/RRvgUXPLIXgGZbf2IzIao
|
||||
wW8xQmxSPmjL8xk037uHGFaAJsTQ3MBv396gwpEWoGQRS0S8Hvbn+mPeZqx2pHGj
|
||||
7DaUaHp3pLHnDi+BeuK1cobvomuL8A/b01k/unK8RCSc43Oz969XL0Imnal0ugBS
|
||||
8kvNU3xHCzaFDmapCJcWNFfBZveA4+1wVMeT4C4oFVmHursCAwEAAaOBnTCBmjAT
|
||||
BgkrBgEEAYI3FAIEBh4EAEMAQTALBgNVHQ8EBAMCAYYwDwYDVR0TAQH/BAUwAwEB
|
||||
/zAdBgNVHQ4EFgQUQjK2FvoE/f5dS3rD/fdMQB1aQ68wNAYDVR0fBC0wKzApoCeg
|
||||
JYYjaHR0cDovL2NybC5zZWN1cmV0cnVzdC5jb20vU1RDQS5jcmwwEAYJKwYBBAGC
|
||||
NxUBBAMCAQAwDQYJKoZIhvcNAQEFBQADggEBADDtT0rhWDpSclu1pqNlGKa7UTt3
|
||||
6Z3q059c4EVlew3KW+JwULKUBRSuSceNQQcSc5R+DCMh/bwQf2AQWnL1mA6s7Ll/
|
||||
3XpvXdMc9P+IBWlCqQVxyLesJugutIxq/3HcuLHfmbx8IVQr5Fiiu1cprp6poxkm
|
||||
D5kuCLDv/WnPmRoJjeOnnyvJNjR7JLN4TJUXpAYmHrZkUjZfYGfZnMUFdAvnZyPS
|
||||
CPyI6a6Lf+Ew9Dd+/cYy2i2eRDAwbO4H3tI0/NL/QPZL9GZGBlSm8jIKYyYwa5vR
|
||||
3ItHuuG51WLQoqD0ZwV4KWMabwTW+MZMo5qxN7SN5ShLHZ4swrhovO0C7jE=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDvDCCAqSgAwIBAgIQB1YipOjUiolN9BPI8PjqpTANBgkqhkiG9w0BAQUFADBK
|
||||
MQswCQYDVQQGEwJVUzEgMB4GA1UEChMXU2VjdXJlVHJ1c3QgQ29ycG9yYXRpb24x
|
||||
GTAXBgNVBAMTEFNlY3VyZSBHbG9iYWwgQ0EwHhcNMDYxMTA3MTk0MjI4WhcNMjkx
|
||||
MjMxMTk1MjA2WjBKMQswCQYDVQQGEwJVUzEgMB4GA1UEChMXU2VjdXJlVHJ1c3Qg
|
||||
Q29ycG9yYXRpb24xGTAXBgNVBAMTEFNlY3VyZSBHbG9iYWwgQ0EwggEiMA0GCSqG
|
||||
SIb3DQEBAQUAA4IBDwAwggEKAoIBAQCvNS7YrGxVaQZx5RNoJLNP2MwhR/jxYDiJ
|
||||
iQPpvepeRlMJ3Fz1Wuj3RSoC6zFh1ykzTM7HfAo3fg+6MpjhHZevj8fcyTiW89sa
|
||||
/FHtaMbQbqR8JNGuQsiWUGMu4P51/pinX0kuleM5M2SOHqRfkNJnPLLZ/kG5VacJ
|
||||
jnIFHovdRIWCQtBJwB1g8NEXLJXr9qXBkqPFwqcIYA1gBBCWeZ4WNOaptvolRTnI
|
||||
HmX5k/Wq8VLcmZg9pYYaDDUz+kulBAYVHDGA76oYa8J719rO+TMg1fW9ajMtgQT7
|
||||
sFzUnKPiXB3jqUJ1XnvUd+85VLrJChgbEplJL4hL/VBi0XPnj3pDAgMBAAGjgZ0w
|
||||
gZowEwYJKwYBBAGCNxQCBAYeBABDAEEwCwYDVR0PBAQDAgGGMA8GA1UdEwEB/wQF
|
||||
MAMBAf8wHQYDVR0OBBYEFK9EBMJBfkiD2045AuzshHrmzsmkMDQGA1UdHwQtMCsw
|
||||
KaAnoCWGI2h0dHA6Ly9jcmwuc2VjdXJldHJ1c3QuY29tL1NHQ0EuY3JsMBAGCSsG
|
||||
AQQBgjcVAQQDAgEAMA0GCSqGSIb3DQEBBQUAA4IBAQBjGghAfaReUw132HquHw0L
|
||||
URYD7xh8yOOvaliTFGCRsoTciE6+OYo68+aCiV0BN7OrJKQVDpI1WkpEXk5X+nXO
|
||||
H0jOZvQ8QCaSmGwb7iRGDBezUqXbpZGRzzfTb+cnCDpOGR86p1hcF895P4vkp9Mm
|
||||
I50mD1hp/Ed+stCNi5O/KU9DaXR2Z0vPB4zmAve14bRDtUstFJ/53CYNv6ZHdAbY
|
||||
iNE6KTCEztI5gGIbqMdXSbxqVVFnFUq+NQfk1XWYN3kwFNspnWzFacxHVaIw98xc
|
||||
f8LDmBxrThaA63p4ZUWiABqvDA1VZDRIuJK58bRQKfJPIx/abKwfROHdI3hRW8cW
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDdzCCAl+gAwIBAgIBADANBgkqhkiG9w0BAQsFADBdMQswCQYDVQQGEwJKUDEl
|
||||
MCMGA1UEChMcU0VDT00gVHJ1c3QgU3lzdGVtcyBDTy4sTFRELjEnMCUGA1UECxMe
|
||||
U2VjdXJpdHkgQ29tbXVuaWNhdGlvbiBSb290Q0EyMB4XDTA5MDUyOTA1MDAzOVoX
|
||||
DTI5MDUyOTA1MDAzOVowXTELMAkGA1UEBhMCSlAxJTAjBgNVBAoTHFNFQ09NIFRy
|
||||
dXN0IFN5c3RlbXMgQ08uLExURC4xJzAlBgNVBAsTHlNlY3VyaXR5IENvbW11bmlj
|
||||
YXRpb24gUm9vdENBMjCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBANAV
|
||||
OVKxUrO6xVmCxF1SrjpDZYBLx/KWvNs2l9amZIyoXvDjChz335c9S672XewhtUGr
|
||||
zbl+dp+++T42NKA7wfYxEUV0kz1XgMX5iZnK5atq1LXaQZAQwdbWQonCv/Q4EpVM
|
||||
VAX3NuRFg3sUZdbcDE3R3n4MqzvEFb46VqZab3ZpUql6ucjrappdUtAtCms1FgkQ
|
||||
hNBqyjoGADdH5H5XTz+L62e4iKrFvlNVspHEfbmwhRkGeC7bYRr6hfVKkaHnFtWO
|
||||
ojnflLhwHyg/i/xAXmODPIMqGplrz95Zajv8bxbXH/1KEOtOghY6rCcMU/Gt1SSw
|
||||
awNQwS08Ft1ENCcadfsCAwEAAaNCMEAwHQYDVR0OBBYEFAqFqXdlBZh8QIH4D5cs
|
||||
OPEK7DzPMA4GA1UdDwEB/wQEAwIBBjAPBgNVHRMBAf8EBTADAQH/MA0GCSqGSIb3
|
||||
DQEBCwUAA4IBAQBMOqNErLlFsceTfsgLCkLfZOoc7llsCLqJX2rKSpWeeo8HxdpF
|
||||
coJxDjrSzG+ntKEju/Ykn8sX/oymzsLS28yN/HH8AynBbF0zX2S2ZTuJbxh2ePXc
|
||||
okgfGT+Ok+vx+hfuzU7jBBJV1uXk3fs+BXziHV7Gp7yXT2g69ekuCkO2r1dcYmh8
|
||||
t/2jioSgrGK+KwmHNPBqAbubKVY8/gA3zyNs8U6qtnRGEmyR7jTV7JqR50S+kDFy
|
||||
1UkC9gLl9B/rfNmWVan/7Ir5mUf/NVoCqgTLiluHcSmRvaS0eg29mvVXIwAHIRc/
|
||||
SjnRBUkLp7Y3gaVdjKozXoEofKd9J+sAro03
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDWjCCAkKgAwIBAgIBADANBgkqhkiG9w0BAQUFADBQMQswCQYDVQQGEwJKUDEY
|
||||
MBYGA1UEChMPU0VDT00gVHJ1c3QubmV0MScwJQYDVQQLEx5TZWN1cml0eSBDb21t
|
||||
dW5pY2F0aW9uIFJvb3RDQTEwHhcNMDMwOTMwMDQyMDQ5WhcNMjMwOTMwMDQyMDQ5
|
||||
WjBQMQswCQYDVQQGEwJKUDEYMBYGA1UEChMPU0VDT00gVHJ1c3QubmV0MScwJQYD
|
||||
VQQLEx5TZWN1cml0eSBDb21tdW5pY2F0aW9uIFJvb3RDQTEwggEiMA0GCSqGSIb3
|
||||
DQEBAQUAA4IBDwAwggEKAoIBAQCzs/5/022x7xZ8V6UMbXaKL0u/ZPtM7orw8yl8
|
||||
9f/uKuDp6bpbZCKamm8sOiZpUQWZJtzVHGpxxpp9Hp3dfGzGjGdnSj74cbAZJ6kJ
|
||||
DKaVv0uMDPpVmDvY6CKhS3E4eayXkmmziX7qIWgGmBSWh9JhNrxtJ1aeV+7AwFb9
|
||||
Ms+k2Y7CI9eNqPPYJayX5HA49LY6tJ07lyZDo6G8SVlyTCMwhwFY9k6+HGhWZq/N
|
||||
QV3Is00qVUarH9oe4kA92819uZKAnDfdDJZkndwi92SL32HeFZRSFaB9UslLqCHJ
|
||||
xrHty8OVYNEP8Ktw+N/LTX7s1vqr2b1/VPKl6Xn62dZ2JChzAgMBAAGjPzA9MB0G
|
||||
A1UdDgQWBBSgc0mZaNyFW2XjmygvV5+9M7wHSDALBgNVHQ8EBAMCAQYwDwYDVR0T
|
||||
AQH/BAUwAwEB/zANBgkqhkiG9w0BAQUFAAOCAQEAaECpqLvkT115swW1F7NgE+vG
|
||||
kl3g0dNq/vu+m22/xwVtWSDEHPC32oRYAmP6SBbvT6UL90qY8j+eG61Ha2POCEfr
|
||||
Uj94nK9NrvjVT8+amCoQQTlSxN3Zmw7vkwGusi7KaEIkQmywszo+zenaSMQVy+n5
|
||||
Bw+SUEmK3TGXX8npN6o7WWWXlDLJs58+OmJYxUmtYg5xpTKqL8aJdkNAExNnPaJU
|
||||
JRDL8Try2frbSVa7pv6nQTXD4IhhyYjH3zYQIphZ6rBK+1YWc26sTfcioU+tHXot
|
||||
RSflMMFe8toTyyVCUZVHA4xsIcx0Qu1T/zOLjw9XARYvz6buyXAiFL39vmwLAw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDIDCCAgigAwIBAgIBHTANBgkqhkiG9w0BAQUFADA5MQswCQYDVQQGEwJGSTEP
|
||||
MA0GA1UEChMGU29uZXJhMRkwFwYDVQQDExBTb25lcmEgQ2xhc3MyIENBMB4XDTAx
|
||||
MDQwNjA3Mjk0MFoXDTIxMDQwNjA3Mjk0MFowOTELMAkGA1UEBhMCRkkxDzANBgNV
|
||||
BAoTBlNvbmVyYTEZMBcGA1UEAxMQU29uZXJhIENsYXNzMiBDQTCCASIwDQYJKoZI
|
||||
hvcNAQEBBQADggEPADCCAQoCggEBAJAXSjWdyvANlsdE+hY3/Ei9vX+ALTU74W+o
|
||||
Z6m/AxxNjG8yR9VBaKQTBME1DJqEQ/xcHf+Js+gXGM2RX/uJ4+q/Tl18GybTdXnt
|
||||
5oTjV+WtKcT0OijnpXuENmmz/V52vaMtmdOQTiMofRhj8VQ7Jp12W5dCsv+u8E7s
|
||||
3TmVToMGf+dJQMjFAbJUWmYdPfz56TwKnoG4cPABi+QjVHzIrviQHgCWctRUz2Ej
|
||||
vOr7nQKV0ba5cTppCD8PtOFCx4j1P5iop7oc4HFx71hXgVB6XGt0Rg6DA5jDjqhu
|
||||
8nYybieDwnPz3BjotJPqdURrBGAgcVeHnfO+oJAjPYok4doh28MCAwEAAaMzMDEw
|
||||
DwYDVR0TAQH/BAUwAwEB/zARBgNVHQ4ECgQISqCqWITTXjwwCwYDVR0PBAQDAgEG
|
||||
MA0GCSqGSIb3DQEBBQUAA4IBAQBazof5FnIVV0sd2ZvnoiYw7JNn39Yt0jSv9zil
|
||||
zqsWuasvfDXLrNAPtEwr/IDva4yRXzZ299uzGxnq9LIR/WFxRL8oszodv7ND6J+/
|
||||
3DEIcbCdjdY0RzKQxmUk96BKfARzjzlvF4xytb1LyHr4e4PDKE6cCepnP7JnBBvD
|
||||
FNr450kkkdAdavphOe9r5yF1BgfYErQhIHBCcYHaPJo2vqZbDWpsmh+Re/n570K6
|
||||
Tk6ezAyNlNzZRZxe7EJQY670XcSxEtzKO6gunRRaBXW37Ndj4ro1tgQIkejanZz2
|
||||
ZrUYrAqmVCY0M9IbwdR/GjqOC6oybtv8TyWf2TLHllpwrN9M
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFcDCCA1igAwIBAgIEAJiWjTANBgkqhkiG9w0BAQsFADBYMQswCQYDVQQGEwJO
|
||||
TDEeMBwGA1UECgwVU3RhYXQgZGVyIE5lZGVybGFuZGVuMSkwJwYDVQQDDCBTdGFh
|
||||
dCBkZXIgTmVkZXJsYW5kZW4gRVYgUm9vdCBDQTAeFw0xMDEyMDgxMTE5MjlaFw0y
|
||||
MjEyMDgxMTEwMjhaMFgxCzAJBgNVBAYTAk5MMR4wHAYDVQQKDBVTdGFhdCBkZXIg
|
||||
TmVkZXJsYW5kZW4xKTAnBgNVBAMMIFN0YWF0IGRlciBOZWRlcmxhbmRlbiBFViBS
|
||||
b290IENBMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEA48d+ifkkSzrS
|
||||
M4M1LGns3Amk41GoJSt5uAg94JG6hIXGhaTK5skuU6TJJB79VWZxXSzFYGgEt9nC
|
||||
UiY4iKTWO0Cmws0/zZiTs1QUWJZV1VD+hq2kY39ch/aO5ieSZxeSAgMs3NZmdO3d
|
||||
Z//BYY1jTw+bbRcwJu+r0h8QoPnFfxZpgQNH7R5ojXKhTbImxrpsX23Wr9GxE46p
|
||||
rfNeaXUmGD5BKyF/7otdBwadQ8QpCiv8Kj6GyzyDOvnJDdrFmeK8eEEzduG/L13l
|
||||
pJhQDBXd4Pqcfzho0LKmeqfRMb1+ilgnQ7O6M5HTp5gVXJrm0w912fxBmJc+qiXb
|
||||
j5IusHsMX/FjqTf5m3VpTCgmJdrV8hJwRVXj33NeN/UhbJCONVrJ0yPr08C+eKxC
|
||||
KFhmpUZtcALXEPlLVPxdhkqHz3/KRawRWrUgUY0viEeXOcDPusBCAUCZSCELa6fS
|
||||
/ZbV0b5GnUngC6agIk440ME8MLxwjyx1zNDFjFE7PZQIZCZhfbnDZY8UnCHQqv0X
|
||||
cgOPvZuM5l5Tnrmd74K74bzickFbIZTTRTeU0d8JOV3nI6qaHcptqAqGhYqCvkIH
|
||||
1vI4gnPah1vlPNOePqc7nvQDs/nxfRN0Av+7oeX6AHkcpmZBiFxgV6YuCcS6/ZrP
|
||||
px9Aw7vMWgpVSzs4dlG4Y4uElBbmVvMCAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB
|
||||
/zAOBgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFP6rAJCYniT8qcwaivsnuL8wbqg7
|
||||
MA0GCSqGSIb3DQEBCwUAA4ICAQDPdyxuVr5Os7aEAJSrR8kN0nbHhp8dB9O2tLsI
|
||||
eK9p0gtJ3jPFrK3CiAJ9Brc1AsFgyb/E6JTe1NOpEyVa/m6irn0F3H3zbPB+po3u
|
||||
2dfOWBfoqSmuc0iH55vKbimhZF8ZE/euBhD/UcabTVUlT5OZEAFTdfETzsemQUHS
|
||||
v4ilf0X8rLiltTMMgsT7B/Zq5SWEXwbKwYY5EdtYzXc7LMJMD16a4/CrPmEbUCTC
|
||||
wPTxGfARKbalGAKb12NMcIxHowNDXLldRqANb/9Zjr7dn3LDWyvfjFvO5QxGbJKy
|
||||
CqNMVEIYFRIYvdr8unRu/8G2oGTYqV9Vrp9canaW2HNnh/tNf1zuacpzEPuKqf2e
|
||||
vTY4SUmH9A4U8OmHuD+nT3pajnnUk+S7aFKErGzp85hwVXIy+TSrK0m1zSBi5Dp6
|
||||
Z2Orltxtrpfs/J92VoguZs9btsmksNcFuuEnL5O7Jiqik7Ab846+HUCjuTaPPoIa
|
||||
Gl6I6lD4WeKDRikL40Rc4ZW2aZCaFG+XroHPaO+Zmr615+F/+PoTRxZMzG0IQOeL
|
||||
eG9QgkRQP2YGiqtDhFZKDyAthg710tvSeopLzaXoTvFeJiUBWSOgftL2fiFX1ye8
|
||||
FVdMpEbB4IMeDExNH08GGeL5qPQ6gqGyeUN51q1veieQA6TqJIc/2b3Z6fJfUEkc
|
||||
7uzXLg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFyjCCA7KgAwIBAgIEAJiWjDANBgkqhkiG9w0BAQsFADBaMQswCQYDVQQGEwJO
|
||||
TDEeMBwGA1UECgwVU3RhYXQgZGVyIE5lZGVybGFuZGVuMSswKQYDVQQDDCJTdGFh
|
||||
dCBkZXIgTmVkZXJsYW5kZW4gUm9vdCBDQSAtIEcyMB4XDTA4MDMyNjExMTgxN1oX
|
||||
DTIwMDMyNTExMDMxMFowWjELMAkGA1UEBhMCTkwxHjAcBgNVBAoMFVN0YWF0IGRl
|
||||
ciBOZWRlcmxhbmRlbjErMCkGA1UEAwwiU3RhYXQgZGVyIE5lZGVybGFuZGVuIFJv
|
||||
b3QgQ0EgLSBHMjCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAMVZ5291
|
||||
qj5LnLW4rJ4L5PnZyqtdj7U5EILXr1HgO+EASGrP2uEGQxGZqhQlEq0i6ABtQ8Sp
|
||||
uOUfiUtnvWFI7/3S4GCI5bkYYCjDdyutsDeqN95kWSpGV+RLufg3fNU254DBtvPU
|
||||
Z5uW6M7XxgpT0GtJlvOjCwV3SPcl5XCsMBQgJeN/dVrlSPhOewMHBPqCYYdu8DvE
|
||||
pMfQ9XQ+pV0aCPKbJdL2rAQmPlU6Yiile7Iwr/g3wtG61jj99O9JMDeZJiFIhQGp
|
||||
5Rbn3JBV3w/oOM2ZNyFPXfUib2rFEhZgF1XyZWampzCROME4HYYEhLoaJXhena/M
|
||||
UGDWE4dS7WMfbWV9whUYdMrhfmQpjHLYFhN9C0lK8SgbIHRrxT3dsKpICT0ugpTN
|
||||
GmXZK4iambwYfp/ufWZ8Pr2UuIHOzZgweMFvZ9C+X+Bo7d7iscksWXiSqt8rYGPy
|
||||
5V6548r6f1CGPqI0GAwJaCgRHOThuVw+R7oyPxjMW4T182t0xHJ04eOLoEq9jWYv
|
||||
6q012iDTiIJh8BIitrzQ1aTsr1SIJSQ8p22xcik/Plemf1WvbibG/ufMQFxRRIEK
|
||||
eN5KzlW/HdXZt1bv8Hb/C3m1r737qWmRRpdogBQ2HbN/uymYNqUg+oJgYjOk7Na6
|
||||
B6duxc8UpufWkjTYgfX8HV2qXB72o007uPc5AgMBAAGjgZcwgZQwDwYDVR0TAQH/
|
||||
BAUwAwEB/zBSBgNVHSAESzBJMEcGBFUdIAAwPzA9BggrBgEFBQcCARYxaHR0cDov
|
||||
L3d3dy5wa2lvdmVyaGVpZC5ubC9wb2xpY2llcy9yb290LXBvbGljeS1HMjAOBgNV
|
||||
HQ8BAf8EBAMCAQYwHQYDVR0OBBYEFJFoMocVHYnitfGsNig0jQt8YojrMA0GCSqG
|
||||
SIb3DQEBCwUAA4ICAQCoQUpnKpKBglBu4dfYszk78wIVCVBR7y29JHuIhjv5tLyS
|
||||
CZa59sCrI2AGeYwRTlHSeYAz+51IvuxBQ4EffkdAHOV6CMqqi3WtFMTC6GY8ggen
|
||||
5ieCWxjmD27ZUD6KQhgpxrRW/FYQoAUXvQwjf/ST7ZwaUb7dRUG/kSS0H4zpX897
|
||||
IZmflZ85OkYcbPnNe5yQzSipx6lVu6xiNGI1E0sUOlWDuYaNkqbG9AclVMwWVxJK
|
||||
gnjIFNkXgiYtXSAfea7+1HAWFpWD2DU5/1JddRwWxRNVz0fMdWVSSt7wsKfkCpYL
|
||||
+63C4iWEst3kvX5ZbJvw8NjnyvLplzh+ib7M+zkXYT9y2zqR2GUBGR2tUKRXCnxL
|
||||
vJxxcypFURmFzI79R6d0lR2o0a9OF7FpJsKqeFdbxU2n5Z4FF5TKsl+gSRiNNOkm
|
||||
bEgeqmiSBeGCc1qb3AdbCG19ndeNIdn8FCCqwkXfP+cAslHkwvgFuXkajDTznlvk
|
||||
N1trSt8sV4pAWja63XVECDdCcAz+3F4hoKOKwJCcaNpQ5kUQR3i2TtJlycM33+FC
|
||||
Y7BXN0Ute4qcvwXqZVUz9zkQxSgqIXobisQk+T8VyJoVIPVVYpbtbZNQvOSqeK3Z
|
||||
ywplh6ZmwcSBo3c6WB4L7oOLnR7SUqTMHW+wmG2UMbX4cQrcufx9MmDm66+KAQ==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFdDCCA1ygAwIBAgIEAJiiOTANBgkqhkiG9w0BAQsFADBaMQswCQYDVQQGEwJO
|
||||
TDEeMBwGA1UECgwVU3RhYXQgZGVyIE5lZGVybGFuZGVuMSswKQYDVQQDDCJTdGFh
|
||||
dCBkZXIgTmVkZXJsYW5kZW4gUm9vdCBDQSAtIEczMB4XDTEzMTExNDExMjg0MloX
|
||||
DTI4MTExMzIzMDAwMFowWjELMAkGA1UEBhMCTkwxHjAcBgNVBAoMFVN0YWF0IGRl
|
||||
ciBOZWRlcmxhbmRlbjErMCkGA1UEAwwiU3RhYXQgZGVyIE5lZGVybGFuZGVuIFJv
|
||||
b3QgQ0EgLSBHMzCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAL4yolQP
|
||||
cPssXFnrbMSkUeiFKrPMSjTysF/zDsccPVMeiAho2G89rcKezIJnByeHaHE6n3WW
|
||||
IkYFsO2tx1ueKt6c/DrGlaf1F2cY5y9JCAxcz+bMNO14+1Cx3Gsy8KL+tjzk7FqX
|
||||
xz8ecAgwoNzFs21v0IJyEavSgWhZghe3eJJg+szeP4TrjTgzkApyI/o1zCZxMdFy
|
||||
KJLZWyNtZrVtB0LrpjPOktvA9mxjeM3KTj215VKb8b475lRgsGYeCasH/lSJEULR
|
||||
9yS6YHgamPfJEf0WwTUaVHXvQ9Plrk7O53vDxk5hUUurmkVLoR9BvUhTFXFkC4az
|
||||
5S6+zqQbwSmEorXLCCN2QyIkHxcE1G6cxvx/K2Ya7Irl1s9N9WMJtxU51nus6+N8
|
||||
6U78dULI7ViVDAZCopz35HCz33JvWjdAidiFpNfxC95DGdRKWCyMijmev4SH8RY7
|
||||
Ngzp07TKbBlBUgmhHbBqv4LvcFEhMtwFdozL92TkA1CvjJFnq8Xy7ljY3r735zHP
|
||||
bMk7ccHViLVlvMDoFxcHErVc0qsgk7TmgoNwNsXNo42ti+yjwUOH5kPiNL6VizXt
|
||||
BznaqB16nzaeErAMZRKQFWDZJkBE41ZgpRDUajz9QdwOWke275dhdU/Z/seyHdTt
|
||||
XUmzqWrLZoQT1Vyg3N9udwbRcXXIV2+vD3dbAgMBAAGjQjBAMA8GA1UdEwEB/wQF
|
||||
MAMBAf8wDgYDVR0PAQH/BAQDAgEGMB0GA1UdDgQWBBRUrfrHkleuyjWcLhL75Lpd
|
||||
INyUVzANBgkqhkiG9w0BAQsFAAOCAgEAMJmdBTLIXg47mAE6iqTnB/d6+Oea31BD
|
||||
U5cqPco8R5gu4RV78ZLzYdqQJRZlwJ9UXQ4DO1t3ApyEtg2YXzTdO2PCwyiBwpwp
|
||||
LiniyMMB8jPqKqrMCQj3ZWfGzd/TtiunvczRDnBfuCPRy5FOCvTIeuXZYzbB1N/8
|
||||
Ipf3YF3qKS9Ysr1YvY2WTxB1v0h7PVGHoTx0IsL8B3+A3MSs/mrBcDCw6Y5p4ixp
|
||||
gZQJut3+TcCDjJRYwEYgr5wfAvg1VUkvRtTA8KCWAg8zxXHzniN9lLf9OtMJgwYh
|
||||
/WA9rjLA0u6NpvDntIJ8CsxwyXmA+P5M9zWEGYox+wrZ13+b8KKaa8MFSu1BYBQw
|
||||
0aoRQm7TIwIEC8Zl3d1Sd9qBa7Ko+gE4uZbqKmxnl4mUnrzhVNXkanjvSr0rmj1A
|
||||
fsbAddJu+2gw7OyLnflJNZoaLNmzlTnVHpL3prllL+U9bTpITAjc5CgSKL59NVzq
|
||||
4BZ+Extq1z7XnvwtdbLBFNUjA9tbbws+eC8N3jONFrdI54OagQ97wUNNVQQXOEpR
|
||||
1VmiiXTTn74eS9fGbbeIJG9gkaSChVtWQbzQRKtqE77RLFi3EjNYsjdj3BP1lB0/
|
||||
QFH1T/U67cjF68IeHRaVesd+QnGTbksVtzDfqu1XhUisHWrdOWnk4Xl4vs4Fv6EM
|
||||
94B7IWcnMFk=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEDzCCAvegAwIBAgIBADANBgkqhkiG9w0BAQUFADBoMQswCQYDVQQGEwJVUzEl
|
||||
MCMGA1UEChMcU3RhcmZpZWxkIFRlY2hub2xvZ2llcywgSW5jLjEyMDAGA1UECxMp
|
||||
U3RhcmZpZWxkIENsYXNzIDIgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMDQw
|
||||
NjI5MTczOTE2WhcNMzQwNjI5MTczOTE2WjBoMQswCQYDVQQGEwJVUzElMCMGA1UE
|
||||
ChMcU3RhcmZpZWxkIFRlY2hub2xvZ2llcywgSW5jLjEyMDAGA1UECxMpU3RhcmZp
|
||||
ZWxkIENsYXNzIDIgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwggEgMA0GCSqGSIb3
|
||||
DQEBAQUAA4IBDQAwggEIAoIBAQC3Msj+6XGmBIWtDBFk385N78gDGIc/oav7PKaf
|
||||
8MOh2tTYbitTkPskpD6E8J7oX+zlJ0T1KKY/e97gKvDIr1MvnsoFAZMej2YcOadN
|
||||
+lq2cwQlZut3f+dZxkqZJRRU6ybH838Z1TBwj6+wRir/resp7defqgSHo9T5iaU0
|
||||
X9tDkYI22WY8sbi5gv2cOj4QyDvvBmVmepsZGD3/cVE8MC5fvj13c7JdBmzDI1aa
|
||||
K4UmkhynArPkPw2vCHmCuDY96pzTNbO8acr1zJ3o/WSNF4Azbl5KXZnJHoe0nRrA
|
||||
1W4TNSNe35tfPe/W93bC6j67eA0cQmdrBNj41tpvi/JEoAGrAgEDo4HFMIHCMB0G
|
||||
A1UdDgQWBBS/X7fRzt0fhvRbVazc1xDCDqmI5zCBkgYDVR0jBIGKMIGHgBS/X7fR
|
||||
zt0fhvRbVazc1xDCDqmI56FspGowaDELMAkGA1UEBhMCVVMxJTAjBgNVBAoTHFN0
|
||||
YXJmaWVsZCBUZWNobm9sb2dpZXMsIEluYy4xMjAwBgNVBAsTKVN0YXJmaWVsZCBD
|
||||
bGFzcyAyIENlcnRpZmljYXRpb24gQXV0aG9yaXR5ggEAMAwGA1UdEwQFMAMBAf8w
|
||||
DQYJKoZIhvcNAQEFBQADggEBAAWdP4id0ckaVaGsafPzWdqbAYcaT1epoXkJKtv3
|
||||
L7IezMdeatiDh6GX70k1PncGQVhiv45YuApnP+yz3SFmH8lU+nLMPUxA2IGvd56D
|
||||
eruix/U0F47ZEUD0/CwqTRV/p2JdLiXTAAsgGh1o+Re49L2L7ShZ3U0WixeDyLJl
|
||||
xy16paq8U4Zt3VekyvggQQto8PT7dL5WXXp59fkdheMtlb71cZBDzI0fmgAKhynp
|
||||
VSJYACPq4xJDKVtHCN2MQWplBqjlIapBtJUhlbl90TSrE9atvNziPTnNvT51cKEY
|
||||
WQPJIrSPnNVeKtelttQKbfi3QBFGmh95DmK/D5fs4C8fF5Q=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIID3TCCAsWgAwIBAgIBADANBgkqhkiG9w0BAQsFADCBjzELMAkGA1UEBhMCVVMx
|
||||
EDAOBgNVBAgTB0FyaXpvbmExEzARBgNVBAcTClNjb3R0c2RhbGUxJTAjBgNVBAoT
|
||||
HFN0YXJmaWVsZCBUZWNobm9sb2dpZXMsIEluYy4xMjAwBgNVBAMTKVN0YXJmaWVs
|
||||
ZCBSb290IENlcnRpZmljYXRlIEF1dGhvcml0eSAtIEcyMB4XDTA5MDkwMTAwMDAw
|
||||
MFoXDTM3MTIzMTIzNTk1OVowgY8xCzAJBgNVBAYTAlVTMRAwDgYDVQQIEwdBcml6
|
||||
b25hMRMwEQYDVQQHEwpTY290dHNkYWxlMSUwIwYDVQQKExxTdGFyZmllbGQgVGVj
|
||||
aG5vbG9naWVzLCBJbmMuMTIwMAYDVQQDEylTdGFyZmllbGQgUm9vdCBDZXJ0aWZp
|
||||
Y2F0ZSBBdXRob3JpdHkgLSBHMjCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoC
|
||||
ggEBAL3twQP89o/8ArFvW59I2Z154qK3A2FWGMNHttfKPTUuiUP3oWmb3ooa/RMg
|
||||
nLRJdzIpVv257IzdIvpy3Cdhl+72WoTsbhm5iSzchFvVdPtrX8WJpRBSiUZV9Lh1
|
||||
HOZ/5FSuS/hVclcCGfgXcVnrHigHdMWdSL5stPSksPNkN3mSwOxGXn/hbVNMYq/N
|
||||
Hwtjuzqd+/x5AJhhdM8mgkBj87JyahkNmcrUDnXMN/uLicFZ8WJ/X7NfZTD4p7dN
|
||||
dloedl40wOiWVpmKs/B/pM293DIxfJHP4F8R+GuqSVzRmZTRouNjWwl2tVZi4Ut0
|
||||
HZbUJtQIBFnQmA4O5t78w+wfkPECAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAO
|
||||
BgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFHwMMh+n2TB/xH1oo2Kooc6rB1snMA0G
|
||||
CSqGSIb3DQEBCwUAA4IBAQARWfolTwNvlJk7mh+ChTnUdgWUXuEok21iXQnCoKjU
|
||||
sHU48TRqneSfioYmUeYs0cYtbpUgSpIB7LiKZ3sx4mcujJUDJi5DnUox9g61DLu3
|
||||
4jd/IroAow57UvtruzvE03lRTs2Q9GcHGcg8RnoNAX3FWOdt5oUwF5okxBDgBPfg
|
||||
8n/Uqgr/Qh037ZTlZFkSIHc40zI+OIF1lnP6aI+xy84fxez6nH7PfrHxBy22/L/K
|
||||
pL/QlwVKvOoYKAKQvVR4CSFx09F9HdkWsKlhPdAKACL8x3vLCWRFCztAgfd9fDL1
|
||||
mMpYjn0q7pBZc2T5NnReJaH1ZgUufzkVqSr7UIuOhWn0
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIID7zCCAtegAwIBAgIBADANBgkqhkiG9w0BAQsFADCBmDELMAkGA1UEBhMCVVMx
|
||||
EDAOBgNVBAgTB0FyaXpvbmExEzARBgNVBAcTClNjb3R0c2RhbGUxJTAjBgNVBAoT
|
||||
HFN0YXJmaWVsZCBUZWNobm9sb2dpZXMsIEluYy4xOzA5BgNVBAMTMlN0YXJmaWVs
|
||||
ZCBTZXJ2aWNlcyBSb290IENlcnRpZmljYXRlIEF1dGhvcml0eSAtIEcyMB4XDTA5
|
||||
MDkwMTAwMDAwMFoXDTM3MTIzMTIzNTk1OVowgZgxCzAJBgNVBAYTAlVTMRAwDgYD
|
||||
VQQIEwdBcml6b25hMRMwEQYDVQQHEwpTY290dHNkYWxlMSUwIwYDVQQKExxTdGFy
|
||||
ZmllbGQgVGVjaG5vbG9naWVzLCBJbmMuMTswOQYDVQQDEzJTdGFyZmllbGQgU2Vy
|
||||
dmljZXMgUm9vdCBDZXJ0aWZpY2F0ZSBBdXRob3JpdHkgLSBHMjCCASIwDQYJKoZI
|
||||
hvcNAQEBBQADggEPADCCAQoCggEBANUMOsQq+U7i9b4Zl1+OiFOxHz/Lz58gE20p
|
||||
OsgPfTz3a3Y4Y9k2YKibXlwAgLIvWX/2h/klQ4bnaRtSmpDhcePYLQ1Ob/bISdm2
|
||||
8xpWriu2dBTrz/sm4xq6HZYuajtYlIlHVv8loJNwU4PahHQUw2eeBGg6345AWh1K
|
||||
Ts9DkTvnVtYAcMtS7nt9rjrnvDH5RfbCYM8TWQIrgMw0R9+53pBlbQLPLJGmpufe
|
||||
hRhJfGZOozptqbXuNC66DQO4M99H67FrjSXZm86B0UVGMpZwh94CDklDhbZsc7tk
|
||||
6mFBrMnUVN+HL8cisibMn1lUaJ/8viovxFUcdUBgF4UCVTmLfwUCAwEAAaNCMEAw
|
||||
DwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAQYwHQYDVR0OBBYEFJxfAN+q
|
||||
AdcwKziIorhtSpzyEZGDMA0GCSqGSIb3DQEBCwUAA4IBAQBLNqaEd2ndOxmfZyMI
|
||||
bw5hyf2E3F/YNoHN2BtBLZ9g3ccaaNnRbobhiCPPE95Dz+I0swSdHynVv/heyNXB
|
||||
ve6SbzJ08pGCL72CQnqtKrcgfU28elUSwhXqvfdqlS5sdJ/PHLTyxQGjhdByPq1z
|
||||
qwubdQxtRbeOlKyWN7Wg0I8VRw7j6IPdj/3vQQF3zCepYoUz8jcI73HPdwbeyBkd
|
||||
iEDPfUYd/x7H4c7/I9vG+o1VTqkC50cRRj70/b17KSa7qWFiNyi2LSr2EIZkyXCn
|
||||
0q23KXB56jzaYyWf/Wi3MOxw+3WKt21gZ7IeyLnp2KhvAotnDU0mV3HaIPzBSlCN
|
||||
sSi6
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFujCCA6KgAwIBAgIJALtAHEP1Xk+wMA0GCSqGSIb3DQEBBQUAMEUxCzAJBgNV
|
||||
BAYTAkNIMRUwEwYDVQQKEwxTd2lzc1NpZ24gQUcxHzAdBgNVBAMTFlN3aXNzU2ln
|
||||
biBHb2xkIENBIC0gRzIwHhcNMDYxMDI1MDgzMDM1WhcNMzYxMDI1MDgzMDM1WjBF
|
||||
MQswCQYDVQQGEwJDSDEVMBMGA1UEChMMU3dpc3NTaWduIEFHMR8wHQYDVQQDExZT
|
||||
d2lzc1NpZ24gR29sZCBDQSAtIEcyMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIIC
|
||||
CgKCAgEAr+TufoskDhJuqVAtFkQ7kpJcyrhdhJJCEyq8ZVeCQD5XJM1QiyUqt2/8
|
||||
76LQwB8CJEoTlo8jE+YoWACjR8cGp4QjK7u9lit/VcyLwVcfDmJlD909Vopz2q5+
|
||||
bbqBHH5CjCA12UNNhPqE21Is8w4ndwtrvxEvcnifLtg+5hg3Wipy+dpikJKVyh+c
|
||||
6bM8K8vzARO/Ws/BtQpgvd21mWRTuKCWs2/iJneRjOBiEAKfNA+k1ZIzUd6+jbqE
|
||||
emA8atufK+ze3gE/bk3lUIbLtK/tREDFylqM2tIrfKjuvqblCqoOpd8FUrdVxyJd
|
||||
MmqXl2MT28nbeTZ7hTpKxVKJ+STnnXepgv9VHKVxaSvRAiTysybUa9oEVeXBCsdt
|
||||
MDeQKuSeFDNeFhdVxVu1yzSJkvGdJo+hB9TGsnhQ2wwMC3wLjEHXuendjIj3o02y
|
||||
MszYF9rNt85mndT9Xv+9lz4pded+p2JYryU0pUHHPbwNUMoDAw8IWh+Vc3hiv69y
|
||||
FGkOpeUDDniOJihC8AcLYiAQZzlG+qkDzAQ4embvIIO1jEpWjpEA/I5cgt6IoMPi
|
||||
aG59je883WX0XaxR7ySArqpWl2/5rX3aYT+YdzylkbYcjCbaZaIJbcHiVOO5ykxM
|
||||
gI93e2CaHt+28kgeDrpOVG2Y4OGiGqJ3UM/EY5LsRxmd6+ZrzsECAwEAAaOBrDCB
|
||||
qTAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUWyV7
|
||||
lqRlUX64OfPAeGZe6Drn8O4wHwYDVR0jBBgwFoAUWyV7lqRlUX64OfPAeGZe6Drn
|
||||
8O4wRgYDVR0gBD8wPTA7BglghXQBWQECAQEwLjAsBggrBgEFBQcCARYgaHR0cDov
|
||||
L3JlcG9zaXRvcnkuc3dpc3NzaWduLmNvbS8wDQYJKoZIhvcNAQEFBQADggIBACe6
|
||||
45R88a7A3hfm5djV9VSwg/S7zV4Fe0+fdWavPOhWfvxyeDgD2StiGwC5+OlgzczO
|
||||
UYrHUDFu4Up+GC9pWbY9ZIEr44OE5iKHjn3g7gKZYbge9LgriBIWhMIxkziWMaa5
|
||||
O1M/wySTVltpkuzFwbs4AOPsF6m43Md8AYOfMke6UiI0HTJ6CVanfCU2qT1L2sCC
|
||||
bwq7EsiHSycR+R4tx5M/nttfJmtS2S6K8RTGRI0Vqbe/vd6mGu6uLftIdxf+u+yv
|
||||
GPUqUfA5hJeVbG4bwyvEdGB5JbAKJ9/fXtI5z0V9QkvfsywexcZdylU6oJxpmo/a
|
||||
77KwPJ+HbBIrZXAVUjEaJM9vMSNQH4xPjyPDdEFjHFWoFN0+4FFQz/EbMFYOkrCC
|
||||
hdiDyyJkvC24JdVUorgG6q2SpCSgwYa1ShNqR88uC1aVVMvOmttqtKay20EIhid3
|
||||
92qgQmwLOM7XdVAyksLfKzAiSNDVQTglXaTpXZ/GlHXQRf0wl0OPkKsKx4ZzYEpp
|
||||
Ld6leNcG2mqeSz53OiATIgHQv2ieY2BrNU0LbbqhPcCT4H8js1WtciVORvnSFu+w
|
||||
ZMEBnunKoGqYDs/YYPIvSbjkQuE4NRb0yG5P94FW6LqjviOvrv1vA+ACOzB2+htt
|
||||
Qc8Bsem4yWb02ybzOqR08kkkW8mw0FfB+j564ZfJ
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFvTCCA6WgAwIBAgIITxvUL1S7L0swDQYJKoZIhvcNAQEFBQAwRzELMAkGA1UE
|
||||
BhMCQ0gxFTATBgNVBAoTDFN3aXNzU2lnbiBBRzEhMB8GA1UEAxMYU3dpc3NTaWdu
|
||||
IFNpbHZlciBDQSAtIEcyMB4XDTA2MTAyNTA4MzI0NloXDTM2MTAyNTA4MzI0Nlow
|
||||
RzELMAkGA1UEBhMCQ0gxFTATBgNVBAoTDFN3aXNzU2lnbiBBRzEhMB8GA1UEAxMY
|
||||
U3dpc3NTaWduIFNpbHZlciBDQSAtIEcyMIICIjANBgkqhkiG9w0BAQEFAAOCAg8A
|
||||
MIICCgKCAgEAxPGHf9N4Mfc4yfjDmUO8x/e8N+dOcbpLj6VzHVxumK4DV644N0Mv
|
||||
Fz0fyM5oEMF4rhkDKxD6LHmD9ui5aLlV8gREpzn5/ASLHvGiTSf5YXu6t+WiE7br
|
||||
YT7QbNHm+/pe7R20nqA1W6GSy/BJkv6FCgU+5tkL4k+73JU3/JHpMjUi0R86TieF
|
||||
nbAVlDLaYQ1HTWBCrpJH6INaUFjpiou5XaHc3ZlKHzZnu0jkg7Y360g6rw9njxcH
|
||||
6ATK72oxh9TAtvmUcXtnZLi2kUpCe2UuMGoM9ZDulebyzYLs2aFK7PayS+VFheZt
|
||||
eJMELpyCbTapxDFkH4aDCyr0NQp4yVXPQbBH6TCfmb5hqAaEuSh6XzjZG6k4sIN/
|
||||
c8HDO0gqgg8hm7jMqDXDhBuDsz6+pJVpATqJAHgE2cn0mRmrVn5bi4Y5FZGkECwJ
|
||||
MoBgs5PAKrYYC51+jUnyEEp/+dVGLxmSo5mnJqy7jDzmDrxHB9xzUfFwZC8I+bRH
|
||||
HTBsROopN4WSaGa8gzj+ezku01DwH/teYLappvonQfGbGHLy9YR0SslnxFSuSGTf
|
||||
jNFusB3hB48IHpmccelM2KX3RxIfdNFRnobzwqIjQAtz20um53MGjMGg6cFZrEb6
|
||||
5i/4z3GcRm25xBWNOHkDRUjvxF3XCO6HOSKGsg0PWEP3calILv3q1h8CAwEAAaOB
|
||||
rDCBqTAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQU
|
||||
F6DNweRBtjpbO8tFnb0cwpj6hlgwHwYDVR0jBBgwFoAUF6DNweRBtjpbO8tFnb0c
|
||||
wpj6hlgwRgYDVR0gBD8wPTA7BglghXQBWQEDAQEwLjAsBggrBgEFBQcCARYgaHR0
|
||||
cDovL3JlcG9zaXRvcnkuc3dpc3NzaWduLmNvbS8wDQYJKoZIhvcNAQEFBQADggIB
|
||||
AHPGgeAn0i0P4JUw4ppBf1AsX19iYamGamkYDHRJ1l2E6kFSGG9YrVBWIGrGvShp
|
||||
WJHckRE1qTodvBqlYJ7YH39FkWnZfrt4csEGDyrOj4VwYaygzQu4OSlWhDJOhrs9
|
||||
xCrZ1x9y7v5RoSJBsXECYxqCsGKrXlcSH9/L3XWgwF15kIwb4FDm3jH+mHtwX6WQ
|
||||
2K34ArZv02DdQEsixT2tOnqfGhpHkXkzuoLcMmkDlm4fS/Bx/uNncqCxv1yL5PqZ
|
||||
IseEuRuNI5c/7SXgz2W79WEE790eslpBIlqhn10s6FvJbakMDHiqYMZWjwFaDGi8
|
||||
aRl5xB9+lwW/xekkUV7U1UtT7dkjWjYDZaPBA61BMPNGG4WQr2W11bHkFlt4dR2X
|
||||
em1ZqSqPe97Dh4kQmUlzeMg9vVE1dCrV8X5pGyq7O70luJpaPXJhkGaH7gzWTdQR
|
||||
dAtq/gsD/KNVV4n+SsuuWxcFyPKNIzFTONItaj+CuY0IavdeQXRuwxF+B6wpYJE/
|
||||
OMpXEA29MC/HpeZBoNquBYeaoKRlbEwJDIm6uNO5wJOKMPqN5ZprFQFOZ6raYlY+
|
||||
hAhm0sQ2fac+EPyI4NSA5QC9qvNOBqN6avlicuMJT+ubDgEj8Z+7fNzcbBGXJbLy
|
||||
tGMU0gYqZ4yD9c7qB9iaah7s5Aq7KkzrCWA5zspi2C5u
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDwzCCAqugAwIBAgIBATANBgkqhkiG9w0BAQsFADCBgjELMAkGA1UEBhMCREUx
|
||||
KzApBgNVBAoMIlQtU3lzdGVtcyBFbnRlcnByaXNlIFNlcnZpY2VzIEdtYkgxHzAd
|
||||
BgNVBAsMFlQtU3lzdGVtcyBUcnVzdCBDZW50ZXIxJTAjBgNVBAMMHFQtVGVsZVNl
|
||||
YyBHbG9iYWxSb290IENsYXNzIDIwHhcNMDgxMDAxMTA0MDE0WhcNMzMxMDAxMjM1
|
||||
OTU5WjCBgjELMAkGA1UEBhMCREUxKzApBgNVBAoMIlQtU3lzdGVtcyBFbnRlcnBy
|
||||
aXNlIFNlcnZpY2VzIEdtYkgxHzAdBgNVBAsMFlQtU3lzdGVtcyBUcnVzdCBDZW50
|
||||
ZXIxJTAjBgNVBAMMHFQtVGVsZVNlYyBHbG9iYWxSb290IENsYXNzIDIwggEiMA0G
|
||||
CSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCqX9obX+hzkeXaXPSi5kfl82hVYAUd
|
||||
AqSzm1nzHoqvNK38DcLZSBnuaY/JIPwhqgcZ7bBcrGXHX+0CfHt8LRvWurmAwhiC
|
||||
FoT6ZrAIxlQjgeTNuUk/9k9uN0goOA/FvudocP05l03Sx5iRUKrERLMjfTlH6VJi
|
||||
1hKTXrcxlkIF+3anHqP1wvzpesVsqXFP6st4vGCvx9702cu+fjOlbpSD8DT6Iavq
|
||||
jnKgP6TeMFvvhk1qlVtDRKgQFRzlAVfFmPHmBiiRqiDFt1MmUUOyCxGVWOHAD3bZ
|
||||
wI18gfNycJ5v/hqO2V81xrJvNHy+SE/iWjnX2J14np+GPgNeGYtEotXHAgMBAAGj
|
||||
QjBAMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgEGMB0GA1UdDgQWBBS/
|
||||
WSA2AHmgoCJrjNXyYdK4LMuCSjANBgkqhkiG9w0BAQsFAAOCAQEAMQOiYQsfdOhy
|
||||
NsZt+U2e+iKo4YFWz827n+qrkRk4r6p8FU3ztqONpfSO9kSpp+ghla0+AGIWiPAC
|
||||
uvxhI+YzmzB6azZie60EI4RYZeLbK4rnJVM3YlNfvNoBYimipidx5joifsFvHZVw
|
||||
IEoHNN/q/xWA5brXethbdXwFeilHfkCoMRN3zUA7tFFHei4R40cR3p1m0IvVVGb6
|
||||
g1XqfMIpiRvpb7PO4gWEyS8+eIVibslfwXhjdFjASBgMmTnrpMwatXlajRWc2BQN
|
||||
9noHV8cigwUtPJslJj0Ys6lDfMjIq2SPDqO/nBudMNva0Bkuqjzx+zOAduTNrRlP
|
||||
BSeOE6Fuwg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDwzCCAqugAwIBAgIBATANBgkqhkiG9w0BAQsFADCBgjELMAkGA1UEBhMCREUx
|
||||
KzApBgNVBAoMIlQtU3lzdGVtcyBFbnRlcnByaXNlIFNlcnZpY2VzIEdtYkgxHzAd
|
||||
BgNVBAsMFlQtU3lzdGVtcyBUcnVzdCBDZW50ZXIxJTAjBgNVBAMMHFQtVGVsZVNl
|
||||
YyBHbG9iYWxSb290IENsYXNzIDMwHhcNMDgxMDAxMTAyOTU2WhcNMzMxMDAxMjM1
|
||||
OTU5WjCBgjELMAkGA1UEBhMCREUxKzApBgNVBAoMIlQtU3lzdGVtcyBFbnRlcnBy
|
||||
aXNlIFNlcnZpY2VzIEdtYkgxHzAdBgNVBAsMFlQtU3lzdGVtcyBUcnVzdCBDZW50
|
||||
ZXIxJTAjBgNVBAMMHFQtVGVsZVNlYyBHbG9iYWxSb290IENsYXNzIDMwggEiMA0G
|
||||
CSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQC9dZPwYiJvJK7genasfb3ZJNW4t/zN
|
||||
8ELg63iIVl6bmlQdTQyK9tPPcPRStdiTBONGhnFBSivwKixVA9ZIw+A5OO3yXDw/
|
||||
RLyTPWGrTs0NvvAgJ1gORH8EGoel15YUNpDQSXuhdfsaa3Ox+M6pCSzyU9XDFES4
|
||||
hqX2iys52qMzVNn6chr3IhUciJFrf2blw2qAsCTz34ZFiP0Zf3WHHx+xGwpzJFu5
|
||||
ZeAsVMhg02YXP+HMVDNzkQI6pn97djmiH5a2OK61yJN0HZ65tOVgnS9W0eDrXltM
|
||||
EnAMbEQgqxHY9Bn20pxSN+f6tsIxO0rUFJmtxxr1XV/6B7h8DR/Wgx6zAgMBAAGj
|
||||
QjBAMA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgEGMB0GA1UdDgQWBBS1
|
||||
A/d2O2GCahKqGFPrAyGUv/7OyjANBgkqhkiG9w0BAQsFAAOCAQEAVj3vlNW92nOy
|
||||
WL6ukK2YJ5f+AbGwUgC4TeQbIXQbfsDuXmkqJa9c1h3a0nnJ85cp4IaH3gRZD/FZ
|
||||
1GSFS5mvJQQeyUapl96Cshtwn5z2r3Ex3XsFpSzTucpH9sry9uetuUg/vBa3wW30
|
||||
6gmv7PO15wWeph6KU1HWk4HMdJP2udqmJQV0eVp+QD6CSyYRMG7hP0HHRwA11fXT
|
||||
91Q+gT3aSWqas+8QPebrb9HIIkfLzM8BMZLZGOMivgkeGj5asuRrDFR6fUNOuIml
|
||||
e9eiPZaGzPImNC1qkp2aGtAw4l1OBLBfiyB+d8E9lYLRRpo7PHi4b6HQDWSieB4p
|
||||
TpPDpFQUWw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEYzCCA0ugAwIBAgIBATANBgkqhkiG9w0BAQsFADCB0jELMAkGA1UEBhMCVFIx
|
||||
GDAWBgNVBAcTD0dlYnplIC0gS29jYWVsaTFCMEAGA1UEChM5VHVya2l5ZSBCaWxp
|
||||
bXNlbCB2ZSBUZWtub2xvamlrIEFyYXN0aXJtYSBLdXJ1bXUgLSBUVUJJVEFLMS0w
|
||||
KwYDVQQLEyRLYW11IFNlcnRpZmlrYXN5b24gTWVya2V6aSAtIEthbXUgU00xNjA0
|
||||
BgNVBAMTLVRVQklUQUsgS2FtdSBTTSBTU0wgS29rIFNlcnRpZmlrYXNpIC0gU3Vy
|
||||
dW0gMTAeFw0xMzExMjUwODI1NTVaFw00MzEwMjUwODI1NTVaMIHSMQswCQYDVQQG
|
||||
EwJUUjEYMBYGA1UEBxMPR2ViemUgLSBLb2NhZWxpMUIwQAYDVQQKEzlUdXJraXll
|
||||
IEJpbGltc2VsIHZlIFRla25vbG9qaWsgQXJhc3Rpcm1hIEt1cnVtdSAtIFRVQklU
|
||||
QUsxLTArBgNVBAsTJEthbXUgU2VydGlmaWthc3lvbiBNZXJrZXppIC0gS2FtdSBT
|
||||
TTE2MDQGA1UEAxMtVFVCSVRBSyBLYW11IFNNIFNTTCBLb2sgU2VydGlmaWthc2kg
|
||||
LSBTdXJ1bSAxMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAr3UwM6q7
|
||||
a9OZLBI3hNmNe5eA027n/5tQlT6QlVZC1xl8JoSNkvoBHToP4mQ4t4y86Ij5iySr
|
||||
LqP1N+RAjhgleYN1Hzv/bKjFxlb4tO2KRKOrbEz8HdDc72i9z+SqzvBV96I01INr
|
||||
N3wcwv61A+xXzry0tcXtAA9TNypN9E8Mg/uGz8v+jE69h/mniyFXnHrfA2eJLJ2X
|
||||
YacQuFWQfw4tJzh03+f92k4S400VIgLI4OD8D62K18lUUMw7D8oWgITQUVbDjlZ/
|
||||
iSIzL+aFCr2lqBs23tPcLG07xxO9WSMs5uWk99gL7eqQQESolbuT1dCANLZGeA4f
|
||||
AJNG4e7p+exPFwIDAQABo0IwQDAdBgNVHQ4EFgQUZT/HiobGPN08VFw1+DrtUgxH
|
||||
V8gwDgYDVR0PAQH/BAQDAgEGMA8GA1UdEwEB/wQFMAMBAf8wDQYJKoZIhvcNAQEL
|
||||
BQADggEBACo/4fEyjq7hmFxLXs9rHmoJ0iKpEsdeV31zVmSAhHqT5Am5EM2fKifh
|
||||
AHe+SMg1qIGf5LgsyX8OsNJLN13qudULXjS99HMpw+0mFZx+CFOKWI3QSyjfwbPf
|
||||
IPP54+M638yclNhOT8NrF7f3cuitZjO1JVOr4PhMqZ398g26rrnZqsZr+ZO7rqu4
|
||||
lzwDGrpDxpa5RXI4s6ehlj2Re37AIVNMh+3yC1SVUZPVIqUNivGTDj5UDrDYyU7c
|
||||
8jEyVupk+eq1nRZmQnLzf9OxMUP8pI4X8W0jq5Rm+K37DwhuJi1/FwcJsoz7UMCf
|
||||
lo3Ptv0AnVoUmr8CRPXBwp8iXqIPoeM=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFQTCCAymgAwIBAgICDL4wDQYJKoZIhvcNAQELBQAwUTELMAkGA1UEBhMCVFcx
|
||||
EjAQBgNVBAoTCVRBSVdBTi1DQTEQMA4GA1UECxMHUm9vdCBDQTEcMBoGA1UEAxMT
|
||||
VFdDQSBHbG9iYWwgUm9vdCBDQTAeFw0xMjA2MjcwNjI4MzNaFw0zMDEyMzExNTU5
|
||||
NTlaMFExCzAJBgNVBAYTAlRXMRIwEAYDVQQKEwlUQUlXQU4tQ0ExEDAOBgNVBAsT
|
||||
B1Jvb3QgQ0ExHDAaBgNVBAMTE1RXQ0EgR2xvYmFsIFJvb3QgQ0EwggIiMA0GCSqG
|
||||
SIb3DQEBAQUAA4ICDwAwggIKAoICAQCwBdvI64zEbooh745NnHEKH1Jw7W2CnJfF
|
||||
10xORUnLQEK1EjRsGcJ0pDFfhQKX7EMzClPSnIyOt7h52yvVavKOZsTuKwEHktSz
|
||||
0ALfUPZVr2YOy+BHYC8rMjk1Ujoog/h7FsYYuGLWRyWRzvAZEk2tY/XTP3VfKfCh
|
||||
MBwqoJimFb3u/Rk28OKRQ4/6ytYQJ0lM793B8YVwm8rqqFpD/G2Gb3PpN0Wp8DbH
|
||||
zIh1HrtsBv+baz4X7GGqcXzGHaL3SekVtTzWoWH1EfcFbx39Eb7QMAfCKbAJTibc
|
||||
46KokWofwpFFiFzlmLhxpRUZyXx1EcxwdE8tmx2RRP1WKKD+u4ZqyPpcC1jcxkt2
|
||||
yKsi2XMPpfRaAok/T54igu6idFMqPVMnaR1sjjIsZAAmY2E2TqNGtz99sy2sbZCi
|
||||
laLOz9qC5wc0GZbpuCGqKX6mOL6OKUohZnkfs8O1CWfe1tQHRvMq2uYiN2DLgbYP
|
||||
oA/pyJV/v1WRBXrPPRXAb94JlAGD1zQbzECl8LibZ9WYkTunhHiVJqRaCPgrdLQA
|
||||
BDzfuBSO6N+pjWxnkjMdwLfS7JLIvgm/LCkFbwJrnu+8vyq8W8BQj0FwcYeyTbcE
|
||||
qYSjMq+u7msXi7Kx/mzhkIyIqJdIzshNy/MGz19qCkKxHh53L46g5pIOBvwFItIm
|
||||
4TFRfTLcDwIDAQABoyMwITAOBgNVHQ8BAf8EBAMCAQYwDwYDVR0TAQH/BAUwAwEB
|
||||
/zANBgkqhkiG9w0BAQsFAAOCAgEAXzSBdu+WHdXltdkCY4QWwa6gcFGn90xHNcgL
|
||||
1yg9iXHZqjNB6hQbbCEAwGxCGX6faVsgQt+i0trEfJdLjbDorMjupWkEmQqSpqsn
|
||||
LhpNgb+E1HAerUf+/UqdM+DyucRFCCEK2mlpc3INvjT+lIutwx4116KD7+U4x6WF
|
||||
H6vPNOw/KP4M8VeGTslV9xzU2KV9Bnpv1d8Q34FOIWWxtuEXeZVFBs5fzNxGiWNo
|
||||
RI2T9GRwoD2dKAXDOXC4Ynsg/eTb6QihuJ49CcdP+yz4k3ZB3lLg4VfSnQO8d57+
|
||||
nile98FRYB/e2guyLXW3Q0iT5/Z5xoRdgFlglPx4mI88k1HtQJAH32RjJMtOcQWh
|
||||
15QaiDLxInQirqWm2BJpTGCjAu4r7NRjkgtevi92a6O2JryPA9gK8kxkRr05YuWW
|
||||
6zRjESjMlfGt7+/cgFhI6Uu46mWs6fyAtbXIRfmswZ/ZuepiiI7E8UuDEq3mi4TW
|
||||
nsLrgxifarsbJGAzcMzs9zLzXNl5fe+epP7JI8Mk7hWSsT2RTyaGvWZzJBPqpK5j
|
||||
wa19hAM8EHiGG3njxPPyBJUgriOCxLM6AGK/5jYk4Ve6xx6QddVfP5VhK8E7zeWz
|
||||
aGHQRiapIVJpLesux+t3zqY6tQMzT3bR51xUAV3LePTJDL/PEo4XLSNolOer/qmy
|
||||
KwbQBM0=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDezCCAmOgAwIBAgIBATANBgkqhkiG9w0BAQUFADBfMQswCQYDVQQGEwJUVzES
|
||||
MBAGA1UECgwJVEFJV0FOLUNBMRAwDgYDVQQLDAdSb290IENBMSowKAYDVQQDDCFU
|
||||
V0NBIFJvb3QgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMDgwODI4MDcyNDMz
|
||||
WhcNMzAxMjMxMTU1OTU5WjBfMQswCQYDVQQGEwJUVzESMBAGA1UECgwJVEFJV0FO
|
||||
LUNBMRAwDgYDVQQLDAdSb290IENBMSowKAYDVQQDDCFUV0NBIFJvb3QgQ2VydGlm
|
||||
aWNhdGlvbiBBdXRob3JpdHkwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIB
|
||||
AQCwfnK4pAOU5qfeCTiRShFAh6d8WWQUe7UREN3+v9XAu1bihSX0NXIP+FPQQeFE
|
||||
AcK0HMMxQhZHhTMidrIKbw/lJVBPhYa+v5guEGcevhEFhgWQxFnQfHgQsIBct+HH
|
||||
K3XLfJ+utdGdIzdjp9xCoi2SBBtQwXu4PhvJVgSLL1KbralW6cH/ralYhzC2gfeX
|
||||
RfwZVzsrb+RH9JlF/h3x+JejiB03HFyP4HYlmlD4oFT/RJB2I9IyxsOrBr/8+7/z
|
||||
rX2SYgJbKdM1o5OaQ2RgXbL6Mv87BK9NQGr5x+PvI/1ry+UPizgN7gr8/g+YnzAx
|
||||
3WxSZfmLgb4i4RxYA7qRG4kHAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNV
|
||||
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBRqOFsmjd6LWvJPelSDGRjjCDWmujANBgkq
|
||||
hkiG9w0BAQUFAAOCAQEAPNV3PdrfibqHDAhUaiBQkr6wQT25JmSDCi/oQMCXKCeC
|
||||
MErJk/9q56YAf4lCmtYR5VPOL8zy2gXE/uJQxDqGfczafhAJO5I1KlOy/usrBdls
|
||||
XebQ79NqZp4VKIV66IIArB6nCWlWQtNoURi+VJq/REG6Sb4gumlc7rh3zc5sH62D
|
||||
lhh9DrUUOYTxKOkto557HnpyWoOzeW/vtPzQCqVYT0bf+215WfKEIlKuD8z7fDvn
|
||||
aspHYcN6+NOSBB+4IIThNlQWx0DeO4pz3N/GCUzf7Nr/1FNCocnyYh0igzyXxfkZ
|
||||
YiesZSLX0zzG5Y6yU8xJzrww/nsOM5D77dIUkR8Hrw==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFcjCCA1qgAwIBAgIQH51ZWtcvwgZEpYAIaeNe9jANBgkqhkiG9w0BAQUFADA/
|
||||
MQswCQYDVQQGEwJUVzEwMC4GA1UECgwnR292ZXJubWVudCBSb290IENlcnRpZmlj
|
||||
YXRpb24gQXV0aG9yaXR5MB4XDTAyMTIwNTEzMjMzM1oXDTMyMTIwNTEzMjMzM1ow
|
||||
PzELMAkGA1UEBhMCVFcxMDAuBgNVBAoMJ0dvdmVybm1lbnQgUm9vdCBDZXJ0aWZp
|
||||
Y2F0aW9uIEF1dGhvcml0eTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIB
|
||||
AJoluOzMonWoe/fOW1mKydGGEghU7Jzy50b2iPN86aXfTEc2pBsBHH8eV4qNw8XR
|
||||
IePaJD9IK/ufLqGU5ywck9G/GwGHU5nOp/UKIXZ3/6m3xnOUT0b3EEk3+qhZSV1q
|
||||
gQdW8or5BtD3cCJNtLdBuTK4sfCxw5w/cP1T3YGq2GN49thTbqGsaoQkclSGxtKy
|
||||
yhwOeYHWtXBiCAEuTk8O1RGvqa/lmr/czIdtJuTJV6L7lvnM4T9TjGxMfptTCAts
|
||||
F/tnyMKtsc2AtJfcdgEWFelq16TheEfOhtX7MfP6Mb40qij7cEwdScevLJ1tZqa2
|
||||
jWR+tSBqnTuBto9AAGdLiYa4zGX+FVPpBMHWXx1E1wovJ5pGfaENda1UhhXcSTvx
|
||||
ls4Pm6Dso3pdvtUqdULle96ltqqvKKyskKw4t9VoNSZ63Pc78/1Fm9G7Q3hub/FC
|
||||
VGqY8A2tl+lSXunVanLeavcbYBT0peS2cWeqH+riTcFCQP5nRhc4L0c/cZyu5SHK
|
||||
YS1tB6iEfC3uUSXxY5Ce/eFXiGvviiNtsea9P63RPZYLhY3Naye7twWb7LuRqQoH
|
||||
EgKXTiCQ8P8NHuJBO9NAOueNXdpm5AKwB1KYXA6OM5zCppX7VRluTI6uSw+9wThN
|
||||
Xo+EHWbNxWCWtFJaBYmOlXqYwZE8lSOyDvR5tMl8wUohAgMBAAGjajBoMB0GA1Ud
|
||||
DgQWBBTMzO/MKWCkO7GStjz6MmKPrCUVOzAMBgNVHRMEBTADAQH/MDkGBGcqBwAE
|
||||
MTAvMC0CAQAwCQYFKw4DAhoFADAHBgVnKgMAAAQUA5vwIhP/lSg209yewDL7MTqK
|
||||
UWUwDQYJKoZIhvcNAQEFBQADggIBAECASvomyc5eMN1PhnR2WPWus4MzeKR6dBcZ
|
||||
TulStbngCnRiqmjKeKBMmo4sIy7VahIkv9Ro04rQ2JyftB8M3jh+Vzj8jeJPXgyf
|
||||
qzvS/3WXy6TjZwj/5cAWtUgBfen5Cv8b5Wppv3ghqMKnI6mGq3ZW6A4M9hPdKmaK
|
||||
ZEk9GhiHkASfQlK3T8v+R0F2Ne//AHY2RTKbxkaFXeIksB7jSJaYV0eUVXoPQbFE
|
||||
JPPB/hprv4j9wabak2BegUqZIJxIZhm1AHlUD7gsL0u8qV1bYH+Mh6XgUmMqvtg7
|
||||
hUAV/h62ZT/FS9p+tXo1KaMuephgIqP0fSdOLeq0dDzpD6QzDxARvBMB1uUO07+1
|
||||
EqLhRSPAzAhuYbeJq4PjJB7mXQfnHyA+z2fI56wwbSdLaG5LKlwCCDTb+HbkZ6Mm
|
||||
nD+iMsJKxYEYMRBWqoTvLQr/uB930r+lWKBi5NdLkXWNiYCYfm3LU05er/ayl4WX
|
||||
udpVBrkk7tfGOB5jGxI7leFYrPLfhNVfmS8NVVvmONsuP3LpSIXLuykTjx44Vbnz
|
||||
ssQwmSNOXfJIoRIM3BKQCZBUkQM8R+XVyWXgt0t97EfTsws+rZ7QdAAO671RrcDe
|
||||
LMDDav7v3Aun+kbfYNucpllQdSNpc5Oy+fwC00fmcc4QAu4njIT/rEUNE1yDMuAl
|
||||
pYYsfPQS
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFODCCAyCgAwIBAgIRAJW+FqD3LkbxezmCcvqLzZYwDQYJKoZIhvcNAQEFBQAw
|
||||
NzEUMBIGA1UECgwLVGVsaWFTb25lcmExHzAdBgNVBAMMFlRlbGlhU29uZXJhIFJv
|
||||
b3QgQ0EgdjEwHhcNMDcxMDE4MTIwMDUwWhcNMzIxMDE4MTIwMDUwWjA3MRQwEgYD
|
||||
VQQKDAtUZWxpYVNvbmVyYTEfMB0GA1UEAwwWVGVsaWFTb25lcmEgUm9vdCBDQSB2
|
||||
MTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAMK+6yfwIaPzaSZVfp3F
|
||||
VRaRXP3vIb9TgHot0pGMYzHw7CTww6XScnwQbfQ3t+XmfHnqjLWCi65ItqwA3GV1
|
||||
7CpNX8GH9SBlK4GoRz6JI5UwFpB/6FcHSOcZrr9FZ7E3GwYq/t75rH2D+1665I+X
|
||||
Z75Ljo1kB1c4VWk0Nj0TSO9P4tNmHqTPGrdeNjPUtAa9GAH9d4RQAEX1jF3oI7x+
|
||||
/jXh7VB7qTCNGdMJjmhnXb88lxhTuylixcpecsHHltTbLaC0H2kD7OriUPEMPPCs
|
||||
81Mt8Bz17Ww5OXOAFshSsCPN4D7c3TxHoLs1iuKYaIu+5b9y7tL6pe0S7fyYGKkm
|
||||
dtwoSxAgHNN/Fnct7W+A90m7UwW7XWjH1Mh1Fj+JWov3F0fUTPHSiXk+TT2YqGHe
|
||||
Oh7S+F4D4MHJHIzTjU3TlTazN19jY5szFPAtJmtTfImMMsJu7D0hADnJoWjiUIMu
|
||||
sDor8zagrC/kb2HCUQk5PotTubtn2txTuXZZNp1D5SDgPTJghSJRt8czu90VL6R4
|
||||
pgd7gUY2BIbdeTXHlSw7sKMXNeVzH7RcWe/a6hBle3rQf5+ztCo3O3CLm1u5K7fs
|
||||
slESl1MpWtTwEhDcTwK7EpIvYtQ/aUN8Ddb8WHUBiJ1YFkveupD/RwGJBmr2X7KQ
|
||||
arMCpgKIv7NHfirZ1fpoeDVNAgMBAAGjPzA9MA8GA1UdEwEB/wQFMAMBAf8wCwYD
|
||||
VR0PBAQDAgEGMB0GA1UdDgQWBBTwj1k4ALP1j5qWDNXr+nuqF+gTEjANBgkqhkiG
|
||||
9w0BAQUFAAOCAgEAvuRcYk4k9AwI//DTDGjkk0kiP0Qnb7tt3oNmzqjMDfz1mgbl
|
||||
dxSR651Be5kqhOX//CHBXfDkH1e3damhXwIm/9fH907eT/j3HEbAek9ALCI18Bmx
|
||||
0GtnLLCo4MBANzX2hFxc469CeP6nyQ1Q6g2EdvZR74NTxnr/DlZJLo961gzmJ1Tj
|
||||
TQpgcmLNkQfWpb/ImWvtxBnmq0wROMVvMeJuScg/doAmAyYp4Db29iBT4xdwNBed
|
||||
Y2gea+zDTYa4EzAvXUYNR0PVG6pZDrlcjQZIrXSHX8f8MVRBE+LHIQ6e4B4N4cB7
|
||||
Q4WQxYpYxmUKeFfyxiMPAdkgS94P+5KFdSpcc41teyWRyu5FrgZLAMzTsVlQ2jqI
|
||||
OylDRl6XK1TOU2+NSueW+r9xDkKLfP0ooNBIytrEgUy7onOTJsjrDNYmiLbAJM+7
|
||||
vVvrdX3pCI6GMyx5dwlppYn8s3CQh3aP0yK7Qs69cwsgJirQmz1wHiRszYd2qReW
|
||||
t88NkvuOGKmYSdGe/mBEciG5Ge3C9THxOUiIkCR1VBatzvT4aRRkOfujuLpwQMcn
|
||||
HL/EVlP6Y2XQ8xwOFvVrhlhNGNTkDY6lnVuR3HYkUD/GKvvZt5y11ubQ2egZixVx
|
||||
SK236thZiNSQvxaz2emsWWFUyBy6ysHK4bkgTI86k4mloMy/0/Z1pHWWbVY=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDZzCCAk+gAwIBAgIQGx+ttiD5JNM2a/fH8YygWTANBgkqhkiG9w0BAQUFADBF
|
||||
MQswCQYDVQQGEwJHQjEYMBYGA1UEChMPVHJ1c3RpcyBMaW1pdGVkMRwwGgYDVQQL
|
||||
ExNUcnVzdGlzIEZQUyBSb290IENBMB4XDTAzMTIyMzEyMTQwNloXDTI0MDEyMTEx
|
||||
MzY1NFowRTELMAkGA1UEBhMCR0IxGDAWBgNVBAoTD1RydXN0aXMgTGltaXRlZDEc
|
||||
MBoGA1UECxMTVHJ1c3RpcyBGUFMgUm9vdCBDQTCCASIwDQYJKoZIhvcNAQEBBQAD
|
||||
ggEPADCCAQoCggEBAMVQe547NdDfxIzNjpvto8A2mfRC6qc+gIMPpqdZh8mQRUN+
|
||||
AOqGeSoDvT03mYlmt+WKVoaTnGhLaASMk5MCPjDSNzoiYYkchU59j9WvezX2fihH
|
||||
iTHcDnlkH5nSW7r+f2C/revnPDgpai/lkQtV/+xvWNUtyd5MZnGPDNcE2gfmHhjj
|
||||
vSkCqPoc4Vu5g6hBSLwacY3nYuUtsuvffM/bq1rKMfFMIvMFE/eC+XN5DL7XSxzA
|
||||
0RU8k0Fk0ea+IxciAIleH2ulrG6nS4zto3Lmr2NNL4XSFDWaLk6M6jKYKIahkQlB
|
||||
OrTh4/L68MkKokHdqeMDx4gVOxzUGpTXn2RZEm0CAwEAAaNTMFEwDwYDVR0TAQH/
|
||||
BAUwAwEB/zAfBgNVHSMEGDAWgBS6+nEleYtXQSUhhgtx67JkDoshZzAdBgNVHQ4E
|
||||
FgQUuvpxJXmLV0ElIYYLceuyZA6LIWcwDQYJKoZIhvcNAQEFBQADggEBAH5Y//01
|
||||
GX2cGE+esCu8jowU/yyg2kdbw++BLa8F6nRIW/M+TgfHbcWzk88iNVy2P3UnXwmW
|
||||
zaD+vkAMXBJV+JOCyinpXj9WV4s4NvdFGkwozZ5BuO1WTISkQMi4sKUraXAEasP4
|
||||
1BIy+Q7DsdwyhEQsb8tGD+pmQQ9P8Vilpg0ND2HepZ5dfWWhPBfnqFVO76DH7cZE
|
||||
f1T1o+CP8HxVIo8ptoGj4W1OLBuAZ+ytIJ8MYmHVl/9D7S3B2l0pKoU/rGXuhg8F
|
||||
jZBf3+6f9L/uHfuY5H+QK4R4EA5sSVPvFVtlRkpdr7r7OnIdzfYliB6XzCGcKQEN
|
||||
ZetX2fNXlrtIzYE=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICjzCCAhWgAwIBAgIQXIuZxVqUxdJxVt7NiYDMJjAKBggqhkjOPQQDAzCBiDEL
|
||||
MAkGA1UEBhMCVVMxEzARBgNVBAgTCk5ldyBKZXJzZXkxFDASBgNVBAcTC0plcnNl
|
||||
eSBDaXR5MR4wHAYDVQQKExVUaGUgVVNFUlRSVVNUIE5ldHdvcmsxLjAsBgNVBAMT
|
||||
JVVTRVJUcnVzdCBFQ0MgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMTAwMjAx
|
||||
MDAwMDAwWhcNMzgwMTE4MjM1OTU5WjCBiDELMAkGA1UEBhMCVVMxEzARBgNVBAgT
|
||||
Ck5ldyBKZXJzZXkxFDASBgNVBAcTC0plcnNleSBDaXR5MR4wHAYDVQQKExVUaGUg
|
||||
VVNFUlRSVVNUIE5ldHdvcmsxLjAsBgNVBAMTJVVTRVJUcnVzdCBFQ0MgQ2VydGlm
|
||||
aWNhdGlvbiBBdXRob3JpdHkwdjAQBgcqhkjOPQIBBgUrgQQAIgNiAAQarFRaqflo
|
||||
I+d61SRvU8Za2EurxtW20eZzca7dnNYMYf3boIkDuAUU7FfO7l0/4iGzzvfUinng
|
||||
o4N+LZfQYcTxmdwlkWOrfzCjtHDix6EznPO/LlxTsV+zfTJ/ijTjeXmjQjBAMB0G
|
||||
A1UdDgQWBBQ64QmG1M8ZwpZ2dEl23OA1xmNjmjAOBgNVHQ8BAf8EBAMCAQYwDwYD
|
||||
VR0TAQH/BAUwAwEB/zAKBggqhkjOPQQDAwNoADBlAjA2Z6EWCNzklwBBHU6+4WMB
|
||||
zzuqQhFkoJ2UOQIReVx7Hfpkue4WQrO/isIJxOzksU0CMQDpKmFHjFJKS04YcPbW
|
||||
RNZu9YO6bVi9JNlWSOrvxKJGgYhqOkbRqZtNyWHa0V1Xahg=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF3jCCA8agAwIBAgIQAf1tMPyjylGoG7xkDjUDLTANBgkqhkiG9w0BAQwFADCB
|
||||
iDELMAkGA1UEBhMCVVMxEzARBgNVBAgTCk5ldyBKZXJzZXkxFDASBgNVBAcTC0pl
|
||||
cnNleSBDaXR5MR4wHAYDVQQKExVUaGUgVVNFUlRSVVNUIE5ldHdvcmsxLjAsBgNV
|
||||
BAMTJVVTRVJUcnVzdCBSU0EgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMTAw
|
||||
MjAxMDAwMDAwWhcNMzgwMTE4MjM1OTU5WjCBiDELMAkGA1UEBhMCVVMxEzARBgNV
|
||||
BAgTCk5ldyBKZXJzZXkxFDASBgNVBAcTC0plcnNleSBDaXR5MR4wHAYDVQQKExVU
|
||||
aGUgVVNFUlRSVVNUIE5ldHdvcmsxLjAsBgNVBAMTJVVTRVJUcnVzdCBSU0EgQ2Vy
|
||||
dGlmaWNhdGlvbiBBdXRob3JpdHkwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIK
|
||||
AoICAQCAEmUXNg7D2wiz0KxXDXbtzSfTTK1Qg2HiqiBNCS1kCdzOiZ/MPans9s/B
|
||||
3PHTsdZ7NygRK0faOca8Ohm0X6a9fZ2jY0K2dvKpOyuR+OJv0OwWIJAJPuLodMkY
|
||||
tJHUYmTbf6MG8YgYapAiPLz+E/CHFHv25B+O1ORRxhFnRghRy4YUVD+8M/5+bJz/
|
||||
Fp0YvVGONaanZshyZ9shZrHUm3gDwFA66Mzw3LyeTP6vBZY1H1dat//O+T23LLb2
|
||||
VN3I5xI6Ta5MirdcmrS3ID3KfyI0rn47aGYBROcBTkZTmzNg95S+UzeQc0PzMsNT
|
||||
79uq/nROacdrjGCT3sTHDN/hMq7MkztReJVni+49Vv4M0GkPGw/zJSZrM233bkf6
|
||||
c0Plfg6lZrEpfDKEY1WJxA3Bk1QwGROs0303p+tdOmw1XNtB1xLaqUkL39iAigmT
|
||||
Yo61Zs8liM2EuLE/pDkP2QKe6xJMlXzzawWpXhaDzLhn4ugTncxbgtNMs+1b/97l
|
||||
c6wjOy0AvzVVdAlJ2ElYGn+SNuZRkg7zJn0cTRe8yexDJtC/QV9AqURE9JnnV4ee
|
||||
UB9XVKg+/XRjL7FQZQnmWEIuQxpMtPAlR1n6BB6T1CZGSlCBst6+eLf8ZxXhyVeE
|
||||
Hg9j1uliutZfVS7qXMYoCAQlObgOK6nyTJccBz8NUvXt7y+CDwIDAQABo0IwQDAd
|
||||
BgNVHQ4EFgQUU3m/WqorSs9UgOHYm8Cd8rIDZsswDgYDVR0PAQH/BAQDAgEGMA8G
|
||||
A1UdEwEB/wQFMAMBAf8wDQYJKoZIhvcNAQEMBQADggIBAFzUfA3P9wF9QZllDHPF
|
||||
Up/L+M+ZBn8b2kMVn54CVVeWFPFSPCeHlCjtHzoBN6J2/FNQwISbxmtOuowhT6KO
|
||||
VWKR82kV2LyI48SqC/3vqOlLVSoGIG1VeCkZ7l8wXEskEVX/JJpuXior7gtNn3/3
|
||||
ATiUFJVDBwn7YKnuHKsSjKCaXqeYalltiz8I+8jRRa8YFWSQEg9zKC7F4iRO/Fjs
|
||||
8PRF/iKz6y+O0tlFYQXBl2+odnKPi4w2r78NBc5xjeambx9spnFixdjQg3IM8WcR
|
||||
iQycE0xyNN+81XHfqnHd4blsjDwSXWXavVcStkNr/+XeTWYRUc+ZruwXtuhxkYze
|
||||
Sf7dNXGiFSeUHM9h4ya7b6NnJSFd5t0dCy5oGzuCr+yDZ4XUmFF0sbmZgIn/f3gZ
|
||||
XHlKYC6SQK5MNyosycdiyA5d9zZbyuAlJQG03RoHnHcAP9Dc1ew91Pq7P8yF1m9/
|
||||
qS3fuQL39ZeatTXaw2ewh0qpKJ4jjv9cJ2vhsE/zB+4ALtRZh8tSQZXq9EfX7mRB
|
||||
VXyNWQKV3WKdwrnuWih0hKWbt5DHDAff9Yk2dDLWKMGwsAvgnEzDHNb842m1R0aB
|
||||
L6KCq9NjRHDEjf8tM7qtj3u1cIiuPhnPQCjY/MiQu12ZIvVS5ljFH4gxQ+6IHdfG
|
||||
jjxDah2nGN59PRbxYvnKkKj9
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDhDCCAwqgAwIBAgIQL4D+I4wOIg9IZxIokYesszAKBggqhkjOPQQDAzCByjEL
|
||||
MAkGA1UEBhMCVVMxFzAVBgNVBAoTDlZlcmlTaWduLCBJbmMuMR8wHQYDVQQLExZW
|
||||
ZXJpU2lnbiBUcnVzdCBOZXR3b3JrMTowOAYDVQQLEzEoYykgMjAwNyBWZXJpU2ln
|
||||
biwgSW5jLiAtIEZvciBhdXRob3JpemVkIHVzZSBvbmx5MUUwQwYDVQQDEzxWZXJp
|
||||
U2lnbiBDbGFzcyAzIFB1YmxpYyBQcmltYXJ5IENlcnRpZmljYXRpb24gQXV0aG9y
|
||||
aXR5IC0gRzQwHhcNMDcxMTA1MDAwMDAwWhcNMzgwMTE4MjM1OTU5WjCByjELMAkG
|
||||
A1UEBhMCVVMxFzAVBgNVBAoTDlZlcmlTaWduLCBJbmMuMR8wHQYDVQQLExZWZXJp
|
||||
U2lnbiBUcnVzdCBOZXR3b3JrMTowOAYDVQQLEzEoYykgMjAwNyBWZXJpU2lnbiwg
|
||||
SW5jLiAtIEZvciBhdXRob3JpemVkIHVzZSBvbmx5MUUwQwYDVQQDEzxWZXJpU2ln
|
||||
biBDbGFzcyAzIFB1YmxpYyBQcmltYXJ5IENlcnRpZmljYXRpb24gQXV0aG9yaXR5
|
||||
IC0gRzQwdjAQBgcqhkjOPQIBBgUrgQQAIgNiAASnVnp8Utpkmw4tXNherJI9/gHm
|
||||
GUo9FANL+mAnINmDiWn6VMaaGF5VKmTeBvaNSjutEDxlPZCIBIngMGGzrl0Bp3ve
|
||||
fLK+ymVhAIau2o970ImtTR1ZmkGxvEeA3J5iw/mjgbIwga8wDwYDVR0TAQH/BAUw
|
||||
AwEB/zAOBgNVHQ8BAf8EBAMCAQYwbQYIKwYBBQUHAQwEYTBfoV2gWzBZMFcwVRYJ
|
||||
aW1hZ2UvZ2lmMCEwHzAHBgUrDgMCGgQUj+XTGoasjY5rw8+AatRIGCx7GS4wJRYj
|
||||
aHR0cDovL2xvZ28udmVyaXNpZ24uY29tL3ZzbG9nby5naWYwHQYDVR0OBBYEFLMW
|
||||
kf3upm7ktS5Jj4d4gYDs5bG1MAoGCCqGSM49BAMDA2gAMGUCMGYhDBgmYFo4e1ZC
|
||||
4Kf8NoRRkSAsdk1DPcQdhCPQrNZ8NQbOzWm9kA3bbEhCHQ6qQgIxAJw9SDkjOVga
|
||||
FRJZap7v1VmyHVIsmXHNxynfGyphe3HR3vPA5Q06Sqotp9iGKt0uEA==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIE0zCCA7ugAwIBAgIQGNrRniZ96LtKIVjNzGs7SjANBgkqhkiG9w0BAQUFADCB
|
||||
yjELMAkGA1UEBhMCVVMxFzAVBgNVBAoTDlZlcmlTaWduLCBJbmMuMR8wHQYDVQQL
|
||||
ExZWZXJpU2lnbiBUcnVzdCBOZXR3b3JrMTowOAYDVQQLEzEoYykgMjAwNiBWZXJp
|
||||
U2lnbiwgSW5jLiAtIEZvciBhdXRob3JpemVkIHVzZSBvbmx5MUUwQwYDVQQDEzxW
|
||||
ZXJpU2lnbiBDbGFzcyAzIFB1YmxpYyBQcmltYXJ5IENlcnRpZmljYXRpb24gQXV0
|
||||
aG9yaXR5IC0gRzUwHhcNMDYxMTA4MDAwMDAwWhcNMzYwNzE2MjM1OTU5WjCByjEL
|
||||
MAkGA1UEBhMCVVMxFzAVBgNVBAoTDlZlcmlTaWduLCBJbmMuMR8wHQYDVQQLExZW
|
||||
ZXJpU2lnbiBUcnVzdCBOZXR3b3JrMTowOAYDVQQLEzEoYykgMjAwNiBWZXJpU2ln
|
||||
biwgSW5jLiAtIEZvciBhdXRob3JpemVkIHVzZSBvbmx5MUUwQwYDVQQDEzxWZXJp
|
||||
U2lnbiBDbGFzcyAzIFB1YmxpYyBQcmltYXJ5IENlcnRpZmljYXRpb24gQXV0aG9y
|
||||
aXR5IC0gRzUwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCvJAgIKXo1
|
||||
nmAMqudLO07cfLw8RRy7K+D+KQL5VwijZIUVJ/XxrcgxiV0i6CqqpkKzj/i5Vbex
|
||||
t0uz/o9+B1fs70PbZmIVYc9gDaTY3vjgw2IIPVQT60nKWVSFJuUrjxuf6/WhkcIz
|
||||
SdhDY2pSS9KP6HBRTdGJaXvHcPaz3BJ023tdS1bTlr8Vd6Gw9KIl8q8ckmcY5fQG
|
||||
BO+QueQA5N06tRn/Arr0PO7gi+s3i+z016zy9vA9r911kTMZHRxAy3QkGSGT2RT+
|
||||
rCpSx4/VBEnkjWNHiDxpg8v+R70rfk/Fla4OndTRQ8Bnc+MUCH7lP59zuDMKz10/
|
||||
NIeWiu5T6CUVAgMBAAGjgbIwga8wDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8E
|
||||
BAMCAQYwbQYIKwYBBQUHAQwEYTBfoV2gWzBZMFcwVRYJaW1hZ2UvZ2lmMCEwHzAH
|
||||
BgUrDgMCGgQUj+XTGoasjY5rw8+AatRIGCx7GS4wJRYjaHR0cDovL2xvZ28udmVy
|
||||
aXNpZ24uY29tL3ZzbG9nby5naWYwHQYDVR0OBBYEFH/TZafC3ey78DAJ80M5+gKv
|
||||
MzEzMA0GCSqGSIb3DQEBBQUAA4IBAQCTJEowX2LP2BqYLz3q3JktvXf2pXkiOOzE
|
||||
p6B4Eq1iDkVwZMXnl2YtmAl+X6/WzChl8gGqCBpH3vn5fJJaCGkgDdk+bW48DW7Y
|
||||
5gaRQBi5+MHt39tBquCWIMnNZBU4gcmU7qKEKQsTb47bDN0lAtukixlE0kF6BWlK
|
||||
WE9gyn6CagsCqiUXObXbf+eEZSqVir2G3l6BFoMtEMze/aiCKm0oHw0LxOXnGiYZ
|
||||
4fQRbxC1lfznQgUy286dUV4otp6F01vvpX1FQHKOtw5rDgb7MzVIcbidJ4vEZV8N
|
||||
hnacRHr2lVz2XTIIM6RUthg/aFzyQkqFOFSDX9HoLPKsEdao7WNq
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEuTCCA6GgAwIBAgIQQBrEZCGzEyEDDrvkEhrFHTANBgkqhkiG9w0BAQsFADCB
|
||||
vTELMAkGA1UEBhMCVVMxFzAVBgNVBAoTDlZlcmlTaWduLCBJbmMuMR8wHQYDVQQL
|
||||
ExZWZXJpU2lnbiBUcnVzdCBOZXR3b3JrMTowOAYDVQQLEzEoYykgMjAwOCBWZXJp
|
||||
U2lnbiwgSW5jLiAtIEZvciBhdXRob3JpemVkIHVzZSBvbmx5MTgwNgYDVQQDEy9W
|
||||
ZXJpU2lnbiBVbml2ZXJzYWwgUm9vdCBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTAe
|
||||
Fw0wODA0MDIwMDAwMDBaFw0zNzEyMDEyMzU5NTlaMIG9MQswCQYDVQQGEwJVUzEX
|
||||
MBUGA1UEChMOVmVyaVNpZ24sIEluYy4xHzAdBgNVBAsTFlZlcmlTaWduIFRydXN0
|
||||
IE5ldHdvcmsxOjA4BgNVBAsTMShjKSAyMDA4IFZlcmlTaWduLCBJbmMuIC0gRm9y
|
||||
IGF1dGhvcml6ZWQgdXNlIG9ubHkxODA2BgNVBAMTL1ZlcmlTaWduIFVuaXZlcnNh
|
||||
bCBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5MIIBIjANBgkqhkiG9w0BAQEF
|
||||
AAOCAQ8AMIIBCgKCAQEAx2E3XrEBNNti1xWb/1hajCMj1mCOkdeQmIN65lgZOIzF
|
||||
9uVkhbSicfvtvbnazU0AtMgtc6XHaXGVHzk8skQHnOgO+k1KxCHfKWGPMiJhgsWH
|
||||
H26MfF8WIFFE0XBPV+rjHOPMee5Y2A7Cs0WTwCznmhcrewA3ekEzeOEz4vMQGn+H
|
||||
LL729fdC4uW/h2KJXwBL38Xd5HVEMkE6HnFuacsLdUYI0crSK5XQz/u5QGtkjFdN
|
||||
/BMReYTtXlT2NJ8IAfMQJQYXStrxHXpma5hgZqTZ79IugvHw7wnqRMkVauIDbjPT
|
||||
rJ9VAMf2CGqUuV/c4DPxhGD5WycRtPwW8rtWaoAljQIDAQABo4GyMIGvMA8GA1Ud
|
||||
EwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgEGMG0GCCsGAQUFBwEMBGEwX6FdoFsw
|
||||
WTBXMFUWCWltYWdlL2dpZjAhMB8wBwYFKw4DAhoEFI/l0xqGrI2Oa8PPgGrUSBgs
|
||||
exkuMCUWI2h0dHA6Ly9sb2dvLnZlcmlzaWduLmNvbS92c2xvZ28uZ2lmMB0GA1Ud
|
||||
DgQWBBS2d/ppSEefUxLVwuoHMnYH0ZcHGTANBgkqhkiG9w0BAQsFAAOCAQEASvj4
|
||||
sAPmLGd75JR3Y8xuTPl9Dg3cyLk1uXBPY/ok+myDjEedO2Pzmvl2MpWRsXe8rJq+
|
||||
seQxIcaBlVZaDrHC1LGmWazxY8u4TB1ZkErvkBYoH1quEPuBUDgMbMzxPcP1Y+Oz
|
||||
4yHJJDnp/RVmRvQbEdBNc6N9Rvk97ahfYtTxP/jgdFcrGJ2BtMQo2pSXpXDrrB2+
|
||||
BxHw1dvd5Yzw1TKwg+ZX4o+/vqGqvz0dtdQ46tewXDpPaj+PwGZsY6rp2aQW9IHR
|
||||
lRQOfc2VNNnSj3BzgXucfr2YYdhFh5iQxeuGMMY1v/D/w1WIg0vvBZIGcfK4mJO3
|
||||
7M2CYfE45k+XmCpajQ==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEGjCCAwICEQCbfgZJoz5iudXukEhxKe9XMA0GCSqGSIb3DQEBBQUAMIHKMQsw
|
||||
CQYDVQQGEwJVUzEXMBUGA1UEChMOVmVyaVNpZ24sIEluYy4xHzAdBgNVBAsTFlZl
|
||||
cmlTaWduIFRydXN0IE5ldHdvcmsxOjA4BgNVBAsTMShjKSAxOTk5IFZlcmlTaWdu
|
||||
LCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxRTBDBgNVBAMTPFZlcmlT
|
||||
aWduIENsYXNzIDMgUHVibGljIFByaW1hcnkgQ2VydGlmaWNhdGlvbiBBdXRob3Jp
|
||||
dHkgLSBHMzAeFw05OTEwMDEwMDAwMDBaFw0zNjA3MTYyMzU5NTlaMIHKMQswCQYD
|
||||
VQQGEwJVUzEXMBUGA1UEChMOVmVyaVNpZ24sIEluYy4xHzAdBgNVBAsTFlZlcmlT
|
||||
aWduIFRydXN0IE5ldHdvcmsxOjA4BgNVBAsTMShjKSAxOTk5IFZlcmlTaWduLCBJ
|
||||
bmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxRTBDBgNVBAMTPFZlcmlTaWdu
|
||||
IENsYXNzIDMgUHVibGljIFByaW1hcnkgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkg
|
||||
LSBHMzCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAMu6nFL8eB8aHm8b
|
||||
N3O9+MlrlBIwT/A2R/XQkQr1F8ilYcEWQE37imGQ5XYgwREGfassbqb1EUGO+i2t
|
||||
KmFZpGcmTNDovFJbcCAEWNF6yaRpvIMXZK0Fi7zQWM6NjPXr8EJJC52XJ2cybuGu
|
||||
kxUccLwgTS8Y3pKI6GyFVxEa6X7jJhFUokWWVYPKMIno3Nij7SqAP395ZVc+FSBm
|
||||
CC+Vk7+qRy+oRpfwEuL+wgorUeZ25rdGt+INpsyow0xZVYnm6FNcHOqd8GIWC6fJ
|
||||
Xwzw3sJ2zq/3avL6QaaiMxTJ5Xpj055iN9WFZZ4O5lMkdBteHRJTW8cs54NJOxWu
|
||||
imi5V5cCAwEAATANBgkqhkiG9w0BAQUFAAOCAQEAERSWwauSCPc/L8my/uRan2Te
|
||||
2yFPhpk0djZX3dAVL8WtfxUfN2JzPtTnX84XA9s1+ivbrmAJXx5fj267Cz3qWhMe
|
||||
DGBvtcC1IyIuBwvLqXTLR7sdwdela8wv0kL9Sd2nic9TutoAWii/gt/4uhMdUIaC
|
||||
/Y4wjylGsB49Ndo4YhYYSq3mtlFs3q9i6wHQHiT+eo8SGhJouPtmmRQURVyu565p
|
||||
F4ErWjfJXir0xuKhXFSbplQAz/DxwceYMBo7Nhbbo27q/a2ywtrvAkcTisDxszGt
|
||||
TxzhT5yvDwyd93gN2PQ1VoDat20Xj50egWTh/sVFuq1ruQp6Tk9LhO5L8X3dEQ==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEMDCCAxigAwIBAgIQUJRs7Bjq1ZxN1ZfvdY+grTANBgkqhkiG9w0BAQUFADCB
|
||||
gjELMAkGA1UEBhMCVVMxHjAcBgNVBAsTFXd3dy54cmFtcHNlY3VyaXR5LmNvbTEk
|
||||
MCIGA1UEChMbWFJhbXAgU2VjdXJpdHkgU2VydmljZXMgSW5jMS0wKwYDVQQDEyRY
|
||||
UmFtcCBHbG9iYWwgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkwHhcNMDQxMTAxMTcx
|
||||
NDA0WhcNMzUwMTAxMDUzNzE5WjCBgjELMAkGA1UEBhMCVVMxHjAcBgNVBAsTFXd3
|
||||
dy54cmFtcHNlY3VyaXR5LmNvbTEkMCIGA1UEChMbWFJhbXAgU2VjdXJpdHkgU2Vy
|
||||
dmljZXMgSW5jMS0wKwYDVQQDEyRYUmFtcCBHbG9iYWwgQ2VydGlmaWNhdGlvbiBB
|
||||
dXRob3JpdHkwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCYJB69FbS6
|
||||
38eMpSe2OAtp87ZOqCwuIR1cRN8hXX4jdP5efrRKt6atH67gBhbim1vZZ3RrXYCP
|
||||
KZ2GG9mcDZhtdhAoWORlsH9KmHmf4MMxfoArtYzAQDsRhtDLooY2YKTVMIJt2W7Q
|
||||
DxIEM5dfT2Fa8OT5kavnHTu86M/0ay00fOJIYRyO82FEzG+gSqmUsE3a56k0enI4
|
||||
qEHMPJQRfevIpoy3hsvKMzvZPTeL+3o+hiznc9cKV6xkmxnr9A8ECIqsAxcZZPRa
|
||||
JSKNNCyy9mgdEm3Tih4U2sSPpuIjhdV6Db1q4Ons7Be7QhtnqiXtRYMh/MHJfNVi
|
||||
PvryxS3T/dRlAgMBAAGjgZ8wgZwwEwYJKwYBBAGCNxQCBAYeBABDAEEwCwYDVR0P
|
||||
BAQDAgGGMA8GA1UdEwEB/wQFMAMBAf8wHQYDVR0OBBYEFMZPoj0GY4QJnM5i5ASs
|
||||
jVy16bYbMDYGA1UdHwQvMC0wK6ApoCeGJWh0dHA6Ly9jcmwueHJhbXBzZWN1cml0
|
||||
eS5jb20vWEdDQS5jcmwwEAYJKwYBBAGCNxUBBAMCAQEwDQYJKoZIhvcNAQEFBQAD
|
||||
ggEBAJEVOQMBG2f7Shz5CmBbodpNl2L5JFMn14JkTpAuw0kbK5rc/Kh4ZzXxHfAR
|
||||
vbdI4xD2Dd8/0sm2qlWkSLoC295ZLhVbO50WfUfXN+pfTXYSNrsf16GBBEYgoyxt
|
||||
qZ4Bfj8pzgCT3/3JknOJiWSe5yvkHJEs0rnOfc5vMZnT5r7SHpDwCRR5XCOrTdLa
|
||||
IR9NmXmd4c8nnxCbHIgNsIpkQTG4DmyQJKSbXHGPurt+HBvbaoAPIbzp26a3QPSy
|
||||
i6mx5O+aGtA9aZnuqCij4Tyz8LIRnM98QObd50N9otg6tamN8jSZxNQQ4Qb9CYQQ
|
||||
O+7ETPTsJ3xCwnR8gooJybQDJbw=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIDODCCAiCgAwIBAgIGIAYFFnACMA0GCSqGSIb3DQEBBQUAMDsxCzAJBgNVBAYT
|
||||
AlJPMREwDwYDVQQKEwhjZXJ0U0lHTjEZMBcGA1UECxMQY2VydFNJR04gUk9PVCBD
|
||||
QTAeFw0wNjA3MDQxNzIwMDRaFw0zMTA3MDQxNzIwMDRaMDsxCzAJBgNVBAYTAlJP
|
||||
MREwDwYDVQQKEwhjZXJ0U0lHTjEZMBcGA1UECxMQY2VydFNJR04gUk9PVCBDQTCC
|
||||
ASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBALczuX7IJUqOtdu0KBuqV5Do
|
||||
0SLTZLrTk+jUrIZhQGpgV2hUhE28alQCBf/fm5oqrl0Hj0rDKH/v+yv6efHHrfAQ
|
||||
UySQi2bJqIirr1qjAOm+ukbuW3N7LBeCgV5iLKECZbO9xSsAfsT8AzNXDe3i+s5d
|
||||
RdY4zTW2ssHQnIFKquSyAVwdj1+ZxLGt24gh65AIgoDzMKND5pCCrlUoSe1b16kQ
|
||||
OA7+j0xbm0bqQfWwCHTD0IgztnzXdN/chNFDDnU5oSVAKOp4yw4sLjmdjItuFhwv
|
||||
JoIQ4uNllAoEwF73XVv4EOLQunpL+943AAAaWyjj0pxzPjKHmKHJUS/X3qwzs08C
|
||||
AwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAcYwHQYDVR0O
|
||||
BBYEFOCMm9slSbPxfIbWskKHC9BroNnkMA0GCSqGSIb3DQEBBQUAA4IBAQA+0hyJ
|
||||
LjX8+HXd5n9liPRyTMks1zJO890ZeUe9jjtbkw9QSSQTaxQGcu8J06Gh40CEyecY
|
||||
MnQ8SG4Pn0vU9x7Tk4ZkVJdjclDVVc/6IJMCopvDI5NOFlV2oHB5bc0hH88vLbwZ
|
||||
44gx+FkagQnIl6Z0x2DEW8xXjrJ1/RsCCdtZb3KTafcxQdaIOL+Hsr0Wefmq5L6I
|
||||
Jd1hJyMctTEHBDa0GpC9oHRxUIltvBTjD4au8as+x6AJzKNI0eDbZOeStc+vckNw
|
||||
i/nDhDwTqn6Sm1dTk/pwwpEOMfmbZ13pljheX7NzTogVZ96edhBiIL5VaZVDADlN
|
||||
9u6wWk5JRFRYX0KD
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFsDCCA5igAwIBAgIQFci9ZUdcr7iXAF7kBtK8nTANBgkqhkiG9w0BAQUFADBe
|
||||
MQswCQYDVQQGEwJUVzEjMCEGA1UECgwaQ2h1bmdod2EgVGVsZWNvbSBDby4sIEx0
|
||||
ZC4xKjAoBgNVBAsMIWVQS0kgUm9vdCBDZXJ0aWZpY2F0aW9uIEF1dGhvcml0eTAe
|
||||
Fw0wNDEyMjAwMjMxMjdaFw0zNDEyMjAwMjMxMjdaMF4xCzAJBgNVBAYTAlRXMSMw
|
||||
IQYDVQQKDBpDaHVuZ2h3YSBUZWxlY29tIENvLiwgTHRkLjEqMCgGA1UECwwhZVBL
|
||||
SSBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5MIICIjANBgkqhkiG9w0BAQEF
|
||||
AAOCAg8AMIICCgKCAgEA4SUP7o3biDN1Z82tH306Tm2d0y8U82N0ywEhajfqhFAH
|
||||
SyZbCUNsIZ5qyNUD9WBpj8zwIuQf5/dqIjG3LBXy4P4AakP/h2XGtRrBp0xtInAh
|
||||
ijHyl3SJCRImHJ7K2RKilTza6We/CKBk49ZCt0Xvl/T29de1ShUCWH2YWEtgvM3X
|
||||
DZoTM1PRYfl61dd4s5oz9wCGzh1NlDivqOx4UXCKXBCDUSH3ET00hl7lSM2XgYI1
|
||||
TBnsZfZrxQWh7kcT1rMhJ5QQCtkkO7q+RBNGMD+XPNjX12ruOzjjK9SXDrkb5wdJ
|
||||
fzcq+Xd4z1TtW0ado4AOkUPB1ltfFLqfpo0kR0BZv3I4sjZsN/+Z0V0OWQqraffA
|
||||
sgRFelQArr5T9rXn4fg8ozHSqf4hUmTFpmfwdQcGlBSBVcYn5AGPF8Fqcde+S/uU
|
||||
WH1+ETOxQvdibBjWzwloPn9s9h6PYq2lY9sJpx8iQkEeb5mKPtf5P0B6ebClAZLS
|
||||
nT0IFaUQAS2zMnaolQ2zepr7BxB4EW/hj8e6DyUadCrlHJhBmd8hh+iVBmoKs2pH
|
||||
dmX2Os+PYhcZewoozRrSgx4hxyy/vv9haLdnG7t4TY3OZ+XkwY63I2binZB1NJip
|
||||
NiuKmpS5nezMirH4JYlcWrYvjB9teSSnUmjDhDXiZo1jDiVN1Rmy5nk3pyKdVDEC
|
||||
AwEAAaNqMGgwHQYDVR0OBBYEFB4M97Zn8uGSJglFwFU5Lnc/QkqiMAwGA1UdEwQF
|
||||
MAMBAf8wOQYEZyoHAAQxMC8wLQIBADAJBgUrDgMCGgUAMAcGBWcqAwAABBRFsMLH
|
||||
ClZ87lt4DJX5GFPBphzYEDANBgkqhkiG9w0BAQUFAAOCAgEACbODU1kBPpVJufGB
|
||||
uvl2ICO1J2B01GqZNF5sAFPZn/KmsSQHRGoqxqWOeBLoR9lYGxMqXnmbnwoqZ6Yl
|
||||
PwZpVnPDimZI+ymBV3QGypzqKOg4ZyYr8dW1P2WT+DZdjo2NQCCHGervJ8A9tDkP
|
||||
JXtoUHRVnAxZfVo9QZQlUgjgRywVMRnVvwdVxrsStZf0X4OFunHB2WyBEXYKCrC/
|
||||
gpf36j36+uwtqSiUO1bd0lEursC9CBWMd1I0ltabrNMdjmEPNXubrjlpC2JgQCA2
|
||||
j6/7Nu4tCEoduL+bXPjqpRugc6bY+G7gMwRfaKonh+3ZwZCc7b3jajWvY9+rGNm6
|
||||
5ulK6lCKD2GTHuItGeIwlDWSXQ62B68ZgI9HkFFLLk3dheLSClIKF5r8GrBQAuUB
|
||||
o2M3IUxExJtRmREOc5wGj1QupyheRDmHVi03vYVElOEMSyycw5KFNGHLD7ibSkNS
|
||||
/jQ6fbjpKdx2qcgw+BRxgMYeNkh0IkFch4LoGHGLQYlE535YW6i4jRPpp2zDR+2z
|
||||
Gp1iro2C6pSe3VkQw63d4k3jMdXH7OjysP6SHhYKGvzZ8/gntsm+HbRsZJB/9OTE
|
||||
W9c3rkIO3aQab3yIVMUWbuF6aC74Or8NpDyJO3inTmODBCEIZ43ygknQW/2xzQ+D
|
||||
hNQ+IIX3Sj0rnP0qCglN6oH4EZw=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEIDCCAwigAwIBAgIQNE7VVyDV7exJ9C/ON9srbTANBgkqhkiG9w0BAQUFADCB
|
||||
qTELMAkGA1UEBhMCVVMxFTATBgNVBAoTDHRoYXd0ZSwgSW5jLjEoMCYGA1UECxMf
|
||||
Q2VydGlmaWNhdGlvbiBTZXJ2aWNlcyBEaXZpc2lvbjE4MDYGA1UECxMvKGMpIDIw
|
||||
MDYgdGhhd3RlLCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxHzAdBgNV
|
||||
BAMTFnRoYXd0ZSBQcmltYXJ5IFJvb3QgQ0EwHhcNMDYxMTE3MDAwMDAwWhcNMzYw
|
||||
NzE2MjM1OTU5WjCBqTELMAkGA1UEBhMCVVMxFTATBgNVBAoTDHRoYXd0ZSwgSW5j
|
||||
LjEoMCYGA1UECxMfQ2VydGlmaWNhdGlvbiBTZXJ2aWNlcyBEaXZpc2lvbjE4MDYG
|
||||
A1UECxMvKGMpIDIwMDYgdGhhd3RlLCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNl
|
||||
IG9ubHkxHzAdBgNVBAMTFnRoYXd0ZSBQcmltYXJ5IFJvb3QgQ0EwggEiMA0GCSqG
|
||||
SIb3DQEBAQUAA4IBDwAwggEKAoIBAQCsoPD7gFnUnMekz52hWXMJEEUMDSxuaPFs
|
||||
W0hoSVk3/AszGcJ3f8wQLZU0HObrTQmnHNK4yZc2AreJ1CRfBsDMRJSUjQJib+ta
|
||||
3RGNKJpchJAQeg29dGYvajig4tVUROsdB58Hum/u6f1OCyn1PoSgAfGcq/gcfomk
|
||||
6KHYcWUNo1F77rzSImANuVud37r8UVsLr5iy6S7pBOhih94ryNdOwUxkHt3Ph1i6
|
||||
Sk/KaAcdHJ1KxtUvkcx8cXIcxcBn6zL9yZJclNqFwJu/U30rCfSMnZEfl2pSy94J
|
||||
NqR32HuHUETVPm4pafs5SSYeCaWAe0At6+gnhcn+Yf1+5nyXHdWdAgMBAAGjQjBA
|
||||
MA8GA1UdEwEB/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgEGMB0GA1UdDgQWBBR7W0XP
|
||||
r87Lev0xkhpqtvNG61dIUDANBgkqhkiG9w0BAQUFAAOCAQEAeRHAS7ORtvzw6WfU
|
||||
DW5FvlXok9LOAz/t2iWwHVfLHjp2oEzsUHboZHIMpKnxuIvW1oeEuzLlQRHAd9mz
|
||||
YJ3rG9XRbkREqaYB7FViHXe4XI5ISXycO1cRrK1zN44veFyQaEfZYGDm/Ac9IiAX
|
||||
xPcW6cTYcvnIc3zfFi8VqT79aie2oetaupgf1eNNZAqdE8hhuvU5HIe6uL17In/2
|
||||
/qxAeeWsEG89jxt5dovEN7MhGITlNgDrYyCZuen+MwS7QcjBAvlEYyCegc5C09Y/
|
||||
LHbTY5xZ3Y+m4Q6gLkH3LpVHz7z9M/P2C2F+fpErgUfCJzDupxBdN49cOSvkBPB7
|
||||
jVaMaA==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICiDCCAg2gAwIBAgIQNfwmXNmET8k9Jj1Xm67XVjAKBggqhkjOPQQDAzCBhDEL
|
||||
MAkGA1UEBhMCVVMxFTATBgNVBAoTDHRoYXd0ZSwgSW5jLjE4MDYGA1UECxMvKGMp
|
||||
IDIwMDcgdGhhd3RlLCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxJDAi
|
||||
BgNVBAMTG3RoYXd0ZSBQcmltYXJ5IFJvb3QgQ0EgLSBHMjAeFw0wNzExMDUwMDAw
|
||||
MDBaFw0zODAxMTgyMzU5NTlaMIGEMQswCQYDVQQGEwJVUzEVMBMGA1UEChMMdGhh
|
||||
d3RlLCBJbmMuMTgwNgYDVQQLEy8oYykgMjAwNyB0aGF3dGUsIEluYy4gLSBGb3Ig
|
||||
YXV0aG9yaXplZCB1c2Ugb25seTEkMCIGA1UEAxMbdGhhd3RlIFByaW1hcnkgUm9v
|
||||
dCBDQSAtIEcyMHYwEAYHKoZIzj0CAQYFK4EEACIDYgAEotWcgnuVnfFSeIf+iha/
|
||||
BebfowJPDQfGAFG6DAJSLSKkQjnE/o/qycG+1E3/n3qe4rF8mq2nhglzh9HnmuN6
|
||||
papu+7qzcMBniKI11KOasf2twu8x+qi58/sIxpHR+ymVo0IwQDAPBgNVHRMBAf8E
|
||||
BTADAQH/MA4GA1UdDwEB/wQEAwIBBjAdBgNVHQ4EFgQUmtgAMADna3+FGO6Lts6K
|
||||
DPgR4bswCgYIKoZIzj0EAwMDaQAwZgIxAN344FdHW6fmCsO99YCKlzUNG4k8VIZ3
|
||||
KMqh9HneteY4sPBlcIx/AlTCv//YoT7ZzwIxAMSNlPzcU9LcnXgWHxUzI1NS41ox
|
||||
XZ3Krr0TKUQNJ1uo52icEvdYPy5yAlejj6EULg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEKjCCAxKgAwIBAgIQYAGXt0an6rS0mtZLL/eQ+zANBgkqhkiG9w0BAQsFADCB
|
||||
rjELMAkGA1UEBhMCVVMxFTATBgNVBAoTDHRoYXd0ZSwgSW5jLjEoMCYGA1UECxMf
|
||||
Q2VydGlmaWNhdGlvbiBTZXJ2aWNlcyBEaXZpc2lvbjE4MDYGA1UECxMvKGMpIDIw
|
||||
MDggdGhhd3RlLCBJbmMuIC0gRm9yIGF1dGhvcml6ZWQgdXNlIG9ubHkxJDAiBgNV
|
||||
BAMTG3RoYXd0ZSBQcmltYXJ5IFJvb3QgQ0EgLSBHMzAeFw0wODA0MDIwMDAwMDBa
|
||||
Fw0zNzEyMDEyMzU5NTlaMIGuMQswCQYDVQQGEwJVUzEVMBMGA1UEChMMdGhhd3Rl
|
||||
LCBJbmMuMSgwJgYDVQQLEx9DZXJ0aWZpY2F0aW9uIFNlcnZpY2VzIERpdmlzaW9u
|
||||
MTgwNgYDVQQLEy8oYykgMjAwOCB0aGF3dGUsIEluYy4gLSBGb3IgYXV0aG9yaXpl
|
||||
ZCB1c2Ugb25seTEkMCIGA1UEAxMbdGhhd3RlIFByaW1hcnkgUm9vdCBDQSAtIEcz
|
||||
MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAsr8nLPvb2FvdeHsbnndm
|
||||
gcs+vHyu86YnmjSjaDFxODNi5PNxZnmxqWWjpYvVj2AtP0LMqmsywCPLLEHd5N/8
|
||||
YZzic7IilRFDGF/Eth9XbAoFWCLINkw6fKXRz4aviKdEAhN0cXMKQlkC+BsUa0Lf
|
||||
b1+6a4KinVvnSr0eAXLbS3ToO39/fR8EtCab4LRarEc9VbjXsCZSKAExQGbY2SS9
|
||||
9irY7CFJXJv2eul/VTV+lmuNk5Mny5K76qxAwJ/C+IDPXfRa3M50hqY+bAtTyr2S
|
||||
zhkGcuYMXDhpxwTWvGzOW/b3aJzcJRVIiKHpqfiYnODz1TEoYRFsZ5aNOZnLwkUk
|
||||
OQIDAQABo0IwQDAPBgNVHRMBAf8EBTADAQH/MA4GA1UdDwEB/wQEAwIBBjAdBgNV
|
||||
HQ4EFgQUrWyqlGCc7eT/+j4KdCtjA/e2Wb8wDQYJKoZIhvcNAQELBQADggEBABpA
|
||||
2JVlrAmSicY59BDlqQ5mU1143vokkbvnRFHfxhY0Cu9qRFHqKweKA3rD6z8KLFIW
|
||||
oCtDuSWQP3CpMyVtRRooOyfPqsMpQhvfO0zAMzRbQYi/aytlryjvsvXDqmbOe1bu
|
||||
t8jLZ8HJnBoYuMTDSQPxYA5QzUbF83d597YV4Djbxy8ooAw/dyZ02SUS2jHaGh7c
|
||||
KUGRIjxpp7sC8rZcJwOJ9Abqm+RyguOhCcHpABnTPtRwa7pxpqpYrvS76Wy274fM
|
||||
m7v/OeZWYdMKp8RcTGB7BXcmer/YB1IsYvdwY9k5vG8cwnncdimvzsUsZAReiDZu
|
||||
MdRAGmI0Nj81Aa6sY6A=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFiDCCA3CgAwIBAgIIfQmX/vBH6nowDQYJKoZIhvcNAQELBQAwYjELMAkGA1UE
|
||||
BhMCQ04xMjAwBgNVBAoMKUdVQU5HIERPTkcgQ0VSVElGSUNBVEUgQVVUSE9SSVRZ
|
||||
IENPLixMVEQuMR8wHQYDVQQDDBZHRENBIFRydXN0QVVUSCBSNSBST09UMB4XDTE0
|
||||
MTEyNjA1MTMxNVoXDTQwMTIzMTE1NTk1OVowYjELMAkGA1UEBhMCQ04xMjAwBgNV
|
||||
BAoMKUdVQU5HIERPTkcgQ0VSVElGSUNBVEUgQVVUSE9SSVRZIENPLixMVEQuMR8w
|
||||
HQYDVQQDDBZHRENBIFRydXN0QVVUSCBSNSBST09UMIICIjANBgkqhkiG9w0BAQEF
|
||||
AAOCAg8AMIICCgKCAgEA2aMW8Mh0dHeb7zMNOwZ+Vfy1YI92hhJCfVZmPoiC7XJj
|
||||
Dp6L3TQsAlFRwxn9WVSEyfFrs0yw6ehGXTjGoqcuEVe6ghWinI9tsJlKCvLriXBj
|
||||
TnnEt1u9ol2x8kECK62pOqPseQrsXzrj/e+APK00mxqriCZ7VqKChh/rNYmDf1+u
|
||||
KU49tm7srsHwJ5uu4/Ts765/94Y9cnrrpftZTqfrlYwiOXnhLQiPzLyRuEH3FMEj
|
||||
qcOtmkVEs7LXLM3GKeJQEK5cy4KOFxg2fZfmiJqwTTQJ9Cy5WmYqsBebnh52nUpm
|
||||
MUHfP/vFBu8btn4aRjb3ZGM74zkYI+dndRTVdVeSN72+ahsmUPI2JgaQxXABZG12
|
||||
ZuGR224HwGGALrIuL4xwp9E7PLOR5G62xDtw8mySlwnNR30YwPO7ng/Wi64HtloP
|
||||
zgsMR6flPri9fcebNaBhlzpBdRfMK5Z3KpIhHtmVdiBnaM8Nvd/WHwlqmuLMc3Gk
|
||||
L30SgLdTMEZeS1SZD2fJpcjyIMGC7J0R38IC+xo70e0gmu9lZJIQDSri3nDxGGeC
|
||||
jGHeuLzRL5z7D9Ar7Rt2ueQ5Vfj4oR24qoAATILnsn8JuLwwoC8N9VKejveSswoA
|
||||
HQBUlwbgsQfZxw9cZX08bVlX5O2ljelAU58VS6Bx9hoh49pwBiFYFIeFd3mqgnkC
|
||||
AwEAAaNCMEAwHQYDVR0OBBYEFOLJQJ9NzuiaoXzPDj9lxSmIahlRMA8GA1UdEwEB
|
||||
/wQFMAMBAf8wDgYDVR0PAQH/BAQDAgGGMA0GCSqGSIb3DQEBCwUAA4ICAQDRSVfg
|
||||
p8xoWLoBDysZzY2wYUWsEe1jUGn4H3++Fo/9nesLqjJHdtJnJO29fDMylyrHBYZm
|
||||
DRd9FBUb1Ov9H5r2XpdptxolpAqzkT9fNqyL7FeoPueBihhXOYV0GkLH6VsTX4/5
|
||||
COmSdI31R9KrO9b7eGZONn356ZLpBN79SWP8bfsUcZNnL0dKt7n/HipzcEYwv1ry
|
||||
L3ml4Y0M2fmyYzeMN2WFcGpcWwlyua1jPLHd+PwyvzeG5LuOmCd+uh8W4XAR8gPf
|
||||
JWIyJyYYMoSf/wA6E7qaTfRPuBRwIrHKK5DOKcFw9C+df/KQHtZa37dG/OaG+svg
|
||||
IHZ6uqbL9XzeYqWxi+7egmaKTjowHz+Ay60nugxe19CxVsp3cbK1daFQqUBDF8Io
|
||||
2c9Si1vIY9RCPqAzekYu9wogRlR+ak8x8YF+QnQ4ZXMn7sZ8uI7XpTrXmKGcjBBV
|
||||
09tL7ECQ8s1uV9JiDnxXk7Gnbc2dg7sq5+W2O3FYrf3RRbxake5TFW/TRQl1brqQ
|
||||
XR4EzzffHqhmsYzmIGrv/EhOdJhCrylvLmrH+33RZjEizIYAfmaDDEL0vTSSwxrq
|
||||
T8p+ck0LcIymSLumoRT2+1hEmRSuqguTaaApJUqlyyvdimYHFngVV3Eb7PVHhPOe
|
||||
MTd61X8kreS8/f3MboPoDKi3QWwH3b08hpcv0g==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIFgzCCA2ugAwIBAgIORea7A4Mzw4VlSOb/RVEwDQYJKoZIhvcNAQEMBQAwTDEg
|
||||
MB4GA1UECxMXR2xvYmFsU2lnbiBSb290IENBIC0gUjYxEzARBgNVBAoTCkdsb2Jh
|
||||
bFNpZ24xEzARBgNVBAMTCkdsb2JhbFNpZ24wHhcNMTQxMjEwMDAwMDAwWhcNMzQx
|
||||
MjEwMDAwMDAwWjBMMSAwHgYDVQQLExdHbG9iYWxTaWduIFJvb3QgQ0EgLSBSNjET
|
||||
MBEGA1UEChMKR2xvYmFsU2lnbjETMBEGA1UEAxMKR2xvYmFsU2lnbjCCAiIwDQYJ
|
||||
KoZIhvcNAQEBBQADggIPADCCAgoCggIBAJUH6HPKZvnsFMp7PPcNCPG0RQssgrRI
|
||||
xutbPK6DuEGSMxSkb3/pKszGsIhrxbaJ0cay/xTOURQh7ErdG1rG1ofuTToVBu1k
|
||||
ZguSgMpE3nOUTvOniX9PeGMIyBJQbUJmL025eShNUhqKGoC3GYEOfsSKvGRMIRxD
|
||||
aNc9PIrFsmbVkJq3MQbFvuJtMgamHvm566qjuL++gmNQ0PAYid/kD3n16qIfKtJw
|
||||
LnvnvJO7bVPiSHyMEAc4/2ayd2F+4OqMPKq0pPbzlUoSB239jLKJz9CgYXfIWHSw
|
||||
1CM69106yqLbnQneXUQtkPGBzVeS+n68UARjNN9rkxi+azayOeSsJDa38O+2HBNX
|
||||
k7besvjihbdzorg1qkXy4J02oW9UivFyVm4uiMVRQkQVlO6jxTiWm05OWgtH8wY2
|
||||
SXcwvHE35absIQh1/OZhFj931dmRl4QKbNQCTXTAFO39OfuD8l4UoQSwC+n+7o/h
|
||||
bguyCLNhZglqsQY6ZZZZwPA1/cnaKI0aEYdwgQqomnUdnjqGBQCe24DWJfncBZ4n
|
||||
WUx2OVvq+aWh2IMP0f/fMBH5hc8zSPXKbWQULHpYT9NLCEnFlWQaYw55PfWzjMpY
|
||||
rZxCRXluDocZXFSxZba/jJvcE+kNb7gu3GduyYsRtYQUigAZcIN5kZeR1Bonvzce
|
||||
MgfYFGM8KEyvAgMBAAGjYzBhMA4GA1UdDwEB/wQEAwIBBjAPBgNVHRMBAf8EBTAD
|
||||
AQH/MB0GA1UdDgQWBBSubAWjkxPioufi1xzWx/B/yGdToDAfBgNVHSMEGDAWgBSu
|
||||
bAWjkxPioufi1xzWx/B/yGdToDANBgkqhkiG9w0BAQwFAAOCAgEAgyXt6NH9lVLN
|
||||
nsAEoJFp5lzQhN7craJP6Ed41mWYqVuoPId8AorRbrcWc+ZfwFSY1XS+wc3iEZGt
|
||||
Ixg93eFyRJa0lV7Ae46ZeBZDE1ZXs6KzO7V33EByrKPrmzU+sQghoefEQzd5Mr61
|
||||
55wsTLxDKZmOMNOsIeDjHfrYBzN2VAAiKrlNIC5waNrlU/yDXNOd8v9EDERm8tLj
|
||||
vUYAGm0CuiVdjaExUd1URhxN25mW7xocBFymFe944Hn+Xds+qkxV/ZoVqW/hpvvf
|
||||
cDDpw+5CRu3CkwWJ+n1jez/QcYF8AOiYrg54NMMl+68KnyBr3TsTjxKM4kEaSHpz
|
||||
oHdpx7Zcf4LIHv5YGygrqGytXm3ABdJ7t+uA/iU3/gKbaKxCXcPu9czc8FB10jZp
|
||||
nOZ7BN9uBmm23goJSFmH63sUYHpkqmlD75HHTOwY3WzvUy2MmeFe8nI+z1TIvWfs
|
||||
pA9MRf/TuTAjB0yPEL+GltmZWrSZVxykzLsViVO6LAUP5MSeGbEYNNVMnbrt9x+v
|
||||
JJUEeKgDu+6B5dpffItKoZB0JaezPkvILFa9x8jvOOJckvB595yEunQtYQEgfn7R
|
||||
8k8HWV+LLUNS60YMlOH1Zkd5d9VUWx+tJDfLRVpOoERIyNiwmcUVhAn21klJwGW4
|
||||
5hpxbqCo8YLoRT5s1gLXCmeDBVrJpBA=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICaTCCAe+gAwIBAgIQISpWDK7aDKtARb8roi066jAKBggqhkjOPQQDAzBtMQsw
|
||||
CQYDVQQGEwJDSDEQMA4GA1UEChMHV0lTZUtleTEiMCAGA1UECxMZT0lTVEUgRm91
|
||||
bmRhdGlvbiBFbmRvcnNlZDEoMCYGA1UEAxMfT0lTVEUgV0lTZUtleSBHbG9iYWwg
|
||||
Um9vdCBHQyBDQTAeFw0xNzA1MDkwOTQ4MzRaFw00MjA1MDkwOTU4MzNaMG0xCzAJ
|
||||
BgNVBAYTAkNIMRAwDgYDVQQKEwdXSVNlS2V5MSIwIAYDVQQLExlPSVNURSBGb3Vu
|
||||
ZGF0aW9uIEVuZG9yc2VkMSgwJgYDVQQDEx9PSVNURSBXSVNlS2V5IEdsb2JhbCBS
|
||||
b290IEdDIENBMHYwEAYHKoZIzj0CAQYFK4EEACIDYgAETOlQwMYPchi82PG6s4ni
|
||||
eUqjFqdrVCTbUf/q9Akkwwsin8tqJ4KBDdLArzHkdIJuyiXZjHWd8dvQmqJLIX4W
|
||||
p2OQ0jnUsYd4XxiWD1AbNTcPasbc2RNNpI6QN+a9WzGRo1QwUjAOBgNVHQ8BAf8E
|
||||
BAMCAQYwDwYDVR0TAQH/BAUwAwEB/zAdBgNVHQ4EFgQUSIcUrOPDnpBgOtfKie7T
|
||||
rYy0UGYwEAYJKwYBBAGCNxUBBAMCAQAwCgYIKoZIzj0EAwMDaAAwZQIwJsdpW9zV
|
||||
57LnyAyMjMPdeYwbY9XJUpROTYJKcx6ygISpJcBMWm1JKWB4E+J+SOtkAjEA2zQg
|
||||
Mgj/mkkCtojeFK9dbJlxjRo/i9fgojaGHAeCOnZT/cKi7e97sIBPWA9LUzm9
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIClDCCAhqgAwIBAgIILCmcWxbtBZUwCgYIKoZIzj0EAwIwfzELMAkGA1UEBhMC
|
||||
VVMxDjAMBgNVBAgMBVRleGFzMRAwDgYDVQQHDAdIb3VzdG9uMRgwFgYDVQQKDA9T
|
||||
U0wgQ29ycG9yYXRpb24xNDAyBgNVBAMMK1NTTC5jb20gRVYgUm9vdCBDZXJ0aWZp
|
||||
Y2F0aW9uIEF1dGhvcml0eSBFQ0MwHhcNMTYwMjEyMTgxNTIzWhcNNDEwMjEyMTgx
|
||||
NTIzWjB/MQswCQYDVQQGEwJVUzEOMAwGA1UECAwFVGV4YXMxEDAOBgNVBAcMB0hv
|
||||
dXN0b24xGDAWBgNVBAoMD1NTTCBDb3Jwb3JhdGlvbjE0MDIGA1UEAwwrU1NMLmNv
|
||||
bSBFViBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5IEVDQzB2MBAGByqGSM49
|
||||
AgEGBSuBBAAiA2IABKoSR5CYG/vvw0AHgyBO8TCCogbR8pKGYfL2IWjKAMTH6kMA
|
||||
VIbc/R/fALhBYlzccBYy3h+Z1MzFB8gIH2EWB1E9fVwHU+M1OIzfzZ/ZLg1Kthku
|
||||
WnBaBu2+8KGwytAJKaNjMGEwHQYDVR0OBBYEFFvKXuXe0oGqzagtZFG22XKbl+ZP
|
||||
MA8GA1UdEwEB/wQFMAMBAf8wHwYDVR0jBBgwFoAUW8pe5d7SgarNqC1kUbbZcpuX
|
||||
5k8wDgYDVR0PAQH/BAQDAgGGMAoGCCqGSM49BAMCA2gAMGUCMQCK5kCJN+vp1RPZ
|
||||
ytRrJPOwPYdGWBrssd9v+1a6cGvHOMzosYxPD/fxZ3YOg9AeUY8CMD32IygmTMZg
|
||||
h5Mmm7I1HrrW9zzRHM76JTymGoEVW/MSD2zuZYrJh6j5B+BimoxcSg==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF6zCCA9OgAwIBAgIIVrYpzTS8ePYwDQYJKoZIhvcNAQELBQAwgYIxCzAJBgNV
|
||||
BAYTAlVTMQ4wDAYDVQQIDAVUZXhhczEQMA4GA1UEBwwHSG91c3RvbjEYMBYGA1UE
|
||||
CgwPU1NMIENvcnBvcmF0aW9uMTcwNQYDVQQDDC5TU0wuY29tIEVWIFJvb3QgQ2Vy
|
||||
dGlmaWNhdGlvbiBBdXRob3JpdHkgUlNBIFIyMB4XDTE3MDUzMTE4MTQzN1oXDTQy
|
||||
MDUzMDE4MTQzN1owgYIxCzAJBgNVBAYTAlVTMQ4wDAYDVQQIDAVUZXhhczEQMA4G
|
||||
A1UEBwwHSG91c3RvbjEYMBYGA1UECgwPU1NMIENvcnBvcmF0aW9uMTcwNQYDVQQD
|
||||
DC5TU0wuY29tIEVWIFJvb3QgQ2VydGlmaWNhdGlvbiBBdXRob3JpdHkgUlNBIFIy
|
||||
MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAjzZlQOHWTcDXtOlG2mvq
|
||||
M0fNTPl9fb69LT3w23jhhqXZuglXaO1XPqDQCEGD5yhBJB/jchXQARr7XnAjssuf
|
||||
OePPxU7Gkm0mxnu7s9onnQqG6YE3Bf7wcXHswxzpY6IXFJ3vG2fThVUCAtZJycxa
|
||||
4bH3bzKfydQ7iEGonL3Lq9ttewkfokxykNorCPzPPFTOZw+oz12WGQvE43LrrdF9
|
||||
HSfvkusQv1vrO6/PgN3B0pYEW3p+pKk8OHakYo6gOV7qd89dAFmPZiw+B6KjBSYR
|
||||
aZfqhbcPlgtLyEDhULouisv3D5oi53+aNxPN8k0TayHRwMwi8qFG9kRpnMphNQcA
|
||||
b9ZhCBHqurj26bNg5U257J8UZslXWNvNh2n4ioYSA0e/ZhN2rHd9NCSFg83XqpyQ
|
||||
Gp8hLH94t2S42Oim9HizVcuE0jLEeK6jj2HdzghTreyI/BXkmg3mnxp3zkyPuBQV
|
||||
PWKchjgGAGYS5Fl2WlPAApiiECtoRHuOec4zSnaqW4EWG7WK2NAAe15itAnWhmMO
|
||||
pgWVSbooi4iTsjQc2KRVbrcc0N6ZVTsj9CLg+SlmJuwgUHfbSguPvuUCYHBBXtSu
|
||||
UDkiFCbLsjtzdFVHB3mBOagwE0TlBIqulhMlQg+5U8Sb/M3kHN48+qvWBkofZ6aY
|
||||
MBzdLNvcGJVXZsb/XItW9XcCAwEAAaNjMGEwDwYDVR0TAQH/BAUwAwEB/zAfBgNV
|
||||
HSMEGDAWgBT5YLvU49U09rj1BoAlp3PbRmmonjAdBgNVHQ4EFgQU+WC71OPVNPa4
|
||||
9QaAJadz20ZpqJ4wDgYDVR0PAQH/BAQDAgGGMA0GCSqGSIb3DQEBCwUAA4ICAQBW
|
||||
s47LCp1Jjr+kxJG7ZhcFUZh1++VQLHqe8RT6q9OKPv+RKY9ji9i0qVQBDb6Thi/5
|
||||
Sm3HXvVX+cpVHBK+Rw82xd9qt9t1wkclf7nxY/hoLVUE0fKNsKTPvDxeH3jnpaAg
|
||||
cLAExbf3cqfeIg29MyVGjGSSJuM+LmOW2puMPfgYCdcDzH2GguDKBAdRUNf/ktUM
|
||||
79qGn5nX67evaOI5JpS6aLe/g9Pqemc9YmeuJeVy6OLk7K4S9ksrPJ/psEDzOFSz
|
||||
/bdoyNrGj1E8svuR3Bznm53htw1yj+KkxKl4+esUrMZDBcJlOSgYAsOCsp0FvmXt
|
||||
ll9ldDz7CTUue5wT/RsPXcdtgTpWD8w74a8CLyKsRspGPKAcTNZEtF4uXBVmCeEm
|
||||
Kf7GUmG6sXP/wwyc5WxqlD8UykAWlYTzWamsX0xhk23RO8yilQwipmdnRC652dKK
|
||||
QbNmC1r7fSOl8hqw/96bg5Qu0T/fkreRrwU7ZcegbLHNYhLDkBvjJc40vG93drEQ
|
||||
w/cFGsDWr3RiSBd3kmmQYRzelYB0VI8YHMPzA9C/pEN1hlMYegouCRw2n5H9gooi
|
||||
S9EOUCXdywMMF8mDAAhONU2Ki+3wApRmLER/y5UnlhetCTCstnEXbosX9hwJ1C07
|
||||
mKVx01QT2WDz9UtmT/rx7iASjbSsV7FFY6GsdqnC+w==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIICjTCCAhSgAwIBAgIIdebfy8FoW6gwCgYIKoZIzj0EAwIwfDELMAkGA1UEBhMC
|
||||
VVMxDjAMBgNVBAgMBVRleGFzMRAwDgYDVQQHDAdIb3VzdG9uMRgwFgYDVQQKDA9T
|
||||
U0wgQ29ycG9yYXRpb24xMTAvBgNVBAMMKFNTTC5jb20gUm9vdCBDZXJ0aWZpY2F0
|
||||
aW9uIEF1dGhvcml0eSBFQ0MwHhcNMTYwMjEyMTgxNDAzWhcNNDEwMjEyMTgxNDAz
|
||||
WjB8MQswCQYDVQQGEwJVUzEOMAwGA1UECAwFVGV4YXMxEDAOBgNVBAcMB0hvdXN0
|
||||
b24xGDAWBgNVBAoMD1NTTCBDb3Jwb3JhdGlvbjExMC8GA1UEAwwoU1NMLmNvbSBS
|
||||
b290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5IEVDQzB2MBAGByqGSM49AgEGBSuB
|
||||
BAAiA2IABEVuqVDEpiM2nl8ojRfLliJkP9x6jh3MCLOicSS6jkm5BBtHllirLZXI
|
||||
7Z4INcgn64mMU1jrYor+8FsPazFSY0E7ic3s7LaNGdM0B9y7xgZ/wkWV7Mt/qCPg
|
||||
CemB+vNH06NjMGEwHQYDVR0OBBYEFILRhXMw5zUE044CkvvlpNHEIejNMA8GA1Ud
|
||||
EwEB/wQFMAMBAf8wHwYDVR0jBBgwFoAUgtGFczDnNQTTjgKS++Wk0cQh6M0wDgYD
|
||||
VR0PAQH/BAQDAgGGMAoGCCqGSM49BAMCA2cAMGQCMG/n61kRpGDPYbCWe+0F+S8T
|
||||
kdzt5fxQaxFGRrMcIQBiu77D5+jNB5n5DQtdcj7EqgIwH7y6C+IwJPt8bYBVCpk+
|
||||
gA0z5Wajs6O7pdWLjwkspl1+4vAHCGht0nxpbl/f5Wpl
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIF3TCCA8WgAwIBAgIIeyyb0xaAMpkwDQYJKoZIhvcNAQELBQAwfDELMAkGA1UE
|
||||
BhMCVVMxDjAMBgNVBAgMBVRleGFzMRAwDgYDVQQHDAdIb3VzdG9uMRgwFgYDVQQK
|
||||
DA9TU0wgQ29ycG9yYXRpb24xMTAvBgNVBAMMKFNTTC5jb20gUm9vdCBDZXJ0aWZp
|
||||
Y2F0aW9uIEF1dGhvcml0eSBSU0EwHhcNMTYwMjEyMTczOTM5WhcNNDEwMjEyMTcz
|
||||
OTM5WjB8MQswCQYDVQQGEwJVUzEOMAwGA1UECAwFVGV4YXMxEDAOBgNVBAcMB0hv
|
||||
dXN0b24xGDAWBgNVBAoMD1NTTCBDb3Jwb3JhdGlvbjExMC8GA1UEAwwoU1NMLmNv
|
||||
bSBSb290IENlcnRpZmljYXRpb24gQXV0aG9yaXR5IFJTQTCCAiIwDQYJKoZIhvcN
|
||||
AQEBBQADggIPADCCAgoCggIBAPkP3aMrfcvQKv7sZ4Wm5y4bunfh4/WvpOz6Sl2R
|
||||
xFdHaxh3a3by/ZPkPQ/CFp4LZsNWlJ4Xg4XOVu/yFv0AYvUiCVToZRdOQbngT0aX
|
||||
qhvIuG5iXmmxX9sqAn78bMrzQdjt0Oj8P2FI7bADFB0QDksZ4LtO7IZl/zbzXmcC
|
||||
C52GVWH9ejjt/uIZALdvoVBidXQ8oPrIJZK0bnoix/geoeOy3ZExqysdBP+lSgQ3
|
||||
6YWkMyv94tZVNHwZpEpox7Ko07fKoZOI68GXvIz5HdkihCR0xwQ9aqkpk8zruFvh
|
||||
/l8lqjRYyMEjVJ0bmBHDOJx+PYZspQ9AhnwC9FwCTyjLrnGfDzrIM/4RJTXq/LrF
|
||||
YD3ZfBjVsqnTdXgDciLKOsMf7yzlLqn6niy2UUb9rwPW6mBo6oUWNmuF6R7As93E
|
||||
JNyAKoFBbZQ+yODJgUEAnl6/f8UImKIYLEJAs/lvOCdLToD0PYFH4Ih86hzOtXVc
|
||||
US4cK38acijnALXRdMbX5J+tB5O2UzU1/Dfkw/ZdFr4hc96SCvigY2q8lpJqPvi8
|
||||
ZVWb3vUNiSYE/CUapiVpy8JtynziWV+XrOvvLsi81xtZPCvM8hnIk2snYxnP/Okm
|
||||
+Mpxm3+T/jRnhE6Z6/yzeAkzcLpmpnbtG3PrGqUNxCITIJRWCk4sbE6x/c+cCbqi
|
||||
M+2HAgMBAAGjYzBhMB0GA1UdDgQWBBTdBAkHovV6fVJTEpKV7jiAJQ2mWTAPBgNV
|
||||
HRMBAf8EBTADAQH/MB8GA1UdIwQYMBaAFN0ECQei9Xp9UlMSkpXuOIAlDaZZMA4G
|
||||
A1UdDwEB/wQEAwIBhjANBgkqhkiG9w0BAQsFAAOCAgEAIBgRlCn7Jp0cHh5wYfGV
|
||||
cpNxJK1ok1iOMq8bs3AD/CUrdIWQPXhq9LmLpZc7tRiRux6n+UBbkflVma8eEdBc
|
||||
Hadm47GUBwwyOabqG7B52B2ccETjit3E+ZUfijhDPwGFpUenPUayvOUiaPd7nNgs
|
||||
PgohyC0zrL/FgZkxdMF1ccW+sfAjRfSda/wZY52jvATGGAslu1OJD7OAUN5F7kR/
|
||||
q5R4ZJjT9ijdh9hwZXT7DrkT66cPYakylszeu+1jTBi7qUD3oFRuIIhxdRjqerQ0
|
||||
cuAjJ3dctpDqhiVAq+8zD8ufgr6iIPv2tS0a5sKFsXQP+8hlAqRSAUfdSSLBv9jr
|
||||
a6x+3uxjMxW3IwiPxg+NQVrdjsW5j+VFP3jbutIbQLH+cU0/4IGiul607BXgk90I
|
||||
H37hVZkLId6Tngr75qNJvTYw/ud3sqB1l7UtgYgXZSD32pAAn8lSzDLKNXz1PQ/Y
|
||||
K9f1JmzJBjSWFupwWRoyeXkLtoh/D1JIPb9s2KJELtFOt3JY04kTlf5Eq/jXixtu
|
||||
nLwsoFvVagCvXzfh1foQC5ichucmj87w7G6KVwuA406ywKBjYZC6VWg3dGq2ktuf
|
||||
oYYitmUnDuy2n0Jg5GfCtdpBC8TTi2EbvPofkSvXRAdeuims2cXp71NIWuuA8ShY
|
||||
Ic2wBlX7Jz9TkHCpBB5XJ7k=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEIDCCAwigAwIBAgIJAISCLF8cYtBAMA0GCSqGSIb3DQEBCwUAMIGcMQswCQYD
|
||||
VQQGEwJQQTEPMA0GA1UECAwGUGFuYW1hMRQwEgYDVQQHDAtQYW5hbWEgQ2l0eTEk
|
||||
MCIGA1UECgwbVHJ1c3RDb3IgU3lzdGVtcyBTLiBkZSBSLkwuMScwJQYDVQQLDB5U
|
||||
cnVzdENvciBDZXJ0aWZpY2F0ZSBBdXRob3JpdHkxFzAVBgNVBAMMDlRydXN0Q29y
|
||||
IEVDQS0xMB4XDTE2MDIwNDEyMzIzM1oXDTI5MTIzMTE3MjgwN1owgZwxCzAJBgNV
|
||||
BAYTAlBBMQ8wDQYDVQQIDAZQYW5hbWExFDASBgNVBAcMC1BhbmFtYSBDaXR5MSQw
|
||||
IgYDVQQKDBtUcnVzdENvciBTeXN0ZW1zIFMuIGRlIFIuTC4xJzAlBgNVBAsMHlRy
|
||||
dXN0Q29yIENlcnRpZmljYXRlIEF1dGhvcml0eTEXMBUGA1UEAwwOVHJ1c3RDb3Ig
|
||||
RUNBLTEwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQDPj+ARtZ+odnbb
|
||||
3w9U73NjKYKtR8aja+3+XzP4Q1HpGjORMRegdMTUpwHmspI+ap3tDvl0mEDTPwOA
|
||||
BoJA6LHip1GnHYMma6ve+heRK9jGrB6xnhkB1Zem6g23xFUfJ3zSCNV2HykVh0A5
|
||||
3ThFEXXQmqc04L/NyFIduUd+Dbi7xgz2c1cWWn5DkR9VOsZtRASqnKmcp0yJF4Ou
|
||||
owReUoCLHhIlERnXDH19MURB6tuvsBzvgdAsxZohmz3tQjtQJvLsznFhBmIhVE5/
|
||||
wZ0+fyCMgMsq2JdiyIMzkX2woloPV+g7zPIlstR8L+xNxqE6FXrntl019fZISjZF
|
||||
ZtS6mFjBAgMBAAGjYzBhMB0GA1UdDgQWBBREnkj1zG1I1KBLf/5ZJC+Dl5mahjAf
|
||||
BgNVHSMEGDAWgBREnkj1zG1I1KBLf/5ZJC+Dl5mahjAPBgNVHRMBAf8EBTADAQH/
|
||||
MA4GA1UdDwEB/wQEAwIBhjANBgkqhkiG9w0BAQsFAAOCAQEABT41XBVwm8nHc2Fv
|
||||
civUwo/yQ10CzsSUuZQRg2dd4mdsdXa/uwyqNsatR5Nj3B5+1t4u/ukZMjgDfxT2
|
||||
AHMsWbEhBuH7rBiVDKP/mZb3Kyeb1STMHd3BOuCYRLDE5D53sXOpZCz2HAF8P11F
|
||||
hcCF5yWPldwX8zyfGm6wyuMdKulMY/okYWLW2n62HGz1Ah3UKt1VkOsqEUc8Ll50
|
||||
soIipX1TH0XsJ5F95yIW6MBoNtjG8U+ARDL54dHRHareqKucBK+tIA5kmE2la8BI
|
||||
WJZpTdwHjFGTot+fDz2LYLSCjaoITmJF4PkL0uDgPFveXHEnJcLmA4GLEFPjx1Wi
|
||||
tJ/X5g==
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIEMDCCAxigAwIBAgIJANqb7HHzA7AZMA0GCSqGSIb3DQEBCwUAMIGkMQswCQYD
|
||||
VQQGEwJQQTEPMA0GA1UECAwGUGFuYW1hMRQwEgYDVQQHDAtQYW5hbWEgQ2l0eTEk
|
||||
MCIGA1UECgwbVHJ1c3RDb3IgU3lzdGVtcyBTLiBkZSBSLkwuMScwJQYDVQQLDB5U
|
||||
cnVzdENvciBDZXJ0aWZpY2F0ZSBBdXRob3JpdHkxHzAdBgNVBAMMFlRydXN0Q29y
|
||||
IFJvb3RDZXJ0IENBLTEwHhcNMTYwMjA0MTIzMjE2WhcNMjkxMjMxMTcyMzE2WjCB
|
||||
pDELMAkGA1UEBhMCUEExDzANBgNVBAgMBlBhbmFtYTEUMBIGA1UEBwwLUGFuYW1h
|
||||
IENpdHkxJDAiBgNVBAoMG1RydXN0Q29yIFN5c3RlbXMgUy4gZGUgUi5MLjEnMCUG
|
||||
A1UECwweVHJ1c3RDb3IgQ2VydGlmaWNhdGUgQXV0aG9yaXR5MR8wHQYDVQQDDBZU
|
||||
cnVzdENvciBSb290Q2VydCBDQS0xMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIB
|
||||
CgKCAQEAv463leLCJhJrMxnHQFgKq1mqjQCj/IDHUHuO1CAmujIS2CNUSSUQIpid
|
||||
RtLByZ5OGy4sDjjzGiVoHKZaBeYei0i/mJZ0PmnK6bV4pQa81QBeCQryJ3pS/C3V
|
||||
seq0iWEk8xoT26nPUu0MJLq5nux+AHT6k61sKZKuUbS701e/s/OojZz0JEsq1pme
|
||||
9J7+wH5COucLlVPat2gOkEz7cD+PSiyU8ybdY2mplNgQTsVHCJCZGxdNuWxu72CV
|
||||
EY4hgLW9oHPY0LJ3xEXqWib7ZnZ2+AYfYW0PVcWDtxBWcgYHpfOxGgMFZA6dWorW
|
||||
hnAbJN7+KIor0Gqw/Hqi3LJ5DotlDwIDAQABo2MwYTAdBgNVHQ4EFgQU7mtJPHo/
|
||||
DeOxCbeKyKsZn3MzUOcwHwYDVR0jBBgwFoAU7mtJPHo/DeOxCbeKyKsZn3MzUOcw
|
||||
DwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAYYwDQYJKoZIhvcNAQELBQAD
|
||||
ggEBACUY1JGPE+6PHh0RU9otRCkZoB5rMZ5NDp6tPVxBb5UrJKF5mDo4Nvu7Zp5I
|
||||
/5CQ7z3UuJu0h3U/IJvOcs+hVcFNZKIZBqEHMwwLKeXx6quj7LUKdJDHfXLy11yf
|
||||
ke+Ri7fc7Waiz45mO7yfOgLgJ90WmMCV1Aqk5IGadZQ1nJBfiDcGrVmVCrDRZ9MZ
|
||||
yonnMlo2HD6CqFqTvsbQZJG2z9m2GM/bftJlo6bEjhcxwft+dtvTheNYsnd6djts
|
||||
L1Ac59v2Z3kf9YKVmgenFK+P3CghZwnS1k1aHBkcjndcw5QkPTJrS37UeJSDvjdN
|
||||
zl/HHk484IkzlQsPpTLWPFp5LBk=
|
||||
-----END CERTIFICATE-----
|
||||
-----BEGIN CERTIFICATE-----
|
||||
MIIGLzCCBBegAwIBAgIIJaHfyjPLWQIwDQYJKoZIhvcNAQELBQAwgaQxCzAJBgNV
|
||||
BAYTAlBBMQ8wDQYDVQQIDAZQYW5hbWExFDASBgNVBAcMC1BhbmFtYSBDaXR5MSQw
|
||||
IgYDVQQKDBtUcnVzdENvciBTeXN0ZW1zIFMuIGRlIFIuTC4xJzAlBgNVBAsMHlRy
|
||||
dXN0Q29yIENlcnRpZmljYXRlIEF1dGhvcml0eTEfMB0GA1UEAwwWVHJ1c3RDb3Ig
|
||||
Um9vdENlcnQgQ0EtMjAeFw0xNjAyMDQxMjMyMjNaFw0zNDEyMzExNzI2MzlaMIGk
|
||||
MQswCQYDVQQGEwJQQTEPMA0GA1UECAwGUGFuYW1hMRQwEgYDVQQHDAtQYW5hbWEg
|
||||
Q2l0eTEkMCIGA1UECgwbVHJ1c3RDb3IgU3lzdGVtcyBTLiBkZSBSLkwuMScwJQYD
|
||||
VQQLDB5UcnVzdENvciBDZXJ0aWZpY2F0ZSBBdXRob3JpdHkxHzAdBgNVBAMMFlRy
|
||||
dXN0Q29yIFJvb3RDZXJ0IENBLTIwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIK
|
||||
AoICAQCnIG7CKqJiJJWQdsg4foDSq8GbZQWU9MEKENUCrO2fk8eHyLAnK0IMPQo+
|
||||
QVqedd2NyuCb7GgypGmSaIwLgQ5WoD4a3SwlFIIvl9NkRvRUqdw6VC0xK5mC8tkq
|
||||
1+9xALgxpL56JAfDQiDyitSSBBtlVkxs1Pu2YVpHI7TYabS3OtB0PAx1oYxOdqHp
|
||||
2yqlO/rOsP9+aij9JxzIsekp8VduZLTQwRVtDr4uDkbIXvRR/u8OYzo7cbrPb1nK
|
||||
DOObXUm4TOJXsZiKQlecdu/vvdFoqNL0Cbt3Nb4lggjEFixEIFapRBF37120Hape
|
||||
az6LMvYHL1cEksr1/p3C6eizjkxLAjHZ5DxIgif3GIJ2SDpxsROhOdUuxTTCHWKF
|
||||
3wP+TfSvPd9cW436cOGlfifHhi5qjxLGhF5DUVCcGZt45vz27Ud+ez1m7xMTiF88
|
||||
oWP7+ayHNZ/zgp6kPwqcMWmLmaSISo5uZk3vFsQPeSghYA2FFn3XVDjxklb9tTNM
|
||||
g9zXEJ9L/cb4Qr26fHMC4P99zVvh1Kxhe1fVSntb1IVYJ12/+CtgrKAmrhQhJ8Z3
|
||||
mjOAPF5GP/fDsaOGM8boXg25NSyqRsGFAnWAoOsk+xWq5Gd/bnc/9ASKL3x74xdh
|
||||
8N0JqSDIvgmk0H5Ew7IwSjiqqewYmgeCK9u4nBit2uBGF6zPXQIDAQABo2MwYTAd
|
||||
BgNVHQ4EFgQU2f4hQG6UnrybPZx9mCAZ5YwwYrIwHwYDVR0jBBgwFoAU2f4hQG6U
|
||||
nrybPZx9mCAZ5YwwYrIwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAYYw
|
||||
DQYJKoZIhvcNAQELBQADggIBAJ5Fngw7tu/hOsh80QA9z+LqBrWyOrsGS2h60COX
|
||||
dKcs8AjYeVrXWoSK2BKaG9l9XE1wxaX5q+WjiYndAfrs3fnpkpfbsEZC89NiqpX+
|
||||
MWcUaViQCqoL7jcjx1BRtPV+nuN79+TMQjItSQzL/0kMmx40/W5ulop5A7Zv2wnL
|
||||
/V9lFDfhOPXzYRZY5LVtDQsEGz9QLX+zx3oaFoBg+Iof6Rsqxvm6ARppv9JYx1RX
|
||||
CI/hOWB3S6xZhBqI8d3LT3jX5+EzLfzuQfogsL7L9ziUwOHQhQ+77Sxzq+3+knYa
|
||||
ZH9bDTMJBzN7Bj8RpFxwPIXAz+OQqIN3+tvmxYxoZxBnpVIt8MSZj3+/0WvitUfW
|
||||
2dCFmU2Umw9Lje4AWkcdEQOsQRivh7dvDDqPys/cA8GiCcjl/YBeyGBCARsaU1q7
|
||||
N6a3vLqE6R5sGtRk2tRD/pOLS/IseRYQ1JMLiI+h2IYURpFHmygk71dSTlxCnKr3
|
||||
Sewn6EAes6aJInKc9Q0ztFijMDvd1GpUk74aTfOTlPf8hAs/hCBcNANExdqtvArB
|
||||
As8e5ZTZ845b2EzwnexhF7sUMlQMAimTHpKG9n/v55IFDlndmQguLvqcAFLTxWYp
|
||||
5KeXRKQOKIETNcX2b2TmQcTVL8w0RSXPQQCWPUouwpaYT05KnJe32x+SMsj/D1Fu
|
||||
1uwJ
|
||||
-----END CERTIFICATE-----
|
||||
@@ -0,0 +1,101 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/404.html">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>404 Page not found - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<header class="page-header">
|
||||
<h1>404 Page not found</h1>
|
||||
</header>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,241 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>GOPROXY手册 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>GOPROXY手册</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/first/">手册前言(使用必读)</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY使用必读 手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" title="手册前言(使用必读)">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/tcp/">TCP代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" title="TCP代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,33 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>GOPROXY手册 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/</link>
|
||||
<description>Recent content in GOPROXY手册 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Thu, 04 Jul 2019 11:00:50 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>手册前言(使用必读)</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/first/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/first/</guid>
|
||||
<description>前言 GOPROXY使用必读 手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>TCP代理</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/tcp/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/tcp/</guid>
|
||||
<description>工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/</title><link rel="canonical" href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/" /></head></html>
|
||||
@@ -0,0 +1,205 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/categories/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/categories/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Categories - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<header class="page-header">
|
||||
<h1>Categories</h1>
|
||||
</header>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="list-group">
|
||||
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册 <span class="badge">2</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说 <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级 <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类 <span class="badge">8</span></a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,51 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>Categories on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/</link>
|
||||
<description>Recent content in Categories on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/categories/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>默认分类</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>GOPROXY手册</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>架构解说</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>细说层级</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1,216 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>架构解说 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>架构解说</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T15:29:47JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/categories/">Categories</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">不用看这里,没什么内容,仅仅为了定义目录和tags。</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>架构解说 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/</link>
|
||||
<description>Recent content in 架构解说 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 14 Jun 2019 15:29:47 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>Categories</title>
|
||||
<link>https://snail.gitee.io/proxy/page/categories/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/categories/</guid>
|
||||
<description>不用看这里,没什么内容,仅仅为了定义目录和tags。</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/</title><link rel="canonical" href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/" /></head></html>
|
||||
@@ -0,0 +1,216 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>细说层级 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>细说层级</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T15:29:47JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/categories/">Categories</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">不用看这里,没什么内容,仅仅为了定义目录和tags。</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>细说层级 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/</link>
|
||||
<description>Recent content in 细说层级 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 14 Jun 2019 15:29:47 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>Categories</title>
|
||||
<link>https://snail.gitee.io/proxy/page/categories/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/categories/</guid>
|
||||
<description>不用看这里,没什么内容,仅仅为了定义目录和tags。</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/</title><link rel="canonical" href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/" /></head></html>
|
||||
@@ -0,0 +1,367 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>默认分类 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>默认分类</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial/">GOPROXY免费版VS商业版</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" title="GOPROXY免费版VS商业版">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:29:13JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/">常见问题解答</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">问:http代理支持https网站吗? 答:goproxy的http代理同时支持http和https网站。 问:socks5代理支持UDP吗? 答</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" title="常见问题解答">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T17:54:31JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">在windows下实现基于dns的自动全局代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" title="在windows下实现基于dns的自动全局代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:37:30JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/cloudflare/">Cloudflare使用简明教程</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" title="Cloudflare使用简明教程">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:02:57JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/">内网穿透也能用CDN???!</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" title="内网穿透也能用CDN???!">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">GOPROXY Free Version VS Commercial Version</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" title="GOPROXY Free Version VS Commercial Version">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">代理之套用CDN</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" title="代理之套用CDN">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,87 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>默认分类 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/</link>
|
||||
<description>Recent content in 默认分类 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>GOPROXY免费版VS商业版</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial/</guid>
|
||||
<description>目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>常见问题解答</title>
|
||||
<link>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:29:13 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</guid>
|
||||
<description>问:http代理支持https网站吗? 答:goproxy的http代理同时支持http和https网站。 问:socks5代理支持UDP吗? 答</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>在windows下实现基于dns的自动全局代理</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 17:54:31 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</guid>
|
||||
<description>在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Cloudflare使用简明教程</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/cloudflare/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:37:30 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/cloudflare/</guid>
|
||||
<description>前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>内网穿透也能用CDN???!</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http-nat-cdn/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:02:57 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http-nat-cdn/</guid>
|
||||
<description>内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>GOPROXY Free Version VS Commercial Version</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</guid>
|
||||
<description>Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>代理之套用CDN</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http_cdn_ws/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:25:06 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http_cdn_ws/</guid>
|
||||
<description>goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/</title><link rel="canonical" href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/" /></head></html>
|
||||
@@ -0,0 +1,295 @@
|
||||
html {
|
||||
font-size: 18px;
|
||||
}
|
||||
|
||||
@media (max-width: 768px) {
|
||||
html {
|
||||
font-size: 15px;
|
||||
}
|
||||
}
|
||||
|
||||
body {
|
||||
font-size: inherit;
|
||||
font-weight: 300;
|
||||
}
|
||||
|
||||
p {
|
||||
margin: 0;
|
||||
}
|
||||
|
||||
img {
|
||||
max-width: 100%;
|
||||
}
|
||||
|
||||
ul,ol {
|
||||
margin: 0;
|
||||
padding: 0;
|
||||
}
|
||||
|
||||
h1, h2, h3, h4, h5, h6 {
|
||||
margin: 0;
|
||||
}
|
||||
|
||||
h1 { font-size: 1.8rem; line-height: 2rem; margin: 1.5rem 0; }
|
||||
h2 { font-size: 1.4rem; line-height: 2rem; margin: 1.5rem 0; }
|
||||
h3 { font-size: 1.2rem; line-height: 1.5rem; margin: 1.5rem 0; }
|
||||
h4, h5, h6 { font-size: 1rem; line-height: 1.5rem; margin: 1.5rem 0; }
|
||||
|
||||
main {
|
||||
display: block;
|
||||
}
|
||||
|
||||
/* Override */
|
||||
.navbar {
|
||||
border-radius: 0;
|
||||
}
|
||||
|
||||
.page-header {
|
||||
margin: 0;
|
||||
margin-bottom: 1rem;
|
||||
padding: 0;
|
||||
padding: 1rem 0;
|
||||
}
|
||||
|
||||
.page-header h1 {
|
||||
margin: 0;
|
||||
}
|
||||
|
||||
/* Layouts */
|
||||
.l-header {
|
||||
font-size: .8rem;
|
||||
}
|
||||
|
||||
.l-footer {
|
||||
font-size: .8rem;
|
||||
padding: 1.5rem 0;
|
||||
color: #999;
|
||||
}
|
||||
|
||||
/* Parts:facts */
|
||||
.p-facts {
|
||||
list-style: none;
|
||||
margin-bottom: .5rem;
|
||||
}
|
||||
|
||||
.p-facts li {
|
||||
display: inline;
|
||||
font-size: .8rem;
|
||||
margin-right: .5rem;
|
||||
}
|
||||
|
||||
.p-facts li i {
|
||||
margin-right: .5rem;
|
||||
color: #999;
|
||||
}
|
||||
|
||||
/* Parts:facts */
|
||||
.p-crumb {
|
||||
font-size: .8rem;
|
||||
margin-bottom: 1.5rem;
|
||||
}
|
||||
|
||||
.p-crumb ol {
|
||||
margin-bottom: 0;
|
||||
}
|
||||
|
||||
/* Parts:terms */
|
||||
.p-terms {
|
||||
list-style: none;
|
||||
}
|
||||
|
||||
.p-terms li {
|
||||
display: inline-block;
|
||||
}
|
||||
|
||||
.p-terms li::after {
|
||||
content: ',';
|
||||
}
|
||||
|
||||
.p-terms li:last-child::after {
|
||||
content: '';
|
||||
}
|
||||
|
||||
/* Parts:section */
|
||||
section {
|
||||
font-size: .8rem;
|
||||
}
|
||||
|
||||
section>header {
|
||||
margin-bottom: .5rem;
|
||||
font-weight: 500;
|
||||
}
|
||||
|
||||
section.bordered {
|
||||
border-top: 1px solid #eee;
|
||||
padding: 1rem 0;
|
||||
}
|
||||
|
||||
/* Parts:article */
|
||||
.p-articles {
|
||||
list-style: none;
|
||||
}
|
||||
|
||||
.p-articles>li {
|
||||
margin-bottom: 2.5rem;
|
||||
}
|
||||
|
||||
.p-articles.bordered>li {
|
||||
border-bottom: 1px solid #eee;
|
||||
margin-bottom: .5rem;
|
||||
}
|
||||
|
||||
.p-articles.bordered>li:last-child {
|
||||
border-bottom: none;
|
||||
}
|
||||
|
||||
article .title {
|
||||
margin: 0;
|
||||
margin-bottom: .5rem;
|
||||
}
|
||||
|
||||
article .thumb {
|
||||
display: block;
|
||||
background-position: center;
|
||||
background-size: cover;
|
||||
}
|
||||
|
||||
article>header {
|
||||
border-bottom: 1px solid #eee;
|
||||
margin-bottom: 1.5rem;
|
||||
}
|
||||
|
||||
article .summary {
|
||||
margin-bottom: .5rem;
|
||||
}
|
||||
|
||||
article.single .thumb {
|
||||
height: 18rem;
|
||||
}
|
||||
|
||||
@media (max-width: 768px) {
|
||||
article.single .thumb {
|
||||
height: 12rem;
|
||||
}
|
||||
}
|
||||
|
||||
article.li .thumb {
|
||||
float: right;
|
||||
width: 12rem;
|
||||
height: 7.5rem;
|
||||
margin-left: 1rem;
|
||||
margin-bottom: 1rem;
|
||||
}
|
||||
|
||||
article.li.sm>header {
|
||||
border-bottom: none;
|
||||
margin-bottom: 0;
|
||||
}
|
||||
|
||||
.article-body h2 {
|
||||
padding: 1rem 0;
|
||||
border-bottom: 2px solid #eceff1;
|
||||
}
|
||||
|
||||
.article-body h2:first-child { margin-top: 0; }
|
||||
|
||||
.article-body h3 {
|
||||
color: #428bca;
|
||||
}
|
||||
|
||||
.article-body h4 {
|
||||
border-left: solid .25rem #428bca;
|
||||
padding: 0 .5rem;
|
||||
}
|
||||
|
||||
.article-body p {
|
||||
margin: 1.5rem 0;
|
||||
line-height: 1.5rem;
|
||||
}
|
||||
|
||||
.article-body a {
|
||||
text-decoration: underline;
|
||||
}
|
||||
|
||||
.article-body ul,
|
||||
.article-body ol {
|
||||
padding-left: 1.5rem;
|
||||
}
|
||||
|
||||
.article-body code {
|
||||
display: inline-block;
|
||||
font-family: Menlo, consolas, monospace;
|
||||
font-size: .8rem;
|
||||
padding: 0 .5rem;
|
||||
line-height: 1.5rem;
|
||||
}
|
||||
|
||||
.article-body pre {
|
||||
margin: 1.5rem 0;
|
||||
padding: 0;
|
||||
font-size: .8rem;
|
||||
border: none;
|
||||
border-radius: 0;
|
||||
}
|
||||
|
||||
.article-body pre code {
|
||||
display: block;
|
||||
line-height: 1rem;
|
||||
padding: 1rem;
|
||||
}
|
||||
|
||||
.article-body blockquote {
|
||||
margin: 1.5rem 0;
|
||||
padding: .5rem 0;
|
||||
font-size: .8rem;
|
||||
border-top: 1px solid #eceff1;
|
||||
border-bottom: 1px solid #eceff1;
|
||||
color: #607d8b;
|
||||
}
|
||||
|
||||
.article-body blockquote p {
|
||||
margin: .5rem 0;
|
||||
line-height: 1rem;
|
||||
}
|
||||
|
||||
.article-body strong {
|
||||
box-shadow: 0 -.5rem 0 0 #5bc0de inset;
|
||||
}
|
||||
|
||||
.article-body em {
|
||||
font-style: normal;
|
||||
font-weight: 700;
|
||||
color: #428bca;
|
||||
}
|
||||
|
||||
.article-body figure { margin: 1.5rem 0; }
|
||||
.article-body figure.left,
|
||||
.article-body figure.right {
|
||||
width: 15rem;
|
||||
height: 12rem;
|
||||
margin-top: 0;
|
||||
}
|
||||
.article-body figure.left { float: left; margin-right: 1rem; }
|
||||
.article-body figure.right { float: right; margin-left: 1rem; }
|
||||
|
||||
@media (max-width: 768px) {
|
||||
.article-body figure.left,
|
||||
.article-body figure.right {
|
||||
float: none;
|
||||
margin: 0;
|
||||
width: auto;
|
||||
height: auto;
|
||||
}
|
||||
}
|
||||
|
||||
.article-body figcaption {
|
||||
padding: .5rem 0;
|
||||
font-size: .8rem;
|
||||
text-align: center;
|
||||
}
|
||||
|
||||
.article-body figcaption a {
|
||||
color: #263238;
|
||||
}
|
||||
|
||||
|
||||

|
After Width: | Height: | Size: 22 KiB |

|
After Width: | Height: | Size: 44 KiB |

|
After Width: | Height: | Size: 22 KiB |

|
After Width: | Height: | Size: 7.0 KiB |

|
After Width: | Height: | Size: 10 KiB |

|
After Width: | Height: | Size: 8.9 KiB |

|
After Width: | Height: | Size: 46 KiB |

|
After Width: | Height: | Size: 28 KiB |

|
After Width: | Height: | Size: 50 KiB |

|
After Width: | Height: | Size: 54 KiB |

|
After Width: | Height: | Size: 43 KiB |
@@ -0,0 +1,419 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/first/">手册前言(使用必读)</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY使用必读 手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" title="手册前言(使用必读)">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial/">GOPROXY免费版VS商业版</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" title="GOPROXY免费版VS商业版">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:29:13JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/">常见问题解答</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">问:http代理支持https网站吗? 答:goproxy的http代理同时支持http和https网站。 问:socks5代理支持UDP吗? 答</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" title="常见问题解答">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T17:54:31JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">在windows下实现基于dns的自动全局代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" title="在windows下实现基于dns的自动全局代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/tcp/">TCP代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" title="TCP代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:37:30JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/cloudflare/">Cloudflare使用简明教程</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" title="Cloudflare使用简明教程">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:02:57JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/">内网穿透也能用CDN???!</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" title="内网穿透也能用CDN???!">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">GOPROXY Free Version VS Commercial Version</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" title="GOPROXY Free Version VS Commercial Version">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">代理之套用CDN</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" title="代理之套用CDN">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
<nav>
|
||||
<ul class="pager">
|
||||
|
||||
|
||||
<li class="disabled"><a href="#">Previous</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/page/2/">Next</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
</nav>
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,123 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/</link>
|
||||
<description>Recent content on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>手册前言(使用必读)</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/first/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/first/</guid>
|
||||
<description>前言 GOPROXY使用必读 手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>GOPROXY免费版VS商业版</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial/</guid>
|
||||
<description>目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>常见问题解答</title>
|
||||
<link>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:29:13 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</guid>
|
||||
<description>问:http代理支持https网站吗? 答:goproxy的http代理同时支持http和https网站。 问:socks5代理支持UDP吗? 答</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>在windows下实现基于dns的自动全局代理</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 17:54:31 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</guid>
|
||||
<description>在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>TCP代理</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/tcp/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/tcp/</guid>
|
||||
<description>工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Cloudflare使用简明教程</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/cloudflare/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:37:30 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/cloudflare/</guid>
|
||||
<description>前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>内网穿透也能用CDN???!</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http-nat-cdn/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:02:57 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http-nat-cdn/</guid>
|
||||
<description>内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>GOPROXY Free Version VS Commercial Version</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</guid>
|
||||
<description>Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>代理之套用CDN</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http_cdn_ws/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:25:06 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http_cdn_ws/</guid>
|
||||
<description>goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Categories</title>
|
||||
<link>https://snail.gitee.io/proxy/page/categories/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/categories/</guid>
|
||||
<description>不用看这里,没什么内容,仅仅为了定义目录和tags。</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>About</title>
|
||||
<link>https://snail.gitee.io/proxy/page/about/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 13:22:19 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/about/</guid>
|
||||
<description>It&rsquo;s YOU!</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1,23 @@
|
||||
|
||||
<!DOCTYPE html>
|
||||
<html lang="en">
|
||||
<head>
|
||||
<meta charset="UTF-8">
|
||||
<title>GOPROXY Manual</title>
|
||||
<meta name="description" content="GOPROXY Manual,GOPROXY 帮助手册">
|
||||
<meta name="viewport" content="width=device-width, user-scalable=no, initial-scale=1.0, maximum-scale=1.0, minimum-scale=1.0">
|
||||
<style>*{-webkit-font-smoothing:antialiased;-webkit-overflow-scrolling:touch;-webkit-tap-highlight-color:rgba(0,0,0,0);-webkit-text-size-adjust:none;-webkit-touch-callout:none;box-sizing:border-box}body:not(.ready){overflow:hidden}body:not(.ready) .app-nav,body:not(.ready)>nav,body:not(.ready) [data-cloak]{display:none}div#app{font-size:30px;font-weight:lighter;margin:40vh auto;text-align:center}div#app:empty:before{content:"Loading..."}.emoji{height:19.2px;height:1.2rem;vertical-align:middle}.progress{background-color:#42b983;background-color:var(--theme-color,#42b983);height:2px;left:0;position:fixed;right:0;top:0;transition:width .2s,opacity .4s;width:0;z-index:5}.search .search-keyword,.search a:hover{color:#42b983;color:var(--theme-color,#42b983)}.search .search-keyword{font-style:normal;font-weight:700}body,html{height:100%}body{-moz-osx-font-smoothing:grayscale;-webkit-font-smoothing:antialiased;color:#34495e;font-family:Source Sans Pro,Helvetica Neue,Arial,sans-serif;font-size:15px;letter-spacing:0;margin:0;overflow-x:hidden}img{max-width:100%}a[disabled]{cursor:not-allowed;opacity:.6}kbd{border:1px solid #ccc;border-radius:3px;display:inline-block;font-size:12px!important;line-height:12px;margin-bottom:3px;padding:3px 5px;vertical-align:middle}.task-list-item{list-style-type:none}li input[type=checkbox]{margin:0 .2em .25em -1.6em;vertical-align:middle}.app-nav{left:0;margin:25px 60px 0 0;position:absolute;right:0;text-align:right;z-index:2}.app-nav p{margin:0}.app-nav>a{margin:0 16px;margin:0 1rem;padding:5px 0}.app-nav li,.app-nav ul{display:inline-block;list-style:none;margin:0}.app-nav a{color:inherit;font-size:16px;text-decoration:none;transition:color .3s}.app-nav a.active,.app-nav a:hover{color:#42b983;color:var(--theme-color,#42b983)}.app-nav a.active{border-bottom:2px solid #42b983;border-bottom:2px solid var(--theme-color,#42b983)}.app-nav li{display:inline-block;margin:0 16px;margin:0 1rem;padding:5px 0;position:relative}.app-nav li ul{background-color:#fff;border:1px solid #ddd;border-bottom-color:#ccc;border-radius:4px;box-sizing:border-box;display:none;max-height:calc(100vh - 61px);overflow-y:scroll;padding:10px 0;position:absolute;right:-15px;text-align:left;top:100%;white-space:nowrap}.app-nav li ul li{display:block;font-size:14px;line-height:16px;line-height:1rem;margin:0;margin:8px 14px;white-space:nowrap}.app-nav li ul a{display:block;font-size:inherit;margin:0;padding:0}.app-nav li ul a.active{border-bottom:0}.app-nav li:hover ul{display:block}.app-nav.no-badge{margin-right:25px}.github-corner{border-bottom:0;position:fixed;right:0;text-decoration:none;top:0;z-index:1}.github-corner svg{color:#fff;fill:#42b983;fill:var(--theme-color,#42b983);height:80px;width:80px}.github-corner:hover .octo-arm{-webkit-animation:a .56s ease-in-out;animation:a .56s ease-in-out}main{display:block;position:relative;width:100vw;height:100%;z-index:0}.anchor{display:inline-block;text-decoration:none;transition:all .3s}.anchor span{color:#34495e}.anchor:hover{text-decoration:underline}.sidebar{border-right:1px solid rgba(0,0,0,.07);overflow-y:auto;padding:40px 0 0;top:0;bottom:0;left:0;position:absolute;transition:-webkit-transform .25s ease-out;transition:transform .25s ease-out;transition:transform .25s ease-out,-webkit-transform .25s ease-out;width:300px;z-index:3}.sidebar>h1{margin:0 auto 16px;margin:0 auto 1rem;font-size:24px;font-size:1.5rem;font-weight:300;text-align:center}.sidebar>h1 a{color:inherit;text-decoration:none}.sidebar>h1 .app-nav{display:block;position:static}.sidebar .sidebar-nav{line-height:2em;padding-bottom:40px}.sidebar ul{margin:0;padding:0}.sidebar li>p{font-weight:700;margin:0}.sidebar ul,.sidebar ul li{list-style:none}.sidebar ul li a{border-bottom:none;display:block}.sidebar ul li ul{padding-left:20px}.sidebar::-webkit-scrollbar{width:4px}.sidebar::-webkit-scrollbar-thumb{background:transparent;border-radius:4px}.sidebar:hover::-webkit-scrollbar-thumb{background:hsla(0,0%,53%,.4)}.sidebar:hover::-webkit-scrollbar-track{background:hsla(0,0%,53%,.1)}.sidebar-toggle{background-color:transparent;background-color:hsla(0,0%,100%,.8);border:0;outline:none;padding:10px;bottom:0;left:0;position:absolute;text-align:center;transition:opacity .3s;width:30px;width:284px;z-index:4}.sidebar-toggle .sidebar-toggle-button:hover{opacity:.4}.sidebar-toggle span{background-color:#42b983;background-color:var(--theme-color,#42b983);display:block;margin-bottom:4px;width:16px;height:2px}body.sticky .sidebar,body.sticky .sidebar-toggle{position:fixed}.content{padding-top:60px;top:0;right:0;bottom:0;left:300px;position:absolute;transition:left .25s ease}.markdown-section{margin:0 auto;max-width:800px;padding:30px 15px 40px;position:relative}.markdown-section>*{box-sizing:border-box;font-size:inherit}.markdown-section>:first-child{margin-top:0!important}.markdown-section hr{border:none;border-bottom:1px solid #eee;margin:2em 0}.markdown-section table{border-collapse:collapse;border-spacing:0;display:block;margin-bottom:16px;margin-bottom:1rem;overflow:auto;width:100%}.markdown-section th{font-weight:700}.markdown-section td,.markdown-section th{border:1px solid #ddd;padding:6px 13px}.markdown-section tr{border-top:1px solid #ccc}.markdown-section p.tip,.markdown-section tr:nth-child(2n){background-color:#f8f8f8}.markdown-section p.tip{border-bottom-right-radius:2px;border-left:4px solid #f66;border-top-right-radius:2px;margin:2em 0;padding:12px 24px 12px 30px;position:relative}.markdown-section p.tip code{background-color:#efefef}.markdown-section p.tip em{color:#34495e}.markdown-section p.tip:before{background-color:#f66;border-radius:100%;color:#fff;content:"!";font-family:Dosis,Source Sans Pro,Helvetica Neue,Arial,sans-serif;font-size:14px;font-weight:700;left:-12px;line-height:20px;position:absolute;width:20px;height:20px;text-align:center;top:14px}.markdown-section p.warn{background:rgba(66,185,131,.1);border-radius:2px;padding:16px;padding:1rem}body.close .sidebar{-webkit-transform:translateX(-300px);transform:translateX(-300px)}body.close .sidebar-toggle{width:auto}body.close .content{left:0}@media print{.app-nav,.github-corner,.sidebar,.sidebar-toggle{display:none}}@media screen and (max-width:768px){.github-corner,.sidebar,.sidebar-toggle{position:fixed}.app-nav{margin-top:16px}.app-nav li ul{top:30px}main{height:auto;overflow-x:hidden}.sidebar{left:-300px;transition:-webkit-transform .25s ease-out;transition:transform .25s ease-out;transition:transform .25s ease-out,-webkit-transform .25s ease-out}.content{left:0;max-width:100vw;position:static;padding-top:20px;transition:-webkit-transform .25s ease;transition:transform .25s ease;transition:transform .25s ease,-webkit-transform .25s ease}.app-nav,.github-corner{transition:-webkit-transform .25s ease-out;transition:transform .25s ease-out;transition:transform .25s ease-out,-webkit-transform .25s ease-out}.sidebar-toggle{background-color:transparent;width:auto;padding:30px 30px 10px 10px}body.close .sidebar{-webkit-transform:translateX(300px);transform:translateX(300px)}body.close .sidebar-toggle{background-color:hsla(0,0%,100%,.8);transition:background-color 1s;width:284px;padding:10px}body.close .content{-webkit-transform:translateX(300px);transform:translateX(300px)}body.close .app-nav,body.close .github-corner{display:none}.github-corner .octo-arm{-webkit-animation:a .56s ease-in-out;animation:a .56s ease-in-out}.github-corner:hover .octo-arm{-webkit-animation:none;animation:none}}@-webkit-keyframes a{0%,to{-webkit-transform:rotate(0);transform:rotate(0)}20%,60%{-webkit-transform:rotate(-25deg);transform:rotate(-25deg)}40%,80%{-webkit-transform:rotate(10deg);transform:rotate(10deg)}}@keyframes a{0%,to{-webkit-transform:rotate(0);transform:rotate(0)}20%,60%{-webkit-transform:rotate(-25deg);transform:rotate(-25deg)}40%,80%{-webkit-transform:rotate(10deg);transform:rotate(10deg)}}section.cover{-webkit-box-align:center;-ms-flex-align:center;align-items:center;background-position:50%;background-repeat:no-repeat;background-size:cover;height:100vh;display:none}section.cover .cover-main{-webkit-box-flex:1;-ms-flex:1;flex:1;margin:-20px 16px 0;text-align:center;z-index:1}section.cover a{color:inherit}section.cover a,section.cover a:hover{text-decoration:none}section.cover p{line-height:24px;line-height:1.5rem;margin:1em 0}section.cover h1{color:inherit;font-size:40px;font-size:2.5rem;font-weight:300;margin:10px 0 40px;margin:.625rem 0 2.5rem;position:relative;text-align:center}section.cover h1 a{display:block}section.cover h1 small{bottom:-7px;bottom:-.4375rem;font-size:16px;font-size:1rem;position:absolute}section.cover blockquote{font-size:24px;font-size:1.5rem;text-align:center}section.cover ul{line-height:1.8;list-style-type:none;margin:1em auto;max-width:500px;padding:0}section.cover .cover-main>p:last-child a{border-color:#42b983;border:1px solid var(--theme-color,#42b983);border-radius:2rem;box-sizing:border-box;color:#42b983;color:var(--theme-color,#42b983);display:inline-block;font-size:16.8px;font-size:1.05rem;letter-spacing:1.6px;letter-spacing:.1rem;margin-right:16px;margin-right:1rem;padding:.75em 32px;padding:.75em 2rem;text-decoration:none;transition:all .15s ease}section.cover .cover-main>p:last-child a:last-child{background-color:#42b983;background-color:var(--theme-color,#42b983);color:#fff;margin-right:0}section.cover .cover-main>p:last-child a:last-child:hover{color:inherit;opacity:.8}section.cover .cover-main>p:last-child a:hover{color:inherit}section.cover blockquote>p>a{border-bottom:2px solid #42b983;border-bottom:2px solid var(--theme-color,#42b983);transition:color .3s}section.cover blockquote>p>a:hover{color:#42b983;color:var(--theme-color,#42b983)}section.cover.show{display:-webkit-box;display:-ms-flexbox;display:flex}section.cover.has-mask .mask{background-color:#fff;opacity:.8;position:absolute;top:0;width:100%;height:100%}.sidebar,body{background-color:#fff}.sidebar{color:#364149}.sidebar li{margin:6px 0 6px 15px}.sidebar ul li a{color:#505d6b;font-size:14px;font-weight:400;overflow:hidden;text-decoration:none;text-overflow:ellipsis;white-space:nowrap}.sidebar ul li a:hover{text-decoration:underline}.sidebar ul li ul{padding:0}.sidebar ul li.active>a{border-right:2px solid;color:#42b983;color:var(--theme-color,#42b983);font-weight:600}.app-sub-sidebar li:before{content:"-";padding-right:4px;float:left}.markdown-section h1,.markdown-section h2,.markdown-section h3,.markdown-section h4,.markdown-section strong{color:#2c3e50;font-weight:600}.markdown-section a{color:#42b983;color:var(--theme-color,#42b983);font-weight:600}.markdown-section h1{font-size:32px;font-size:2rem;margin:0 0 16px;margin:0 0 1rem}.markdown-section h2{font-size:28px;font-size:1.75rem;margin:45px 0 12.8px;margin:45px 0 .8rem}.markdown-section h3{font-size:24px;font-size:1.5rem;margin:40px 0 9.6px;margin:40px 0 .6rem}.markdown-section h4{font-size:20px;font-size:1.25rem}.markdown-section h5,.markdown-section h6{font-size:16px;font-size:1rem}.markdown-section h6{color:#777}.markdown-section figure,.markdown-section p{margin:1.2em 0}.markdown-section ol,.markdown-section p,.markdown-section ul{line-height:25.6px;line-height:1.6rem;word-spacing:.8px;word-spacing:.05rem}.markdown-section ol,.markdown-section ul{padding-left:24px;padding-left:1.5rem}.markdown-section blockquote{border-left:4px solid #42b983;border-left:4px solid var(--theme-color,#42b983);color:#858585;margin:2em 0;padding-left:20px}.markdown-section blockquote p{font-weight:600;margin-left:0}.markdown-section iframe{margin:1em 0}.markdown-section em{color:#7f8c8d}.markdown-section code{border-radius:2px;color:#e96900;font-size:12.8px;font-size:.8rem;margin:0 2px;padding:3px 5px;white-space:pre-wrap}.markdown-section code,.markdown-section pre{background-color:#f8f8f8;font-family:Roboto Mono,Monaco,courier,monospace}.markdown-section pre{-moz-osx-font-smoothing:initial;-webkit-font-smoothing:initial;line-height:24px;line-height:1.5rem;margin:1.2em 0;overflow:auto;padding:0 22.4px;padding:0 1.4rem;position:relative;word-wrap:normal}.token.cdata,.token.comment,.token.doctype,.token.prolog{color:#8e908c}.token.namespace{opacity:.7}.token.boolean,.token.number{color:#c76b29}.token.punctuation{color:#525252}.token.property{color:#c08b30}.token.tag{color:#2973b7}.token.string{color:#42b983;color:var(--theme-color,#42b983)}.token.selector{color:#6679cc}.token.attr-name{color:#2973b7}.language-css .token.string,.style .token.string,.token.entity,.token.url{color:#22a2c9}.token.attr-value,.token.control,.token.directive,.token.unit{color:#42b983;color:var(--theme-color,#42b983)}.token.keyword{color:#e96900}.token.atrule,.token.regex,.token.statement{color:#22a2c9}.token.placeholder,.token.variable{color:#3d8fd1}.token.deleted{text-decoration:line-through}.token.inserted{border-bottom:1px dotted #202746;text-decoration:none}.token.italic{font-style:italic}.token.bold,.token.important{font-weight:700}.token.important{color:#c94922}.token.entity{cursor:help}.markdown-section pre>code{-moz-osx-font-smoothing:initial;-webkit-font-smoothing:initial;background-color:#f8f8f8;border-radius:2px;color:#525252;display:block;font-family:Roboto Mono,Monaco,courier,monospace;font-size:12.8px;font-size:.8rem;line-height:inherit;margin:0 2px;max-width:inherit;overflow:inherit;padding:2.2em 5px;white-space:inherit}.markdown-section code:after,.markdown-section code:before{letter-spacing:.8px;letter-spacing:.05rem}code .token{-moz-osx-font-smoothing:initial;-webkit-font-smoothing:initial;min-height:24px;min-height:1.5rem}pre:after{color:#ccc;content:attr(data-lang);font-size:9.6px;font-size:.6rem;font-weight:600;height:15px;line-height:15px;padding:5px 10px 0;position:absolute;right:0;text-align:right;top:0}</style>
|
||||
</head>
|
||||
<body>
|
||||
<div id="app">loading……</div>
|
||||
</body>
|
||||
<script>
|
||||
window.$docsify = {
|
||||
name: 'GOPROXY',
|
||||
maxLevel: 2,
|
||||
repo: 'snail007/goproxy',
|
||||
homepage:"manual.md",
|
||||
}
|
||||
</script>
|
||||
<script src="https://cdnjs.cloudflare.com/ajax/libs/docsify/4.9.1/docsify.min.js"></script>
|
||||
</html>
|
||||
@@ -0,0 +1,1864 @@
|
||||
## How to Install
|
||||
|
||||
### 1. Linux Install
|
||||
|
||||
[click me get Linux installation](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E4%B8%8B%E8%BD%BD%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
### 2. MacOS Install
|
||||
|
||||
[click me get MacOS installation](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
### 3. Windows Install
|
||||
|
||||
[click me get Windows installation](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
### 4. Others Install
|
||||
|
||||
[click me get Windows installation](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E6%89%8B%E5%8A%A8%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
## Purchase Commercial Edition
|
||||
|
||||
This manual describes the functions, all of which are included in the commercial version; the free version of advanced functional parameters such as authentication is not included;
|
||||
If you encounter some commands when you use the free version to execute some commands, a prompt similar to the following xxx parameter does not exist, indicating that this parameter is a function of the commercial version.
|
||||
`err: unknown long flag '-a'`
|
||||
Comparison between the features of the free version and the commercial version, detailed operations on how to purchase and use the commercial version [please click here to view](https://snail.gitee.io/proxy/page/free_vs_commercial_en/)
|
||||
|
||||
## First Start
|
||||
|
||||
### 1. Environment
|
||||
|
||||
The manual tutorial, the default system is linux, the program is proxy; all operations require root privileges;
|
||||
|
||||
If you are windows, please use the windows version of proxy.exe.
|
||||
|
||||
### 2. Using configuration files
|
||||
|
||||
The next tutorial will introduce the usage method through the command line parameters, or you can get the parameters by reading the configuration file.
|
||||
|
||||
The specific format is to specify the configuration file by the @ symbol, for example: proxy @configfile.txt
|
||||
|
||||
The format in configfile.txt is that the first line is the name of the subcommand, and the second line starts with one parameter per line.
|
||||
|
||||
Format: `parameter Parameter value`, direct write parameter without parameter value, for example: --nolog
|
||||
|
||||
For example, the contents of configfile.txt are as follows:
|
||||
|
||||
```shell
|
||||
Http
|
||||
-t tcp
|
||||
-p :33080
|
||||
--forever
|
||||
```
|
||||
|
||||
### 3. Debug output
|
||||
|
||||
By default, the information output by the log does not include the number of file lines. In some cases, in order to troubleshoot the program, the problem is quickly located.
|
||||
|
||||
You can use the --debug parameter to output the number of lines of code and milliseconds.
|
||||
|
||||
### 4. Using log files
|
||||
|
||||
By default, the log is displayed directly in the console. If you want to save to a file, you can use the --log parameter.
|
||||
|
||||
For example: --log proxy.log, the log will be output to the proxy.log to facilitate troubleshooting.
|
||||
|
||||
|
||||
### 5. Generate the certificate file required for encrypted communication
|
||||
|
||||
The http, tcp, udp proxy process communicates with the upstream. For security, we use encrypted communication. Of course, we can choose not to encrypt the communication. All the communication and the upstream communication in this tutorial are encrypted, and the certificate file is required.
|
||||
|
||||
1. Generate a self-signed certificate and key file with the following command.
|
||||
`proxy keygen -C proxy`
|
||||
The certificate file proxy.crt and the key file proxy.key will be generated under the current program directory.
|
||||
|
||||
2. Use the following command to generate a new certificate using the self-signed certificate proxy.crt and the key file proxy.key: goproxy.crt and goproxy.key.
|
||||
`proxy keygen -s -C proxy -c goproxy`
|
||||
The certificate file goproxy.crt and the key file goproxy.key will be generated under the current program directory.
|
||||
|
||||
3. By default, the domain name inside the certificate is random and can be specified using the `-n test.com` parameter.
|
||||
|
||||
4. More usage: `proxy keygen --help`.
|
||||
|
||||
### 6. Running in the background
|
||||
|
||||
After the proxy is executed by default, you cannot close the command line if you want to keep the proxy running.
|
||||
|
||||
If you want to run the proxy in the background, the command line can be closed, just add the --daemon parameter at the end of the command.
|
||||
|
||||
For example:
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080" --daemon`
|
||||
|
||||
### 7. Guardian running
|
||||
The daemon runs the parameter --forever, for example: `proxy http --forever` ,
|
||||
|
||||
The proxy will fork the child process, and then monitor the child process. If the child process exits abnormally, restart the child process after 5 seconds.
|
||||
|
||||
This parameter is matched with the background running parameter --daemon and log parameter --log, which can guarantee that the proxy will always execute in the background without accidentally exiting.
|
||||
|
||||
And you can see the output log content of the proxy through the log file.
|
||||
|
||||
For example: `proxy http -p ":9090" --forever --log proxy.log --daemon`
|
||||
|
||||
### 8. Security advice
|
||||
|
||||
When the VPS is behind the nat device, the vps network card IP is the intranet IP. At this time, you can use the -g parameter to add the vps external network ip to prevent the infinite loop.
|
||||
|
||||
Suppose your vps external network ip is 23.23.23.23. The following command sets 23.23.23.23 with the -g parameter.
|
||||
|
||||
`proxy http -g "23.23.23.23"`
|
||||
|
||||
### 9. Load balancing and high availability
|
||||
|
||||
The HTTP(S)\SOCKS5\SPS proxy supports upper-level load balancing and high availability, and multiple upstream repeat-P parameters can be used.
|
||||
|
||||
The load balancing policy supports five types, which can be specified by the `--lb-method` parameter:
|
||||
|
||||
Roundrobin used in turn
|
||||
|
||||
Leastconn uses the minimum number of connections
|
||||
|
||||
Leasttime uses the least connection time
|
||||
|
||||
Hash uses a fixed upstream based on the client address
|
||||
|
||||
Weight Select a upstream according to the weight and number of connections of each upstream
|
||||
|
||||
prompt:
|
||||
|
||||
1. The load balancing check interval can be set by `--lb-retrytime` in milliseconds.
|
||||
|
||||
2. The load balancing connection timeout can be set by `--lb-timeout` in milliseconds.
|
||||
|
||||
3. If the load balancing policy is weight, the -P format is: 2.2.2.2: 3880?w=1, where 1 is the weight and an integer greater than 0.
|
||||
|
||||
4. If the load balancing policy is hash, the default is to select the upstream based on the client address. You can select the upstream by using the destination address of the access `--lb-hashtarget`.
|
||||
|
||||
5. The TCP proxies has no parameter `--lb-hashtarget`.
|
||||
|
||||
6. Default is load balancing + high availability mode. If the parameter `--lb-onlyha` is used, only the high availability mode is used, then a node is selected according to the load balancing strategy, and this node will be used until it is not alive, then another node will be selected for using, thus cycling.
|
||||
|
||||
7. If the all nodes are not alive, a random node will be selected for using.
|
||||
|
||||
### 10. Agent springboard jump
|
||||
|
||||
Http (s) agent, SPS agent, intranet penetration, tcp agent support the connection of upstreams through intermediate third-party agents,
|
||||
|
||||
The parameters are: --jumper, all the formats are as follows:
|
||||
|
||||
```text
|
||||
http://username:password@host:port
|
||||
http://host:port
|
||||
https://username:password@host:port
|
||||
https://host:port
|
||||
socks5://username:password@host:port
|
||||
socks5://host:port
|
||||
socks5s://username:password@host:port
|
||||
socks5s://host:port
|
||||
ss://method:password@host:port
|
||||
```
|
||||
|
||||
Http,socks5 represents the normal http and socks5 proxy.
|
||||
|
||||
Https,socks5s represents the http and socks5 agents protected by tls.
|
||||
|
||||
That is http proxy over TLS, socks over TLS.
|
||||
|
||||
### 11. Domain Name Black and White List
|
||||
|
||||
The socks/http(s)/sps proxy supports domain name black and white lists.
|
||||
|
||||
Use the --stop parameter to specify a domain name blacklist file, then the connection will be disconnected when the user connects these domains in the file.
|
||||
|
||||
Specify a domain name whitelist file with the --only parameter, then the connection will be disconnected when the user connects to a domain other than those domains in the file.
|
||||
|
||||
If both --stop and --only are set, then only --only will work.
|
||||
|
||||
The format of the black and white domain name list file is as follows:
|
||||
|
||||
```text
|
||||
**.baidu.com
|
||||
*.taobao.com
|
||||
A.com
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
?.qq.com
|
||||
```
|
||||
|
||||
Description:
|
||||
|
||||
1. One domain name per line, domain name writing supports wildcards `*` and `?`, `*` represents any number of characters, `?` represents an arbitrary character,
|
||||
|
||||
2.`**.baidu.com` Matches no matter how many levels all suffixes are ..baidu.com`.
|
||||
|
||||
3.`*.taobao.com` The matching suffix is the third-level domain name of `.taobao.com`.
|
||||
|
||||
4. It can also be an IP address directly.
|
||||
|
||||
5.`#` at the beginning of the comment.
|
||||
|
||||
### 12. Client IP Blacklist and Whitelist
|
||||
|
||||
socks/http(s)/sps/tcp/udp/dns/ intranet penetration bridge/intranet penetration tbridge, support client IP black and white list.
|
||||
|
||||
Use the --ip-deny parameter to specify a client IP blacklist list file, then the connection will be disconnected when the user's IP is in this file.
|
||||
|
||||
Use the --ip-allow parameter to specify a client IP whitelist file, then the connection will be disconnected when the user's IP is not in the file.
|
||||
|
||||
If both --ip-deny and --ip-allow are set, then only --ip-allow will work.
|
||||
|
||||
The format of the client IP blacklist and whitelist file is as follows:
|
||||
|
||||
```text
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
192.168.1?.*
|
||||
```
|
||||
|
||||
Description:
|
||||
|
||||
1. One domain name per domain, domain name writing supports wildcards `*` and `?`, `*` represents any number of characters, `?` represents an arbitrary character.
|
||||
|
||||
2.`#` at the beginning of the comment.
|
||||
|
||||
### 13. Protocol loading file
|
||||
|
||||
There are many places in the proxy's various proxy functions to set a file. For example: --blocked Specifies a domain name list file that goes directly to the upper level. The parameter value is the path of the file.
|
||||
|
||||
If the parameter supports the protocol loading file, the file path can be not only the file path, but also:
|
||||
|
||||
a. The base64 encoding at the beginning of "base64://" indicates the contents of the above file, for example: base64://ajfpoajsdfa=
|
||||
|
||||
b. "str://" at the beginning of the English comma separated multiple, such as: str://xxx, yyy
|
||||
|
||||
The proxy's blocked, direct, stop, only, hosts, resolve.rules, rewriter.rules, ip.allow, ip.deny files support protocol loading.
|
||||
|
||||
|
||||
### 14.Concurrent client connections
|
||||
|
||||
socks5\sps\http proxies, the parameter that controls the number of concurrent client connections is: `--max-conns-rate`, which controls the maximum number of client connections per second, default: 20, 0 is unlimited
|
||||
|
||||
### 15 Listen on multiple ports
|
||||
|
||||
"tcp / http / socks / sps" supports listen on multiple ports and range ports.
|
||||
Under normal circumstances, it is sufficient to listen on one port, but if you need to listen on multiple ports, the -p parameter is supported.
|
||||
The format is: `-p 0.0.0.0:80,0.0.0.0:443,.0.0.0.0:8000-9000,:5000-6000`, more The bindings can be separated by commas.
|
||||
|
||||
## 1.HTTP Proxies
|
||||
|
||||
### 1.1. Ordinary level HTTP proxy
|
||||
|
||||
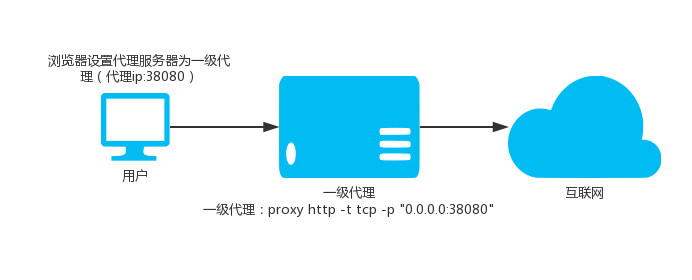
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080"`
|
||||
|
||||
Listen port argument `-p` can be:
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000 and 9001 to 9999, 1002 total ports
|
||||
```
|
||||
|
||||
### 1.2. Ordinary secondary HTTP proxy
|
||||
|
||||
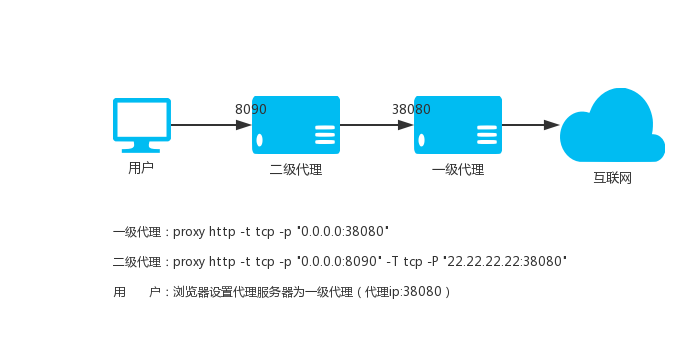
|
||||
|
||||
Use local port 8090, assuming the upstream HTTP proxy is `22.22.22.22:8080`
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" `
|
||||
|
||||
We can also specify the black and white list file of the website domain name, one domain name per line, the matching rule is the rightmost match, for example: baidu.com, the match is *.*.baidu.com, the blacklist domain name goes directly to the upstream agent, whitelist The domain name does not go to the upstream agent.
|
||||
|
||||
`proxy http -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt`
|
||||
|
||||
### 1.3.HTTP secondary agent (encryption)
|
||||
|
||||
> Note: The `proxy.crt` and `proxy.key` used by the secondary proxy should be consistent with the primary proxy.
|
||||
|
||||
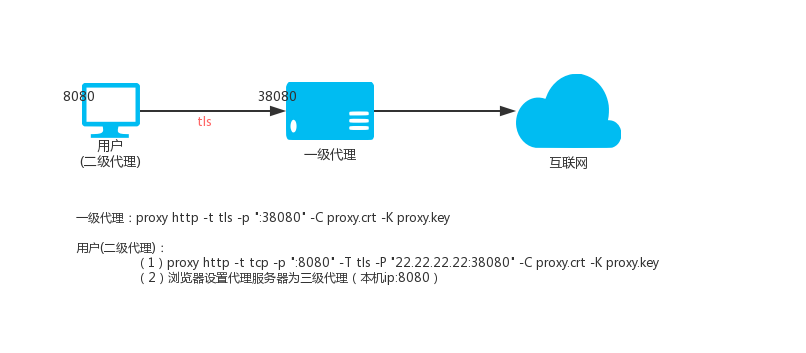
|
||||
Level 1 HTTP proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Secondary HTTP proxy (local Linux)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS.
|
||||
|
||||
Secondary HTTP proxy (local windows)
|
||||
`proxy.exe http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then set your windos system, the proxy that needs to go through the proxy Internet program is http mode, the address is: 127.0.0.1, the port is: 8080, the program can access the Internet through vps through the encrypted channel.
|
||||
|
||||
### 1.4.HTTP Level 3 Agent (Encryption)
|
||||
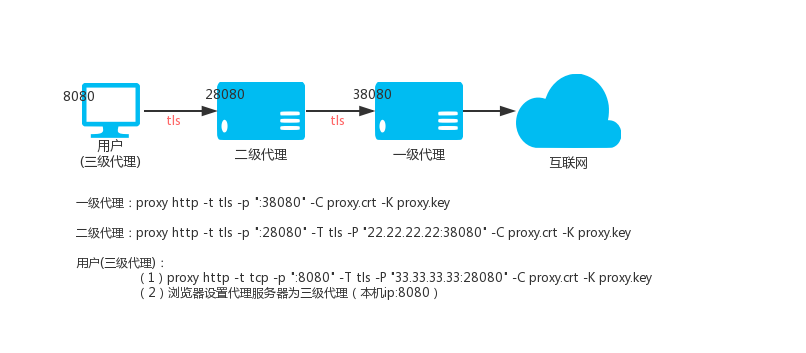
|
||||
Level 1 HTTP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
Secondary HTTP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy http -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 HTTP proxy (local)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then accessing the local port 8080 is to access the proxy port 38080 on the primary HTTP proxy.
|
||||
|
||||
### 1.5.Basic certification
|
||||
For the proxy HTTP protocol, we can perform Basic authentication. The authenticated username and password can be specified on the command line.
|
||||
`proxy http -t tcp -p ":33080" -a "user1:pass1" -a "user2:pass2"`
|
||||
For multiple users, repeat the -a parameter.
|
||||
It can also be placed in a file in the format of a "username:password" and then specified with -F.
|
||||
`proxy http -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
In addition, the http(s) proxy also integrates external HTTP API authentication. We can specify an http url interface address with the --auth-url parameter.
|
||||
Then when there is a user connection, the proxy will request the url in GET mode, and bring the following four parameters. If the HTTP status code 204 is returned, the authentication is successful.
|
||||
In other cases, the authentication failed.
|
||||
For example:
|
||||
`proxy http -t tcp -p ":33080" --auth-url "http://test.com/auth.php"`
|
||||
When the user connects, the proxy will request the url ("http://test.com/auth.php") in GET mode.
|
||||
Take five parameters: user, pass, ip, local_ip, target:
|
||||
Http://test.com/auth.php?user={USER}&pass={PASS}&ip={IP}&local_ip={LOCAL_IP}&target={TARGET}
|
||||
User: username
|
||||
Pass: password
|
||||
Ip: User's IP, for example: 192.168.1.200
|
||||
Local_ip: IP of the server accessed by the user, for example: 3.3.3.3
|
||||
Target: URL accessed by the user, for example: http://demo.com:80/1.html or https://www.baidu.com:80
|
||||
|
||||
If there is no -a or -F or --auth-url parameter, the Basic authentication is turned off.
|
||||
|
||||
### 1.6. HTTP proxy traffic is forced to go to the upper HTTP proxy
|
||||
By default, the proxy will intelligently determine whether a website domain name is inaccessible. If it is not accessible, it will go to the upper level HTTP proxy. With --always, all HTTP proxy traffic can be forced to go to the upper HTTP proxy.
|
||||
`proxy http --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
### 1.7.HTTP(S) via SSH relay
|
||||
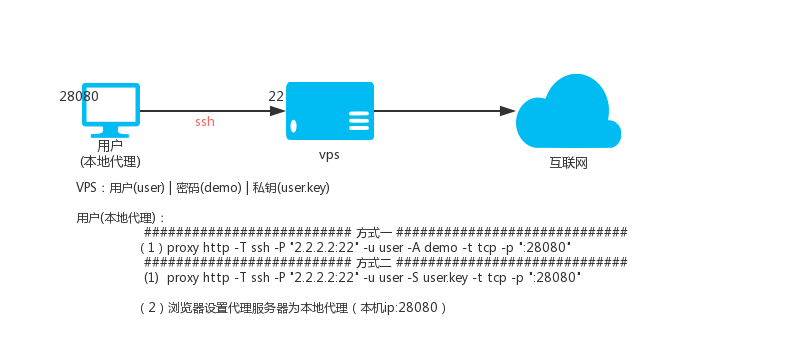
|
||||
Description: The principle of ssh transfer is to use the forwarding function of ssh, that is, after you connect to ssh, you can access the target address through ssh proxy.
|
||||
Suppose there is: vps
|
||||
- IP is 2.2.2.2, ssh port is 22, ssh username is: user, ssh user password is: demo
|
||||
- The user's ssh private key name is user.key
|
||||
|
||||
#### *1.7.1 How to ssh username and password*
|
||||
Local HTTP(S) proxy port 28080, executing:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080"`
|
||||
#### *1.7.2 How to ssh username and key*
|
||||
Local HTTP(S) proxy port 28080, executing:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080"`
|
||||
|
||||
### 1.8.KCP protocol transmission
|
||||
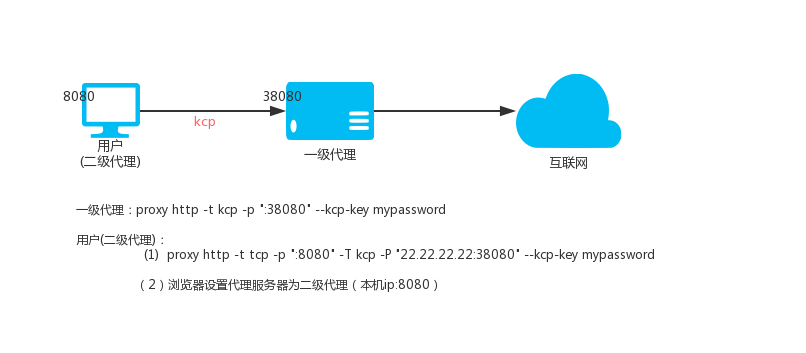
|
||||
The KCP protocol requires the --kcp-key parameter to set a password for encrypting and decrypting data.
|
||||
|
||||
Level 1 HTTP proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy http -t kcp -p ":38080" --kcp-key mypassword`
|
||||
|
||||
Secondary HTTP proxy (local Linux)
|
||||
`proxy http -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS, the data is transmitted through the kcp protocol, note that the kcp is the udp protocol, so the firewall needs to release the 380p udp protocol.
|
||||
|
||||
### 1.9 HTTP(S) Reverse Proxy
|
||||
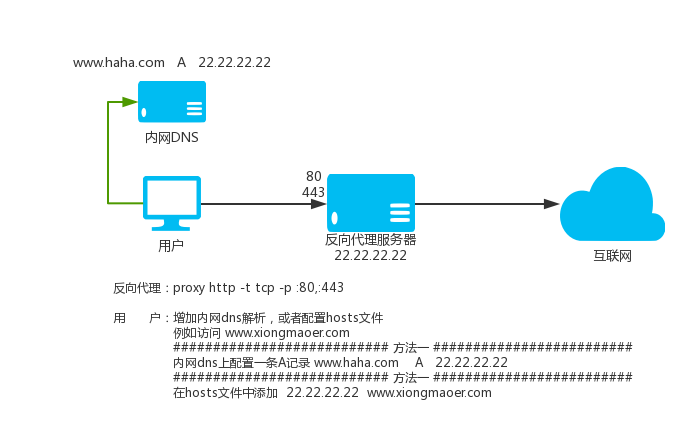
|
||||
The proxy not only supports the proxy setting in other software, but also provides proxy services for other software. It also supports directly parsing the requested website domain name to the proxy listening ip, and then the proxy listens to the 80 and 443 ports, then the proxy will automatically You proxy access to the HTTP(S) website you need to access.
|
||||
|
||||
How to use:
|
||||
On the "last level proxy proxy" machine, because the proxy is to be disguised as all websites, the default HTTP port of the website is 80, HTTPS is 443, and the proxy can listen to ports 80 and 443. Parameters -p multiple addresses with commas segmentation.
|
||||
`proxy http -t tcp -p :80,:443`
|
||||
|
||||
This command starts a proxy agent on the machine, and listens to ports 80 and 443 at the same time. It can be used as a normal proxy, or directly resolve the domain name that needs to be proxyed to the IP of this machine.
|
||||
|
||||
If there is a upstream agent, then refer to the above tutorial to set the upstream, the use is exactly the same.
|
||||
`proxy http -t tcp -p :80,:443 -T tls -P "2.2.2.2:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Note:
|
||||
The DNS resolution result of the server where the proxy is located cannot be affected by the custom resolution, otherwise it will be infinite loop. The proxy proxy should specify the `--dns 8.8.8.8` parameter.
|
||||
|
||||
### 1.10 HTTP(S) Transparent Proxy
|
||||
This mode needs to have a certain network foundation. If the related concepts are not understood, please search for it yourself.
|
||||
Assuming the proxy is now running on the router, the startup command is as follows:
|
||||
`proxy http -t tcp -p :33080 -T tls -P "2.2.2.2:33090" -C proxy.crt -K proxy.key`
|
||||
|
||||
Then add the iptables rule, here are the reference rules:
|
||||
```shell
|
||||
#Upper proxy server IP address:
|
||||
Proxy_server_ip=2.2.2.2
|
||||
|
||||
#路由器Running port for proxy listening:
|
||||
Proxy_local_port=33080
|
||||
|
||||
#The following does not need to be modified
|
||||
#create a new chain named PROXY
|
||||
Iptables -t nat -N PROXY
|
||||
|
||||
# Ignore your PROXY server's addresses
|
||||
# It's very IMPORTANT, just be careful.
|
||||
|
||||
Iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
# Ignore LANs IP address
|
||||
Iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
Iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
# Anything to port 80 443 should be redirected to PROXY's local port
|
||||
Iptables -t nat -A PROXY -p tcp --dport 80 -j REDIRECT --to-ports $proxy_local_port
|
||||
Iptables -t nat -A PROXY -p tcp --dport 443 -j REDIRECT --to-ports $proxy_local_port
|
||||
|
||||
# Apply the rules to nat client
|
||||
Iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
# Apply the rules to localhost
|
||||
Iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
- Clear the entire chain iptables -F Chain names such as iptables -t nat -F PROXY
|
||||
- Delete the specified user-defined chain iptables -X chain name such as iptables -t nat -X PROXY
|
||||
- Remove rules from the selected chain iptables -D chain name Rule details such as iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 1.11 Custom DNS
|
||||
--dns-address and --dns-ttl parameters, used to specify the dns (--dns-address) used by the proxy to access the domain name.
|
||||
And the analysis result cache time (--dns-ttl) seconds, to avoid system dns interference to the proxy, in addition to the cache function can also reduce the dns resolution time to improve access speed.
|
||||
For example:
|
||||
`proxy http -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 1.12 Custom encryption
|
||||
The proxy's http(s) proxy can encrypt tcp data via tls standard encryption and kcp protocol on top of tcp, in addition to support customization after tls and kcp.
|
||||
Encryption, that is to say, custom encryption and tls|kcp can be used in combination. The internal use of AES256 encryption, you only need to define a password when you use it.
|
||||
Encryption is divided into two parts, one is whether the local (-z) encryption and decryption, and the other is whether the transmission with the upstream (-Z) is encrypted or decrypted.
|
||||
Custom encryption requires both ends to be proxy. The following two levels and three levels are used as examples:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
### 1.13 Compressed transmission
|
||||
The proxy http(s) proxy can encrypt tcp data through tls standard encryption and kcp protocol on top of tcp, and can also compress data before custom encryption.
|
||||
That is to say, compression and custom encryption and tls|kcp can be used in combination. Compression is divided into two parts, one part is local (-m) compression transmission.
|
||||
Part of it is compressed with the upstream (-M) transmission.
|
||||
Compression requires both sides to be proxy. Compression also protects (encrypted) data to a certain extent. The following uses Level 2 and Level 3 as examples:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
### 1.14 Load Balancing
|
||||
|
||||
The HTTP(S) proxy supports upper-level load balancing, and multiple upstream repeat-P parameters can be used.
|
||||
|
||||
`proxy http --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080`
|
||||
|
||||
### 1.14.1 Setting the retry interval and timeout time
|
||||
|
||||
`proxy http --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp - p :33080`
|
||||
|
||||
### 1.14.2 Setting weights
|
||||
|
||||
`proxy http --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -t tcp - p :33080`
|
||||
|
||||
### 1.14.3 Use the target address to select the upstream
|
||||
|
||||
`proxy http --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp -p :33080`
|
||||
|
||||
### 1.15 Speed limit
|
||||
|
||||
The speed limit is 100K, which can be specified by the `-l` parameter, for example: 100K 2000K 1M . 0 means no limit.
|
||||
|
||||
`proxy http -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 1.16 Specifying Outgoing IP
|
||||
|
||||
The `--bind-listen` parameter can be used to open the client connection with the portal IP, and use the portal IP as the outgoing IP to access the target website. If the incorrect IP is bound, the proxy will not work. At this point, the proxy will try to bind the target without binding the IP, and the log will prompt.
|
||||
|
||||
`proxy http -t tcp -p 2.2.2.2:33080 --bind-listen`
|
||||
|
||||
### 1.17 Certificate parameters use base64 data
|
||||
|
||||
By default, the -C, -K parameter is the path to the crt certificate and the key file.
|
||||
|
||||
If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
|
||||
### 1.18 Intelligent mode
|
||||
Intelligent mode setting, can be one of intelligent|direct|parent.
|
||||
The default is: intelligent.
|
||||
The meaning of each value is as follows:
|
||||
`--intelligent=direct`, the targets in the blocked are not directly connected.
|
||||
`--intelligent=parent`, the target that is not in the direct is going to the higher level.
|
||||
`--intelligent=intelligent`, blocked and direct have no targets, intelligently determine whether to use the upstream access target.
|
||||
|
||||
### 1.19 Help
|
||||
`proxy help http`
|
||||
|
||||
## 2.TCP Proxies
|
||||
|
||||
### 2.1. Ordinary level TCP proxy
|
||||
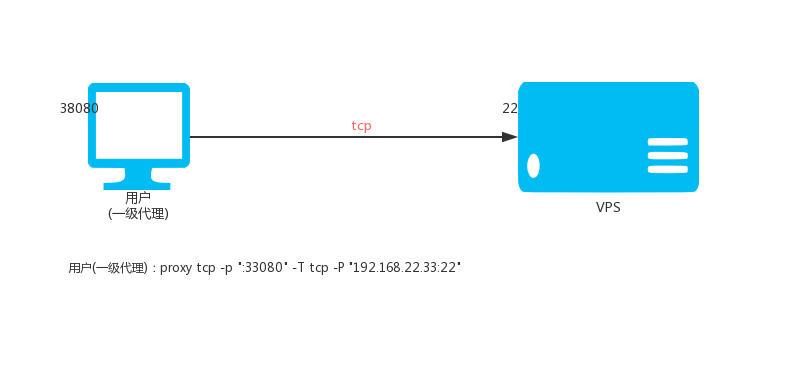
|
||||
Local execution:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22"`
|
||||
Then access the local port 33080 is to access port 22 of 192.168.22.33.
|
||||
|
||||
The `-p` parameter supports :
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000, 9001 to 9999 for a total of 1002 ports
|
||||
```
|
||||
|
||||
If the number of local listening ports is greater than 1, the corresponding upper port corresponding to the local port will be connected, and the port in `-P` will be ignored.
|
||||
|
||||
If you need a connection from all ports, connect to the upper specified port, you can add the parameter `--lock-port`.
|
||||
|
||||
such as:
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:0"`
|
||||
|
||||
Then the connection of the `33080` port will connect to the `33080` port of 192.168.22.33, and the other ports are similar. The local and upper ports are the same. At this time, the port in the parameter `-P` uses `0`.
|
||||
|
||||
If you want to connect the ports of `33080`, `33081`, etc. to the `22` port of 192.168.22.33, you can add the parameter `--lock-port`.
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:22" --lock-port`
|
||||
|
||||
### 2.2. Ordinary secondary TCP proxy
|
||||
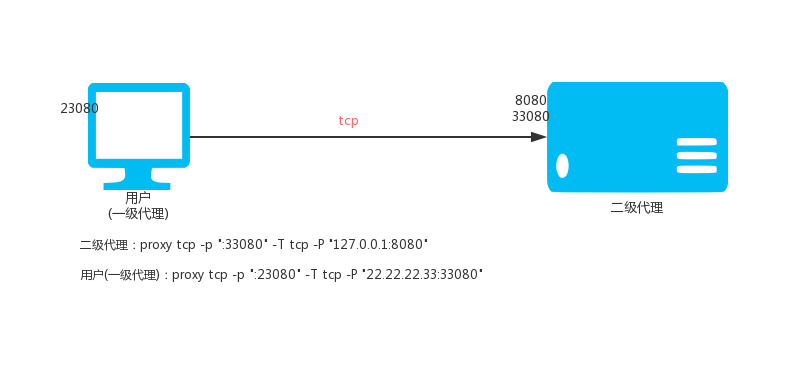
|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
Local execution:
|
||||
`proxy tcp -p ":23080" -T tcp -P "22.22.22.33:33080"`
|
||||
Then access the local port 23080 is to access port 8020 of 22.22.22.33.
|
||||
|
||||
### 2.3. Ordinary three-level TCP proxy
|
||||
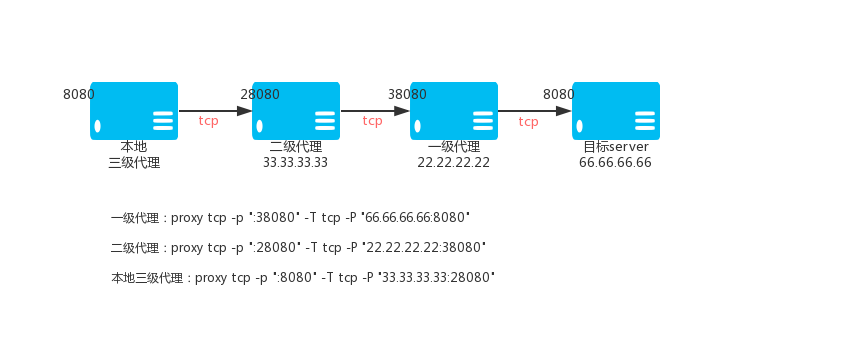
|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -p ":38080" -T tcp -P "66.66.66.66:8080"`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy tcp -p ":8080" -T tcp -P "33.33.33.33:28080"`
|
||||
Then access the local port 8080 is to access the port 8080 of 66.66.66.66 through the encrypted TCP tunnel.
|
||||
|
||||
### 2.4. Encrypting secondary TCP proxy
|
||||
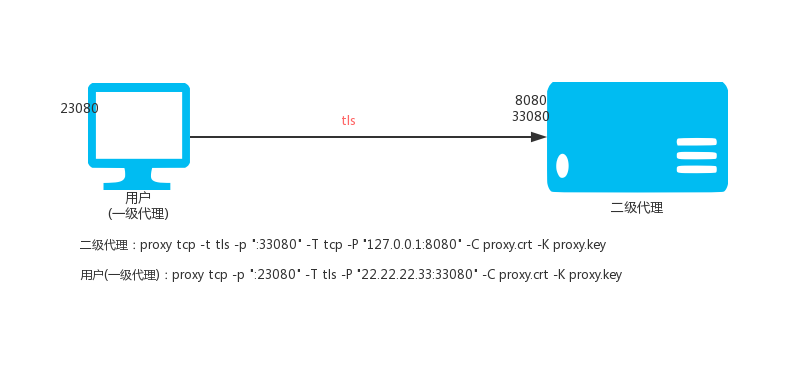
|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -t tls -p ":33080" -T tcp -P "127.0.0.1:8080" -C proxy.crt -K proxy.key`
|
||||
Local execution:
|
||||
`proxy tcp -p ":23080" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 23080 is to access the port 8080 of 22.22.22.33 through the encrypted TCP tunnel.
|
||||
|
||||
### 2.5.Encrypting Level 3 TCP Agent
|
||||
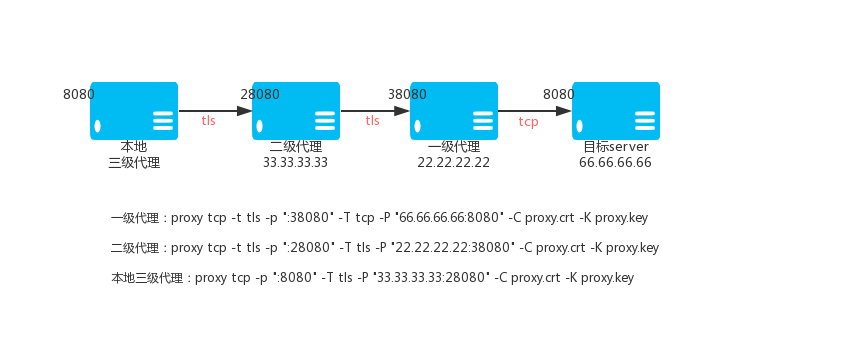
|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T tcp -P "66.66.66.66:8080" -C proxy.crt -K proxy.key`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 8080 is to access the port 8080 of 66.66.66.66 through the encrypted TCP tunnel.
|
||||
|
||||
### 2.6 Connecting to a upstream through a proxy
|
||||
Sometimes the network where the proxy is located cannot directly access the external network. You need to use an https or socks5 proxy to access the Internet. Then this time
|
||||
The -J parameter can help you to connect the proxy to the peer-P through the https or socks5 proxy when mapping the proxy tcp port, mapping the external port to the local.
|
||||
The -J parameter format is as follows:
|
||||
|
||||
Https proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Https://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Https://host:port
|
||||
|
||||
Socks5 proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Socks5://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Socks5://host:port
|
||||
|
||||
Host: the IP or domain name of the proxy
|
||||
Port: the port of the proxy
|
||||
|
||||
### 2.7 Specify Outgoing IP
|
||||
When the TCP proxy is a superior type (parameter: -T) is tcp, it supports the specified exit IP. Using the `--bind-listen` parameter, you can open the client to connect with the portal IP, and use the portal IP as the outgoing IP to access the target website. If an incorrect IP is bound, the proxy will not work, the proxy will try to bind the target without binding the IP, and the log will prompt.
|
||||
|
||||
`proxy tcp -p ":33080" -T tcp -P" 192.168.22.33:22" -B`
|
||||
|
||||
### 2.8 Speed limit, connections limit
|
||||
|
||||
The parameter `--max-conns` can limit the maximum number of connections per port.
|
||||
For example, limit the maximum number of connections per port:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --max-conns 1000`
|
||||
The parameter `--rate-limit` can limit the rate of each tcp connection.
|
||||
For example, limit the connection rate of each tcp to 100k/s:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --rate-limit 100k`
|
||||
|
||||
### 2.9 Compressed transmission
|
||||
|
||||
`--c` controls whether to compress transmission between local and client, default false;` --C` controls whether to compress transmission between local and upstream, default false.
|
||||
|
||||
Examples:
|
||||
|
||||
VPS (IP: 22.22.22.33) implementation:
|
||||
`proxy tcp -t tcp --c -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
Local execution:
|
||||
`proxy tcp -t tcp -p ":23080" -T tcp -P "22.22.22.33:33080" --C`
|
||||
|
||||
### 2.10 View Help
|
||||
`proxy help tcp`
|
||||
|
||||
## 3.UDP Proxies
|
||||
|
||||
### 3.1. Ordinary UDP proxy
|
||||
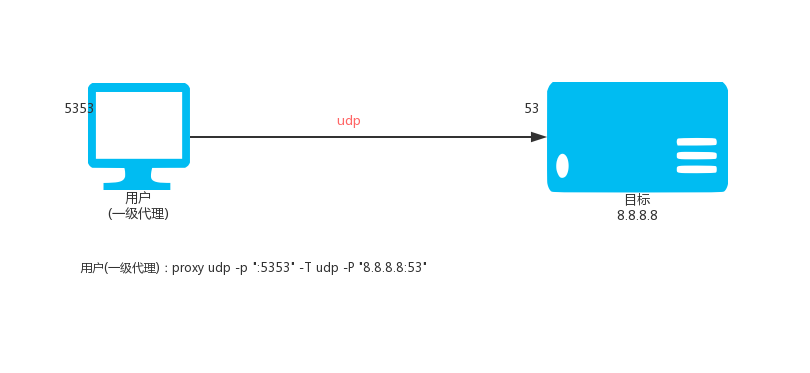
|
||||
Local execution:
|
||||
`proxy udp -p ":5353" -T udp -P "8.8.8.8:53"`
|
||||
Then access the local UDP: 5353 port is to access 8.8.8.8 UDP: 53 port.
|
||||
|
||||
The `-p` parameter supports :
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000, 9001 to 9999 for a total of 1002 ports
|
||||
```
|
||||
|
||||
If the number of local listening ports is greater than 1, the corresponding upper port corresponding to the local port will be connected, and the port in `-P` will be ignored.
|
||||
|
||||
If you need a connection from all ports, connect to the upper specified port, you can add the parameter `--lock-port`.
|
||||
|
||||
such as:
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:0"`
|
||||
|
||||
Then the connection of the `33080` port will connect to the `33080` port of 192.168.22.33, and the other ports are similar. The local and upper ports are the same. At this time, the port in the parameter `-P` uses `0`.
|
||||
|
||||
If you want to connect the ports of `33080`, `33081`, etc. to the `2222` port of 192.168.22.33, you can add the parameter `--lock-port`.
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:2222" --lock-port`
|
||||
|
||||
### 3.2. Ordinary secondary UDP proxy
|
||||
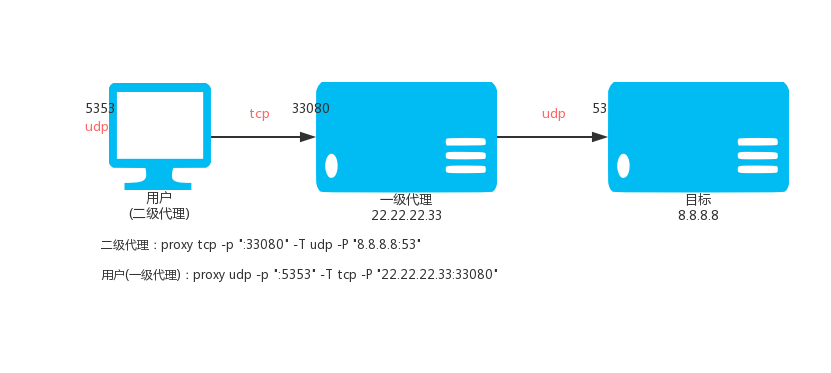
|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -p ":33080" -T udp -P "8.8.8.8:53"`
|
||||
Local execution:
|
||||
`proxy udp -p ":5353" -T tcp -P "22.22.22.33:33080"`
|
||||
Then access the local UDP: 5353 port is through the TCP tunnel, through the VPS access 8.8.8.8 UDP: 53 port.
|
||||
|
||||
### 3.3. Ordinary three-level UDP proxy
|
||||
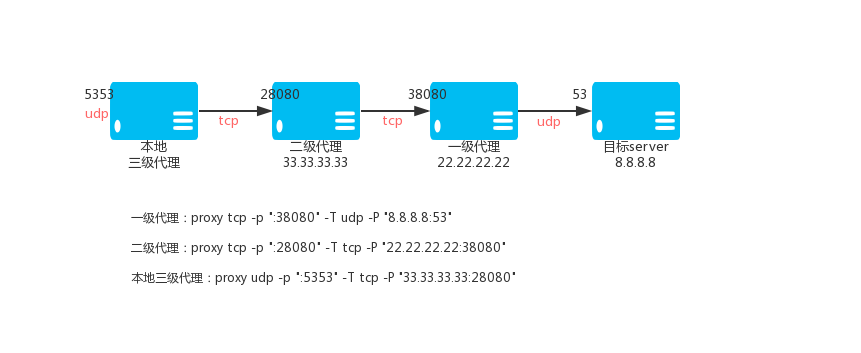
|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -p ":38080" -T udp -P "8.8.8.8:53"`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy udp -p ":5353" -T tcp -P "33.33.33.33:28080"`
|
||||
Then access to the local 5353 port is through the TCP tunnel, through the VPS to access port 8.8.8.8.
|
||||
|
||||
### 3.4. Encrypting secondary UDP proxy
|
||||
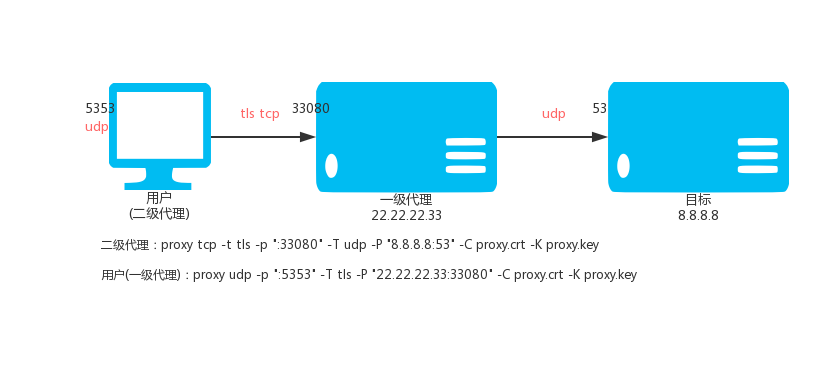
|
||||
VPS (IP: 22.22.2.33) is executed:
|
||||
`proxy tcp -t tls -p ":33080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
Local execution:
|
||||
`proxy udp -p ":5353" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
Then access the local UDP: 5353 port is through the encrypted TCP tunnel, through the VPS access 8.8.8.8 UDP: 53 port.
|
||||
|
||||
### 3.5. Encryption Level 3 UDP Agent
|
||||
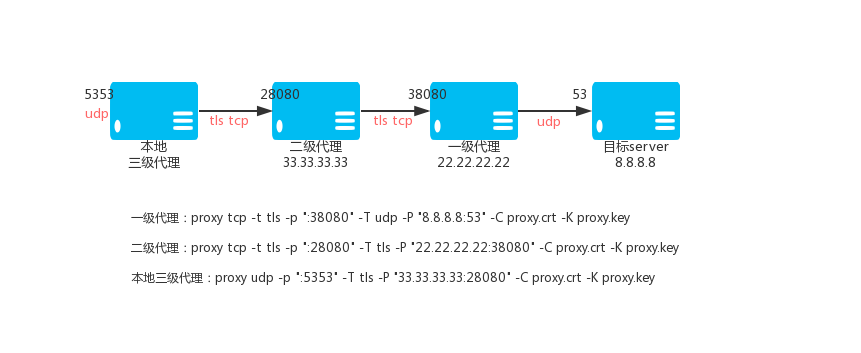
|
||||
Primary TCP proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
Secondary TCP proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 TCP proxy (local)
|
||||
`proxy udp -p ":5353" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then access the local 5353 port is to access the 8.8.8.8 port 53 through VPS_01 through the encrypted TCP tunnel.
|
||||
|
||||
### 3.6 Specify Outgoing IP
|
||||
When the UDP upstream proxies (parameter: -T) is udp, it supports the specified outgoing IP. Using the `--bind-listen` parameter, you can open the client to connect with the server IP, and use the server IP as the outgoing IP to access the target. If an incorrect IP is bound, the proxy will not work.
|
||||
|
||||
`proxy udp -p ":33080" -T udp -P "192.168.22.33:2222" -B`
|
||||
|
||||
### 3.7 Help
|
||||
`proxy help udp`
|
||||
|
||||
## 4. Expose Intranet
|
||||
|
||||
### 4.1 principle description
|
||||
Intranet penetration, divided into two versions, "multi-link version" and "multiplexed version", generally like a web service, this service is not a long-term connection, it is recommended to use "multi-link version", if it is to keep long The time connection suggests using a "multiplexed version."
|
||||
1. Multi-link version, the corresponding sub-command is tserver, tclient, tbridge.
|
||||
1. Multiplexed version, the corresponding subcommand is server, client, bridge.
|
||||
1. The parameters of the multi-link version and the multiplex version are exactly the same.
|
||||
1. The multiplexed version of the server, client can open the compressed transmission, the parameter is --c.
|
||||
1. server, client either open compression, or not open, can not open only one.
|
||||
|
||||
The following tutorial uses the "multiplexed version" as an example to illustrate how to use it.
|
||||
The intranet penetration consists of three parts: client, server, and bridge; client and server actively connect to the bridge for bridging.
|
||||
|
||||
### 4.2 TCP common usage
|
||||
Background:
|
||||
- Company Machine A provides web service port 80
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
At home, you can access the port 80 of company machine A by accessing port 28080 of the VPS.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.3 WeChat interface local development
|
||||
Background:
|
||||
- Your own notebook provides nginx service port 80
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
Fill in the address in the webpage callback interface configuration of WeChat's development account: http://22.22.22.22/calback.php
|
||||
Then you can access the calback.php under the 80 port of the notebook. If you need to bind the domain name, you can use your own domain name.
|
||||
For example: wx-dev.xxx.com resolves to 22.22.22.22, and then in your own notebook nginx
|
||||
Configure the domain name wx-dev.xxx.com to the specific directory.
|
||||
|
||||
|
||||
Steps:
|
||||
1. Execute on vps to ensure that port 80 of vps is not occupied by other programs.
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":80@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on your laptop
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.4 UDP common usage
|
||||
Background:
|
||||
- Company Machine A provides DNS resolution service, UDP: port 53
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
At home, you can use the company machine A to perform domain name resolution services by setting the local dns to 22.22.22.22.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server --udp -r ":53@:53" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.5 advanced usage one
|
||||
Background:
|
||||
- Company Machine A provides web service port 80
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
In order to be safe, I don't want to have access to the company machine A on the VPS, and I can access the port 28080 of the machine at home.
|
||||
Access to port 80 of company machine A via an encrypted tunnel.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on your home computer
|
||||
`proxy server -r ":28080@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.6 Advanced Usage II
|
||||
Tip:
|
||||
If multiple clients are connected to the same bridge at the same time, you need to specify a different key, which can be set by the --k parameter, and --k can be any unique string.
|
||||
Just be the only one on the same bridge.
|
||||
When the server is connected to the bridge, if there are multiple clients connecting to the same bridge at the same time, you need to use the --k parameter to select the client.
|
||||
Expose multiple ports by repeating the -r parameter. The format of -r is: "local IP: local port @clientHOST:client port".
|
||||
|
||||
Background:
|
||||
- Company Machine A provides web service port 80, ftp service port 21
|
||||
- There is a VPS, public network IP: 22.22.22.22
|
||||
|
||||
Demand:
|
||||
At home, you can access the port 80 of company machine A by accessing port 28080 of the VPS.
|
||||
At home, I can access the 21 port of company machine A by accessing port 29090 of the VPS.
|
||||
|
||||
Steps:
|
||||
Execute on vps
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -r ":29090@:21" --k test -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. Execute on company machine A
|
||||
`proxy client --k test -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Complete
|
||||
|
||||
### 4.7.server -r parameter
|
||||
The full format of -r is: `PROTOCOL://LOCAL_IP:LOCAL_PORT@[CLIENT_KEY]CLIENT_LOCAL_HOST:CLIENT_LOCAL_PORT`
|
||||
|
||||
4.7.1. Protocol PROTOCOL: tcp or udp.
|
||||
For example: `-r "udp://:10053@:53" -r "tcp://:10800@:1080" -r ":8080@:80"`
|
||||
If the --udp parameter is specified, PROTOCOL defaults to udp, then:`-r ":8080@:80"` defaults to udp;
|
||||
If the --udp parameter is not specified, PROTOCOL defaults to tcp, then: `-r ":8080@:80"` defaults to tcp;
|
||||
|
||||
4.7.2. CLIENT_KEY: The default is default.
|
||||
For example: -r "udp://:10053@[test1]:53" -r "tcp://:10800@[test2]:1080" -r ":8080@:80"
|
||||
If the --k parameter is specified, such as --k test, then: `-r ":8080@:80"`CLIENT_KEY defaults to test;
|
||||
If the --k parameter is not specified, then: `-r ":8080@:80"`CLIENT_KEY defaults to default;
|
||||
|
||||
4.7.3. LOCAL_IP is empty. The default is: `0.0.0.0`, CLIENT_LOCAL_HOST is empty. The default is: `127.0.0.1`;
|
||||
|
||||
### 4.8.server and client connect bridge through proxy
|
||||
Sometimes the network where the server or client is located cannot directly access the external network. You need to use an https or socks5 proxy to access the Internet. Then this time
|
||||
The -J parameter can help you to connect the server or client to the bridge via https or socks5.
|
||||
The -J parameter format is as follows:
|
||||
|
||||
Https proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Https://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Https://host:port
|
||||
|
||||
Socks5 proxy writing:
|
||||
The proxy needs authentication, username: username password: password
|
||||
Socks5://username:password@host:port
|
||||
Agent does not require authentication
|
||||
Socks5://host:port
|
||||
|
||||
Host: the IP or domain name of the proxy
|
||||
Port: the port of the proxy
|
||||
|
||||
### 4.9. Expose HTTP service
|
||||
|
||||
Usually the HTTP request client will use the server's ip and port to set the HOST field, but it is not the same as the expected backend actual HOST, which causes tcp to be passed.However, the backend relies on the HOST field to locate the virtual host and it will not work. Now use the `--http-host` parameter to force the HOST field value of the http header to be the actual value of the backend.Domain names and ports can be easily solved. After using the `--http-host` parameter, two headers will be added to the header of each HTTP request. The `X-Forwarded-For` and `X-Real-IP` values are the client IP, so the backend http service can easily obtain the real IP address of the client.
|
||||
|
||||
The format of the `server`-http-host parameter is as follows:
|
||||
|
||||
`--http-host www.test.com:80@2200`, if the server listens to multiple ports, just repeat the `--http-host` parameter to set the HOST for each port.
|
||||
|
||||
Example:
|
||||
|
||||
For example, the client local nginx, 127.0.0.1:80 provides a web service, which is bound to a domain name `local.com`.
|
||||
|
||||
Then the server startup parameters can be as follows:
|
||||
|
||||
`proxy server -P :30000 -r :2500@127.0.0.1:80 --http-host local.com@2500`
|
||||
|
||||
Explanation:
|
||||
|
||||
`-r :2500@127.0.0.1:80` and `--http-host local.com:80@2500` The 2500 port is the port that the server listens locally.
|
||||
|
||||
When the http protocol is used to request the ip:2500 port of the server, the header HOST field of http will be set to `local.com`.
|
||||
|
||||
### 4.10 About traffic statistics
|
||||
If you start a server docking peer separately, it is the proxy-admin control panel. You need to create a new mapping in the upper-level control panel to obtain the ID of the mapping rule.
|
||||
|
||||
Then start the server and add the parameter --server-id=the ID of the mapping rule to count the traffic.
|
||||
|
||||
### 4.11 About p2p
|
||||
Intranet penetration support When the server and client network conditions are met, the server and client are directly connected through p2p. The opening method is:
|
||||
|
||||
When starting the bridge, server, client, add the `--p2p` parameter. The server's -r parameter can be used to enable p2p (ptcp and pudp) for the port.
|
||||
|
||||
If the p2p hole fails between the server and the client, the bridge transfer data is automatically switched.
|
||||
|
||||
### 4.12 Client key whitelist
|
||||
The intranet penetrating bridge can set the client key whitelist. The parameter is --client-keys. The format can be:
|
||||
|
||||
a. File name, file content One client key can only contain the alphanumeric underscore, which is the value of the client startup parameter --k. Only the client key can connect to the whitelist client. The line starting with # is a comment.
|
||||
|
||||
b. The base64 encoding at the beginning of "base64://" is the content of the file described in a above, for example: base64://ajfpoajsdfa=
|
||||
|
||||
c. "str://" multiple keywords separated by a comma at the beginning, such as: str://default,company,school
|
||||
|
||||
The default is empty, allowing all keys.
|
||||
|
||||
### 4.13 Network NAT Type Judgment
|
||||
|
||||
Senat type judgment, easy to check whether the network supports p2p, you can execute: `proxy tools -a nattype`
|
||||
|
||||
### 4.14 Help
|
||||
`proxy help bridge`
|
||||
`proxy help server`
|
||||
`proxy help client`
|
||||
|
||||
## 5.SOCKS5 Proxies
|
||||
prompt:
|
||||
|
||||
SOCKS5 proxy, support CONNECT, UDP protocol, does not support BIND, supports username and password authentication.
|
||||
|
||||
*** If your VPS is Alibaba Cloud, Tencent Cloud is a VPS, if ifconfig can't see your public IP, you can only see the intranet IP, ***
|
||||
|
||||
*** Then you need to add the `-g VPS public network IP` parameter, the UDP function of the SOCKS5 proxy can work normally. ***
|
||||
|
||||
***The udp function of socks5 is turned off by default, and can be turned on by `--udp`. The default is a random port for handshake, and performance can be improved by fixing a port.
|
||||
Set by parameter `--udp-port 0`, `0` represents a free port is randomly selected, or you can manually specify a specific port. ***
|
||||
|
||||
### 5.1. Ordinary SOCKS5 Agent
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080"`
|
||||
|
||||
Listen port argument `-p` can be:
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000 and 9001 to 9999, 1002 total ports
|
||||
```
|
||||
|
||||
### 5.2. Ordinary secondary SOCKS5 agent
|
||||
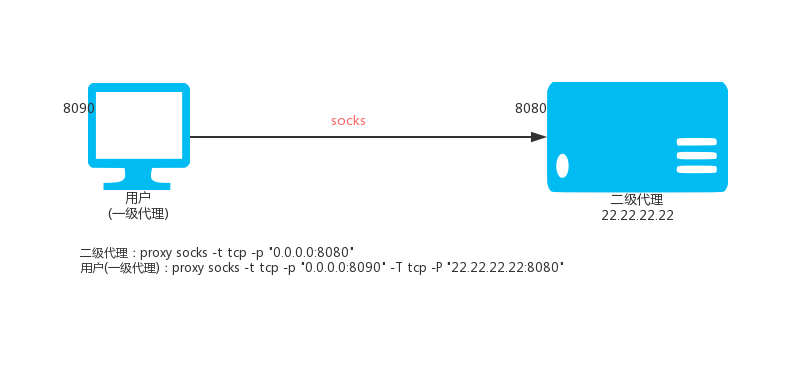
|
||||
Use local port 8090, assuming the upstream SOCKS5 proxy is `22.22.22.22:8080`
|
||||
`proxy socks -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" `
|
||||
We can also specify the black and white list file of the website domain name, one domain name and one domain name, the matching rule is the rightmost match, for example: baidu.com, the match is *.*.baidu.com, the blacklist domain name domain name goes directly to the upstream agent, white The domain name of the list does not go to the upstream agent; if the domain name is in the blacklist and in the whitelist, the blacklist works.
|
||||
`proxy socks -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt`
|
||||
|
||||
### 5.3. SOCKS Level 2 Agent (Encryption)
|
||||
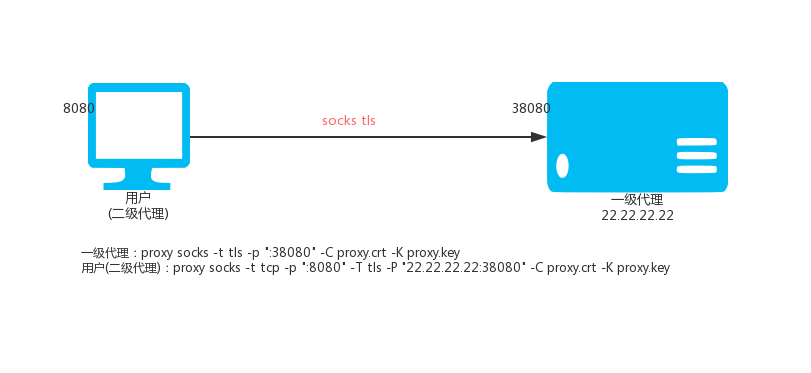
|
||||
Level 1 SOCKS proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
Secondary SOCKS proxy (local Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS.
|
||||
|
||||
Secondary SOCKS proxy (local windows)
|
||||
`proxy.exe socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Then set your windos system, the proxy that needs to go through the proxy Internet program is the socks5 mode, the address is: 127.0.0.1, the port is: 8080, the program can access the Internet through vps through the encrypted channel.
|
||||
|
||||
### 5.4. SOCKS Level 3 Agent (Encryption)
|
||||
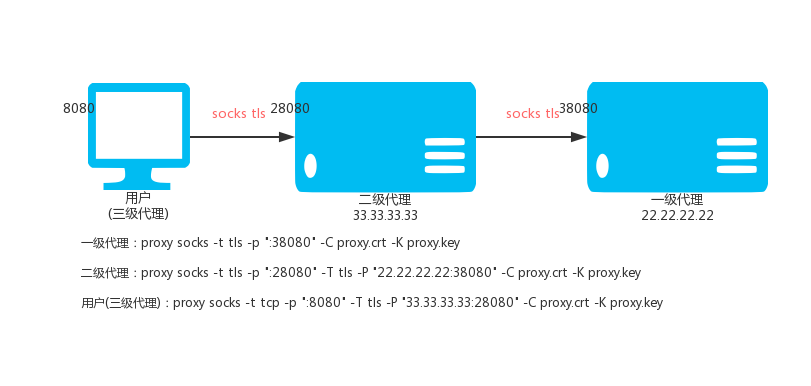
|
||||
Level 1 SOCKS proxy VPS_01, IP: 22.22.22.22
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
Secondary SOCKS proxy VPS_02, IP: 33.33.33.33
|
||||
`proxy socks -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
Level 3 SOCKS proxy (local)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
Then accessing the local port 8080 is to access the proxy port 38080 on the first-level SOCKS proxy.
|
||||
|
||||
### 5.5. SOCKS proxy traffic is forced to go to the upper level SOCKS proxy
|
||||
By default, the proxy will intelligently determine whether a website domain name is inaccessible. If it is not accessible, it will go to the upstream SOCKS proxy. With --always, all SOCKS proxy traffic can be forced to go to the upper SOCKS proxy.
|
||||
`proxy socks --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
### 5.6. SOCKS via SSH relay
|
||||
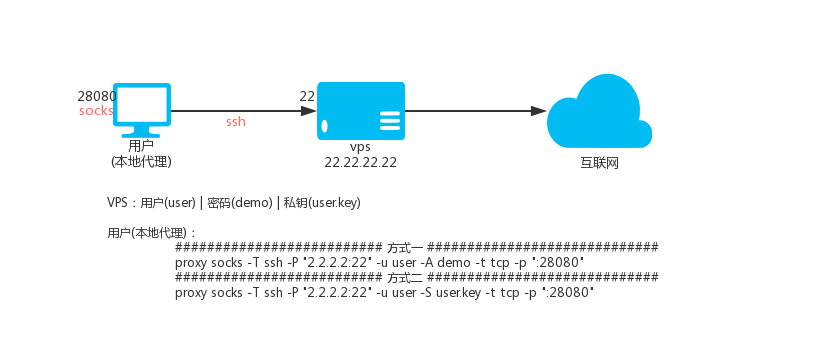
|
||||
Description: The principle of ssh transfer is to use the forwarding function of ssh, that is, after you connect to ssh, you can access the target address through ssh proxy.
|
||||
Suppose there is: vps
|
||||
- IP is 2.2.2.2, ssh port is 22, ssh username is: user, ssh user password is: demo
|
||||
- The user's ssh private key name is user.key
|
||||
|
||||
#### *5.6.1 How to ssh username and password*
|
||||
Local SOCKS5 proxy port 28080, execute:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080"`
|
||||
#### *5.6.2 How to ssh username and key*
|
||||
Local SOCKS5 proxy port 28080, execute:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080"`
|
||||
|
||||
Then access the local port 28080 is to access the target address through the VPS.
|
||||
|
||||
### 5.7. Certification
|
||||
For the socks5 proxy protocol, we can perform username and password authentication. The authenticated username and password can be specified on the command line.
|
||||
`proxy socks -t tcp -p ":33080" -a "user1:pass1" -a "user2:pass2"`
|
||||
For multiple users, repeat the -a parameter.
|
||||
It can also be placed in a file in the format of a "username:password" and then specified with -F.
|
||||
`proxy socks -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
In addition, the socks5 agent also integrates external HTTP API authentication. We can specify an http url interface address with the --auth-url parameter.
|
||||
Then when there is a user connection, the proxy will request the url in GET mode, with the following three parameters. If the HTTP status code 204 is returned, the authentication is successful.
|
||||
In other cases, the authentication failed.
|
||||
For example:
|
||||
`proxy socks -t tcp -p ":33080" --auth-url "http://test.com/auth.php"`
|
||||
When the user connects, the proxy will request the url ("http://test.com/auth.php") in GET mode.
|
||||
Bring four parameters: user, pass, ip, local_ip:
|
||||
Http://test.com/auth.php?user={USER}&pass={PASS}&ip={IP}&local_ip={LOCAL_IP}
|
||||
User: username
|
||||
Pass: password
|
||||
Ip: User's IP, for example: 192.168.1.200
|
||||
Local_ip: IP of the server accessed by the user, for example: 3.3.3.3
|
||||
|
||||
If there is no -a or -F or --auth-url parameter, the authentication is turned off.
|
||||
|
||||
### 5.8.KCP protocol transmission
|
||||
The KCP protocol requires the --kcp-key parameter to set a password for encrypting and decrypting data.
|
||||
|
||||
Level 1 HTTP proxy (VPS, IP: 22.22.22.22)
|
||||
`proxy socks -t kcp -p ":38080" --kcp-key mypassword`
|
||||
|
||||
Secondary HTTP proxy (local Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
Then access the local port 8080 is to access the proxy port 38080 on the VPS, the data is transmitted through the kcp protocol.
|
||||
|
||||
notice:
|
||||
|
||||
When using the kcp protocol locally, you need to specify the vps public network IP with -g, and the UDP function of socks5 is fully used. At this time, -g is the IP address in the UDP address returned to the client.
|
||||
|
||||
### 5.9. Custom DNS
|
||||
--dns-address and --dns-ttl parameters, used to specify the dns (--dns-address) used by the proxy to access the domain name.
|
||||
And the analysis result cache time (--dns-ttl) seconds, to avoid system dns interference to the proxy, in addition to the cache function can also reduce the dns resolution time to improve access speed.
|
||||
For example:
|
||||
`proxy socks -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 5.10 Custom Encryption
|
||||
The proxy's socks proxy can encrypt tcp data through tls standard encryption and kcp protocol on top of tcp. In addition, it supports custom encryption after tls and kcp, which means that custom encryption and tls|kcp can be used together. The internal use of AES256 encryption, you only need to define a password when you use it.
|
||||
Encryption is divided into two parts, one is whether the local (-z) encryption and decryption, and the other is whether the transmission with the upstream (-Z) is encrypted or decrypted.
|
||||
|
||||
Custom encryption requires both sides to be proxy.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Secondary instance
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
### 5.11 Compressed transmission
|
||||
The proxy's socks proxy can encrypt tcp data through custom encryption and tls standard encryption and kcp protocol on top of tcp. It can also be used before custom encryption.
|
||||
Compress the data, that is, the compression function and the custom encryption and tls|kcp can be used in combination, and the compression is divided into two parts.
|
||||
Part of it is local (-m) compression transmission, and part is whether the transmission with the upstream (-M) is compressed.
|
||||
|
||||
Compression requires both sides to be proxy, and compression also protects (encrypts) data to some extent.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
### 5.12 Load Balancing
|
||||
|
||||
The SOCKS proxy supports the upper-level load balancing, and multiple upstream repeat-P parameters can be used.
|
||||
|
||||
`proxy socks --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.1 Setting the retry interval and timeout time
|
||||
|
||||
`proxy socks --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.2 Setting weights
|
||||
|
||||
`proxy socks --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.3 Use the target address to select the upstream
|
||||
|
||||
`proxy socks --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.13 Speed limit
|
||||
|
||||
The speed limit is 100K, which can be specified by the `-l` parameter, for example: 100K 2000K 1M . 0 means no limit.
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 5.14 Specifying Outgoing IP
|
||||
|
||||
The `--bind-listen` parameter can be used to open the client connection with the portal IP, and use the portal IP as the outgoing IP to access the target website. If the ingress IP is an intranet IP, the egress IP does not use the ingress IP.
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 --bind-listen`
|
||||
|
||||
### 5.15 Cascade Certification
|
||||
|
||||
SOCKS5 supports cascading authentication, and -A can set upstream authentication information.
|
||||
|
||||
upstream:
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -a user:pass`
|
||||
|
||||
local:
|
||||
|
||||
`proxy socks -T tcp -P 2.2.2.2:33080 -A user:pass -t tcp -p :33080`
|
||||
|
||||
### 5.16 Certificate parameters use base64 data
|
||||
|
||||
By default, the -C, -K parameter is the path to the crt certificate and the key file.
|
||||
|
||||
If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
|
||||
|
||||
### 5.17 Intelligent mode
|
||||
Intelligent mode setting, can be one of intelligent|direct|parent.
|
||||
The default is: intelligent.
|
||||
The meaning of each value is as follows:
|
||||
`--intelligent=direct`, the targets in the blocked are not directly connected.
|
||||
`--intelligent=parent`, the target that is not in the direct is going to the higher level.
|
||||
`--intelligent=intelligent`, blocked and direct have no targets, intelligently determine whether to use the upstream access target.
|
||||
|
||||
### 5.18 Fixed UDP PORT
|
||||
|
||||
By default, the port number of the UDP function of socks5, the proxy is installed in the `rfc1982 draft` request, which is randomly specified during the protocol handshake process and does not need to be specified in advance.
|
||||
|
||||
However, in some cases, you need to fix the UDP function port. You can use the parameter `--udp-port port number` to fix the port number of the UDP function. For example:
|
||||
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080" --udp-port 38080`
|
||||
|
||||
### 5.19 Help
|
||||
`proxy help socks`
|
||||
|
||||
## 6.SPS Protocol Convert
|
||||
|
||||
### 6.1 Function introduction
|
||||
The proxy protocol conversion uses the sps subcommand. The sps itself does not provide the proxy function. It only accepts the proxy request to "convert and forward" to the existing http(s) proxy or the socks5 proxy or ss proxy; the sps can put the existing http(s) proxy or socks5 proxy or ss proxy is converted to a port that supports both http(s) and socks5 and ss proxies, and the http(s) proxy supports forward proxy and reverse proxy (SNI), converted SOCKS5 proxy, UDP function is still supported when the upper level is SOCKS5 or SS; in addition, for the existing http(s) proxy or socks5 proxy, three modes of tls, tcp, and kcp are supported, and chain connection is supported, that is, multiple sps node levels can be supported. The connection builds an encrypted channel.
|
||||
|
||||
The encryption methods supported by the `ss` function are: aes-128-cfb, aes-128-ctr, aes-128-gcm, aes-192-cfb, aes-192-ctr, aes-192-gcm, aes-256- Cfb , aes-256-ctr , aes-256-gcm , bf-cfb , cast5-cfb , chacha20 , chacha20-ietf , chacha20-ietf-poly1305 , des-cfb , rc4-md5 , rc4-md5-6 , salsa20 , Xchacha20
|
||||
|
||||
Listen port argument `-p` can be:
|
||||
|
||||
```text
|
||||
-p ":8081" listen on 8081
|
||||
-p ":8081,:8082" listen on 8081 and 8082
|
||||
-p ":8081,:8082,:9000-9999" listen on 8081 and 8082 and 9000 and 9001 to 9999, 1002 total ports
|
||||
```
|
||||
|
||||
notice:
|
||||
|
||||
When using the kcp protocol locally, you need to specify the vps public network IP with -g, and the UDP function of socks5 is fully used. At this time, -g is the IP address in the UDP address returned to the client.
|
||||
|
||||
The udp function of ss is turned off by default and can be turned on by `--ssudp`. The udp function of socks5 is turned off by default and can be turned on by `--udp`, The default is a random port for handshake, and performance can be improved by fixing a port.
|
||||
Set by parameter `--udp-port 0`, `0` represents a free port is randomly selected, or you can manually specify a specific port.
|
||||
|
||||
### 6.2 HTTP(S) to HTTP(S)+SOCKS5+SS
|
||||
Suppose there is already a normal http(s) proxy: 127.0.0.1:8080. Now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss encryption: Aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a tls http(s) proxy: 127.0.0.1:8080. Now we turn it into a normal proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, and tls requires a certificate file. , ss encryption: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S http -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a kcp http(s) proxy (password is: demo123): 127.0.0.1:8080, now we turn it into a normal proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss encryption: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S http -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.3 SOCKS5 to HTTP(S)+SOCKS5+SS
|
||||
Suppose there is already a normal socks5 proxy: 127.0.0.1:8080, now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss encryption: aes-192 -cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S socks -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a tls socks5 proxy: 127.0.0.1:8080, now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, tls requires certificate file, ss encryption Mode: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S socks -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
Suppose there is already a kcp socks5 proxy (password: demo123): 127.0.0.1:8080, now we turn it into a common proxy that supports both http(s) and socks5 and ss. The converted local port is 18080, ss Encryption method: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S socks -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.4 SS to HTTP(S)+SOCKS5+SS
|
||||
SPS upstream and local support ss protocol, the upstream can be SPS or standard ss service.
|
||||
SPS locally provides HTTP(S)\SOCKS5\SPS three defaults. When the upstream is SOCKS5, the converted SOCKS5 and SS support UDP.
|
||||
Suppose there is already a normal SS or SPS proxy (ss is enabled, encryption: aes-256-cfb, password: demo): 127.0.0.1:8080, now we turn it to support both http(s) and socks5 and The ordinary proxy of ss, the converted local port is 18080, the converted ss encryption mode: aes-192-cfb, ss password: pass.
|
||||
The command is as follows:
|
||||
`proxy sps -S ss -H aes-256-cfb -J pass -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`.
|
||||
|
||||
### 6.5 Chained connection
|
||||
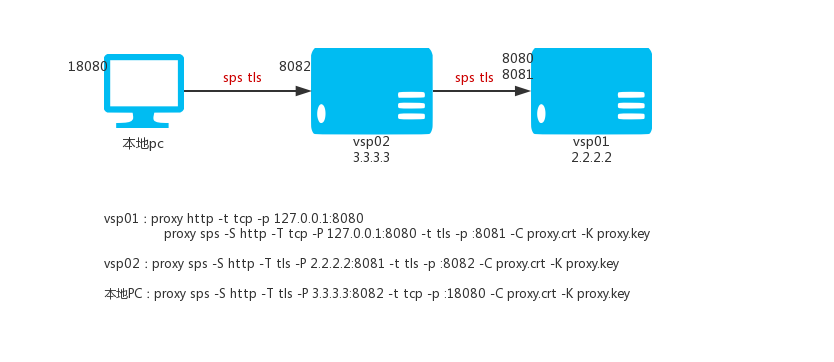
|
||||
The above mentioned multiple sps nodes can be connected to build encrypted channels in a hierarchical connection, assuming the following vps and the home PC.
|
||||
Vps01:2.2.2.2
|
||||
Vps02:3.3.3.3
|
||||
Now we want to use pc and vps01 and vps02 to build an encrypted channel. This example uses tls encryption or kcp. Accessing local 18080 port on the PC is to access the local 8080 port of vps01.
|
||||
First on vps01 (2.2.2.2) we run a locally accessible http(s) proxy and execute:
|
||||
`proxy http -t tcp -p 127.0.0.1:8080`
|
||||
|
||||
Then run a sps node on vps01 (2.2.2.2) and execute:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tls -p :8081 -C proxy.crt -K proxy.key`
|
||||
|
||||
Then run a sps node on vps02 (3.3.3.3) and execute:
|
||||
`proxy sps -S http -T tls -P 2.2.2.2:8081 -t tls -p :8082 -C proxy.crt -K proxy.key`
|
||||
|
||||
Then run a sps node on the pc and execute:
|
||||
`proxy sps -S http -T tls -P 3.3.3.3:8082 -t tcp -p :18080 -C proxy.crt -K proxy.key`
|
||||
|
||||
carry out.
|
||||
|
||||
### 6.6 Authentication
|
||||
Sps supports http(s)\socks5 proxy authentication, which can be cascaded and has four important pieces of information:
|
||||
1: The user sends the authentication information `user-auth`.
|
||||
2: Set the local authentication information `local-auth`.
|
||||
3: Set the connection authentication information 'parent-auth` used by the upstream.
|
||||
4: The authentication information `auth-info-to-parent` that is finally sent to the upstream.
|
||||
Their situation is as follows:
|
||||
|
||||
User-auth | local-auth | parent-auth | auth-info-to-paren
|
||||
| ------ | ------ | ------ | ------
|
||||
| Yes / No | Yes | Yes | From parent-auth
|
||||
| Yes / No | No | Yes | From parent-auth
|
||||
| Yes / No | Yes | No | No
|
||||
| No | No | No | No
|
||||
| Yes | No | No | From user-auth
|
||||
|
||||
For the sps proxy we can perform username and password authentication. The authenticated username and password can be specified on the command line.
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0:0: "`
|
||||
For multiple users, repeat the -a parameter.
|
||||
Can also be placed in a file, the format is one line a `username: password: number of connections: rate: upstream`, and then specified with -F.
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
If the upstream has authentication, the lower level can set the authentication information with the -A parameter, for example:
|
||||
upstream: `proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0: 0:"`
|
||||
Subordinate: `proxy sps -S http -T tcp -P 127.0.0.1:8080 -A "user1:pass1" -t tcp -p ":33080" `
|
||||
|
||||
For more details on certification, please refer to `9.API Certification` and `10.Local Certification`
|
||||
|
||||
### 6.7 Multiple Upstream
|
||||
|
||||
If there are multiple upstreams, they can be specified by multiple -Ps.
|
||||
|
||||
such as:
|
||||
|
||||
`proxy sps -P http://127.0.0.1:3100 -P socks5://127.0.0.1:3200`
|
||||
|
||||
The complete format of `-P` is as follows:
|
||||
|
||||
`protocol://a:[email protected]:33080#1`
|
||||
|
||||
Each section is explained below:
|
||||
|
||||
`protocol://` is the protocol type, possible types and contains the following:
|
||||
|
||||
```text
|
||||
Http is equivalent to -S http -T tcp
|
||||
Https is equivalent to -S http -T tls --parent-tls-single , which is http(s) proxy over TLS
|
||||
Https2 is equivalent to -S http -T tls
|
||||
Socks5 is equivalent to -S socks -T tcp
|
||||
Socks5s is equivalent to -S socks -T tls --parent-tls-single , which is socks over TLS
|
||||
Socks5s2 is equivalent to -S socks -T tls
|
||||
Ss is equivalent to -S ss -T tcp
|
||||
Httpws is equivalent to -S http -T ws
|
||||
Httpwss is equivalent to -S http -T wss
|
||||
Socks5ws is equivalent to -S socks -T ws
|
||||
Socks5wss is equivalent to -S socks -T wss
|
||||
```
|
||||
|
||||
`a:b` is the username and password of the proxy authentication. If it is ss, `a` is the encryption method, `b` is the password, and no username password can be left blank, for example: `http://2.2.2.2:33080` If the username and password are protected, special symbols can be encoded using urlencode.
|
||||
|
||||
`2.2.2.2:33080` is the upstream address, the format is: `IP (or domain name): port `, if the underlying is ws/wss protocol can also bring the path, such as: `2.2.2.2: 33080/ws`;
|
||||
You can also set the `encryption method` and `password` of `ws\wss` by appending the query parameters `m` and `k`, for example: `2.2.2.2:33080/ws?m=aes-192-cfb&k=password`
|
||||
|
||||
`#1` When multiple upper-level load balancing is a weighting strategy, the weights are rarely used.
|
||||
|
||||
### 6.8 Custom Encryption
|
||||
The proxy sps proxy can encrypt tcp data through tls standard encryption and kcp protocol on top of tcp, in addition to support after tls and kcp
|
||||
Custom encryption, that is, custom encryption and tls|kcp can be used in combination, internally using AES256 encryption, only need to define it when using
|
||||
A password can be used, the encryption is divided into two parts, one part is whether the local (-z) encryption and decryption, and the part is the encryption and decryption with the upstream (-Z) transmission.
|
||||
|
||||
Custom encryption requires both sides to be proxy.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Suppose there is already an http(s) proxy: `6.6.6.6:6666`
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through encrypted transmission with the upstream.
|
||||
|
||||
### 6.9 Compressed transmission
|
||||
The proxy sps proxy can encrypt tcp data through custom encryption and tls standard encryption and kcp protocol on top of tcp. It can also be used before custom encryption.
|
||||
Compress the data, that is, the compression function and the custom encryption and tls|kcp can be used in combination, and the compression is divided into two parts.
|
||||
Part of it is local (-m) compression transmission, and part is whether the transmission with the upstream (-M) is compressed.
|
||||
|
||||
Compression requires both sides to be proxy, and compression also protects (encrypts) data to some extent.
|
||||
|
||||
The following two levels, three levels for example:
|
||||
|
||||
Secondary instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
Local secondary execution:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
|
||||
Three-level instance
|
||||
|
||||
Execute on level 1 vps (ip: 2.2.2.2):
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
Execute on the secondary vps (ip: 3.3.3.3):
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
Local three-level execution:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
In this way, when the website is accessed through the local agent 8080, the target website is accessed through compression with the upstream.
|
||||
|
||||
### 6.10 Disabling the protocol
|
||||
By default, SPS supports http(s) and socks5 two proxy protocols. We can disable a protocol by parameter.
|
||||
For example:
|
||||
1. Disable the HTTP(S) proxy function to retain only the SOCKS5 proxy function, parameter: `--disable-http`.
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-http`
|
||||
|
||||
1. Disable the SOCKS5 proxy function to retain only the HTTP(S) proxy function, parameter: `--disable-socks`.
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-socks`
|
||||
|
||||
### 6.11 Speed limit
|
||||
|
||||
Suppose there is a SOCKS5 upstream:
|
||||
|
||||
`proxy socks -p 2.2.2.2:33080 -z password -t tcp`
|
||||
|
||||
SPS lower level, speed limit 100K
|
||||
|
||||
`proxy sps -S socks -P 2.2.2.2:33080 -T tcp -Z password -l 100K -t tcp -p :33080`
|
||||
|
||||
It can be specified by the `-l` parameter, for example: 100K 2000K 1M . 0 means no limit.
|
||||
|
||||
### 6.12 Specifying Outgoing IP
|
||||
|
||||
The `--bind-listen` parameter can be used to open the client connection with the portal IP, and use the portal IP as the outgoing IP to access the target website. If the ingress IP is an intranet IP, the egress IP does not use the ingress IP.
|
||||
|
||||
`proxy sps -S socks -P 2.2.2.2:33080 -T tcp -Z password -l 100K -t tcp --bind-listen -p :33080`
|
||||
|
||||
### 6.13 Certificate parameters use base64 data
|
||||
|
||||
By default, the -C, -K parameter is the path to the crt certificate and the key file.
|
||||
|
||||
If it is the beginning of base64://, then the latter data is considered to be base64 encoded and will be used after decoding.
|
||||
|
||||
### 6.14 Independent Service
|
||||
A sps port can complete the full-featured proxy `http\socks\ss` function.
|
||||
The following command is to open the http(s)\ss\socks service with one click, and enable the udp of socks5 and the udp of ss at the same time.
|
||||
`proxy sps -p: 33080 --ssudp --udp --udp-port 0`
|
||||
|
||||
### 6.15 Target Redirection
|
||||
The https(s)\socks5\ss proxy function provided by the sps function, the client connects to the specified "target" through the sps proxy. This "target" is generally a website or an arbitrary tcp address.
|
||||
The website "target" is generally foo.com: 80, foo.com: 443, sps supports the use of the --rewrite parameter to specify a "target" redirection rule file, redirect the target, the client is non-perceived,
|
||||
For example, if you redirect to "target": demo.com:80 to 192.168.0.12:80, then the client visits the website demo.com, in fact, the website service provided by 192.168.0.12.
|
||||
Example of a "target" redirection rule file:
|
||||
|
||||
```text
|
||||
# example
|
||||
Www.a.com:80 10.0.0.2:8080
|
||||
**.b.com:80 10.0.0.2:80
|
||||
192.168.0.11:80 10.0.0.2:8080
|
||||
```
|
||||
|
||||
When sps is an independent service, an additional local socks5 service will be opened to occupy a random port. Now the parameter `--self-port` can be manually specified when needed. The default is 0 to use random.
|
||||
|
||||
### 6.16 Fixed UDP PORT
|
||||
|
||||
By default, the port number of the UDP function of ss's socks5 is specified by the `rfc1982 draft`. It is randomly specified during the protocol handshake process and does not need to be specified in advance.
|
||||
|
||||
However, in some cases, you need to fix the UDP function port. You can fix the port number of the UDP function by the parameter `--udp-port port_number`, for example:
|
||||
|
||||
`proxy sps -t tcp -p "0.0.0.0:38080" --udp-port 38081`
|
||||
|
||||
It should be noted that the ss function of sps also has UDP function, and the UDP port of ss is the same as the tcp port, so avoid the conflict between the UDP port of socks5 and the UDP port of ss.
|
||||
|
||||
To specify a port that is different from the tcp port.
|
||||
|
||||
### 6.17 iptables 透明代理
|
||||
The sps mode supports the iptables transparent forwarding support of the Linux system, which is commonly referred to as the iptables transparent proxy. If a iptables transparent proxy is performed on the gateway device, the device that is connected through the gateway can realize a non-aware proxy.
|
||||
|
||||
Example start command:
|
||||
|
||||
`proxy sps --redir -p :8888 -P httpws: //1.1.1.1:33080`
|
||||
|
||||
Here it is assumed that there is an http superior proxy 1.1.1.1:33080, which uses ws to transmit data.
|
||||
|
||||
Then add iptables rules, here are the reference rules:
|
||||
|
||||
```shell
|
||||
#upstream proxy server IP address:
|
||||
proxy_server_ip = 1.1.1.1
|
||||
|
||||
#Router running proxy listening port:
|
||||
proxy_local_port = 33080
|
||||
|
||||
#There is no need to modify the following
|
||||
#create a new chain named PROXY
|
||||
iptables -t nat -N PROXY
|
||||
|
||||
#Ignore your PROXY server's addresses
|
||||
#It's very IMPORTANT, just be careful。
|
||||
|
||||
iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
#Ignore LANs IP address
|
||||
iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
#Anything to port 80 443 should be redirected to PROXY's local port
|
||||
iptables -t nat -A PROXY -p tcp -j REDIRECT --to-ports $proxy_local_port
|
||||
#Apply the rules to nat client
|
||||
iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
#Apply the rules to localhost
|
||||
iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
|
||||
- Clear the entire chain iptables -F chain name such as iptables -t nat -F PROXY
|
||||
- Delete the specified user-defined chain iptables -X chain name e.g. iptables -t nat -X PROXY
|
||||
- Delete rule from selected chain iptables -D chain name rule details e.g. iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 6.18 Help
|
||||
|
||||
`proxy help sps`
|
||||
|
||||
## 7.KCP Configuration
|
||||
|
||||
### 7.1 Configuration Introduction
|
||||
Many functions of the proxy support the kcp protocol. Any function that uses the kcp protocol supports the configuration parameters described here.
|
||||
Therefore, the KCP configuration parameters are introduced here.
|
||||
|
||||
### 7.2 Detailed configuration
|
||||
There are a total of 17 KCP configuration parameters, you can not set them, they have default values, if for the best effect,
|
||||
You need to configure the parameters according to your own network conditions. Because the kcp configuration is complex, it requires a certain network basics.
|
||||
If you want to get more detailed configuration and explanation of kcp parameters, please search for yourself. The command line name for each parameter, along with the default values and simple function descriptions are as follows:
|
||||
```
|
||||
--kcp-key="secrect" pre-shared secret between client and server
|
||||
--kcp-method="aes" encrypt/decrypt method, can be: aes, aes-128, aes-192, salsa20, blowfish,
|
||||
Twofish, cast5, 3des, tea, xtea, xor, sm4, none
|
||||
--kcp-mode="fast" profiles: fast3, fast2, fast, normal, manual
|
||||
--kcp-mtu=1350 set maximum transmission unit for UDP packets
|
||||
--kcp-sndwnd=1024 set send window size(num of packets)
|
||||
--kcp-rcvwnd=1024 set receive window size(num of packets)
|
||||
--kcp-ds=10 set reed-solomon erasure coding - datashard
|
||||
--kcp-ps=3 set reed-solomon erasure coding - parityshard
|
||||
--kcp-dscp=0 set DSCP(6bit)
|
||||
--kcp-nocomp disable compression
|
||||
--kcp-acknodelay be carefull! flush ack immediately when a packet is received
|
||||
--kcp-nodelay=0 be carefull!
|
||||
--kcp-interval=50 be carefull!
|
||||
--kcp-resend=0 be carefull!
|
||||
--kcp-nc=0 be carefull! no congestion
|
||||
--kcp-sockbuf=4194304 be carefull!
|
||||
--kcp-keepalive=10 be carefull!
|
||||
```
|
||||
Tip:
|
||||
Parameters: -- four fast3, fast2, fast, normal modes in kcp-mode,
|
||||
Equivalent to setting the following four parameters:
|
||||
Normal:`--nodelay=0 --interval=40 --resend=2 --nc=1`
|
||||
Fast :`--nodelay=0 --interval=30 --resend=2 --nc=1`
|
||||
Fast2:`--nodelay=1 --interval=20 --resend=2 --nc=1`
|
||||
Fast3:`--nodelay=1 --interval=10 --resend=2 --nc=1`
|
||||
|
||||
## 8. Security DNS
|
||||
|
||||
### 8.1 Introduction
|
||||
DNS is known as the service provided by UDP port 53, but with the development of the network, some well-known DNS servers also support TCP mode dns query, such as Google's 8.8.8.8, the DNS anti-pollution server principle of the proxy is to start a proxy DNS proxy locally. Server, which uses TCP to perform dns query through the upstream agent. If it communicates with the upstream agent, it can perform secure and pollution-free DNS resolution. It also supports independent services, concurrent parsing, and enhanced enhanced hosts file function to support flexible concurrent parsing and forwarding.
|
||||
|
||||
Dns resolution order:
|
||||
1. Use the parameter --hosts to parse.
|
||||
2. If the domain name to be resolved is not found in 1, it is parsed using the parameter --forward rule.
|
||||
3. The domain name to be resolved is not found in 1 and 2, and the default --default parsing is used. The default default behavior parameter values are three: proxy, direct, and system.
|
||||
The three parameter values are explained as follows:
|
||||
Proxy: The domain name is resolved by the dns server specified by the -q parameter.
|
||||
Direct: Connect to the dns server specified by the -q parameter to resolve the domain name through the local network.
|
||||
System: resolves the domain name through the system dns.
|
||||
|
||||
Tip:
|
||||
The host file format specified by the --hosts parameter is the same as the system hosts file, and the domain name supports wildcards. You can refer to the hosts file.
|
||||
The parsing forwarding rule file specified by the --forward parameter can be referenced to the resolve.rules file. The domain name supports wildcards. It supports multiple dns servers for each domain name to be parsed concurrently. Whoever resolves the fastest resolution will use the resolution result.
|
||||
The -q parameter can specify multiple remote dns servers to perform concurrent parsing. Whoever resolves the fastest parsing success, the default is: 1.1.1.1, 8.8.8.8, 9.9.9.9, multiple comma-separated,
|
||||
For example, you can also bring ports: 1.1.1.1, 8.8.8.8#53, 9.9.9.9
|
||||
|
||||
If you are a standalone service, you don't need a upstream:
|
||||
Can perform:
|
||||
`proxy dns --default system -p :5353`
|
||||
Or
|
||||
`proxy dns --default direct -p :5353`
|
||||
|
||||
### 8.2 Example of use
|
||||
|
||||
#### 8.2.1 Normal HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
Local execution:
|
||||
`proxy dns -S http -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides DNS resolution.
|
||||
|
||||
#### 8.2.2 Ordinary SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
Local execution:
|
||||
`proxy dns -S socks -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides DNS resolution.
|
||||
|
||||
#### 8.2.3 TLS encrypted HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy http -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S http -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.4 TLS-encrypted SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy socks -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S socks -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.5 KCP encrypted HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy http -t kcp -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S http -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.6 KCP encrypted SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy socks -t kcp -p :33080`
|
||||
Local execution:
|
||||
`proxy dns -S socks -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.7 Custom encrypted HTTP(S) upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy http -t tcp -p :33080 -z password`
|
||||
Local execution:
|
||||
`proxy dns -S http -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
#### 8.2.8 Custom encrypted SOCKS5 upstream agent
|
||||
|
||||
Suppose there is a upstream agent: 2.2.2.2:33080
|
||||
The commands executed by the upstream agent are:
|
||||
`proxy socks -t kcp -p :33080 -z password`
|
||||
Local execution:
|
||||
`proxy dns -S socks -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
Then the local UDP port 53 provides a secure anti-pollution DNS resolution function.
|
||||
|
||||
## 9.API Authentication
|
||||
|
||||
The proxy's http(s)/socks5/sps proxy function supports user-to-agent access via the API.
|
||||
|
||||
### What can I do through the API?
|
||||
|
||||
- User dimension, which controls the single connection rate and controls the maximum number of connections.
|
||||
- IP dimension, which controls the single connection rate and controls the maximum number of connections.
|
||||
- Dynamic upstream, can dynamically obtain its upstream from the API according to the user or client IP, and support http(s)/socks5/ss upstream.
|
||||
- Authenticate every connection, regardless of whether client authentication is required.
|
||||
- Cache authentication results, time can be set to reduce API pressure.
|
||||
|
||||
#### Specific use
|
||||
The proxy's http(s)/socks5/sps proxy API function is controlled by three parameters: `--auth-url` and `--auth-nouser` and `--auth-cache`.
|
||||
The parameter `--auth-url` is the HTTP API interface address. When the client connects, the proxy will request the url in GET mode, with the following parameters. If the HTTP status code 204 is returned, the authentication is successful. In other cases, the authentication fails.
|
||||
|
||||
An example of a complete request API:
|
||||
`http://test.com/auth.php?user=a&pass=b&client_addr=127.0.0.1:49892&local_addr=127.0.0.1:8100&target=http%3A%2F%2Fwww.baidu.com&service=http&sps=0`
|
||||
|
||||
#### Parameter Description
|
||||
`user and pass` When the proxy turns on authentication, here is the username and password provided by the client.
|
||||
`client_addr` The address used by the client to access the proxy, format IP: port.
|
||||
`local_addr` The proxy address accessed by the client, format IP: port.
|
||||
`service` Proxy type, divided into: http, socks.
|
||||
Whether the `sps` proxy is provided by sps, 1: yes, 0: no.
|
||||
`target` The target to be accessed by the client. If it is an http(s) proxy, the target is the specific url accessed; if it is a socks5 proxy, the target is empty.
|
||||
|
||||
#### Example
|
||||
Suppose --auth-url http://127.0.0.1:333/auth.php points to a php interface address.
|
||||
The contents of auth.php are as follows:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#all users and password
|
||||
$alluser=[
|
||||
"user1"=>"pass1",
|
||||
"user2"=>"pass2",
|
||||
"user3"=>"pass3",
|
||||
"user4"=>"pass4",
|
||||
];
|
||||
$proxy_ip=$_GET['local_addr'];
|
||||
$user_ip=$_GET['client_addr'];
|
||||
$service=$_GET['service'];
|
||||
$is_sps=$_GET['sps']=='1';
|
||||
$user=$_GET['user'];
|
||||
$pass=$_GET['pass'];
|
||||
$target=$_GET['target'];
|
||||
|
||||
//business checking
|
||||
//....
|
||||
$ok=false;
|
||||
foreach ($alluser as $dbuser => $dbpass) {
|
||||
if ($user==$dbuser&&$pass==$dbpass){
|
||||
$ok=true;
|
||||
break;
|
||||
}
|
||||
}
|
||||
|
||||
//set the authentication result
|
||||
if($ok){
|
||||
header("userconns:1000");
|
||||
header("ipconns:2000");
|
||||
header("userrate:3000");
|
||||
header("iprate:8000");
|
||||
header("UPSTREAM:http://127.0.0.1:3500?parent-type=tcp");
|
||||
header("HTTP/1.1 204 No Content");
|
||||
}
|
||||
```
|
||||
|
||||
#### Explanation
|
||||
Userconns: The maximum number of connections for the user, not limited to 0 or not set this header.
|
||||
Ipcons: The maximum number of connections for the user IP, not limited to 0 or not set this header.
|
||||
Userrate: User's single TCP connection rate limit, in bytes/second, is not limited to 0 or does not set this header.
|
||||
Iprate: The single TCP connection rate limit of the user IP, in bytes/second, not limited to 0 or not set this header.
|
||||
Upstream: The upstream used, not empty, or not set this header.
|
||||
|
||||
#### Tips
|
||||
1. By default, `--auth-url` is required to provide the user name and password. If you do not need the client to provide the username and password, and authenticate, you can add `--auth-nouser`. The visit will still access the authentication address `--auth-url` for authentication. Only the $user authentication username and the $pass authentication password received in the php interface are empty when client didn't send username and password.
|
||||
2. Connection limit priority: User authentication file limit - "File ip.limit limit -" API user limit - "API IP limit -" command line global connection limit.
|
||||
3. Rate Limit Priority: User Authentication File Rate Limit - "File ip.limit Rate Limit -" API User Rate Limit - "API IP Rate Limit - "Command Line Global Rate Limit.
|
||||
3. The upstream obtains the priority: the upstream of the user authentication file - the file ip.limit upstream-"API upstream-" command line specifies the upstream.
|
||||
4.`--auth-cache` authentication cache, cache the authentication result for a certain period of time, improve performance, reduce the pressure on the authentication interface, --auth-cache unit seconds, default 0, set 0 to close the cache.
|
||||
|
||||
#### upstream detailed description
|
||||
|
||||
1. When the parameter `sps` is 0.
|
||||
When the service is http, upstream only supports http(s) proxy, and does not support authentication. If authentication is required, it can be replaced by sps. Format:
|
||||
`http://127.0.0.1:3100?argk=argv`
|
||||
When the service is a socks, the upstream only supports the socks5 proxy. The format is:
|
||||
`socks5://127.0.0.1:3100?argk=argv`
|
||||
|
||||
Explanation: `http://`,`socks5://` is fixed, `127.0.0.1:3100` is the address of the upstream
|
||||
|
||||
2. When `sps` is 1.
|
||||
Upstream supports socks5, http(s) proxy, support authentication, format: `protocol://a:b@2.2.2.2:33080?argk=argv`, please refer to SPS chapter for details, **multiple upstreams** , the description of the `-P` parameter.
|
||||
3. Parameters, `?` followed by `argk=argv` are parameters: parameter name = parameter value, multiple parameters are connected with `&`.
|
||||
All the supported parameters are as follows, and the meaning of the command line with the same name is the same.
|
||||
1. parent-type : upper-level transport type, support tcp, tls, ws, wss
|
||||
2. parent-ws-method: The encryption method of the upper-level ws transmission type, the supported value is the same as the value range supported by the command line.
|
||||
3. parent-ws-password: The upper-level ws transmission type encryption password, the alphanumeric password
|
||||
4. parent-tls-single : Whether the upper-level tls transport type is a one-way tls, which can be: true | false
|
||||
5. timeout : timeout for establishing tcp connection, number, in milliseconds
|
||||
6. ca : The base64-encoded string of the upper-level tls transport type ca certificate file.
|
||||
7. cert : The base64 encoded string of the higher level tls transport type certificate file.
|
||||
8. key : The base64 encoded string of the higher-level tls transport type certificate key file.
|
||||
|
||||
### Traffic report / Traffic limit / Traffic statistics
|
||||
|
||||
The proxy's http (s) / socks5 / sps / tcp / udp proxy function supports traffic reporting. You can set an http interface address through the parameter `--traffic-url`.
|
||||
The proxy will report the traffic used for this connection to this address.Specifically, the proxy sends an HTTP to GET request to the HTTP URL address set by `--traffic-url`.
|
||||
There are two reporting modes, which can be specified by the `--traffic-mode` parameter. It can be reported in the normal mode or in the fast mode.
|
||||
|
||||
1. Report in `normal` normal mode
|
||||
When the connection is released, the proxy will report the traffic used for this connection to this `--traffic-url` address.
|
||||
|
||||
2. Report in `fast` mode
|
||||
For each connection that has been established, the proxy will `timely` report the traffic generated by this connection to this` --traffic-url` address.
|
||||
`Timing` defaults to 5 seconds, and you can modify` Timing` to the appropriate number of seconds via the parameter `--traffic-interval`.
|
||||
|
||||
The traffic reporting function combined with the above API authentication function can control the user's traffic usage in real time. The traffic is reported to the interface. The interface writes the traffic data to the database, and then the authentication API queries the database to determine the traffic usage and determine whether the user can be successfully authenticated.
|
||||
|
||||
The following is a complete URL request example:
|
||||
|
||||
`http://127.0.0.1:33088/user/traffic?bytes=337&client_addr=127.0.0.1%3A51035&id=http&server_addr =127.0.0.1%3A33088&target_addr=myip.ipip.net%3A80&username=a`
|
||||
|
||||
Request parameter description:
|
||||
id: service id flag.
|
||||
server_addr: proxies's address requested by the client, format: IP: port.
|
||||
client_addr: client address, format: IP: port.
|
||||
target_addr: target address, format: "IP: port", when tcp / udp proxy, this is empty.
|
||||
User name: proxy authentication user name, this is empty when tcp / udp proxy.
|
||||
bytes: the number of traffic bytes used by the user.
|
||||
|
||||
#### Tips
|
||||
|
||||
The `--traffic-url` URL must response the HTTP status code` 204`. Only when the traffic is reported will the report be considered successful, and if it response other status codes, it will be considered that the reported traffic failed, and the log will be output.
|
||||
|
||||
#### traffic flow
|
||||
|
||||
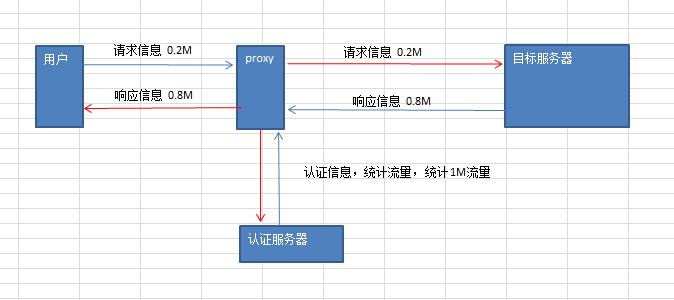
|
||||
|
||||
|
||||
### Disconnect the user's connection
|
||||
|
||||
The proxy's http (s) / socks5 / sps proxy function supports a control interface, which can be specified by the parameter --control-url http interface address,
|
||||
Then the proxy will interval send all the usernames or client IPs currently connected to the proxy to this URL. Specifically, the proxy sends an HTTP to POST request to the HTTP URL address set by --control-url.
|
||||
|
||||
`interval` defaults to 30 seconds, this value can be modified via the --control-sleep parameter.
|
||||
|
||||
When the user expires, or the user's traffic has been used up, the authentication API can only control the user cannot create a new connection, but the connection with the proxy has been established and the connection cannot be immediately disconnected.
|
||||
Then this problem can be solved through the control interface. The control interface will return the content through the control interface in the slowest `interval` time, and the end is invalid when the user establishes the connection.
|
||||
|
||||
#### Request Description
|
||||
|
||||
The proxy sends an HTTP POST request to the control interface URL. There are two fields in the form data: user and ip.
|
||||
|
||||
user: the user name currently connected to the proxy, multiple are separated by commas, for example: user1, user2
|
||||
|
||||
ip: The IP address of the client currently connected to the proxy, multiple are separated by commas, for example: 1.1.1.1, 2.2.2.2
|
||||
|
||||
#### Response Data Description
|
||||
|
||||
The data returned by the control interface is invalid user and IP, the format is a json object data, there are two fields user and ip.
|
||||
|
||||
For example: {"user": "a, b", "ip": ""}
|
||||
|
||||
user: the user name currently connected to the proxy, multiple are separated by commas, not left blank, for example: user1, user2
|
||||
|
||||
ip: The ip address of the client currently connected to the proxy. Multiple are separated by commas and not left blank.
|
||||
|
||||
The connection between the returned user and ip will be disconnected by proxy.
|
||||
|
||||
#### Example
|
||||
Suppose --control-url `http://127.0.0.1:33088/user/control.php` points to a PHP interface address.
|
||||
The content of control.php is as follows:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#revcieve proxy post data
|
||||
$userArr=explode(",",$_POST['user']);
|
||||
$ipArr=$_GET['ip'];
|
||||
|
||||
//invalid users array
|
||||
$badUsers=[];
|
||||
|
||||
foreach ($userArr as $user) {
|
||||
//logic business, push invalid user into $badUsers
|
||||
$badUsers[]=$user;
|
||||
}
|
||||
$data=["user"=>implode(","$badUsers),"ip"=>""];
|
||||
|
||||
echo json_encode($data);
|
||||
```
|
||||
|
||||
|
||||
## 10. Authentication
|
||||
|
||||
The proxy http(s)/socks5/sps proxy function supports the user to access the proxy pair through the configuration file, and supports the http(s) proxy ``Proxy Basic proxy authentication` and the socks5 proxy authentication.
|
||||
|
||||
### start using
|
||||
The proxy's http(s)/socks5/sps proxy function can pass
|
||||
`--auth-file`, `--max-conns`, `--ip-limit`, `--rate-limit`, `-a` These five parameters control.
|
||||
|
||||
#### Detailed explanation of parameters
|
||||
|
||||
##### `--auth-file`
|
||||
The authenticated user name and password file. This parameter specifies a file, one line per rule, in the format: "username: password: number of connections: rate: upstream".
|
||||
`Connection number` is the maximum number of connections for the user. The 'rate' is the maximum speed of each tcp connection of the user. The unit is: byte/second. The upper level is the upper level used by the user.
|
||||
Not only can the authenticated user be set by `--auth-file`, but also the `-a` parameter can be set directly. Multiple users can repeat multiple `-a` parameters.
|
||||
For example: `proxy http -a a:b:0:0: -a c:d:0:0:`
|
||||
|
||||
Example explanation:
|
||||
For example: `user:pass:100:10240:http://192.168.1.1:3100`
|
||||
`user` is the authentication username
|
||||
`pass` is the authentication user password (cannot contain a colon:)
|
||||
`100` is the maximum number of connections for this user, not limited to write 0
|
||||
`10240` is the rate limit of this user's single tcp connection, the unit is: byte / sec, no limit write 0
|
||||
`http://192.168.1.1:3100` is the upstream used by this user, no space is left blank
|
||||
|
||||
##### `--max-conns`
|
||||
Limit the maximum number of global connections for the proxy service, a number, 0 is unrestricted, default is 0.
|
||||
|
||||
##### `--ip-limit`
|
||||
Controls the number of connections and connection rate of the client IP. This parameter specifies a file, one rule per line, and the beginning of # is gaze.
|
||||
The sample file ip.limit, the rule format is as follows:
|
||||
`127.0.0.1:100:10240:http://192.168.1.1:3100`
|
||||
Rule interpretation:
|
||||
`127.0.0.1` is the IP to be restricted
|
||||
`100` is the maximum number of connections for this IP, not limited to write 0
|
||||
`10240` is the rate limit of IP single tcp connection, the unit is: byte / s, no limit write 0
|
||||
`http://192.168.1.1:3100` is the upstream used by this IP, and it is not left blank.
|
||||
|
||||
##### `--rate-limit`
|
||||
Limit the speed of each tcp connection of the service, for example: 100K 2000K 1M . 0 means unlimited, default 0.
|
||||
|
||||
## 11. Cluster
|
||||
|
||||
The proxy supports the cluster management. The proxy is installed on each machine node as an agent, with the control panel [`proxyadmin cluster edition`] (https://github.com/snail007/proxy-admin-cluster) Unified management of proxy services on massive machines.
|
||||
|
||||
If the proxy is to be run as an agent, assume that the cluster port address of the control panel is: `1.1.1.1: 55333`.
|
||||
|
||||
The command example is as follows:
|
||||
|
||||
`proxy agent -k xxx -c 1.1.1.1:55333 -i test`
|
||||
|
||||
Command explanation:
|
||||
|
||||
agent: is a function parameter, which means running agent mode.
|
||||
|
||||
-k : The encryption and decryption key for communication with `proxyadmin cluster edition`. This key is set in the configuration file of` proxyadmin cluster edition`.
|
||||
|
||||
-c : The cluster port address of `proxyadmin cluster edition`, format: IP:port.
|
||||
|
||||
-i : The unique identifier of the agent ensures that each agent is different. The "unique identifier" specified here is used when adding a node to the control panel. The IP is filled with this "unique identifier".
|
||||
If -i is not specified, the default is empty, and the control panel adds the IP field to fill in: the agent's internet IP.
|
||||
|
||||
-u: proxy parameter, empty by default. You can specify an agent, and the agent will communicate with the cluster through this agent.
|
||||
The format is the same as that of `--jumper`. For details, please refer to the `--jumper` part of the manual.
|
||||
|
||||
notice:
|
||||
|
||||
When the client service is configured in the control panel, all nodes use the same key, which leads to only one client working. To solve this problem,
|
||||
Client service parameters can use placeholders: `{AGENT_ID}` to refer to the agent’s id as the client’s key, so as to ensure that each client has a unique key.
|
||||
|
||||
For example, client service parameters:
|
||||
|
||||
`client -T tcp -P 1.1.1.1:30000 --k {AGENT_ID}`
|
||||
@@ -0,0 +1,1963 @@
|
||||
## 如何安装
|
||||
|
||||
### 1. Linux安装
|
||||
|
||||
[点击查看Linux安装教程](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E4%B8%8B%E8%BD%BD%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
### 2. 苹果Mac系统安装
|
||||
|
||||
[点击查看苹果Mac系统安装教程](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
### 3. Windows安装
|
||||
|
||||
为了方便操作,推荐Windows用户使用proxy-admin面板,[点击查看Windows安装教程](https://github.com/snail007/proxy_admin_free/blob/master/README_ZH.md#%E8%A7%86%E9%A2%91%E5%AE%89%E8%A3%85%E6%95%99%E7%A8%8B)
|
||||
|
||||
当然你也可以使用命令行goproxy[点击查看手动安装](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E6%89%8B%E5%8A%A8%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
### 4. 其它平台安装
|
||||
|
||||
[点击查看其它安装教程](https://github.com/snail007/goproxy/blob/master/README_ZH.md#%E6%89%8B%E5%8A%A8%E5%AE%89%E8%A3%85-goproxy)
|
||||
|
||||
## 免费版、商业版说明
|
||||
|
||||
本手册描述功能,`proxyadmin商业版`和`goproxy商业版`全部包含;认证等高级功能参数免费版和VIP控制面板不包含;
|
||||
|
||||
如果您用`goproxy免费版`执行某些命令或者`proxyadmin 免费版`、`proxyadmin VIP版`服务启动失败的时候遇到,类似如下xxx参数不存在的提示,说明这个参数是商业版的功能,您需要下载并购买商业版授权才能使用.
|
||||
` err : unknown short flag '-a'`
|
||||
|
||||
以下软件都是相互独立使用,没有依赖关系,需要购买的也是分别单独购买使用。
|
||||
|
||||
软件名称 | 免费版功能 | 商业版功能 | 购买使用 | 特点 | 传送门
|
||||
:----------- | :---: | :---: | :---: | :---: | :---:
|
||||
proxyadmin 免费版 | √ | x | x| Web界面操作,支持Linux,Windows,macOS,免费使用,服务数量有限制,适合个人,小白和白嫖党 | [下载安装](https://github.com/snail007/proxy_admin_free)
|
||||
proxyadmin VIP版 | √ | x | √| Web界面操作,支持更多平台,功能和免费版一样,服务数量无限制,适合个体户或者小集体 | [下载安装](https://github.com/snail007/proxy-admin-vip)
|
||||
proxyadmin 商业版 | √ | √ | √|Web界面操作,支持更多平台,无限制,适合集体或公司对外提供服务 | [下载安装](https://github.com/snail007/proxy-admin-commercial)
|
||||
proxyadmin 集群版| √ | √ | √|Web界面操作,支持Linux,Windows,macOS,无限制,配合`goproxy 商业版`,可以实现以组为单位,管理海量机器上的proxy服务,适合有大量机器的集体或公司对外提供服务 | [下载安装](https://github.com/snail007/proxy-admin-cluster)
|
||||
goproxy 免费版 | √ | x | x|命令行操作,全平台支持,免费使用,稳定且灵活,适合一切熟悉命令行的大佬或集体或公司白嫖,自用或者大规模部署对外服务 | [下载安装](https://github.com/snail007/goproxy)
|
||||
goproxy 商业版| √ | √ | √|命令行操作,全平台支持,稳定且灵活,适合集体或公司大规模部署对外提供服务 | [下载安装](https://github.com/snail007/goproxy)
|
||||
|
||||
关于免费版功能和商业版功能对比请看这里,[`免费版`和`商业版`功能对比](https://snail.gitee.io/proxy/page/free_vs_commercial/).
|
||||
|
||||
[商业版激活绑定教程](https://snail.gitee.io/proxy/page/free_vs_commercial/)
|
||||
|
||||
提示:
|
||||
|
||||
**免费和付费软件均没有额外技术支持,不按着手册操作的一切问题请自行解决。付费软件免费享有`手册功能`使用指导和`首次安装配置`指导。**
|
||||
|
||||
## FAQ
|
||||
|
||||
[别点我](https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/)
|
||||
|
||||
## 首次使用必看,谢谢!!!
|
||||
|
||||
### 1. 环境
|
||||
|
||||
该手册教程,默认系统是linux,程序是proxy;所有操作需要root权限;
|
||||
|
||||
如果你的是windows,请使用windows版本的proxy.exe即可。
|
||||
|
||||
### 2. 使用配置文件
|
||||
|
||||
接下来的教程都是通过命令行参数介绍使用方法,也可以通过读取配置文件获取参数。
|
||||
|
||||
具体格式是通过@符号指定配置文件,例如:proxy @configfile.txt
|
||||
|
||||
configfile.txt里面的格式是,第一行是子命令名称,第二行开始一行一个参数,
|
||||
|
||||
格式:`参数 参数值`,没有参数值的直接写参数,比如:--nolog
|
||||
|
||||
比如configfile.txt内容如下:
|
||||
|
||||
```shell
|
||||
http
|
||||
-t tcp
|
||||
-p :33080
|
||||
--forever
|
||||
```
|
||||
|
||||
### 3. 调试输出
|
||||
|
||||
默认情况下,日志输出的信息不包含文件行数,某些情况下为了排除程序问题,快速定位问题,
|
||||
|
||||
可以使用--debug参数,输出代码行数和毫秒时间。
|
||||
|
||||
### 4. 使用日志文件
|
||||
|
||||
默认情况下,日志是直接在控制台显示出来的,如果要保存到文件,可以使用--log参数,
|
||||
|
||||
比如: --log proxy.log,日志就会输出到proxy.log方便排除问题。
|
||||
|
||||
|
||||
### 5. 生成加密通讯需要的证书文件
|
||||
|
||||
http(s)代理、tcp代理、udp代理、socks5代理、内网穿透等功能和上级通讯的时候,为了安全我们采用TLS加密通讯,当然可以选择不加密通信通讯,本教程所有和上级通讯都采用加密,需要证书文件。
|
||||
|
||||
***所有端必须使用相同的proxy.crt和proxy.key***
|
||||
|
||||
1.通过下面的命令生成自签名的证书和key文件。
|
||||
`proxy keygen -C proxy`
|
||||
会在当前程序目录下面生成证书文件proxy.crt和key文件proxy.key。
|
||||
|
||||
2.通过下面的命令生,使用自签名证书proxy.crt和key文件proxy.key签发新证书:goproxy.crt和goproxy.key。
|
||||
`proxy keygen -s -C proxy -c goproxy`
|
||||
会在当前程序目录下面生成证书文件goproxy.crt和key文件goproxy.key。
|
||||
|
||||
3.默认情况下证书的里面的域名是随机的,可以使用`-n test.com`参数指定。
|
||||
|
||||
4.更多用法:`proxy keygen --help`。
|
||||
|
||||
### 6. 后台运行
|
||||
|
||||
默认执行proxy之后,如果要保持proxy运行,不能关闭命令行。
|
||||
|
||||
如果想在后台运行proxy,命令行可以关闭,只需要在命令最后加上--daemon参数即可。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080" --daemon`
|
||||
|
||||
### 7. 守护运行
|
||||
守护运行参数--forever,比如: `proxy http --forever` ,
|
||||
|
||||
proxy会fork子进程,然后监控子进程,如果子进程异常退出,5秒后重启子进程。
|
||||
|
||||
该参数配合后台运行参数--daemon和日志参数--log,可以保障proxy一直在后台执行不会因为意外退出,
|
||||
|
||||
而且可以通过日志文件看到proxy的输出日志内容。
|
||||
|
||||
比如: `proxy http -p ":9090" --forever --log proxy.log --daemon`
|
||||
|
||||
### 8. 安全建议
|
||||
|
||||
当VPS在nat设备后面,vps上网卡IP都是内网IP,这个时候可以通过-g参数添加vps的外网ip防止死循环。
|
||||
|
||||
假设你的vps外网ip是23.23.23.23,下面命令通过-g参数设置23.23.23.23
|
||||
|
||||
`proxy http -g "23.23.23.23"`
|
||||
|
||||
### 9. 负载均衡和高可用
|
||||
|
||||
HTTP(S)\SOCKS5\SPS\TCP代理支持上级负载均衡和高可用,多个上级重复-P参数即可。
|
||||
|
||||
负载均衡策略支持5种,可以通过`--lb-method`参数指定:
|
||||
|
||||
roundrobin 轮流使用
|
||||
|
||||
leastconn 使用最小连接数的
|
||||
|
||||
leasttime 使用连接时间最小的
|
||||
|
||||
hash 使用根据客户端地址计算出一个固定上级
|
||||
|
||||
weight 根据每个上级的权重和连接数情况,选择出一个上级
|
||||
|
||||
提示:
|
||||
|
||||
1.负载均衡检查时间间隔可以通过`--lb-retrytime`设置,单位毫秒
|
||||
|
||||
2.负载均衡连接超时时间可以通过`--lb-timeout`设置,单位毫秒
|
||||
|
||||
3.如果负载均衡策略是权重(weight),-P格式为:2.2.2.2:3880?w=1,1就是权重,大于0的整数。
|
||||
|
||||
4.如果负载均衡策略是hash,默认是根据客户端地址选择上级,可以通过开关`--lb-hashtarget`使用访问的目标地址选择上级。
|
||||
|
||||
5.TCP代理没有参数`--lb-hashtarget`.
|
||||
|
||||
6.默认是负载均衡+高可用模式,如果使用了参数`--lb-onlyha`就只使用高可用模式,依据负载均衡策略选择一个节点,之后就一直使用这个节点,直到这个节点不再存活,那么会依据负载均衡策略再选择一个节点使用,以此循环.
|
||||
|
||||
7.如果检查节点全部不再存活,那么每次连接都会随机选取一个节点使用.
|
||||
|
||||
### 10. 代理跳板跳转
|
||||
|
||||
http(s)代理,SPS代理,内网穿透,tcp代理都支持通过中间第三方代理连接上级,
|
||||
|
||||
参数是:--jumper,所有格式如下:
|
||||
|
||||
```text
|
||||
http://username:password@host:port
|
||||
http://host:port
|
||||
https://username:password@host:port
|
||||
https://host:port
|
||||
socks5://username:password@host:port
|
||||
socks5://host:port
|
||||
socks5s://username:password@host:port
|
||||
socks5s://host:port
|
||||
ss://method:password@host:port
|
||||
```
|
||||
|
||||
http,socks5代表的是普通的http和socks5代理。
|
||||
|
||||
https,socks5s代表的是通过tls保护的http和socks5代理,
|
||||
|
||||
也就是http代理 over TLS , socks over TLS。
|
||||
|
||||
### 11. 域名黑白名单
|
||||
|
||||
socks/http(s)/sps代理都支持域名黑白名单。
|
||||
|
||||
用--stop参数指定一个域名黑名单列表文件,那么当用户连接文件里面这些域名的时候连接就会被断开。
|
||||
|
||||
用--only参数指定一个域名白名单列表文件,那么当用户连接文件里面这些域名之外的域名的时候连接就会被断开。
|
||||
|
||||
如果同时设置了--stop和--only,那么只有--only会起作用。
|
||||
|
||||
黑白域名名单文件内容格式如下:
|
||||
|
||||
```text
|
||||
**.baidu.com
|
||||
*.taobao.com
|
||||
a.com
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
?.qq.com
|
||||
```
|
||||
|
||||
说明:
|
||||
|
||||
1.一行一个域名,域名写法支持通配符`*`和`?`,`*`代表任意个字符,`?`代表一个任意字符,
|
||||
|
||||
2.`**.baidu.com` 匹配无论是多少级所有后缀是`.baidu.com`的域名。
|
||||
|
||||
3.`*.taobao.com` 匹配后缀是`.taobao.com`的三级域名。
|
||||
|
||||
4.还可以直接是IP地址。
|
||||
|
||||
5.`#`开头的为注释。
|
||||
|
||||
### 12. 客户端IP黑白名单
|
||||
|
||||
socks/http(s)/sps/tcp/udp/dns/内网穿透bridge/内网穿透tbridge,都支持客户端IP黑白名单。
|
||||
|
||||
用--ip-deny参数指定一个客户端IP黑名单列表文件,那么当用户的IP在这个文件里面的时候连接就会被断开。
|
||||
|
||||
用--ip-allow参数指定一个客户端IP白名单列表文件,那么当用户的IP不在这个文件里面的时候连接就会被断开。
|
||||
|
||||
如果同时设置了--ip-deny和--ip-allow,那么只有--ip-allow会起作用。
|
||||
|
||||
客户端IP黑白名单文件内容格式如下:
|
||||
|
||||
```text
|
||||
192.168.1.1
|
||||
192.168.*.*
|
||||
192.168.1?.*
|
||||
```
|
||||
|
||||
说明:
|
||||
|
||||
1.一行一个域名,域名写法支持通配符`*`和`?`,`*`代表任意个字符,`?`代表一个任意字符。
|
||||
|
||||
2.`#`开头的为注释。
|
||||
|
||||
### 13. 协议加载文件
|
||||
|
||||
proxy的各种代理功能里面很多地方都有参数设置一个文件,比如:--blocked 指定一个直接走上级的域名列表文件,参数值是文件的路径,
|
||||
|
||||
如果参数支持协议加载文件,那么文件路径不仅可以是文件路径,还可以是:
|
||||
|
||||
a.“base64://”开头的base64编码的上面说明的文件内容,比如:base64://ajfpoajsdfa=
|
||||
|
||||
b.”str://“开头的英文逗号分割的多个,比如:str://xxx,yyy
|
||||
|
||||
proxy的blocked,direct,stop,only,hosts,resolve.rules,rewriter.rules,ip.allow,ip.deny 文件支持协议加载。
|
||||
|
||||
### 14. 客户端并发连接数
|
||||
|
||||
socks5\sps\http代理,控制客户端并发连接数参数是:`--max-conns-rate`,控制每秒客户端的最大连接数,默认20, 0为不限制.
|
||||
|
||||
### 15 监听多个端口
|
||||
|
||||
`tcp/http/socks/sps`支持同时监听多个端口以及范围端口。
|
||||
一般情况下监听一个端口就可以,不过如果需要同时监听多个两个端口,或者范围端口,那么-p参数是支持的,
|
||||
格式是:`-p 0.0.0.0:80,0.0.0.0:443,0.0.0.0:8000-9000,:5000-6000`,多个绑定用逗号分隔即可。
|
||||
|
||||
## 1.HTTP代理
|
||||
|
||||
### 1.1.普通一级HTTP代理
|
||||
|
||||

|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:38080"`
|
||||
|
||||
-p参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
### 1.2.普通二级HTTP代理
|
||||
|
||||

|
||||
|
||||
使用本地端口8090,假设上级HTTP代理是`22.22.22.22:8080`
|
||||
|
||||
`proxy http -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" `
|
||||
|
||||
我们还可以指定网站域名的黑白名单文件,一行一个域名,匹配规则是最右匹配,比如:baidu.com,匹配的是*.*.baidu.com,黑名单的域名直接走上级代理,白名单的域名不走上级代理。
|
||||
|
||||
`proxy http -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt`
|
||||
|
||||
### 1.3.HTTP二级代理(加密)
|
||||
|
||||
> 注意: 后面二级代理使用的`proxy.crt`和`proxy.key`应与一级代理一致
|
||||
|
||||

|
||||
一级HTTP代理(VPS,IP:22.22.22.22)
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
二级HTTP代理(本地Linux)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080。
|
||||
|
||||
二级HTTP代理(本地windows)
|
||||
`proxy.exe http -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
然后设置你的windos系统中,需要通过代理上网的程序的代理为http模式,地址为:127.0.0.1,端口为:8080,程序即可通过加密通道通过vps上网。
|
||||
|
||||
### 1.4.HTTP三级代理(加密)
|
||||

|
||||
一级HTTP代理VPS_01,IP:22.22.22.22
|
||||
`proxy http -t tls -p ":38080" -C proxy.crt -K proxy.key`
|
||||
二级HTTP代理VPS_02,IP:33.33.33.33
|
||||
`proxy http -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
三级HTTP代理(本地)
|
||||
`proxy http -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地的8080端口就是访问一级HTTP代理上面的代理端口38080。
|
||||
|
||||
### 1.5.Basic认证,API认证
|
||||
|
||||
请参考`9.API认证` 和 `10.本地认证`
|
||||
|
||||
### 1.6.HTTP代理流量强制走上级HTTP代理
|
||||
默认情况下,proxy会智能判断一个网站域名是否无法访问,如果无法访问才走上级HTTP代理.通过--always可以使全部HTTP代理流量强制走上级HTTP代理。
|
||||
`proxy http --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
|
||||
### 1.7.HTTP(S)通过SSH中转
|
||||

|
||||
说明:ssh中转的原理是利用了ssh的转发功能,就是你连接上ssh之后,可以通过ssh代理访问目标地址。
|
||||
假设有:vps
|
||||
- IP是2.2.2.2, ssh端口是22, ssh用户名是:user, ssh用户密码是:demo
|
||||
- 用户user的ssh私钥名称是user.key
|
||||
|
||||
#### *1.7.1 ssh用户名和密码的方式*
|
||||
本地HTTP(S)代理28080端口,执行:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080"`
|
||||
#### *1.7.2 ssh用户名和密钥的方式*
|
||||
本地HTTP(S)代理28080端口,执行:
|
||||
`proxy http -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080"`
|
||||
|
||||
### 1.8.KCP协议传输
|
||||

|
||||
KCP协议需要--kcp-key参数设置一个密码用于加密解密数据
|
||||
|
||||
一级HTTP代理(VPS,IP:22.22.22.22)
|
||||
`proxy http -t kcp -p ":38080" --kcp-key mypassword`
|
||||
|
||||
二级HTTP代理(本地Linux)
|
||||
`proxy http -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080,数据通过kcp协议传输,注意kcp走的是udp协议协议,所以防火墙需放开38080的udp协议。
|
||||
|
||||
### 1.9 HTTP(S)反向代理
|
||||

|
||||
proxy不仅支持在其他软件里面通过设置代理的方式,为其他软件提供代理服务,而且支持直接把请求的网站域名解析到proxy监听的ip上,然后proxy监听80和443端口,那么proxy就会自动为你代理访问需要访问的HTTP(S)网站。
|
||||
|
||||
使用方式:
|
||||
在"最后一级proxy代理"的机器上,因为proxy要伪装成所有网站,网站默认的端口HTTP是80,HTTPS是443,让proxy监听80和443端口即可.参数-p多个地址用逗号分割。
|
||||
`proxy http -t tcp -p :80,:443`
|
||||
|
||||
这个命令就在机器上启动了一个proxy代理,同时监听80和443端口,既可以当作普通的代理使用,也可以直接把需要代理的域名解析到这个机器的IP上。
|
||||
|
||||
如果有上级代理那么参照上面教程设置上级即可,使用方式完全一样。
|
||||
`proxy http -t tcp -p :80,:443 -T tls -P "2.2.2.2:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
注意:
|
||||
proxy所在的服务器的DNS解析结果不能受到自定义的解析影响,不然就死循环了,proxy代理最好指定`--dns 8.8.8.8`参数。
|
||||
|
||||
### 1.10 HTTP(S)透明代理
|
||||
该模式需要具有一定的网络基础,相关概念不懂的请自行搜索解决。
|
||||
假设proxy现在在路由器上运行,启动命令如下:
|
||||
`proxy http -t tcp -p :33080 -T tls -P "2.2.2.2:33090" -C proxy.crt -K proxy.key`
|
||||
|
||||
然后添加iptables规则,下面是参考规则:
|
||||
```shell
|
||||
#上级proxy服务端服务器IP地址:
|
||||
proxy_server_ip=2.2.2.2
|
||||
|
||||
#路由器运行proxy监听的端口:
|
||||
proxy_local_port=33080
|
||||
|
||||
#下面的就不用修改了
|
||||
#create a new chain named PROXY
|
||||
iptables -t nat -N PROXY
|
||||
|
||||
# Ignore your PROXY server's addresses
|
||||
# It's very IMPORTANT, just be careful。
|
||||
|
||||
iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
# Ignore LANs IP address
|
||||
iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
# Anything to port 80 443 should be redirected to PROXY's local port
|
||||
iptables -t nat -A PROXY -p tcp --dport 80 -j REDIRECT --to-ports $proxy_local_port
|
||||
iptables -t nat -A PROXY -p tcp --dport 443 -j REDIRECT --to-ports $proxy_local_port
|
||||
|
||||
# Apply the rules to nat client
|
||||
iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
# Apply the rules to localhost
|
||||
iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
- 清空整个链 iptables -F 链名比如iptables -t nat -F PROXY
|
||||
- 删除指定的用户自定义链 iptables -X 链名 比如 iptables -t nat -X PROXY
|
||||
- 从所选链中删除规则 iptables -D 链名 规则详情 比如 iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 1.11 自定义DNS
|
||||
--dns-address和--dns-ttl参数,用于自己指定proxy访问域名的时候使用的dns(--dns-address)
|
||||
以及解析结果缓存时间(--dns-ttl)秒数,避免系统dns对proxy的干扰,另外缓存功能还能减少dns解析时间提高访问速度。
|
||||
比如:
|
||||
`proxy http -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 1.12 自定义加密
|
||||
proxy的http(s)代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行自定义
|
||||
加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义一个密码即可,
|
||||
加密分为两个部分,一部分是本地(-z)是否加密解密,一部分是与上级(-Z)传输是否加密解密。
|
||||
自定义加密要求两端都是proxy才可以,下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
本地二级执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -z demo_password -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
本地三级执行:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
### 1.13 压缩传输
|
||||
proxy的http(s)代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,在自定义加密之前还可以对数据进行压缩,
|
||||
也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的,压缩分为两个部分,一部分是本地(-m)是否压缩传输,
|
||||
一部分是与上级(-M)传输是否压缩。
|
||||
压缩要求两端都是proxy才可以,压缩也在一定程度上保护了(加密)数据,下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
本地二级执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy http -t tcp -m -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy http -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
本地三级执行:
|
||||
`proxy http -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
### 1.14 负载均衡
|
||||
|
||||
HTTP(S)代理支持上级负载均衡,多个上级重复-P参数即可。
|
||||
|
||||
`proxy http --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080`
|
||||
|
||||
### 1.14.1 设置重试间隔和超时时间
|
||||
|
||||
`proxy http --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp -p :33080`
|
||||
|
||||
### 1.14.2 设置权重
|
||||
|
||||
`proxy http --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -t tcp -p :33080`
|
||||
|
||||
### 1.14.3 使用目标地址选择上级
|
||||
|
||||
`proxy http --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -t tcp -p :33080`
|
||||
|
||||
### 1.15 限速
|
||||
|
||||
限速100K,通过`-l`参数即可指定,比如:100K 2000K 1M . 0意味着无限制。
|
||||
|
||||
`proxy http -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 1.16 指定出口IP
|
||||
|
||||
`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy http -t tcp -p :33080 --bind-listen`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy http -t tcp -p 5.5.5.5:6666 --bind-listen`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy http -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 1.17 证书参数使用base64数据
|
||||
|
||||
默认情况下-C,-K参数是crt证书和key文件的路径,
|
||||
|
||||
如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
|
||||
### 1.18 智能模式
|
||||
智能模式设置,可以是intelligent|direct|parent三者之一。
|
||||
默认是:intelligent。
|
||||
每个值的含义如下:
|
||||
`--intelligent=direct`,不在blocked里面的目标都直连。
|
||||
`--intelligent=parent`,不在direct里面的目标都走上级。
|
||||
`--intelligent=intelligent`,blocked和direct里面都没有的目标,智能判断是否使用上级访问目标。
|
||||
|
||||
### 1.19 查看帮助
|
||||
`proxy help http`
|
||||
|
||||
## 2.TCP代理
|
||||
|
||||
### 2.1 普通一级TCP代理
|
||||

|
||||
本地执行:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22"`
|
||||
那么访问本地33080端口就是访问192.168.22.33的22端口。
|
||||
|
||||
`-p`参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
如果本地监听端口数量大于1,那么将会连接与本地端口一致的对应上级端口,忽略`-P`里面的端口。
|
||||
|
||||
如果需要所有端口进来的连接,都连接到上级指定端口,可以加上参数`--lock-port`。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:0"`
|
||||
|
||||
那么`33080`端口进来的连接,将会连接192.168.22.33的`33080`端口,其它端口以此类推,本地和上级端口一致,此时参数`-P`里面的端口用`0`。
|
||||
|
||||
如果想无论是`33080`,`33081`等端口进来的连接都连接到192.168.22.33的`22`端口,可以加上参数`--lock-port`
|
||||
|
||||
`proxy tcp -p ":33080-33085" -T tcp -P "192.168.22.33:22" --lock-port`
|
||||
|
||||
|
||||
### 2.2 普通二级TCP代理
|
||||

|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
本地执行:
|
||||
`proxy tcp -p ":23080" -T tcp -P "22.22.22.33:33080"`
|
||||
那么访问本地23080端口就是访问22.22.22.33的8080端口。
|
||||
|
||||
### 2.3 普通三级TCP代理
|
||||

|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -p ":38080" -T tcp -P "66.66.66.66:8080"`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
三级TCP代理(本地)
|
||||
`proxy tcp -p ":8080" -T tcp -P "33.33.33.33:28080"`
|
||||
那么访问本地8080端口就是通过加密TCP隧道访问66.66.66.66的8080端口。
|
||||
|
||||
### 2.4 加密二级TCP代理
|
||||

|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -t tls -p ":33080" -T tcp -P "127.0.0.1:8080" -C proxy.crt -K proxy.key`
|
||||
本地执行:
|
||||
`proxy tcp -p ":23080" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地23080端口就是通过加密TCP隧道访问22.22.22.33的8080端口。
|
||||
|
||||
### 2.5 加密三级TCP代理
|
||||

|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T tcp -P "66.66.66.66:8080" -C proxy.crt -K proxy.key`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
三级TCP代理(本地)
|
||||
`proxy tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地8080端口就是通过加密TCP隧道访问66.66.66.66的8080端口。
|
||||
|
||||
### 2.6 通过代理连接上级
|
||||
有时候proxy所在的网络不能直接访问外网,需要通过一个https或者socks5代理才能上网,那么这个时候
|
||||
-J参数就可以帮助你让proxy的tcp端口映射的时候通过https或者socks5代理去连接上级-P,将外部端口映射到本地。
|
||||
-J参数格式如下:
|
||||
|
||||
https代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
https://username:password@host:port
|
||||
代理不需要认证
|
||||
https://host:port
|
||||
|
||||
socks5代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
socks5://username:password@host:port
|
||||
代理不需要认证
|
||||
socks5://host:port
|
||||
|
||||
host:代理的IP或者域名
|
||||
port:代理的端口
|
||||
|
||||
### 2.7 指定出口IP
|
||||
|
||||
当TCP代理当上级类型(参数:-T)是tcp当时候,支持指定`出口IP`。`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy tcp -t tcp -p :33080 --bind-listen -T tcp -P 2.2.2.2:3322`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy tcp -t tcp -p 5.5.5.5:6666 --bind-listen -T tcp -P 2.2.2.2:3322`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy tcp -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888 -T tcp -P 2.2.2.2:3322`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 2.8 限速,限制连接数
|
||||
|
||||
参数`--max-conns`可以限制每个端口的最大连接数。
|
||||
比如限制每个端口最多1000个连接数:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --max-conns 1000`
|
||||
参数`--rate-limit`可以限制每个tcp连接的速率。
|
||||
比如限制每个tcp连接速率为100k/s:
|
||||
`proxy tcp -p ":33080" -T tcp -P "192.168.22.33:22" --rate-limit 100k`
|
||||
|
||||
### 2.9 压缩传输
|
||||
|
||||
`--c`控制本地和客户端之间是否压缩传输,默认false;`--C`控制本地和上级之间是否压缩传输,默认false。
|
||||
|
||||
示例:
|
||||
|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -t tcp --c -p ":33080" -T tcp -P "127.0.0.1:8080"`
|
||||
本地执行:
|
||||
`proxy tcp -t tcp -p ":23080" -T tcp -P "22.22.22.33:33080" --C`
|
||||
|
||||
### 2.10 查看帮助
|
||||
`proxy help tcp`
|
||||
|
||||
## 3.UDP代理
|
||||
|
||||
### 3.1.普通一级UDP代理
|
||||

|
||||
本地执行:
|
||||
`proxy udp -p ":5353" -T udp -P "8.8.8.8:53"`
|
||||
那么访问本地UDP:5353端口就是访问8.8.8.8的UDP:53端口。
|
||||
|
||||
`-p`参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
如果本地监听端口数量大于1,那么将会连接与本地端口一致的对应上级端口,忽略`-P`里面的端口。
|
||||
|
||||
如果需要所有端口进来的连接,都连接到上级指定端口,可以加上参数`--lock-port`。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:0"`
|
||||
|
||||
那么`33080`端口进来的连接,将会连接192.168.22.33的`33080`端口,其它端口以此类推,本地和上级端口一致,此时参数`-P`里面的端口用`0`。
|
||||
|
||||
如果想无论是`33080`,`33081`等端口进来的连接都连接到192.168.22.33的`2222`端口,可以加上参数`--lock-port`
|
||||
|
||||
`proxy udp -p ":33080-33085" -T udp -P "192.168.22.33:2222" --lock-port`
|
||||
|
||||
### 3.2.普通二级UDP代理
|
||||

|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -p ":33080" -T udp -P "8.8.8.8:53"`
|
||||
本地执行:
|
||||
`proxy udp -p ":5353" -T tcp -P "22.22.22.33:33080"`
|
||||
那么访问本地UDP:5353端口就是通过TCP隧道,通过VPS访问8.8.8.8的UDP:53端口。
|
||||
|
||||
### 3.3.普通三级UDP代理
|
||||

|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -p ":38080" -T udp -P "8.8.8.8:53"`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -p ":28080" -T tcp -P "22.22.22.22:38080"`
|
||||
三级TCP代理(本地)
|
||||
`proxy udp -p ":5353" -T tcp -P "33.33.33.33:28080"`
|
||||
那么访问本地5353端口就是通过TCP隧道,通过VPS访问8.8.8.8的53端口。
|
||||
|
||||
### 3.4.加密二级UDP代理
|
||||

|
||||
VPS(IP:22.22.22.33)执行:
|
||||
`proxy tcp -t tls -p ":33080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
本地执行:
|
||||
`proxy udp -p ":5353" -T tls -P "22.22.22.33:33080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地UDP:5353端口就是通过加密TCP隧道,通过VPS访问8.8.8.8的UDP:53端口。
|
||||
|
||||
### 3.5.加密三级UDP代理
|
||||

|
||||
一级TCP代理VPS_01,IP:22.22.22.22
|
||||
`proxy tcp -t tls -p ":38080" -T udp -P "8.8.8.8:53" -C proxy.crt -K proxy.key`
|
||||
二级TCP代理VPS_02,IP:33.33.33.33
|
||||
`proxy tcp -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key`
|
||||
三级TCP代理(本地)
|
||||
`proxy udp -p ":5353" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key`
|
||||
那么访问本地5353端口就是通过加密TCP隧道,通过VPS_01访问8.8.8.8的53端口。
|
||||
|
||||
### 3.6 指定出口IP
|
||||
|
||||
当UDP代理当上级类型(参数:-T)是udp当时候,支持指定`出口IP`。使用`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
`proxy udp -p ":33080" -T udp -P "192.168.22.33:2222" -B`
|
||||
|
||||
### 3.7 查看帮助
|
||||
`proxy help udp`
|
||||
|
||||
## 4.内网穿透
|
||||
### 4.1、原理说明
|
||||
内网穿透,分为两个版本,“多链接版本”和“多路复用版本”,一般像web服务这种不是长时间连接的服务建议用“多链接版本”,如果是要保持长时间连接建议使用“多路复用版本”。
|
||||
1. 多链接版本,对应的子命令是tserver,tclient,tbridge。
|
||||
1. 多路复用版本,对应的子命令是server,client,bridge。
|
||||
1. 多链接版本和多路复用版本的参数和使用方式完全一样。
|
||||
1. 多路复用版本的server,client可以开启压缩传输,参数是--c。
|
||||
1. server,client要么都开启压缩,要么都不开启,不能只开一个。
|
||||
|
||||
下面的教程以“多路复用版本”为例子,说明使用方法。
|
||||
内网穿透由三部分组成:client端,server端,bridge端;client和server主动连接bridge端进行桥接。
|
||||
|
||||
### 4.2、TCP普通用法
|
||||
背景:
|
||||
- 公司机器A提供了web服务80端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在家里能够通过访问VPS的28080端口访问到公司机器A的80端口
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.3、微信接口本地开发
|
||||
背景:
|
||||
- 自己的笔记本提供了nginx服务80端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在微信的开发帐号的网页回调接口配置里面填写地址:http://22.22.22.22/calback.php
|
||||
然后就可以访问到笔记本的80端口下面的calback.php,如果需要绑定域名,可以用自己的域名
|
||||
比如:wx-dev.xxx.com解析到22.22.22.22,然后在自己笔记本的nginx里
|
||||
配置域名wx-dev.xxx.com到具体的目录即可。
|
||||
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行,确保vps的80端口没被其它程序占用。
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":80@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在自己笔记本上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.4、UDP普通用法
|
||||
背景:
|
||||
- 公司机器A提供了DNS解析服务,UDP:53端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在家里能够通过设置本地dns为22.22.22.22,使用公司机器A进行域名解析服务。
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server --udp -r ":53@:53" -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.5、高级用法一
|
||||
背景:
|
||||
- 公司机器A提供了web服务80端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
为了安全,不想在VPS上能够访问到公司机器A,在家里能够通过访问本机的28080端口,
|
||||
通过加密隧道访问到公司机器A的80端口。
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在家里电脑上执行
|
||||
`proxy server -r ":28080@:80" -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.6、高级用法二
|
||||
提示:
|
||||
如果同时有多个client连接到同一个bridge,需要指定不同的key,可以通过--k参数设定,--k可以是任意唯一字符串,
|
||||
只要在同一个bridge上唯一即可。
|
||||
server连接到bridge的时候,如果同时有多个client连接到同一个bridge,需要使用--k参数选择client。
|
||||
暴露多个端口重复-r参数即可.-r格式是:"本地IP:本地端口@clientHOST:client端口"。
|
||||
|
||||
背景:
|
||||
- 公司机器A提供了web服务80端口,ftp服务21端口
|
||||
- 有VPS一个,公网IP:22.22.22.22
|
||||
|
||||
需求:
|
||||
在家里能够通过访问VPS的28080端口访问到公司机器A的80端口
|
||||
在家里能够通过访问VPS的29090端口访问到公司机器A的21端口
|
||||
|
||||
步骤:
|
||||
1. 在vps上执行
|
||||
`proxy bridge -p ":33080" -C proxy.crt -K proxy.key`
|
||||
`proxy server -r ":28080@:80" -r ":29090@:21" --k test -P "127.0.0.1:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 在公司机器A上面执行
|
||||
`proxy client --k test -P "22.22.22.22:33080" -C proxy.crt -K proxy.key`
|
||||
|
||||
1. 完成
|
||||
|
||||
### 4.7.server的-r参数
|
||||
-r完整格式是:`PROTOCOL://LOCAL_IP:LOCAL_PORT@[CLIENT_KEY]CLIENT_LOCAL_HOST:CLIENT_LOCAL_PORT`
|
||||
|
||||
4.7.1.协议PROTOCOL:tcp、udp、ptcp、pudp。
|
||||
比如: `-r "udp://:10053@:53" -r "tcp://:10800@:1080" -r ":8080@:80"`
|
||||
如果指定了--udp参数,PROTOCOL默认为udp,那么:`-r ":8080@:80"`默认为udp;
|
||||
如果没有指定--udp参数,PROTOCOL默认为tcp,那么:`-r ":8080@:80"`默认为tcp;
|
||||
|
||||
4.7.2.CLIENT_KEY:默认是default。
|
||||
比如: -r "udp://:10053@[test1]:53" -r "tcp://:10800@[test2]:1080" -r ":8080@:80"
|
||||
如果指定了--k参数,比如--k test,那么:`-r ":8080@:80"`CLIENT_KEY默认为test;
|
||||
如果没有指定--k参数,那么:`-r ":8080@:80"`CLIENT_KEY默认为default;
|
||||
|
||||
4.7.3.LOCAL_IP为空默认是:`0.0.0.0`,CLIENT_LOCAL_HOST为空默认是:`127.0.0.1`;
|
||||
|
||||
### 4.8.server和client通过代理连接bridge
|
||||
有时候server或者client所在的网络不能直接访问外网,需要通过一个https或者socks5代理才能上网,那么这个时候
|
||||
-J参数就可以帮助你让server或者client通过https或者socks5代理去连接bridge。
|
||||
-J参数格式如下:
|
||||
|
||||
https代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
https://username:password@host:port
|
||||
代理不需要认证
|
||||
https://host:port
|
||||
|
||||
socks5代理写法:
|
||||
代理需要认证,用户名:username 密码:password
|
||||
socks5://username:password@host:port
|
||||
代理不需要认证
|
||||
socks5://host:port
|
||||
|
||||
host:代理的IP或者域名
|
||||
port:代理的端口
|
||||
|
||||
### 4.9.内网穿透HTTP服务
|
||||
|
||||
通常HTTP请求客户端会使用server的ip和端口去设置HOST字段,但是与期望的后端实际HOST不一样,这样就造成了tcp是通的, 但后端依赖HOST字段定位虚拟主机就不能工作.现在用`--http-host`参数强制设置http头部的HOST字段值为后端实际的域名和端口即可轻松解决,另外使用了`--http-host`参数之后,会在每个HTTP请求的头部增加两个头部 `X-Forwarded-For` 和 `X-Real-IP` 值是客户端IP, 这样后端http服务就能方便的获取用户端真实IP地址。
|
||||
|
||||
`server`的--http-host参数格式如下:
|
||||
|
||||
`--http-host www.test.com:80@2200`,如果server监听多个端口,只需要重复`--http-host`参数设置每个端口的HOST即可。
|
||||
|
||||
实例:
|
||||
|
||||
比如client本地nginx,127.0.0.1:80提供了web服务,其中绑定了一个域名`local.com`。
|
||||
|
||||
那么server的启动参数可以如下:
|
||||
|
||||
`proxy server -P :30000 -r :2500@127.0.0.1:80 --http-host local.com@2500`
|
||||
|
||||
解释:
|
||||
|
||||
`-r :2500@127.0.0.1:80` 和 `--http-host local.com:80@2500` 里面的2500端口是server本地监听的端口
|
||||
|
||||
当使用http协议请求server的ip:2500端口的时候,http的头部HOST字段就会被设置为`local.com`。
|
||||
|
||||
另外只有设置了`--http-host`参数
|
||||
|
||||
|
||||
### 4.10 关于流量统计
|
||||
|
||||
如果单独启动一个server对接上级是proxy-admin控制面板,需要在上级控制面板里面新建一个映射,获得个映射规则的ID,
|
||||
|
||||
然后启动server的时候加上参数 --server-id=映射规则的ID 才能统计到流量。
|
||||
|
||||
### 4.11 关于p2p
|
||||
内网穿透支持在server和client网络情况满足的情况下,server和client之间通过p2p直接连接,开启方法是:
|
||||
|
||||
在启动bridge,server,client到时候都加上`--p2p`参数即可。server的-r参数可以针对端口是否启用p2p(ptcp和pudp)。
|
||||
|
||||
如果server和client之间p2p打洞失败,那么会自动切换使用bridge中转传输数据。
|
||||
|
||||
### 4.12 客户端key白名单
|
||||
内网穿透bridge可以设置客户端key白名单,参数是--client-keys,格式可以是:
|
||||
|
||||
a.文件名,文件内容一行一个客户端key只能包含数字字母下划线,也就是客户端启动参数--k的值,只有客户端key在此白名单的客户端才能连接。# 开头的行,为注释。
|
||||
|
||||
b.“base64://”开头的base64编码的上面a说明的文件内容,比如:base64://ajfpoajsdfa=
|
||||
|
||||
c.”str://“开头的英文逗号分割的多个key,比如:str://default,company,school
|
||||
|
||||
默认是空,允许所有key。
|
||||
|
||||
### 4.13 网络NAT类型判断
|
||||
|
||||
nat类型判断,方便查看网络是否支持p2p,可以执行:`proxy tools -a nattype`
|
||||
|
||||
### 4.14 查看帮助
|
||||
`proxy help bridge`
|
||||
`proxy help server`
|
||||
`proxy help client`
|
||||
|
||||
## 5.SOCKS5代理
|
||||
提示:
|
||||
|
||||
SOCKS5代理,支持CONNECT,UDP协议,不支持BIND,支持用户名密码认证。
|
||||
|
||||
***如果你的VPS是阿里云,腾讯云这种VPS,就是ifconfig看不见你的公网IP,只能看见内网IP,***
|
||||
|
||||
***那么需要加上`-g VPS公网IP`参数,SOCKS5代理的UDP功能才能正常工作。***
|
||||
|
||||
***socks5的udp功能默认关闭,可以通过--udp开启,默认是握手随机端口,可以通过固定一个端口提高性能,
|
||||
通过参数--udp-port 0设置,0代表随机选择一个空闲端口,也可以手动指定一个具体端口。***
|
||||
|
||||
### 5.1 普通SOCKS5代理
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080" --udp-port 0 --udp`
|
||||
|
||||
-p参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
### 5.2.普通二级SOCKS5代理
|
||||

|
||||
使用本地端口8090,假设上级SOCKS5代理是`22.22.22.22:8080`
|
||||
`proxy socks -t tcp -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" --udp-port 0 --udp`
|
||||
我们还可以指定网站域名的黑白名单文件,一行一个域名,匹配规则是最右匹配,比如:baidu.com,匹配的是*.*.baidu.com,黑名单的域名域名直接走上级代理,白名单的域名不走上级代理;如果域名即在黑名单又在白名单中,那么黑名单起作用。
|
||||
`proxy socks -p "0.0.0.0:8090" -T tcp -P "22.22.22.22:8080" -b blocked.txt -d direct.txt --udp-port 0 --udp`
|
||||
|
||||
### 5.3.SOCKS二级代理(加密)
|
||||

|
||||
一级SOCKS代理(VPS,IP:22.22.22.22)
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
|
||||
二级SOCKS代理(本地Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080。
|
||||
|
||||
二级SOCKS代理(本地windows)
|
||||
`proxy.exe socks -t tcp -p ":8080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
然后设置你的windos系统中,需要通过代理上网的程序的代理为socks5模式,地址为:127.0.0.1,端口为:8080,程序即可通过加密通道通过vps上网。
|
||||
|
||||
### 5.4.SOCKS三级代理(加密)
|
||||

|
||||
一级SOCKS代理VPS_01,IP:22.22.22.22
|
||||
`proxy socks -t tls -p ":38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
二级SOCKS代理VPS_02,IP:33.33.33.33
|
||||
`proxy socks -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
三级SOCKS代理(本地)
|
||||
`proxy socks -t tcp -p ":8080" -T tls -P "33.33.33.33:28080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
那么访问本地的8080端口就是访问一级SOCKS代理上面的代理端口38080。
|
||||
|
||||
### 5.5.SOCKS代理流量强制走上级SOCKS代理
|
||||
默认情况下,proxy会智能判断一个网站域名是否无法访问,如果无法访问才走上级SOCKS代理.通过--always可以使全部SOCKS代理流量强制走上级SOCKS代理。
|
||||
`proxy socks --always -t tls -p ":28080" -T tls -P "22.22.22.22:38080" -C proxy.crt -K proxy.key --udp-port 0 --udp`
|
||||
|
||||
### 5.6.SOCKS通过SSH中转
|
||||

|
||||
说明:ssh中转的原理是利用了ssh的转发功能,就是你连接上ssh之后,可以通过ssh代理访问目标地址。
|
||||
假设有:vps
|
||||
- IP是2.2.2.2, ssh端口是22, ssh用户名是:user, ssh用户密码是:demo
|
||||
- 用户user的ssh私钥名称是user.key
|
||||
|
||||
#### *5.6.1 ssh用户名和密码的方式*
|
||||
本地SOCKS5代理28080端口,执行:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -D demo -t tcp -p ":28080" --udp-port 0 --udp`
|
||||
#### *5.6.2 ssh用户名和密钥的方式*
|
||||
本地SOCKS5代理28080端口,执行:
|
||||
`proxy socks -T ssh -P "2.2.2.2:22" -u user -S user.key -t tcp -p ":28080" --udp-port 0 --udp`
|
||||
|
||||
那么访问本地的28080端口就是通过VPS访问目标地址。
|
||||
|
||||
### 5.7.认证
|
||||
对于socks5代理协议我们可以进行用户名密码认证,认证的用户名和密码可以在命令行指定
|
||||
`proxy socks -t tcp -p ":33080" -a "user1:pass1" -a "user2:pass2"`
|
||||
多个用户,重复-a参数即可。
|
||||
也可以放在文件中,格式是一行一个"用户名:密码",然后用-F指定。
|
||||
`proxy socks -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
### 5.8.KCP协议传输
|
||||
KCP协议需要--kcp-key参数设置一个密码用于加密解密数据
|
||||
|
||||
一级HTTP代理(VPS,IP:22.22.22.22)
|
||||
`proxy socks -t kcp -p ":38080" --kcp-key mypassword -g 22.22.22.22`
|
||||
|
||||
二级HTTP代理(本地Linux)
|
||||
`proxy socks -t tcp -p ":8080" -T kcp -P "22.22.22.22:38080" --kcp-key mypassword`
|
||||
那么访问本地的8080端口就是访问VPS上面的代理端口38080,数据通过kcp协议传输。
|
||||
|
||||
提示:
|
||||
|
||||
当本地使用kcp协议时,需要用-g指定vps公网IP,socks5的UDP功能才能正常使用.这时-g是返回给客户端的UDP地址中的IP地址.
|
||||
|
||||
### 5.9.自定义DNS
|
||||
--dns-address和--dns-ttl参数,用于自己指定proxy访问域名的时候使用的dns(--dns-address)
|
||||
以及解析结果缓存时间(--dns-ttl)秒数,避免系统dns对proxy的干扰,另外缓存功能还能减少dns解析时间提高访问速度。
|
||||
比如:
|
||||
`proxy socks -p ":33080" --dns-address "8.8.8.8:53" --dns-ttl 300`
|
||||
|
||||
### 5.10 自定义加密
|
||||
proxy的socks代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行自定义加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义一个密码即可,
|
||||
加密分为两个部分,一部分是本地(-z)是否加密解密,一部分是与上级(-Z)传输是否加密解密。
|
||||
|
||||
自定义加密要求两端都是proxy才可以。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
本地二级执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -z demo_password -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
本地三级执行:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
### 5.11 压缩传输
|
||||
proxy的socks代理在tcp之上可以通过自定义加密和tls标准加密以及kcp协议加密tcp数据,在自定义加密之前还可以
|
||||
对数据进行压缩,也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的,压缩分为两个部分,
|
||||
一部分是本地(-m)是否压缩传输,一部分是与上级(-M)传输是否压缩。
|
||||
|
||||
压缩要求两端都是proxy才可以,压缩也在一定程度上保护了(加密)数据。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
本地二级执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy socks -t tcp -m -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy socks -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
本地三级执行:
|
||||
`proxy socks -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
### 5.12 负载均衡
|
||||
|
||||
SOCKS代理支持上级负载均衡,多个上级重复-P参数即可。
|
||||
|
||||
`proxy socks --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.1 设置重试间隔和超时时间
|
||||
|
||||
`proxy socks --lb-method=leastconn --lb-retrytime 300 --lb-timeout 300 -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.2 设置权重
|
||||
|
||||
`proxy socks --lb-method=weight -T tcp -P 1.1.1.1:33080?w=1 -P 2.1.1.1:33080?w=2 -P 3.1.1.1:33080?w=1 -p :33080 -t tcp`
|
||||
|
||||
### 5.12.3 使用目标地址选择上级
|
||||
|
||||
`proxy socks --lb-hashtarget --lb-method=hash -T tcp -P 1.1.1.1:33080 -P 2.1.1.1:33080 -P 3.1.1.1:33080 -p :33080 -t tcp`
|
||||
|
||||
### 5.13 限速
|
||||
|
||||
限速100K,通过`-l`参数即可指定,比如:100K 2000K 1M . 0意味着无限制。
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -l 100K`
|
||||
|
||||
### 5.14 指定出口IP
|
||||
|
||||
`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy socks -t tcp -p :33080 --bind-listen`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy socks -t tcp -p 5.5.5.5:6666 --bind-listen`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy socks -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 5.15 级联认证
|
||||
|
||||
SOCKS5支持级联认证,-A可以设置上级认证信息。
|
||||
|
||||
上级:
|
||||
|
||||
`proxy socks -t tcp -p 2.2.2.2:33080 -a user:pass`
|
||||
|
||||
本地:
|
||||
|
||||
`proxy socks -T tcp -P 2.2.2.2:33080 -A user:pass -t tcp -p :33080`
|
||||
|
||||
请更多认证细节,请参考`9.API认证` 和 `10.本地认证`
|
||||
|
||||
### 5.16 证书参数使用base64数据
|
||||
|
||||
默认情况下-C,-K参数是crt证书和key文件的路径,
|
||||
|
||||
如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
|
||||
|
||||
### 5.17 智能模式
|
||||
智能模式设置,可以是intelligent|direct|parent三者之一。
|
||||
默认是:intelligent。
|
||||
每个值的含义如下:
|
||||
`--intelligent=direct`,不在blocked里面的目标都直连。
|
||||
`--intelligent=parent`,不在direct里面的目标都走上级。
|
||||
`--intelligent=intelligent`,blocked和direct里面都没有的目标,智能判断是否使用上级访问目标。
|
||||
|
||||
### 5.18 固定UDP功能端口
|
||||
|
||||
默认情况下socks5的UDP功能的端口号,proxy是按着`rfc1982草案`要求,使用协议握手过程中随机指定,不需要提前指定。
|
||||
|
||||
但是某些情况下,需要固定UDP功能端口,可以通过参数`--udp-port 端口号`用来固定UDP功能的端口号,比如:
|
||||
|
||||
`proxy socks -t tcp -p "0.0.0.0:38080" --udp-port 38080`
|
||||
|
||||
### 5.19 查看帮助
|
||||
`proxy help socks`
|
||||
|
||||
## 6.SPS协议转换
|
||||
|
||||
### 6.1 功能介绍
|
||||
代理协议转换使用的是sps子命令,sps可以把已经存在的http(s)代理或者socks5代理或ss代理转换为一个端口同时支持http(s)和socks5和ss的代理,而且http(s)代理支持正向代理和反向代理(SNI),当上级是SOCKS5时,转换后的SOCKS5或者SS代理仍然支持UDP功能;另外对于已经存在的http(s)代理或者socks5代理,支持tls、tcp、kcp三种模式,支持链式连接,也就是可以多个sps结点层级连接构建加密通道。
|
||||
|
||||
`ss`功能支持的加密方法为:aes-128-cfb , aes-128-ctr , aes-128-gcm , aes-192-cfb , aes-192-ctr , aes-192-gcm , aes-256-cfb , aes-256-ctr , aes-256-gcm , bf-cfb , cast5-cfb , chacha20 , chacha20-ietf , chacha20-ietf-poly1305 , des-cfb , rc4-md5 , rc4-md5-6 , salsa20 , xchacha20
|
||||
|
||||
本地监听端口-p参数支持的写法:
|
||||
|
||||
```text
|
||||
-p ":8081" 监听8081
|
||||
-p ":8081,:8082" 监听8081和8082
|
||||
-p ":8081,:8082,:9000-9999" 监听8081和8082以及9000,9001至9999,共1002个端口
|
||||
```
|
||||
|
||||
提示:
|
||||
|
||||
当本地使用kcp协议时,需要用-g指定vps公网IP,socks5的UDP功能才能正常使用.这时-g是返回给客户端的UDP地址中的IP地址.
|
||||
|
||||
ss的udp功能默认关闭,可以通过--ssudp开启。socks5的udp功能默认关闭,可以通过--udp开启,默认是握手随机端口,可以通过固定一个端口提高性能,
|
||||
通过参数--udp-port 0设置,0代表随机选择一个空闲端口,也可以手动指定一个具体端口。
|
||||
|
||||
### 6.2 HTTP(S)转HTTP(S)+SOCKS5+SS
|
||||
转换后的SOCKS5或者SS代理不具备UDP功能。
|
||||
假设已经存在一个普通的http(s)代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个tls的http(s)代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,tls需要证书文件,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S http -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个kcp的http(s)代理(密码是:demo123):127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S http -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.3 SOCKS5转HTTP(S)+SOCKS5+SS
|
||||
如果上级是SOCKS5而且支持UDP功能,那么转换后的SOCKS5或者SS代理仍然支持UDP功能。
|
||||
假设已经存在一个普通的socks5代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S socks -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个tls的socks5代理:127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,tls需要证书文件,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S socks -T tls -P 127.0.0.1:8080 -t tcp -p :18080 -C proxy.crt -K proxy.key -h aes-192-cfb -j pass`
|
||||
|
||||
假设已经存在一个kcp的socks5代理(密码是:demo123):127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S socks -T kcp -P 127.0.0.1:8080 -t tcp -p :18080 --kcp-key demo123 -h aes-192-cfb -j pass`
|
||||
|
||||
### 6.4 SS转HTTP(S)+SOCKS5+SS
|
||||
SPS上级和本地支持ss协议,上级可以是SPS或者标准的ss服务,转换后的SOCKS5或者SS代理不具备UDP功能。
|
||||
假设已经存在一个普通的SS或者SPS代理(开启了ss,加密方式:aes-256-cfb,密码:demo):127.0.0.1:8080,现在我们把它转为同时支持http(s)和socks5和ss的普通代理,转换后的本地端口为18080,转换后的ss加密方式:aes-192-cfb,ss密码:pass。
|
||||
命令如下:
|
||||
`proxy sps -S ss -H aes-256-cfb -J pass -T tcp -P 127.0.0.1:8080 -t tcp -p :18080 -h aes-192-cfb -j pass`。
|
||||
|
||||
### 6.5 链式连接
|
||||

|
||||
上面提过多个sps结点可以层级连接构建加密通道,假设有如下vps和家里的pc电脑。
|
||||
vps01:2.2.2.2
|
||||
vps02:3.3.3.3
|
||||
现在我们想利用pc和vps01和vps02构建一个加密通道,本例子用tls加密也可以用kcp,在pc上访问本地18080端口就是访问vps01的本地8080端口。
|
||||
首先在vps01(2.2.2.2)上我们运行一个只有本地可以访问的http(s)代理,执行:
|
||||
`proxy http -t tcp -p 127.0.0.1:8080`
|
||||
|
||||
然后在vps01(2.2.2.2)上运行一个sps结点,执行:
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tls -p :8081 -C proxy.crt -K proxy.key`
|
||||
|
||||
然后在vps02(3.3.3.3)上运行一个sps结点,执行:
|
||||
`proxy sps -S http -T tls -P 2.2.2.2:8081 -t tls -p :8082 -C proxy.crt -K proxy.key`
|
||||
|
||||
然后在pc上运行一个sps结点,执行:
|
||||
`proxy sps -S http -T tls -P 3.3.3.3:8082 -t tcp -p :18080 -C proxy.crt -K proxy.key`
|
||||
|
||||
完成。
|
||||
|
||||
### 6.6 认证功能
|
||||
sps支持http(s)\socks5代理认证,可以级联认证,有四个重要的信息:
|
||||
1:用户发送认证信息`user-auth`。
|
||||
2:设置的本地认证信息`local-auth`。
|
||||
3:设置的连接上级使用的认证信息`parent-auth`。
|
||||
4:最终发送给上级的认证信息`auth-info-to-parent`。
|
||||
他们的情况关系如下:
|
||||
|
||||
| user-auth | local-auth | parent-auth | auth-info-to-paren
|
||||
| ------ | ------ | ------ | ------
|
||||
| 有/没有 | 有 | 有 | 来自parent-auth
|
||||
| 有/没有 | 没有 | 有 | 来自parent-auth
|
||||
| 有/没有 | 有 | 没有 | 无
|
||||
| 没有 | 没有 | 没有 | 无
|
||||
| 有 | 没有 | 没有 | 来自user-auth
|
||||
|
||||
对于sps代理我们可以进行用户名密码认证,认证的用户名和密码可以在命令行指定
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0:0:"`
|
||||
多个用户,重复-a参数即可。
|
||||
也可以放在文件中,格式是一行一个`用户名:密码:连接数:速率:上级`,然后用-F指定。
|
||||
`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -F auth-file.txt`
|
||||
|
||||
如果上级有认证,下级可以通过-A参数设置认证信息,比如:
|
||||
上级:`proxy sps -S http -T tcp -P 127.0.0.1:8080 -t tcp -p ":33080" -a "user1:pass1:0:0:" -a "user2:pass2:0:0:"`
|
||||
下级:`proxy sps -S http -T tcp -P 127.0.0.1:8080 -A "user1:pass1" -t tcp -p ":33080" `
|
||||
|
||||
请更多认证细节,请参考`9.API认证` 和 `10.本地认证`
|
||||
|
||||
### 6.7 多个上级
|
||||
|
||||
如果存在多个上级,可以通过多个-P指定。
|
||||
|
||||
比如:
|
||||
|
||||
`proxy sps -P http://127.0.0.1:3100 -P socks5://127.0.0.1:3200`
|
||||
|
||||
`-P`完整格式如下:
|
||||
|
||||
`protocol://a:b@2.2.2.2:33080#1`
|
||||
|
||||
下面对每部分进行解释:
|
||||
|
||||
`protocol://` 是协议类型,可能的类型以及含有如下:
|
||||
|
||||
```text
|
||||
http 等价于 -S http -T tcp
|
||||
https 等价于 -S http -T tls --parent-tls-single , 也就是http(s)代理 over TLS
|
||||
https2 等价于 -S http -T tls
|
||||
socks5 等价于 -S socks -T tcp
|
||||
socks5s 等价于 -S socks -T tls --parent-tls-single , 也就是socks over TLS
|
||||
socks5s2 等价于 -S socks -T tls
|
||||
ss 等价于 -S ss -T tcp
|
||||
httpws 等价于 -S http -T ws
|
||||
httpwss 等价于 -S http -T wss
|
||||
socks5ws 等价于 -S socks -T ws
|
||||
socks5wss 等价于 -S socks -T wss
|
||||
```
|
||||
|
||||
`a:b`是代理认证的用户名密码,如果是ss,`a`是加密方法,`b`是密码,没有用户名密码可以留空比如:`http://2.2.2.2:33080`,如果用户名和密码保护特殊符号可以使用urlencode进行编码。
|
||||
|
||||
`2.2.2.2:33080`是上级地址,格式是:`IP(或域名):端口`,如果底层是ws/wss协议还可以带上路径,比如:`2.2.2.2:33080/ws`;
|
||||
还能通过附加查询参数`m`和`k`设置`ws\wss`的`加密方法`和`密码`,比如:`2.2.2.2:33080/ws?m=aes-192-cfb&k=password`
|
||||
|
||||
`#1`多个上级的负载均衡是权重策略时候,设置的权重,很少用到。
|
||||
|
||||
### 6.8 自定义加密
|
||||
proxy的sps代理在tcp之上可以通过tls标准加密以及kcp协议加密tcp数据,除此之外还支持在tls和kcp之后进行
|
||||
自定义加密,也就是说自定义加密和tls|kcp是可以联合使用的,内部采用AES256加密,使用的时候只需要自己定义
|
||||
一个密码即可,加密分为两个部分,一部分是本地(-z)是否加密解密,一部分是与上级(-Z)传输是否加密解密。
|
||||
|
||||
自定义加密要求两端都是proxy才可以。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
假设已经存在一个http(s)代理:`6.6.6.6:6666`
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
本地二级执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -Z demo_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -S http -T tcp -P 6.6.6.6:6666 -t tcp -z demo_password -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -Z demo_password -t tcp -z other_password -p :8888`
|
||||
本地三级执行:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -Z other_password -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级加密传输访问目标网站。
|
||||
|
||||
### 6.9 压缩传输
|
||||
proxy的sps代理在tcp之上可以通过自定义加密和tls标准加密以及kcp协议加密tcp数据,在自定义加密之前还可以
|
||||
对数据进行压缩,也就是说压缩功能和自定义加密和tls|kcp是可以联合使用的,压缩分为两个部分,
|
||||
一部分是本地(-m)是否压缩传输,一部分是与上级(-M)传输是否压缩。
|
||||
|
||||
压缩要求两端都是proxy才可以,压缩也在一定程度上保护了(加密)数据。
|
||||
|
||||
下面分别用二级,三级为例:
|
||||
|
||||
二级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
本地二级执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:777 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
|
||||
三级实例
|
||||
|
||||
一级vps(ip:2.2.2.2)上执行:
|
||||
`proxy sps -t tcp -m -p :7777`
|
||||
二级vps(ip:3.3.3.3)上执行:
|
||||
`proxy sps -T tcp -P 2.2.2.2:7777 -M -t tcp -m -p :8888`
|
||||
本地三级执行:
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080`
|
||||
这样通过本地代理8080访问网站的时候就是通过与上级压缩传输访问目标网站。
|
||||
|
||||
### 6.10 禁用协议
|
||||
SPS默认情况下一个端口支持http(s)和socks5两种代理协议,我们可以通过参数禁用某个协议
|
||||
比如:
|
||||
1.禁用HTTP(S)代理功能只保留SOCKS5代理功能,参数:`--disable-http`。
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-http`
|
||||
|
||||
1.禁用SOCKS5代理功能只保留HTTP(S)代理功能,参数:`--disable-socks`。
|
||||
`proxy sps -T tcp -P 3.3.3.3:8888 -M -t tcp -p :8080 --disable-socks`
|
||||
|
||||
### 6.11 限速
|
||||
|
||||
假设存在SOCKS5上级:
|
||||
|
||||
`proxy socks -p 2.2.2.2:33080 -z password -t tcp`
|
||||
|
||||
sps下级,限速100K
|
||||
|
||||
`proxy sps -S socks -P 2.2.2.2:33080 -T tcp -Z password -l 100K -t tcp -p :33080`
|
||||
|
||||
通过`-l`参数即可指定,比如:100K 2000K 1M . 0意味着无限制。
|
||||
|
||||
### 6.12 指定出口IP
|
||||
|
||||
`--bind-listen`参数,就可以开启客户端用`入口IP`连接过来的,就用`入口IP`作为`出口IP`访问目标网站的功能。如果绑定了不正确的IP会导致代理不能工作。
|
||||
|
||||
普通多IP用法:
|
||||
|
||||
`proxy sps -t tcp -p :33080 --bind-listen`
|
||||
|
||||
上面的写法适合本机有大量IP,不想一个一个单独写,比如本机有IP`3.3.3.3`,当客户端使用`3.3.3.3`连接代理,那么`3.3.3.3`就会作为客户端的出口IP,
|
||||
这里的`3.3.3.3`就是`入口IP`和`出口IP`,你会发现`入口IP`和`出口IP`是一样的,`--bind-listen`这种模式人为不能干预`入口IP`和`出口IP`。
|
||||
|
||||
单独用法:
|
||||
|
||||
本机有IP:`5.5.5.5`,开一个代理端口`6666`,凡是通过`5.5.5.5:6666`端口进来的,都使用`5.5.5.5`作为出口IP。
|
||||
|
||||
命令如下:
|
||||
|
||||
`proxy sps -t tcp -p 5.5.5.5:6666 --bind-listen`
|
||||
|
||||
#### 自由指定出口IP
|
||||
|
||||
上面的`--bind-listen`参数虽然可以指定出口IP,但是`入口IP`和`出口IP`不能人为干预。如果想入口IP和出口IP不一样,
|
||||
可以使用`--bind-ip`参数,格式:`IP:端口`,比如: `1.1.1.1:8080`,`[2000:0:0:0:0:0:0:1]:8080`。
|
||||
多个绑定需求,可以重复`--bind-ip`参数即可。
|
||||
|
||||
比如本机有IP`5.5.5.5`,`6.6.6.6`,监听了`8888`和`7777`两个端口,命令如下:
|
||||
|
||||
`proxy sps -t tcp -p :8888,:7777 --bind-ip 5.5.5.5:7777 --bind-ip 6.6.6.6:8888`
|
||||
|
||||
那么客户端访问`7777`端口,出口IP就是`5.5.5.5`,访问`8888`端口,出口IP就是`6.6.6.6`,如果同时设置了`--bind-ip`和`--bind-listen`,`--bind-ip`的优先级更高。
|
||||
|
||||
### 6.13 证书参数使用base64数据
|
||||
|
||||
默认情况下-C,-K参数是crt证书和key文件的路径,
|
||||
|
||||
如果是base64://开头,那么就认为后面的数据是base64编码的,会解码后使用。
|
||||
|
||||
### 6.14 独立服务
|
||||
sps一个端口可完成完整功能的代理`http(s)\socks\ss`功能。
|
||||
下面这个命令,就是一键开启http(s)\ss\socks服务,同时开启socks5的udp和ss的udp功能。
|
||||
`proxy sps -p :33080 --ssudp --udp --udp-port 0`
|
||||
|
||||
### 6.15 目标重定向
|
||||
sps功能提供的http(s)\socks5\ss代理功能,客户端通过sps代理去连接指定的“目标”,这个“目标”一般是网站也可能是任意的tcp地址,
|
||||
网站”目标“一般是foo.com:80,foo.com:443,sps支持使用--rewrite参数指定一个“目标”重定向规则文件,对目标进行重定向,客户端是无感知的,
|
||||
比如你对“目标”:demo.com:80重定向到192.168.0.12:80,那么客户端访问网站demo.com,其实访问的是192.168.0.12提供的网站服务。
|
||||
“目标”重定向规则文件示例:
|
||||
|
||||
```text
|
||||
# example
|
||||
www.a.com:80 10.0.0.2:8080
|
||||
**.b.com:80 10.0.0.2:80
|
||||
192.168.0.11:80 10.0.0.2:8080
|
||||
```
|
||||
|
||||
### 6.16 固定UDP功能端口
|
||||
|
||||
默认情况下sps的socks5的UDP功能的端口号是按着`rfc1982草案`要求,使用协议握手过程中随机指定,不需要提前指定。
|
||||
|
||||
但是某些情况下,需要固定UDP功能端口,可以通过参数`--udp-port 端口号`用来固定UDP功能的端口号,比如:
|
||||
|
||||
`proxy sps -t tcp -p "0.0.0.0:38080" --udp-port 38081`
|
||||
|
||||
需要注意的是,sps的ss功能也有UDP功能,而且ss的UDP端口和tcp端口是一样的,所以要避免socks5的UDP端口和ss的UDP端口冲突,
|
||||
|
||||
要指定和tcp端口不一样的端口。
|
||||
|
||||
### 6.17 iptables 透明代理
|
||||
sps模式支持Linux系统的iptables转发支持,也就是通常所说的iptables透明代理,如果在网关设备上进行iptables透明代理,那么对通过网关联网的设备就能实现无感知的代理。
|
||||
|
||||
启动命令实例:
|
||||
|
||||
`proxy sps --redir -p :8888 -P httpws://1.1.1.1:33080`
|
||||
|
||||
这里假设存在一个http的上级代理1.1.1.1:33080,使用ws传输数据。
|
||||
|
||||
然后添加iptables规则,下面是参考规则:
|
||||
```shell
|
||||
#上级proxy服务端服务器IP地址:
|
||||
proxy_server_ip=1.1.1.1
|
||||
|
||||
#路由器运行proxy监听的端口:
|
||||
proxy_local_port=33080
|
||||
|
||||
#下面的就不用修改了
|
||||
#create a new chain named PROXY
|
||||
iptables -t nat -N PROXY
|
||||
|
||||
# Ignore your PROXY server's addresses
|
||||
# It's very IMPORTANT, just be careful。
|
||||
|
||||
iptables -t nat -A PROXY -d $proxy_server_ip -j RETURN
|
||||
|
||||
# Ignore LANs IP address
|
||||
iptables -t nat -A PROXY -d 0.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 10.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 127.0.0.0/8 -j RETURN
|
||||
iptables -t nat -A PROXY -d 169.254.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 172.16.0.0/12 -j RETURN
|
||||
iptables -t nat -A PROXY -d 192.168.0.0/16 -j RETURN
|
||||
iptables -t nat -A PROXY -d 224.0.0.0/4 -j RETURN
|
||||
iptables -t nat -A PROXY -d 240.0.0.0/4 -j RETURN
|
||||
|
||||
# Anything to port 80 443 should be redirected to PROXY's local port
|
||||
iptables -t nat -A PROXY -p tcp -j REDIRECT --to-ports $proxy_local_port
|
||||
# Apply the rules to nat client
|
||||
iptables -t nat -A PREROUTING -p tcp -j PROXY
|
||||
# Apply the rules to localhost
|
||||
iptables -t nat -A OUTPUT -p tcp -j PROXY
|
||||
```
|
||||
- 清空整个链 iptables -F 链名比如iptables -t nat -F PROXY
|
||||
- 删除指定的用户自定义链 iptables -X 链名 比如 iptables -t nat -X PROXY
|
||||
- 从所选链中删除规则 iptables -D 链名 规则详情 比如 iptables -t nat -D PROXY -d 223.223.192.0/255.255.240.0 -j RETURN
|
||||
|
||||
### 6.18 查看帮助
|
||||
|
||||
`proxy help sps`
|
||||
|
||||
## 7.KCP配置
|
||||
|
||||
### 7.1 配置介绍
|
||||
proxy的很多功能都支持kcp协议,凡是使用了kcp协议的功能都支持这里介绍的配置参数。
|
||||
所以这里统一对KCP配置参数进行介绍。
|
||||
|
||||
### 7.2 详细配置
|
||||
所有的KCP配置参数共有17个,你可以都不用设置,他们都有默认值,如果为了或者最好的效果,
|
||||
就需要自己根据自己根据网络情况对参数进行配置。由于kcp配置很复杂需要一定的网络基础知识,
|
||||
如果想获得kcp参数更详细的配置和解说,请自行搜索。每个参数的命令行名称以及默认值和简单的功能说明如下:
|
||||
```
|
||||
--kcp-key="secrect" pre-shared secret between client and server
|
||||
--kcp-method="aes" encrypt/decrypt method, can be: aes, aes-128, aes-192, salsa20, blowfish,
|
||||
twofish, cast5, 3des, tea, xtea, xor, sm4, none
|
||||
--kcp-mode="fast" profiles: fast3, fast2, fast, normal, manual
|
||||
--kcp-mtu=1350 set maximum transmission unit for UDP packets
|
||||
--kcp-sndwnd=1024 set send window size(num of packets)
|
||||
--kcp-rcvwnd=1024 set receive window size(num of packets)
|
||||
--kcp-ds=10 set reed-solomon erasure coding - datashard
|
||||
--kcp-ps=3 set reed-solomon erasure coding - parityshard
|
||||
--kcp-dscp=0 set DSCP(6bit)
|
||||
--kcp-nocomp disable compression
|
||||
--kcp-acknodelay be carefull! flush ack immediately when a packet is received
|
||||
--kcp-nodelay=0 be carefull!
|
||||
--kcp-interval=50 be carefull!
|
||||
--kcp-resend=0 be carefull!
|
||||
--kcp-nc=0 be carefull! no congestion
|
||||
--kcp-sockbuf=4194304 be carefull!
|
||||
--kcp-keepalive=10 be carefull!
|
||||
```
|
||||
提示:
|
||||
参数:--kcp-mode中的四种fast3, fast2, fast, normal模式,
|
||||
相当于设置了下面四个参数:
|
||||
normal:`--nodelay=0 --interval=40 --resend=2 --nc=1`
|
||||
fast :`--nodelay=0 --interval=30 --resend=2 --nc=1`
|
||||
fast2:`--nodelay=1 --interval=20 --resend=2 --nc=1`
|
||||
fast3:`--nodelay=1 --interval=10 --resend=2 --nc=1`
|
||||
|
||||
## 8.安全DNS
|
||||
|
||||
### 8.1 介绍
|
||||
众所周知DNS是UDP端口53提供的服务,但是随着网络的发展一些知名DNS服务器也支持TCP方式dns查询,比如谷歌的8.8.8.8,proxy的DNS防污染服务器原理就是在本地启动一个proxy的DNS代理服务器,它用TCP的方式通过上级代理进行dns查询。如果它和上级代理通讯采用加密的方式,那么就可以进行安全无污染的DNS解析,还支持独立服务,并发解析,支持增强的hosts文件功能支持灵活的并发解析转发。
|
||||
|
||||
dns解析顺序:
|
||||
1.使用参数--hosts解析。
|
||||
2.要解析的域名在1中没有找到,就使用参数--forward规则解析。
|
||||
3.要解析的域名在1和2中都没有找到,就使用默认--default解析,--default默认行为参数值有三种:proxy,direct,system。
|
||||
三种参数值解释如下:
|
||||
proxy:通过上级去连接-q参数指定的dns服务器去解析域名。
|
||||
direct:通过本地网络去连接-q参数指定的dns服务器去解析域名。
|
||||
system:通过系统dns去解析域名。
|
||||
|
||||
提示:
|
||||
--hosts 参数指定的host文件格式和系统hosts文件一致,而且域名支持通配符,可以参考hosts文件。
|
||||
--forward 参数指定的解析转发规则文件,格式可以参考resolve.rules文件,域名支持通配符,支持为每个域名指定多个dns服务器并发解析,谁最快解析成功就用谁的解析结果。
|
||||
-q 参数可以指定多个远程dns服务器,执行并发解析谁最快解析成功就用谁的解析结果,默认是:1.1.1.1,8.8.8.8,9.9.9.9,多个用逗号分割,
|
||||
比如还可以带端口:1.1.1.1,8.8.8.8#53,9.9.9.9
|
||||
|
||||
如果独立服务,不需要上级:
|
||||
可以执行:
|
||||
`proxy dns --default system -p :5353`
|
||||
or
|
||||
`proxy dns --default direct -p :5353`
|
||||
|
||||
### 8.2 使用示例
|
||||
|
||||
#### 8.2.1 普通HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
本地执行:
|
||||
`proxy dns -S http -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了DNS解析功能。
|
||||
|
||||
#### 8.2.2 普通SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
本地执行:
|
||||
`proxy dns -S socks -T tcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了DNS解析功能。
|
||||
|
||||
#### 8.2.3 TLS加密的HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy http -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S http -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.4 TLS加密的SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy socks -t tls -C proxy.crt -K proxy.key -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S socks -T tls -P 2.2.2.2:33080 -C proxy.crt -K proxy.key -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.5 KCP加密的HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy http -t kcp -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S http -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.6 KCP加密的SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy socks -t kcp -p :33080`
|
||||
本地执行:
|
||||
`proxy dns -S socks -T kcp -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.7 自定义加密的HTTP(S)上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy http -t tcp -p :33080 -z password`
|
||||
本地执行:
|
||||
`proxy dns -S http -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
#### 8.2.8 自定义加密的SOCKS5上级代理
|
||||
|
||||
假设有一个上级代理:2.2.2.2:33080
|
||||
上级代理执行的命令是:
|
||||
`proxy socks -t kcp -p :33080 -z password`
|
||||
本地执行:
|
||||
`proxy dns -S socks -T tcp -Z password -P 2.2.2.2:33080 -p :53`
|
||||
那么本地的UDP端口53就提供了安全防污染DNS解析功能。
|
||||
|
||||
## 9.API认证,限速,控制连接数,限流量
|
||||
|
||||
proxy的http(s)/socks5/sps代理功能,支持通过API控制用户对代理对访问。
|
||||
|
||||
### 通过API可以干什么?
|
||||
|
||||
- 用户维度,控制单个连接速率,控制最大连接数。
|
||||
- IP维度,控制单个连接速率,控制最大连接数。
|
||||
- 动态上级,可以根据用户或者客户端IP,动态的从API获取其上级,支持http(s)/socks5/ss上级。
|
||||
- 认证每一个连接,无论是否要求客户端认证。
|
||||
- 缓存认证结果,时间可以设置,减轻API压力。
|
||||
|
||||
#### 具体使用
|
||||
proxy的http(s)/socks5/sps代理API功能,通过`--auth-url`和`--auth-nouser`和`--auth-cache`三个参数控制。
|
||||
参数`--auth-url`是HTTP API接口地址,客户端连接的时候,proxy会GET方式请求这url,带上下面参数,如果返回HTTP状态码204,代表认证成功,其它情况认为认证失败。
|
||||
|
||||
一个完整的请求API的示例:
|
||||
`http://test.com/auth.php?user=a&pass=b&client_addr=127.0.0.1:49892&local_addr=127.0.0.1:8100&target=http%3A%2F%2Fwww.baidu.com&service=http&sps=0`
|
||||
|
||||
#### 参数说明
|
||||
`user和pass` 当代理开启了认证功能,这里就是客户端提供的用户名和密码。
|
||||
`client_addr` 客户端访问代理时的用的地址,格式IP:端口。
|
||||
`local_addr` 客户端访问的代理地址,格式IP:端口。
|
||||
`service` 代理类型,分为:http、socks。
|
||||
`sps` 代理是否是sps提供的,1:是,0:否。
|
||||
`target` 客户端要访问的目标,如果是http(s)代理,target是访问的具体url;如果是socks5代理,target是空。
|
||||
|
||||
#### 示例
|
||||
假设--auth-url http://127.0.0.1:333/auth.php 指向了一个php接口地址.
|
||||
auth.php内容如下:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#设置所有的用户名密码,前面是用户名,后面是对应密码
|
||||
$alluser=[
|
||||
"user1"=>"pass1",
|
||||
"user2"=>"pass2",
|
||||
"user3"=>"pass3",
|
||||
"user4"=>"pass4",
|
||||
];
|
||||
$proxy_ip=$_GET['local_addr'];
|
||||
$user_ip=$_GET['client_addr'];
|
||||
$service=$_GET['service'];
|
||||
$is_sps=$_GET['sps']=='1';
|
||||
$user=$_GET['user'];
|
||||
$pass=$_GET['pass'];
|
||||
$target=$_GET['target'];
|
||||
//业务逻辑判断
|
||||
//....
|
||||
$ok=false;
|
||||
foreach ($alluser as $dbuser => $dbpass) {
|
||||
if ($user==$dbuser&&$pass==$dbpass){
|
||||
$ok=true;
|
||||
break;
|
||||
}
|
||||
}
|
||||
//设置认证结果
|
||||
if($ok){
|
||||
header("userconns:1000");
|
||||
header("ipconns:2000");
|
||||
header("userrate:3000");
|
||||
header("iprate:8000");
|
||||
header("UPSTREAM:http://127.0.0.1:3500?parent-type=tcp");
|
||||
header("HTTP/1.1 204 No Content");
|
||||
}
|
||||
```
|
||||
|
||||
#### 解释
|
||||
userconns:用户的最大连接数,不限制为0或者不设置这个头部。
|
||||
ipconns:用户IP的最大连接数,不限制为0或者不设置这个头部。
|
||||
userrate:用户的单个TCP连接速率限制,单位:字节/秒,不限制为0或者不设置这个头部。
|
||||
iprate:用户IP的单个TCP连接速率限制,单位:字节/秒,不限制为0或者不设置这个头部。
|
||||
upstream:使用的上级,没有为空,或者不设置这个头部。
|
||||
|
||||
#### 提示
|
||||
1.默认情况下,设置了`--auth-url`是强制要求客户端提供用户名和密码的;如果不需要强制要求客户端提供用户名密码,并认证,可以加上`--auth-nouser`,每次访问仍然会访问认证地址`--auth-url`进行认证,当客户端没有发生认证信息当时候,php接口里面接收的$user认证用户名和$pass认证密码都为空。
|
||||
2.连接数限制优先级:用户认证文件连接数限制-》文件ip.limit连接数限制-》API用户连接数限制-》API的IP连接数限制-》命令行全局连接数限制。
|
||||
3.速率限制优先级:用户认证文件速率限制-》文件ip.limit速率限制-》API用户速率限制-》API的IP速率限制-》命令行全局速率限制。
|
||||
3.上级获取优先级:用户认证文件的upstream-》文件ip.limit的upstream-》API的upstream-》命令行指定的上级。
|
||||
4.`--auth-cache`认证缓存,对认证结果缓存一定时间,提升性能,降低认证接口压力,--auth-cache 单位秒,默认0, 设置0是关闭缓存。
|
||||
|
||||
#### upstream详细说明
|
||||
|
||||
1.当参数`sps`是0的时候。
|
||||
service是http时,upstream只支持http(s)代理,不支持认证,如需要认证可以用sps代替,格式:
|
||||
`http://127.0.0.1:3100?argk=argv`
|
||||
service是socks时,upstream只支持socks5代理,格式:
|
||||
`socks5://127.0.0.1:3100?argk=argv`
|
||||
|
||||
解释:`http://`,`socks5://` 是固定的,`127.0.0.1:3100`是上级的地址
|
||||
|
||||
2.当`sps`是1的时候。
|
||||
upstream支持socks5、http(s)代理,支持认证,格式:`protocol://a:b@2.2.2.2:33080?argk=argv`,具体介绍请参考SPS章节的,**多个上级**,`-P`参数的说明。
|
||||
3.参数,`?`后面`argk=argv`是参数:参数名称=参数值,多个参数用`&`连接。
|
||||
支持的所有参数如下,和命令行同名参数意义一致。
|
||||
1. parent-type : 上级底层传输类型,支持 tcp,tls,ws,wss。
|
||||
2. parent-ws-method : 上级底层ws传输类型的加密方法,支持的值和命令行支持的值范围一样。
|
||||
3. parent-ws-password : 上级底层ws传输类型的加密密码,数字字母组成的密码。
|
||||
4. parent-tls-single : 上级底层tls传输类型是否是单向tls,可以是:true | false。
|
||||
5. timeout : 建立tcp连接的超时时间,数字,单位毫秒。
|
||||
6. ca : 上级底层tls传输类型的ca证书文件经过base64编码后的字符串。
|
||||
7. cert : 上级底层tls传输类型的证书文件经过base64编码后的字符串。
|
||||
8. key : 上级底层tls传输类型的证书密钥文件经过base64编码后的字符串。
|
||||
|
||||
### 流量上报/流量统计/流量限制
|
||||
|
||||
proxy的http(s)/socks5/sps/tcp/udp代理功能支持流量上报,可以通过参数`--traffic-url`设置一个http接口地址。
|
||||
proxy会把连接使用的流量上报到这个地址,具体情况是,proxy发送一个HTTP到GET请求到`--traffic-url`设置的HTTP URL地址.
|
||||
上报模式有两种,可以通过`--traffic-mode`参数指定,可以是`normal`普通模式上报,也可以是`fast`快速模式上报。
|
||||
1. `normal`普通模式上报
|
||||
当连接释放时,proxy会把此次连接使用的流量上报到这个`--traffic-url`地址.
|
||||
2. `fast`快速模式上报
|
||||
对已经建立的每个连接,proxy会`定时`把这个连接产生的流量上报到这个这个`--traffic-url`地址.
|
||||
`定时`默认是5秒,可以通过参数`--traffic-interval`修改`定时`为合适的秒数。
|
||||
流量上报功能结合上面的API认证功能可以实现实时控制用户的流量使用,流量统计,流量限制;流量上报到接口,接口把流量数据写入数据库,然后认证API查询数据库判断用户或者IP流量使用情况,用来确定用户是否可以认证成功.
|
||||
|
||||
下面是一个完整的URL请求实例:
|
||||
|
||||
`http://127.0.0.1:33088/user/traffic?bytes=337&client_addr=127.0.0.1%3A51035&id=http&server_addr=127.0.0.1%3A33088&target_addr=myip.ipip.net%3A80&username=a`
|
||||
|
||||
请求参数说明:
|
||||
id: 服务id标志.
|
||||
server_addr: 客户端请求的代理地址,格式: `IP:端口`.
|
||||
client_addr: 客户端地址,格式: `IP:端口`.
|
||||
target_addr: 目标地址,格式: `IP:端口`,tcp/udp代理时,这个是空.
|
||||
username: 代理认证用户名,tcp/udp代理时,这个是空.
|
||||
bytes: 此次使用的流量字节数.
|
||||
|
||||
#### 提示
|
||||
|
||||
访问的`--traffic-url`地址接口必须返回HTTP状态码`204`,流量上报才认为上报成功,返回其它状态码将认为上报流量失败,会输出相关日志。
|
||||
|
||||
#### 流量上报原理
|
||||
|
||||

|
||||
|
||||
### 主动断开用户连接
|
||||
|
||||
proxy的http(s)/socks5/sps代理功能支持`控制接口`,可以通过参数`--control-url`指定的http接口地址,
|
||||
那么proxy就会`定期`的把当前连接到proxy的全部用户名或客户端IP发送到此URL,具体情况是,proxy发送一个HTTP的POST请求到`--control-url`设置的HTTP URL地址.`定期`默认是30秒,可以通过`--control-sleep`参数修改此值。
|
||||
当用户过期,或者用户流量已经用完,通过认证API只能控制用户不能新建连接,但是已经和proxy建立当连接没法立刻断开,
|
||||
那么通过控制接口可以解决这个问题,控制接口会在最慢`定期`时间内通过控制接口返回的内容,结束已经无效的用户建立的连接。
|
||||
|
||||
#### 控制接口请求说明
|
||||
|
||||
proxy会向控制接口URL发送一个HTTP POST请求,表单数据中有两个字段:user和ip。
|
||||
|
||||
user:当前连接到proxy的用户名,多个使用英文逗号分割,比如:user1,user2
|
||||
|
||||
ip:当前连接到proxy的客户端ip地址,多个使用英文逗号分割,比如:1.1.1.1,2.2.2.2
|
||||
|
||||
#### 控制接口返回数据说明
|
||||
|
||||
控制接口返回的数据是无效的用户和IP,格式是一个json对象数据,有两个字段user和ip。
|
||||
|
||||
比如:{"user":"a,b","ip":""}
|
||||
|
||||
user:当前连接到proxy的用户名,多个使用英文逗号分割,没有留空,比如:user1,user2
|
||||
|
||||
ip:当前连接到proxy的客户端ip地址,多个使用英文逗号分割,没有留空,比如:1.1.1.1,2.2.2.2
|
||||
|
||||
返回的用户和ip已经建立的连接会被proxy断开。
|
||||
|
||||
#### 示例
|
||||
假设--control-url `http://127.0.0.1:33088/user/control.php` 指向了一个php接口地址.
|
||||
control.php内容如下:
|
||||
|
||||
```php
|
||||
<?php
|
||||
#接收proxy post过来的数据
|
||||
$userArr=explode(",",$_POST['user']);
|
||||
$ipArr=$_GET['ip'];
|
||||
|
||||
//无效用户列表
|
||||
$badUsers=[];
|
||||
|
||||
foreach ($userArr as $user) {
|
||||
//逻辑判断用户$user是否无效,如果无效就放入$badUsers
|
||||
$badUsers[]=$user;
|
||||
}
|
||||
$data=["user"=>implode(","$badUsers),"ip"=>""];
|
||||
|
||||
echo json_encode($data);
|
||||
```
|
||||
|
||||
### 使用代理
|
||||
|
||||
http(s)/socks5/sps认证API(`--auth-url`)、控制API(`--control-url`)、流量上报API(`--traffic-url`)三个地址的访问,支持通过代理访问,参数是:`--auth-proxy`,格式和`--jumper`格式一致,详细详细请参考`--jumper`。
|
||||
|
||||
## 10.本地认证,限速,控制连接数
|
||||
|
||||
proxy的http(s)/socks5/sps代理功能,支持通过配置文件控制用户对代理对访问,支持开启http(s)代理``Proxy Basic 代理认证`,socks5代理认证。
|
||||
|
||||
### 开始使用
|
||||
proxy的http(s)/socks5/sps代理功能可以通过
|
||||
`--auth-file`,`--max-conns`,`--ip-limit`,`--rate-limit`,`-a`这五个参数控制。
|
||||
|
||||
#### 参数详细解释
|
||||
|
||||
##### `--auth-file`
|
||||
认证的用户名和密码文件,该参数指定一个文件,一行一条规则,格式是:"用户名:密码:连接数:速率:上级"。
|
||||
`连接数`是用户最大连接数,`速率`是用户每个tcp连接最大速度,单位是:字节/秒,`上级`是用户使用的上级。
|
||||
不仅可以通过`--auth-file`设置认证用户,也可以直接用`-a`参数设置,多个用户就重复多个`-a`参数即可。
|
||||
比如:`proxy http -a a:b:0:0: -a c:d:0:0:`
|
||||
|
||||
实例解释:
|
||||
比如:`user:pass:100:10240:http://192.168.1.1:3100`
|
||||
`user`是认证用户名
|
||||
`pass`是认证用户密码(不能包含冒号:)
|
||||
`100`是这个用户的最大连接数,不限制写0
|
||||
`10240`是这个用户单个tcp连接的速率限制,单位是:字节/秒,不限制写0
|
||||
`http://192.168.1.1:3100`是这个用户使用的上级,没有就留空
|
||||
|
||||
##### `--max-conns`
|
||||
限制代理服务的全局最大连接数,一个数字,0为不限制,默认0。
|
||||
|
||||
##### `--ip-limit`
|
||||
控制客户端IP的连接数和连接速率,该参数指定一个文件,一行一条规则,#开头的是注视。
|
||||
示例文件ip.limit,规则格式如下:
|
||||
`127.0.0.1:100:10240:http://192.168.1.1:3100`
|
||||
规则解释:
|
||||
`127.0.0.1`是要限制的IP
|
||||
`100`是这个IP的最大连接数,不限制写0
|
||||
`10240`是IP单个tcp连接的速率限制,单位是:字节/s,不限制写0
|
||||
`http://192.168.1.1:3100`是这个IP使用的上级,没有就留空
|
||||
|
||||
##### `--rate-limit`
|
||||
限制服务的每一个tcp连接的速度,比如:100K 2000K 1M . 0意味着无限制,默认0。
|
||||
|
||||
## 11.集群管理
|
||||
|
||||
proxy支持集群管理功能,此时proxy安装在每个机器节点上作为agent,配合控制面板[`proxyadmin集群版`](https://github.com/snail007/proxy-admin-cluster),就能够实现统一管理海量机器上的proxy服务。
|
||||
|
||||
proxy如果要作为agent运行,假设控制面板的集群端口地址是:`1.1.1.1:55333`.
|
||||
|
||||
命令示例如下:
|
||||
|
||||
`proxy agent -k xxx -c 1.1.1.1:55333 -i test`
|
||||
|
||||
命令解释:
|
||||
|
||||
agent : 是功能参数,表示运行agent模式。
|
||||
|
||||
-k :和`proxyadmin集群版`通讯加密解密的密钥,这个密钥是在`proxyadmin集群版`的配置文件里面设置的。
|
||||
|
||||
-c :`proxyadmin集群版`的集群端口地址,格式:IP:端口。
|
||||
|
||||
-i : agent唯一标识,保证每个agent的都不一样,此处指定的`唯一标识`,在控制面板添加节点的时候用到,IP一栏填写这个`唯一标识`。
|
||||
如果-i不指定,默认是空,控制面板添加节点的时候IP一栏填写:agent的出口IP。
|
||||
|
||||
-u: 代理参数,默认是空。可以指定一个代理,agent会通过这个代理与cluster通讯。
|
||||
格式和`--jumper`格式一致,详细情况请参考手册中`--jumper`部分。
|
||||
|
||||
提示:
|
||||
|
||||
1.当控制面板里面配置了client服务,那么所有节点都使用相同都key那么就导致,只有一个client可以工作,为了解决这个问题,
|
||||
client服务参数里面可以通过使用占位符:`{AGENT_ID}`引用agent的id当作client的key,这样就可以保证每个客户端都有唯一的key。
|
||||
|
||||
比如client服务参数:
|
||||
|
||||
`client -T tcp -P 1.1.1.1:30000 --k {AGENT_ID}`
|
||||
|
||||
2.如果使用了代理参数`-u`,务必设置唯一标示参数`-i`,不然cluster无法区分不同的agent,agent将不能正常工作。
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/</title><link rel="canonical" href="https://snail.gitee.io/proxy/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/" /></head></html>
|
||||
@@ -0,0 +1,243 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T15:29:47JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/categories/">Categories</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">不用看这里,没什么内容,仅仅为了定义目录和tags。</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T13:22:19JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/about/">About</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">It’s YOU!</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
<nav>
|
||||
<ul class="pager">
|
||||
|
||||
|
||||
<li><a href="/proxy/">Previous</a></li>
|
||||
|
||||
|
||||
|
||||
<li class="disabled"><a href="#">Next</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
</nav>
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,304 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/page/about/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>About - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="It&rsquo;s YOU!">
|
||||
|
||||
<meta property="og:title" content="About - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/page/about/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="It&rsquo;s YOU!">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/page/about/">
|
||||
<meta name="twitter:title" content="About - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="It&rsquo;s YOU!">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "About - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-14T13:22:19JST",
|
||||
"dateModified": "2019-06-14T13:22:19JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "It\x26rsquo;s YOU!"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/page/" itemprop="url"><span itemprop="title">page</span></a></li>
|
||||
|
||||
<li class="active">About</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T13:22:19JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">About</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body"><figure>
|
||||
<img css="" src="https://snail.gitee.io/proxy/img/1.jpg" alt="About img/1.jpg">
|
||||
|
||||
</figure>
|
||||
|
||||
<p>It’s YOU!</p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,327 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/page/categories/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Categories - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="不用看这里,没什么内容,仅仅为了定义目录和tags。">
|
||||
|
||||
<meta property="og:title" content="Categories - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/page/categories/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="不用看这里,没什么内容,仅仅为了定义目录和tags。">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/page/categories/">
|
||||
<meta name="twitter:title" content="Categories - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="不用看这里,没什么内容,仅仅为了定义目录和tags。">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "Categories - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-14T15:29:47JST",
|
||||
"dateModified": "2019-06-14T15:29:47JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "不用看这里,没什么内容,仅仅为了定义目录和tags。"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/page/" itemprop="url"><span itemprop="title">page</span></a></li>
|
||||
|
||||
<li class="active">Categories</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T15:29:47JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">Categories</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body"><p>不用看这里,没什么内容,仅仅为了定义目录和tags。</p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/">架构解说</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/">细说层级</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/ws/">ws</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,336 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>常见问题解答 - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="goproxy常见问答">
|
||||
|
||||
<meta property="og:title" content="常见问题解答 - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="goproxy常见问答">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/">
|
||||
<meta name="twitter:title" content="常见问题解答 - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="goproxy常见问答">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "常见问题解答 - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-14T16:29:13JST",
|
||||
"dateModified": "2019-06-14T16:29:13JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "goproxy常见问答"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/page/" itemprop="url"><span itemprop="title">page</span></a></li>
|
||||
|
||||
<li class="active">常见问题解答</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:29:13JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">常见问题解答</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h3 id="问-http代理支持https网站吗">问:http代理支持https网站吗?</h3>
|
||||
|
||||
<p>答:goproxy的http代理同时支持http和https网站。</p>
|
||||
|
||||
<h3 id="问-socks5代理支持udp吗">问:socks5代理支持UDP吗?</h3>
|
||||
|
||||
<p>答:goproxy的socks5代理是完全按着<a href="https://tools.ietf.org/html/rfc1928">rfc1982</a>草案实现的,支持UDP功能,草案规定UDP端口是在代理握手请求过程中服务端动态指定的,不需要提前指定。如果你使用的socks5客户端是标准客户端,是不需要你手动指定UDP端口的。</p>
|
||||
|
||||
<h3 id="问-什么是http代理-https代理">问:什么是http代理?https代理?</h3>
|
||||
|
||||
<p>答:无论是<code>http代理</code>还是<code>https代理</code>,都支持同时代理访问<code>http</code>和<code>https</code>网站。<br />
|
||||
<code>http代理</code>和<code>https代理</code>里的http和https和你访问的网站是否是http(https)是无关的。<br />
|
||||
<code>http代理</code>:客户端和代理服务器之间是<code>tcp</code>传输数据。<br />
|
||||
<code>https代理</code>:客户端和代理服务器之间是<code>tls</code>加密传输数据。<br />
|
||||
http代理是使用最广泛的代理,大部分客户端都不支持https代理。</p>
|
||||
|
||||
<h3 id="问-goproxy的http代理是http代理还是https代理">问:goproxy的http代理是http代理还是https代理?</h3>
|
||||
|
||||
<p>答:goproxy支持http代理,https代理,https双向认证代理。<br />
|
||||
至于提供什么类型的代理,是参数<code>-t</code>决定的:<br />
|
||||
http代理 :<code>-t tcp</code><br />
|
||||
https代理:<code>-t tls --local-tls-single</code>,服务端需要设置tls证书。<br />
|
||||
https双向认证代理:<code>-t tls</code>,服务端和客户端都需要设置一样的tls证书。</p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,596 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/page/free_vs_commercial/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>GOPROXY免费版VS商业版 - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="GOPROXY 免费版VS商业版">
|
||||
|
||||
<meta property="og:title" content="GOPROXY免费版VS商业版 - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/page/free_vs_commercial/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="GOPROXY 免费版VS商业版">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/page/free_vs_commercial/">
|
||||
<meta name="twitter:title" content="GOPROXY免费版VS商业版 - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="GOPROXY 免费版VS商业版">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "GOPROXY免费版VS商业版 - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-26T13:19:15JST",
|
||||
"dateModified": "2019-06-26T13:19:15JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "GOPROXY 免费版VS商业版"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/page/" itemprop="url"><span itemprop="title">page</span></a></li>
|
||||
|
||||
<li class="active">GOPROXY免费版VS商业版</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">GOPROXY免费版VS商业版</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h4 id="目前-goproxy-和-sdk-提供免费版和商业版-功能对比如下">目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。</h4>
|
||||
|
||||
<table>
|
||||
<thead>
|
||||
<tr>
|
||||
<th align="left"> </th>
|
||||
<th align="center"> 免费版 </th>
|
||||
<th align="center"> 商业版 </th>
|
||||
</tr>
|
||||
</thead>
|
||||
|
||||
<tbody>
|
||||
<tr>
|
||||
<td align="left"><code>TCP转发</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>UDP转发</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>HTTP(S)代理</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Socks5代理</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Socks5代理UDP支持</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SPS综合代理</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SPS上级认证</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>内网穿透</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>DNS代理,防污染,独立DNS服务</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>HTTP(S)代理认证,认证API,负载均衡</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SOCKS5代理认证,认证API,负载均衡</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SPS代理认证,认证API,负载均衡</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>STOP&ONLY黑白名单</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>客户端IP黑白名单</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>检查更新,失败退出</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">×</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>单机进程数量限制</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">×</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>手册完整功能</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>需要联网认证</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>限速功能</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>http/socks5/tcp代理指定出口IP</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>目标连接重定向</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>docker</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>免费更新至更多功能的商业版</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>http(s)\socks\sps,上级ws/wss支持路径和独立加密</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>用户限速,IP限速</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>用户限连接数,IP限连接数</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>API动态选择上级代理</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>socks5/http(s)/sps/tcp/udp代理监听支持端口范围</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
</tbody>
|
||||
</table>
|
||||
|
||||
<h4 id="商业版授权方式分为两种">商业版授权方式分为两种</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>程序和机器绑定,单个机器方式授权,针对<code>机器码</code>收费。</p></li>
|
||||
|
||||
<li><p>程序和不和机器绑定,授权码方式授权,针对<code>授权码</code>收费。</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="商业版使用">商业版使用</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>去平台授权平台 <a href="https://gpm.host900.com/?lang=zh-CN">https://gpm.host900.com/?lang=zh-CN</a> 注册一个用户。</p></li>
|
||||
|
||||
<li><p>如果使用<code>机器码</code>授权方式,首次执行:<code>proxy http</code>,控制面板执行<code>proxy-admin</code>, 并<strong>等待程序自己退出,不要手动结束程序</strong>,
|
||||
然后会在当前目录下面生成id.txt文件,控制面板 Linux: <code>/etc/gpa/id.txt</code>,Windows: <code>C:\gpa\id.txt</code>,里面是当前机器的机器码,
|
||||
然后在授权后台自助在线购买机器码。然后点击菜单<code>我的机器码</code>,点击列表操作列的<code>修改</code>,把id.txt内的机器码填入到机器码输入框里面,然后保存即可完成授权。
|
||||
或者联系 <code>[email protected]</code> 购买卡密,去授权平台后台点击菜单<code>添加机器码</code>输入<code>卡密</code>完成机器码购买。</p></li>
|
||||
|
||||
<li><p>如果是<code>授权码</code>方式授权,首先购买授权码,然后会在授权平台里面看见自己的授权码。加上授权码参数<code>--authcode 授权码</code>启动程序即可,也可以设置环境变量<code>LIC_AUTHCODE</code>内容为授权码,如果没有使用参数<code>--authcode</code>,程序尝试从环境变量<code>LIC_AUTHCODE</code>获取授权码。如果是sdk,start方法有授权码参数,使用购买的授权码即可。</p></li>
|
||||
|
||||
<li><p>商业版下载,打开下面下载地址后,下载文件列表中文件名后缀是:_commercial.tar.gz的为商业版。请根据自己系统情况下载。
|
||||
下载地址:<code>https://github.com/snail007/goproxy/releases</code></p></li>
|
||||
|
||||
<li><p>完全手册:<a href="https://github.com/snail007/goproxy/blob/master/README_ZH.md">https://github.com/snail007/goproxy/blob/master/README_ZH.md</a><br />
|
||||
新版手册:<a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/</a></p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="提醒">提醒</h4>
|
||||
|
||||
<p>商业版只会在启动的时候联网检查一次授权,后期不会再联网检查,只会在<code>授权码</code>、<code>机器码</code>到期的时候再检查一次,如果48小时内无法成功检查授权程序会退出。
|
||||
如果系统发现用户恶意使用或传播自己的<code>授权码</code>、<code>机器码</code>,官方有权终止其使用,并不负任何责任。</p>
|
||||
|
||||
<h4 id="购买商业版">购买商业版</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>购买商业版,授权后台可以在线购买,特殊需求发送邮件到:<code>[email protected]</code> 。</p></li>
|
||||
|
||||
<li><p>除了联系管理员购买卡密,还可以在线购买机器码。首先登录授权平台,点击菜单:机器码管理->在线购买,可以完成少量机器码的购买。如果需要一次购买很多,可以根据网页提示联系管理员。</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="商业版免费试用">商业版免费试用</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>购买商业版之前你可以免费试用7天,以用来确定GOPROXY商业版功能是否满足你的需求。</p></li>
|
||||
|
||||
<li><p>试用步骤:登录<a href="https://gpm.host900.com/?lang=zh-CN">授权平台</a> -> 机器码管理 -> 在线购买 -> 点击”开始试用”。</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="商业版用户须知">商业版用户须知</h4>
|
||||
|
||||
<p>1、官方免费提供首次安装指导。</p>
|
||||
|
||||
<p>2、商业版用户可以提一些商业功能意见,官方会针对意见的合理性等情况进行评估,如果意见被采纳,在未来新版本中会加入。</p>
|
||||
|
||||
<p>3、商业版用户可以免费更新至功能更多的商业版新版。</p>
|
||||
|
||||
<p>4、没有技术支持。</p>
|
||||
|
||||
<h4 id="不能访问授权的解决办法">不能访问授权的解决办法</h4>
|
||||
|
||||
<p>商业版必须可以在线访问授权才能使用,如果您在使用proxy过程中出现服务器可以访问互联网,但是proxy提示访问授权信息失败。可以按着以下方法解决。</p>
|
||||
|
||||
<h5 id="1-如果您的proxy机器可以访问互联网-由于机器dns可能不能正确解析更新域名-可以指定dns启动proxy">1.如果您的proxy机器可以访问互联网,由于机器DNS可能不能正确解析更新域名,可以指定DNS启动proxy。</h5>
|
||||
|
||||
<p>Linux启动命令示例:</p>
|
||||
|
||||
<pre><code class="language-shell">LIC_DNS=8.8.4.4:53 ./proxy http -p :9090
|
||||
</code></pre>
|
||||
|
||||
<p>Windows启动命令示例</p>
|
||||
|
||||
<pre><code class="language-shell">set LIC_DNS=8.8.4.4:53
|
||||
./proxy.exe http -p :9090
|
||||
</code></pre>
|
||||
|
||||
<h5 id="2-如果proxy是在内网环境不能直接访问互联网-你可以在能够访问互联网的机器上启动一个http代理-然后给proxy使用">2.如果proxy是在内网环境不能直接访问互联网,你可以在能够访问互联网的机器上启动一个http代理,然后给proxy使用。</h5>
|
||||
|
||||
<p>比如: proxy在192.168.1.10,不能直接访问互联网。</p>
|
||||
|
||||
<p>在192.168.1.200机器可以访问互联网,那么可以在192.168.1.200机器启动:</p>
|
||||
|
||||
<p><code>./proxy http -p :8080 -q 8.8.4.4:53</code></p>
|
||||
|
||||
<p>在192.168.1.10上面启动命令:</p>
|
||||
|
||||
<p><code>LIC_PROXY=http://192.168.1.200:8080 ./proxy http -p :9090</code></p>
|
||||
|
||||
<h5 id="3-如果内网有现成的http代理-那么2步骤里面不需要自己启动一个代理-lic-proxy直接使用现成的http代理即可">3.如果内网有现成的http代理,那么2步骤里面不需要自己启动一个代理,LIC_PROXY直接使用现成的http代理即可。</h5>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/">商业版</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,605 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>GOPROXY Free Version VS Commercial Version - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="GOPROXY Free Version VS Commercial Version">
|
||||
|
||||
<meta property="og:title" content="GOPROXY Free Version VS Commercial Version - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="GOPROXY Free Version VS Commercial Version">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">
|
||||
<meta name="twitter:title" content="GOPROXY Free Version VS Commercial Version - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="GOPROXY Free Version VS Commercial Version">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "GOPROXY Free Version VS Commercial Version - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-26T13:19:15JST",
|
||||
"dateModified": "2019-06-26T13:19:15JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "GOPROXY Free Version VS Commercial Version"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/page/" itemprop="url"><span itemprop="title">page</span></a></li>
|
||||
|
||||
<li class="active">GOPROXY Free Version VS Commercial Version</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">GOPROXY Free Version VS Commercial Version</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h4 id="currently-goproxy-and-sdk-are-available-in-both-free-and-commercial-versions">Currently, GOPROXY and SDK are available in both free and commercial versions.</h4>
|
||||
|
||||
<table>
|
||||
<thead>
|
||||
<tr>
|
||||
<th align="left">Function</th>
|
||||
<th align="center">Free</th>
|
||||
<th align="center">|Commercial </th>
|
||||
</tr>
|
||||
</thead>
|
||||
|
||||
<tbody>
|
||||
<tr>
|
||||
<td align="left"><code>TCP forwarding</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>UDP forwarding</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>HTTP(S)Agent</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Socks5 Agent</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Socks5 proxy UDP support</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SPS Integrated Agent</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SPS superior certification</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Intranet penetration</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>DNS proxy, anti-pollution, independent DNS service</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>HTTP(S) proxy authentication, authentication API, load balancing</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SOCKS5 proxy authentication, authentication API, load balancing</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>SPS proxy authentication, authentication API, load balancing</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>STOP&ONLY blacklist and whitelist</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Client IP blacklist and whitelist</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Check for updates, failed to exit</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">×</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Single machine process limit</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">×</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Manual full function</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Need network authentication</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Speed limit function</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>http/socks5/tcp fllow IP</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Target connection redirection</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>docker</code></td>
|
||||
<td align="center">√</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Free update to more features of the commercial version</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>http(s)\socks\sps, superior ws/wss support path and independent encryption</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Limit user or ip traffic rate</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>Limit user or ip connections count</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>API dynamic upstream</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
|
||||
<tr>
|
||||
<td align="left"><code>socks5/http(s)/sps/tcp/udp listen on range ports support</code></td>
|
||||
<td align="center">×</td>
|
||||
<td align="center">√</td>
|
||||
</tr>
|
||||
</tbody>
|
||||
</table>
|
||||
|
||||
<h4 id="there-are-two-types-of-commercial-licenses">There are two types of commercial licenses</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>Program and machine binding, single machine mode authorization, charge for <code>machine code</code>.</p></li>
|
||||
|
||||
<li><p>The program is not bound to the machine, authorized code mode authorization, and charged for the <code>authorization code</code>.</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="commercial-version-uses">Commercial version uses:</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>Go to the authorization platform <a href="https://gpm.host900.com/?lang=en-US">https://gpm.host900.com/?lang=en-US</a> to register a user.</p></li>
|
||||
|
||||
<li><p>If you use the <code>machine code</code> authorization method, the first execution: <code>proxy http</code> , then waiting for it exit, and then it will generate an id.txt file in the current directory, which is the machine code of the current machine. If it is sdk, the MacCode method can be called to get the current machine. Machine code; then purchase <code>card secret code</code>, go to the authorization platform background click menu to add machine code, input <code>card secret code</code> to complete the activation of the machine code, then click on the <code>machine list</code> in the menu, click on the list operation column <code>modify</code>, Fill in the machine code in id.txt into the machine code input box, and then save to complete the authorization.</p></li>
|
||||
|
||||
<li><p>If it is authorized by the <code>Authorization Code</code> method, first purchase the authorization code, and then you will see your authorization code in the authorization platform. Add the authorization code parameter <code>--authcode your_authorization_code</code> to start the program. You can also set the environment variable <code>LIC_AUTHCODE</code> as the authorization code. If the parameter <code>--authcode</code> is not used, the program tries to obtain the authorization from the environment variable <code>LIC_AUTHCODE</code>. code. If it is sdk, the start method has an authorization code parameter, and the purchased authorization code can be used.</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="remind">Remind:</h4>
|
||||
|
||||
<p>The commercial version will only check the authorization once online at the time of startup. It will not check the network again later. It will only be checked once the authorization code expires. If the authorization program cannot be successfully checked within 48 hours, it will exit.
|
||||
If the system finds that the user maliciously propagates its own ‘authorization code’, the official has the right to terminate the use of the authorization code and is not responsible for it.</p>
|
||||
|
||||
<h4 id="payment">Payment</h4>
|
||||
|
||||
<p>Buy the commercial version, please email to : [email protected] or telegram : arraykeys .</p>
|
||||
|
||||
<p>BTC and ETH are accepted.</p>
|
||||
|
||||
<p>BTC ADDRESS: <code>1BJcBhGhREiz1q3VTYoiVPuAZy5PGxRG9z</code></p>
|
||||
|
||||
<figure>
|
||||
<img css="width:150px;" src="https://snail.gitee.io/proxy/img/btc.png" alt="GOPROXY Free Version VS Commercial Version img/btc.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<p>ETH ADDRESS: <code>0x0fA4c567768d2E59E6221152EA52F4842866AFC8</code></p>
|
||||
|
||||
<figure>
|
||||
<img css="width:150px;" src="https://snail.gitee.io/proxy/img/eth.png" alt="GOPROXY Free Version VS Commercial Version img/eth.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<h4 id="commercial-edition-trial">Commercial Edition Trial</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>Before purchasing the commercial version, you can try it for free for 7 days to determine if the GOPROXY Commercial Edition feature fit your needs.</p></li>
|
||||
|
||||
<li><p>Trial steps: Log in to <a href="https://gpm.host900.com/?lang=en-US">Authorization Platform</a> -> My Machine Code -> Buy Online -> Click “Start Trial”.</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="commercial-edition-user-additional-benefits">Commercial Edition User Additional Benefits</h4>
|
||||
|
||||
<p>1.the official free of charge provides simple technical guidance.</p>
|
||||
|
||||
<p>2.the commercial version of the user can put forward some commercial functional opinions, the official will evaluate the reasonableness of the opinions, etc. If the opinions are adopted, they will be added in the new version in the future.</p>
|
||||
|
||||
<p>3.the commercial version of the user can be updated to commercial version of the new version for free.</p>
|
||||
|
||||
<p>4.Commercial version download, open the download address below, the file name suffix in the download file list is: _commercial.tar.gz for the commercial version. Please download according to your own system.
|
||||
Download address: <code>https://github.com/snail007/goproxy/releases</code></p>
|
||||
|
||||
<p>5.Full Manual:<a href="https://github.com/snail007/goproxy/blob/master/README.md">https://github.com/snail007/goproxy/blob/master/README.md</a>
|
||||
New Manual:<a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/</a></p>
|
||||
|
||||
<h4 id="can-t-access-the-authorized-solution">Can’t access the authorized solution</h4>
|
||||
|
||||
<p>The commercial version must be online authorized. If you are using the proxy, the server can access the Internet, but the proxy can not access to the authorization information. Can be solved as follows.</p>
|
||||
|
||||
<h5 id="1-if-your-proxy-machine-can-access-the-internet-you-can-specify-the-dns-startup-proxy-because-the-machine-dns-may-not-correctly-resolve-the-updated-domain-name">1. If your proxy machine can access the Internet, you can specify the DNS startup proxy because the machine DNS may not correctly resolve the updated domain name.</h5>
|
||||
|
||||
<p>Linux startup command example:</p>
|
||||
|
||||
<pre><code class="language-shell">LIC_DNS=8.8.4.4:53 ./proxy http -p :9090
|
||||
</code></pre>
|
||||
|
||||
<p>Windows startup command example</p>
|
||||
|
||||
<pre><code class="language-shell">Set LIC_DNS=8.8.4.4:53
|
||||
./proxy.exe http -p :9090
|
||||
</code></pre>
|
||||
|
||||
<h5 id="2-if-the-proxy-is-not-able-to-access-the-internet-directly-in-the-internal-network-environment-you-can-start-an-http-proxy-on-the-machine-that-can-access-the-internet-and-then-use-it-for-the-proxy">2. If the proxy is not able to access the Internet directly in the internal network environment, you can start an http proxy on the machine that can access the Internet, and then use it for the proxy.</h5>
|
||||
|
||||
<p>For example: The proxy is at <code>192.168.1.10</code> and cannot access the Internet directly.</p>
|
||||
|
||||
<p>The machine can access the Internet at <code>192.168.1.200</code>, then it can be started on the <code>192.168.1.200</code> machine:</p>
|
||||
|
||||
<p><code>./proxy http -p :8080 -q 8.8.4.4:53</code></p>
|
||||
|
||||
<p>Start the command above <code>192.168.1.10</code>:</p>
|
||||
|
||||
<p><code>LIC_PROXY=http://192.168.1.200:8080 ./proxy http -p :9090</code></p>
|
||||
|
||||
<h5 id="3-if-the-intranet-has-a-ready-made-http-proxy-then-you-don-t-need-to-start-a-proxy-yourself-in-the-2-steps-lic-proxy-can-use-the-ready-made-http-proxy-directly">3. If the intranet has a ready-made http proxy, then you don’t need to start a proxy yourself in the 2 steps. LIC_PROXY can use the ready-made http proxy directly.</h5>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/">商业版</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/commercial/">commercial</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,296 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/page/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/page/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Pages - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>Pages</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial/">GOPROXY免费版VS商业版</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" title="GOPROXY免费版VS商业版">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:29:13JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/">常见问题解答</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">问:http代理支持https网站吗? 答:goproxy的http代理同时支持http和https网站。 问:socks5代理支持UDP吗? 答</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" title="常见问题解答">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">GOPROXY Free Version VS Commercial Version</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" title="GOPROXY Free Version VS Commercial Version">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T15:29:47JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/categories/">Categories</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">不用看这里,没什么内容,仅仅为了定义目录和tags。</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T13:22:19JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/about/">About</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">It’s YOU!</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,60 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>Pages on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/page/</link>
|
||||
<description>Recent content in Pages on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Wed, 26 Jun 2019 13:19:15 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/page/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>GOPROXY免费版VS商业版</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial/</guid>
|
||||
<description>目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>常见问题解答</title>
|
||||
<link>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:29:13 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</guid>
|
||||
<description>问:http代理支持https网站吗? 答:goproxy的http代理同时支持http和https网站。 问:socks5代理支持UDP吗? 答</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>GOPROXY Free Version VS Commercial Version</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</guid>
|
||||
<description>Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Categories</title>
|
||||
<link>https://snail.gitee.io/proxy/page/categories/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/categories/</guid>
|
||||
<description>不用看这里,没什么内容,仅仅为了定义目录和tags。</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>About</title>
|
||||
<link>https://snail.gitee.io/proxy/page/about/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 13:22:19 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/about/</guid>
|
||||
<description>It&rsquo;s YOU!</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/page/</title><link rel="canonical" href="https://snail.gitee.io/proxy/page/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/page/" /></head></html>
|
||||
@@ -0,0 +1,337 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/posts/cloudflare/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Cloudflare使用简明教程 - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="Cloudflare使用简明教程">
|
||||
|
||||
<meta property="og:title" content="Cloudflare使用简明教程 - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/posts/cloudflare/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="Cloudflare使用简明教程">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/posts/cloudflare/">
|
||||
<meta name="twitter:title" content="Cloudflare使用简明教程 - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="Cloudflare使用简明教程">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "Cloudflare使用简明教程 - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-28T17:37:30JST",
|
||||
"dateModified": "2019-06-28T17:37:30JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "Cloudflare使用简明教程"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/posts/" itemprop="url"><span itemprop="title">posts</span></a></li>
|
||||
|
||||
<li class="active">Cloudflare使用简明教程</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:37:30JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">Cloudflare使用简明教程</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h4 id="前言">前言</h4>
|
||||
|
||||
<p>GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉,为了更好的使用GOPROXY,就找了几个高质量的怎么使用cloudflare免费套餐的文章。</p>
|
||||
|
||||
<h4 id="教程">教程</h4>
|
||||
|
||||
<p>1.不需要修改域名DNS,可以直接使用二级域名加速:<a href="https://www.geekzu.cn/archives/free-cname-cloudflare-with-ssl.html">https://www.geekzu.cn/archives/free-cname-cloudflare-with-ssl.html</a></p>
|
||||
|
||||
<p>2.需要修改域名DNS,使用一级域名加速:<a href="https://ask.dobunkan.com/q-26886.html">https://ask.dobunkan.com/q-26886.html</a></p>
|
||||
|
||||
<p>3.<a href="/goproxy/posts/cloudflare/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/cdn/">CDN</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,413 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/posts/domain-cf/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法 - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="域名解析 域名控制台+极客+cloudflare 的配置方法">
|
||||
|
||||
<meta property="og:title" content="域名解析 域名控制台+极客+cloudflare 的配置方法 - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/posts/domain-cf/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="域名解析 域名控制台+极客+cloudflare 的配置方法">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/posts/domain-cf/">
|
||||
<meta name="twitter:title" content="域名解析 域名控制台+极客+cloudflare 的配置方法 - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="域名解析 域名控制台+极客+cloudflare 的配置方法">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "域名解析 域名控制台\x2b极客\x2bcloudflare 的配置方法 - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-07-05T08:20:48JST",
|
||||
"dateModified": "2019-07-05T08:20:48JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "域名解析 域名控制台\x2b极客\x2bcloudflare 的配置方法"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/posts/" itemprop="url"><span itemprop="title">posts</span></a></li>
|
||||
|
||||
<li class="active">域名解析 域名控制台+极客+cloudflare 的配置方法</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">域名解析 域名控制台+极客+cloudflare 的配置方法</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h4 id="准备工作">准备工作</h4>
|
||||
|
||||
<p>本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。</p>
|
||||
|
||||
<p>首先你要去 cloudflare 官网 <a href="https://dash.cloudflare.com/sign-up">https://dash.cloudflare.com/sign-up</a> 注册一个账号,然后登录,提示你添加域名的时候,不要添加,略过即可。</p>
|
||||
|
||||
<h4 id="操作步骤">操作步骤</h4>
|
||||
|
||||
<p>前提有一顶级域名domain.com,有一VPS,IP地址为111.222.111.222,要求二级域名test.domain.com指向上述IP地址。</p>
|
||||
|
||||
<h5 id="1-在域名domain-com服务器上进行解析">1、在域名domain.com服务器上进行解析</h5>
|
||||
|
||||
<p>例如:</p>
|
||||
|
||||
<p>主记录:vps1</p>
|
||||
|
||||
<p>记录类型:A</p>
|
||||
|
||||
<p>记录值:111.222.111.222</p>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/1.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/1.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<h5 id="2-登陆https-su-geekzu-org平台">2、登陆<a href="https://su.geekzu.org平台">https://su.geekzu.org平台</a></h5>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/2.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/2.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/3.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/3.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/4.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/4.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/5.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/5.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<h5 id="3-点击编辑-添加-填写二级域名test-和回源地址-vps-domain-com到相应的位置-提交">3、点击编辑-》添加-》填写二级域名test,和回源地址:vps.domain.com到相应的位置-》提交</h5>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/6.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/6.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<h5 id="4-提交后会看到如下">4、提交后会看到如下:</h5>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/7.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/7.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<p>这时域名test.domain.com</p>
|
||||
|
||||
<p>回源地址:vps1.domain.com</p>
|
||||
|
||||
<p>CNAME地址:test.domain.com.cdn.cloudflare.net</p>
|
||||
|
||||
<h5 id="5-回到域名解析服务器">5、回到域名解析服务器</h5>
|
||||
|
||||
<p>主机记录:test
|
||||
记录类型:CNAME
|
||||
记录值(也就是上面的CNAME地址):test.domain.com.cdn.cloudflare.net</p>
|
||||
|
||||
<p>填写完成后保存即可。</p>
|
||||
|
||||
<figure>
|
||||
<img css="width:90%" src="https://snail.gitee.io/proxy/img/domain-cloudflare/8.png" alt="域名解析 域名控制台+极客+cloudflare 的配置方法 img/domain-cloudflare/8.png">
|
||||
|
||||
</figure>
|
||||
|
||||
<h5 id="6-如果需要开启ssl-需登陆到cloudflare-crypto-ssl-设置为full">6、如果需要开启ssl,需登陆到cloudflare,Crypto -> SSL ->设置为Full</h5>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/cdn/">cdn</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/domain/">domain</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/ws/">ws</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/cloudflare/">cloudflare</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,347 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/posts/http-nat-cdn/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>内网穿透也能用CDN???! - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="内网穿透通过CDN服务http服务">
|
||||
|
||||
<meta property="og:title" content="内网穿透也能用CDN???! - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/posts/http-nat-cdn/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="内网穿透通过CDN服务http服务">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/posts/http-nat-cdn/">
|
||||
<meta name="twitter:title" content="内网穿透也能用CDN???! - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="内网穿透通过CDN服务http服务">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "内网穿透也能用CDN???! - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-28T17:02:57JST",
|
||||
"dateModified": "2019-06-28T17:02:57JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "内网穿透通过CDN服务http服务"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/posts/" itemprop="url"><span itemprop="title">posts</span></a></li>
|
||||
|
||||
<li class="active">内网穿透也能用CDN???!</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:02:57JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">内网穿透也能用CDN???!</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h4 id="内网穿透之套cdn">内网穿透之套CDN</h4>
|
||||
|
||||
<p><strong>好处就不用说了吧,两个字稳!</strong></p>
|
||||
|
||||
<p>假如在windows上配置了可以访问的连接 <a href="http://127.0.0.1:801/abc/index.php">http://127.0.0.1:801/abc/index.php</a> , 如何能使用VPS+CDN做内网穿透呢?</p>
|
||||
|
||||
<p>配置如下:</p>
|
||||
|
||||
<h5 id="1-在vps上执行-配置无误后-再加上-daemon">1. 在VPS上执行(配置无误后,再加上–daemon)</h5>
|
||||
|
||||
<p><code>./proxy bridge -t ws -p ":8080" -C proxy.crt -K proxy.key</code></p>
|
||||
|
||||
<p><code>./proxy server -T ws -r ":8880@:801" -P "127.0.0.1:8080" -C proxy.crt -K proxy.key</code></p>
|
||||
|
||||
<h5 id="2-在windows上执行">2. 在windows上执行</h5>
|
||||
|
||||
<p><code>proxy.exe client -T ws -P "your.domain.com:8080" -C proxy.crt -K proxy.key</code></p>
|
||||
|
||||
<h5 id="3-这时在浏览器里访问-http-your-domain-com-8880-abc-index-php-就会看到电脑中的页面了">3. 这时在浏览器里访问:<a href="http://your.domain.com:8880/abc/index.php">http://your.domain.com:8880/abc/index.php</a> ,就会看到电脑中的页面了。</h5>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/">内网穿透</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/cdn/">cdn</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,411 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>代理之套用CDN - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="http代理前置CDN,保护你的后端代理">
|
||||
|
||||
<meta property="og:title" content="代理之套用CDN - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/posts/http_cdn_ws/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="http代理前置CDN,保护你的后端代理">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/posts/http_cdn_ws/">
|
||||
<meta name="twitter:title" content="代理之套用CDN - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="http代理前置CDN,保护你的后端代理">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "代理之套用CDN - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-06-14T16:25:06JST",
|
||||
"dateModified": "2019-06-14T16:25:06JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "http代理前置CDN,保护你的后端代理"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/posts/" itemprop="url"><span itemprop="title">posts</span></a></li>
|
||||
|
||||
<li class="active">代理之套用CDN</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">代理之套用CDN</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h3 id="goproxy代理之套用cdn">goproxy代理之套用CDN</h3>
|
||||
|
||||
<h4 id="准备">准备</h4>
|
||||
|
||||
<ol>
|
||||
<li>在VPS上<a href="https://github.com/snail007/goproxy/releases">下载</a>对应平台的执行文件,这里以Linux为例。<br /></li>
|
||||
<li>在电脑上<a href="https://github.com/snail007/goproxy/releases">下载</a>对应平台的执行文件,这里以Windows为例。<br /></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="1-proxy本地http代理-ws-wss-cdn-ws-wss-vps的proxy提供的http代理">1. proxy本地http代理 <–ws\wss–> CDN <–ws\wss–> VPS的proxy提供的http代理</h4>
|
||||
|
||||
<p>1.1. VPS上的命令 ./proxy http -t ws -p “0.0.0.0:8080”</p>
|
||||
|
||||
<p>1.2 Cloudflare上的设置 Crypto -> SSL ->设置为Off</p>
|
||||
|
||||
<p>1.3 windows计算机上的命令 proxy.exe http -t tcp -p “0.0.0.0:8090” -T ws -P “your.domain.com:8080”</p>
|
||||
|
||||
<p>1.4 计算机上的代理设置 “127.0.0.1:8090 http”</p>
|
||||
|
||||
<h4 id="2-proxy本地http代理-ws-wss-cdn-ws-wss-vps的proxy提供的http代理">2. proxy本地http代理 <–ws\wss–> CDN <–ws\wss–> VPS的proxy提供的http代理</h4>
|
||||
|
||||
<p>2.1 VPS上的命令 ./proxy http -t wss -p “0.0.0.0:8443”</p>
|
||||
|
||||
<p>2.2 Cloudflare上的设置 Crypto -> SSL ->设置为Full</p>
|
||||
|
||||
<p>2.3 windows计算机上的命令 proxy.exe http -t tcp -p “0.0.0.0:8090” -T wss -P “your.domain.com:8443”</p>
|
||||
|
||||
<p>2.4 计算机上的代理设置 “127.0.0.1:8090 http”</p>
|
||||
|
||||
<h4 id="3-proxy本地http代理-ws-wss-cdn-ws-wss-vps的proxy提供的http-basic认证-代理-成功">3. proxy本地http代理 <–ws\wss–> CDN <–ws\wss–> VPS的proxy提供的http+Basic认证 代理 (成功)</h4>
|
||||
|
||||
<p>3.1 VPS上的命令 ./proxy http -t ws -p “0.0.0.0:8080” -a “user:pass”</p>
|
||||
|
||||
<p>3.2 Cloudflare上的设置 Crypto -> SSL ->设置为Off</p>
|
||||
|
||||
<p>3.3 windows计算机上的命令 proxy.exe http -t tcp -p “0.0.0.0:8090” -T ws -P “your.domain.com:8080”</p>
|
||||
|
||||
<p>3.4 计算机上的代理设置 “127.0.0.1:8090 http”</p>
|
||||
|
||||
<h4 id="4-proxy本地http代理-ws-wss-cdn-ws-wss-vps的proxy提供的http-加密方式-密码-代理-成功">4. proxy本地http代理 <–ws\wss–> CDN <–ws\wss–> VPS的proxy提供的http+加密方式+密码 代理 (成功)</h4>
|
||||
|
||||
<p>4.1 VPS上的命令 ./proxy http -t wss -p “0.0.0.0:8443” –parent-ws-method=“chacha20-ietf-poly1305” –parent-ws-password=“snail007/goproxy”</p>
|
||||
|
||||
<p>4.2 Cloudflare上的设置 Crypto -> SSL ->设置为Full</p>
|
||||
|
||||
<p>4.3 windows计算机上的命令 proxy.exe http -t tcp -p “0.0.0.0:8090” -T wss -P “your.domain.com:8443” –local-ws-method=“chacha20-ietf-poly1305” –local-ws-password=“snail007/goproxy”</p>
|
||||
|
||||
<p>4.4 计算机上的代理设置 “127.0.0.1:8090 http”</p>
|
||||
|
||||
<p>4.5 相关参数介绍 “–local-ws-method:加密方式–parent-ws-password:设置密码”</p>
|
||||
|
||||
<h4 id="5-proxy本地socks5代理-ws-wss-cdn-ws-wss-vps的proxy提供的socks5代理">5. proxy本地socks5代理 <–ws\wss–> CDN <–ws\wss–> VPS的proxy提供的socks5代理</h4>
|
||||
|
||||
<p>5.1 VPS上的命令 ./proxy socks -t ws -p “0.0.0.0:8080”</p>
|
||||
|
||||
<p>5.2 Cloudflare上的设置 Crypto -> SSL ->设置为Off</p>
|
||||
|
||||
<p>5.3 windows计算机上的命令 proxy.exe socks –always -t tcp -p “0.0.0.0:8090” -T ws -P “your.domain.com:8080”</p>
|
||||
|
||||
<p>5.4 计算机上的代理设置 “127.0.0.1:8090 socks5 [Remote DNS]”</p>
|
||||
|
||||
<h4 id="备注">备注</h4>
|
||||
|
||||
<p>1、Cloudflare支持的回源端口</p>
|
||||
|
||||
<pre><code class="language-text">HTTP 端口为:
|
||||
80
|
||||
8080
|
||||
8880
|
||||
2052
|
||||
2082
|
||||
2086
|
||||
2095
|
||||
HTTPs 端口为:
|
||||
443
|
||||
2053
|
||||
2083
|
||||
2087
|
||||
2096
|
||||
8443
|
||||
</code></pre>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/cdn/">cdn</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/ws/">ws</a></li>
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/cloudflare/">cloudflare</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,304 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/posts/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/posts/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Posts - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>Posts</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T17:54:31JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">在windows下实现基于dns的自动全局代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" title="在windows下实现基于dns的自动全局代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:37:30JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/cloudflare/">Cloudflare使用简明教程</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" title="Cloudflare使用简明教程">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:02:57JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/">内网穿透也能用CDN???!</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" title="内网穿透也能用CDN???!">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">代理之套用CDN</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" title="代理之套用CDN">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,60 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>Posts on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/</link>
|
||||
<description>Recent content in Posts on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/posts/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>在windows下实现基于dns的自动全局代理</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 17:54:31 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</guid>
|
||||
<description>在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Cloudflare使用简明教程</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/cloudflare/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:37:30 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/cloudflare/</guid>
|
||||
<description>前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>内网穿透也能用CDN???!</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http-nat-cdn/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:02:57 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http-nat-cdn/</guid>
|
||||
<description>内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>代理之套用CDN</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http_cdn_ws/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:25:06 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http_cdn_ws/</guid>
|
||||
<description>goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/posts/</title><link rel="canonical" href="https://snail.gitee.io/proxy/posts/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/posts/" /></head></html>
|
||||
@@ -0,0 +1,391 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>在windows下实现基于dns的自动全局代理 - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="在windows下实现基于dns的自动全局代理">
|
||||
|
||||
<meta property="og:title" content="在windows下实现基于dns的自动全局代理 - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="在windows下实现基于dns的自动全局代理">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">
|
||||
<meta name="twitter:title" content="在windows下实现基于dns的自动全局代理 - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="在windows下实现基于dns的自动全局代理">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "在windows下实现基于dns的自动全局代理 - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-07-04T17:54:31JST",
|
||||
"dateModified": "2019-07-04T17:54:31JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "在windows下实现基于dns的自动全局代理"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/posts/" itemprop="url"><span itemprop="title">posts</span></a></li>
|
||||
|
||||
<li class="active">在windows下实现基于dns的自动全局代理</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T17:54:31JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">在windows下实现基于dns的自动全局代理</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h3 id="在windows下实现基于dns的自动全局代理">在windows下实现基于dns的自动全局代理。</h3>
|
||||
|
||||
<p>本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。</p>
|
||||
|
||||
<p>本文提供了两种方式:1.使用CDN作为中间传输层 2.不使用CDN;根据自己情况二选一即可。</p>
|
||||
|
||||
<h4 id="1-正常配置篇">1.正常配置篇</h4>
|
||||
|
||||
<p>服务端为机器A</p>
|
||||
|
||||
<p>1、在上级服务端执行:</p>
|
||||
|
||||
<p><code>./proxy http -t ws -p 0.0.0.0:8443 —-daemon</code></p>
|
||||
|
||||
<p>3、在电脑上:</p>
|
||||
|
||||
<p>1)修改proxy目录下面的hosts文件,该文件和proxy.exe程序一起。</p>
|
||||
|
||||
<p>添加如下内容:</p>
|
||||
|
||||
<pre><code class="language-text">127.0.0.1 **.**
|
||||
|
||||
</code></pre>
|
||||
|
||||
<p>2)修改本地网络连接的dns地址为127.0.0.1。</p>
|
||||
|
||||
<p>3)本机启动一个二级sps监听80和443。</p>
|
||||
|
||||
<p><code>proxy.exe sps -P httpws://IP_A:8443 -p :80,:443 -q 8.8.8.8:53</code></p>
|
||||
|
||||
<p>4)本地启动一个dns监听53 <code>.\proxy.exe dns -P http://127.0.0.1:80 --hosts .\hosts</code> 。</p>
|
||||
|
||||
<h4 id="2-配合cdn配置篇">2.配合CDN配置篇</h4>
|
||||
|
||||
<p>1、配置好cloudflare,CDN加速域名为:your.domain.com。</p>
|
||||
|
||||
<p>2、在上级服务端执行:</p>
|
||||
|
||||
<p>首先生成证书:</p>
|
||||
|
||||
<p><code>proxy keygen -C proxy</code></p>
|
||||
|
||||
<p>然后:</p>
|
||||
|
||||
<p><code>./proxy http -t wss -p 0.0.0.0:8443 —-daemon</code></p>
|
||||
|
||||
<p>3、在电脑上:</p>
|
||||
|
||||
<p>1)修改proxy目录下面的hosts文件,该文件和proxy.exe程序一起。</p>
|
||||
|
||||
<p>添加如下内容:</p>
|
||||
|
||||
<pre><code class="language-text">111.222.111.222 your.domain.com
|
||||
|
||||
127.0.0.1 **.**
|
||||
|
||||
</code></pre>
|
||||
|
||||
<p>2)修改本地网络连接的dns地址为127.0.0.1。</p>
|
||||
|
||||
<p>3)本机启动一个二级sps监听80和443。</p>
|
||||
|
||||
<p><code>proxy.exe sps -P httpwss://your.domain.com:8443 -p :80,:443 -q 8.8.8.8:53</code></p>
|
||||
|
||||
<p>4)本地启动一个dns监听53 <code>.\proxy.exe dns -P http://127.0.0.1:80 -—hosts .\hosts</code> 。</p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/">默认分类</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/">全局代理</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1 @@
|
||||
User-agent: *
|
||||
@@ -0,0 +1,179 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<urlset xmlns="http://www.sitemaps.org/schemas/sitemap/0.9"
|
||||
xmlns:xhtml="http://www.w3.org/1999/xhtml">
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/usage/first/</loc>
|
||||
<lastmod>2019-07-04T11:00:50+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/page/free_vs_commercial/</loc>
|
||||
<lastmod>2019-06-26T13:19:15+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/</loc>
|
||||
<lastmod>2019-06-14T16:29:13+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/categories/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/posts/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/cdn/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/cloudflare/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/domain/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/ws/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/posts/domain-cf/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB/</loc>
|
||||
<lastmod>2019-07-05T08:20:48+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/</loc>
|
||||
<lastmod>2019-07-04T17:54:31+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</loc>
|
||||
<lastmod>2019-07-04T17:54:31+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/</loc>
|
||||
<lastmod>2019-07-04T11:00:50+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/usage/tcp/</loc>
|
||||
<lastmod>2019-07-04T11:00:50+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/usage/</loc>
|
||||
<lastmod>2019-07-04T11:00:50+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/tcp/</loc>
|
||||
<lastmod>2019-07-04T11:00:50+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/posts/cloudflare/</loc>
|
||||
<lastmod>2019-06-28T17:37:30+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/</loc>
|
||||
<lastmod>2019-06-28T17:02:57+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/posts/http-nat-cdn/</loc>
|
||||
<lastmod>2019-06-28T17:02:57+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</loc>
|
||||
<lastmod>2019-06-26T13:19:15+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/page/</loc>
|
||||
<lastmod>2019-06-26T13:19:15+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/commercial/</loc>
|
||||
<lastmod>2019-06-26T13:19:15+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/</loc>
|
||||
<lastmod>2019-06-26T13:19:15+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/posts/http_cdn_ws/</loc>
|
||||
<lastmod>2019-06-14T16:25:06+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/page/categories/</loc>
|
||||
<lastmod>2019-06-14T15:29:47+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4/</loc>
|
||||
<lastmod>2019-06-14T15:29:47+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7/</loc>
|
||||
<lastmod>2019-06-14T15:29:47+08:00</lastmod>
|
||||
<priority>0</priority>
|
||||
</url>
|
||||
|
||||
<url>
|
||||
<loc>https://snail.gitee.io/proxy/page/about/</loc>
|
||||
<lastmod>2019-06-14T13:22:19+08:00</lastmod>
|
||||
</url>
|
||||
|
||||
</urlset>
|
||||
@@ -0,0 +1,283 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/cdn/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/cdn/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>cdn - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>cdn</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:37:30JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/cloudflare/">Cloudflare使用简明教程</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" title="Cloudflare使用简明教程">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:02:57JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/">内网穿透也能用CDN???!</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" title="内网穿透也能用CDN???!">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">代理之套用CDN</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" title="代理之套用CDN">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,51 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>cdn on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/cdn/</link>
|
||||
<description>Recent content in cdn on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/cdn/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Cloudflare使用简明教程</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/cloudflare/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:37:30 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/cloudflare/</guid>
|
||||
<description>前言 GOPROXY底层传输协议支持ws,可以利用cdn加速,使用cdn需要域名解析知识以及cdn的一些知识,那么很多小伙伴对cdn不是很熟悉</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>内网穿透也能用CDN???!</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http-nat-cdn/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:02:57 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http-nat-cdn/</guid>
|
||||
<description>内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>代理之套用CDN</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http_cdn_ws/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:25:06 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http_cdn_ws/</guid>
|
||||
<description>goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/cdn/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/cdn/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/cdn/" /></head></html>
|
||||
@@ -0,0 +1,241 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/cloudflare/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/cloudflare/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>cloudflare - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>cloudflare</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">代理之套用CDN</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" title="代理之套用CDN">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,33 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>cloudflare on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/cloudflare/</link>
|
||||
<description>Recent content in cloudflare on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/cloudflare/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>代理之套用CDN</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http_cdn_ws/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:25:06 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http_cdn_ws/</guid>
|
||||
<description>goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/cloudflare/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/cloudflare/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/cloudflare/" /></head></html>
|
||||
@@ -0,0 +1,220 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/commercial/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/commercial/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>commercial - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>commercial</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">GOPROXY Free Version VS Commercial Version</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" title="GOPROXY Free Version VS Commercial Version">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>commercial on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/commercial/</link>
|
||||
<description>Recent content in commercial on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Wed, 26 Jun 2019 13:19:15 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/commercial/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>GOPROXY Free Version VS Commercial Version</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</guid>
|
||||
<description>Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/commercial/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/commercial/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/commercial/" /></head></html>
|
||||
@@ -0,0 +1,220 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/domain/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/domain/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>domain - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>domain</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>domain on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/domain/</link>
|
||||
<description>Recent content in domain on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/domain/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/domain/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/domain/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/domain/" /></head></html>
|
||||
@@ -0,0 +1,215 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Tags - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<header class="page-header">
|
||||
<h1>Tags</h1>
|
||||
</header>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="list-group">
|
||||
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn <span class="badge">4</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare <span class="badge">2</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws <span class="badge">3</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理 <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透 <span class="badge">1</span></a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版 <span class="badge">2</span></a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,96 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>Tags on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/</link>
|
||||
<description>Recent content in Tags on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>cdn</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/cdn/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/cdn/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>cloudflare</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/cloudflare/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/cloudflare/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>domain</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/domain/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/domain/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>ws</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/ws/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/ws/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>全局代理</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 17:54:31 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>tcp</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/tcp/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/tcp/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>内网穿透</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:02:57 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>commercial</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/commercial/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/commercial/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>商业版</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/</guid>
|
||||
<description></description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1,220 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/tcp/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/tcp/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>tcp - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>tcp</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/tcp/">TCP代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" title="TCP代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>tcp on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/tcp/</link>
|
||||
<description>Recent content in tcp on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Thu, 04 Jul 2019 11:00:50 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/tcp/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>TCP代理</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/tcp/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/tcp/</guid>
|
||||
<description>工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/tcp/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/tcp/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/tcp/" /></head></html>
|
||||
@@ -0,0 +1,258 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/ws/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/ws/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>ws - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>ws</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-05T08:20:48JST">Jul 5, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/domain-cf/">域名解析 域名控制台+极客+cloudflare 的配置方法</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" title="域名解析 域名控制台+极客+cloudflare 的配置方法">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T16:25:06JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/">代理之套用CDN</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" title="代理之套用CDN">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-14T15:29:47JST">Jun 14, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/categories/">Categories</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">不用看这里,没什么内容,仅仅为了定义目录和tags。</div>
|
||||
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,42 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>ws on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/ws/</link>
|
||||
<description>Recent content in ws on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 05 Jul 2019 08:20:48 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/ws/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>域名解析 域名控制台+极客+cloudflare 的配置方法</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/domain-cf/</link>
|
||||
<pubDate>Fri, 05 Jul 2019 08:20:48 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/domain-cf/</guid>
|
||||
<description>准备工作 本文综合的介绍了cloudflare注册使用,从域名解析到回源,完成了一个二级域使用cloudflare的CDN加速的配置过程。 首先</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>代理之套用CDN</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http_cdn_ws/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 16:25:06 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http_cdn_ws/</guid>
|
||||
<description>goproxy代理之套用CDN 准备 在VPS上下载对应平台的执行文件,这里以Linux为例。 在电脑上下载对应平台的执行文件,这里以Window</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>Categories</title>
|
||||
<link>https://snail.gitee.io/proxy/page/categories/</link>
|
||||
<pubDate>Fri, 14 Jun 2019 15:29:47 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/categories/</guid>
|
||||
<description>不用看这里,没什么内容,仅仅为了定义目录和tags。</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/ws/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/ws/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/ws/" /></head></html>
|
||||
@@ -0,0 +1,220 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>全局代理 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>全局代理</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T17:54:31JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/">在windows下实现基于dns的自动全局代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" title="在windows下实现基于dns的自动全局代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>全局代理 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/</link>
|
||||
<description>Recent content in 全局代理 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Thu, 04 Jul 2019 17:54:31 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>在windows下实现基于dns的自动全局代理</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 17:54:31 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/</guid>
|
||||
<description>在windows下实现基于dns的自动全局代理。 本方法需要监听本地80和443端口,所以如果你有程序占用了这两个端口,请关闭相应的程序。 本文</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86/" /></head></html>
|
||||
@@ -0,0 +1,220 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>内网穿透 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>内网穿透</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-28T17:02:57JST">Jun 28, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/posts/">posts</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/">内网穿透也能用CDN???!</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" title="内网穿透也能用CDN???!">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,24 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>内网穿透 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/</link>
|
||||
<description>Recent content in 内网穿透 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Fri, 28 Jun 2019 17:02:57 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>内网穿透也能用CDN???!</title>
|
||||
<link>https://snail.gitee.io/proxy/posts/http-nat-cdn/</link>
|
||||
<pubDate>Fri, 28 Jun 2019 17:02:57 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/posts/http-nat-cdn/</guid>
|
||||
<description>内网穿透之套CDN 好处就不用说了吧,两个字稳! 假如在windows上配置了可以访问的连接 http://127.0.0.1:801/abc/index.php , 如何能使用VPS+CDN做内网穿透呢? 配置如下:</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F/" /></head></html>
|
||||
@@ -0,0 +1,241 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>商业版 - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>商业版</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial/">GOPROXY免费版VS商业版</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" title="GOPROXY免费版VS商业版">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-06-26T13:19:15JST">Jun 26, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/page/">page</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/">GOPROXY Free Version VS Commercial Version</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" title="GOPROXY Free Version VS Commercial Version">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,33 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>商业版 on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/</link>
|
||||
<description>Recent content in 商业版 on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Wed, 26 Jun 2019 13:19:15 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>GOPROXY免费版VS商业版</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial/</guid>
|
||||
<description>目前,GOPROXY 和 SDK 提供免费版和商业版,功能对比如下。 免费版 商业版 TCP转发 √ √ UDP转发 √ √ HTTP(S)代理 √ √ Socks5代理 √ √</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>GOPROXY Free Version VS Commercial Version</title>
|
||||
<link>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</link>
|
||||
<pubDate>Wed, 26 Jun 2019 13:19:15 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/page/free_vs_commercial_en/</guid>
|
||||
<description>Currently, GOPROXY and SDK are available in both free and commercial versions. Function Free |Commercial TCP forwarding √ √ UDP forwarding √ √ HTTP(S)Agent √ √ Socks5 Agent √ √ Socks5 proxy UDP support √ √ SPS Integrated Agent √ √ SPS superior certification √ √ Intranet penetration √ √ DNS proxy, anti-pollution, independent DNS service √ √ HTTP(S) proxy authentication, authentication API, load balancing × √ SOCKS5 proxy authentication,</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/</title><link rel="canonical" href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88/" /></head></html>
|
||||
@@ -0,0 +1,419 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/usage/first/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>手册前言(使用必读) - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="GOPROXY手册使用">
|
||||
|
||||
<meta property="og:title" content="手册前言(使用必读) - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/usage/first/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="GOPROXY手册使用">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/usage/first/">
|
||||
<meta name="twitter:title" content="手册前言(使用必读) - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="GOPROXY手册使用">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "手册前言(使用必读) - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-07-04T11:00:50JST",
|
||||
"dateModified": "2019-07-04T11:00:50JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "GOPROXY手册使用"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/usage/" itemprop="url"><span itemprop="title">usage</span></a></li>
|
||||
|
||||
<li class="active">手册前言(使用必读)</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">手册前言(使用必读)</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h3 id="前言">前言</h3>
|
||||
|
||||
<h4 id="goproxy使用必读">GOPROXY使用必读</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释,不然直接看具体手册章节必然会出现理解偏差,导致不能正确的使用goproxy。</p></li>
|
||||
|
||||
<li><p>goproxy的很多功能都使用了相同的核心技术,比如底层传输:tcps传输协议,ws协议,kcp参数,黑白名单,认证等,它们的用法是一样的。
|
||||
为了手册的简洁,相同的功能的说明,就放在这里统一说明,不在每个地方重复的说明。</p></li>
|
||||
|
||||
<li><p>proxy功能很多,往往你想要用的只是其中一个功能,那么不要被手册其它功能内容吓到和干扰,你只需要看前言和你需要用到的功能的手册部分即可!</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="名词解释">名词解释</h4>
|
||||
|
||||
<p>本站包括项目手册,如果没有特殊说明:</p>
|
||||
|
||||
<ol>
|
||||
<li><p><code>goproxy</code>,<code>proxy</code>,均指本项目:<a href="https://github.com/snail007/goproxy">https://github.com/snail007/goproxy</a> 。</p></li>
|
||||
|
||||
<li><p><code>本地</code>,均指<code>需要使用代理的应用程序</code>直接连接的<code>代理</code>,一般是你日常使用的机器,也可能是一个服务器。</p></li>
|
||||
|
||||
<li><p><code>代理链</code>,指多个相连的代理组成的一个代理链条,一个代理链中至少有两个上下相连的代理,链条中的每一个代理不一定都是proxy提供的,可以是第三方标准代理。</p>
|
||||
|
||||
<p>为了区分,链条的 <strong><em>末端</em></strong> 是入口,称为<code>本地代理</code>是最后一级;链条的 <strong><em>顶端</em></strong> 是出口,称为<code>一级</code>代理。</p>
|
||||
|
||||
<p>连接一级代理的是二级代理,连接二级代理的是三级级代理,以此类推。</p>
|
||||
|
||||
<p>由此可见,本地和一级代理是链条的两端,链条中至少两个代理,链条中间的称为n级代理,越靠近本地n就越大。</p>
|
||||
|
||||
<p>如果链条只有两个代理,那么二级代理和本地代理指的是同一个代理。</p></li>
|
||||
|
||||
<li><p><code>本级</code>,均指链条中,任意一个代理。</p></li>
|
||||
|
||||
<li><p><code>上级</code>,<code>父级</code>,<code>parent</code>,均指:本级代理连接的上一级代理,可以是proxy提供的代理也可以是第三方标准代理。</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="分层架构">分层架构</h4>
|
||||
|
||||
<ol>
|
||||
<li><p>goproxy数据流动架构,主要分为两层。</p></li>
|
||||
|
||||
<li><p>上层是我们熟悉的各种标准服务:socks5代理,http(s)代理,sps代理(ss+http(s)+socks5),tcp代理,udp代理,dns代理,内网穿透。</p>
|
||||
|
||||
<p>也就是命令中的第一参数,代表服务,也称为功能模块,功能。比如:http,socks,sps,tcp,udp,dns等。</p></li>
|
||||
|
||||
<li><p>下层也就是底层,负责数据传输,传输的协议和有很多,比如:tcp,tcps,ws,tls,wss,tou,kcp,不同的协议使用的基础协议也是不一样的,</p>
|
||||
|
||||
<p>其中除了tou和kcp使用UDP作为基础协议之外,其它传输协议均是基于TCP。也就是说tou和kcp监听的是UDP端口,其它监听的是TCP端口。</p>
|
||||
|
||||
<p>传输协议在proxy的参数中体现为-T、-t,-T是连接上级使用的传输协议。-t是本地监听的端口使用的传输协议。</p>
|
||||
|
||||
<p>本级代理的-T和和上级代理的-t应该是一致的,不然是无法通讯的,这很好理解,对方说什么语言你用什么语言去聆听才能明白对方说些什么。</p></li>
|
||||
</ol>
|
||||
|
||||
<h4 id="ip地址">IP地址</h4>
|
||||
|
||||
<p>由于代理示例用到各种IP,示例中统一用IP_X,X是机器名词代号,比如A,B,这样的形式表示一个机器的IP;你在复制命令后实际使用前,记得一定要根据自己情况替换IP_X为你自己的实际IP地址。如果示例中提到了机器A,那么默认它的IP地址就是IP_A,不再重复声明。</p>
|
||||
|
||||
<h4 id="高级使用">高级使用</h4>
|
||||
|
||||
<p>proxy命令格式是:proxy <code>功能名称</code> 参数1 参数2 参数n…,proxy功能名称和功能介绍如下:</p>
|
||||
|
||||
<p><code>http</code> http(s)代理</p>
|
||||
|
||||
<p><code>socks</code> socks5代理</p>
|
||||
|
||||
<p><code>sps</code> http(s)+socks5+ss综合代理,一个端口同时支持3种代理</p>
|
||||
|
||||
<p><code>tcp</code> tcp代理,tcp端口转发</p>
|
||||
|
||||
<p><code>udp</code> udp代理,udp端口转发</p>
|
||||
|
||||
<p><code>dns</code> dns代理,dns服务器,dns转发</p>
|
||||
|
||||
<p><code>bridge</code> 多路复用版内网穿透的bridge端</p>
|
||||
|
||||
<p><code>client</code> 多路复用版内网穿透的client端</p>
|
||||
|
||||
<p><code>server</code> 多路复用版内网穿透的server端</p>
|
||||
|
||||
<p><code>tbridge</code> 多链接版内网穿透的bridge端</p>
|
||||
|
||||
<p><code>tclient</code> 多链接版内网穿透的client端</p>
|
||||
|
||||
<p><code>tserver</code> 多链接版内网穿透的server端</p>
|
||||
|
||||
<p>由于每个功能参数众多,有的很少用,默认值就能很好工作,手册只是介绍了高频的参数的使用,未提及的参数可以通过 proxy help <code>功能名称</code> ,查看到功能相关所有的参数。</p>
|
||||
|
||||
<p>如果你想深入了解和掌握proxy每个功能的用法,那么动起手来试试每个参数吧,去体会,去感受就能深刻理解并熟练掌握它。</p>
|
||||
|
||||
<h4 id="kcp配置">KCP配置</h4>
|
||||
|
||||
<p>很多功能的底层传输协议都支持kcp,kcp参数都是以<code>--kcp</code>开头,可以通过proxy help 功能名称 ,比如:proxy help http,去查看所有的参数,包括kcp参数。</p>
|
||||
|
||||
<p>虽然参数很多,但是proxy针对大众情况,设置了一波默认值,如果发现默认参数不合你口味,那么你就需要自己搜索kcp每个参数的意思和用法,资料很多,本手册不再赘述。</p>
|
||||
|
||||
<p>当然最简单的用法就是设置一个kcp密码即可,KCP协议需要–kcp-key参数设置一个密码用于加密解密数据。</p>
|
||||
|
||||
<h4 id="tls证书">TLS证书</h4>
|
||||
|
||||
<p>为了安全很多功能都可以使用底层tls传输协议加密传输数据,tls需要一个proxy.crt证书文件和一个私钥proxy.key文件。</p>
|
||||
|
||||
<p>这两个文件可以通过命令:<code>proxy keygen proxy</code> 生成。</p>
|
||||
|
||||
<p>另外,tls证书只需要在一个proxy端生成,其它端复制过去即可,要保证所有端证书一样。</p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/">GOPROXY手册</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,241 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
<link rel="alternate" type="application/rss+xml" title="RSS" href="https://snail.gitee.io/proxy/usage/index.xml">
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/usage/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>Usages - GOPROXY IN ACTION</title>
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
|
||||
<header class="page-header">
|
||||
<h1>Usages</h1>
|
||||
</header>
|
||||
|
||||
|
||||
<ul class="p-articles">
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/first/">手册前言(使用必读)</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">前言 GOPROXY使用必读 手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" title="手册前言(使用必读)">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
<li><article class="li">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
<h2 class="title"><a href="https://snail.gitee.io/proxy/usage/tcp/">TCP代理</a></h2>
|
||||
</header>
|
||||
|
||||
|
||||
<div class="summary">工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</div>
|
||||
|
||||
|
||||
<footer>
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" title="TCP代理">Read More…</a>
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
</li>
|
||||
|
||||
</ul>
|
||||
|
||||
|
||||
|
||||
|
||||
</div>
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,33 @@
|
||||
<?xml version="1.0" encoding="utf-8" standalone="yes" ?>
|
||||
<rss version="2.0" xmlns:atom="http://www.w3.org/2005/Atom">
|
||||
<channel>
|
||||
<title>Usages on GOPROXY IN ACTION</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/</link>
|
||||
<description>Recent content in Usages on GOPROXY IN ACTION</description>
|
||||
<generator>Hugo -- gohugo.io</generator>
|
||||
<language>zh-CN</language>
|
||||
<lastBuildDate>Thu, 04 Jul 2019 11:00:50 +0800</lastBuildDate>
|
||||
|
||||
<atom:link href="https://snail.gitee.io/proxy/usage/index.xml" rel="self" type="application/rss+xml" />
|
||||
|
||||
|
||||
<item>
|
||||
<title>手册前言(使用必读)</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/first/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/first/</guid>
|
||||
<description>前言 GOPROXY使用必读 手册和项目中使用了一部分的名词,它们本身的含义和在goproxy的专有含义是不一样的,所以前言中对这些名词做了解释</description>
|
||||
</item>
|
||||
|
||||
<item>
|
||||
<title>TCP代理</title>
|
||||
<link>https://snail.gitee.io/proxy/usage/tcp/</link>
|
||||
<pubDate>Thu, 04 Jul 2019 11:00:50 +0800</pubDate>
|
||||
|
||||
<guid>https://snail.gitee.io/proxy/usage/tcp/</guid>
|
||||
<description>工作原理 tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。 上级可以是p</description>
|
||||
</item>
|
||||
|
||||
</channel>
|
||||
</rss>
|
||||
@@ -0,0 +1 @@
|
||||
<!DOCTYPE html><html><head><title>https://snail.gitee.io/proxy/usage/</title><link rel="canonical" href="https://snail.gitee.io/proxy/usage/"/><meta name="robots" content="noindex"><meta charset="utf-8" /><meta http-equiv="refresh" content="0; url=https://snail.gitee.io/proxy/usage/" /></head></html>
|
||||
@@ -0,0 +1,357 @@
|
||||
<!DOCTYPE html>
|
||||
<html>
|
||||
<head>
|
||||
<meta charset="utf-8">
|
||||
<meta name="pinterest" content="nopin">
|
||||
<meta name="viewport" content="width=device-width,minimum-scale=1,initial-scale=1">
|
||||
<meta name="generator" content="Hugo 0.56.3" />
|
||||
|
||||
|
||||
|
||||
<link rel="canonical" href="https://snail.gitee.io/proxy/usage/tcp/">
|
||||
|
||||
|
||||
<link href="//maxcdn.bootstrapcdn.com/font-awesome/4.5.0/css/font-awesome.min.css" rel="stylesheet">
|
||||
<link rel="stylesheet" href="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/css/bootstrap.min.css">
|
||||
<link rel="stylesheet" href="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/styles/solarized_dark.min.css">
|
||||
<title>TCP代理 - GOPROXY IN ACTION</title>
|
||||
|
||||
<meta name="description" content="GOPROXY手册之TCP代理的使用">
|
||||
|
||||
<meta property="og:title" content="TCP代理 - GOPROXY IN ACTION">
|
||||
<meta property="og:type" content="article">
|
||||
<meta property="og:url" content="https://snail.gitee.io/proxy/usage/tcp/">
|
||||
<meta property="og:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
<meta property="og:site_name" content="GOPROXY IN ACTION">
|
||||
<meta property="og:description" content="GOPROXY手册之TCP代理的使用">
|
||||
<meta property="og:locale" content="zh_CN">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:site" content="GOPROXY IN ACTION">
|
||||
<meta name="twitter:url" content="https://snail.gitee.io/proxy/usage/tcp/">
|
||||
<meta name="twitter:title" content="TCP代理 - GOPROXY IN ACTION">
|
||||
<meta name="twitter:description" content="GOPROXY手册之TCP代理的使用">
|
||||
<meta name="twitter:image" content="https://snail.gitee.io/proxy/images/default.png">
|
||||
|
||||
|
||||
<script type="application/ld+json">
|
||||
{
|
||||
"@context": "http://schema.org",
|
||||
"@type": "NewsArticle",
|
||||
"mainEntityOfPage": {
|
||||
"@type": "WebPage",
|
||||
"@id":"https:\/\/snail.gitee.io\/proxy\/"
|
||||
},
|
||||
"headline": "TCP代理 - GOPROXY IN ACTION",
|
||||
"image": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images\/default.png",
|
||||
"height": 800,
|
||||
"width": 800
|
||||
},
|
||||
"datePublished": "2019-07-04T11:00:50JST",
|
||||
"dateModified": "2019-07-04T11:00:50JST",
|
||||
"author": {
|
||||
"@type": "Person",
|
||||
"name": "GOPROXY IN ACTION"
|
||||
},
|
||||
"publisher": {
|
||||
"@type": "Organization",
|
||||
"name": "GOPROXY IN ACTION",
|
||||
"logo": {
|
||||
"@type": "ImageObject",
|
||||
"url": "https:\/\/snail.gitee.io\/proxy\/images/logo.png",
|
||||
"width": 600,
|
||||
"height": 60
|
||||
}
|
||||
},
|
||||
"description": "GOPROXY手册之TCP代理的使用"
|
||||
}
|
||||
</script>
|
||||
|
||||
|
||||
<link href="https://snail.gitee.io/proxy/css/styles.css" rel="stylesheet">
|
||||
|
||||
|
||||
</head>
|
||||
|
||||
<body>
|
||||
|
||||
|
||||
|
||||
|
||||
<header class="l-header">
|
||||
<nav class="navbar navbar-default">
|
||||
<div class="container">
|
||||
<div class="navbar-header">
|
||||
<button type="button" class="navbar-toggle collapsed" data-toggle="collapse" data-target="#navbar" aria-expanded="false">
|
||||
<span class="sr-only">Toggle navigation</span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
<span class="icon-bar"></span>
|
||||
</button>
|
||||
<a class="navbar-brand" href="https://snail.gitee.io/proxy/">GOPROXY IN ACTION</a>
|
||||
</div>
|
||||
|
||||
|
||||
<div id="navbar" class="collapse navbar-collapse">
|
||||
|
||||
<ul class="nav navbar-nav navbar-right">
|
||||
|
||||
|
||||
<li><a href="https://github.com/snail007/goproxy/releases/">下载</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/manual/zh/#/">完全手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="https://snail007.github.io/goproxy/categories/goproxy%E6%89%8B%E5%86%8C/">新版手册</a></li>
|
||||
|
||||
|
||||
|
||||
<li><a href="/proxy/about/">关于</a></li>
|
||||
|
||||
|
||||
</ul>
|
||||
|
||||
</div>
|
||||
|
||||
|
||||
</div>
|
||||
</nav>
|
||||
</header>
|
||||
|
||||
<main>
|
||||
<div class="container">
|
||||
|
||||
<div class="row">
|
||||
<div class="col-md-8">
|
||||
|
||||
<nav class="p-crumb">
|
||||
<ol class="breadcrumb">
|
||||
<li><a href="https://snail.gitee.io/proxy/"><i class="fa fa-home" aria-hidden="true"></i></a></li>
|
||||
|
||||
<li itemscope="" itemtype="http://data-vocabulary.org/Breadcrumb"><a href="https://snail.gitee.io/proxy/usage/" itemprop="url"><span itemprop="title">usage</span></a></li>
|
||||
|
||||
<li class="active">TCP代理</li>
|
||||
</ol>
|
||||
</nav>
|
||||
|
||||
<article class="single">
|
||||
<header>
|
||||
<ul class="p-facts">
|
||||
<li><i class="fa fa-calendar" aria-hidden="true"></i><time datetime="2019-07-04T11:00:50JST">Jul 4, 2019</time></li>
|
||||
<li><i class="fa fa-bookmark" aria-hidden="true"></i><a href="https://snail.gitee.io/proxy/usage/">usage</a></li>
|
||||
|
||||
</ul>
|
||||
|
||||
<h1 class="title">TCP代理</h1>
|
||||
</header>
|
||||
|
||||
|
||||
|
||||
<div class="article-body">
|
||||
|
||||
<h3 id="工作原理">工作原理</h3>
|
||||
|
||||
<p>tcp代理,也称为tcp端口转发,工作原理就是,把proxy监听端口进来的tcp连接的数据原样转发到上级监听的一个端口。</p>
|
||||
|
||||
<p>上级可以是proxy的tcp代理也可以是具体的第三方服务,如果上级是tcp代理,那么就组成了转发链。至于转发链可以做什么看自己业务需求。</p>
|
||||
|
||||
<h3 id="使用示例">使用示例</h3>
|
||||
|
||||
<h4 id="转发ssh的22端口">转发ssh的22端口</h4>
|
||||
|
||||
<p>典型场景,一个机器A拥有公网IP,B机器和A机器在一个局域网,机器B处于内网中,外网不能直接访问。想通过ssh连接A机器的2022端口实现ssh登录B机器的ssh的22端口。</p>
|
||||
|
||||
<p>A机器执行:</p>
|
||||
|
||||
<p><code>proxy tcp -t tcp -p :2022 -T tcp -P IP_B:22</code></p>
|
||||
|
||||
<p>任何机器上 执行 <code>ssh root@IP_A:2022</code> 即可登录B机器。</p>
|
||||
|
||||
<h4 id="转发链">转发链</h4>
|
||||
|
||||
<p>典型场景,公网机器A由于公司或者其它网络限制导致你不能直接访问,B机器和A机器在一个局域网,机器B处于内网中,外网不能直接访问。想通过ssh连接A机器的2022端口实现ssh登录B机器的ssh的22端口,但是公网机器C你可以访问,C也可以访问A,那么你就可以这样组成转发链:你本地ssh ->>> C ->>> A ->>> B,最终达到你安全访问B机器的目的。</p>
|
||||
|
||||
<p>A机器执行:</p>
|
||||
|
||||
<p><code>proxy tcp -t ws -p :2022 -T tcp -P IP_B:22</code></p>
|
||||
|
||||
<p>机器C执行:</p>
|
||||
|
||||
<p><code>proxy tcp -t tcp -p :2022 -T ws -P IP_A:2022</code></p>
|
||||
|
||||
<p>任何机器上,当然包括你的机器,执行 <code>ssh root@IP_C:2022</code> 即可登录B机器。</p>
|
||||
</div>
|
||||
|
||||
<footer class="article-footer">
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">CATEGORIES</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C/">GOPROXY手册</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
|
||||
<section class="bordered">
|
||||
<header>
|
||||
<div class="panel-title">TAGS</div>
|
||||
</header>
|
||||
<div>
|
||||
<ul class="p-terms">
|
||||
|
||||
<li><a href="https://snail.gitee.io/proxy/tags/tcp/">tcp</a></li>
|
||||
|
||||
</ul>
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</footer>
|
||||
|
||||
</article>
|
||||
|
||||
|
||||
<div id="disqus_thread"></div>
|
||||
<script type="application/javascript">
|
||||
var disqus_config = function () {
|
||||
|
||||
|
||||
|
||||
};
|
||||
(function() {
|
||||
if (["localhost", "127.0.0.1"].indexOf(window.location.hostname) != -1) {
|
||||
document.getElementById('disqus_thread').innerHTML = 'Disqus comments not available by default when the website is previewed locally.';
|
||||
return;
|
||||
}
|
||||
var d = document, s = d.createElement('script'); s.async = true;
|
||||
s.src = '//' + "goproxy" + '.disqus.com/embed.js';
|
||||
s.setAttribute('data-timestamp', +new Date());
|
||||
(d.head || d.body).appendChild(s);
|
||||
})();
|
||||
</script>
|
||||
<noscript>Please enable JavaScript to view the <a href="https://disqus.com/?ref_noscript">comments powered by Disqus.</a></noscript>
|
||||
<a href="https://disqus.com" class="dsq-brlink">comments powered by <span class="logo-disqus">Disqus</span></a>
|
||||
</div>
|
||||
|
||||
<div class="col-md-4">
|
||||
|
||||
<aside class="l-sidebar">
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">LATESTS</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/first/" class="list-group-item">手册前言(使用必读)</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial/" class="list-group-item">GOPROXY免费版VS商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/faq/goproxy%E5%B8%B8%E8%A7%81%E9%97%AE%E9%A2%98%E8%A7%A3%E7%AD%94/" class="list-group-item">常见问题解答</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/domain-cf/" class="list-group-item">域名解析 域名控制台+极客+cloudflare 的配置方法</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/windows-global-proxy-using-dns/" class="list-group-item">在windows下实现基于dns的自动全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/usage/tcp/" class="list-group-item">TCP代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/cloudflare/" class="list-group-item">Cloudflare使用简明教程</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http-nat-cdn/" class="list-group-item">内网穿透也能用CDN???!</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/page/free_vs_commercial_en/" class="list-group-item">GOPROXY Free Version VS Commercial Version</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/posts/http_cdn_ws/" class="list-group-item">代理之套用CDN</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">CATEGORY</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E9%BB%98%E8%AE%A4%E5%88%86%E7%B1%BB" class="list-group-item">默认分类</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/goproxy%E6%89%8B%E5%86%8C" class="list-group-item">goproxy手册</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E6%9E%B6%E6%9E%84%E8%A7%A3%E8%AF%B4" class="list-group-item">架构解说</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/categories/%E7%BB%86%E8%AF%B4%E5%B1%82%E7%BA%A7" class="list-group-item">细说层级</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
<section class="panel panel-default">
|
||||
<div class="panel-heading">
|
||||
<div class="panel-title">TAG</div>
|
||||
</div>
|
||||
<div class="list-group">
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cdn" class="list-group-item">cdn</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/ws" class="list-group-item">ws</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/cloudflare" class="list-group-item">cloudflare</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%95%86%E4%B8%9A%E7%89%88" class="list-group-item">商业版</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/commercial" class="list-group-item">commercial</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/domain" class="list-group-item">domain</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/tcp" class="list-group-item">tcp</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%85%A8%E5%B1%80%E4%BB%A3%E7%90%86" class="list-group-item">全局代理</a>
|
||||
|
||||
<a href="https://snail.gitee.io/proxy/tags/%E5%86%85%E7%BD%91%E7%A9%BF%E9%80%8F" class="list-group-item">内网穿透</a>
|
||||
|
||||
</div>
|
||||
</section>
|
||||
|
||||
|
||||
</aside>
|
||||
|
||||
|
||||
</div>
|
||||
</div>
|
||||
|
||||
</div>
|
||||
</main>
|
||||
|
||||
<footer class="l-footer">
|
||||
<div class="container">
|
||||
<p><span class="h-logo">© GOPROXY IN ACTION</span></p>
|
||||
</div>
|
||||
</footer>
|
||||
|
||||
<script src="//code.jquery.com/jquery-3.1.1.min.js"></script>
|
||||
<script src="//maxcdn.bootstrapcdn.com/bootstrap/3.3.7/js/bootstrap.min.js"></script>
|
||||
<script src="//cdnjs.cloudflare.com/ajax/libs/highlight.js/8.4/highlight.min.js"></script>
|
||||
<script>hljs.initHighlightingOnLoad();</script>
|
||||
<script>
|
||||
$(function(){
|
||||
$("img[css]").each(function(){
|
||||
$(this).attr("style",$(this).attr("css"));
|
||||
});
|
||||
});
|
||||
</script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -0,0 +1,28 @@
|
||||
# Proxy-GUI
|
||||
Based on the proxy platform SDK, the author and many enthusiasts have developed the GUI version of the proxy for each platform.
|
||||
|
||||
## Windows
|
||||
|
||||
- Official java version, Project Homepage:[goproxy-jui](https://github.com/snail007/goproxy-jui)
|
||||
- Official C# version, Project Homepage:[gptool-csharp](https://github.com/snail007/gptool-csharp)
|
||||
|
||||
## Linux
|
||||
|
||||
- Official java version, Project Homepage:[goproxy-jui](https://github.com/snail007/goproxy-jui)
|
||||
|
||||
## MacOS
|
||||
|
||||
- Coming Soon ...
|
||||
|
||||
## Android
|
||||
|
||||
- goproxy official plugin of ss . Download address:[ss-plugin-goproxy](https://github.com/snail007/goproxy-ss-plugin-android)
|
||||
|
||||
|
||||
## IOS
|
||||
|
||||
- Coming Soon ...
|
||||
|
||||
## Cross-platform
|
||||
|
||||
- proxy-web,A cross-platform web UI version,project home page:[proxy-web](https://github.com/yincongcyincong/proxy-web)
|
||||
@@ -0,0 +1,27 @@
|
||||
# Proxy-GUI
|
||||
基于proxy的各平台SDK,作者和众多热心人士开发了各平台的GUI版本的proxy,下面分平台介绍.
|
||||
|
||||
## Windows
|
||||
|
||||
- 官方java版本,项目主页:[goproxy-jui](https://github.com/snail007/goproxy-jui)
|
||||
- 官方c#版本,项目主页:[gptool-csharp](https://github.com/snail007/gptool-csharp)
|
||||
|
||||
## Linux
|
||||
|
||||
- 官方java版本,项目主页:[goproxy-jui](https://github.com/snail007/goproxy-jui)
|
||||
|
||||
## MacOS
|
||||
|
||||
- Coming Soon ...
|
||||
|
||||
## Android
|
||||
|
||||
- 官方goproxy的ss插件,下载地址:[ss-plugin-goproxy](https://github.com/snail007/goproxy-ss-plugin-android)
|
||||
|
||||
## IOS
|
||||
|
||||
- Coming Soon ...
|
||||
|
||||
## 跨平台
|
||||
|
||||
- proxy-web,一个跨平台的web UI版本,项目主页:[proxy-web](https://github.com/yincongcyincong/proxy-web)
|
||||
@@ -0,0 +1,7 @@
|
||||
# domain support wildcard and comment line stared with #
|
||||
# **.google.com match all domain subfix with .google.com
|
||||
# *.youtube.com only math level 3 sub domain of .youtube.com
|
||||
|
||||
# example
|
||||
10.0.2.2 **.a.com
|
||||
10.0.2.2 *.c.com
|
||||
@@ -0,0 +1,32 @@
|
||||
#!/bin/bash
|
||||
F="proxy-linux-amd64.tar.gz"
|
||||
manual="https://snail.gitee.io/proxy/manual/"
|
||||
set -e
|
||||
WORKDIR="/tmp/proxy"
|
||||
rm -rf $WORKDIR
|
||||
mkdir $WORKDIR
|
||||
cp $F $WORKDIR
|
||||
cd /tmp/proxy
|
||||
echo -e ">>> installing ... \n"
|
||||
tar zxvf $F >/dev/null
|
||||
set +e
|
||||
killall -9 proxy >/dev/null 2>&1
|
||||
set -e
|
||||
cp -f proxy /usr/bin/
|
||||
chmod +x /usr/bin/proxy
|
||||
if [ ! -e /etc/proxy ]; then
|
||||
mkdir /etc/proxy
|
||||
cp blocked /etc/proxy
|
||||
cp direct /etc/proxy
|
||||
fi
|
||||
if [ ! -e /etc/proxy/proxy.crt ]; then
|
||||
cd /etc/proxy/
|
||||
proxy keygen -C proxy >/dev/null 2>&1
|
||||
fi
|
||||
rm -rf /tmp/proxy
|
||||
version=`proxy --version 2>&1`
|
||||
echo -e ">>> install done, thanks for using snail007/goproxy $version\n"
|
||||
echo -e ">>> install path /usr/bin/proxy\n"
|
||||
echo -e ">>> configuration path /etc/proxy\n"
|
||||
echo -e ">>> uninstall just exec : rm /usr/bin/proxy && rm -rf /etc/proxy\n"
|
||||
echo -e ">>> How to using? Please visit : $manual\n"
|
||||
@@ -0,0 +1,38 @@
|
||||
#!/bin/bash
|
||||
F="proxy-linux-amd64.tar.gz"
|
||||
set -e
|
||||
if [ -e /tmp/proxy ]; then
|
||||
rm -rf /tmp/proxy
|
||||
fi
|
||||
mkdir /tmp/proxy
|
||||
cd /tmp/proxy
|
||||
|
||||
echo -e "\n>>> downloading ... $F\n"
|
||||
manual="https://snail.gitee.io/proxy/manual/"
|
||||
LAST_VERSION=$(curl --silent "https://mirrors.host900.com/https://api.github.com/repos/snail007/goproxy/releases/latest" | grep -Po '"tag_name":"\K.*?(?=")')
|
||||
wget -t 1 "https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/${LAST_VERSION}/$F"
|
||||
|
||||
echo -e ">>> installing ... \n"
|
||||
# #install proxy
|
||||
tar zxvf $F >/dev/null
|
||||
set +e
|
||||
killall -9 proxy >/dev/null 2>&1
|
||||
set -e
|
||||
cp -f proxy /usr/bin/
|
||||
chmod +x /usr/bin/proxy
|
||||
if [ ! -e /etc/proxy ]; then
|
||||
mkdir /etc/proxy
|
||||
cp blocked /etc/proxy
|
||||
cp direct /etc/proxy
|
||||
fi
|
||||
if [ ! -e /etc/proxy/proxy.crt ]; then
|
||||
cd /etc/proxy/
|
||||
proxy keygen -C proxy >/dev/null 2>&1
|
||||
fi
|
||||
rm -rf /tmp/proxy
|
||||
version=`proxy --version 2>&1`
|
||||
echo -e ">>> install done, thanks for using snail007/goproxy $version\n"
|
||||
echo -e ">>> install path /usr/bin/proxy\n"
|
||||
echo -e ">>> configuration path /etc/proxy\n"
|
||||
echo -e ">>> uninstall just exec : rm /usr/bin/proxy && rm -rf /etc/proxy\n"
|
||||
echo -e ">>> How to using? Please visit : $manual\n"
|
||||
@@ -0,0 +1,37 @@
|
||||
#!/bin/bash
|
||||
F="proxy-linux-amd64_commercial.tar.gz"
|
||||
set -e
|
||||
if [ -e /tmp/proxy ]; then
|
||||
rm -rf /tmp/proxy
|
||||
fi
|
||||
mkdir /tmp/proxy
|
||||
cd /tmp/proxy
|
||||
echo -e "\n>>> downloading ... $F\n"
|
||||
manual="https://snail.gitee.io/proxy/manual/"
|
||||
LAST_VERSION=$(curl --silent "https://mirrors.host900.com/https://api.github.com/repos/snail007/goproxy/releases/latest" | grep -Po '"tag_name":"\K.*?(?=")')
|
||||
wget -t 1 "https://mirrors.host900.com/https://github.com/snail007/goproxy/releases/download/${LAST_VERSION}/$F"
|
||||
|
||||
echo -e ">>> installing ... \n"
|
||||
# #install proxy
|
||||
tar zxvf $F >/dev/null
|
||||
set +e
|
||||
killall -9 proxy >/dev/null 2>&1
|
||||
set -e
|
||||
cp -f proxy /usr/bin/
|
||||
chmod +x /usr/bin/proxy
|
||||
if [ ! -e /etc/proxy ]; then
|
||||
mkdir /etc/proxy
|
||||
cp blocked /etc/proxy
|
||||
cp direct /etc/proxy
|
||||
fi
|
||||
if [ ! -e /etc/proxy/proxy.crt ]; then
|
||||
cd /etc/proxy/
|
||||
proxy keygen -C proxy >/dev/null 2>&1
|
||||
fi
|
||||
rm -rf /tmp/proxy
|
||||
version=`proxy --version 2>&1`
|
||||
echo -e ">>> install done, thanks for using snail007/goproxy $version\n"
|
||||
echo -e ">>> install path /usr/bin/proxy\n"
|
||||
echo -e ">>> configuration path /etc/proxy\n"
|
||||
echo -e ">>> uninstall just exec : rm /usr/bin/proxy && rm -rf /etc/proxy\n"
|
||||
echo -e ">>> How to using? Please visit : $manual\n"
|
||||
@@ -0,0 +1,32 @@
|
||||
#!/bin/bash
|
||||
F="proxy-linux-amd64_commercial.tar.gz"
|
||||
manual="https://snail.gitee.io/proxy/manual/"
|
||||
set -e
|
||||
WORKDIR="/tmp/proxy"
|
||||
rm -rf $WORKDIR
|
||||
mkdir $WORKDIR
|
||||
cp $F $WORKDIR
|
||||
cd /tmp/proxy
|
||||
echo -e ">>> installing ... \n"
|
||||
tar zxvf $F >/dev/null
|
||||
set +e
|
||||
killall -9 proxy >/dev/null 2>&1
|
||||
set -e
|
||||
cp -f proxy /usr/bin/
|
||||
chmod +x /usr/bin/proxy
|
||||
if [ ! -e /etc/proxy ]; then
|
||||
mkdir /etc/proxy
|
||||
cp blocked /etc/proxy
|
||||
cp direct /etc/proxy
|
||||
fi
|
||||
if [ ! -e /etc/proxy/proxy.crt ]; then
|
||||
cd /etc/proxy/
|
||||
proxy keygen -C proxy >/dev/null 2>&1
|
||||
fi
|
||||
rm -rf /tmp/proxy
|
||||
version=`proxy --version 2>&1`
|
||||
echo -e ">>> install done, thanks for using snail007/goproxy $version\n"
|
||||
echo -e ">>> install path /usr/bin/proxy\n"
|
||||
echo -e ">>> configuration path /etc/proxy\n"
|
||||
echo -e ">>> uninstall just exec : rm /usr/bin/proxy && rm -rf /etc/proxy\n"
|
||||
echo -e ">>> How to using? Please visit : $manual\n"
|
||||
@@ -0,0 +1,38 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"log"
|
||||
"os"
|
||||
"os/signal"
|
||||
"proxy/services"
|
||||
"syscall"
|
||||
)
|
||||
|
||||
const APP_VERSION = "3.0"
|
||||
|
||||
func main() {
|
||||
err := initConfig()
|
||||
if err != nil {
|
||||
log.Fatalf("err : %s", err)
|
||||
}
|
||||
Clean(&service.S)
|
||||
}
|
||||
func Clean(s *services.Service) {
|
||||
signalChan := make(chan os.Signal, 1)
|
||||
cleanupDone := make(chan bool)
|
||||
signal.Notify(signalChan,
|
||||
os.Interrupt,
|
||||
syscall.SIGHUP,
|
||||
syscall.SIGINT,
|
||||
syscall.SIGTERM,
|
||||
syscall.SIGQUIT)
|
||||
go func() {
|
||||
for _ = range signalChan {
|
||||
fmt.Println("\nReceived an interrupt, stopping services...")
|
||||
(*s).Clean()
|
||||
cleanupDone <- true
|
||||
}
|
||||
}()
|
||||
<-cleanupDone
|
||||
}
|
||||
@@ -0,0 +1,19 @@
|
||||
# domain support wildcard and comment line stared with #
|
||||
# **.google.com match all domain subfix with .google.com
|
||||
# *.youtube.com only math level 3 sub domain of .youtube.com
|
||||
|
||||
#example
|
||||
|
||||
**.google.com proxy
|
||||
*.youtube.com
|
||||
*.baidu.com 114.114.114.114,system,direct
|
||||
b.com
|
||||
c.com
|
||||
d.com 8.8.8.8:53
|
||||
e.com
|
||||
|
||||
#explain
|
||||
|
||||
#using `proxy >>> -q` to resolve **.google.com and *.youtube.com
|
||||
#using 114.114.114.114:53 and system and `direct >>> -q` to resolve *.baidu.com and b.com and c.com
|
||||
#using 8.8.8.8:53 to resolve **.google.com and *.youtube.com
|
||||
@@ -0,0 +1,4 @@
|
||||
# example
|
||||
www.a.com:80 10.0.0.2:8080
|
||||
**.b.com:80 10.0.0.2:80
|
||||
192.168.0.11:80 10.0.0.2:8080
|
||||
@@ -0,0 +1,75 @@
|
||||
package services
|
||||
|
||||
// tcp := app.Command("tcp", "proxy on tcp mode")
|
||||
// t := tcp.Flag("tcp-timeout", "tcp timeout milliseconds when connect to real server or parent proxy").Default("2000").Int()
|
||||
|
||||
const (
|
||||
TYPE_TCP = "tcp"
|
||||
TYPE_UDP = "udp"
|
||||
TYPE_HTTP = "http"
|
||||
TYPE_TLS = "tls"
|
||||
CONN_CONTROL = uint8(1)
|
||||
CONN_SERVER = uint8(2)
|
||||
CONN_CLIENT = uint8(3)
|
||||
)
|
||||
|
||||
type Args struct {
|
||||
Local *string
|
||||
Parent *string
|
||||
CertBytes []byte
|
||||
KeyBytes []byte
|
||||
}
|
||||
type TunnelServerArgs struct {
|
||||
Args
|
||||
IsUDP *bool
|
||||
Key *string
|
||||
Timeout *int
|
||||
}
|
||||
type TunnelClientArgs struct {
|
||||
Args
|
||||
IsUDP *bool
|
||||
Key *string
|
||||
Timeout *int
|
||||
}
|
||||
type TunnelBridgeArgs struct {
|
||||
Args
|
||||
Timeout *int
|
||||
}
|
||||
type TCPArgs struct {
|
||||
Args
|
||||
ParentType *string
|
||||
IsTLS *bool
|
||||
Timeout *int
|
||||
PoolSize *int
|
||||
CheckParentInterval *int
|
||||
}
|
||||
|
||||
type HTTPArgs struct {
|
||||
Args
|
||||
Always *bool
|
||||
HTTPTimeout *int
|
||||
Interval *int
|
||||
Blocked *string
|
||||
Direct *string
|
||||
AuthFile *string
|
||||
Auth *[]string
|
||||
ParentType *string
|
||||
LocalType *string
|
||||
Timeout *int
|
||||
PoolSize *int
|
||||
CheckParentInterval *int
|
||||
}
|
||||
type UDPArgs struct {
|
||||
Args
|
||||
ParentType *string
|
||||
Timeout *int
|
||||
PoolSize *int
|
||||
CheckParentInterval *int
|
||||
}
|
||||
|
||||
func (a *TCPArgs) Protocol() string {
|
||||
if *a.IsTLS {
|
||||
return "tls"
|
||||
}
|
||||
return "tcp"
|
||||
}
|
||||
@@ -0,0 +1,219 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"io"
|
||||
"log"
|
||||
"net"
|
||||
"proxy/utils"
|
||||
"runtime/debug"
|
||||
"strconv"
|
||||
)
|
||||
|
||||
type HTTP struct {
|
||||
outPool utils.OutPool
|
||||
cfg HTTPArgs
|
||||
checker utils.Checker
|
||||
basicAuth utils.BasicAuth
|
||||
}
|
||||
|
||||
func NewHTTP() Service {
|
||||
return &HTTP{
|
||||
outPool: utils.OutPool{},
|
||||
cfg: HTTPArgs{},
|
||||
checker: utils.Checker{},
|
||||
basicAuth: utils.BasicAuth{},
|
||||
}
|
||||
}
|
||||
func (s *HTTP) InitService() {
|
||||
s.InitBasicAuth()
|
||||
if *s.cfg.Parent != "" {
|
||||
s.checker = utils.NewChecker(*s.cfg.HTTPTimeout, int64(*s.cfg.Interval), *s.cfg.Blocked, *s.cfg.Direct)
|
||||
}
|
||||
}
|
||||
func (s *HTTP) StopService() {
|
||||
if s.outPool.Pool != nil {
|
||||
s.outPool.Pool.ReleaseAll()
|
||||
}
|
||||
}
|
||||
func (s *HTTP) Start(args interface{}) (err error) {
|
||||
s.cfg = args.(HTTPArgs)
|
||||
if *s.cfg.Parent != "" {
|
||||
log.Printf("use %s parent %s", *s.cfg.ParentType, *s.cfg.Parent)
|
||||
s.InitOutConnPool()
|
||||
}
|
||||
|
||||
s.InitService()
|
||||
|
||||
host, port, _ := net.SplitHostPort(*s.cfg.Local)
|
||||
p, _ := strconv.Atoi(port)
|
||||
sc := utils.NewServerChannel(host, p)
|
||||
if *s.cfg.LocalType == TYPE_TCP {
|
||||
err = sc.ListenTCP(s.callback)
|
||||
} else {
|
||||
err = sc.ListenTls(s.cfg.CertBytes, s.cfg.KeyBytes, s.callback)
|
||||
}
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
log.Printf("%s http(s) proxy on %s", *s.cfg.LocalType, (*sc.Listener).Addr())
|
||||
return
|
||||
}
|
||||
|
||||
func (s *HTTP) Clean() {
|
||||
s.StopService()
|
||||
}
|
||||
func (s *HTTP) callback(inConn net.Conn) {
|
||||
defer func() {
|
||||
if err := recover(); err != nil {
|
||||
log.Printf("http(s) conn handler crashed with err : %s \nstack: %s", err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
req, err := utils.NewHTTPRequest(&inConn, 4096, s.IsBasicAuth(), &s.basicAuth)
|
||||
if err != nil {
|
||||
if err != io.EOF {
|
||||
log.Printf("decoder error , form %s, ERR:%s", err, inConn.RemoteAddr())
|
||||
}
|
||||
utils.CloseConn(&inConn)
|
||||
return
|
||||
}
|
||||
address := req.Host
|
||||
|
||||
useProxy := true
|
||||
if *s.cfg.Parent == "" {
|
||||
useProxy = false
|
||||
} else if *s.cfg.Always {
|
||||
useProxy = true
|
||||
} else {
|
||||
if req.IsHTTPS() {
|
||||
s.checker.Add(address, true, req.Method, "", nil)
|
||||
} else {
|
||||
s.checker.Add(address, false, req.Method, req.URL, req.HeadBuf)
|
||||
}
|
||||
//var n, m uint
|
||||
useProxy, _, _ = s.checker.IsBlocked(req.Host)
|
||||
//log.Printf("blocked ? : %v, %s , fail:%d ,success:%d", useProxy, address, n, m)
|
||||
}
|
||||
log.Printf("use proxy : %v, %s", useProxy, address)
|
||||
//os.Exit(0)
|
||||
err = s.OutToTCP(useProxy, address, &inConn, &req)
|
||||
if err != nil {
|
||||
if *s.cfg.Parent == "" {
|
||||
log.Printf("connect to %s fail, ERR:%s", address, err)
|
||||
} else {
|
||||
log.Printf("connect to %s parent %s fail", *s.cfg.ParentType, *s.cfg.Parent)
|
||||
}
|
||||
utils.CloseConn(&inConn)
|
||||
}
|
||||
}
|
||||
func (s *HTTP) OutToTCP(useProxy bool, address string, inConn *net.Conn, req *utils.HTTPRequest) (err error) {
|
||||
inAddr := (*inConn).RemoteAddr().String()
|
||||
inLocalAddr := (*inConn).LocalAddr().String()
|
||||
//防止死循环
|
||||
if s.IsDeadLoop(inLocalAddr, req.Host) {
|
||||
utils.CloseConn(inConn)
|
||||
err = fmt.Errorf("dead loop detected , %s", req.Host)
|
||||
return
|
||||
}
|
||||
var outConn net.Conn
|
||||
var _outConn interface{}
|
||||
if useProxy {
|
||||
_outConn, err = s.outPool.Pool.Get()
|
||||
if err == nil {
|
||||
outConn = _outConn.(net.Conn)
|
||||
}
|
||||
} else {
|
||||
outConn, err = utils.ConnectHost(address, *s.cfg.Timeout)
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("connect to %s , err:%s", *s.cfg.Parent, err)
|
||||
utils.CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
|
||||
outAddr := outConn.RemoteAddr().String()
|
||||
outLocalAddr := outConn.LocalAddr().String()
|
||||
|
||||
if req.IsHTTPS() && !useProxy {
|
||||
req.HTTPSReply()
|
||||
} else {
|
||||
outConn.Write(req.HeadBuf)
|
||||
}
|
||||
utils.IoBind((*inConn), outConn, func(isSrcErr bool, err error) {
|
||||
log.Printf("conn %s - %s - %s -%s released [%s]", inAddr, inLocalAddr, outLocalAddr, outAddr, req.Host)
|
||||
utils.CloseConn(inConn)
|
||||
utils.CloseConn(&outConn)
|
||||
}, func(n int, d bool) {}, 0)
|
||||
log.Printf("conn %s - %s - %s - %s connected [%s]", inAddr, inLocalAddr, outLocalAddr, outAddr, req.Host)
|
||||
return
|
||||
}
|
||||
func (s *HTTP) OutToUDP(inConn *net.Conn) (err error) {
|
||||
return
|
||||
}
|
||||
func (s *HTTP) InitOutConnPool() {
|
||||
if *s.cfg.ParentType == TYPE_TLS || *s.cfg.ParentType == TYPE_TCP {
|
||||
//dur int, isTLS bool, certBytes, keyBytes []byte,
|
||||
//parent string, timeout int, InitialCap int, MaxCap int
|
||||
s.outPool = utils.NewOutPool(
|
||||
*s.cfg.CheckParentInterval,
|
||||
*s.cfg.ParentType == TYPE_TLS,
|
||||
s.cfg.CertBytes, s.cfg.KeyBytes,
|
||||
*s.cfg.Parent,
|
||||
*s.cfg.Timeout,
|
||||
*s.cfg.PoolSize,
|
||||
*s.cfg.PoolSize*2,
|
||||
)
|
||||
}
|
||||
}
|
||||
func (s *HTTP) InitBasicAuth() (err error) {
|
||||
s.basicAuth = utils.NewBasicAuth()
|
||||
if *s.cfg.AuthFile != "" {
|
||||
var n = 0
|
||||
n, err = s.basicAuth.AddFromFile(*s.cfg.AuthFile)
|
||||
if err != nil {
|
||||
err = fmt.Errorf("auth-file ERR:%s", err)
|
||||
return
|
||||
}
|
||||
log.Printf("auth data added from file %d , total:%d", n, s.basicAuth.Total())
|
||||
}
|
||||
if len(*s.cfg.Auth) > 0 {
|
||||
n := s.basicAuth.Add(*s.cfg.Auth)
|
||||
log.Printf("auth data added %d, total:%d", n, s.basicAuth.Total())
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *HTTP) IsBasicAuth() bool {
|
||||
return *s.cfg.AuthFile != "" || len(*s.cfg.Auth) > 0
|
||||
}
|
||||
func (s *HTTP) IsDeadLoop(inLocalAddr string, host string) bool {
|
||||
inIP, inPort, err := net.SplitHostPort(inLocalAddr)
|
||||
if err != nil {
|
||||
return false
|
||||
}
|
||||
outDomain, outPort, err := net.SplitHostPort(host)
|
||||
if err != nil {
|
||||
return false
|
||||
}
|
||||
if inPort == outPort {
|
||||
var outIPs []net.IP
|
||||
outIPs, err = net.LookupIP(outDomain)
|
||||
if err == nil {
|
||||
for _, ip := range outIPs {
|
||||
if ip.String() == inIP {
|
||||
return true
|
||||
}
|
||||
}
|
||||
}
|
||||
interfaceIPs, err := utils.GetAllInterfaceAddr()
|
||||
if err == nil {
|
||||
for _, localIP := range interfaceIPs {
|
||||
for _, outIP := range outIPs {
|
||||
if localIP.Equal(outIP) {
|
||||
return true
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
return false
|
||||
}
|
||||
@@ -0,0 +1,48 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"log"
|
||||
"runtime/debug"
|
||||
)
|
||||
|
||||
type Service interface {
|
||||
Start(args interface{}) (err error)
|
||||
Clean()
|
||||
}
|
||||
type ServiceItem struct {
|
||||
S Service
|
||||
Args interface{}
|
||||
Name string
|
||||
}
|
||||
|
||||
var servicesMap = map[string]*ServiceItem{}
|
||||
|
||||
func Regist(name string, s Service, args interface{}) {
|
||||
servicesMap[name] = &ServiceItem{
|
||||
S: s,
|
||||
Args: args,
|
||||
Name: name,
|
||||
}
|
||||
}
|
||||
func Run(name string) (service *ServiceItem, err error) {
|
||||
service, ok := servicesMap[name]
|
||||
if ok {
|
||||
go func() {
|
||||
defer func() {
|
||||
err := recover()
|
||||
if err != nil {
|
||||
log.Fatalf("%s servcie crashed, ERR: %s\ntrace:%s", name, err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
err := service.S.Start(service.Args)
|
||||
if err != nil {
|
||||
log.Fatalf("%s servcie fail, ERR: %s", name, err)
|
||||
}
|
||||
}()
|
||||
}
|
||||
if !ok {
|
||||
err = fmt.Errorf("service %s not found", name)
|
||||
}
|
||||
return
|
||||
}
|
||||
@@ -0,0 +1,170 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"io"
|
||||
"log"
|
||||
"net"
|
||||
"proxy/utils"
|
||||
"runtime/debug"
|
||||
"time"
|
||||
|
||||
"strconv"
|
||||
)
|
||||
|
||||
type TCP struct {
|
||||
outPool utils.OutPool
|
||||
cfg TCPArgs
|
||||
}
|
||||
|
||||
func NewTCP() Service {
|
||||
return &TCP{
|
||||
outPool: utils.OutPool{},
|
||||
cfg: TCPArgs{},
|
||||
}
|
||||
}
|
||||
func (s *TCP) InitService() {
|
||||
s.InitOutConnPool()
|
||||
}
|
||||
func (s *TCP) StopService() {
|
||||
if s.outPool.Pool != nil {
|
||||
s.outPool.Pool.ReleaseAll()
|
||||
}
|
||||
}
|
||||
func (s *TCP) Start(args interface{}) (err error) {
|
||||
s.cfg = args.(TCPArgs)
|
||||
if *s.cfg.Parent != "" {
|
||||
log.Printf("use %s parent %s", *s.cfg.ParentType, *s.cfg.Parent)
|
||||
} else {
|
||||
log.Fatalf("parent required for %s %s", s.cfg.Protocol(), *s.cfg.Local)
|
||||
}
|
||||
|
||||
s.InitService()
|
||||
|
||||
host, port, _ := net.SplitHostPort(*s.cfg.Local)
|
||||
p, _ := strconv.Atoi(port)
|
||||
sc := utils.NewServerChannel(host, p)
|
||||
if !*s.cfg.IsTLS {
|
||||
err = sc.ListenTCP(s.callback)
|
||||
} else {
|
||||
err = sc.ListenTls(s.cfg.CertBytes, s.cfg.KeyBytes, s.callback)
|
||||
}
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
log.Printf("%s proxy on %s", s.cfg.Protocol(), (*sc.Listener).Addr())
|
||||
return
|
||||
}
|
||||
|
||||
func (s *TCP) Clean() {
|
||||
s.StopService()
|
||||
}
|
||||
func (s *TCP) callback(inConn net.Conn) {
|
||||
defer func() {
|
||||
if err := recover(); err != nil {
|
||||
log.Printf("%s conn handler crashed with err : %s \nstack: %s", s.cfg.Protocol(), err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
var err error
|
||||
switch *s.cfg.ParentType {
|
||||
case TYPE_TCP:
|
||||
fallthrough
|
||||
case TYPE_TLS:
|
||||
err = s.OutToTCP(&inConn)
|
||||
case TYPE_UDP:
|
||||
err = s.OutToUDP(&inConn)
|
||||
default:
|
||||
err = fmt.Errorf("unkown parent type %s", *s.cfg.ParentType)
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("connect to %s parent %s fail, ERR:%s", *s.cfg.ParentType, *s.cfg.Parent, err)
|
||||
utils.CloseConn(&inConn)
|
||||
}
|
||||
}
|
||||
func (s *TCP) OutToTCP(inConn *net.Conn) (err error) {
|
||||
var outConn net.Conn
|
||||
var _outConn interface{}
|
||||
_outConn, err = s.outPool.Pool.Get()
|
||||
if err == nil {
|
||||
outConn = _outConn.(net.Conn)
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("connect to %s , err:%s", *s.cfg.Parent, err)
|
||||
utils.CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
inAddr := (*inConn).RemoteAddr().String()
|
||||
inLocalAddr := (*inConn).LocalAddr().String()
|
||||
outAddr := outConn.RemoteAddr().String()
|
||||
outLocalAddr := outConn.LocalAddr().String()
|
||||
utils.IoBind((*inConn), outConn, func(isSrcErr bool, err error) {
|
||||
log.Printf("conn %s - %s - %s -%s released", inAddr, inLocalAddr, outLocalAddr, outAddr)
|
||||
utils.CloseConn(inConn)
|
||||
utils.CloseConn(&outConn)
|
||||
}, func(n int, d bool) {}, 0)
|
||||
log.Printf("conn %s - %s - %s -%s connected", inAddr, inLocalAddr, outLocalAddr, outAddr)
|
||||
return
|
||||
}
|
||||
func (s *TCP) OutToUDP(inConn *net.Conn) (err error) {
|
||||
log.Printf("conn created , remote : %s ", (*inConn).RemoteAddr())
|
||||
for {
|
||||
srcAddr, body, err := utils.ReadUDPPacket(inConn)
|
||||
if err == io.EOF || err == io.ErrUnexpectedEOF {
|
||||
//log.Printf("connection %s released", srcAddr)
|
||||
utils.CloseConn(inConn)
|
||||
break
|
||||
}
|
||||
//log.Debugf("udp packet revecived:%s,%v", srcAddr, body)
|
||||
dstAddr, err := net.ResolveUDPAddr("udp", *s.cfg.Parent)
|
||||
if err != nil {
|
||||
log.Printf("can't resolve address: %s", err)
|
||||
utils.CloseConn(inConn)
|
||||
break
|
||||
}
|
||||
clientSrcAddr := &net.UDPAddr{IP: net.IPv4zero, Port: 0}
|
||||
conn, err := net.DialUDP("udp", clientSrcAddr, dstAddr)
|
||||
if err != nil {
|
||||
log.Printf("connect to udp %s fail,ERR:%s", dstAddr.String(), err)
|
||||
continue
|
||||
}
|
||||
conn.SetDeadline(time.Now().Add(time.Millisecond * time.Duration(*s.cfg.Timeout)))
|
||||
_, err = conn.Write(body)
|
||||
if err != nil {
|
||||
log.Printf("send udp packet to %s fail,ERR:%s", dstAddr.String(), err)
|
||||
continue
|
||||
}
|
||||
//log.Debugf("send udp packet to %s success", dstAddr.String())
|
||||
buf := make([]byte, 512)
|
||||
len, _, err := conn.ReadFromUDP(buf)
|
||||
if err != nil {
|
||||
log.Printf("read udp response from %s fail ,ERR:%s", dstAddr.String(), err)
|
||||
continue
|
||||
}
|
||||
respBody := buf[0:len]
|
||||
//log.Debugf("revecived udp packet from %s , %v", dstAddr.String(), respBody)
|
||||
_, err = (*inConn).Write(utils.UDPPacket(srcAddr, respBody))
|
||||
if err != nil {
|
||||
log.Printf("send udp response fail ,ERR:%s", err)
|
||||
utils.CloseConn(inConn)
|
||||
break
|
||||
}
|
||||
//log.Printf("send udp response success ,from:%s", dstAddr.String())
|
||||
}
|
||||
return
|
||||
|
||||
}
|
||||
func (s *TCP) InitOutConnPool() {
|
||||
if *s.cfg.ParentType == TYPE_TLS || *s.cfg.ParentType == TYPE_TCP {
|
||||
//dur int, isTLS bool, certBytes, keyBytes []byte,
|
||||
//parent string, timeout int, InitialCap int, MaxCap int
|
||||
s.outPool = utils.NewOutPool(
|
||||
*s.cfg.CheckParentInterval,
|
||||
*s.cfg.ParentType == TYPE_TLS,
|
||||
s.cfg.CertBytes, s.cfg.KeyBytes,
|
||||
*s.cfg.Parent,
|
||||
*s.cfg.Timeout,
|
||||
*s.cfg.PoolSize,
|
||||
*s.cfg.PoolSize*2,
|
||||
)
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,183 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"bufio"
|
||||
"encoding/binary"
|
||||
"fmt"
|
||||
"log"
|
||||
"net"
|
||||
"proxy/utils"
|
||||
"strconv"
|
||||
"sync"
|
||||
"time"
|
||||
)
|
||||
|
||||
type BridgeItem struct {
|
||||
ServerChn chan *net.Conn
|
||||
ClientChn chan *net.Conn
|
||||
ClientControl *net.Conn
|
||||
Once *sync.Once
|
||||
Key string
|
||||
}
|
||||
type TunnelBridge struct {
|
||||
cfg TunnelBridgeArgs
|
||||
br utils.ConcurrentMap
|
||||
}
|
||||
|
||||
func NewTunnelBridge() Service {
|
||||
return &TunnelBridge{
|
||||
cfg: TunnelBridgeArgs{},
|
||||
br: utils.NewConcurrentMap(),
|
||||
}
|
||||
}
|
||||
|
||||
func (s *TunnelBridge) InitService() {
|
||||
|
||||
}
|
||||
func (s *TunnelBridge) Check() {
|
||||
if s.cfg.CertBytes == nil || s.cfg.KeyBytes == nil {
|
||||
log.Fatalf("cert and key file required")
|
||||
}
|
||||
|
||||
}
|
||||
func (s *TunnelBridge) StopService() {
|
||||
|
||||
}
|
||||
func (s *TunnelBridge) Start(args interface{}) (err error) {
|
||||
s.cfg = args.(TunnelBridgeArgs)
|
||||
s.Check()
|
||||
s.InitService()
|
||||
host, port, _ := net.SplitHostPort(*s.cfg.Local)
|
||||
p, _ := strconv.Atoi(port)
|
||||
sc := utils.NewServerChannel(host, p)
|
||||
|
||||
err = sc.ListenTls(s.cfg.CertBytes, s.cfg.KeyBytes, func(inConn net.Conn) {
|
||||
reader := bufio.NewReader(inConn)
|
||||
var connType uint8
|
||||
err = binary.Read(reader, binary.LittleEndian, &connType)
|
||||
if err != nil {
|
||||
utils.CloseConn(&inConn)
|
||||
return
|
||||
}
|
||||
var key string
|
||||
var connTypeStrMap = map[uint8]string{CONN_SERVER: "server", CONN_CLIENT: "client", CONN_CONTROL: "client"}
|
||||
if connType == CONN_SERVER || connType == CONN_CLIENT || connType == CONN_CONTROL {
|
||||
var keyLength uint16
|
||||
err = binary.Read(reader, binary.LittleEndian, &keyLength)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
_key := make([]byte, keyLength)
|
||||
n, err := reader.Read(_key)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
if n != int(keyLength) {
|
||||
return
|
||||
}
|
||||
key = string(_key)
|
||||
log.Printf("connection from %s , key: %s", connTypeStrMap[connType], key)
|
||||
}
|
||||
switch connType {
|
||||
case CONN_SERVER:
|
||||
s.ServerConn(&inConn, key)
|
||||
case CONN_CLIENT:
|
||||
s.ClientConn(&inConn, key)
|
||||
case CONN_CONTROL:
|
||||
s.ClientControlConn(&inConn, key)
|
||||
default:
|
||||
log.Printf("unkown conn type %d", connType)
|
||||
utils.CloseConn(&inConn)
|
||||
}
|
||||
})
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
log.Printf("proxy on tunnel bridge mode %s", (*sc.Listener).Addr())
|
||||
return
|
||||
}
|
||||
func (s *TunnelBridge) Clean() {
|
||||
s.StopService()
|
||||
}
|
||||
func (s *TunnelBridge) ClientConn(inConn *net.Conn, key string) {
|
||||
chn, _ := s.ConnChn(key, CONN_CLIENT)
|
||||
chn <- inConn
|
||||
}
|
||||
func (s *TunnelBridge) ServerConn(inConn *net.Conn, key string) {
|
||||
chn, _ := s.ConnChn(key, CONN_SERVER)
|
||||
chn <- inConn
|
||||
}
|
||||
func (s *TunnelBridge) ClientControlConn(inConn *net.Conn, key string) {
|
||||
_, item := s.ConnChn(key, CONN_CLIENT)
|
||||
utils.CloseConn(item.ClientControl)
|
||||
if item.ClientControl != nil {
|
||||
*item.ClientControl = *inConn
|
||||
} else {
|
||||
item.ClientControl = inConn
|
||||
}
|
||||
log.Printf("set client control conn,remote: %s", (*inConn).RemoteAddr())
|
||||
}
|
||||
func (s *TunnelBridge) ConnChn(key string, typ uint8) (chn chan *net.Conn, item *BridgeItem) {
|
||||
s.br.SetIfAbsent(key, &BridgeItem{
|
||||
ServerChn: make(chan *net.Conn, 10000),
|
||||
ClientChn: make(chan *net.Conn, 10000),
|
||||
Once: &sync.Once{},
|
||||
Key: key,
|
||||
})
|
||||
_item, _ := s.br.Get(key)
|
||||
item = _item.(*BridgeItem)
|
||||
item.Once.Do(func() {
|
||||
s.ChnDeamon(item)
|
||||
})
|
||||
if typ == CONN_CLIENT {
|
||||
chn = item.ClientChn
|
||||
} else {
|
||||
chn = item.ServerChn
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *TunnelBridge) ChnDeamon(item *BridgeItem) {
|
||||
go func() {
|
||||
log.Printf("%s conn chan deamon started", item.Key)
|
||||
for {
|
||||
var clientConn *net.Conn
|
||||
var serverConn *net.Conn
|
||||
serverConn = <-item.ServerChn
|
||||
log.Printf("%s server conn picked up", item.Key)
|
||||
OUT:
|
||||
for {
|
||||
_item, _ := s.br.Get(item.Key)
|
||||
Item := _item.(*BridgeItem)
|
||||
var err error
|
||||
if Item.ClientControl != nil && *Item.ClientControl != nil {
|
||||
_, err = (*Item.ClientControl).Write([]byte{'0'})
|
||||
} else {
|
||||
err = fmt.Errorf("client control conn not exists")
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("%s client control conn write signal fail, err: %s, retrying...", item.Key, err)
|
||||
utils.CloseConn(Item.ClientControl)
|
||||
*Item.ClientControl = nil
|
||||
Item.ClientControl = nil
|
||||
time.Sleep(time.Second * 3)
|
||||
continue
|
||||
} else {
|
||||
select {
|
||||
case clientConn = <-item.ClientChn:
|
||||
log.Printf("%s client conn picked up", item.Key)
|
||||
break OUT
|
||||
case <-time.After(time.Second * time.Duration(*s.cfg.Timeout*5)):
|
||||
log.Printf("%s client conn picked timeout, retrying...", item.Key)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
utils.IoBind(*serverConn, *clientConn, func(isSrcErr bool, err error) {
|
||||
utils.CloseConn(serverConn)
|
||||
utils.CloseConn(clientConn)
|
||||
log.Printf("%s conn %s - %s - %s - %s released", item.Key, (*serverConn).RemoteAddr(), (*serverConn).LocalAddr(), (*clientConn).LocalAddr(), (*clientConn).RemoteAddr())
|
||||
}, func(i int, b bool) {}, 0)
|
||||
log.Printf("%s conn %s - %s - %s - %s created", item.Key, (*serverConn).RemoteAddr(), (*serverConn).LocalAddr(), (*clientConn).LocalAddr(), (*clientConn).RemoteAddr())
|
||||
}
|
||||
}()
|
||||
}
|
||||
@@ -0,0 +1,215 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"crypto/tls"
|
||||
"encoding/binary"
|
||||
"fmt"
|
||||
"io"
|
||||
"log"
|
||||
"net"
|
||||
"proxy/utils"
|
||||
"time"
|
||||
)
|
||||
|
||||
type TunnelClient struct {
|
||||
cfg TunnelClientArgs
|
||||
}
|
||||
|
||||
func NewTunnelClient() Service {
|
||||
return &TunnelClient{
|
||||
cfg: TunnelClientArgs{},
|
||||
}
|
||||
}
|
||||
|
||||
func (s *TunnelClient) InitService() {
|
||||
}
|
||||
func (s *TunnelClient) Check() {
|
||||
if *s.cfg.Parent != "" {
|
||||
log.Printf("use tls parent %s", *s.cfg.Parent)
|
||||
} else {
|
||||
log.Fatalf("parent required")
|
||||
}
|
||||
if s.cfg.CertBytes == nil || s.cfg.KeyBytes == nil {
|
||||
log.Fatalf("cert and key file required")
|
||||
}
|
||||
}
|
||||
func (s *TunnelClient) StopService() {
|
||||
}
|
||||
func (s *TunnelClient) Start(args interface{}) (err error) {
|
||||
s.cfg = args.(TunnelClientArgs)
|
||||
s.Check()
|
||||
s.InitService()
|
||||
|
||||
for {
|
||||
ctrlConn, err := s.GetInConn(CONN_CONTROL)
|
||||
if err != nil {
|
||||
log.Printf("control connection err: %s", err)
|
||||
time.Sleep(time.Second * 3)
|
||||
utils.CloseConn(&ctrlConn)
|
||||
continue
|
||||
}
|
||||
if *s.cfg.IsUDP {
|
||||
log.Printf("proxy on udp tunnel client mode")
|
||||
} else {
|
||||
log.Printf("proxy on tcp tunnel client mode")
|
||||
}
|
||||
for {
|
||||
signal := make([]byte, 1)
|
||||
if signal[0] == 1 {
|
||||
continue
|
||||
}
|
||||
_, err = ctrlConn.Read(signal)
|
||||
if err != nil {
|
||||
utils.CloseConn(&ctrlConn)
|
||||
log.Printf("read connection signal err: %s", err)
|
||||
break
|
||||
}
|
||||
log.Printf("signal revecived:%s", signal)
|
||||
if *s.cfg.IsUDP {
|
||||
go s.ServeUDP()
|
||||
} else {
|
||||
go s.ServeConn()
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
func (s *TunnelClient) Clean() {
|
||||
s.StopService()
|
||||
}
|
||||
func (s *TunnelClient) GetInConn(typ uint8) (outConn net.Conn, err error) {
|
||||
outConn, err = s.GetConn()
|
||||
if err != nil {
|
||||
err = fmt.Errorf("connection err: %s", err)
|
||||
return
|
||||
}
|
||||
keyBytes := []byte(*s.cfg.Key)
|
||||
keyLength := uint16(len(keyBytes))
|
||||
pkg := new(bytes.Buffer)
|
||||
binary.Write(pkg, binary.LittleEndian, typ)
|
||||
binary.Write(pkg, binary.LittleEndian, keyLength)
|
||||
binary.Write(pkg, binary.LittleEndian, keyBytes)
|
||||
_, err = outConn.Write(pkg.Bytes())
|
||||
if err != nil {
|
||||
err = fmt.Errorf("write connection data err: %s ,retrying...", err)
|
||||
utils.CloseConn(&outConn)
|
||||
return
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *TunnelClient) GetConn() (conn net.Conn, err error) {
|
||||
var _conn tls.Conn
|
||||
_conn, err = utils.TlsConnectHost(*s.cfg.Parent, *s.cfg.Timeout, s.cfg.CertBytes, s.cfg.KeyBytes)
|
||||
if err == nil {
|
||||
conn = net.Conn(&_conn)
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *TunnelClient) ServeUDP() {
|
||||
var inConn net.Conn
|
||||
var err error
|
||||
for {
|
||||
for {
|
||||
inConn, err = s.GetInConn(CONN_CLIENT)
|
||||
if err != nil {
|
||||
utils.CloseConn(&inConn)
|
||||
log.Printf("connection err: %s, retrying...", err)
|
||||
time.Sleep(time.Second * 3)
|
||||
continue
|
||||
} else {
|
||||
break
|
||||
}
|
||||
}
|
||||
log.Printf("conn created , remote : %s ", inConn.RemoteAddr())
|
||||
for {
|
||||
srcAddr, body, err := utils.ReadUDPPacket(&inConn)
|
||||
if err == io.EOF || err == io.ErrUnexpectedEOF {
|
||||
log.Printf("connection %s released", srcAddr)
|
||||
utils.CloseConn(&inConn)
|
||||
break
|
||||
}
|
||||
//log.Printf("udp packet revecived:%s,%v", srcAddr, body)
|
||||
go s.processUDPPacket(&inConn, srcAddr, body)
|
||||
}
|
||||
}
|
||||
}
|
||||
func (s *TunnelClient) processUDPPacket(inConn *net.Conn, srcAddr string, body []byte) {
|
||||
dstAddr, err := net.ResolveUDPAddr("udp", *s.cfg.Local)
|
||||
if err != nil {
|
||||
log.Printf("can't resolve address: %s", err)
|
||||
utils.CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
clientSrcAddr := &net.UDPAddr{IP: net.IPv4zero, Port: 0}
|
||||
conn, err := net.DialUDP("udp", clientSrcAddr, dstAddr)
|
||||
if err != nil {
|
||||
log.Printf("connect to udp %s fail,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
conn.SetDeadline(time.Now().Add(time.Millisecond * time.Duration(*s.cfg.Timeout)))
|
||||
_, err = conn.Write(body)
|
||||
if err != nil {
|
||||
log.Printf("send udp packet to %s fail,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
//log.Printf("send udp packet to %s success", dstAddr.String())
|
||||
buf := make([]byte, 512)
|
||||
len, _, err := conn.ReadFromUDP(buf)
|
||||
if err != nil {
|
||||
log.Printf("read udp response from %s fail ,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
respBody := buf[0:len]
|
||||
//log.Printf("revecived udp packet from %s , %v", dstAddr.String(), respBody)
|
||||
_, err = (*inConn).Write(utils.UDPPacket(srcAddr, respBody))
|
||||
if err != nil {
|
||||
log.Printf("send udp response fail ,ERR:%s", err)
|
||||
utils.CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
//log.Printf("send udp response success ,from:%s", dstAddr.String())
|
||||
}
|
||||
func (s *TunnelClient) ServeConn() {
|
||||
var inConn, outConn net.Conn
|
||||
var err error
|
||||
for {
|
||||
inConn, err = s.GetInConn(CONN_CLIENT)
|
||||
if err != nil {
|
||||
utils.CloseConn(&inConn)
|
||||
log.Printf("connection err: %s, retrying...", err)
|
||||
time.Sleep(time.Second * 3)
|
||||
continue
|
||||
} else {
|
||||
break
|
||||
}
|
||||
}
|
||||
|
||||
i := 0
|
||||
for {
|
||||
i++
|
||||
outConn, err = utils.ConnectHost(*s.cfg.Local, *s.cfg.Timeout)
|
||||
if err == nil || i == 3 {
|
||||
break
|
||||
} else {
|
||||
if i == 3 {
|
||||
log.Printf("connect to %s err: %s, retrying...", *s.cfg.Local, err)
|
||||
time.Sleep(2 * time.Second)
|
||||
continue
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
if err != nil {
|
||||
utils.CloseConn(&inConn)
|
||||
utils.CloseConn(&outConn)
|
||||
log.Printf("build connection error, err: %s", err)
|
||||
return
|
||||
}
|
||||
|
||||
utils.IoBind(inConn, outConn, func(isSrcErr bool, err error) {
|
||||
log.Printf("%s conn %s - %s - %s - %s released", *s.cfg.Key, inConn.RemoteAddr(), inConn.LocalAddr(), outConn.LocalAddr(), outConn.RemoteAddr())
|
||||
utils.CloseConn(&inConn)
|
||||
utils.CloseConn(&outConn)
|
||||
}, func(i int, b bool) {}, 0)
|
||||
log.Printf("%s conn %s - %s - %s - %s created", *s.cfg.Key, inConn.RemoteAddr(), inConn.LocalAddr(), outConn.LocalAddr(), outConn.RemoteAddr())
|
||||
}
|
||||
@@ -0,0 +1,209 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"bufio"
|
||||
"bytes"
|
||||
"crypto/tls"
|
||||
"encoding/binary"
|
||||
"io"
|
||||
"log"
|
||||
"net"
|
||||
"proxy/utils"
|
||||
"runtime/debug"
|
||||
"strconv"
|
||||
"strings"
|
||||
"time"
|
||||
)
|
||||
|
||||
type TunnelServer struct {
|
||||
cfg TunnelServerArgs
|
||||
udpChn chan UDPItem
|
||||
sc utils.ServerChannel
|
||||
}
|
||||
|
||||
func NewTunnelServer() Service {
|
||||
return &TunnelServer{
|
||||
cfg: TunnelServerArgs{},
|
||||
udpChn: make(chan UDPItem, 50000),
|
||||
}
|
||||
}
|
||||
|
||||
type UDPItem struct {
|
||||
packet *[]byte
|
||||
localAddr *net.UDPAddr
|
||||
srcAddr *net.UDPAddr
|
||||
}
|
||||
|
||||
func (s *TunnelServer) InitService() {
|
||||
s.UDPConnDeamon()
|
||||
}
|
||||
func (s *TunnelServer) Check() {
|
||||
if *s.cfg.Parent != "" {
|
||||
log.Printf("use tls parent %s", *s.cfg.Parent)
|
||||
} else {
|
||||
log.Fatalf("parent required")
|
||||
}
|
||||
if s.cfg.CertBytes == nil || s.cfg.KeyBytes == nil {
|
||||
log.Fatalf("cert and key file required")
|
||||
}
|
||||
}
|
||||
func (s *TunnelServer) StopService() {
|
||||
}
|
||||
func (s *TunnelServer) Start(args interface{}) (err error) {
|
||||
s.cfg = args.(TunnelServerArgs)
|
||||
s.Check()
|
||||
s.InitService()
|
||||
host, port, _ := net.SplitHostPort(*s.cfg.Local)
|
||||
p, _ := strconv.Atoi(port)
|
||||
s.sc = utils.NewServerChannel(host, p)
|
||||
|
||||
if *s.cfg.IsUDP {
|
||||
err = s.sc.ListenUDP(func(packet []byte, localAddr, srcAddr *net.UDPAddr) {
|
||||
s.udpChn <- UDPItem{
|
||||
packet: &packet,
|
||||
localAddr: localAddr,
|
||||
srcAddr: srcAddr,
|
||||
}
|
||||
})
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
log.Printf("proxy on udp tunnel server mode %s", (*s.sc.UDPListener).LocalAddr())
|
||||
} else {
|
||||
err = s.sc.ListenTCP(func(inConn net.Conn) {
|
||||
defer func() {
|
||||
if err := recover(); err != nil {
|
||||
log.Printf("tserver conn handler crashed with err : %s \nstack: %s", err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
var outConn net.Conn
|
||||
for {
|
||||
outConn, err = s.GetOutConn()
|
||||
if err != nil {
|
||||
utils.CloseConn(&outConn)
|
||||
log.Printf("connect to %s fail, err: %s, retrying...", *s.cfg.Parent, err)
|
||||
time.Sleep(time.Second * 3)
|
||||
continue
|
||||
} else {
|
||||
break
|
||||
}
|
||||
}
|
||||
|
||||
utils.IoBind(inConn, outConn, func(isSrcErr bool, err error) {
|
||||
utils.CloseConn(&outConn)
|
||||
utils.CloseConn(&inConn)
|
||||
log.Printf("%s conn %s - %s - %s - %s released", *s.cfg.Key, inConn.RemoteAddr(), inConn.LocalAddr(), outConn.LocalAddr(), outConn.RemoteAddr())
|
||||
}, func(i int, b bool) {}, 0)
|
||||
|
||||
log.Printf("%s conn %s - %s - %s - %s created", *s.cfg.Key, inConn.RemoteAddr(), inConn.LocalAddr(), outConn.LocalAddr(), outConn.RemoteAddr())
|
||||
})
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
log.Printf("proxy on tunnel server mode %s", (*s.sc.Listener).Addr())
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *TunnelServer) Clean() {
|
||||
s.StopService()
|
||||
}
|
||||
func (s *TunnelServer) GetOutConn() (outConn net.Conn, err error) {
|
||||
outConn, err = s.GetConn()
|
||||
if err != nil {
|
||||
log.Printf("connection err: %s", err)
|
||||
return
|
||||
}
|
||||
keyBytes := []byte(*s.cfg.Key)
|
||||
keyLength := uint16(len(keyBytes))
|
||||
pkg := new(bytes.Buffer)
|
||||
binary.Write(pkg, binary.LittleEndian, CONN_SERVER)
|
||||
binary.Write(pkg, binary.LittleEndian, keyLength)
|
||||
binary.Write(pkg, binary.LittleEndian, keyBytes)
|
||||
_, err = outConn.Write(pkg.Bytes())
|
||||
if err != nil {
|
||||
log.Printf("write connection data err: %s ,retrying...", err)
|
||||
utils.CloseConn(&outConn)
|
||||
return
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *TunnelServer) GetConn() (conn net.Conn, err error) {
|
||||
var _conn tls.Conn
|
||||
_conn, err = utils.TlsConnectHost(*s.cfg.Parent, *s.cfg.Timeout, s.cfg.CertBytes, s.cfg.KeyBytes)
|
||||
if err == nil {
|
||||
conn = net.Conn(&_conn)
|
||||
}
|
||||
return
|
||||
}
|
||||
func (s *TunnelServer) UDPConnDeamon() {
|
||||
go func() {
|
||||
defer func() {
|
||||
if err := recover(); err != nil {
|
||||
log.Printf("udp conn deamon crashed with err : %s \nstack: %s", err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
var outConn net.Conn
|
||||
var cmdChn = make(chan bool, 1)
|
||||
|
||||
var err error
|
||||
for {
|
||||
item := <-s.udpChn
|
||||
RETRY:
|
||||
if outConn == nil {
|
||||
for {
|
||||
outConn, err = s.GetOutConn()
|
||||
if err != nil {
|
||||
cmdChn <- true
|
||||
outConn = nil
|
||||
utils.CloseConn(&outConn)
|
||||
log.Printf("connect to %s fail, err: %s, retrying...", *s.cfg.Parent, err)
|
||||
time.Sleep(time.Second * 3)
|
||||
continue
|
||||
} else {
|
||||
go func(outConn net.Conn) {
|
||||
go func() {
|
||||
<-cmdChn
|
||||
outConn.Close()
|
||||
}()
|
||||
for {
|
||||
srcAddrFromConn, body, err := utils.ReadUDPPacket(&outConn)
|
||||
if err == io.EOF || err == io.ErrUnexpectedEOF {
|
||||
log.Printf("udp connection deamon exited, %s -> %s", outConn.LocalAddr(), outConn.RemoteAddr())
|
||||
break
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("parse revecived udp packet fail, err: %s", err)
|
||||
continue
|
||||
}
|
||||
//log.Printf("udp packet revecived over parent , local:%s", srcAddrFromConn)
|
||||
_srcAddr := strings.Split(srcAddrFromConn, ":")
|
||||
if len(_srcAddr) != 2 {
|
||||
log.Printf("parse revecived udp packet fail, addr error : %s", srcAddrFromConn)
|
||||
continue
|
||||
}
|
||||
port, _ := strconv.Atoi(_srcAddr[1])
|
||||
dstAddr := &net.UDPAddr{IP: net.ParseIP(_srcAddr[0]), Port: port}
|
||||
_, err = s.sc.UDPListener.WriteToUDP(body, dstAddr)
|
||||
if err != nil {
|
||||
log.Printf("udp response to local %s fail,ERR:%s", srcAddrFromConn, err)
|
||||
continue
|
||||
}
|
||||
//log.Printf("udp response to local %s success", srcAddrFromConn)
|
||||
}
|
||||
}(outConn)
|
||||
break
|
||||
}
|
||||
}
|
||||
}
|
||||
writer := bufio.NewWriter(outConn)
|
||||
writer.Write(utils.UDPPacket(item.srcAddr.String(), *item.packet))
|
||||
err := writer.Flush()
|
||||
if err != nil {
|
||||
outConn = nil
|
||||
log.Printf("write udp packet to %s fail ,flush err:%s", *s.cfg.Parent, err)
|
||||
goto RETRY
|
||||
}
|
||||
//log.Printf("write packet %v", *item.packet)
|
||||
}
|
||||
}()
|
||||
}
|
||||
@@ -0,0 +1,211 @@
|
||||
package services
|
||||
|
||||
import (
|
||||
"bufio"
|
||||
"fmt"
|
||||
"hash/crc32"
|
||||
"io"
|
||||
"log"
|
||||
"net"
|
||||
"proxy/utils"
|
||||
"runtime/debug"
|
||||
"strconv"
|
||||
"strings"
|
||||
"time"
|
||||
)
|
||||
|
||||
type UDP struct {
|
||||
p utils.ConcurrentMap
|
||||
outPool utils.OutPool
|
||||
cfg UDPArgs
|
||||
sc *utils.ServerChannel
|
||||
}
|
||||
|
||||
func NewUDP() Service {
|
||||
return &UDP{
|
||||
outPool: utils.OutPool{},
|
||||
p: utils.NewConcurrentMap(),
|
||||
}
|
||||
}
|
||||
func (s *UDP) InitService() {
|
||||
if *s.cfg.ParentType != TYPE_UDP {
|
||||
s.InitOutConnPool()
|
||||
}
|
||||
}
|
||||
func (s *UDP) StopService() {
|
||||
if s.outPool.Pool != nil {
|
||||
s.outPool.Pool.ReleaseAll()
|
||||
}
|
||||
}
|
||||
func (s *UDP) Start(args interface{}) (err error) {
|
||||
s.cfg = args.(UDPArgs)
|
||||
if *s.cfg.Parent != "" {
|
||||
log.Printf("use %s parent %s", *s.cfg.ParentType, *s.cfg.Parent)
|
||||
} else {
|
||||
log.Fatalf("parent required for udp %s", *s.cfg.Local)
|
||||
}
|
||||
|
||||
s.InitService()
|
||||
|
||||
host, port, _ := net.SplitHostPort(*s.cfg.Local)
|
||||
p, _ := strconv.Atoi(port)
|
||||
sc := utils.NewServerChannel(host, p)
|
||||
s.sc = &sc
|
||||
err = sc.ListenUDP(s.callback)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
log.Printf("udp proxy on %s", (*sc.UDPListener).LocalAddr())
|
||||
return
|
||||
}
|
||||
|
||||
func (s *UDP) Clean() {
|
||||
s.StopService()
|
||||
}
|
||||
func (s *UDP) callback(packet []byte, localAddr, srcAddr *net.UDPAddr) {
|
||||
defer func() {
|
||||
if err := recover(); err != nil {
|
||||
log.Printf("udp conn handler crashed with err : %s \nstack: %s", err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
var err error
|
||||
switch *s.cfg.ParentType {
|
||||
case TYPE_TCP:
|
||||
fallthrough
|
||||
case TYPE_TLS:
|
||||
err = s.OutToTCP(packet, localAddr, srcAddr)
|
||||
case TYPE_UDP:
|
||||
err = s.OutToUDP(packet, localAddr, srcAddr)
|
||||
default:
|
||||
err = fmt.Errorf("unkown parent type %s", *s.cfg.ParentType)
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("connect to %s parent %s fail, ERR:%s", *s.cfg.ParentType, *s.cfg.Parent, err)
|
||||
}
|
||||
}
|
||||
func (s *UDP) GetConn(connKey string) (conn net.Conn, isNew bool, err error) {
|
||||
isNew = !s.p.Has(connKey)
|
||||
var _conn interface{}
|
||||
if isNew {
|
||||
_conn, err = s.outPool.Pool.Get()
|
||||
if err != nil {
|
||||
return nil, false, err
|
||||
}
|
||||
s.p.Set(connKey, _conn)
|
||||
} else {
|
||||
_conn, _ = s.p.Get(connKey)
|
||||
}
|
||||
conn = _conn.(net.Conn)
|
||||
return
|
||||
}
|
||||
func (s *UDP) OutToTCP(packet []byte, localAddr, srcAddr *net.UDPAddr) (err error) {
|
||||
numLocal := crc32.ChecksumIEEE([]byte(localAddr.String()))
|
||||
numSrc := crc32.ChecksumIEEE([]byte(srcAddr.String()))
|
||||
mod := uint32(*s.cfg.PoolSize)
|
||||
if mod == 0 {
|
||||
mod = 10
|
||||
}
|
||||
connKey := uint64((numLocal/10)*10 + numSrc%mod)
|
||||
conn, isNew, err := s.GetConn(fmt.Sprintf("%d", connKey))
|
||||
if err != nil {
|
||||
log.Printf("upd get conn to %s parent %s fail, ERR:%s", *s.cfg.ParentType, *s.cfg.Parent, err)
|
||||
return
|
||||
}
|
||||
if isNew {
|
||||
go func() {
|
||||
defer func() {
|
||||
if err := recover(); err != nil {
|
||||
log.Printf("udp conn handler out to tcp crashed with err : %s \nstack: %s", err, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
log.Printf("conn %d created , local: %s", connKey, srcAddr.String())
|
||||
for {
|
||||
srcAddrFromConn, body, err := utils.ReadUDPPacket(&conn)
|
||||
if err == io.EOF || err == io.ErrUnexpectedEOF {
|
||||
//log.Printf("connection %d released", connKey)
|
||||
s.p.Remove(fmt.Sprintf("%d", connKey))
|
||||
break
|
||||
}
|
||||
if err != nil {
|
||||
log.Printf("parse revecived udp packet fail, err: %s", err)
|
||||
continue
|
||||
}
|
||||
//log.Printf("udp packet revecived over parent , local:%s", srcAddrFromConn)
|
||||
_srcAddr := strings.Split(srcAddrFromConn, ":")
|
||||
if len(_srcAddr) != 2 {
|
||||
log.Printf("parse revecived udp packet fail, addr error : %s", srcAddrFromConn)
|
||||
continue
|
||||
}
|
||||
port, _ := strconv.Atoi(_srcAddr[1])
|
||||
dstAddr := &net.UDPAddr{IP: net.ParseIP(_srcAddr[0]), Port: port}
|
||||
_, err = s.sc.UDPListener.WriteToUDP(body, dstAddr)
|
||||
if err != nil {
|
||||
log.Printf("udp response to local %s fail,ERR:%s", srcAddr, err)
|
||||
continue
|
||||
}
|
||||
//log.Printf("udp response to local %s success", srcAddr)
|
||||
}
|
||||
}()
|
||||
}
|
||||
//log.Printf("select conn %d , local: %s", connKey, srcAddr.String())
|
||||
writer := bufio.NewWriter(conn)
|
||||
//fmt.Println(conn, writer)
|
||||
writer.Write(utils.UDPPacket(srcAddr.String(), packet))
|
||||
err = writer.Flush()
|
||||
if err != nil {
|
||||
log.Printf("write udp packet to %s fail ,flush err:%s", *s.cfg.Parent, err)
|
||||
return
|
||||
}
|
||||
//log.Printf("write packet %v", packet)
|
||||
return
|
||||
}
|
||||
func (s *UDP) OutToUDP(packet []byte, localAddr, srcAddr *net.UDPAddr) (err error) {
|
||||
//log.Printf("udp packet revecived:%s,%v", srcAddr, packet)
|
||||
dstAddr, err := net.ResolveUDPAddr("udp", *s.cfg.Parent)
|
||||
if err != nil {
|
||||
log.Printf("resolve udp addr %s fail fail,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
clientSrcAddr := &net.UDPAddr{IP: net.IPv4zero, Port: 0}
|
||||
conn, err := net.DialUDP("udp", clientSrcAddr, dstAddr)
|
||||
if err != nil {
|
||||
log.Printf("connect to udp %s fail,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
conn.SetDeadline(time.Now().Add(time.Millisecond * time.Duration(*s.cfg.Timeout)))
|
||||
_, err = conn.Write(packet)
|
||||
if err != nil {
|
||||
log.Printf("send udp packet to %s fail,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
//log.Printf("send udp packet to %s success", dstAddr.String())
|
||||
buf := make([]byte, 512)
|
||||
len, _, err := conn.ReadFromUDP(buf)
|
||||
if err != nil {
|
||||
log.Printf("read udp response from %s fail ,ERR:%s", dstAddr.String(), err)
|
||||
return
|
||||
}
|
||||
//log.Printf("revecived udp packet from %s , %v", dstAddr.String(), respBody)
|
||||
_, err = s.sc.UDPListener.WriteToUDP(buf[0:len], srcAddr)
|
||||
if err != nil {
|
||||
log.Printf("send udp response to cluster fail ,ERR:%s", err)
|
||||
return
|
||||
}
|
||||
//log.Printf("send udp response to cluster success ,from:%s", dstAddr.String())
|
||||
return
|
||||
}
|
||||
func (s *UDP) InitOutConnPool() {
|
||||
if *s.cfg.ParentType == TYPE_TLS || *s.cfg.ParentType == TYPE_TCP {
|
||||
//dur int, isTLS bool, certBytes, keyBytes []byte,
|
||||
//parent string, timeout int, InitialCap int, MaxCap int
|
||||
s.outPool = utils.NewOutPool(
|
||||
*s.cfg.CheckParentInterval,
|
||||
*s.cfg.ParentType == TYPE_TLS,
|
||||
s.cfg.CertBytes, s.cfg.KeyBytes,
|
||||
*s.cfg.Parent,
|
||||
*s.cfg.Timeout,
|
||||
*s.cfg.PoolSize,
|
||||
*s.cfg.PoolSize*2,
|
||||
)
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,3 @@
|
||||
#!/bin/bash
|
||||
rm -rf /usr/bin/proxy
|
||||
echo "uninstall done"
|
||||
@@ -0,0 +1,363 @@
|
||||
package utils
|
||||
|
||||
import (
|
||||
"bufio"
|
||||
"bytes"
|
||||
"crypto/tls"
|
||||
"crypto/x509"
|
||||
"encoding/binary"
|
||||
"errors"
|
||||
"fmt"
|
||||
"io"
|
||||
"log"
|
||||
"net"
|
||||
"net/http"
|
||||
"os"
|
||||
"os/exec"
|
||||
"sync"
|
||||
|
||||
"runtime/debug"
|
||||
"strconv"
|
||||
"strings"
|
||||
"time"
|
||||
)
|
||||
|
||||
func IoBind(dst io.ReadWriter, src io.ReadWriter, fn func(isSrcErr bool, err error), cfn func(count int, isPositive bool), bytesPreSec float64) {
|
||||
var one = &sync.Once{}
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("IoBind crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
var err error
|
||||
var isSrcErr bool
|
||||
if bytesPreSec > 0 {
|
||||
newreader := NewReader(src)
|
||||
newreader.SetRateLimit(bytesPreSec)
|
||||
_, isSrcErr, err = ioCopy(dst, newreader, func(c int) {
|
||||
cfn(c, false)
|
||||
})
|
||||
|
||||
} else {
|
||||
_, isSrcErr, err = ioCopy(dst, src, func(c int) {
|
||||
cfn(c, false)
|
||||
})
|
||||
}
|
||||
if err != nil {
|
||||
one.Do(func() {
|
||||
fn(isSrcErr, err)
|
||||
})
|
||||
}
|
||||
}()
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("IoBind crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
var err error
|
||||
var isSrcErr bool
|
||||
if bytesPreSec > 0 {
|
||||
newReader := NewReader(dst)
|
||||
newReader.SetRateLimit(bytesPreSec)
|
||||
_, isSrcErr, err = ioCopy(src, newReader, func(c int) {
|
||||
cfn(c, true)
|
||||
})
|
||||
} else {
|
||||
_, isSrcErr, err = ioCopy(src, dst, func(c int) {
|
||||
cfn(c, true)
|
||||
})
|
||||
}
|
||||
if err != nil {
|
||||
one.Do(func() {
|
||||
fn(isSrcErr, err)
|
||||
})
|
||||
}
|
||||
}()
|
||||
}
|
||||
func ioCopy(dst io.Writer, src io.Reader, fn ...func(count int)) (written int64, isSrcErr bool, err error) {
|
||||
buf := make([]byte, 32*1024)
|
||||
for {
|
||||
nr, er := src.Read(buf)
|
||||
if nr > 0 {
|
||||
nw, ew := dst.Write(buf[0:nr])
|
||||
if nw > 0 {
|
||||
written += int64(nw)
|
||||
if len(fn) == 1 {
|
||||
fn[0](nw)
|
||||
}
|
||||
}
|
||||
if ew != nil {
|
||||
err = ew
|
||||
break
|
||||
}
|
||||
if nr != nw {
|
||||
err = io.ErrShortWrite
|
||||
break
|
||||
}
|
||||
}
|
||||
if er != nil {
|
||||
err = er
|
||||
isSrcErr = true
|
||||
break
|
||||
}
|
||||
}
|
||||
return written, isSrcErr, err
|
||||
}
|
||||
func TlsConnectHost(host string, timeout int, certBytes, keyBytes []byte) (conn tls.Conn, err error) {
|
||||
h := strings.Split(host, ":")
|
||||
port, _ := strconv.Atoi(h[1])
|
||||
return TlsConnect(h[0], port, timeout, certBytes, keyBytes)
|
||||
}
|
||||
|
||||
func TlsConnect(host string, port, timeout int, certBytes, keyBytes []byte) (conn tls.Conn, err error) {
|
||||
conf, err := getRequestTlsConfig(certBytes, keyBytes)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
_conn, err := net.DialTimeout("tcp", fmt.Sprintf("%s:%d", host, port), time.Duration(timeout)*time.Millisecond)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
return *tls.Client(_conn, conf), err
|
||||
}
|
||||
func getRequestTlsConfig(certBytes, keyBytes []byte) (conf *tls.Config, err error) {
|
||||
var cert tls.Certificate
|
||||
cert, err = tls.X509KeyPair(certBytes, keyBytes)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
serverCertPool := x509.NewCertPool()
|
||||
ok := serverCertPool.AppendCertsFromPEM(certBytes)
|
||||
if !ok {
|
||||
err = errors.New("failed to parse root certificate")
|
||||
}
|
||||
conf = &tls.Config{
|
||||
RootCAs: serverCertPool,
|
||||
Certificates: []tls.Certificate{cert},
|
||||
ServerName: "proxy",
|
||||
InsecureSkipVerify: false,
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func ConnectHost(hostAndPort string, timeout int) (conn net.Conn, err error) {
|
||||
conn, err = net.DialTimeout("tcp", hostAndPort, time.Duration(timeout)*time.Millisecond)
|
||||
return
|
||||
}
|
||||
func ListenTls(ip string, port int, certBytes, keyBytes []byte) (ln *net.Listener, err error) {
|
||||
var cert tls.Certificate
|
||||
cert, err = tls.X509KeyPair(certBytes, keyBytes)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
clientCertPool := x509.NewCertPool()
|
||||
ok := clientCertPool.AppendCertsFromPEM(certBytes)
|
||||
if !ok {
|
||||
err = errors.New("failed to parse root certificate")
|
||||
}
|
||||
config := &tls.Config{
|
||||
ClientCAs: clientCertPool,
|
||||
ServerName: "proxy",
|
||||
Certificates: []tls.Certificate{cert},
|
||||
ClientAuth: tls.RequireAndVerifyClientCert,
|
||||
}
|
||||
_ln, err := tls.Listen("tcp", fmt.Sprintf("%s:%d", ip, port), config)
|
||||
if err == nil {
|
||||
ln = &_ln
|
||||
}
|
||||
return
|
||||
}
|
||||
func PathExists(_path string) bool {
|
||||
_, err := os.Stat(_path)
|
||||
if err != nil && os.IsNotExist(err) {
|
||||
return false
|
||||
}
|
||||
return true
|
||||
}
|
||||
func HTTPGet(URL string, timeout int) (err error) {
|
||||
tr := &http.Transport{}
|
||||
var resp *http.Response
|
||||
var client *http.Client
|
||||
defer func() {
|
||||
if resp != nil && resp.Body != nil {
|
||||
resp.Body.Close()
|
||||
}
|
||||
tr.CloseIdleConnections()
|
||||
}()
|
||||
client = &http.Client{Timeout: time.Millisecond * time.Duration(timeout), Transport: tr}
|
||||
resp, err = client.Get(URL)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func CloseConn(conn *net.Conn) {
|
||||
if conn != nil && *conn != nil {
|
||||
(*conn).SetDeadline(time.Now().Add(time.Millisecond))
|
||||
(*conn).Close()
|
||||
}
|
||||
}
|
||||
func Keygen() (err error) {
|
||||
cmd := exec.Command("sh", "-c", "openssl genrsa -out proxy.key 2048")
|
||||
out, err := cmd.CombinedOutput()
|
||||
if err != nil {
|
||||
log.Printf("err:%s", err)
|
||||
return
|
||||
}
|
||||
fmt.Println(string(out))
|
||||
cmd = exec.Command("sh", "-c", `openssl req -new -key proxy.key -x509 -days 3650 -out proxy.crt -subj /C=CN/ST=BJ/O="Localhost Ltd"/CN=proxy`)
|
||||
out, err = cmd.CombinedOutput()
|
||||
if err != nil {
|
||||
log.Printf("err:%s", err)
|
||||
return
|
||||
}
|
||||
fmt.Println(string(out))
|
||||
return
|
||||
}
|
||||
func GetAllInterfaceAddr() ([]net.IP, error) {
|
||||
|
||||
ifaces, err := net.Interfaces()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
addresses := []net.IP{}
|
||||
for _, iface := range ifaces {
|
||||
|
||||
if iface.Flags&net.FlagUp == 0 {
|
||||
continue // interface down
|
||||
}
|
||||
// if iface.Flags&net.FlagLoopback != 0 {
|
||||
// continue // loopback interface
|
||||
// }
|
||||
addrs, err := iface.Addrs()
|
||||
if err != nil {
|
||||
continue
|
||||
}
|
||||
|
||||
for _, addr := range addrs {
|
||||
var ip net.IP
|
||||
switch v := addr.(type) {
|
||||
case *net.IPNet:
|
||||
ip = v.IP
|
||||
case *net.IPAddr:
|
||||
ip = v.IP
|
||||
}
|
||||
// if ip == nil || ip.IsLoopback() {
|
||||
// continue
|
||||
// }
|
||||
ip = ip.To4()
|
||||
if ip == nil {
|
||||
continue // not an ipv4 address
|
||||
}
|
||||
addresses = append(addresses, ip)
|
||||
}
|
||||
}
|
||||
if len(addresses) == 0 {
|
||||
return nil, fmt.Errorf("no address Found, net.InterfaceAddrs: %v", addresses)
|
||||
}
|
||||
//only need first
|
||||
return addresses, nil
|
||||
}
|
||||
func UDPPacket(srcAddr string, packet []byte) []byte {
|
||||
addrBytes := []byte(srcAddr)
|
||||
addrLength := uint16(len(addrBytes))
|
||||
bodyLength := uint16(len(packet))
|
||||
pkg := new(bytes.Buffer)
|
||||
binary.Write(pkg, binary.LittleEndian, addrLength)
|
||||
binary.Write(pkg, binary.LittleEndian, addrBytes)
|
||||
binary.Write(pkg, binary.LittleEndian, bodyLength)
|
||||
binary.Write(pkg, binary.LittleEndian, packet)
|
||||
return pkg.Bytes()
|
||||
}
|
||||
func ReadUDPPacket(conn *net.Conn) (srcAddr string, packet []byte, err error) {
|
||||
reader := bufio.NewReader(*conn)
|
||||
var addrLength uint16
|
||||
var bodyLength uint16
|
||||
err = binary.Read(reader, binary.LittleEndian, &addrLength)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
_srcAddr := make([]byte, addrLength)
|
||||
n, err := reader.Read(_srcAddr)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
if n != int(addrLength) {
|
||||
return
|
||||
}
|
||||
srcAddr = string(_srcAddr)
|
||||
|
||||
err = binary.Read(reader, binary.LittleEndian, &bodyLength)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
packet = make([]byte, bodyLength)
|
||||
n, err = reader.Read(packet)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
if n != int(bodyLength) {
|
||||
return
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
// type sockaddr struct {
|
||||
// family uint16
|
||||
// data [14]byte
|
||||
// }
|
||||
|
||||
// const SO_ORIGINAL_DST = 80
|
||||
|
||||
// realServerAddress returns an intercepted connection's original destination.
|
||||
// func realServerAddress(conn *net.Conn) (string, error) {
|
||||
// tcpConn, ok := (*conn).(*net.TCPConn)
|
||||
// if !ok {
|
||||
// return "", errors.New("not a TCPConn")
|
||||
// }
|
||||
|
||||
// file, err := tcpConn.File()
|
||||
// if err != nil {
|
||||
// return "", err
|
||||
// }
|
||||
|
||||
// // To avoid potential problems from making the socket non-blocking.
|
||||
// tcpConn.Close()
|
||||
// *conn, err = net.FileConn(file)
|
||||
// if err != nil {
|
||||
// return "", err
|
||||
// }
|
||||
|
||||
// defer file.Close()
|
||||
// fd := file.Fd()
|
||||
|
||||
// var addr sockaddr
|
||||
// size := uint32(unsafe.Sizeof(addr))
|
||||
// err = getsockopt(int(fd), syscall.SOL_IP, SO_ORIGINAL_DST, uintptr(unsafe.Pointer(&addr)), &size)
|
||||
// if err != nil {
|
||||
// return "", err
|
||||
// }
|
||||
|
||||
// var ip net.IP
|
||||
// switch addr.family {
|
||||
// case syscall.AF_INET:
|
||||
// ip = addr.data[2:6]
|
||||
// default:
|
||||
// return "", errors.New("unrecognized address family")
|
||||
// }
|
||||
|
||||
// port := int(addr.data[0])<<8 + int(addr.data[1])
|
||||
|
||||
// return net.JoinHostPort(ip.String(), strconv.Itoa(port)), nil
|
||||
// }
|
||||
|
||||
// func getsockopt(s int, level int, name int, val uintptr, vallen *uint32) (err error) {
|
||||
// _, _, e1 := syscall.Syscall6(syscall.SYS_GETSOCKOPT, uintptr(s), uintptr(level), uintptr(name), uintptr(val), uintptr(unsafe.Pointer(vallen)), 0)
|
||||
// if e1 != 0 {
|
||||
// err = e1
|
||||
// }
|
||||
// return
|
||||
// }
|
||||
@@ -0,0 +1,97 @@
|
||||
package utils
|
||||
|
||||
import (
|
||||
"context"
|
||||
"io"
|
||||
"time"
|
||||
|
||||
"golang.org/x/time/rate"
|
||||
)
|
||||
|
||||
const burstLimit = 1000 * 1000 * 1000
|
||||
|
||||
type Reader struct {
|
||||
r io.Reader
|
||||
limiter *rate.Limiter
|
||||
ctx context.Context
|
||||
}
|
||||
|
||||
type Writer struct {
|
||||
w io.Writer
|
||||
limiter *rate.Limiter
|
||||
ctx context.Context
|
||||
}
|
||||
|
||||
// NewReader returns a reader that implements io.Reader with rate limiting.
|
||||
func NewReader(r io.Reader) *Reader {
|
||||
return &Reader{
|
||||
r: r,
|
||||
ctx: context.Background(),
|
||||
}
|
||||
}
|
||||
|
||||
// NewReaderWithContext returns a reader that implements io.Reader with rate limiting.
|
||||
func NewReaderWithContext(r io.Reader, ctx context.Context) *Reader {
|
||||
return &Reader{
|
||||
r: r,
|
||||
ctx: ctx,
|
||||
}
|
||||
}
|
||||
|
||||
// NewWriter returns a writer that implements io.Writer with rate limiting.
|
||||
func NewWriter(w io.Writer) *Writer {
|
||||
return &Writer{
|
||||
w: w,
|
||||
ctx: context.Background(),
|
||||
}
|
||||
}
|
||||
|
||||
// NewWriterWithContext returns a writer that implements io.Writer with rate limiting.
|
||||
func NewWriterWithContext(w io.Writer, ctx context.Context) *Writer {
|
||||
return &Writer{
|
||||
w: w,
|
||||
ctx: ctx,
|
||||
}
|
||||
}
|
||||
|
||||
// SetRateLimit sets rate limit (bytes/sec) to the reader.
|
||||
func (s *Reader) SetRateLimit(bytesPerSec float64) {
|
||||
s.limiter = rate.NewLimiter(rate.Limit(bytesPerSec), burstLimit)
|
||||
s.limiter.AllowN(time.Now(), burstLimit) // spend initial burst
|
||||
}
|
||||
|
||||
// Read reads bytes into p.
|
||||
func (s *Reader) Read(p []byte) (int, error) {
|
||||
if s.limiter == nil {
|
||||
return s.r.Read(p)
|
||||
}
|
||||
n, err := s.r.Read(p)
|
||||
if err != nil {
|
||||
return n, err
|
||||
}
|
||||
if err := s.limiter.WaitN(s.ctx, n); err != nil {
|
||||
return n, err
|
||||
}
|
||||
return n, nil
|
||||
}
|
||||
|
||||
// SetRateLimit sets rate limit (bytes/sec) to the writer.
|
||||
func (s *Writer) SetRateLimit(bytesPerSec float64) {
|
||||
s.limiter = rate.NewLimiter(rate.Limit(bytesPerSec), burstLimit)
|
||||
s.limiter.AllowN(time.Now(), burstLimit) // spend initial burst
|
||||
}
|
||||
|
||||
// Write writes bytes from p.
|
||||
func (s *Writer) Write(p []byte) (int, error) {
|
||||
if s.limiter == nil {
|
||||
return s.w.Write(p)
|
||||
}
|
||||
n, err := s.w.Write(p)
|
||||
if err != nil {
|
||||
return n, err
|
||||
}
|
||||
if err := s.limiter.WaitN(s.ctx, n); err != nil {
|
||||
return n, err
|
||||
}
|
||||
return n, err
|
||||
}
|
||||
@@ -0,0 +1,315 @@
|
||||
package utils
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"sync"
|
||||
)
|
||||
|
||||
var SHARD_COUNT = 32
|
||||
|
||||
// A "thread" safe map of type string:Anything.
|
||||
// To avoid lock bottlenecks this map is dived to several (SHARD_COUNT) map shards.
|
||||
type ConcurrentMap []*ConcurrentMapShared
|
||||
|
||||
// A "thread" safe string to anything map.
|
||||
type ConcurrentMapShared struct {
|
||||
items map[string]interface{}
|
||||
sync.RWMutex // Read Write mutex, guards access to internal map.
|
||||
}
|
||||
|
||||
// Creates a new concurrent map.
|
||||
func NewConcurrentMap() ConcurrentMap {
|
||||
m := make(ConcurrentMap, SHARD_COUNT)
|
||||
for i := 0; i < SHARD_COUNT; i++ {
|
||||
m[i] = &ConcurrentMapShared{items: make(map[string]interface{})}
|
||||
}
|
||||
return m
|
||||
}
|
||||
|
||||
// GetShard returns shard under given key
|
||||
func (m ConcurrentMap) GetShard(key string) *ConcurrentMapShared {
|
||||
return m[uint(fnv32(key))%uint(SHARD_COUNT)]
|
||||
}
|
||||
|
||||
func (m ConcurrentMap) MSet(data map[string]interface{}) {
|
||||
for key, value := range data {
|
||||
shard := m.GetShard(key)
|
||||
shard.Lock()
|
||||
shard.items[key] = value
|
||||
shard.Unlock()
|
||||
}
|
||||
}
|
||||
|
||||
// Sets the given value under the specified key.
|
||||
func (m ConcurrentMap) Set(key string, value interface{}) {
|
||||
// Get map shard.
|
||||
shard := m.GetShard(key)
|
||||
shard.Lock()
|
||||
shard.items[key] = value
|
||||
shard.Unlock()
|
||||
}
|
||||
|
||||
// Callback to return new element to be inserted into the map
|
||||
// It is called while lock is held, therefore it MUST NOT
|
||||
// try to access other keys in same map, as it can lead to deadlock since
|
||||
// Go sync.RWLock is not reentrant
|
||||
type UpsertCb func(exist bool, valueInMap interface{}, newValue interface{}) interface{}
|
||||
|
||||
// Insert or Update - updates existing element or inserts a new one using UpsertCb
|
||||
func (m ConcurrentMap) Upsert(key string, value interface{}, cb UpsertCb) (res interface{}) {
|
||||
shard := m.GetShard(key)
|
||||
shard.Lock()
|
||||
v, ok := shard.items[key]
|
||||
res = cb(ok, v, value)
|
||||
shard.items[key] = res
|
||||
shard.Unlock()
|
||||
return res
|
||||
}
|
||||
|
||||
// Sets the given value under the specified key if no value was associated with it.
|
||||
func (m ConcurrentMap) SetIfAbsent(key string, value interface{}) bool {
|
||||
// Get map shard.
|
||||
shard := m.GetShard(key)
|
||||
shard.Lock()
|
||||
_, ok := shard.items[key]
|
||||
if !ok {
|
||||
shard.items[key] = value
|
||||
}
|
||||
shard.Unlock()
|
||||
return !ok
|
||||
}
|
||||
|
||||
// Get retrieves an element from map under given key.
|
||||
func (m ConcurrentMap) Get(key string) (interface{}, bool) {
|
||||
// Get shard
|
||||
shard := m.GetShard(key)
|
||||
shard.RLock()
|
||||
// Get item from shard.
|
||||
val, ok := shard.items[key]
|
||||
shard.RUnlock()
|
||||
return val, ok
|
||||
}
|
||||
|
||||
// Count returns the number of elements within the map.
|
||||
func (m ConcurrentMap) Count() int {
|
||||
count := 0
|
||||
for i := 0; i < SHARD_COUNT; i++ {
|
||||
shard := m[i]
|
||||
shard.RLock()
|
||||
count += len(shard.items)
|
||||
shard.RUnlock()
|
||||
}
|
||||
return count
|
||||
}
|
||||
|
||||
// Looks up an item under specified key
|
||||
func (m ConcurrentMap) Has(key string) bool {
|
||||
// Get shard
|
||||
shard := m.GetShard(key)
|
||||
shard.RLock()
|
||||
// See if element is within shard.
|
||||
_, ok := shard.items[key]
|
||||
shard.RUnlock()
|
||||
return ok
|
||||
}
|
||||
|
||||
// Remove removes an element from the map.
|
||||
func (m ConcurrentMap) Remove(key string) {
|
||||
// Try to get shard.
|
||||
shard := m.GetShard(key)
|
||||
shard.Lock()
|
||||
delete(shard.items, key)
|
||||
shard.Unlock()
|
||||
}
|
||||
|
||||
// Pop removes an element from the map and returns it
|
||||
func (m ConcurrentMap) Pop(key string) (v interface{}, exists bool) {
|
||||
// Try to get shard.
|
||||
shard := m.GetShard(key)
|
||||
shard.Lock()
|
||||
v, exists = shard.items[key]
|
||||
delete(shard.items, key)
|
||||
shard.Unlock()
|
||||
return v, exists
|
||||
}
|
||||
|
||||
// IsEmpty checks if map is empty.
|
||||
func (m ConcurrentMap) IsEmpty() bool {
|
||||
return m.Count() == 0
|
||||
}
|
||||
|
||||
// Used by the Iter & IterBuffered functions to wrap two variables together over a channel,
|
||||
type Tuple struct {
|
||||
Key string
|
||||
Val interface{}
|
||||
}
|
||||
|
||||
// Iter returns an iterator which could be used in a for range loop.
|
||||
//
|
||||
// Deprecated: using IterBuffered() will get a better performence
|
||||
func (m ConcurrentMap) Iter() <-chan Tuple {
|
||||
chans := snapshot(m)
|
||||
ch := make(chan Tuple)
|
||||
go fanIn(chans, ch)
|
||||
return ch
|
||||
}
|
||||
|
||||
// IterBuffered returns a buffered iterator which could be used in a for range loop.
|
||||
func (m ConcurrentMap) IterBuffered() <-chan Tuple {
|
||||
chans := snapshot(m)
|
||||
total := 0
|
||||
for _, c := range chans {
|
||||
total += cap(c)
|
||||
}
|
||||
ch := make(chan Tuple, total)
|
||||
go fanIn(chans, ch)
|
||||
return ch
|
||||
}
|
||||
|
||||
// Returns a array of channels that contains elements in each shard,
|
||||
// which likely takes a snapshot of `m`.
|
||||
// It returns once the size of each buffered channel is determined,
|
||||
// before all the channels are populated using goroutines.
|
||||
func snapshot(m ConcurrentMap) (chans []chan Tuple) {
|
||||
chans = make([]chan Tuple, SHARD_COUNT)
|
||||
wg := sync.WaitGroup{}
|
||||
wg.Add(SHARD_COUNT)
|
||||
// Foreach shard.
|
||||
for index, shard := range m {
|
||||
go func(index int, shard *ConcurrentMapShared) {
|
||||
// Foreach key, value pair.
|
||||
shard.RLock()
|
||||
chans[index] = make(chan Tuple, len(shard.items))
|
||||
wg.Done()
|
||||
for key, val := range shard.items {
|
||||
chans[index] <- Tuple{key, val}
|
||||
}
|
||||
shard.RUnlock()
|
||||
close(chans[index])
|
||||
}(index, shard)
|
||||
}
|
||||
wg.Wait()
|
||||
return chans
|
||||
}
|
||||
|
||||
// fanIn reads elements from channels `chans` into channel `out`
|
||||
func fanIn(chans []chan Tuple, out chan Tuple) {
|
||||
wg := sync.WaitGroup{}
|
||||
wg.Add(len(chans))
|
||||
for _, ch := range chans {
|
||||
go func(ch chan Tuple) {
|
||||
for t := range ch {
|
||||
out <- t
|
||||
}
|
||||
wg.Done()
|
||||
}(ch)
|
||||
}
|
||||
wg.Wait()
|
||||
close(out)
|
||||
}
|
||||
|
||||
// Items returns all items as map[string]interface{}
|
||||
func (m ConcurrentMap) Items() map[string]interface{} {
|
||||
tmp := make(map[string]interface{})
|
||||
|
||||
// Insert items to temporary map.
|
||||
for item := range m.IterBuffered() {
|
||||
tmp[item.Key] = item.Val
|
||||
}
|
||||
|
||||
return tmp
|
||||
}
|
||||
|
||||
// Iterator callback,called for every key,value found in
|
||||
// maps. RLock is held for all calls for a given shard
|
||||
// therefore callback sess consistent view of a shard,
|
||||
// but not across the shards
|
||||
type IterCb func(key string, v interface{})
|
||||
|
||||
// Callback based iterator, cheapest way to read
|
||||
// all elements in a map.
|
||||
func (m ConcurrentMap) IterCb(fn IterCb) {
|
||||
for idx := range m {
|
||||
shard := (m)[idx]
|
||||
shard.RLock()
|
||||
for key, value := range shard.items {
|
||||
fn(key, value)
|
||||
}
|
||||
shard.RUnlock()
|
||||
}
|
||||
}
|
||||
|
||||
// Keys returns all keys as []string
|
||||
func (m ConcurrentMap) Keys() []string {
|
||||
count := m.Count()
|
||||
ch := make(chan string, count)
|
||||
go func() {
|
||||
// Foreach shard.
|
||||
wg := sync.WaitGroup{}
|
||||
wg.Add(SHARD_COUNT)
|
||||
for _, shard := range m {
|
||||
go func(shard *ConcurrentMapShared) {
|
||||
// Foreach key, value pair.
|
||||
shard.RLock()
|
||||
for key := range shard.items {
|
||||
ch <- key
|
||||
}
|
||||
shard.RUnlock()
|
||||
wg.Done()
|
||||
}(shard)
|
||||
}
|
||||
wg.Wait()
|
||||
close(ch)
|
||||
}()
|
||||
|
||||
// Generate keys
|
||||
keys := make([]string, 0, count)
|
||||
for k := range ch {
|
||||
keys = append(keys, k)
|
||||
}
|
||||
return keys
|
||||
}
|
||||
|
||||
//Reviles ConcurrentMap "private" variables to json marshal.
|
||||
func (m ConcurrentMap) MarshalJSON() ([]byte, error) {
|
||||
// Create a temporary map, which will hold all item spread across shards.
|
||||
tmp := make(map[string]interface{})
|
||||
|
||||
// Insert items to temporary map.
|
||||
for item := range m.IterBuffered() {
|
||||
tmp[item.Key] = item.Val
|
||||
}
|
||||
return json.Marshal(tmp)
|
||||
}
|
||||
|
||||
func fnv32(key string) uint32 {
|
||||
hash := uint32(2166136261)
|
||||
const prime32 = uint32(16777619)
|
||||
for i := 0; i < len(key); i++ {
|
||||
hash *= prime32
|
||||
hash ^= uint32(key[i])
|
||||
}
|
||||
return hash
|
||||
}
|
||||
|
||||
// Concurrent map uses Interface{} as its value, therefor JSON Unmarshal
|
||||
// will probably won't know which to type to unmarshal into, in such case
|
||||
// we'll end up with a value of type map[string]interface{}, In most cases this isn't
|
||||
// out value type, this is why we've decided to remove this functionality.
|
||||
|
||||
// func (m *ConcurrentMap) UnmarshalJSON(b []byte) (err error) {
|
||||
// // Reverse process of Marshal.
|
||||
|
||||
// tmp := make(map[string]interface{})
|
||||
|
||||
// // Unmarshal into a single map.
|
||||
// if err := json.Unmarshal(b, &tmp); err != nil {
|
||||
// return nil
|
||||
// }
|
||||
|
||||
// // foreach key,value pair in temporary map insert into our concurrent map.
|
||||
// for key, val := range tmp {
|
||||
// m.Set(key, val)
|
||||
// }
|
||||
// return nil
|
||||
// }
|
||||
@@ -0,0 +1,145 @@
|
||||
package utils
|
||||
|
||||
import (
|
||||
"log"
|
||||
"sync"
|
||||
"time"
|
||||
)
|
||||
|
||||
//ConnPool to use
|
||||
type ConnPool interface {
|
||||
Get() (conn interface{}, err error)
|
||||
Put(conn interface{})
|
||||
ReleaseAll()
|
||||
Len() (length int)
|
||||
}
|
||||
type poolConfig struct {
|
||||
Factory func() (interface{}, error)
|
||||
IsActive func(interface{}) bool
|
||||
Release func(interface{})
|
||||
InitialCap int
|
||||
MaxCap int
|
||||
}
|
||||
|
||||
func NewConnPool(poolConfig poolConfig) (pool ConnPool, err error) {
|
||||
p := netPool{
|
||||
config: poolConfig,
|
||||
conns: make(chan interface{}, poolConfig.MaxCap),
|
||||
lock: &sync.Mutex{},
|
||||
}
|
||||
//log.Printf("pool MaxCap:%d", poolConfig.MaxCap)
|
||||
if poolConfig.MaxCap > 0 {
|
||||
err = p.initAutoFill(false)
|
||||
if err == nil {
|
||||
p.initAutoFill(true)
|
||||
}
|
||||
}
|
||||
return &p, nil
|
||||
}
|
||||
|
||||
type netPool struct {
|
||||
conns chan interface{}
|
||||
lock *sync.Mutex
|
||||
config poolConfig
|
||||
}
|
||||
|
||||
func (p *netPool) initAutoFill(async bool) (err error) {
|
||||
var worker = func() (err error) {
|
||||
for {
|
||||
//log.Printf("pool fill: %v , len: %d", p.Len() <= p.config.InitialCap/2, p.Len())
|
||||
if p.Len() <= p.config.InitialCap/2 {
|
||||
p.lock.Lock()
|
||||
errN := 0
|
||||
for i := 0; i < p.config.InitialCap; i++ {
|
||||
c, err := p.config.Factory()
|
||||
if err != nil {
|
||||
errN++
|
||||
if async {
|
||||
continue
|
||||
} else {
|
||||
p.lock.Unlock()
|
||||
return err
|
||||
}
|
||||
}
|
||||
select {
|
||||
case p.conns <- c:
|
||||
default:
|
||||
p.config.Release(c)
|
||||
break
|
||||
}
|
||||
if p.Len() >= p.config.InitialCap {
|
||||
break
|
||||
}
|
||||
}
|
||||
if errN > 0 {
|
||||
log.Printf("fill conn pool fail , ERRN:%d", errN)
|
||||
}
|
||||
p.lock.Unlock()
|
||||
}
|
||||
if !async {
|
||||
return
|
||||
}
|
||||
time.Sleep(time.Second * 2)
|
||||
}
|
||||
}
|
||||
if async {
|
||||
go worker()
|
||||
} else {
|
||||
err = worker()
|
||||
}
|
||||
return
|
||||
|
||||
}
|
||||
|
||||
func (p *netPool) Get() (conn interface{}, err error) {
|
||||
// defer func() {
|
||||
// log.Printf("pool len : %d", p.Len())
|
||||
// }()
|
||||
p.lock.Lock()
|
||||
defer p.lock.Unlock()
|
||||
// for {
|
||||
select {
|
||||
case conn = <-p.conns:
|
||||
if p.config.IsActive(conn) {
|
||||
return
|
||||
}
|
||||
p.config.Release(conn)
|
||||
default:
|
||||
conn, err = p.config.Factory()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return conn, nil
|
||||
}
|
||||
// }
|
||||
return
|
||||
}
|
||||
|
||||
func (p *netPool) Put(conn interface{}) {
|
||||
if conn == nil {
|
||||
return
|
||||
}
|
||||
p.lock.Lock()
|
||||
defer p.lock.Unlock()
|
||||
if !p.config.IsActive(conn) {
|
||||
p.config.Release(conn)
|
||||
}
|
||||
select {
|
||||
case p.conns <- conn:
|
||||
default:
|
||||
p.config.Release(conn)
|
||||
}
|
||||
}
|
||||
func (p *netPool) ReleaseAll() {
|
||||
p.lock.Lock()
|
||||
defer p.lock.Unlock()
|
||||
close(p.conns)
|
||||
for c := range p.conns {
|
||||
p.config.Release(c)
|
||||
}
|
||||
p.conns = make(chan interface{}, p.config.InitialCap)
|
||||
|
||||
}
|
||||
func (p *netPool) Len() (length int) {
|
||||
return len(p.conns)
|
||||
}
|
||||
@@ -0,0 +1,126 @@
|
||||
package utils
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"log"
|
||||
"net"
|
||||
"runtime/debug"
|
||||
)
|
||||
|
||||
type ServerChannel struct {
|
||||
ip string
|
||||
port int
|
||||
Listener *net.Listener
|
||||
UDPListener *net.UDPConn
|
||||
errAcceptHandler func(err error)
|
||||
}
|
||||
|
||||
func NewServerChannel(ip string, port int) ServerChannel {
|
||||
return ServerChannel{
|
||||
ip: ip,
|
||||
port: port,
|
||||
errAcceptHandler: func(err error) {
|
||||
fmt.Printf("accept error , ERR:%s", err)
|
||||
},
|
||||
}
|
||||
}
|
||||
func (sc *ServerChannel) SetErrAcceptHandler(fn func(err error)) {
|
||||
sc.errAcceptHandler = fn
|
||||
}
|
||||
func (sc *ServerChannel) ListenTls(certBytes, keyBytes []byte, fn func(conn net.Conn)) (err error) {
|
||||
sc.Listener, err = ListenTls(sc.ip, sc.port, certBytes, keyBytes)
|
||||
if err == nil {
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("ListenTls crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
for {
|
||||
var conn net.Conn
|
||||
conn, err = (*sc.Listener).Accept()
|
||||
if err == nil {
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("connection handler crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
fn(conn)
|
||||
}()
|
||||
} else {
|
||||
sc.errAcceptHandler(err)
|
||||
(*sc.Listener).Close()
|
||||
break
|
||||
}
|
||||
}
|
||||
}()
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (sc *ServerChannel) ListenTCP(fn func(conn net.Conn)) (err error) {
|
||||
var l net.Listener
|
||||
l, err = net.Listen("tcp", fmt.Sprintf("%s:%d", sc.ip, sc.port))
|
||||
if err == nil {
|
||||
sc.Listener = &l
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("ListenTCP crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
for {
|
||||
var conn net.Conn
|
||||
conn, err = (*sc.Listener).Accept()
|
||||
if err == nil {
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("connection handler crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
fn(conn)
|
||||
}()
|
||||
} else {
|
||||
sc.errAcceptHandler(err)
|
||||
break
|
||||
}
|
||||
}
|
||||
}()
|
||||
}
|
||||
return
|
||||
}
|
||||
func (sc *ServerChannel) ListenUDP(fn func(packet []byte, localAddr, srcAddr *net.UDPAddr)) (err error) {
|
||||
addr := &net.UDPAddr{IP: net.ParseIP(sc.ip), Port: sc.port}
|
||||
l, err := net.ListenUDP("udp", addr)
|
||||
if err == nil {
|
||||
sc.UDPListener = l
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("ListenUDP crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
for {
|
||||
var buf = make([]byte, 2048)
|
||||
n, srcAddr, err := (*sc.UDPListener).ReadFromUDP(buf)
|
||||
if err == nil {
|
||||
packet := buf[0:n]
|
||||
go func() {
|
||||
defer func() {
|
||||
if e := recover(); e != nil {
|
||||
log.Printf("udp data handler crashed , err : %s , \ntrace:%s", e, string(debug.Stack()))
|
||||
}
|
||||
}()
|
||||
fn(packet, addr, srcAddr)
|
||||
}()
|
||||
} else {
|
||||
sc.errAcceptHandler(err)
|
||||
break
|
||||
}
|
||||
}
|
||||
}()
|
||||
}
|
||||
return
|
||||
}
|
||||
@@ -0,0 +1,462 @@
|
||||
package utils
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"crypto/tls"
|
||||
"encoding/base64"
|
||||
"fmt"
|
||||
"io"
|
||||
"io/ioutil"
|
||||
"log"
|
||||
"net"
|
||||
"net/url"
|
||||
"strings"
|
||||
"time"
|
||||
)
|
||||
|
||||
type Checker struct {
|
||||
data ConcurrentMap
|
||||
blockedMap ConcurrentMap
|
||||
directMap ConcurrentMap
|
||||
interval int64
|
||||
timeout int
|
||||
}
|
||||
type CheckerItem struct {
|
||||
IsHTTPS bool
|
||||
Method string
|
||||
URL string
|
||||
Domain string
|
||||
Host string
|
||||
Data []byte
|
||||
SuccessCount uint
|
||||
FailCount uint
|
||||
}
|
||||
|
||||
//NewChecker args:
|
||||
//timeout : tcp timeout milliseconds ,connect to host
|
||||
//interval: recheck domain interval seconds
|
||||
func NewChecker(timeout int, interval int64, blockedFile, directFile string) Checker {
|
||||
ch := Checker{
|
||||
data: NewConcurrentMap(),
|
||||
interval: interval,
|
||||
timeout: timeout,
|
||||
}
|
||||
ch.blockedMap = ch.loadMap(blockedFile)
|
||||
ch.directMap = ch.loadMap(directFile)
|
||||
if !ch.blockedMap.IsEmpty() {
|
||||
log.Printf("blocked file loaded , domains : %d", ch.blockedMap.Count())
|
||||
}
|
||||
if !ch.directMap.IsEmpty() {
|
||||
log.Printf("direct file loaded , domains : %d", ch.directMap.Count())
|
||||
}
|
||||
ch.start()
|
||||
return ch
|
||||
}
|
||||
|
||||
func (c *Checker) loadMap(f string) (dataMap ConcurrentMap) {
|
||||
dataMap = NewConcurrentMap()
|
||||
if PathExists(f) {
|
||||
_contents, err := ioutil.ReadFile(f)
|
||||
if err != nil {
|
||||
log.Printf("load file err:%s", err)
|
||||
return
|
||||
}
|
||||
for _, line := range strings.Split(string(_contents), "\n") {
|
||||
line = strings.Trim(line, "\r \t")
|
||||
if line != "" {
|
||||
dataMap.Set(line, true)
|
||||
}
|
||||
}
|
||||
}
|
||||
return
|
||||
}
|
||||
func (c *Checker) start() {
|
||||
go func() {
|
||||
for {
|
||||
for _, v := range c.data.Items() {
|
||||
go func(item CheckerItem) {
|
||||
if c.isNeedCheck(item) {
|
||||
//log.Printf("check %s", item.Domain)
|
||||
var conn net.Conn
|
||||
var err error
|
||||
if item.IsHTTPS {
|
||||
conn, err = ConnectHost(item.Host, c.timeout)
|
||||
if err == nil {
|
||||
conn.SetDeadline(time.Now().Add(time.Millisecond))
|
||||
conn.Close()
|
||||
}
|
||||
} else {
|
||||
err = HTTPGet(item.URL, c.timeout)
|
||||
}
|
||||
if err != nil {
|
||||
item.FailCount = item.FailCount + 1
|
||||
} else {
|
||||
item.SuccessCount = item.SuccessCount + 1
|
||||
}
|
||||
c.data.Set(item.Host, item)
|
||||
}
|
||||
}(v.(CheckerItem))
|
||||
}
|
||||
time.Sleep(time.Second * time.Duration(c.interval))
|
||||
}
|
||||
}()
|
||||
}
|
||||
func (c *Checker) isNeedCheck(item CheckerItem) bool {
|
||||
var minCount uint = 5
|
||||
if (item.SuccessCount >= minCount && item.SuccessCount > item.FailCount) ||
|
||||
(item.FailCount >= minCount && item.SuccessCount > item.FailCount) ||
|
||||
c.domainIsInMap(item.Host, false) ||
|
||||
c.domainIsInMap(item.Host, true) {
|
||||
return false
|
||||
}
|
||||
return true
|
||||
}
|
||||
func (c *Checker) IsBlocked(address string) (blocked bool, failN, successN uint) {
|
||||
if c.domainIsInMap(address, true) {
|
||||
//log.Printf("%s in blocked ? true", address)
|
||||
return true, 0, 0
|
||||
}
|
||||
if c.domainIsInMap(address, false) {
|
||||
//log.Printf("%s in direct ? true", address)
|
||||
return false, 0, 0
|
||||
}
|
||||
|
||||
_item, ok := c.data.Get(address)
|
||||
if !ok {
|
||||
//log.Printf("%s not in map, blocked true", address)
|
||||
return true, 0, 0
|
||||
}
|
||||
item := _item.(CheckerItem)
|
||||
|
||||
return item.FailCount >= item.SuccessCount, item.FailCount, item.SuccessCount
|
||||
}
|
||||
func (c *Checker) domainIsInMap(address string, blockedMap bool) bool {
|
||||
u, err := url.Parse("http://" + address)
|
||||
if err != nil {
|
||||
log.Printf("blocked check , url parse err:%s", err)
|
||||
return true
|
||||
}
|
||||
domainSlice := strings.Split(u.Hostname(), ".")
|
||||
if len(domainSlice) > 1 {
|
||||
subSlice := domainSlice[:len(domainSlice)-1]
|
||||
topDomain := strings.Join(domainSlice[len(domainSlice)-1:], ".")
|
||||
checkDomain := topDomain
|
||||
for i := len(subSlice) - 1; i >= 0; i-- {
|
||||
checkDomain = subSlice[i] + "." + checkDomain
|
||||
if !blockedMap && c.directMap.Has(checkDomain) {
|
||||
return true
|
||||
}
|
||||
if blockedMap && c.blockedMap.Has(checkDomain) {
|
||||
return true
|
||||
}
|
||||
}
|
||||
}
|
||||
return false
|
||||
}
|
||||
func (c *Checker) Add(address string, isHTTPS bool, method, URL string, data []byte) {
|
||||
if c.domainIsInMap(address, false) || c.domainIsInMap(address, true) {
|
||||
return
|
||||
}
|
||||
if !isHTTPS && strings.ToLower(method) != "get" {
|
||||
return
|
||||
}
|
||||
var item CheckerItem
|
||||
u := strings.Split(address, ":")
|
||||
item = CheckerItem{
|
||||
URL: URL,
|
||||
Domain: u[0],
|
||||
Host: address,
|
||||
Data: data,
|
||||
IsHTTPS: isHTTPS,
|
||||
Method: method,
|
||||
}
|
||||
c.data.SetIfAbsent(item.Host, item)
|
||||
}
|
||||
|
||||
type BasicAuth struct {
|
||||
data ConcurrentMap
|
||||
}
|
||||
|
||||
func NewBasicAuth() BasicAuth {
|
||||
return BasicAuth{
|
||||
data: NewConcurrentMap(),
|
||||
}
|
||||
}
|
||||
func (ba *BasicAuth) AddFromFile(file string) (n int, err error) {
|
||||
_content, err := ioutil.ReadFile(file)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
userpassArr := strings.Split(strings.Replace(string(_content), "\r", "", -1), "\n")
|
||||
for _, userpass := range userpassArr {
|
||||
if strings.HasPrefix("#", userpass) {
|
||||
continue
|
||||
}
|
||||
u := strings.Split(strings.Trim(userpass, " "), ":")
|
||||
if len(u) == 2 {
|
||||
ba.data.Set(u[0], u[1])
|
||||
n++
|
||||
}
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (ba *BasicAuth) Add(userpassArr []string) (n int) {
|
||||
for _, userpass := range userpassArr {
|
||||
u := strings.Split(userpass, ":")
|
||||
if len(u) == 2 {
|
||||
ba.data.Set(u[0], u[1])
|
||||
n++
|
||||
}
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (ba *BasicAuth) Check(userpass string) (ok bool) {
|
||||
u := strings.Split(strings.Trim(userpass, " "), ":")
|
||||
if len(u) == 2 {
|
||||
if p, _ok := ba.data.Get(u[0]); _ok {
|
||||
return p.(string) == u[1]
|
||||
}
|
||||
}
|
||||
return
|
||||
}
|
||||
func (ba *BasicAuth) Total() (n int) {
|
||||
n = ba.data.Count()
|
||||
return
|
||||
}
|
||||
|
||||
type HTTPRequest struct {
|
||||
HeadBuf []byte
|
||||
conn *net.Conn
|
||||
Host string
|
||||
Method string
|
||||
URL string
|
||||
hostOrURL string
|
||||
isBasicAuth bool
|
||||
basicAuth *BasicAuth
|
||||
}
|
||||
|
||||
func NewHTTPRequest(inConn *net.Conn, bufSize int, isBasicAuth bool, basicAuth *BasicAuth) (req HTTPRequest, err error) {
|
||||
buf := make([]byte, bufSize)
|
||||
len := 0
|
||||
req = HTTPRequest{
|
||||
conn: inConn,
|
||||
}
|
||||
len, err = (*inConn).Read(buf[:])
|
||||
if err != nil {
|
||||
if err != io.EOF {
|
||||
err = fmt.Errorf("http decoder read err:%s", err)
|
||||
}
|
||||
CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
req.HeadBuf = buf[:len]
|
||||
index := bytes.IndexByte(req.HeadBuf, '\n')
|
||||
if index == -1 {
|
||||
err = fmt.Errorf("http decoder data line err:%s", string(req.HeadBuf)[:50])
|
||||
CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
fmt.Sscanf(string(req.HeadBuf[:index]), "%s%s", &req.Method, &req.hostOrURL)
|
||||
if req.Method == "" || req.hostOrURL == "" {
|
||||
err = fmt.Errorf("http decoder data err:%s", string(req.HeadBuf)[:50])
|
||||
CloseConn(inConn)
|
||||
return
|
||||
}
|
||||
req.Method = strings.ToUpper(req.Method)
|
||||
req.isBasicAuth = isBasicAuth
|
||||
req.basicAuth = basicAuth
|
||||
log.Printf("%s:%s", req.Method, req.hostOrURL)
|
||||
|
||||
if req.IsHTTPS() {
|
||||
err = req.HTTPS()
|
||||
} else {
|
||||
err = req.HTTP()
|
||||
}
|
||||
return
|
||||
}
|
||||
func (req *HTTPRequest) HTTP() (err error) {
|
||||
if req.isBasicAuth {
|
||||
err = req.BasicAuth()
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
}
|
||||
req.URL, err = req.getHTTPURL()
|
||||
if err == nil {
|
||||
u, _ := url.Parse(req.URL)
|
||||
req.Host = u.Host
|
||||
req.addPortIfNot()
|
||||
}
|
||||
return
|
||||
}
|
||||
func (req *HTTPRequest) HTTPS() (err error) {
|
||||
req.Host = req.hostOrURL
|
||||
req.addPortIfNot()
|
||||
//_, err = fmt.Fprint(*req.conn, "HTTP/1.1 200 Connection established\r\n\r\n")
|
||||
return
|
||||
}
|
||||
func (req *HTTPRequest) HTTPSReply() (err error) {
|
||||
_, err = fmt.Fprint(*req.conn, "HTTP/1.1 200 Connection established\r\n\r\n")
|
||||
return
|
||||
}
|
||||
func (req *HTTPRequest) IsHTTPS() bool {
|
||||
return req.Method == "CONNECT"
|
||||
}
|
||||
|
||||
func (req *HTTPRequest) BasicAuth() (err error) {
|
||||
|
||||
//log.Printf("request :%s", string(b[:n]))
|
||||
authorization, err := req.getHeader("Authorization")
|
||||
if err != nil {
|
||||
fmt.Fprint((*req.conn), "HTTP/1.1 401 Unauthorized\r\nWWW-Authenticate: Basic realm=\"\"\r\n\r\nUnauthorized")
|
||||
CloseConn(req.conn)
|
||||
return
|
||||
}
|
||||
//log.Printf("Authorization:%s", authorization)
|
||||
basic := strings.Fields(authorization)
|
||||
if len(basic) != 2 {
|
||||
err = fmt.Errorf("authorization data error,ERR:%s", authorization)
|
||||
CloseConn(req.conn)
|
||||
return
|
||||
}
|
||||
user, err := base64.StdEncoding.DecodeString(basic[1])
|
||||
if err != nil {
|
||||
err = fmt.Errorf("authorization data parse error,ERR:%s", err)
|
||||
CloseConn(req.conn)
|
||||
return
|
||||
}
|
||||
authOk := (*req.basicAuth).Check(string(user))
|
||||
//log.Printf("auth %s,%v", string(user), authOk)
|
||||
if !authOk {
|
||||
fmt.Fprint((*req.conn), "HTTP/1.1 401 Unauthorized\r\n\r\nUnauthorized")
|
||||
CloseConn(req.conn)
|
||||
err = fmt.Errorf("basic auth fail")
|
||||
return
|
||||
}
|
||||
return
|
||||
}
|
||||
func (req *HTTPRequest) getHTTPURL() (URL string, err error) {
|
||||
if !strings.HasPrefix(req.hostOrURL, "/") {
|
||||
return req.hostOrURL, nil
|
||||
}
|
||||
_host, err := req.getHeader("host")
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
URL = fmt.Sprintf("http://%s%s", _host, req.hostOrURL)
|
||||
return
|
||||
}
|
||||
func (req *HTTPRequest) getHeader(key string) (val string, err error) {
|
||||
key = strings.ToUpper(key)
|
||||
lines := strings.Split(string(req.HeadBuf), "\r\n")
|
||||
for _, line := range lines {
|
||||
line := strings.SplitN(strings.Trim(line, "\r\n "), ":", 2)
|
||||
if len(line) == 2 {
|
||||
k := strings.ToUpper(strings.Trim(line[0], " "))
|
||||
v := strings.Trim(line[1], " ")
|
||||
if key == k {
|
||||
val = v
|
||||
return
|
||||
}
|
||||
}
|
||||
}
|
||||
err = fmt.Errorf("can not find HOST header")
|
||||
return
|
||||
}
|
||||
|
||||
func (req *HTTPRequest) addPortIfNot() (newHost string) {
|
||||
//newHost = req.Host
|
||||
port := "80"
|
||||
if req.IsHTTPS() {
|
||||
port = "443"
|
||||
}
|
||||
if (!strings.HasPrefix(req.Host, "[") && strings.Index(req.Host, ":") == -1) || (strings.HasPrefix(req.Host, "[") && strings.HasSuffix(req.Host, "]")) {
|
||||
//newHost = req.Host + ":" + port
|
||||
//req.headBuf = []byte(strings.Replace(string(req.headBuf), req.Host, newHost, 1))
|
||||
req.Host = req.Host + ":" + port
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
type OutPool struct {
|
||||
Pool ConnPool
|
||||
dur int
|
||||
isTLS bool
|
||||
certBytes []byte
|
||||
keyBytes []byte
|
||||
address string
|
||||
timeout int
|
||||
}
|
||||
|
||||
func NewOutPool(dur int, isTLS bool, certBytes, keyBytes []byte, address string, timeout int, InitialCap int, MaxCap int) (op OutPool) {
|
||||
op = OutPool{
|
||||
dur: dur,
|
||||
isTLS: isTLS,
|
||||
certBytes: certBytes,
|
||||
keyBytes: keyBytes,
|
||||
address: address,
|
||||
timeout: timeout,
|
||||
}
|
||||
var err error
|
||||
op.Pool, err = NewConnPool(poolConfig{
|
||||
IsActive: func(conn interface{}) bool { return true },
|
||||
Release: func(conn interface{}) {
|
||||
if conn != nil {
|
||||
conn.(net.Conn).SetDeadline(time.Now().Add(time.Millisecond))
|
||||
conn.(net.Conn).Close()
|
||||
// log.Println("conn released")
|
||||
}
|
||||
},
|
||||
InitialCap: InitialCap,
|
||||
MaxCap: MaxCap,
|
||||
Factory: func() (conn interface{}, err error) {
|
||||
conn, err = op.getConn()
|
||||
return
|
||||
},
|
||||
})
|
||||
if err != nil {
|
||||
log.Fatalf("init conn pool fail ,%s", err)
|
||||
} else {
|
||||
if InitialCap > 0 {
|
||||
log.Printf("init conn pool success")
|
||||
op.initPoolDeamon()
|
||||
} else {
|
||||
log.Printf("conn pool closed")
|
||||
}
|
||||
}
|
||||
return
|
||||
}
|
||||
func (op *OutPool) getConn() (conn interface{}, err error) {
|
||||
if op.isTLS {
|
||||
var _conn tls.Conn
|
||||
_conn, err = TlsConnectHost(op.address, op.timeout, op.certBytes, op.keyBytes)
|
||||
if err == nil {
|
||||
conn = net.Conn(&_conn)
|
||||
}
|
||||
} else {
|
||||
conn, err = ConnectHost(op.address, op.timeout)
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (op *OutPool) initPoolDeamon() {
|
||||
go func() {
|
||||
if op.dur <= 0 {
|
||||
return
|
||||
}
|
||||
log.Printf("pool deamon started")
|
||||
for {
|
||||
time.Sleep(time.Second * time.Duration(op.dur))
|
||||
conn, err := op.getConn()
|
||||
if err != nil {
|
||||
log.Printf("pool deamon err %s , release pool", err)
|
||||
op.Pool.ReleaseAll()
|
||||
} else {
|
||||
conn.(net.Conn).SetDeadline(time.Now().Add(time.Millisecond))
|
||||
conn.(net.Conn).Close()
|
||||
}
|
||||
}
|
||||
}()
|
||||
}
|
||||